
#FactCheck-Viral Video of Assam MLA Assaulting Man Misleadingly Shared as BJP MLA
Executive Summary
A video is being shared on social media with the claim that a BJP MLA assaulted a man during a bridge inauguration ceremony in Assam. In the viral clip, a man is seen grabbing a young man and slapping him amid a crowd. He is then seen uprooting a banana plant and attacking the same man with it. A research done by the Research Wing of the CyberPeace found the claim accompanying the viral video to be misleading. The research revealed that the man seen assaulting the youth is not a BJP MLA, but former AIUDF MLA Samsul Huda. The video is being shared on social media with his identity falsely described as that of a BJP MLA.
Claim:
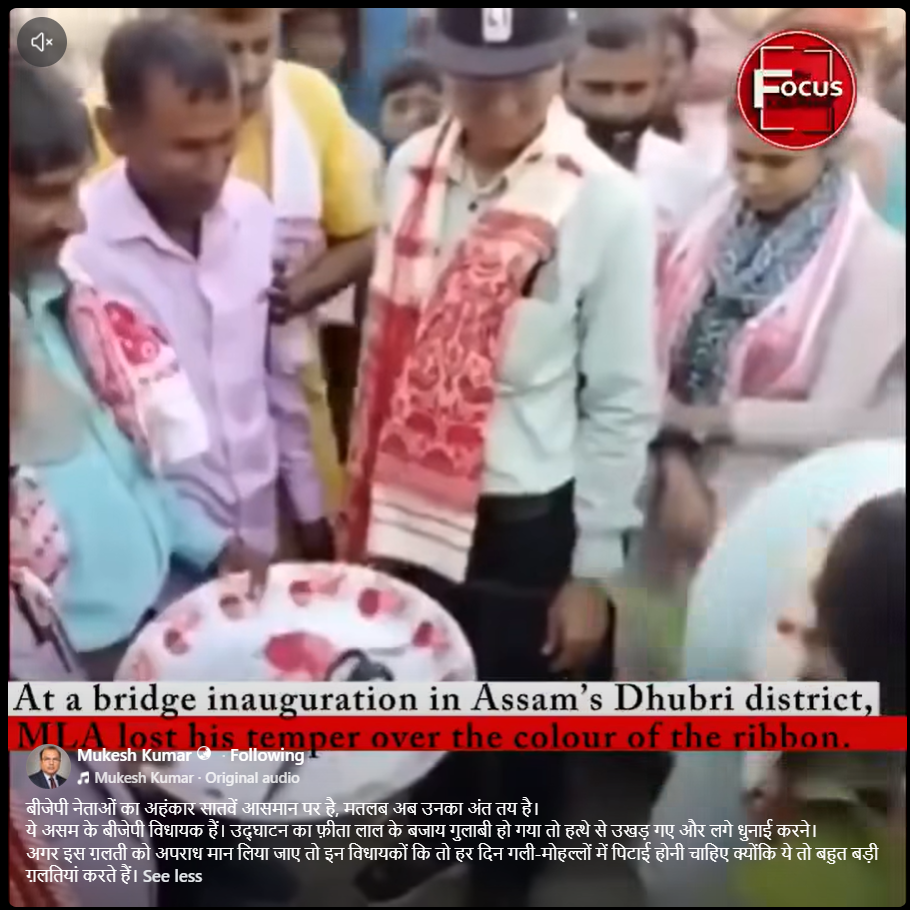
A Facebook user shared the viral video with the caption: “The arrogance of BJP leaders is at its peak, which means their end is now certain. He is a BJP MLA from Assam. When the inauguration ribbon turned pink instead of red, he lost his temper and started beating the person.” The post further stated: “If this mistake is considered a crime, then these MLAs should be beaten every day in the streets and neighbourhoods because they commit much bigger mistakes.”
The link to the post, its archive link, and a screenshot are provided below.
Factcheck
To verify the authenticity of the viral claim, the Desk first extracted keyframes from the video and conducted a reverse image search using Google Lens. During the search, the Desk found the same video on the official YouTube channel of Northeast Live, which was uploaded on March 18, 2025. The link to the post and a screenshot are provided below.
https://www.youtube.com/watch?v=L5zrgLbI6NA
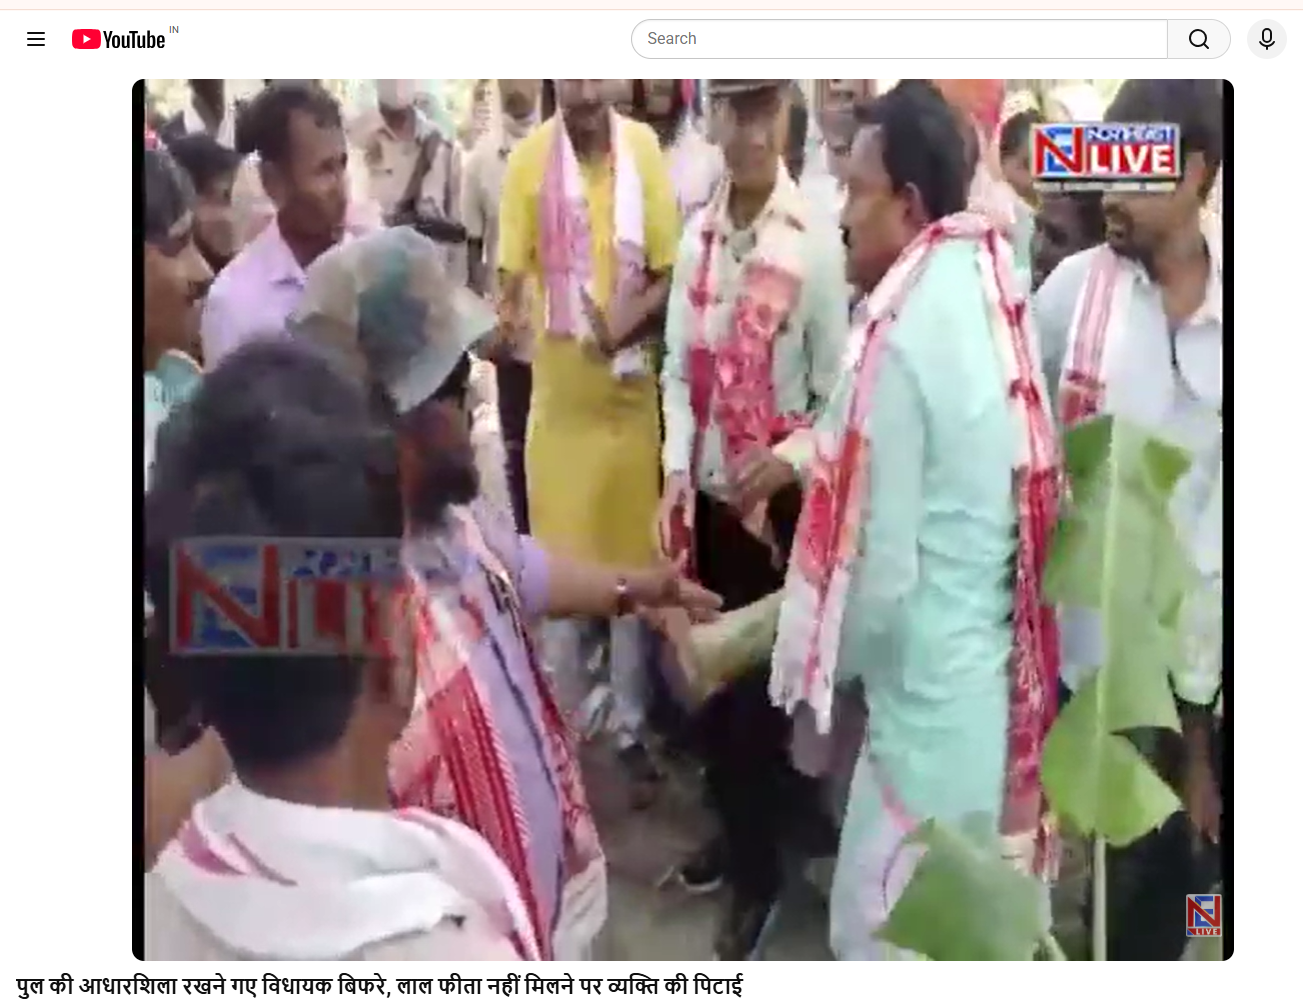
According to the video report, former AIUDF MLA from Bilasipara East, Samsul Huda, lost his temper over an issue while attending the foundation stone-laying ceremony of a bridge in Bilasipara, Assam. During the incident, he assaulted an employee of the construction company who was standing nearby. As the research progressed, the Desk found a report published by India Today NE on March 20, 2025, which carried the same visuals from the viral video. The link to the report and a screenshot are provided below.
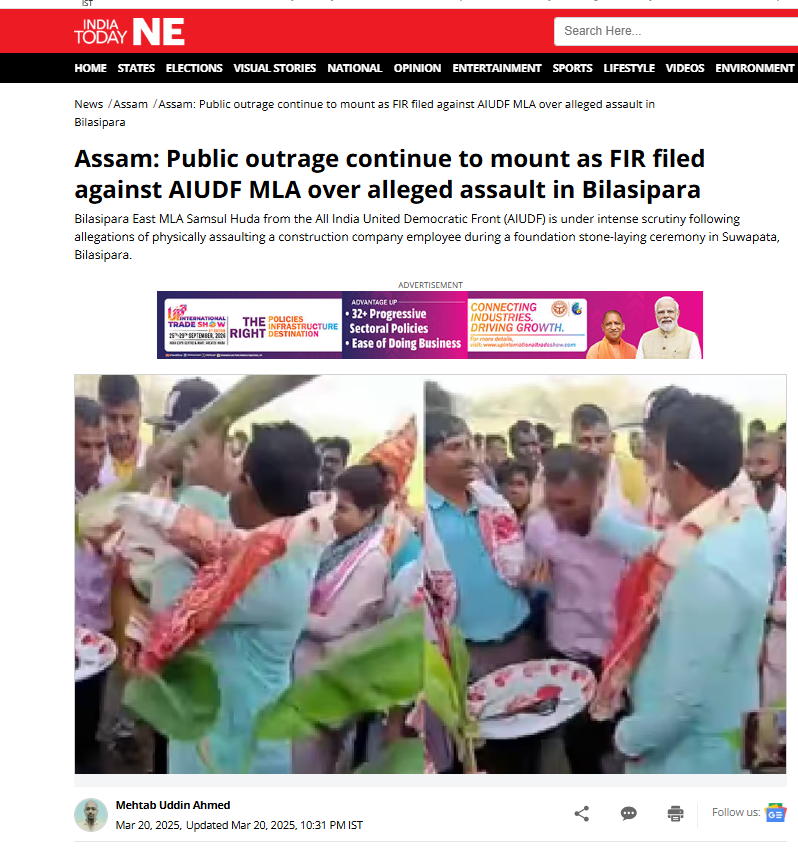
According to the report, former AIUDF MLA from Bilasipara East in Assam’s Dhubri district, Samsul Huda, had attended a bridge foundation stone-laying ceremony, where he assaulted an employee of the construction company.
Conclusion
The Desk’s research found the claim accompanying the viral video to be misleading. The person seen assaulting the youth in the video is not a BJP MLA, but former AIUDF MLA Samsul Huda. The video is being shared on social media with his identity falsely described as that of a BJP MLA.

Related Blogs
Executive Summary
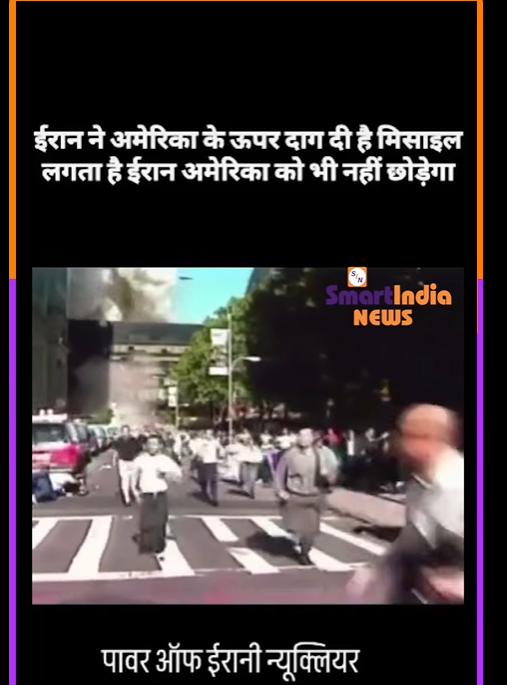
Amid the ongoing war between the United States–Israel alliance and Iran since February 28, 2026, two videos are going viral across social media platforms. The clips show people running in panic, with visuals suggesting a large-scale attack. Users are sharing these videos with the claim that they depict Iran’s recent strikes on Israel. However, a research by the CyberPeace has found both claims to be false. The viral posts are misleading, as the videos are actually from the 9/11 terrorist attacks on the World Trade Center in New York, United States. They have no connection to the current conflict involving Iran or Israel.
Claim
A Facebook page titled ‘Bihar Ko Nihar’ shared one of the videos on March 25, 2026, with the caption: “Iran has launched its most powerful attack on Israel so far. Thousands of soldiers are reported dead, triggering massive protests within the country, and Israel appears completely helpless.” Similarly, another video is being circulated with the false claim that Iran has launched a missile attack on the United States.
The above claims are being widely shared by multiple users across different social media platforms. Archived versions of these posts are also available.
- https://www.facebook.com/reel/4317571078525937
- https://www.facebook.com/reel/1485000739860984
- https://perma.cc/E98R-A4CT
Fact Check
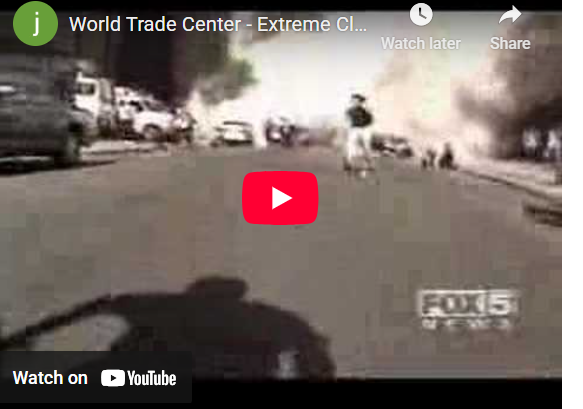
To verify the authenticity of the videos, keyframes were extracted and analyzed using Google Lens. The first viral clip was traced back to a YouTube video uploaded on September 11, 2007, by a channel named ‘Jumperwtc’, which clearly identifies the footage as being from the World Trade Center attacks in the United States. This confirms that the viral video is a segment from that older footage.
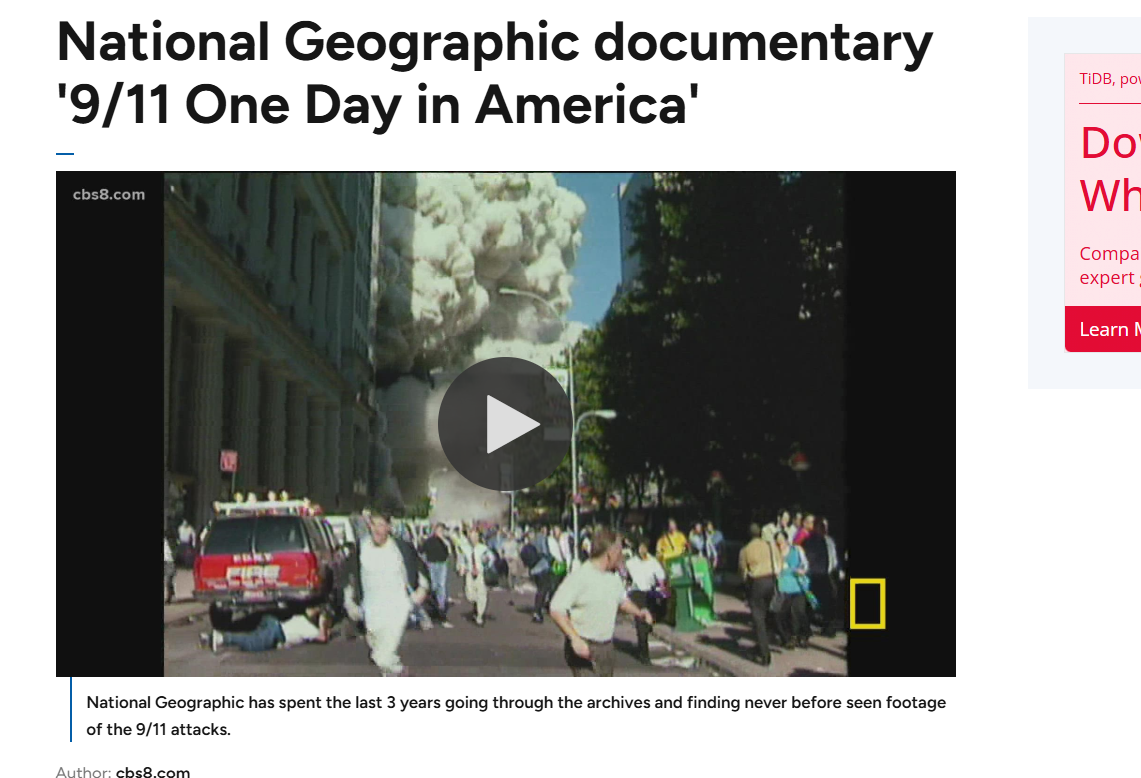
For the second video, reverse image searches led to a report published on CBS8.com on September 10, 2021, where the same visuals were found. Further reesearch revealed that the footage also appears in a video uploaded on September 11, 2021, by the YouTube channel ‘CBS 8 San Diego’. The viral segment can be seen around the 1:11 timestamp in that video.
Conclusion
Both viral videos being shared as recent attacks by Iran on Israel or the United States are actually old clips from the 9/11 attacks on the World Trade Center in New York. The claims are false, and the videos are unrelated to the ongoing conflict in West Asia.

Executive Summary:
CVE 2024-3094 is a backdoor vulnerability recently found in Kali Linux installations that happened between March 26th to 29th. This vulnerability was found in XZ package version 5.6.0 to 5.6.1. It could allow the malicious actor to compromise SSHD authentication, and grant unauthorized access to the entire system remotely. The users who have installed or updated Kali Linux during the said time are advised to update their system to safeguard against this vulnerability.
The Dangerous Backdoor
The use of the malicious implant found in XZ Utils as a remote code execution tool makes it more dangerous, because of its ability to compromise the affected systems. Initially, researchers believed the vulnerability enabled an authentication bypass for the OpenSSH server (SSHD) process. However, further analysis revealed it is better characterized as a remote code execution (RCE) vulnerability.
The backdoor intercepts the RSA_public_decrypt function, verifies the host's signature using a fixed Ed448 key, and if successful, executes malicious code passed by the attacker via the system() function. This leaves no trace in SSHD logs and makes it difficult to detect the vulnerability.
Impacted Linux Distributions
The compromised versions of XZ Utils have been found in the following Linux distributions released in March 2024:
- Kali Linux (between March 26 and March 29)
- openSUSE Tumbleweed and openSUSE MicroOS (March 7 to March 28)
- Fedora 41, Fedora Rawhide, and Fedora Linux 40 beta
- Debian (testing, unstable, and experimental distributions only)
- Arch Linux container images (February 29 to March 29)
- Meanwhile, distributions such as Red Hat Enterprise Linux (RHEL), SUSE Linux Enterprise, openSUSE Leap, and Debian Stable are not believed to be affected.
How Did This Happen?
The malicious code appears to have been inserted by taking advantage of a typical control transfer vulnerability. The original maintainer of the XZ Libs project on GitHub handed over control of the repository to an account that had been contributing to various data compression-related projects for several years. It was at this point that the backdoor was implanted in the project code.
Fortunately, the Potential Disaster Was Averted
As per Igor Kuznetsov, head of Kaspersky's Global Research and Analysis Team (GReAT), the vulnerability CVE-2024-3094 is considered as the largest scale attack that has happened in the Linux ecosystem history. Because it targeted the primary remote management tool for Linux servers on the internet which is SSH servers.
As this vulnerability was detected in the testing and rolling distributions in the short period of time, where the latest software packages are used. This results to the minimum damage to the linux users and so far no case of CVE-2024-3094 being actively exploited have been detected.
Staying Safe
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) advises that users who installed or updated the affected operating systems in March immediately roll back to XZ Utils 5.4.6 version and be on alert for any malicious activity. It is recommended to change the passwords in the case of a distribution where a weak version of XZ Utils has been installed.
The Yara rule has been released to detect any infected systems by CVE-2024-3094 Vulnerability.
Conclusion
The discovery of the XZ Utils backdoor provides a reminder to be vigilant in the open source software environment. This supply chain attack highlights the importance of strong security measures, elaborate code reviews, and regular distribution of security updates to provide shield against such vulnerabilities. Always staying informed and taking the necessary precautions, Linux users can mitigate the potential impact of this vulnerability to keep their systems safe.
References :
- https://thehackernews.com/2024/03/urgent-secret-backdoor-found-in-xz.html
- https://www.helpnetsecurity.com/2024/03/29/cve-2024-3094-linux-backdoor/
- https://www.kali.org/blog/about-the-xz-backdoor/
- https://www.kaspersky.com/blog/cve-2024-3094-vulnerability-backdoor/50873/
- https://www.rapid7.com/blog/post/2024/04/01/etr-backdoored-xz-utils-cve-2024-3094/

Executive Summary:
Recently PAN-OS software of Palo Alto Networks was discovered with the critical vulnerability CVE-2024-3400. It is the software used to power all their networks in the next generation firewalls. This vulnerability is a common injection vulnerability which provides access to unauthenticated attackers to execute random code having root privileges on the attacked system. This has been exploited actively by threat actors, leaving many organizations at risk for severe cyberattacks. This report helps to understand the exploitation, detection, mitigations and recommendations for this vulnerability.

Understanding The CVE-2024-3400 Vulnerability:
CVE-2024-3400 impacts the particular version of PAN-OS and a certain configuration susceptible to this kind of a security issue. It is a command injection, which exists in the GlobalProtect module of the PAN-OS software. The vulnerability can be exploited by an unauthorized user to run any code on the firewall having root privileges. This targets Active Directory database (ntds.dit), important data (DPAPI), and Windows event logs (Microsoft-Windows-TerminalServices-LocalSessionManager%4Operational.evtx) and also login data, cookies, and local state data for Chrome and Microsoft Edge from specific targets leading attackers to capture the browser master key and steal sensitive information of the organization.
The CVE-2024-3400 has been provided with a critical severity rating of 10.0. The following two weaknesses make this CVE highly severe:
- CWE-77: Improper Neutralization of Special Elements used in a Command ('Command Injection')
- CWE-20: Improper Input Validation.
Impacted Products:
The affected version of PAN-OS by CVE-2024-3400 are-

Only the versions 10.2, 11.0, and 11.1, setup with GlobalProtect Gateway or GlobalProtect Portal are exploited by this vulnerability. Whereas the Cloud NGFW, Panorama appliances and Prisma Access are not affected.
Detecting Potential Exploitation:
Palo Alto Networks has confirmed that they are aware of the exploitation of this particular vulnerability by threat actors. In a recent publication they have given acknowledgement to Volexity for identifying the vulnerability. There is an increasing number of organizations that face severe and immediate risk by this exploitation. Third parties also have released the proof of concept for the vulnerability.
The suggestions were provided by Palo Alto Networks to detect this critical vulnerability. To detect this vulnerability, the following command shall be run on the command-line interface of PAN-OS device:
grep pattern "failed to unmarshal session(.\+.\/" mp-log gpsvc.log*
This command looks through device logs for specific entries related to vulnerability.
These log entries should contain a long, random-looking code called a GUID (Globally Unique Identifier) between the words "session(" and ")". If an attacker has tried to exploit the vulnerability, this section might contain a file path or malicious code instead of a GUID.
Presence of such entries in your logs, could be a sign of a potential attack to hack your device which may look like:
- failed to unmarshal session(../../some/path)
A normal, harmless log entry would look like this:
- failed to unmarshal session(01234567-89ab-cdef-1234-567890abcdef)
Further investigations and actions shall be needed to secure the system in case the GUID entries were not found and suspicious.
Mitigation and Recommendations:
Mitigation of the risks posed by the critical CVE-2024-3400 vulnerability, can be accomplished by the following recommended steps:
- Immediately update Software: This vulnerability is fixed in software releases namely PAN-OS 10.2.9-h1, PAN-OS 11.0.4-h1, PAN-OS 11.1.2-h3, and all higher versions. Updating software to these versions will protect your systems fully against potential exploitation.
- Leverage Hotfixes: Palo Alto Networks has released hotfixes for commonly deployed maintenance releases of PAN-OS 10.2, 11.0, and 11.1 for the users who cannot upgrade to the latest versions immediately. These hotfixes do provide a temporary solution while you prepare for the full upgrade.
- Enable Threat Prevention: Incase of available Threat Prevention subscription, enable Threat IDs 95187, 95189, and 95191 to block attacks targeting the CVE-2024-3400 vulnerability. These Threat IDs are available in Applications and Threats content version 8836-8695 and later.
- Apply Vulnerability Protection: Ensure that vulnerability protection has been applied in the GlobalProtect interface to prevent the exploitation on the device. It can be implemented using these instructions.
- Monitor Advisory Updates: Regularly checking for the updates to the official advisory of Palo Alto Networks. This helps to stay up to date of the new releases of the guidance and threat prevention IDs of CVE-2024-3400.
- Disable Device Telemetry – Optional: It is suggested to disable the device telemetry as an additional precautionary measure.
- Remediation: If there is an active exploitation observed, follow the steps mentioned in this Knowledge Base article by Palo Alto Networks.
Implementation of the above mitigation measures and recommendations would be in a position to greatly reduce the risk of exploitation you might face from a cyber attack targeting the CVE-2024-3400 vulnerability in Palo Alto Networks' PAN-OS software.
Conclusion:
The immediate response should be taken against the offensive use of the critical CVE-2024-3400 vulnerability found in the PAN-OS platform of Palo Alto Networks. Organizations should actively respond by implementing the suggested mitigation measures such as upgrading to the patched versions, enabling threat prevention and applying vulnerability protection to immediately protect from this vulnerability. Regular monitoring, implementing security defense mechanisms and security audits are the necessary measures that help to combat emerging threats and save critical resources.
