
#FactCheck -AI-Generated Video Falsely Shared as BJP-Led Border Fencing on West Bengal-Bangladesh Border
Executive Summary
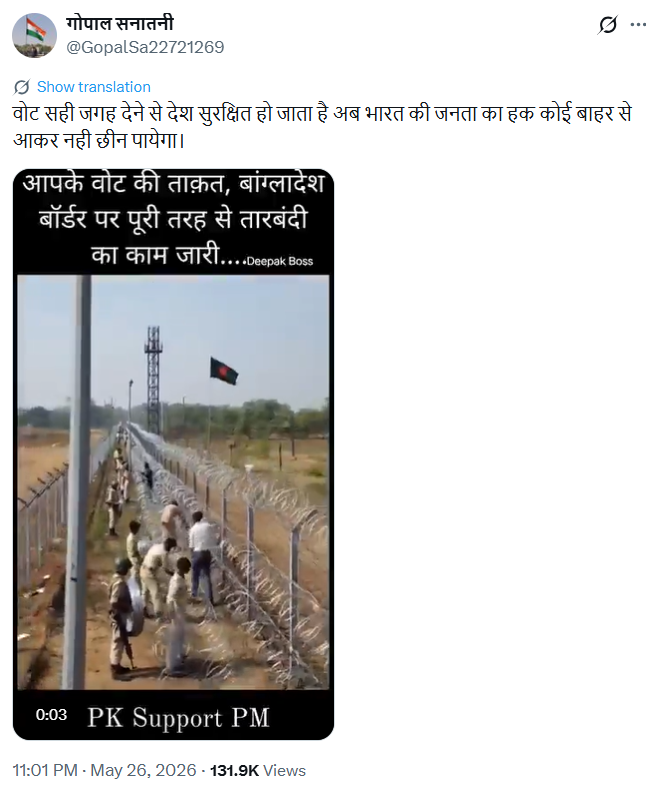
A video showing people installing fencing along a border has gone viral on social media. In the clip, several individuals along with security personnel can be seen laying barbed wire fencing near a border area. The video is being shared with the claim that it shows fencing work underway on the India-Bangladesh border in West Bengal after the Bharatiya Janata Party (BJP) allegedly came to power in the state.
However, CyberPeace Research Wing investigation found the viral claim to be false. The video is not from a real incident and has been created using Artificial Intelligence (AI).
Claim
An X user named “Gopal Sanatani” shared the viral video on May 26, 2026, with the caption:“Voting in the right place keeps the country secure. Now no outsider will be able to snatch the rights of Indian citizens.”The archived link to the post is provided below.
Fact Check
To verify the authenticity of the viral claim, we extracted several key frames from the video and conducted reverse image searches using Google. However, we could not find any credible information or authentic reports related to the visuals shown in the clip. We also searched using relevant keywords on Google, but no trustworthy news reports connected to the claim were found.
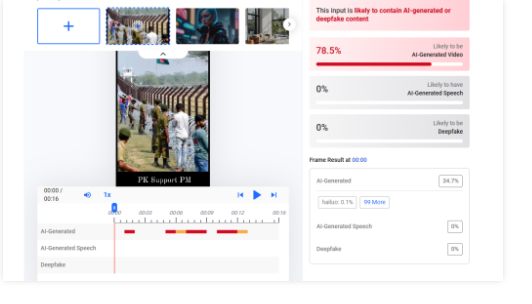
Upon closely examining the video, several visual inconsistencies became noticeable. At one point, an object resembling a piece of paper suddenly appears in a soldier’s hand and then disappears moments later. In another scene, a man installing the fencing appears to pass directly through the barbed wire and emerges unharmed, despite the sharp wires visible in the video. These irregularities raised suspicion that the clip had been artificially generated. To further investigate, we analysed the video using AI detection tools. The analysis conducted through Hive Moderation indicated a high probability — around 80 percent — that the video was AI-generated.
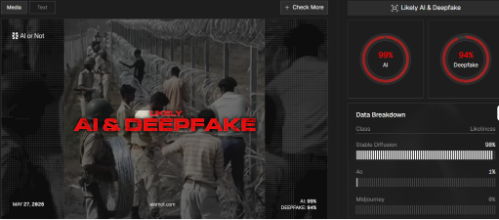
Additionally, the video was examined using another AI detection platform, “AI or Not,” which indicated nearly a 99 percent likelihood that the clip had been created using artificial intelligence.
Conclusion
Our investigation found that the viral video claiming to show fencing work along the West Bengal-Bangladesh border is fake. The footage does not depict a real incident and was generated using Artificial Intelligence (AI).

Related Blogs
Executive Summary
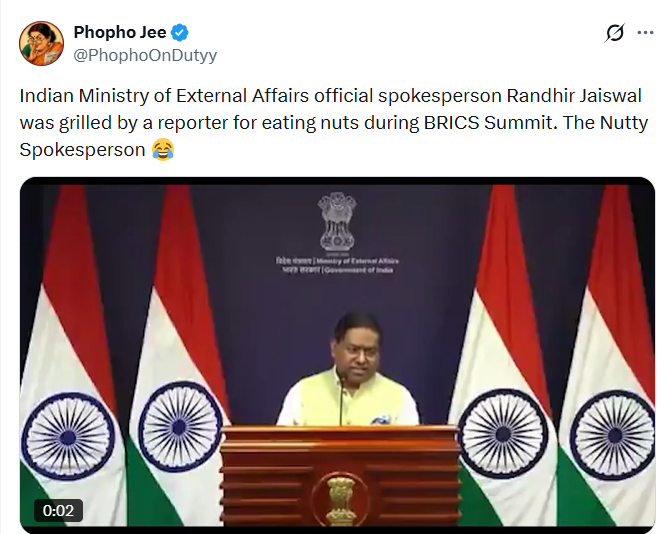
A video is being shared on social media with the claim that Ministry of External Affairs spokesperson Randhir Jaiswal was seen eating nuts during the BRICS Summit. The post claims that a reporter questioned him about eating nuts during the event. The video is also being shared with the sarcastic caption, “The Nutty Spokesperson.” Through the post, an attempt is being made to suggest that a reporter questioned Randhir Jaiswal about eating nuts during a press briefing. CyberPeace Research found that in the original video, Ministry of External Affairs spokesperson Randhir Jaiswal was responding to a question about Pakistan’s announcement of a 7 million Pakistani rupee bounty on Jaish-e-Mohammed chief Masood Azhar. Jaiswal addressed the announcement during the regular media briefing held on September 15, 2026. In his response, Jaiswal said that such announcements by Pakistan were not new and that the country should take concrete action against terrorism. However, the video being circulated on social media has been digitally edited using the original footage to falsely suggest that a reporter had questioned Jaiswal about eating nuts.
Claim:
During the BRICS Summit, a reporter questioned Ministry of External Affairs spokesperson Randhir Jaiswal about eating nuts and confronted him over it.
https://x.com/PhophoOnDutyy/status/2099940769876640084?s=20
Fact Check
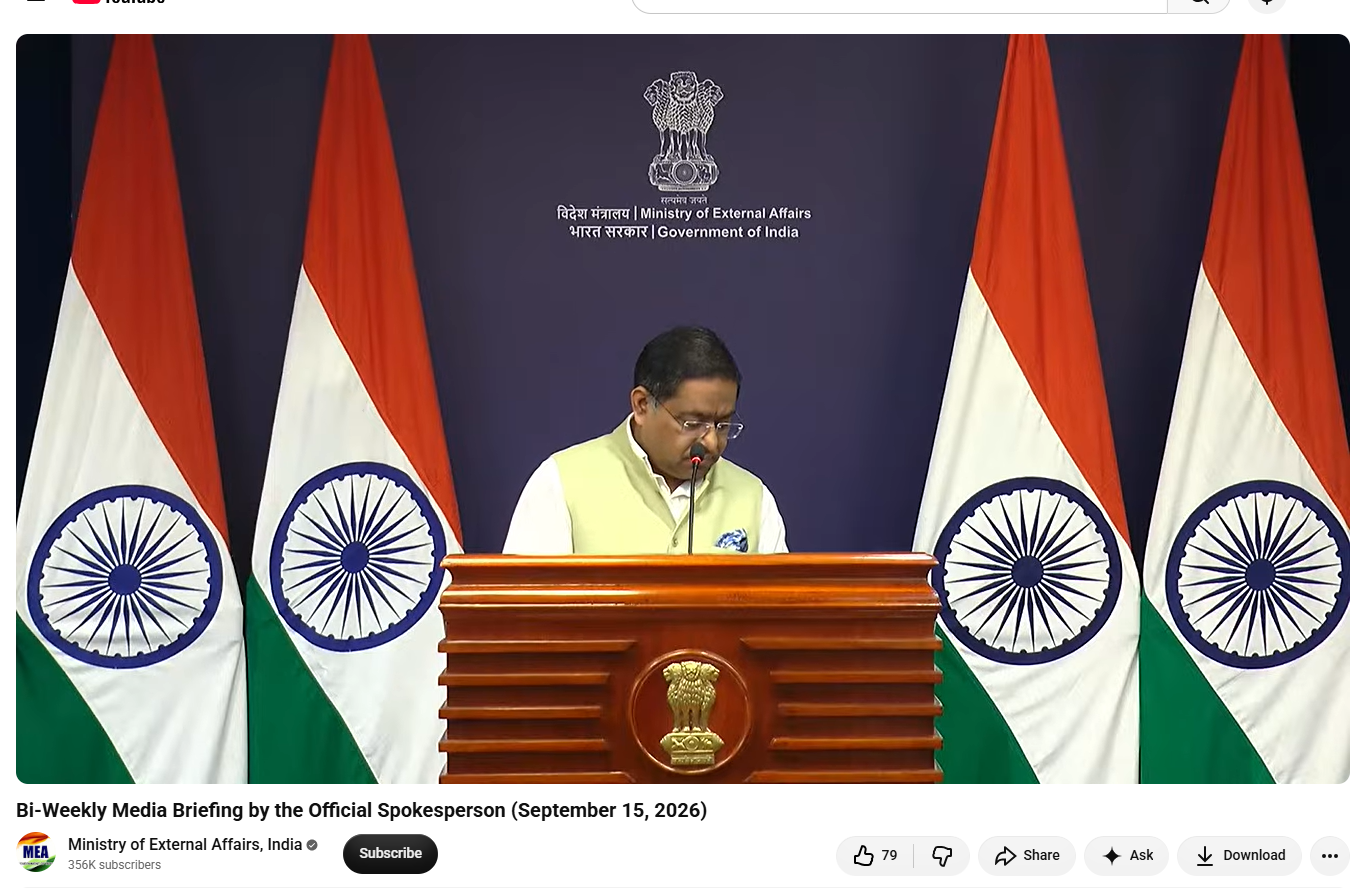
To verify the claim, we conducted a Google search using relevant keywords. During the search, we did not find any credible media report supporting the claim.As part of our research, we conducted a reverse image search of keyframes from the video. We found the original video on the YouTube channel of the Ministry of External Affairs, India. In the original video, Randhir Jaiswal was responding to a question about Pakistan’s announcement of a 7 million Pakistani rupee bounty on Masood Azhar.The reporter does not question Jaiswal about eating nuts anywhere in the original video. This establishes that the original footage has been edited and presented with a false context. Therefore, the claim being circulated on social media is false.
https://www.youtube.com/live/dw-qqLolRgc
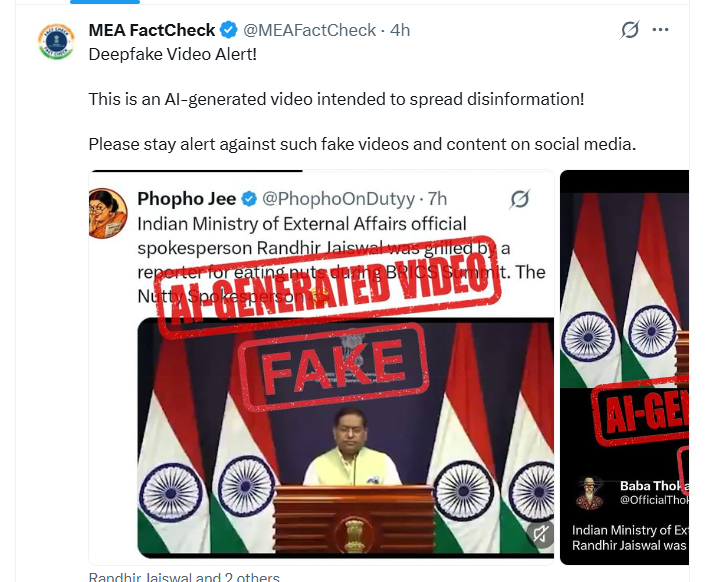
As part of our further research, we checked the official X account of MEA FactCheck. It also identified the video as AI-generated.
https://x.com/MEAFactCheck/status/2100076244805255501?s=20
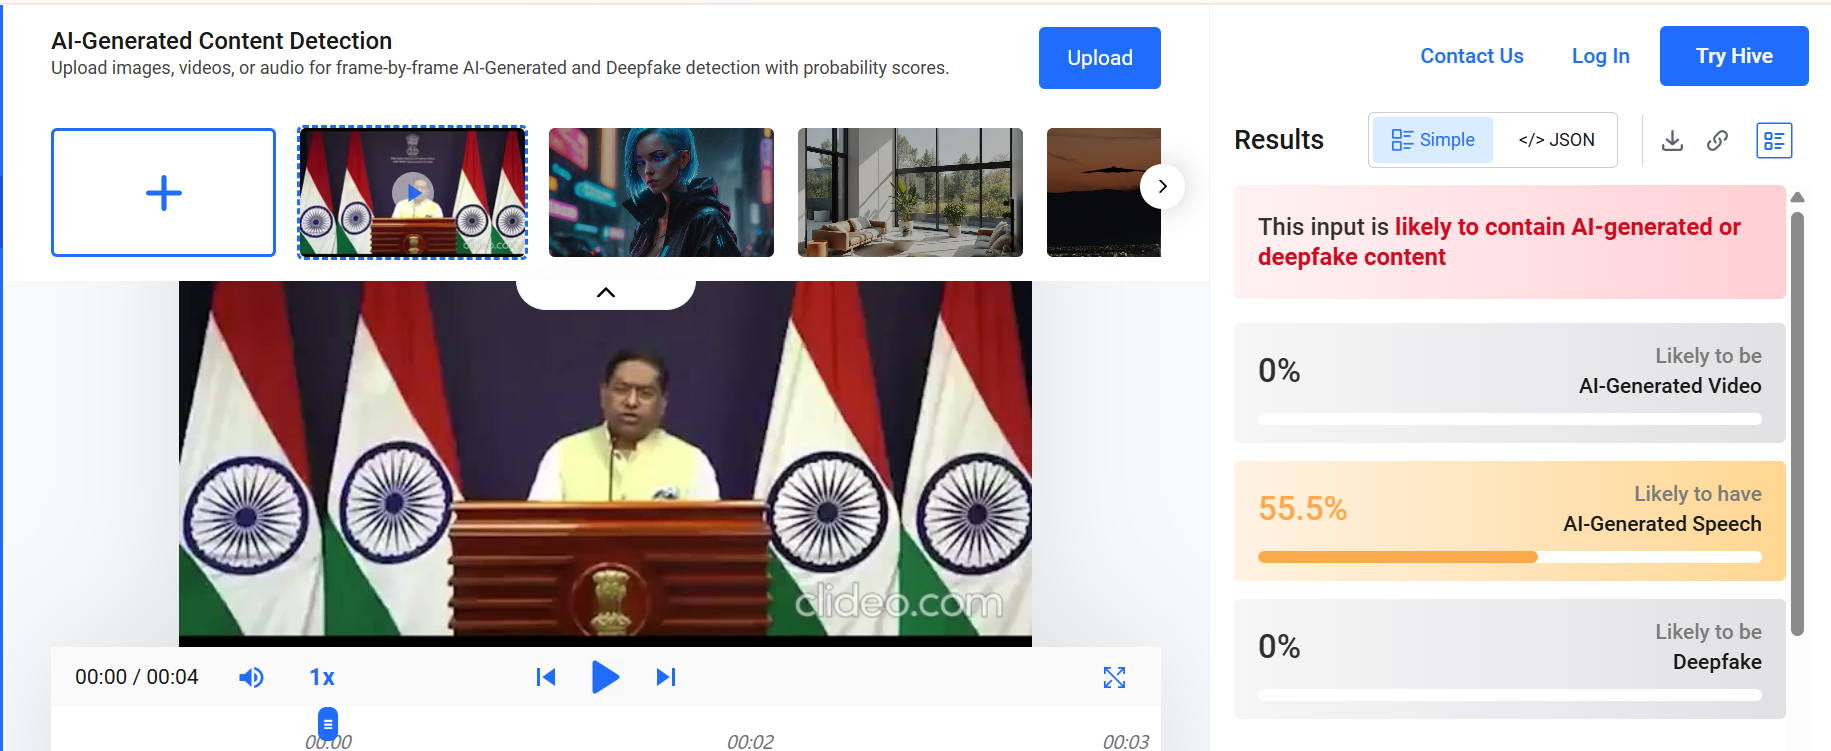
The video was scanned using the AI detection tool Hive Moderation. According to the results, the video has a 55% probability of being AI-generated.
Conclusion
Our research found that the video being shared on social media is fake and edited. In the original video, Ministry of External Affairs spokesperson Randhir Jaiswal was responding to a question about Pakistan’s announcement of a 7 million Pakistani rupee bounty on Masood Azhar.At no point in the original video does the reporter question Jaiswal about eating nuts.
The footage being circulated has been digitally manipulated and presented in a different context. The official X account of MEA FactCheck also identified the video as AI-generated. Therefore, the claim that Jaiswal was questioned by a reporter about eating nuts is false and misleading.
Introduction
Somewhere right now, a model is reading a library. It does not read like you or I, savouring a good line or skipping to the end. It does not copy, clean and convert text into numbers at the scale that a human reader could. The copyright questions these models raise are not new, but they are new in scale, and they implicate a legal order that prizes borders. A book written in Lagos can be replicated on a server in Virginia, used to train a model sold in Berlin. Whose laws apply? The honest answer is: we don't know.
A Treaty Written Before Computers
The Berne Convention is one of the most important international agreements on copyright, with over 180 countries being party to it. According to Article 9(1) of the Berne Convention, authors have the exclusive right to allow or prohibit the reproduction of their works in any form or way. Article 9(2) provides that certain countries may implement exceptions to the rights granted by the convention, as long as they are consistent with the three-step test. More specifically, a national law exception should be confined to a certain category of works, not prejudice the work’s normal use, and not unreasonably prejudice the rights of the author.
This explains how the Berne Convention could apply to copyright protection for AI. Developers of such technology often argue that since the output of a given model rarely resembles anything learned from the examples provided, there is no copying occurring. However, the Agreed Statements of the WIPO Copyright Treaty provide that the reproduction of a protected item in digital format also constitutes a reproduction. Therefore, if a work is used to train a model, this can be considered a reproduction, and the question then emerges whether a national exception applies.
Three Jurisdictions, Three Answers
Countries have responded in different ways to that question. The United States draws on its fair use doctrine, a flexible, four-factor test that was never intended for machine learning but dominates AI-related disputes anyway. Japan’s Article 30-4 permits uses of works for the purpose of data analysis where the use is not for the enjoyment of the work’s expression, which captures a lot of what training entails. And the European Union’s approach falls somewhere in the middle: its text and data mining rules allow mining of lawfully accessible works, but rightsholders can specify in a machine-readable manner that they do not want their works mined, and developers are required to seek permission.
A recent roundtable from the Columbia Undergraduate Law Review argues that the EU model fits the three-step test best because the opt-out keeps a licensing market alive and gives authors control before their work is used rather than after. It argues that broad US fair use and Japan's provision both struggle at the second and third steps, since they can undercut a foreseeable licensing market. That is one scholarly view and not settled law. The EU system also has its own weak spot: an opt-out only protects authors who know it exists and have the technical means to use it.
Bartz v. Anthropic in Brief
Bartz v. Anthropic is the case that puts these debates in front of a judge. Three authors, including Andrea Bartz, Charles Graeber and Kirk Wallace Johnson, filed a lawsuit against the Anthropic company for using part of their works to create the central library used by Claude and to train the models used in its creation. In addition, in June 2025, Judge William Alsup approved the separation of the case, considering each instance of use separately.
On training, he granted summary judgement for Anthropic, holding the use was fair and describing it as exceedingly transformative. He compared it to a reader who studies great writing in order to produce something new. It mattered that the authors did not allege Claude's outputs reproduced their books, so the case turned on inputs alone. He also held that buying print books and scanning them into digital copies was fair use, since it only changed the format of copies Anthropic already owned. But he refused to excuse the more than seven million pirated books Anthropic downloaded to build a permanent library. Building that library from pirated copies, he found, was its own use and not a transformative one, and that part was set for trial.
Two observations are worth making in relation to those thinking across borders. First, the court's assumption that there might be a market for training licences, but its observation that this is not a market which the Copyright Act entitles authors to control, is quite inconsistent with Berne's concern for normal exploitation. Moreover, the order makes no reference to Berne at all, bearing out the observation that the US courts apply the domestic statute and not the treaty.
The story did not end there. Anthropic agreed to a $1.5 billion class settlement covering roughly 482,000 works, and the court granted final approval on 20 July 2026. It resolves claims about past acquisition and copying, so the training ruling remains a trial court's view rather than binding precedent.
Where Borders Break the System
The deeper trouble is that none of this travels well. Berne is not self-executing in the United States, so judges apply the domestic statute, and nobody is required to ask whether a fair use ruling passes the three-step test. Meanwhile, training can happen in one country, on work from dozens of others, for a product used everywhere. The same book might be freely usable in Tokyo, subject to an opt-out in Paris and defended as fair use in San Francisco.
The roundtable suggests one way forward: a new WIPO special agreement, along the lines of the WIPO Copyright Treaty, in response to the internet. It would provide guidance on the application of the three-step test to training, regard licensing markets as an ordinary part of exploitation, and require minimum standards for reservations of rights and compensation. There is one major potential obstacle: many of the most influential AI companies are based in the US, which has a record of opposing international obligations that impinge on fair use. A deal would apply only to the extent that it is not controlled by the US, where most of the training takes place. Market forces, in the form of the so-called Brussels effect, may prove more influential than negotiations at WIPO.
Conclusion
Bartz’s analysis illustrates the importance of characterising a specific use at the level of a particular court. While the former had been viewed as an activity and the latter as an acquisition, the distinction between the use of a work and its acquisition appears more likely to transcend borders than the concept of fair use. Berne was designed to create a common ground for authors. Whether this convention would be able to fulfil its function in the era of generative AI depends on the willingness of nations to adopt a joint understanding of what constitutes its foundations for machines.

Introduction
The automobile business is fast expanding, with vehicles becoming sophisticated, interconnected gadgets equipped with cutting-edge digital technology. This integration improves convenience, safety, and efficiency while also exposing automobiles to a new set of cyber risks. Electric vehicles (EVs) are equipped with sophisticated computer systems that manage various functions, such as acceleration, braking, and steering. If these systems are compromised, it could result in hazardous situations, including the remote control of the vehicle or unauthorized access to sensitive data. The automotive sector is evolving with the rise of connected car stakeholders, exposing new vulnerabilities for hackers to exploit.
Why Automotive Cybersecurity is required
Cybersecurity threats to automotives result from hardware, software and overall systems redundancy. Additional concerns include general privacy clauses that justify collecting and transferring data to “third-party vendors”, without explicitly disclosing who such third parties are and the manner of processing personal data. For example, infotainment platform data may show popular music and the user’s preferences, which may be used by the music industry to improve marketing strategies. Similarly, it is lesser known that any data relating to behavioural tracking data, such as driving patterns etc., are also logged by the original equipment manufacturer.
Hacking is not limited to attackers gaining control of an electronic automobile; it includes malicious actors hacking charging stations to manipulate the systems. In Russia, EV charging stations were hacked in Moscow to display pro-Ukraine and anti-Putin messages such as “Glory to Ukraine” and “Death to the enemy” in the backdrop of the Russia-Ukraine war. Other examples include instances from the Isle of Wight, where hackers controlled the EV monitor to show inappropriate content and display high voltage fault codes to EV owners, preventing them from charging their vehicles with empty batteries.
UN Economic Commission for Europe releases Regulation 155 for Automobiles
UN Economic Commission for Europe Regulation 155 lays down uniform provisions concerning the approval of vehicles with regard to cybersecurity and cybersecurity management systems (CSMS). This was originally a part of the Commission.s Work Paper (W.P.) 29 that aimed to harmonise vehicular regulations for vehicles and vehicle equipment. Regulation 155 has a two-prong objective; first, to ensure cybersecurity at the organisational level and second, to ensure adequate designs of the vehicle architecture. A critical aspect in this context is the implementation of a certified CSMS by all companies that bring vehicles to market. Notably, this requirement alters the perspective of manufacturers; their responsibilities no longer conclude with the start of production (SOP). Instead, manufacturers are now required to continuously monitor and assess the safety systems throughout the entire life cycle of a vehicle, including making any necessary improvements.
This Regulation reflects the highly dynamic nature of software development and assurance. Moreover, the management system is designed to ensure compliance with safety requirements across the entire supply chain. This is a significant challenge, considering that suppliers currently account for over 70 per cent of the software volume.
The Regulation, which is binding in nature for 64 member countries, came into force in 2021. UNECE countries were required to be compliant with the Regulations by July 2022 for all new vehicles and by July 2024, the Regulation was set to apply to all vehicles. It is believed that the Regulation will become a de facto global standard, since vehicles authorised in a particular country may not be brought into the global market or the market of any UNECE member country based on any other authorisation. In such a scenario, OEMs of non-member countries may be required to give a “self-declaration”, declaring the equipment’s conformity with cybersecurity standards.
Conclusion
To compete and ensure trust, global car makers must deliver a robust cybersecurity framework that meets evolving regulations. The UNECE regulations in this regard are driving this direction by requiring automotive original equipment manufacturers (OEMs) to integrate vehicle cybersecurity throughout the entire value chain. The ‘security by design' approach aims to build a connected car that is trusted by all. Automotive cybersecurity involves measures and technologies to protect connected vehicles and their onboard systems from growing digital threats.
References:
- “Electric vehicle cyber security risks and best practices (2023)”, Cyber Talk, 1 August 2023. https://www.cybertalk.org/2023/08/01/electric-vehicle-cyber-security-risks-and-best-practices-2023/#:~:text=EVs%20are%20equipped%20with%20complex,unauthorized%20access%20to%20sensitive%20data.
- Gordon, Aaron, “Russian Electric Vehicle Chargers Hacked, Tell Users “PUTIN IS A D*******D”, Vice, 28 February 2022. https://www.vice.com/en/article/russian-electric-vehicle-chargers-hacked-tell-users-putin-is-a-dickhead/
- “Isle of Wight: Council’s electric vehicle chargers hacked to show porn site”, BBC, 6 April 2022. https://www.bbc.com/news/uk-england-hampshire-61006816
- Sandler, Manuel, “UN Regulation No. 155: What You Need to Know about UN R155”, Cyres Consulting, 1 June 2022. https://www.cyres-consulting.com/un-regulation-no-155-requirements-what-you-need-to-know/?srsltid=AfmBOopV1pH1mg6M2Nn439N1-EyiU-gPwH2L4vq5tmP0Y2vUpQR-yfP7#A_short_overview_Background_knowledge_on_UN_Regulation_No_155
- https://unece.org/wp29-introduction?__cf_chl_tk=ZYt.Sq4MrXvTwSiYURi_essxUCGCysfPq7eSCg1oXLA-1724839918-0.0.1.1-13972
