
#FactCheck-Videos of Thai Army Falsely Shared as Chinese Troops Entering Arunachal Pradesh
Introduction
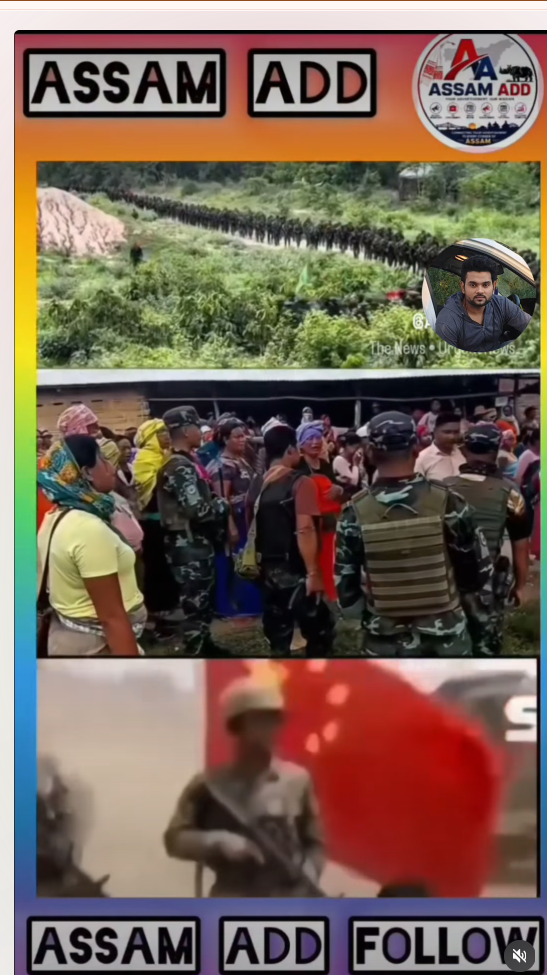
Two videos are being widely circulated on social media with the claim that Chinese troops have entered Arunachal Pradesh, India. The first video shows a large group of soldiers marching in formation, while the second shows armed personnel disembarking from military trucks. Social media users claim that the footage shows Chinese soldiers advancing into Indian territory. CyberPeace Research Wing’s research found the claim to be false. The two viral videos are unrelated to India and actually show Thai Army personnel during military training exercises. Both the Government of India and the Indian Army have also dismissed the claim of any recent Chinese intrusion into Indian territory.
Claim
An Instagram user, "mtkv.ideo," shared the viral videos on July 7, 2026, with the caption,"Chinese army has entered 60 km inside India."
https://www.instagram.com/reels/DaehrgExzUl/
Fact Check
To verify the claim, we extracted several keyframes from the viral videos and conducted a reverse image search using Google Lens.
During the research, we found one of the videos posted on June 16, 2026, on the Facebook page "Liangpha Kha Khaeng."
https://www.facebook.com/reel/992963226961409
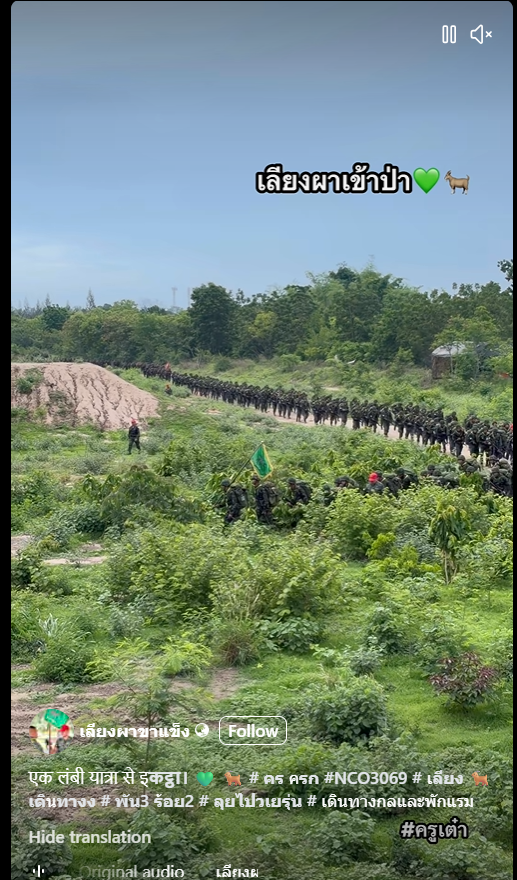
According to the information provided with the post, the video shows a training exercise of Non-Commissioned Officers (NCOs) from the 3rd Battalion, 2nd Regiment of the Royal Thai Army. The page also contains several other posts featuring Thai military drills and training activities. We further reviewed the Facebook page and found multiple training videos featuring the same flag carried by soldiers in the viral footage, confirming that the personnel shown belong to the Thai Army, not the Chinese military.
https://www.facebook.com/profile.php?id=61588894033585&locale=hi_IN

We also found a report published by The Times of India, quoting Union Minister Kiren Rijiju, who dismissed claims of any Chinese intrusion into Arunachal Pradesh. Rijiju clarified that no intrusion had taken place, adding that occasional movement across undemarcated areas occurs because the boundary has not been fully delineated. https://timesofindia.indiatimes.com/india/no-intrusion-transgression-in-absence-of-demarcation-kiran-rijiju/articleshow/132101410.cms

Conclusion
Our research found that the viral claim is false. The videos being shared as evidence of Chinese troops entering Arunachal Pradesh actually show Royal Thai Army personnel participating in military training exercises in Thailand. There is no evidence that the footage is related to India or that it depicts any recent Chinese military intrusion into Indian territory. Government officials have also rejected the viral claim.

Related Blogs
India’s cities are rapidly embracing digital technologies, transforming the way essential urban services operate. From traffic management and water supply to online grievance redressal, connected systems are making city life more efficient. As the Prime Minister has emphasised, smart cities are not just a fancy concept; they aim to ensure basic services, including housing and infrastructure for the urban poor, are delivered comprehensively and equitably.
But improved cybersecurity has become essential with th increasing reliance on digital systems in daily life. A single breach in digital public systems could jeopardise citizen data and interrupt vital services. In light of this, MoHUA organised the National Conference on Making Cities Cyber Secure in collaboration with MHA and MeitY. This is in spirit with the goal of Digital India, which is to create a safer online environment for all. More than 300 representatives from Central Ministries, National Cybersecurity Agencies, State Governments, State IT and Urban Development Secretaries, Additional Director Generals, Municipal Commissioners, CEOs of Smart Cities, and representatives from organisations like CERT-In, NCIIPC, I4C, and STQC attended the conference.
Key Initiatives Presented
MoHUA showcased a series of city-level cybersecurity initiatives designed to create a common framework for all smart cities. These include:
- Mandatory appointment of Chief Information Security Officers (CISOs) at city level which maintain and oversee the security of digital infrastructure in smart cites
- Completion of regular cybersecurity audits to identify and address vulnerabilities in there seem
- Consistent Risk Management Across Services: A structured approach to risk management will be used so that critical areas like traffic systems, utilities and public services all follow the same high standards of protection.
CISOs and Cybersecurity Frameworks
At the conference, the Union Home Secretary underscored a clear message: every city needs its own Chief Information Security Officer (CISO) backed by a capable technical team. This isn’t just a box-ticking exercise. A dedicated CISO brings focus to meeting national security norms, coordinating quick responses to cyber incidents, and lifting the overall level of cyber hygiene in the city.
Naming a single officer also creates accountability and gradually builds local expertise instead of constant dependence on outside consultants. Over time, this leadership position can help cities develop their own in-house capacity to manage the increasingly complex digital systems that keep public services running.
The SPV Dimension: Beyond Implementation
An important theme of the conference was the future of Special Purpose Vehicles (SPVs)(SPVs means government-backed companies set up under the Companies Act, 2013 with joint shareholding between State/UT administrations and Urban Local Bodies to implement the Smart Cities Mission) which have been the implementing arms of the Smart Cities Mission. Drawing from Advisory No. 27 (June 2025), stakeholders discussed repositioning SPVs as dynamic, innovation-driven bodies capable of supporting long-term urban development beyond the initial project phase.
Key points included:
- Expanding SPVs’ role in consultancy, investment facilitation, technology integration, and policy research.
- Ensuring SPVs act as hubs of expertise and innovation, rather than just project managers.
- Aligning SPV functions with the evolving cybersecurity and technology needs of urban local bodies.
This expanded mandate could allow SPVs to become sustainable institutions that continuously support cities in managing digital risks and adopting new technologies responsibly.
Building a Culture of Cyber Preparedness
One clear takeaway from the conference was that cybersecurity can’t just be added on later — it needs to be part of every step in the digital planning process, from purchasing technology and designing systems to daily operations. Experts from the Intelligence Bureau (IB) pointed out that as more government services go online, the potential risks grow, and cities must always be ready to respond. They highlighted emerging cyber risks linked to the rapid digitisation of governance.
Some of the practical steps highlighted included regular security audits, penetration testing, staff training, and campaigns to raise awareness among citizens. Equally important to have CISO which lead cybersecurity and creating strong communication channels between city teams, state agencies, and national cybersecurity bodies, so that information is shared promptly and responses can be coordinated effectively
Conclusion
The Ministry of Home Affairs’ directive on strengthening cybersecurity in smart cities represents a major milestone in safeguarding India’s urban digital infrastructure and shows the government's proactive step in cybersecurity . By mandating the appointment of Chief Information Security Officers (CISOs), enforcing regular audits, and promoting structured risk management, the MHA has set clear expectations for city administration. The conference also highlighted the evolving role of Special Purpose Vehicles (SPVs) in supporting long-term technological resilience. Embedding cybersecurity at every stage of planning, from system design to daily operations, signals a shift toward a culture of proactive defence. As highlighted by the Intelligence Bureau, emerging cyber risks linked to the rapid digitisation of governance make robust cybersecurity measures the need of the hour for India’s smart cities.
- https://www.pib.gov.in/PressReleasePage.aspx?PRID=2146180
- https://www.pib.gov.in/PressReleasePage.aspx?PRID=2135474
- https://m.economictimes.com/news/economy/infrastructure/pm-narendra-modi-launches-smart-city-projects/articleshow/52916581.cms
- https://the420.in/mha-orders-stronger-cybersecurity-in-smart-cities/
- https://www.newindianexpress.com/nation/2025/Sep/20/tighten-cyber-security-measures-in-smart-cities-mha-to-housing-ministry

Introduction
CyberPeace Chronicles is a one-stop for the latest edition of news, updates, and findings in global cyberspace. As we step into the cyberage, it is pertinent that we need to incorporate cybersecurity practices in our day-to-day activities. From laptops to automated homes and cars, we are all surrounded by technology in some form or another. Thus, with the increased dependency, we need to eradicate the scope of vulnerabilities and threats around us and create robust and sustainable safety mechanisms for us and future generations.
What, When and How?
- WIN-RAR Update: CVE-2023-33831, a serious vulnerability, was identified in WinRAR versions prior to 6.23 in April 2023. When users attempted to access seemingly harmless files inside ZIP archives, this vulnerability allowed attackers to run arbitrary code. Cybercriminals transmitted malware families like DarkMe, GuLoader, and Remcos RAT by taking advantage of this vulnerability. It is essential to update WinRAR to version 6.23 or later in order to protect your computer and your data. Follow the following steps to secure your device -
- Checking Your Current WinRAR Version
- Downloading the Latest WinRAR Version
- Installing the Updated WinRAR
- Completing the Installation
- Verifying the Update
- Cleaning Up
- Indonesian Hacker Groups Target Indian Digital Infrastructure: As India geared up to host the G20 delegation as part of the Leadership Summit, various reports pointed towards different forms and intensity-based cyber attacks on Indian organisations and digital infrastructure. Tech firms in India have been successful in tracing the origination of the attacks to be from Indonesia. It is believed that hacker groups backed by anti-India elements have been trying to target the digital resources of India. Organisations and central agencies like Computer Emergency Response Team (CERT-In), National Critical Information Infrastructure Protection Centre (NCIIPC), I4C (Indian Cybercrime Coordination Centre), Delhi Police, Intelligence Bureau (IB), Research and Analysis Wing (R&AW), National Investigation Agency (NIA) and Central Bureau of Investigation (CBI) have constantly been working in keeping the Digital interests of India safe and secure, and with the ongoing G20 summit, it is very pertinent to be mindful of potential threats prevailing to prepare counter tactics for the same.
- CLOP Ransomware: The CL0P ransomware is thought to have initially surfaced in 2019 and was developed by a cybercriminal organisation that spoke Russian. The threat actor FIN11 (also known as TA505 and Snakefly), who is notorious for being financially driven, is frequently connected to the CL0P ransomware, which had its roots at the beginning of 2019. By utilising this technique, CL0P has targeted businesses utilising the "Accellion FTA" file transfer appliance's vulnerable version. Accordingly, it has been asserted that the following vulnerabilities have been used to access victim data and maybe switch to victim networks. Numerous well-publicized attacks carried out by CL0P have had an impact on organisations all across the world. Especially for Managed File Transfer (MFT) programmes, the CL0P performers are well known for their talent in developing zero-day vulnerabilities. The gang went after Accellion File Transfer Appliance (FTA) devices in both 2020 and 2021, then early in 2023, they went after Fortran/Linoma GoAnywhere MFT servers, and then later in June, they went after MOVEit transfer deployments. Up to 500 organisations are thought to have been harmed by this aggressive operation. Some of the ways to mitigate the risk are as follows:
- Regular Software Updates: Updating programmes and systems helps prevent known security flaws that fraudsters frequently exploit.
- Employee Training: Employee training can significantly lower the likelihood of successful penetration by educating staff members about phishing scams and safe internet conduct.
- Network Segmentation: By separating networks and restricting lateral movement, a ransomware attack's potential effects can be reduced.
- Regular Data backups: Data backups can lessen the effects of encryption and deter payment by regularly backing up data and storing it offsite.
- Security solutions: Putting in place effective cybersecurity measures like firewalls, intrusion detection systems, and cutting-edge endpoint protection can greatly improve an organisation's defences.
- Increased scrutiny for SIM card vendors: As phishing and smishing scams are on the rise in India, the Telecom Regulatory Authority of India (TRAI) has repeatedly issued notifications and consultation papers to address this growing concern. Earlier this year, TRAI notified that promotional calling will not be continued from 10-digit personal numbers. Instead, companies will now have to take authorised 9-digit numbers for promotional calls and SMSs. Similarly, to increase the efficiency of the same, TRAI has laid down that all the SIM card vendors will now have to be verified again, and any discrepancy found against any of the vendors will lead to blacklisting and penal actions against the vendor.
Conclusion
In conclusion, the digital landscape in 2023 is rife with both opportunities and challenges. The recent discovery of a critical vulnerability in WinRAR underscores the importance of regularly updating software to protect against malicious attacks. It is imperative for users to follow the provided steps to secure their devices and safeguard their data. Furthermore, the cyber threat landscape continues to evolve, with Indonesian hacker groups targeting Indian digital infrastructure, particularly during significant events like the G20 summit. Indian organisations and cybersecurity agencies are working diligently to defend against these threats and ensure the security of digital assets. The emergence of ransomware attacks, exemplified by the CL0P ransomware, serves as a stark reminder of the need for robust cybersecurity measures. Regular software updates, employee training, network segmentation, data backups, and advanced security solutions are crucial components of a comprehensive defence strategy against ransomware and other cyber threats. Additionally, the Telecom Regulatory Authority of India's efforts to enhance security in the telecommunications sector, such as stricter verification of SIM card vendors, demonstrate a proactive approach to addressing the rising threat of phishing and smishing scams. In this dynamic digital landscape, staying informed and implementing proactive cybersecurity measures is essential for individuals, organisations, and nations to protect their digital assets and maintain a secure online environment. Vigilance, collaboration, and ongoing adaptation are key to meeting the challenges posed by cyber threats in 2023 and beyond.

Introduction
In the era of digitalisation, social media has become an essential part of our lives, with people spending a lot of time updating every moment of their lives on these platforms. Social media networks such as WhatsApp, Facebook, and YouTube have emerged as significant sources of Information. However, the proliferation of misinformation is alarming since misinformation can have grave consequences for individuals, organisations, and society as a whole. Misinformation can spread rapidly via social media, leaving a higher impact on larger audiences. Bad actors can exploit algorithms for their benefit or some other agenda, using tactics such as clickbait headlines, emotionally charged language, and manipulated algorithms to increase false information.
Impact
The impact of misinformation on our lives is devastating, affecting individuals, communities, and society as a whole. False or misleading health information can have serious consequences, such as believing in unproven remedies or misinformation about some vaccines can cause serious illness, disability, or even death. Any misinformation related to any financial scheme or investment can lead to false or poor financial decisions that could lead to bankruptcy and loss of long-term savings.
In a democratic nation, misinformation plays a vital role in forming a political opinion, and the misinformation spread on social media during elections can affect voter behaviour, damage trust, and may cause political instability.
Mitigating strategies
The best way to minimise or stop the spreading of misinformation requires a multi-faceted approach. These strategies include promoting media literacy with critical thinking, verifying information before sharing, holding social media platforms accountable, regulating misinformation, supporting critical research, and fostering healthy means of communication to build a resilient society.
To put an end to the cycle of misinformation and move towards a better future, we must create plans to combat the spread of false information. This will require coordinated actions from individuals, communities, tech companies, and institutions to promote a culture of information accuracy and responsible behaviour.
The widespread spread of false information on social media platforms presents serious problems for people, groups, and society as a whole. It becomes clear that battling false information necessitates a thorough and multifaceted strategy as we go deeper into comprehending the nuances of this problem.
Encouraging consumers to develop media literacy and critical thinking abilities is essential to preventing the spread of false information. Being educated is essential for equipping people to distinguish between reliable sources and false information. Giving individuals the skills to assess information critically will enable them to choose the content they share and consume with knowledge. Public awareness campaigns should be used to promote and include initiatives that aim to improve media literacy in school curriculum.
Ways to Stop Misinformation
As we have seen, misinformation can cause serious implications; the best way to minimise or stop the spreading of misinformation requires a multifaceted approach; here are some strategies to combat misinformation.
- Promote Media Literacy with Critical Thinking: Educate individuals about how to critically evaluate information, fact check, and recognise common tactics used to spread misinformation, the users must use their critical thinking before forming any opinion or perspective and sharing the content.
- Verify Information: we must encourage people to verify the information before sharing, especially if it seems sensational or controversial, and encourage the consumption of news or any information from a reputable source of news that follows ethical journalistic standards.
- Accountability: Advocate for social media networks' openness and responsibility in the fight against misinformation. Encourage platforms to put in place procedures to detect and delete fraudulent content while boosting credible sources.
- Regulate Misinformation: Looking at the current situation, it is important to advocate for policies and regulations that address the spread of misinformation while safeguarding freedom of expression. Transparency in online communication by identifying the source of information and disclosing any conflict of interest.
- Support Critical Research: Invest in research and study on the sources, impacts, and remedies to misinformation. Support collaborative initiatives by social scientists, psychologists, journalists, and technology to create evidence-based techniques for countering misinformation.
Conclusion
To prevent the cycle of misinformation and move towards responsible use of the Internet, we must create strategies to combat the spread of false information. This will require coordinated actions from individuals, communities, tech companies, and institutions to promote a culture of information accuracy and responsible behaviour.
