
#FactCheck: Scripted Video Falsely Claims Indian Father Married His Biological Daughter Over Dowry
Executive Summary
A video is going viral on social media, claiming that an Indian Hindu father married his own biological daughter because he could not afford to pay her dowry. CyberPeace Research found that the video features scripted content being presented as a real-life incident, making the claim misleading. The claim that the man married his own biological daughter is false.
Claim:
A video is being shared on social media with the claim that an Indian Hindu father married his own biological daughter because he was unable to afford her dowry.
https://x.com/i/birdwatch/t/2112470461011599390?source=6
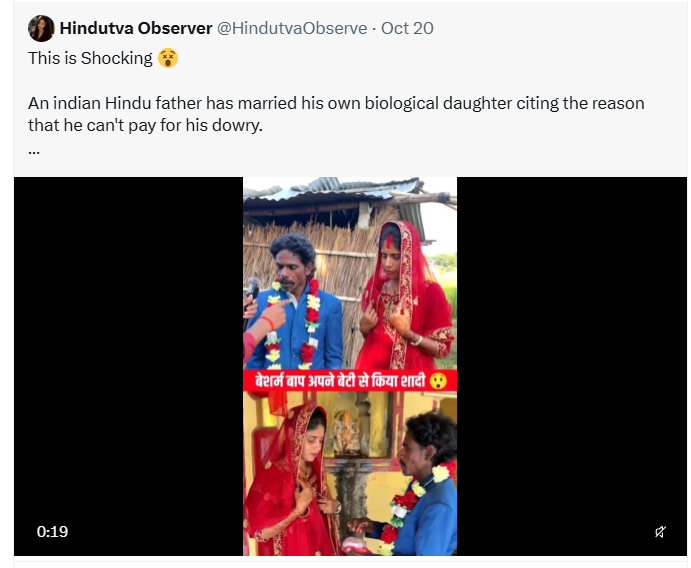
Fact Check
To verify the viral video, we conducted a reverse image search of its keyframes. However, we did not find any credible media reports about the incident. As the next step in our research, we found the video on a Facebook account named Kundan Kumar Mukhiya, where the creator had identified the video as scripted content.
https://www.facebook.com/reel/1170873325369168
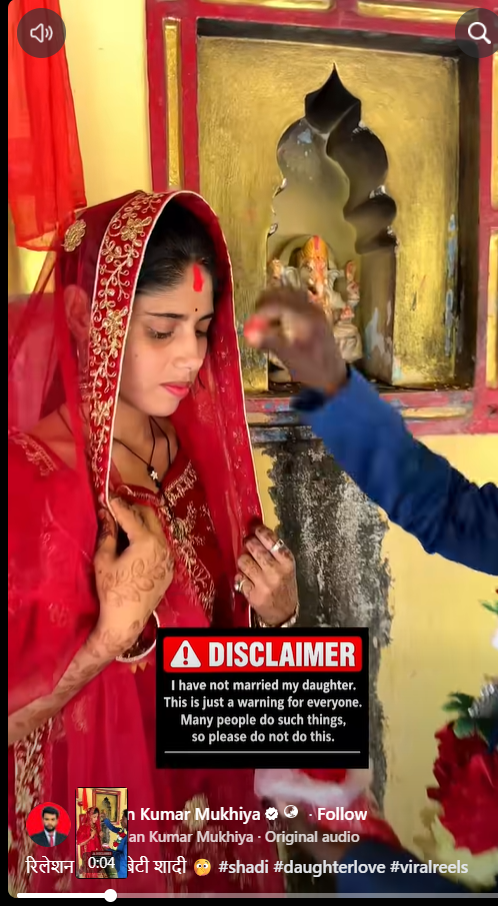
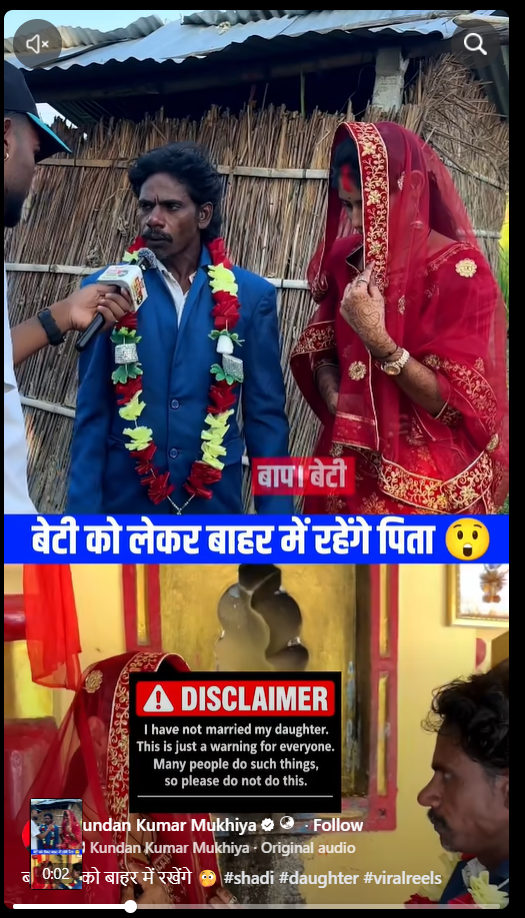
As the next step in our research, we found another video on the same page, which was also identified as scripted content.
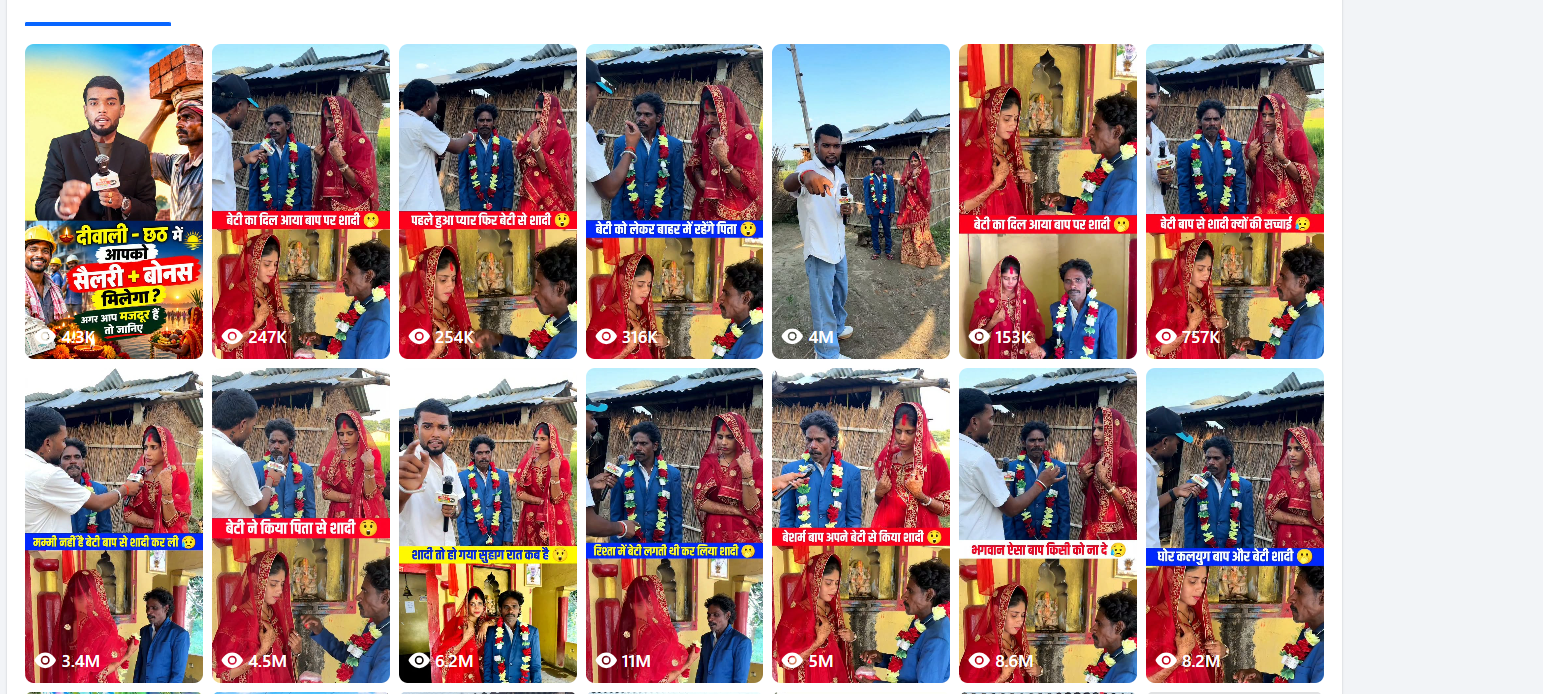
We examined the user's Facebook account and found that he is a content creator who makes scripted videos.
Conclusion
Our research found that the video features scripted content being shared with a misleading claim, presenting it as a real-life incident. The claim that the man married his own biological daughter is false.

Related Blogs

Introduction
India’s telecommunications infrastructure is one of the world’s largest and most complex, serving over a billion users across urban and rural landscapes. With rampant digitisation and mobile penetration, the vulnerability of telecom networks to cyber threats has grown exponentially. On April 24, 2025, the Ministry of Communications (MOC) released a draft of the “Telecommunications (Telecom Cyber Security) Amendment Rules, 2025,” to update the prior Telecommunications (Telecom Cyber Security) Rules, 2024, to improve cybersecurity in India's telecom industry and fortify network security. Public comments and recommendations regarding these draft rules can be sent to the department by July 24, 2025, after they have been made available for public comment. These rules are enacted under the Telecommunications Act, 2023, to enhance national cybersecurity in the telecom domain. These rules aim to prevent misuse of telecom networks and reinforce data and infrastructure protection mechanisms across service providers.
Safeguarding the Spectrum: Unpacking the 2025 Cybersecurity Revisions
The menace of fraudulent SIM cards deals the issue of cyber threats a fresh hand. The rising number of digital scams can also be attributed to unverified or fake mobile numbers. Fraudulent SIM cards have often been linked to various cybercrimes such as phishing, vishing, SIM swapping and identity theft. The situation has worsened in the face of easy availability of pre-activated SIM cards and weak KYC enforcement. In a recent example, as per reports of June 28, 2025, the Special Task Force (STF) found that the accused was operating a criminal nexus where he utilised fake documents and the Aadhaar credentials of law-abiding locals to activate numerous SIM cards. Following activation, the SIMs were either transferred to other telecom carriers for additional exploitation or sold illegally. This poses a serious concern for the data protection of vulnerable individuals, especially those in rural areas, whose credentials have been compromised.
Given the adverse state of cybersecurity in the telecom industry, the Telecommunications (Telecom Cyber Security) Rules, 2024, were passed on 22nd November, 2024, which put various telecom entities under an obligation to actively prevent cybersecurity threats by adopting such policies that mitigate cybersecurity risks and notify the same to the Central Government. The 2024 Telecom Cybersecurity Rules were a significant step in fortifying India’s telecom infrastructure against cyber threats, but they primarily focused on licensed telecom service providers, leaving behind a large segment of digital platforms operating outside the traditional telecom framework largely unregulated.
Expanding the Net: Key Revisions Under the 2025 Cybersecurity Amendment Rules
The amended rules of 2025 adequately address the regulatory blind spot that is created by the rapid expansion of online services, fintech apps, OTT platforms and social media networks, as these platforms often rely on telecom identifiers such as mobile numbers for user onboarding and service delivery. This regulatory blind spot was exploited for fraud, impersonation and other cybercrimes, especially in the absence of standardised identity verification mechanisms. The proposed regulations would give the government the authority to require private companies’ clients to provide identification if they use a mobile number. For a fee, businesses can also undertake this kind of verification on their own. “ The draft rules introduce a new category called “Telecommunication Identifier User Entities’ (TIUEs), extending cybersecurity compliance obligations to a broad category that now captures any entity using telecom identifiers to deliver digital services. It also creates a unified, government-backed verification framework, enabling better interoperability and uniform user identification norms across sectors.
While strengthening national digital security is the goal of the Telecom Cybersecurity (Amendment) Rules, 2025, the proposed rules create a great deal of uncertainty and compliance difficulties, especially for private digital platforms. A broad definition of Telecommunication Identifier User businesses (TIUEs) may include a variety of businesses, including e-commerce services, fintech apps and OTT platforms, under the purview of required mobile number verification. Given that many platforms already have advanced internal processes in place to verify users, this scope uncertainty creates significant concerns regarding operational clarity.
Conclusion
The Telecommunications (Telecom Cyber Security) Amendment Rules, 2025, represent a necessary evolution in India’s quest to secure its telecom ecosystem amid growing cyber threats. The draft regulations recognise the evolving landscape of digital services by broadening the legal scope to encompass Telecommunication Identifier User Entities (TIUEs). Though the goal of creating a strong, transparent and accountable framework is admirable, more clarification and stakeholder involvement are required due to the scope’s vagueness and the possible compliance burden on digital platforms. A truly durable telecom cybersecurity regime will require striking the correct balance between security, viability and privacy.
References
- https://www.cyberpeace.org/resources/blogs/the-government-enforces-key-sections-of-the-telecommunication-act-2023
- https://www.cyberpeace.org/resources/blogs/govt-notifies-the-telecommunications-telecom-cyber-security-rules-2024
- https://the420.in/uttarakhand-stf-busts-fake-sim-racket-linked-to-cyber-crimes-and-nepal-network/
- https://www.thehindu.com/business/dot-puts-out-draft-rules-to-enable-mobile-user-validation/article69741367.ece
- https://www.scconline.com/blog/post/2025/06/28/dot-telecom-cyber-security-draft-policy-update/

Introduction:
The Federal Bureau of Investigation (FBI) focuses on threats and is an intelligence-driven agency with both law enforcement and intelligence responsibilities. The FBI has the power and duty to look into certain offences that are entrusted to it and to offer other law enforcement agencies cooperation services including fingerprint identification, lab tests, and training. In order to support its own investigations as well as those of its collaborators and to better comprehend and address the security dangers facing the United States, the FBI also gathers, disseminates, and analyzes intelligence.
The FBI’s Internet Crime Complaint Center (IC3) Functions combating cybercrime:
- Collection: Internet crime victims can report incidents and notify the relevant authorities of potential illicit Internet behavior using the IC3. Law enforcement frequently advises and directs victims to use www.ic3.gov to submit a complaint.
- Analysis: To find new dangers and trends, the IC3 examines and examines data that users submit via its website.
- Public Awareness: The website posts public service announcements, business alerts, and other publications outlining specific frauds. Helps to raise awareness and make people become aware of Internet crimes and how to stay protected.
- Referrals: The IC3 compiles relevant complaints to create referrals, which are sent to national, international, local, and state law enforcement agencies for possible investigation. If law enforcement conducts an investigation and finds evidence of a crime, the offender may face legal repercussions.
Alarming increase in cyber crime cases:
In the recently released 2022 Internet Crime Report by the FBI's Internet Crime Complaint Center (IC3), the statistics paint a concerning picture of cybercrime in the United States. FBI’s Internet Crime Complaint Center (IC3) received 39,416 cases of extortion in 2022. The number of cases in 2021 stood at 39,360.
FBI officials emphasize the growing scope and sophistication of cyber-enabled crimes, which come from around the world. They highlight the importance of reporting incidents to IC3 and stress the role of law enforcement and private-sector partnerships.
About Internet Crime Complaint Center IC3:
IC3 was established in May 2000 by the FBI to receive complaints related to internet crimes.
It has received over 7.3 million complaints since its inception, averaging around 651,800 complaints per year over the last five years. IC3's mission is to provide the public with a reliable reporting mechanism for suspected cyber-enabled criminal activity and to collaborate with law enforcement and industry partners.
The FBI encourages the public to regularly review consumer and industry alerts published by IC3. An victim of an internet crime are urged to submit a complaint to IC3, and can also file a complaint on behalf of another person. These statistics underscore the ever-evolving and expanding threat of cybercrime and the importance of vigilance and reporting to combat this growing challenge.
What is sextortion?
The use or threatened use of a sexual image or video of another person without that person’s consent, derived from online encounters or social media websites or applications, primarily to extort money from that person or asking for sexual favours and giving warning to distribute that picture or video to that person’s friends, acquaintances, spouse, partner, or co-workers or in public domain.
Sextortion is an online crime that can be understood as, when an bad actor coerces a young person into creating or sharing a sexual image or video of themselves and then uses it to get something from such young person, such as other sexual images, money, or even sexual favours. Reports highlights that more and more kids are being blackmailed in this way. Sextortion can also happen to adults. Sextortion can also take place by taking your pictures from social media account and converting those pictures into sexually explicit content by morphing such images or creating deepfake by miusing deepfake technologies.
Sextortion in the age of AI and advanced technologies:
AI and deep fake technology make sextortion even more dangerous and pernicious. A perpetrator can now produce a high-quality deep fake that convincingly shows a victim engaged in explicit acts — even if the person has not done any such thing.
Legal Measures available in cases of sextortion:
In India, cybersecurity is governed primarily by the Indian Penal Code (IPC) and the Information Technology Act, 2000 (IT Act). Addressing cyber crimes such as hacking, identity theft, and the publication of obscene material online, sextortion and other cyber crimes. The IT Act covers various aspects of electronic governance and e-commerce, with providing provisions for defining such offences and providing punishment for such offences.
Recently Digital Personal Data Protection Act, 2023 has been enacted by the Indian Government to protect the digital personal data of the Individuals. These laws collectively establish the legal framework for cybersecurity and cybercrime prevention in India. Victims are urged to report the crime to local law enforcement and its cybercrime divisions. Law enforcement will investigate sextortion cases reports and will undertake appropriate legal action.
How to stay protected from evolving cases of sextortion: Best Practices:
- Report the Crime to law enforcement agency and social media platform or Internet service provider.
- Enable Two-step verification as an extra layer of protection.
- Keep your laptop Webcams covered when not in use.
- Stay protected from malware and phishing Attacks.
- Protect your personal information on your social media account, and also monitor your social media accounts in order to identify any suspicious activity. You can also set and review privacy settings of your social media accounts.
Conclusion:
Sextortion cases has been increased in recent time. Knowing the risk, being aware of rules and regulations, and by following best practices will help in preventing such crime and help you to stay safe and also avoid the chance of being victimized. It is important to spreading awareness about such growing cyber crimes and empowering the people to report it and it is also significant to provide support to victims. Let’s all unite in order to fight against such cyber crimes and also to make life a safer place on the internet or digital space.
References:
- https://www.ic3.gov/Media/PDF/AnnualReport/2022_IC3ElderFraudReport.pdf
- https://octillolaw.com/insights/fbi-ic3-releases-2022-internet-crime-report/
- https://www.iafci.org/app_themes/docs/Federal%20Agency/2022_IC3Report.pdf
Introduction
With the increasing frequency and severity of cyber-attacks on critical sectors, the government of India has formulated the National Cyber Security Reference Framework (NCRF) 2023, aimed to address cybersecurity concerns in India. In today’s digital age, the security of critical sectors is paramount due to the ever-evolving landscape of cyber threats. Cybersecurity measures are crucial for protecting essential sectors such as banking, energy, healthcare, telecommunications, transportation, strategic enterprises, and government enterprises. This is an essential step towards safeguarding these critical sectors and preparing for the challenges they face in the face of cyber threats. Protecting critical sectors from cyber threats is an urgent priority that requires the development of robust cybersecurity practices and the implementation of effective measures to mitigate risks.
Overview of the National Cyber Security Policy 2013
The National Cyber Security Policy of 2013 was the first attempt to address cybersecurity concerns in India. However, it had several drawbacks that limited its effectiveness in mitigating cyber risks in the contemporary digital age. The policy’s outdated guidelines, insufficient prevention and response measures, and lack of legal implications hindered its ability to protect critical sectors adequately. Moreover, the policy should have kept up with the rapidly evolving cyber threat landscape and emerging technologies, leaving organisations vulnerable to new cyber-attacks. The 2013 policy failed to address the evolving nature of cyber threats, leaving organisations needing updated guidelines to combat new and sophisticated attacks.
As a result, an updated and more comprehensive policy, the National Cyber Security Reference Framework 2023, was necessary to address emerging challenges and provide strategic guidance for protecting critical sectors against cyber threats.
Highlights of NCRF 2023
Strategic Guidance: NCRF 2023 has been developed to provide organisations with strategic guidance to address their cybersecurity concerns in a structured manner.
Common but Differentiated Responsibility (CBDR): The policy is based on a CBDR approach, recognising that different organisations have varying levels of cybersecurity needs and responsibilities.
Update of National Cyber Security Policy 2013: NCRF supersedes the National Cyber Security Policy 2013, which was due for an update to align with the evolving cyber threat landscape and emerging challenges.
Different from CERT-In Directives: NCRF is distinct from the directives issued by the Indian Computer Emergency Response Team (CERT-In) published in April 2023. It provides a comprehensive framework rather than specific directives for reporting cyber incidents.
Combination of robust strategies: National Cyber Security Reference Framework 2023 will provide strategic guidance, a revised structure, and a proactive approach to cybersecurity, enabling organisations to tackle the growing cyberattacks in India better and safeguard critical sectors. Rising incidents of malware attacks on critical sectors
In recent years, there has been a significant increase in malware attacks targeting critical sectors. These sectors, including banking, energy, healthcare, telecommunications, transportation, strategic enterprises, and government enterprises, play a crucial role in the functioning of economies and the well-being of societies. The escalating incidents of malware attacks on these sectors have raised concerns about the security and resilience of critical infrastructure.
Banking: The banking sector handles sensitive financial data and is a prime target for cybercriminals due to the potential for financial fraud and theft.
Energy: The energy sector, including power grids and oil companies, is critical for the functioning of economies, and disruptions can have severe consequences for national security and public safety.
Healthcare: The healthcare sector holds valuable patient data, and cyber-attacks can compromise patient privacy and disrupt healthcare services. Malware attacks on healthcare organisations can result in the theft of patient records, ransomware incidents that cripple healthcare operations, and compromise medical devices.
Telecommunications: Telecommunications infrastructure is vital for reliable communication, and attacks targeting this sector can lead to communication disruptions and compromise the privacy of transmitted data. The interconnectedness of telecommunications networks globally presents opportunities for cybercriminals to launch large-scale attacks, such as Distributed Denial-of-Service (DDoS) attacks.
Transportation: Malware attacks on transportation systems can lead to service disruptions, compromise control systems, and pose safety risks.
Strategic Enterprises: Strategic enterprises, including defence, aerospace, intelligence agencies, and other sectors vital to national security, face sophisticated malware attacks with potentially severe consequences. Cyber adversaries target these enterprises to gain unauthorised access to classified information, compromise critical infrastructure, or sabotage national security operations.
Government Enterprises: Government organisations hold a vast amount of sensitive data and provide essential services to citizens, making them targets for data breaches and attacks that can disrupt critical services.
Conclusion
The sectors of banking, energy, healthcare, telecommunications, transportation, strategic enterprises, and government enterprises face unique vulnerabilities and challenges in the face of cyber-attacks. By recognising the significance of safeguarding these sectors, we can emphasise the need for proactive cybersecurity measures and collaborative efforts between public and private entities. Strengthening regulatory frameworks, sharing threat intelligence, and adopting best practices are essential to ensure our critical infrastructure’s resilience and security. Through these concerted efforts, we can create a safer digital environment for these sectors, protecting vital services and preserving the integrity of our economy and society. The rising incidents of malware attacks on critical sectors emphasise the urgent need for updated cybersecurity policy, enhanced cybersecurity measures, a collaboration between public and private entities, and the development of proactive defence strategies. National Cyber Security Reference Framework 2023 will help in addressing the evolving cyber threat landscape, protect critical sectors, fill the gaps in sector-specific best practices, promote collaboration, establish a regulatory framework, and address the challenges posed by emerging technologies. By providing strategic guidance, this framework will enhance organisations’ cybersecurity posture and ensure the protection of critical infrastructure in an increasingly digitised world.
