
#FactCheck-Old Cargo Ship Fire Video Misrepresented as Drone Strike on Indian Vessel Near Oman
Executive Summary
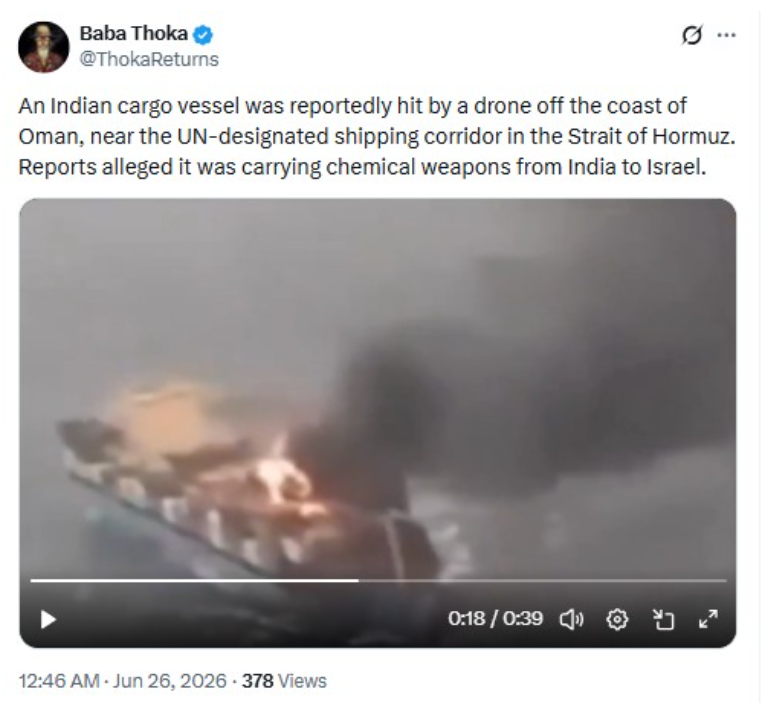
A video is being widely shared on social media showing an Indian cargo vessel engulfed in flames. It is being claimed that the ship was carrying chemical weapons to Israel and was hit by a drone near the Strait of Hormuz off the coast of Oman, after which it caught fire. CyberPeace Research Wing research found the claim to be misleading. The viral video does not show any such incident. Instead, it shows an Indian cargo vessel on fire, but in a completely different context unrelated to any drone strike or weapons shipment allegation.
Claim
The video circulating online is being shared with the claim that it shows an Indian cargo ship carrying chemical weapons to Israel, which was struck by a drone near the Strait of Hormuz off the coast of Oman and subsequently caught fire. https://x.com/ThokaReturns/status/2070224570792251728 , https://x.com/ThokaReturns/status/2070224570792251728
FactCheck
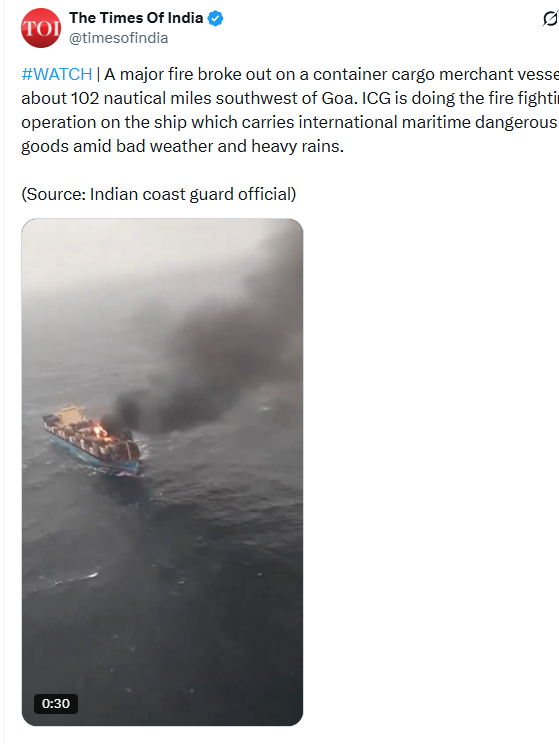
A reverse image search of keyframes from the viral video led us to a Times of India post dated July 19, 2024, on X (formerly Twitter), which contained the same visuals. The report stated that a major fire broke out on a container cargo vessel approximately 102 nautical miles southwest of Goa, following which the Indian Coast Guard launched firefighting operations. A comparison between the news footage and the viral video confirmed that both refer to the same incident. https://x.com/timesofindia/status/1814352708473856175
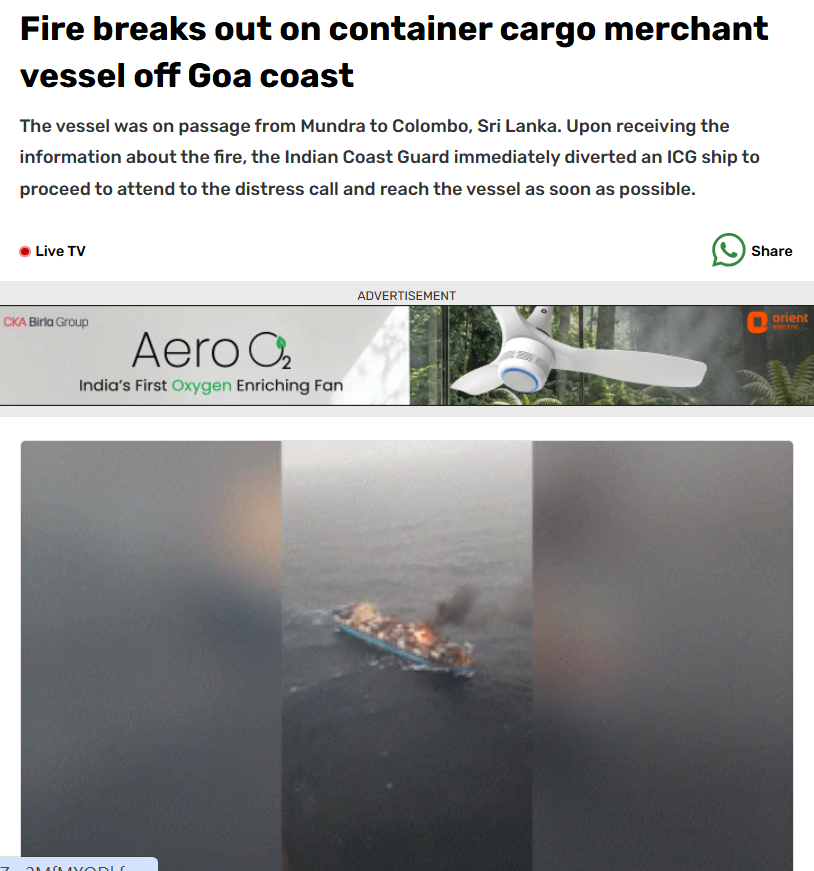
We also found an India Today report on the incident, which stated that the vessel was travelling from Mundra to Colombo, Sri Lanka, when the fire broke out. The Indian Coast Guard immediately diverted one of its ships to respond to the distress call. https://www.indiatoday.in/india/story/fire-breaks-out-container-cargo-merchant-vessel-off-goa-coast-rescue-ops-2569320-2024-07-19
Conclusion
Our research confirms that an old and unrelated video has been shared on social media as visuals of an Indian cargo vessel allegedly hit by a drone off the coast of Oman

Related Blogs

Introduction
In the face of escalating cybercrimes in India, criminals are adopting increasingly inventive methods to deceive victims. Imagine opening your phone to the notification of an incoming message from a stranger with a friendly introduction - a beginning that appears harmless, but is the beginning of an awful financial nightmare. "Pig Butchering '' scam—an increasingly sophisticated form of deception that's gaining more widespread popularity. Unlike any other scams, this one plays a long game, spinning a web of trust before it strikes. It's a modern-day financial thriller happening in the real world, with real victims. "pig butchering" scam, involves building trust through fake profiles and manipulating victims emotionally to extort money. The scale of such scams has raised concerns, emphasising the need for awareness and vigilance in the face of evolving cyber threats.
How does 'Pig Butchering' Scam Work?
At its core, the scam starts innocuously, often with a stranger reaching out via text, social media, or apps like WhatsApp or WeChat. The scammer, hiding behind a well-crafted and realistic online persona, seeks to forge a connection. This could be under the pretence of friendship or romance, employing fake photos and stories to seem authentic. Gradually, the scammer builds a rapport, engaging in personal and often non-financial conversations. They may portray themselves as a widow, single parent, or even a military member to evoke empathy and trust. Over time, this connection pivots to investment opportunities, with the scammer presenting lucrative tips or suggestions in stocks or cryptocurrencies. Initially, modest investments are encouraged, and falsified returns are shown to lure in larger sums. Often, the scammer claims affiliation with a profitable financial institution or success in cryptocurrency trading. They direct victims to specific, usually fraudulent, trading platforms under their control. The scam reaches its peak when significant investments are made, only for the scammer to manipulate the situation, block access to the trading platform, or vanish, leaving the victim with substantial losses.
Real-Life Examples and Global Reach
These scams are not confined to one region. In India, for instance, scammers use emotional manipulation, often starting with a WhatsApp message from an unknown, attractive individual. They pose as professionals offering part-time jobs, leading victims through tasks that escalate in investment and complexity. These usually culminate in cryptocurrency investments, with victims unable to withdraw their funds, the money often traced to accounts in Dubai.
In the West, several cases highlight the scam's emotional and financial toll: A Michigan woman was lured by an online boyfriend claiming to make money from gold trading. She invested through a fake brokerage, losing money while being emotionally entangled. A Canadian man named Sajid Ikram lost nearly $400,000 in a similar scam, initially misled by a small successful withdrawal. In California, a man lost $440,000, succumbing to pressure to invest more, including retirement savings and borrowed money. A Maryland victim faced continuous demands from scammers, losing almost $1.4 million in hopes of recovering previous losses. A notable case involved US authorities seizing about $9 million in cryptocurrency linked to a global pig butchering scam, showcasing its extensive reach.
Safeguarding Against Such Scams
Vigilance is crucial to prevent falling victim to these scams. Be skeptical of unsolicited contacts and wary of investment advice from strangers. Conduct thorough research before any financial engagement, particularly on unfamiliar platforms. Indian Cyber Crime Coordination Center warns of red flags like sudden large virtual currency transactions, interest in high-return investments mentioned by new online contacts, and atypical customer behaviour.
Victims should report incidents to various Indian and foreign websites and the Securities Exchange Commission. Financial institutions are advised to report suspicious activities related to these scams. In essence, the pig butchering scam is a cunning blend of emotional manipulation and financial fraud. Staying informed and cautious is key to avoiding these sophisticated traps.
Conclusion
The Pig Butchering Scams are one of the many new breeds of emerging cyber scams that have become a bone of contention for cyber security organisations. It is imperative for netizens to stay vigilant and well-informed about the dynamics of cyberspace and emerging cyber crimes.
References
- https://www.sentinelassam.com/more-news/national-news/from-impersonating-cbi-officers-to-pig-butchering-cyber-criminals-get-creative
- https://hiindia.com/from-impersonating-cbi-officers-to-pig-butchering-cyber-criminals-get-creative/

Pretext
The Army Welfare Education Society has informed the Parents and students that a Scam is targeting the Army schools Students. The Scamster approaches the students by faking the voice of a female and a male. The scamster asks for the personal information and photos of the students by telling them they are taking details for the event, which is being organised by the Army welfare education society for the celebration of independence day. The Army welfare education society intimated that Parents to beware of these calls from scammers.
The students of Army Schools of Jammu & Kashmir, Noida, are getting calls from the scamster. The students were asked to share sensitive information. Students across the country are getting calls and WhatsApp messages from two numbers, which end with 1715 and 2167. The Scamster are posing to be teachers and asking for the students’ names on the pretext of adding them to the WhatsApp Groups. The scamster then sends forms links to the WhatsApp groups and asking students to fill out the form to seek more sensitive information.
Do’s
- Do Make sure to verify the caller.
- Do block the caller while finding it suspicious.
- Do be careful while sharing personal Information.
- Do inform the School Authorities while receiving these types of calls and messages posing to be teachers.
- Do Check the legitimacy of any agency and organisation while telling the details
- Do Record Calls asking for personal information.
- Do inform parents about scam calling.
- Do cross-check the caller and ask for crucial information.
- Do make others aware of the scam.
Don’ts
- Don’t answer anonymous calls or unknown calls from anyone.
- Don’t share personal information with anyone.
- Don’t Share OTP with anyone.
- Don’t open suspicious links.
- Don’t fill any forms, asking for personal information
- Don’t confirm your identity until you know the caller.
- Don’t Reply to messages asking for financial information.
- Don’t go to a fake website by following a prompt call.
- Don’t share bank Details and passwords.
- Don’t Make payment over a prompt fake call.
Introduction
In today’s digital environment, national security challenges extend well beyond traditional military domains. One growing concern is the unauthorised extraction of information, which is increasingly being used through subtle and gradual methods rather than overt force. Recent advisories point to a rising pattern in which foreign organisations seek to recruit individuals to collect and handle sensitive material, often using financial cybercrime networks as part of their operational ecosystem. This trend has implications for journalists, defence personnel, researchers, students, and academics working in strategic, geopolitical, and security-related fields. The core risk lies in the fact that these activities can proceed quietly and without coercion, with participants sometimes unaware that their actions may contribute to intelligence gathering efforts.
Digital Platforms as Vectors for Targeted Recruitment
Professional networking and job portals have become central to modern career development. The same visibility that supports professional advancement is being misused by others. Foreign entities reportedly use these platforms to identify individuals with experience in journalism, defence services, strategic studies, cybersecurity, and international relations.
Early-career professionals and students from reputed Higher Education Institutions (HEIs) are particularly vulnerable because they seek freelance work, research experience and international partnerships. Initial outreach is often framed as legitimate consultancy, research assistance, or content development work, which creates the impression of professional credibility through normal business operations.
Task-Based Information Extraction
The organisation assigns writing and research duties to new employees, which seem simple to perform. The topics of source-based articles and analytical pieces include the following two subjects about India.
- The first subject examines India's foreign relations with its strategic partnerships.
- The second subject investigates how armed forces operate through different military movements.
- The third subject focuses on defence procurement activities, which include weapon system development and modernisation projects.
- The fourth subject investigates military activities through joint training exercises and war simulation exercises.
The public possesses most of this knowledge, but its threat emerges from the process of collecting and interpreting data with contextual information. The collection of insights from various sources enables organisations to identify operational patterns, strategic priorities and capacity evaluations which go beyond particular data points.
The Financial Cybercrime Nexus
The financial system that pays contributors presents itself as a major problem for this activity. Payments are often routed through:
- Indian bank accounts, including student accounts
- Funds originating from cyber fraud or financial crimes
- Occasional overseas transfers structured to avoid scrutiny
The system establishes a direct connection between financial cybercrime activities and the theft of confidential information, which brings unintentional danger of legal issues and public image damage to those involved. The Indian legal system considers all connections to illegal financial activities as serious offenses even when the person involved did not intend to commit any crime.
Concealed Identities and Data Harvesting
The entities that conduct recruitment activities willfully hide their real identities. The organisation uses intermediaries for their operations, which they present as foreign consulting firms, think tanks and analytics companies. Contributors who have defence or security experience will face requests to provide their personal data, which includes their PAN and Aadhaar information.
The collection of such data raises significant concerns. The system creates permanent privacy hazards that permit unauthorised access to personal data and identity theft and coercive practices. The ultimate use of this information often remains opaque to the individuals providing it.
Why Incremental Leakage Matters
The threat operates silently because it lacks the visibility of major cyberattacks. The combined effect of all articles and research notes becomes dangerous because no single element can cause harm. Hostile organisations can use incremental information leakage to undermine national security because they can analyse their gathered data to create:
- maps of strategic capabilities,
- defence readiness evaluations,
- security and foreign policy narrative control.
The process of information sovereignty erosion occurs through the establishment of undefined boundaries between journalism and academic research, and consultancy and strategic analysis. The lack of clear boundaries between journalism and academic research, consultancy and strategic analysis makes it difficult to determine who is responsible for research outcomes.
The Role of Institutions and Individuals
The universities and media outlets, together with the professional organizations have essential functions in their quest to diminish environmental effects. The organisation should perform the following proactive steps:
- The organisation should organise training programs which will educate people about its services.
- The organisation should require researchers to conduct thorough investigations before they accept paid assignments for research work and writing tasks.
- The organisation should recommend that people do not share their identity documents except when their institution requires it for authentication purposes.
- The organisation should create specific methods to report any suspicious activities that people might encounter.
Students and professionals need to understand that their specialised knowledge and trustworthiness can be used against them. People must protect their digital identities through three actions, which include verifying their affiliations and assessing the complete effects of their daily activities.
Conclusion
Cyber enabled threats to national security increasingly operate in grey zones, which makes their legality, legitimacy, and true intent difficult to assess. The convergence of foreign recruitment efforts, financial cybercrime, and covert information gathering creates a persistent risk that is still not widely recognised or fully understood. The state does not bear exclusive responsibility for protecting sensitive information. National resilience in an interconnected knowledge economy requires organisations to develop three core capacities, which include institutional awareness and restraint and institutional vigilance. Cyber resilience depends on two essential factors, which include secure systems and informed citizens, because data continues to determine power relationships.
References
- https://reports.weforum.org/docs/WEF_Global_Cybersecurity_Outlook_2025.pdf
- https://www.cyber-espionage.ch/
- https://www.theguardian.com/world/2025/nov/18/mi5-issues-alert-to-mps-and-peers-over-chinese-espionage
- http://cybercrimejournal.com/menuscript/index.php/cybercrimejournal/article/download/263/92
- https://www.researchgate.net/publication/368461675_Cyber_Espionage_Consequences_as_a_Growing_Threat
