

Post Session Report on Universal Acceptance and Multilingual Internet at BIT University under CyberPeace Center of Excellence (CCoE)
11th November 2022 CyberPeace Foundation in association with Universal Acceptance has successfully conducted the workshop on Universal Acceptance and Multilingual Internet for the students and faculties of BIT University under CyberPeace Center of Excellence (CCoE).
CyberPeace Foundation has always been engaged towards the aim of spreading awareness regarding the various developments, avenues, opportunities and threats regarding cyberspace. The same has been the keen principle of the CyberPeace Centre of Excellence setup in collaboration with various esteemed educational institutes. We at CyberPeace Foundation would like to take the collaborations and our efforts to a new height of knowledge and awareness by proposing a workshop on UNIVERSAL ACCEPTANCE AND MULTILINGUAL INTERNET. This workshop was instrumental in providing the academia and research community a wholesome outlook towards the multilingual spectrum of internet including Internationalized domain names and email address Internationalization.
Date –11th November 2022
Time – 10:00 AM to 12:00 PM
Duration – 2 hours
Mode - Online
Audience – Academia and Research Community
Participants Joined- 15
Crowd Classification - Engineering students (1st and 4th year, all streams) and Faculties members
Organizer : Mr. Harish Chowdhary : UA Ambassador
Moderator: Ms. Pooja Tomar, Project coordinator cum trainer
Speakers - Mr. Abdalmonem Galila, Abdalmonem: Vice Chair , Universal Acceptance Steering Group (UASG)and
Mr. Mahesh D Kulkarni Director, Evaris Systems and Former Senior Director, CDAC, Government of India,First session was delivered by Mr. Abdalmonem Galila, Abdalmonem: Vice Chair , Universal Acceptance Steering Group (UASG) “Universal Acceptance( UA) and why UA matters?”
- What is universal acceptance?
- UA is cornerstone to a digitally inclusive internet by ensuring all domain names and email addresses in all languages, script and character length.
- Achieving UA ensures that every person has the ability to navigate the internet.
- Different UA issues were also discussed and explained.
- Tagated systems by the UA and implication were discussed in detail.
Second session was delivered by Mr. Mahesh D Kulkarni, ES Director Evaris on the topic of “IDNs in Indian languages perspective- challenges and solutions”.
- The multilingual diversity of India was focused on and its impact.
- Most students were not aware of what Unicode, IDNS is and their usage.
- Students were briefed by giving real time examples on IDN, Domain name implementation using local language.
- In depth knowledge of and practical exposure of Universal Acceptance and Multilingual Internet has been served to the students.
- Tools and Resources for Domain Name and Domain Languages were explained.
- Languages nuances of Multilingual diversity of India explained with real time facts and figures.
- Given the idea of IDN Email,Homograph attack,Homographic variant with proper real time examples.
- Explained about the security threats and IDNA protocols.
- Given the explanation on ABNF.
- Explained the stages of Universal Acceptance.
Related Blogs
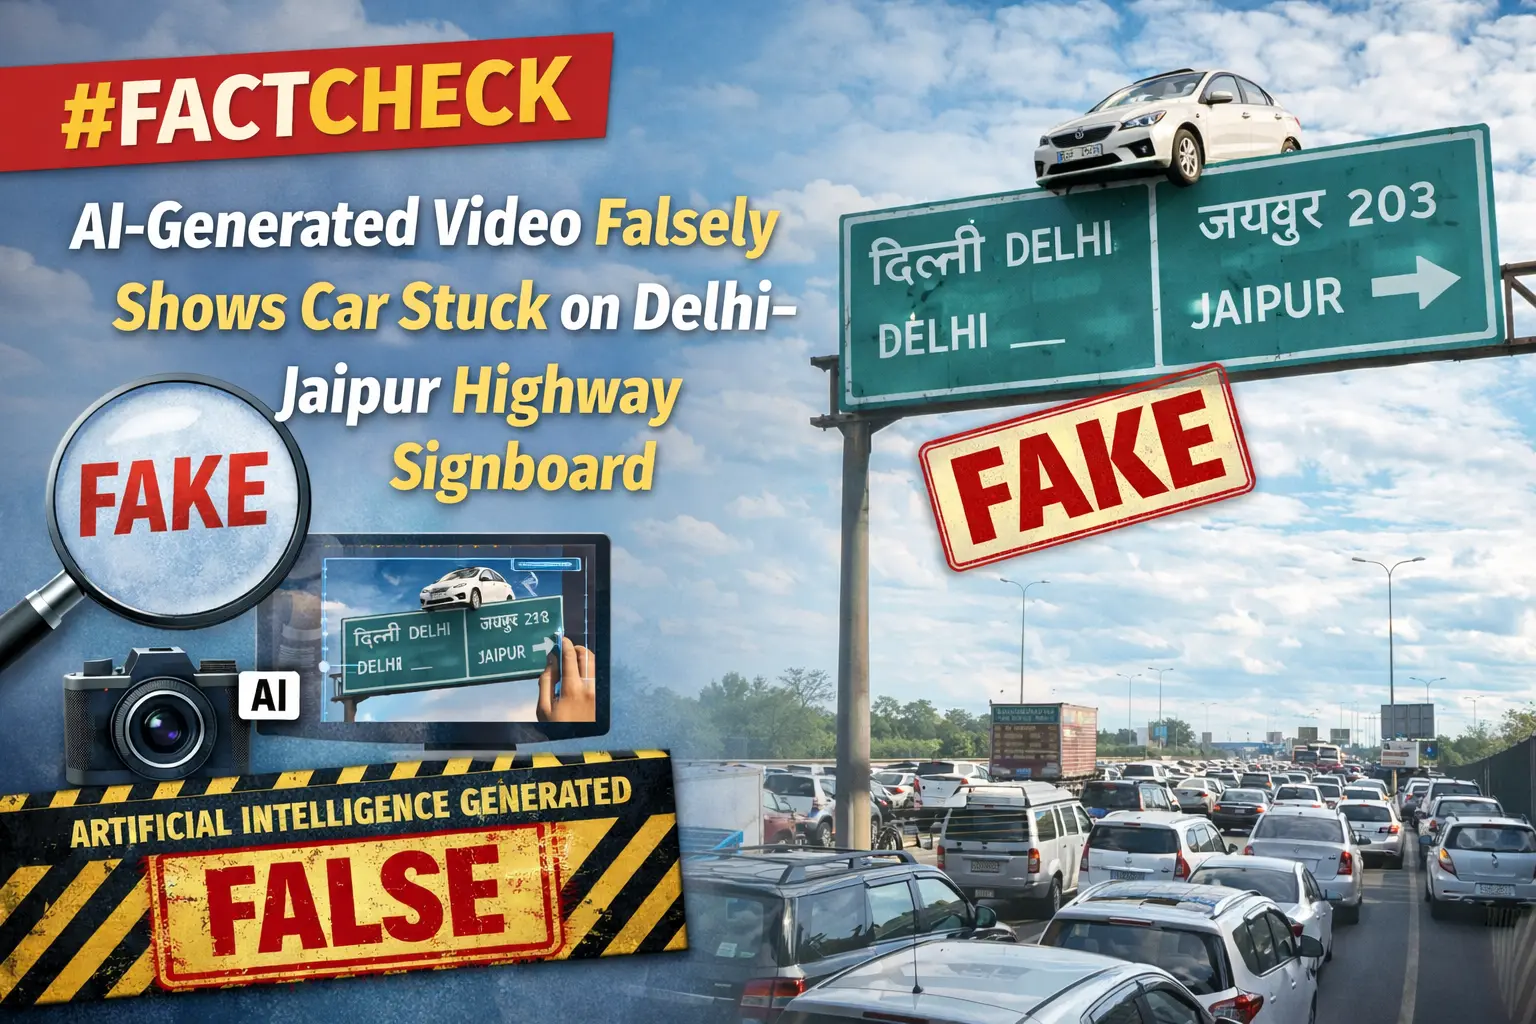
Executive Summary
A shocking video showing a car hanging from a highway signboard is going viral on social media. The clip allegedly shows a black Mahindra Thar stuck on an overhead direction signboard on the Delhi–Jaipur Highway (NH-48). Social media users are widely sharing the video, claiming it shows a real road accident. However, a research by CyberPeace found the viral claim to be false. Our findings reveal that the circulating video is not real but AI-generated.
Claim
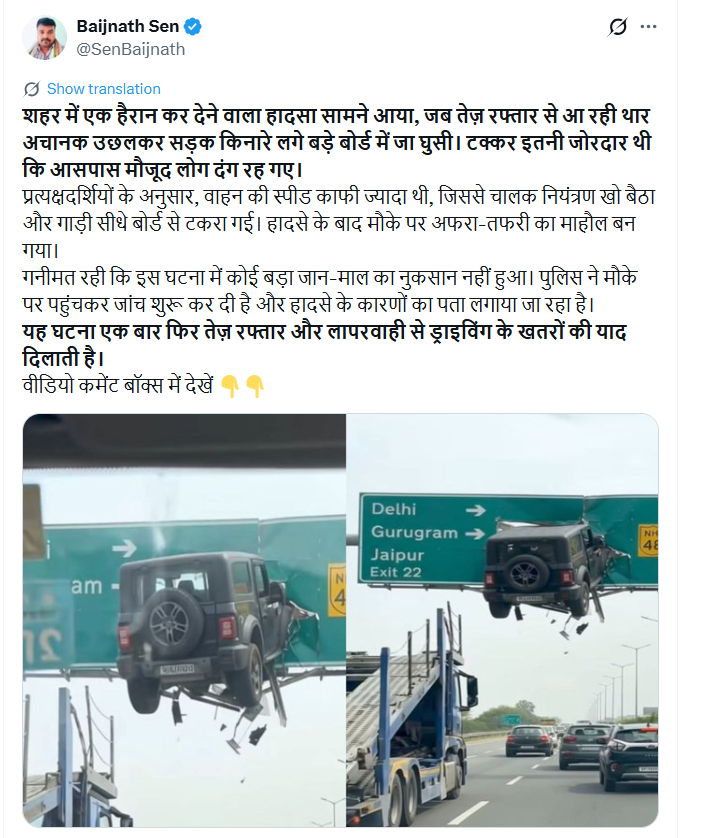
Social media users are sharing the clip as footage of an actual road accident. A viral post on X (formerly Twitter) claims that the incident took place on the Delhi–Jaipur Highway, showing a black Mahindra & Mahindra Thar lodged in a highway signboard.
- https://x.com/SenBaijnath/status/2024098520006029504
- https://archive.ph/cmr5e
Fact Check
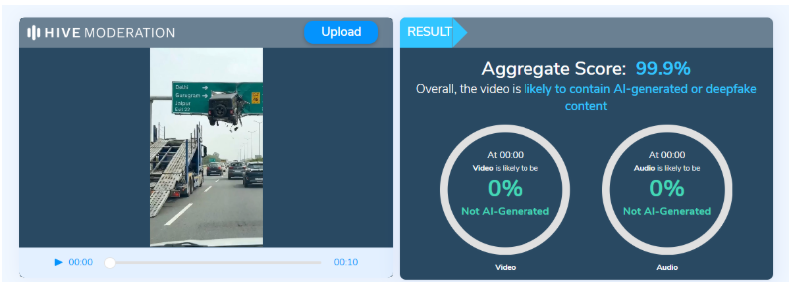
On closely examining the viral video, several inconsistencies were observed that are commonly associated with AI-generated content. For instance, it appears highly improbable for a heavy vehicle to get stuck precisely at the center of a signboard at such a height. Despite the scale of the alleged incident, traffic on the highway below continues moving normally without any disruption. Additionally, the text visible on the right side of the signboard appears distorted and unusually written. To further verify the authenticity of the video, we analysed it using the AI detection tool Hive Moderation, which indicated a 99.9% probability that the video was AI-generated.
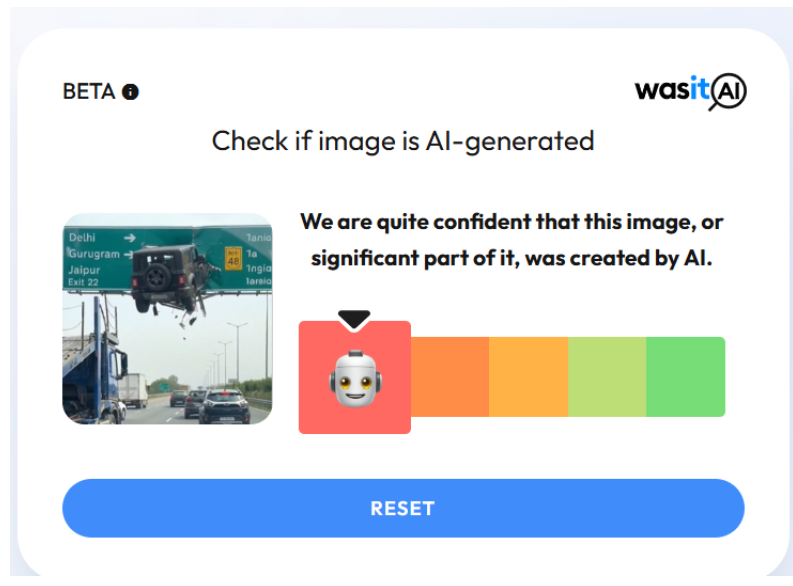
Another AI image detection tool, WasitAI, also found that the visuals in the viral clip were largely AI-generated.
Conclusion
Based on our research and available evidence, it is clear that the viral video showing a Mahindra Thar hanging from a highway signboard is not real but AI-generated.
Introduction
In the contemporary information environment, misinformation has emerged as a subtle yet powerful force capable of shaping public perception, influencing behavior, and undermining institutional credibility. Unlike overt falsehoods, misinformation often gains traction because it appears authentic, familiar, and authoritative. The rapid circulation of content through digital platforms has intensified this challenge, allowing altered or misleading material to reach wide audiences before verification mechanisms can respond. When misinformation mimics official communication, its impact becomes especially concerning, as citizens tend to place implicit trust in documents that carry the appearance of state authority. This growing vulnerability of public information systems was illustrated by the calendar incident in Himachal Pradesh in January 2026.
The calendar incident of Himachal Pradesh in January 2026 shows how a small lie can lead to large social and governance problems. A person whose identity is still unknown posted a modified version of the Government Calendar 2026, changing the official dates and resulting in public confusion and reputational damage to the Printing and Stationery Department. The incident may not appear very serious at first sight, but it indicates a deeper systemic issue. Misinformation is posing increasing dangers to public information ecosystems, especially when official documents are misrepresented and disseminated through digital platforms.
Misinformation as a Governance Challenge
Government calendars and official documents are necessary for public awareness and administrative coordination, and their manipulation impedes the credibility of institutions and the trustworthiness of governance. In Himachal Pradesh, modified dates might have led to confusion regarding public holidays, interference in school and administrative planning, and misinformation among the people. Such misinformation is a direct interference in the social contract that exists between the citizens and the State, where accurate information is the foundation of trust, compliance, and participation.
Impact on Citizens: Confusion, Distrust, and Digital Fatigue
For the general public, the dissemination of fake government information leads to a situation where people are confused and, at the same time, lose their trust in the government communication channels. If someone continuously gets to see the changed or misleading information misrepresented as credible, that person will find it hard to differentiate the truth from lies in the end.
This results in:
- Decision paralysis occurs when the public cannot make up their minds and either postpones or refrains from action due to the doubts they have
- Erosion of trust, not only in one department but also in the whole government communications department
- Digital fatigue occurs when people stop following public information completely, since they think that all content can be unreliable
Misinformation in a digital society is not limited to one platform only. It spreads quickly through direct messaging apps, community groups, and social networks, thus creating greater confusion among people before the official clarifications can reach the same audience.
Institutional Harm and Reputational Damage
The intentional tampering with official documents is not only a violation of ethics but also a crime and an immoral act from a governance perspective. The Printing and Stationery Department noted that such practices tarnish the public image of government bodies, which are based on accuracy, neutrality, and trust.
When untrue material gets to be known as official content:
- Departments have to communicate reactively.
- Money and manpower that could have been used for the normal administrative work are now spent on the control of the situation.
The registration of a First Information Report (FIR) in this matter is an indication of the gradual shift in the perception of law enforcement agencies that misinformation is not a playful act but rather a technology-assisted crime with serious consequences.
The Role of Verifiable Information and Trusted Sources
Such occurrences stress the need for trustworthy information as well as confirmed sources to be at the centre of the digital era. It should be the responsibility of the authorities to lead the citizens to practice and ENABLING to depend on official websites, verified social media accounts, government portals, and press releases for authentication.
Platform Responsibility and Digital Literacy
The spread of misinformation poses a significant challenge for social media platforms, which frequently amplify highly engaging content. There are some ways that the social media networks can try to limit the damage, and these are: tagging of non-verified material, limiting the sharing and working with authorities in the area of fact-checking support. However, one more thing which is crucial here is ‘public knowledge’ about digital platforms, as even unintentional dissemination of fake “official” materials can lead to legal and social repercussions. The advice of the Himachal state government is a good thing, but constantly informing the public is still a requirement.
Legal Accountability as a Deterrent
The active participation of the Cyber Crime Cells unequivocally indicates that digital misinformation, especially involving government documents, will face severe consequences. The establishment of legal responsibility acts as a preventive measure and reiterates the notion that the right to speak one's mind does not cover the right to lie or undermine public institutions. Nonetheless, to have an effective enforcement, it has to be accompanied by preventive actions such as good communication, strong governance, and public trust-building. Consistent enforcement against digital misinformation can contribute to greater accountability within society. Digital Literacy programs should be conducted periodically for netizens and institutions.
Conclusion
The incident of the creation of fake calendars in Himachal Pradesh served as a signal for the authorities to adopt accurate communication strategies. The ratification of misinformation can be achieved only if there is shared participation of governments, digital platforms, citizens and civil societies. The main goal of all this is to maintain public trust and the dissemination of information in democratic processes.
India’s Rapid Digital Expansion
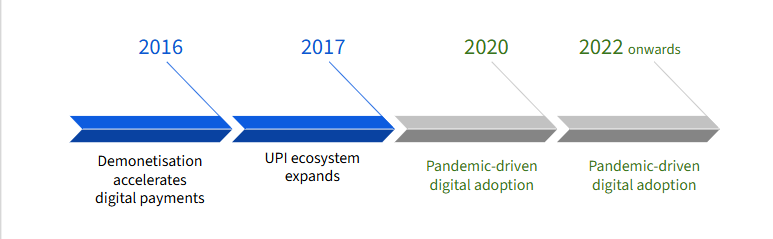
Over the past decade, India has experienced a rapid digitalisation process. The rise of digital financial services, affordable internet costs, and the penetration of smartphones have transformed the way people communicate, transact and do business online.
Online payment systems, including Unified Payments Interface (UPI), have enabled real-time transactions between banks and financial systems. As much as these systems have enhanced access to finance and efficiency, they have also created new opportunities for cybercriminals.
Cybercrime has evolved alongside the shift of financial and social interactions to digital platforms. The fraud attacks on online payments, online banking, and personal information have become common and increasingly costly.
To analyse the scale and trend of cybercrime in India, this analysis will use the datasets released by the National Crime Records Bureau (NCRB) and financial fraud data released by the Indian Cyber Crime Coordination Centre (I4C) under the Ministry of Home Affairs.
The Rise of Cybercrime in India
The Rise of Cybercrime in India
Source: National Crime Records Bureau – Crime in India Reports
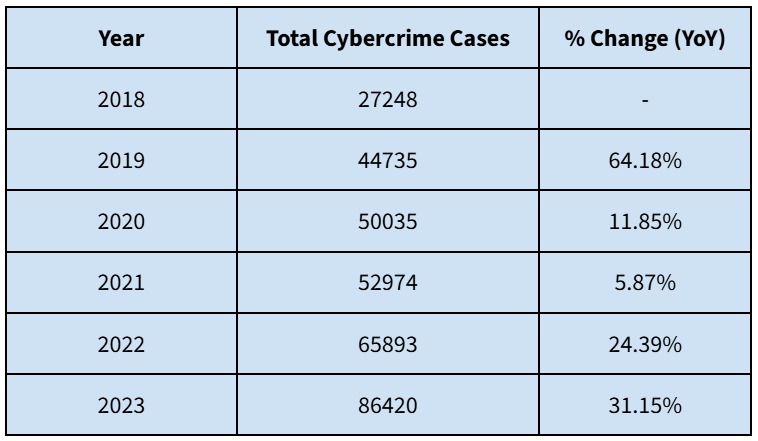
The data released by the NCRB documents cybercrime incidents registered by the police at the national level under the Information Technology Act, 2000 (IT Act) and criminal provisions covering offences such as cheating, impersonation, and digital fraud. In the past, the offences were listed in the provisions of the Indian Penal Code (IPC). Following criminal law reforms in India, on 1 July 2024, the Bharatiya Nyaya Sanhita (BNS), which replaced the IPC, came into force. Section 419 (cheating by impersonation), IPC, would be related to BNS Section 319 and Section 420 (cheating and dishonestly inducing delivery of property), which would be related to BNS Section 318(4). Similarly, crimes involving forgery and use of forged documents or electronic documents, which were previously contained in the IPC Sections 465-471, are dealt with in BNS Sections 335-340.
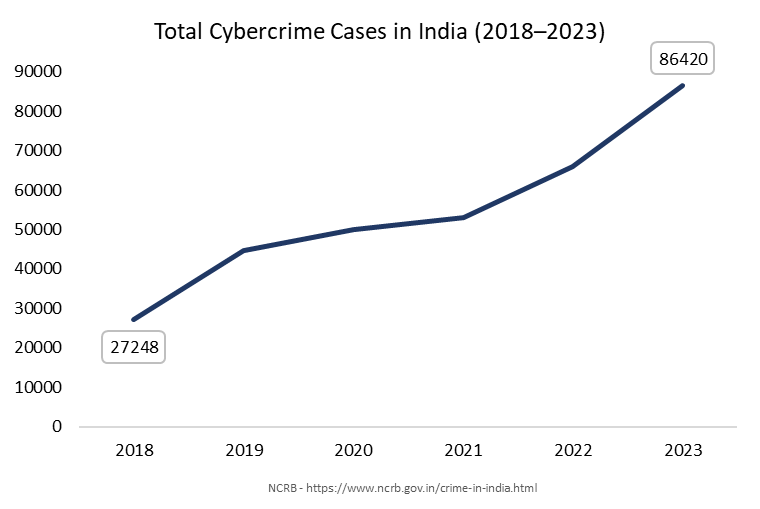
The data published by the NCRB represent the number of crimes that reached the point of the First Information Report (FIR) registration, meaning they reflect only cybercrime cases that were formally presented to the law enforcement system to investigate, rather than all complaints reported. The data shows that cybercrime cases increased from 27,248 in 2018 to 86,420 in 2023, a 3.17-fold increase in 5 years.
Two structural shifts are visible: the post-pandemic jump and subsequent acceleration.
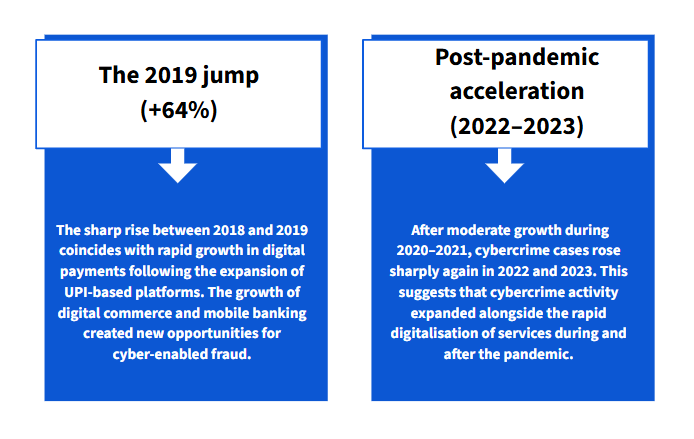
However, these figures likely underestimate the true scale of cybercrime because many incidents are reported only through online complaint portals and may not result in FIR registration.
The Financial Scale of Digital Fraud
The Financial Scale of Digital Fraud
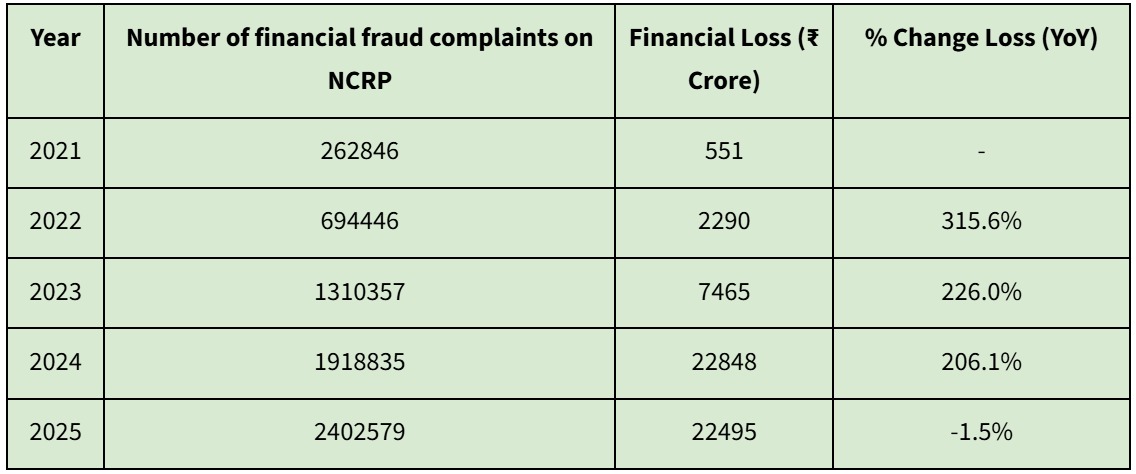
This dataset tracks financial fraud complaints reported through the National Cyber Crime Reporting Portal (NCRP) and the estimated financial losses associated with those complaints.
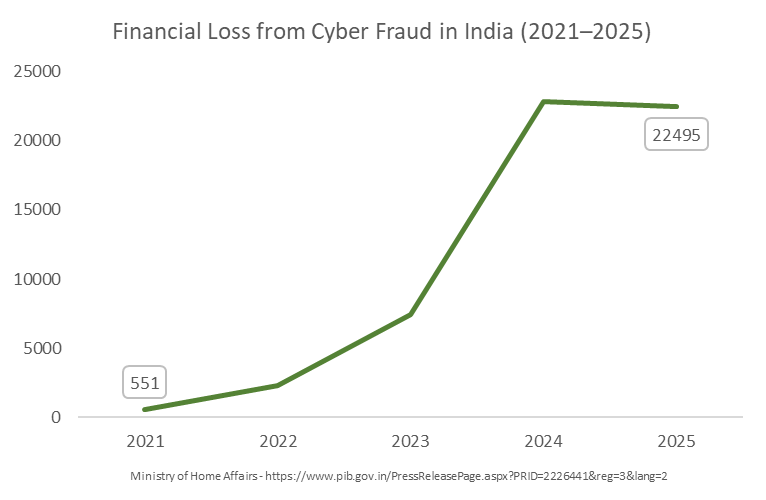
The financial losses reported between 2021 and 2024 increased by 41 times over four years, compared to 2021, from 551 crore to 22,848 crore. At the same time, the number of complaints rose from 262,846 to over 1.9 million, an increase of ~623%, indicating both rising victimisation and greater public awareness of reporting mechanisms.
The contrast between these two trends is striking:
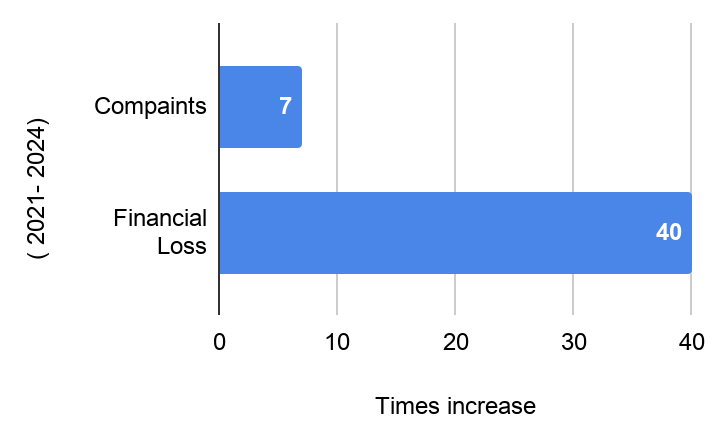
While complaints increased by around 7 times, financial losses increased by over 40 times.
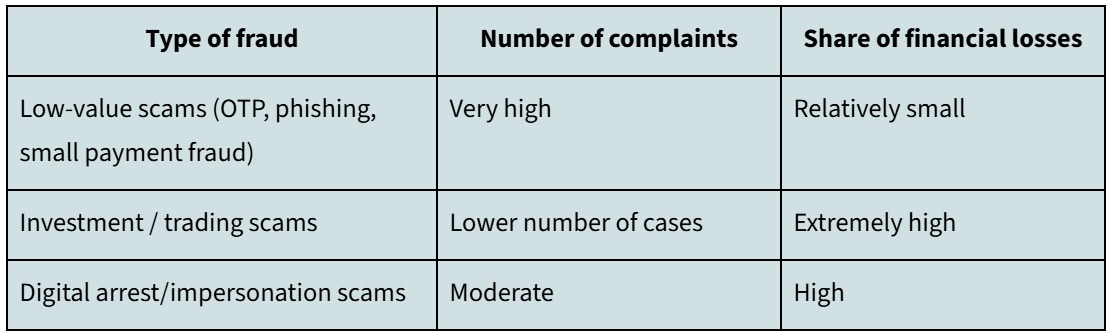
Distribution of Cyber-Fraud Complaints and Financial Losses by Fraud Type
This divergence implies an uneven relationship between the number of incidents and the financial damage that they inflict. Most cyber fraud incidents involve relatively small transaction values; however, a smaller group of fraud categories result in disproportionate numbers of financial losses.
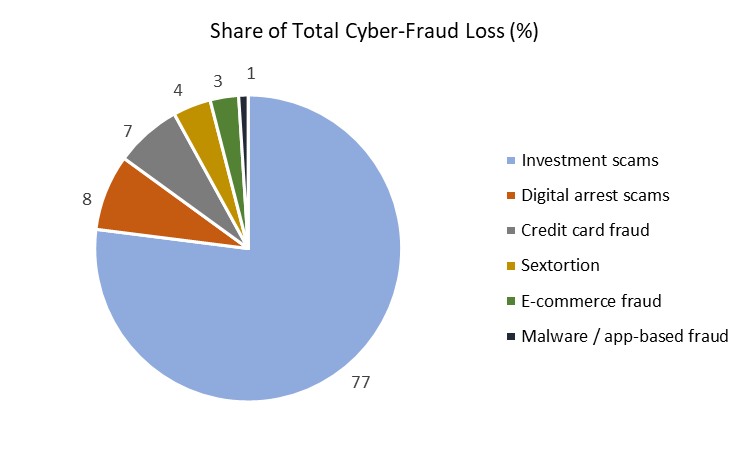
Distribution of Financial Losses Across Major Cyber-Fraud Categories in India
As reported by The Indian Express, based on the data compiled by the I4C, investment-related scams alone account for roughly 77% of reported cyber-fraud losses, followed by smaller shares from “digital arrest” scams (8%), credit card fraud (7%), sextortion (4%), e-commerce fraud (3%), and malware or app-based fraud (1%). This distribution means that even though scams with lower values, like phishing, OTP fraud, and small payment fraud, produce a high proportion of complaints, few categories of fraud produce most of the financial losses.
Analysis
1. Cybercrime is expanding faster than most traditional crimes: The fact that cybercrime cases have tripled in five years shows that cyber offences are presently becoming a significant element of Indian crime. Unlike conventional crimes that require physical proximity, cybercrime can be conducted remotely and at scale, enabling perpetrators to target large numbers of victims simultaneously.
2. Financial losses are concentrated in a small set of fraud categories: As cases of cybercrimes have been on the increase, the monetary losses of digital fraud cases have been increasing at a higher rate. The fact that the number of reported financial losses has increased 40 times in 4 years indicates that cybercrime has a very high economic impact.
3. Complaint volumes and financial damage follow different patterns: When comparing complaints and financial losses, it is evident that cyber fraud losses are unevenly distributed across types of incidents. Most of the prevalent scams reported, including phishing or OTP fraud, involve relatively small transaction values but yield a high portion of complaints. Conversely, fewer categories of fraud, especially investment-based schemes, contribute a significantly higher percentage of total financial losses.
4. Digital financial infrastructure has expanded the attack surface: India’s rapid adoption of digital payment systems, mobile banking and digital financial systems has dramatically increased the number of potential victims of cybercriminals. The scale of online transactions creates new vulnerabilities that organised cybercrime networks take advantage of.
5. Reporting improvements reveal previously hidden crime: The expansion of national reporting systems has enhanced the transparency in the trends of cybercrime. The increase in the number of complaints recorded is partially due to improved reporting systems and not necessarily to the increased criminal activity, meaning that previous data might have understated the magnitude of cyber fraud.
Recommendations
1. Move from reactive policing to proactive cyber-risk monitoring: The conventional models of policing focus on investigation of crimes that have already taken place. With such a magnitude and pace of cyber fraud, India should have systems that are designed to detect and prevent the fraud at its early stages, such as real-time observation of suspicious patterns in transactions by financial institutions.
2. Strengthen financial intelligence sharing across institutions: There are a lot of instances of cyber fraud that use more than one bank, payment system, and telecommunication provider. To detect new networks of fraud sooner, it can be suggested to establish more information-sharing measures between the financial institution and law enforcement agencies.
3. Target organised cyber fraud networks rather than individual incidents: Many digital scams operate through organised networks that coordinate phishing, mule accounts, and fake payment channels. The solution in regard to this involves dismantling these networks through investigative procedures instead of treating incidents on a case-by-case basis.
4. Improve recovery mechanisms for stolen funds: The recovery of the funds lost is one of the most difficult issues in cases of cyber fraud. Expanding systems such as the Citizen Financial Cyber Fraud Reporting and Management System (CFCFRMS) can improve the speed at which fraudulent transactions are frozen or reversed.
5. Strengthen digital financial literacy: A significant percentage of cyber frauds are based on social engineering methods that take advantage of user behaviour as opposed to technical weaknesses. Victimisation can be greatly reduced through specific public awareness efforts on typical scam schemes.
Conclusion
India’s experience illustrates a broader global trend: as economies digitise, crime increasingly follows the flow of digital money. While cybercrime incidents are rising steadily, the much faster growth in financial losses suggests that cybercriminals are becoming more organised, technologically sophisticated, and economically motivated.
References:
- https://indianexpress.com/article/india/indians-lost-rs-53000-crore-fraud-cheating-cases-six-years-maharashtra-2025-10452185/
- https://www.pib.gov.in/PressReleasePage.aspx?PRID=2226441®=3&lang=2 -
- https://www.ncrb.gov.in/crime-in-india.html
- https://i4c.mha.gov.in/index.aspx
- https://i4c.mha.gov.in/index.aspx
