
#FactCheck - Old SBI ATM Site Turned Salon Misrepresented in Viral Social Media Claim
Executive Summary
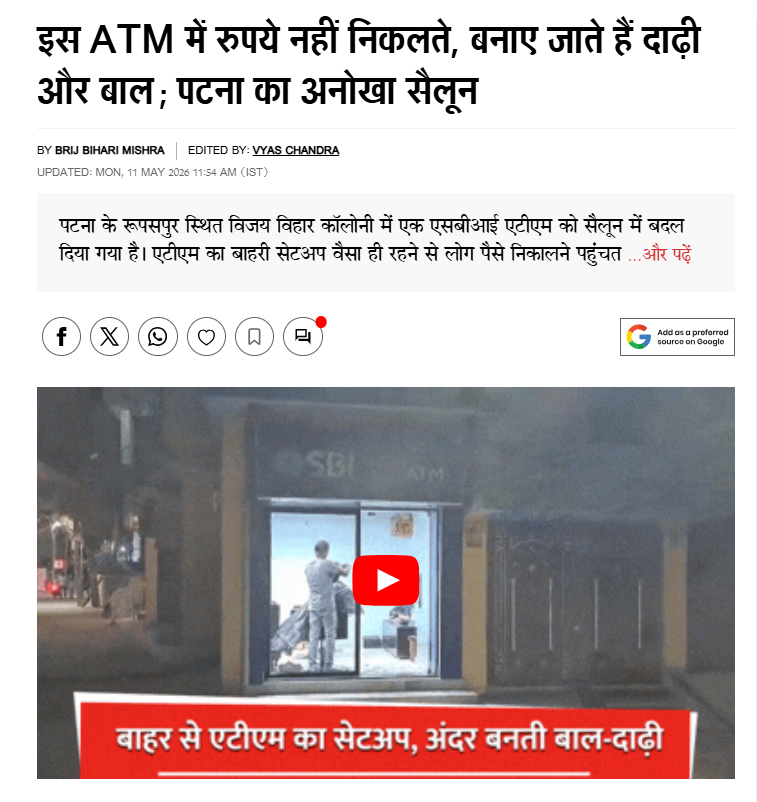
A video is going viral on social media claiming that a salon has been opened inside a State Bank of India (SBI) ATM in Bihar. The video is also being used by some users to take political jibes at the central and state governments led by the Bharatiya Janata Party (BJP). However, the CyberPeace Research Wing’s research has found that this claim is misleading. The location shown in the viral video was earlier an SBI ATM, which had been shut down around six months ago. After the bank discontinued its operations at the site, the ATM machine and other equipment were removed. However, the external structure of the ATM cabin and the SBI signage were not removed at that time. After the premises were vacated, the property owner rented out the space to a salon operator. Since the SBI board and branding were still visible on the structure, the video created confusion and went viral with misleading claims.
Following the circulation of the video, the bank later removed its signage from the location and also cleared all remaining SBI branding from the structure. Our research also found that the bank had removed the ATM machine and equipment months earlier, but the cabin structure and SBI board were left behind. After that, the space was rented out for commercial use as a salon. In this context, it would be incorrect to claim that a salon was opened inside an active SBI ATM.
Claim
A Facebook user ‘Soumitra Roy’ shared a video on 11 May 2026 claiming:
“Someone has opened a barber shop inside an SBI ATM in Bihar. The BJP’s double-engine government has developed Bihar so much that loan EMIs can now be deducted directly inside ATMs. This is Modi’s masterstroke.”
- https://www.facebook.com/reel/980962511535926
- https://perma.cc/WTY2-WEQQ

Fact Check
To verify the viral claim, a keyword search based on the video was conducted. Several media reports were found, which clarified the full context of the incident. A report uploaded on the YouTube channel ‘Live Cities’ on 12 May 2026 stated that a salon was running at a former ATM location in Danapur, Bihar. The bank had already vacated the premises about six months earlier, but its signage had not been removed. The report also includes an interview with the property owner, who confirmed that the bank had removed its ATM machine and equipment six months ago and later the space was rented out to a salon operator.

The viral video was also found on the Jagran website in a news report dated 11 May 2026. The report states that an SBI ATM previously existed at the location. The bank had removed the ATM machine due to operational reasons but left behind the external structure and signage. Later, the space was rented out to a salon operator, who began running his business from the same setup.
Conclusion
Our research found that the viral post is misleading. It is incorrect to claim that a salon was opened inside an SBI ATM. The truth is that the bank had shut down the ATM at this location around six months ago and removed all machines and equipment. After that, the premises were rented out to a salon operator, which led to confusion due to the presence of old SBI signage.

Related Blogs
Introduction
At 4 pm on August 3, 2026, representatives of Meta, X, Snapchat and Google walked into a room in Parliament to face India's Standing Committee on Communications and Information Technology. On paper, it looked like one more instance of a routine that has repeated for half a decade: a Big Tech company gets called in, questioned, and sent away with a warning. But this summons, and the fortnight of scrutiny that has followed it, reveals something different about the direction of India's digital governance in 2026. The government's question has stopped being, "Will you take this post down?" It has increasingly become, "How does your platform actually work, and can we redesign the parts we don't like?"
The trigger: A technical glitch that became a systemic complaint
The proximate cause of the August 3 hearing was almost trivial by itself. On July 23, Prime Minister Narendra Modi posted a video on Instagram and Facebook about the government's crackdown on examination paper leaks. Meta briefly restricted the Facebook version before restoring it, blaming the removal on a technical error in its automated filters.
That explanation didn't satisfy the Ministry of Electronics and Information Technology (MEITY), which called it inadequate, and the incident became the occasion for a much broader reckoning. Committee chairperson Nishikant Dubey summoned Meta, X, Snapchat and Google to examine three things: the online safety of women and children; the data privacy of ordinary citizens, including farmers and labourers; and how far platforms actually comply with India's law-and-order requirements. Days later, MeitY brought Meta's global team in for two days of direct questioning that stretched into a third day of technical discussions covering child sexual abuse material (CSAM), deepfakes, bot accounts and, notably, the design of Instagram's content-recommendation algorithm itself.
From takedown notices to systems audits
For most of the last decade, India's approach to online harm ran through blocking orders and the "notice-and-takedown" machinery built into the IT Rules, 2021: a court or government authority flags a specific URL or post, the platform has a fixed window to act, and non-compliance risks the loss of legal immunity. It was a model built around individual pieces of content.
What is unfolding now looks structurally different. Officials aren't only asking Meta to remove a video; they are asking why its recommendation systems keep resurfacing flagged material, why "verified" accounts belonging to prominent or official figures don't have extra layers of human review before restriction, and why bot-detection and CSAM-screening pipelines aren't catching harmful content before it spreads. The Supreme Court-monitored committee tracking "digital arrest" fraud has gone further still, directing MeitY, the Department of Telecommunications and the Indian Cyber Crime Coordination Centre (I4C) to study time-based restrictions on audio and video calls altogether, a proposal that touches the basic architecture of how calling features work, not any single conversation.
Parliament's committee has separately pushed for a national registration system that would require every intermediary operating in India to publicly list its grievance officer, nodal contact and compliance officer as a response to law enforcement's repeated difficulty simply reaching a platform when something goes wrong. It has also asked for tighter regulation of digital advertising, which officials say is routinely exploited for cyber fraud, and for rules under Section 67C of the IT Act governing how long intermediaries must preserve user data. None of this is about any one post; it is about redesigning the infrastructure platforms use to operate in India.
Messaging apps and the encryption problem
Nowhere is the shift from "content" to "architecture" clearer than in the government's dealings with peer-to-peer messaging platforms. WhatsApp has spent years contesting the traceability requirement under Rule 4(2) of the IT Rules in the Delhi High Court, arguing it would rather exit India than build a permanent capability to identify the "first originator" of every message since doing so would mean re-engineering its end-to-end encryption for all users, not just suspects.
That fight has resurfaced in a new form. In a submission to the parliamentary committee, WhatsApp argued that new rules requiring platforms to detect and label AI-generated "synthetic" content cannot technically apply inside encrypted chats because no one outside a conversation "not even WhatsApp" can see what's inside it. Signal has proven even harder to engage with: MeitY told the committee it has struggled to establish formal contact with the app, which does not publicly list a grievance officer, exposing how little leverage the government currently has over encrypted, minimally staffed platforms compared with advertising-funded giants like Meta and Google. The proposal to cap or restrict call durations to fight "digital arrest" scams is, in effect, an attempt to regulate a messaging feature rather than any message sent through it, perhaps the clearest sign yet that the fight has moved from posts to plumbing.
The future of "safe harbour"
Underpinning all of this is Section 79 of the IT Act, the "safe harbour" clause that shields platforms from liability for what their users post, provided they exercise due diligence. That protection is now being squeezed from three directions at once. The parliamentary committee has unanimously recommended withdrawing safe harbour from platforms that don't comply with Indian law and said it should be pulled specifically from Meta unless its CEO apologises over the PM's video takedown, though a committee cannot itself revoke a statutory protection; only Parliament can amend Section 79. Separately, the Supreme Court-monitored panel on digital-arrest fraud is examining an explicit provision making intermediaries liable for the misuse of their platforms so that fraud victims could claim compensation directly. And MeitY's draft Second Amendment Rules, circulated in March 2026, go furthest of all: they propose making safe harbour conditional on real-time compliance with executive directions, rather than a general protection available to any platform that follows published rules, which is a more direct, command-driven model than even the European Union's Digital Services Act.
Why this matters beyond the headlines
For the ordinary internet user, none of this is abstract. A registration-and-disclosure regime, together with faster and more accountable grievance handling, could make it easier to get genuinely harmful content addressed. But architecture-level intervention cuts both ways. Rules aimed at traceability or at labelling encrypted content risk weakening the very privacy protections that make messaging apps trustworthy in the first place, and a safe harbour that hinges on obeying informal executive directions, rather than settled published law, hands the government far more day-to-day leverage over what stays online. The Supreme Court has listed the digital-arrest matter for September 16; how it, and Parliament, ultimately treat Section 79 will decide whether India's platforms remain neutral pipes carrying other people's speech or become extensions of state enforcement.
Conclusion
India’s digital-governance battle is no longer confined to individual posts or takedown orders. It is increasingly about the architecture beneath the internet: recommendation engines, encryption, verification, data retention and safe-harbour protections. That shift may strengthen accountability and user safety, but it also expands the state’s influence over digital infrastructure. As Parliament and the Supreme Court confront these questions, India faces a fundamental choice: regulate platforms or reshape how they operate.
Sources
- Parliament panel summons Meta, X, Google, Snapchat over digital safety — Hindustan Times
- Parliamentary panel summons Meta, Google, X and Snapchat over social media regulation — Economic Times
- Parliamentary Panel Summons Meta, X, Google on Digital Safety Rules — Asianet Newsable
- Panel Summons Meta, X, Snapchat, Google for Safety Review — New Kerala
- Meta, X, Google and Snapchat summoned by parliamentary panel on August 3 — BestMediaInfo

Introduction
Cyber-attacks are another threat in this digital world, not exclusive to a single country, that could significantly disrupt global movements, commerce, and international relations all of which experienced first-hand when a cyber-attack occurred at Heathrow, the busiest airport in Europe, which threw their electronic check-in and baggage systems into a state of chaos. Not only were there chaos and delays at Heathrow, airports across Europe including Brussels, Berlin, and Dublin experienced delay and had to conduct manual check-ins for some flights further indicating just how interconnected the world of aviation is in today's world. Though Heathrow assured passengers that the "vast majority of flights" would operate, hundreds were delayed or postponed for hours as those passengers stood in a queue while nearly every European airport's flying schedule was also negatively impacted.
The Anatomy of the Attack
The attack specifically targeted Muse software by Collins Aerospace, a software built to allow various airlines to share check-in desks and boarding gates. The disruption initially perceived to be technical issues soon turned into a logistical nightmare, with airlines relying on Muse having to engage in horror-movie-worthy manual steps hand-tagging luggage, verifying boarding passes over the phone, and manually boarding passengers. While British Airways managed to revert to a backup system, most other carriers across Heathrow and partner airports elsewhere in Europe had to resort to improvised manual solutions.
The trauma was largely borne by the passengers. Stories emerged about travelers stranded on the tarmac, old folks left barely able to walk without assistance, and even families missing important connections. It served to remind everyone that the aviation world, with its schedules interlocked tightly across borders, can see even a localized system failure snowball into a continental-level crisis.
Cybersecurity Meets Aviation Infrastructure
In the last two decades, aviation has become one of the more digitally dependent industries in the world. From booking systems and baggage handling issues to navigation and air traffic control, digital systems are the invisible scaffold on which flight operations are supported. Though this digitalization has increased the scale of operations and enhanced efficiency, it must have also created many avenues for cyber threats. Cyber attackers increasingly realize that to target aviation is not just about money but about leverage. Just interfering with the check-in system of a major hub like Heathrow is more than just financial disruption; it causes panic and hits the headlines, making it much more attractive for criminal gangs and state-sponsored threat actors.
The Heathrow incident is like the worldwide IT crash in July 2024-thwarting activities of flights caused by a botched Crowdstrike update. Both prove the brittleness of digital dependencies in aviation, where one failure point triggering uncontrollable ripple effects spanning multiple countries. Unlike conventional cyber incidents contained within corporate networks, cyber-attacks in aviation spill on to the public sphere in real time, disturbing millions of lives.
Response and Coordination
Heathrow Airport first added extra employees to assist with manual check-in and told passengers to check flight statuses before traveling. The UK's National Cyber Security Centre (NCSC) collaborated with Collins Aerospace, the Department for Transport, and law enforcement agencies to investigate the extent and source of the breach. Meanwhile, the European Commission published a statement that they are "closely following the development" of the cyber incident while assuring passengers that no evidence of a "widespread or serious" breach has been observed.
According to passengers, the reality was quite different. Massive passenger queues, bewildering announcements, and departure time confirmations cultivated an atmosphere of chaos. The wrenching dissonance between the reassurances from official channel and Kirby needs to be resolved about what really happens in passenger experiences. During such incidents, technical restoration and communication flow are strategies for retaining public trust in incidents.
Attribution and the Shadow of Ransomware
As with many cyber-attacks, questions on its attribution arose quite promptly. Rumours of hackers allegedly working for the Kremlin escaped into the air quite possibly inside seconds of the realization, Cybersecurity experts justifiably advise against making conclusions hastily. Extortion ransomware gangs stand the last chance to hold the culprits, whereas state actors cannot be ruled out, especially considering Russian military activity under European airspace. Meanwhile, Collins Aerospace has refused to comment on the attack, its precise nature, or where it originated, emphasizing an inherent difficulty in cyberattribution.
What is clear is the way these attacks bestow criminal leverage and dollars. In previous ransomware attacks against critical infrastructure, cybercriminal gangs have extorted millions of dollars from their victims. In aviation terms, the stakes grow exponentially, not only in terms of money but national security and diplomatic relations as well as human safety.
Broader Implications for Aviation Cybersecurity
This incident brings to consideration several core resilience issues within aviation systems. Traditionally, the airports and airlines had placed premium on physical security, but today, the equally important concept of digital resilience has come into being. Systems such as Muse, which bind multiple airlines into shared infrastructure, offer efficiency but, at the same time, also concentrate that risk. A cyber disruption in one place will cascade across dozens of carriers and multiple airports, thereby amplifying the scale of that disruption.
The case also brings forth redundancy and contingency planning as an urgent concern. While BA systems were able to stand on backups, most other airlines could not claim that advantage. It is about time that digital redundancies, be it in the form of parallel systems or isolated backups or even AI-driven incident response frameworks, are built into aviation as standard practice and soon.
On the policy plane, this incident draws attention to the necessity for international collaboration. Aviation is therefore transnational, and cyber incidents standing on this domain cannot possibly be handled by national agencies only. Eurocontrol, the European Commission, and cross-border cybersecurity task forces must spearhead this initiative to ensure aviation-wide resilience.
Human Stories Amid a Digital Crisis
Beyond technical jargon and policy response, the human stories had perhaps the greatest impact coming from Heathrow. Passengers spoke of hours spent queuing, heading to funerals, and being hungry and exhausted as they waited for their flights. For many, the cyber-attack was no mere headline; instead, it was ¬ a living reality of disruption.
These stories reflect the fact that cybersecurity is no hunger strike; it touches people's lives. In critical sectors such as aviation, one hour of disruption means missed connections for passengers, lost revenue for airlines, and inculcates immense emotional stress. Crisis management must therefore entail technical recovery and passenger care, communication, and support on the ground.
Conclusion
The cybersecurity crisis of Heathrow and other European airports emphasizes the threat of cyber disruption on the modern legitimacy of aviation. The use of increased connectivity for airport processes means that any cyber disruption present, no matter how small, can affect scheduling issues regionally or on other continents, even threatening lives. The occurrences confirm a few things: a resilient solution should provide redundancy not efficiency; international networking and collaboration is paramount; and communicating with the traveling public is just as important (if not more) as the technical recovery process.
As governments, airlines, and technology providers analyse the disruption, the question is longer if aviation can withstand cyber threats, but to what extent it will be prepared to defend itself against those attacks. The Heathrow crisis is a reminder that the stake of cybersecurity is not just about a data breach or outright stealing of money but also about stealing the very systems that keep global mobility in motion. Now, the aviation industry is tested to make this disruption an opportunity to fortify the digital defences and start preparing for the next inevitable production.
References
- https://www.bbc.com/news/articles/c3drpgv33pxo
- https://www.theguardian.com/business/2025/sep/21/delays-continue-at-heathrow-brussels-and-berlin-airports-after-alleged-cyber-attack
- https://www.reuters.com/business/aerospace-defense/eu-agency-says-third-party-ransomware-behind-airport-disruptions-2025-09-22/

A few of us were sitting together, talking shop - which, for moms, inevitably circles back to children, their health and education. Mothers of teenagers were concerned that their children seemed to spend an excessive amount of time online and had significantly reduced verbal communication at home.
Reena shared that she was struggling to understand her two boys, who had suddenly transformed from talkative, lively children into quiet, withdrawn teenagers.
Naaz nodded. “My daughter is glued to her device. I just can’t get her off it! What do I do, girls? Any suggestions?”
Mou sighed, “And what about the rising scams? I keep warning my kids about online threats, but I’m not sure I’m doing enough.”
Not just scams, those come later. What worries me more are the videos and photos of unsuspecting children being edited and misused on digital platforms,” added Reena.
The Digital Parenting Dilemma
For parents, it’s a constant challenge—allowing children internet access means exposing them to potential risks while restricting it invites criticism for being overly strict.
‘What do I do?’ is a question that troubles many parents, as they know how addictive phones and gaming devices can be. (Fun fact: Even parents sometimes struggle to resist endlessly scrolling through social media!)
‘What should I tell them, and when?’ This becomes a pressing concern when parents hear about cyberbullying, online grooming, or even cyberabduction.
‘How do I ensure they stay cybersafe?’ This remains an ongoing worry, as children grow and their online activities evolve.
Whether it’s a single-child, dual-income household, a two-child, single-income family, or any other combination, parents have their hands full managing work, chores, and home life. Sometimes, children have to be left alone—with grandparents, caregivers, or even by themselves for a few hours—making it difficult to monitor their digital lives. While smartphones help parents stay connected and track their child’s location, they can also expose children to risks if not used responsibly.
Breaking It Down
Start cybersafety discussions early and tailor them to your child’s age.
For simplicity, let’s categorize learning into five key age groups:
- 0 – 2 years
- 3 – 7 years
- 8 – 12 years
- 13 – 16 years
- 16 – 19 years
Let’s explore the key safety messages for each stage.
Reminder:
Children will always test boundaries and may resist rules. The key is to lead by example—practice cybersafety as a family.
0 – 2 Years: Newborns & Infants
Pediatricians recommend avoiding screen exposure for children under two years old. If you occasionally allow screen time (for example, while changing them), keep it to a minimum. Children are easily distracted—use this to your advantage.
What can you do?
- Avoid watching TV or using mobile devices in front of them.
- Keep activity books, empty boxes, pots, and ladles handy to engage them.
3 – 7 Years: Toddlers & Preschoolers
Cybersafety education should ideally begin when a child starts engaging with screens. At this stage, parents have complete control over what their child watches and for how long.
What can you do?
- Keep screen time limited and fully supervised.
- Introduce basic cybersecurity concepts, such as stranger danger and good picture vs. bad picture.
- Encourage offline activities—educational toys, books, and games.
- Restrict your own screen time when your child is awake to set a good example.
- Set up parental controls and create child-specific accounts on devices.Secure all devices with comprehensive security software.
8 – 12 Years: Primary & Preteens
Cyber-discipline should start now. Strengthen rules, set clear boundaries, and establish consequences for rule violations.
What can you do?
- Increase screen time gradually to accommodate studies, communication, and entertainment.
- Teach them about privacy and the dangers of oversharing personal information.
- Continue stranger-danger education, including safe/unsafe websites and apps.
- Emphasize reviewing T&Cs before downloading apps.Introduce concepts like scams, phishing, deepfakes, and virus attacks using real-life examples.
- Keep banking and credit card credentials private—children may unintentionally share sensitive information.
Cyber Safety Mantras:
- STOP. THINK. ACT.
- Do Not Trust Blindly Online.
13 – 16 Years: The Teenage Phase
Teenagers are likely to resist rules and demand independence, but if cybersecurity has been a part of their upbringing, they will tolerate parental oversight.
What can you do?
- Continue parental controls but allow greater access to previously restricted content.
- Encourage open conversations about digital safety and online threats.
- Respect their need for privacy but remain involved as a silent observer.
- Discuss cyberbullying, harassment, and online reputation management.
- Keep phones out of bedrooms at night and maintain device-free zones during family time.
- Address online relationships and risks like dating scams, sextortion, and trafficking.
16 – 19 Years: The Transition to Adulthood
By this stage, children have developed a sense of responsibility and maturity. It’s time to gradually loosen control while reinforcing good digital habits.
What can you do?
- Monitor their online presence without being intrusive.Maintain open discussions—teens still value parental advice.
- Stay updated on digital trends so you can offer relevant guidance.
- Encourage digital balance by planning device-free family outings.
Final Thoughts
As a parent, your role is not just to set rules but to empower your child to navigate the digital world safely. Lead by example, encourage responsible usage, and create an environment where your child feels comfortable discussing online challenges with you.
Wishing you a safe and successful digital parenting journey!
