
Securing Digital Banking: RBI Mandates Migration to [.]bank[.]in Domains
Introduction
The Reserve Bank of India (RBI) has mandated banks to switch their digital banking domains to 'Bank.in' by October 31, 2025, as part of a strategy to modernise the sector and maintain consumer confidence. The move is expected to provide a consistent and secure interface for online banking, as a response to the increasing threats posed by cybercriminals who exploit vulnerabilities in online platforms. The RBI's directive is seen as a proactive measure to address the growing concerns over cybersecurity in the banking sector.
RBI Circular - Migration to '.bank.in' domain
The official circular released by the RBI dated April 22, 2025, read as follows:
“It has now been decided to operationalise the ‘. bank.in’ domain for banks through the Institute for Development and Research in Banking Technology (IDRBT), which has been authorised by National Internet Exchange of India (NIXI), under the aegis of the Ministry of Electronics and Information Technology (MeitY), to serve as the exclusive registrar for this domain. Banks may contact IDRBT at sahyog@idrbt.ac.in to initiate the registration process. IDRBT shall guide the banks on various aspects related to application process and migration to new domain.”
“All banks are advised to commence the migration of their existing domains to the ‘.bank.in’ domain and complete the process at the earliest and in any case, not later than October 31, 2025.”
CyberPeace Outlook
The Reserve Bank of India's directive mandating banks to shift to the 'Bank.in' domain by October 31, 2025, represents a strategic and forward-looking measure to modernise the nation’s digital banking infrastructure. With this initiative, the RBI is setting a new benchmark in cybersecurity by creating a trusted, exclusive domain that banks must adopt. This move will drastically reduce cyber threats, phishing attacks, and fake banking websites, which have been major sources of financial fraud. This fixed domain will simplify verification for consumers and tech platforms to more easily identify legitimate banking websites and apps. Furthermore, a strong drop in online financial fraud will have a long-term effect by this order. Since phishing and domain spoofing are two of the most prevalent forms of cybercrime, a shift to a strictly regulated domain name system will remove the potential for lookalike URLs and fraudulent websites that mimic banks. As India’s digital economy grows, RBI’s move is timely, essential, and future-ready.
References

Related Blogs

Introduction
The Ministry of Communications, Department of Telecommunications notified the Telecommunications (Telecom Cyber Security) Rules, 2024 on 22nd November 2024. These rules were notified to overcome the vulnerabilities that rapid technological advancements pose. The evolving nature of cyber threats has contributed to strengthening and enhancing telecom cyber security. These rules empower the central government to seek traffic data and any other data (other than the content of messages) from service providers.
Background Context
The Telecommunications Act of 2023 was passed by Parliament in December, receiving the President's assent and being published in the official Gazette on December 24, 2023. The act is divided into 11 chapters 62 sections and 3 schedules. The said act has repealed the old legislation viz. Indian Telegraph Act of 1885 and the Indian Wireless Telegraphy Act of 1933. The government has enforced the act in phases. Sections 1, 2, 10-30, 42-44, 46, 47, 50-58, 61, and 62 came into force on June 26, 2024. While, sections 6-8, 48, and 59(b) were notified to be effective from July 05, 2024.
These rules have been notified under the powers granted by Section 22(1) and Section 56(2)(v) of the Telecommunications Act, 2023.
Key Provisions of the Rules
These rules collectively aim to reinforce telecom cyber security and ensure the reliability of telecommunication networks and services. They are as follows:
The Central Government agency authorized by it may request traffic or other data from a telecommunication entity through the Central Government portal to safeguard and ensure telecom cyber security. In addition, the Central Govt. can instruct telecommunication entities to establish the necessary infrastructure and equipment for data collection, processing, and storage from designated points.
● Obligations Relating To Telecom Cybersecurity:
Telecom entities must adhere to various obligations to prevent cyber security risks. Telecommunication cyber security must not be endangered, and no one is allowed to send messages that could harm it. Misuse of telecommunication equipment such as identifiers, networks, or services is prohibited. Telecommunication entities are also required to comply with directions and standards issued by the Central Govt. and furnish detailed reports of actions taken on the government portal.
● Compulsory Measures To Be Taken By Every Telecommunication Entity:
Telecom entities must adopt and notify the Central Govt. of a telecom cyber security policy to enhance cybersecurity. They have to identify and mitigate risks of security incidents, ensure timely responses, and take appropriate measures to address such incidents and minimize their impact. Periodic telecom cyber security audits must be conducted to assess network resilience against potential threats for telecom entities. They must report security incidents promptly to the Central Govt. and establish facilities like a Security Operations Centre.
● Reporting of Security Incidents:
- Telecommunication entities must report the detection of security incidents affecting their network or services within six hours.
- 24 hours are provided for submitting detailed information about the incident, including the number of affected users, the duration, geographical scope, the impact on services, and the remedial measures implemented.
The Central Govt. may require the affected entity to provide further information, such as its cyber security policy, or conduct a security audit.
CyberPeace Policy Analysis
The notified rules reflect critical updates from their draft version, including the obligation to report incidents immediately upon awareness. This ensures greater privacy for consumers while still enabling robust cybersecurity oversight. Importantly, individuals whose telecom identifiers are suspended or disconnected due to security concerns must be given a copy of the order and a chance to appeal, ensuring procedural fairness. The notified rules have removed "traffic data" and "message content" definitions that may lead to operational ambiguities. While the rules establish a solid foundation for protecting telecom networks, they pose significant compliance challenges, particularly for smaller operators who may struggle with costs associated with audits, infrastructure, and reporting requirements.
Conclusion
The Telecom Cyber Security Rules, 2024 represent a comprehensive approach to securing India’s communication networks against cyber threats. Mandating robust cybersecurity policies, rapid incident reporting, and procedural safeguards allows the rules to balance national security with privacy and fairness. However, addressing implementation challenges through stakeholder collaboration and detailed guidelines will be key to ensuring compliance without overburdening telecom operators. With adaptive execution, these rules have the potential to enhance the resilience of India’s telecom sector and also position the country as a global leader in digital security standards.
References
● Telecommunications Act, 2023 https://acrobat.adobe.com/id/urn:aaid:sc:AP:767484b8-4d05-40b3-9c3d-30c5642c3bac
● CyberPeace First Read of the Telecommunications Act, 2023 https://www.cyberpeace.org/resources/blogs/the-government-enforces-key-sections-of-the-telecommunication-act-2023
● Telecommunications (Telecom Cyber Security) Rules, 2024

The United Nations in December 2019 passed a resolution that established an open-ended ad hoc committee. This committee was tasked to develop a ‘comprehensive international convention on countering the use of ICTs for criminal purposes’. The UN Convention on Cybercrime is an initiative of the UN member states to foster the principles of international cooperation and establish legal frameworks to provide mechanisms for combating cybercrime. The negotiations for the convention had started in early 2022. It became the first binding international criminal justice treaty to have been negotiated in over 20 years upon its adoption by the UN General Assembly.
This convention addresses the limitations of the Budapest Convention on Cybercrime by encircling a broader range of issues and perspectives from the member states. The UN Convention against Cybercrime will open for signature at a formal ceremony hosted in Hanoi, Viet Nam, in 2025. The convention will finally enter into force 90 days after being ratified by the 40th signatory.
Objectives and Features of the Convention
- The UN Convention against Cybercrime addresses various aspects of cybercrime. These include prevention, investigation, prosecution and international cooperation.
- The convention aims to establish common standards for criminalising cyber offences. These include offences like hacking, identity theft, online fraud, distribution of illegal content, etc. It outlines procedural and technical measures for law enforcement agencies for effective investigation and prosecution while ensuring due process and privacy protection.
- Emphasising the importance of cross-border collaboration among member states, the convention provides mechanisms for mutual legal assistance, extradition and sharing of information and expertise. The convention aims to enhance the capacity of developing countries to combat cybercrime through technical assistance, training, and resources.
- It seeks to balance security measures with the protection of fundamental rights. The convention highlights the importance of safeguarding human rights and privacy in cybercrime investigations and enforcement.
- The Convention emphasises the importance of prevention through awareness campaigns, education, and the promotion of a culture of cybersecurity. It encourages collaborations through public-private partnerships to enhance cybersecurity measures and raise awareness, such as protecting vulnerable groups like children, from cyber threats and exploitation.
Key Provisions of the UN Cybercrime Convention
Some key provisions of the Convention are as follows:
- The convention differentiates cyber-dependent crimes like hacking from cyber-enabled crimes like online fraud. It defines digital evidence and establishes standards for its collection, preservation, and admissibility in legal proceedings.
- It defines offences against confidentiality, integrity, and availability of computer data and includes unauthorised access, interference with data, and system sabotage. Further, content-related offences include provisions against distributing illegal content, such as CSAM and hate speech. It criminalises offences like identity theft, online fraud and intellectual property violations.
- LEAs are provided with tools for electronic surveillance, data interception, and access to stored data, subject to judicial oversight. It outlines the mechanisms for cross-border investigations, extradition, and mutual legal assistance.
- The establishment of a central body to coordinate international efforts, share intelligence, and provide technical assistance includes the involvement of experts from various fields to advise on emerging threats, legal developments, and best practices.
Comparisons with the Budapest Convention
The Budapest Convention was adopted by the Committee of Ministers of the Council of Europe at the 109th Session on 8 November 2001. This Convention was the first international treaty that addressed internet and computer crimes. A comparison between the two Conventions is as follows:
- The global participation in the UNCC is inclusive of all UN member states whereas the latter had primarily European with some non-European signatories.
- The scope of the UNCC is broader and covers a wide range of cyber threats and cybercrimes, whereas the Budapest convention is focused on specific offences like hacking and fraud.
- UNCC strongly focuses on privacy and human rights protections and the Budapest Convention had limited focus on human rights.
- UNCC has extensive provisions for assistance to developing countries and this is in contrast to the Budapest Convention which did not focus much on capacity building.
Future Outlook
The development of the UNCC was a complex process. The diverse views on key issues have been noted and balancing different legal systems, cultural perspectives and policy priorities has been a challenge. The rapid technology evolution that is taking place requires the Convention to be adaptable to effectively address emerging cyber threats. Striking a balance remains a critical concern. The Convention aims to provide a blended approach to tackling cybercrime by addressing the needs of countries, both developed and developing.
Conclusion
The resolution containing the UN Convention against Cybercrime is a step in global cooperation to combat cybercrime. It was adopted without a vote by the 193-member General Assembly and is expected to enter into force 90 days after ratification by the 40th signatory. The negotiations and consultations are finalised for the Convention and it is open for adoption and ratification by member states. It seeks to provide a comprehensive legal framework that addresses the challenges posed by cyber threats while respecting human rights and promoting international collaboration.
References
- https://consultation.dpmc.govt.nz/un-cybercrime-convention/principlesandobjectives/supporting_documents/Background.pdf
- https://news.un.org/en/story/2024/12/1158521
- https://www.interpol.int/en/News-and-Events/News/2024/INTERPOL-welcomes-adoption-of-UN-convention-against-cybercrime#:~:text=The%20UN%20convention%20establishes%20a,and%20grooming%3B%20and%20money%20laundering
- https://www.cnbctv18.com/technology/united-nations-adopts-landmark-global-treaty-to-combat-cybercrime-19529854.htm
Introduction
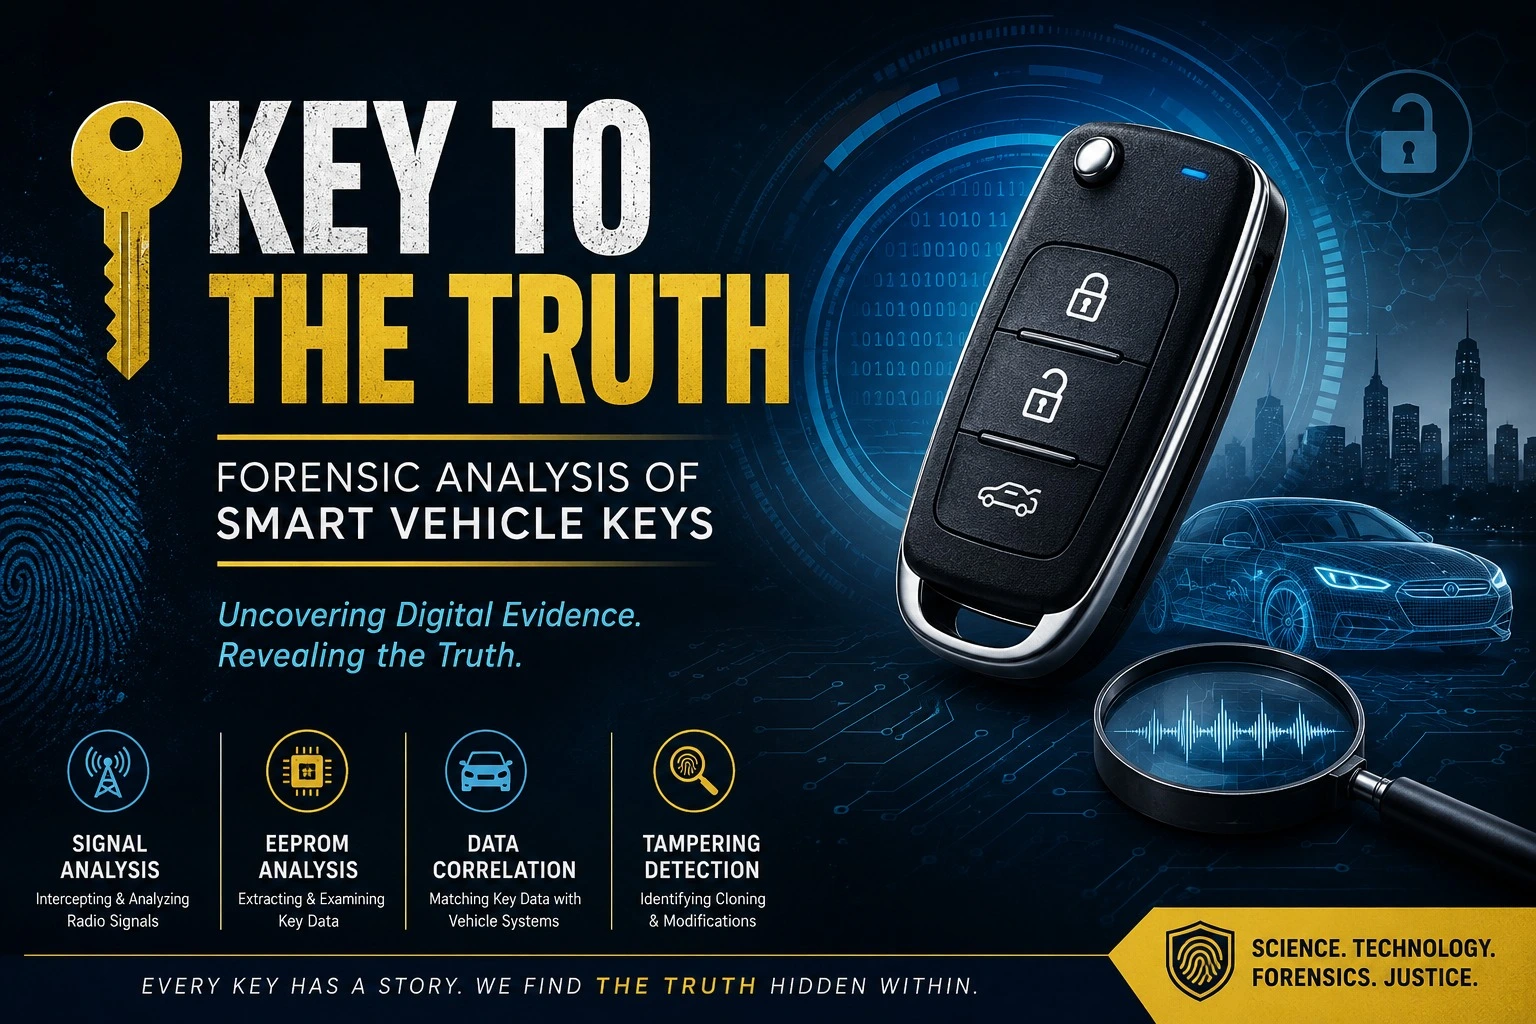
With the modernization of automobiles, so have the methods employed by criminals who seek to commit thefts. The old method of smashing a car window or bypassing an engine lock is no longer prevalent. Modern car thieves employ cloning techniques for keys and digital signals, and sophisticated methods to commit crimes without any traces left behind. In an era where intelligence is crucial, the forensic examination of car keys has become an indispensable tool for investigations, providing clues buried within ordinary car keys.
The Need for Car Key Forensics Today
Daily, thousands of cars worth millions are being hacked or stolen around the globe. The shocking thing is that most of these hacks do not have any sign of breakage or forced entry. It is because the thieves use vulnerabilities in the wireless key systems to unlock the vehicles without leaving any trace behind. Therefore, car-key forensics has now become more important than ever before.
Forensic Value of Smart Key
The smart key is not just comprised of locking and unlocking features for vehicles. Actually, it operates as a miniature computer within the key itself. Information such as pairing records, frequency of use, or the last instance that the key was used to unlock something could be contained in smart keys, thus offering evidence of any criminal activity conducted using these items.
Patterns of Vehicle Theft
Through the examination of the chip in a key, one will be able to establish whether the key was legally programmed or had been tampered with by some other means. Such forensics become more important when trying to detect and monitor any car theft rings, which employ cloning machines or software.
Confirming Ownership and Authenticity
In cases involving insurance claims or fraud, smart key data can help confirm whether the person making a claim actually owned or used the car during the incident. It’s digital proof that goes beyond what paperwork or statements can show.
Strengthening Legal Cases
When brought to court, data doesn’t lie. A properly handled forensic examination of a car key can provide hard evidence — the kind that holds up under questioning and supports or disproves claims with complete accuracy. In many cases, this small device becomes the most reliable witness in the investigation.
A Real-Life Example
Consider the following scenario: An expensive SUV is stolen from a parking lot secured with security surveillance. No one is captured on camera and there is no sign of forced entry. After days of investigation, the police end up arresting a suspect with a smart key.
During forensic analysis of the smart key, it is revealed that:
- The transponder has an ID number which can be matched against the immobilizer installed in the vehicle.
- The rolling code counter has been incremented in such a way that the date corresponds with the report of theft of the vehicle.
- The extracted information helps match the pair timestamp of the key with the particular make and model of the vehicle.
All this from a single piece of evidence – the smart key.
Inside a Smart Key: Where the Data Lives
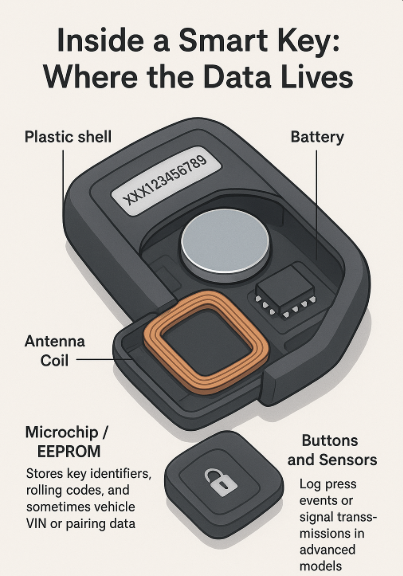
An average smart key is not only a remote but also a multi-level set of data carriers:
- Plastic Shell– could include serial numbers and information on the manufacture.
- Battery – helps calculate the time of using the key or detect any modifications.
- Antenna Coil – sends encrypted information to the immobilizer of a car. Draw the picture of this element.
- Microchip / EEPROM – holds key identification code, rolling code, VIN number, and/or other information of the vehicle.
- Buttons / sensors – could record any pressing or transmission actions in some cases.
All the little devices above, once properly studied via forensics software, provide valuable information.
How the Investigator Uncovers the Truth
In relation to investigating the true story about a vehicle, it is no different than handling other forms of digital evidence, as forensic analysts treat the car key in the same way. It is nothing more than an encrypted device in your hands, and using special techniques, they are able to reveal the information contained within the device.
Some of the methods used by modern forensic laboratories include:
1. Intercepting Radio Signals
Any intelligent key transmits radio signals to communicate with a car. Specialists employ advanced antennas and radio frequency (RF) analysers to catch and analyse them. This way, it is possible to understand the interaction between the key and the car – how often was it used, what kind of authentication procedure takes place, and if the signal matches the car’s one or has been forged somehow.
2. Checking Out the Key’s Brain (Analysis of EEPROM)
There is always a special chip on the key that is responsible for its activity. The chip contains an important memory module (EEPROM – Electrically Erasable Programmable Read-Only Memory), which holds various data, including key IDs and rolling codes. It can be carefully retrieved via advanced tools. Thus, it is possible to determine whether somebody tried to tamper with the key.
3. The Correlation between the Key and Car’s Information
The information stored inside the key will not be used separately since investigators will correlate the key's data with that of the vehicle itself (ECU and immobilizer). If the two kinds of information coincide, the investigation may conclude that the key belongs to the vehicle. Otherwise, this may mean either cloning or tampering.
4. Identifying the Tampering and Cloning Evidence
As was mentioned above, thieves sometimes resort to using unlawful programming devices for duplicating smart car keys. In order to detect possible cloning, experts examine the key using various diagnostic devices to find out whether the keys were modified by changing the encryption code, frequencies, and hardware itself.
At the end of the process, some kind of miracle occurs because of the following: all actions committed with this particular key become documented, recorded inside the device itself. Even if someone tries to hide anything or remove any information concerning this particular incident, there will always remain some data.
Car Key Forensics in the Future
The evolution of cars to connect with other devices and adopt self-driving technologies requires new investigative methods to be used for vehicle-related crimes. Advanced car keys or smartphone apps that replace physical keys will likely incorporate biometric authentication, cloud integration, or blockchain records of key activity in the near future.
Such improvements will pose several threats and offer many benefits:
- Artificial intelligence tools can determine if the car key is cloned based on its behaviour pattern.
- Blockchain validation ensures all key-related activities are recorded and cannot be altered.
- Cyber-forensic protocols will become increasingly necessary for investigating criminal activity related to vehicles.
Car key forensics technology will not only allow solving crimes but may become instrumental in crime prevention.
Conclusion
A car key in this era is more than just an unlocking mechanism; it is a miniature data storage facility, which can yield information about the user, intentions, and access rights. The more cars become technologically advanced, the more the examination of smart keys becomes necessary as part of correlating physical evidence with digital investigation. It clearly indicates how small objects such as keys can play pivotal roles in cracking cases.
