
#FactCheck-Viral Video Claiming a Shooting Incident at Patna High School is Actually From a Film Set
Executive Summary
A 22-second video is circulating on social media platform X (formerly Twitter) with a claim that a shooting incident took place at Patna High School in Bihar. The video shows several masked men running around with weapons in their hands, accompanied by the sound of gunfire. A text overlay on the video reads "Patna High School." However, an research by the CyberPeace Research Wing has revealed that this claim is entirely fake and misleading. The video does not depict a real shooting; it captures an authorized movie/web series shooting on the school premises.
The Claim
Social media users are sharing the video claiming that a real firing incident occurred at Patna High School in Patna, Bihar. https://x.com/IraRuhi/status/2070334893830357499
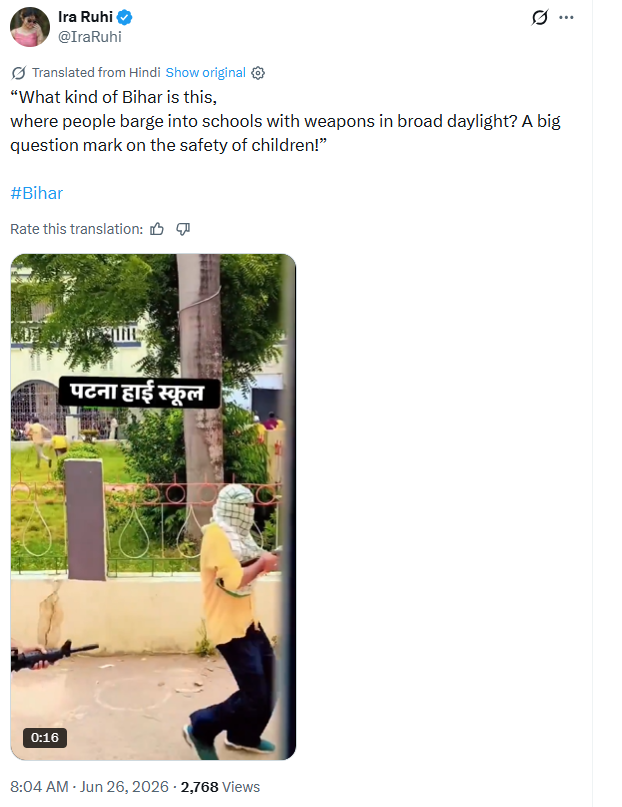
Fact Check
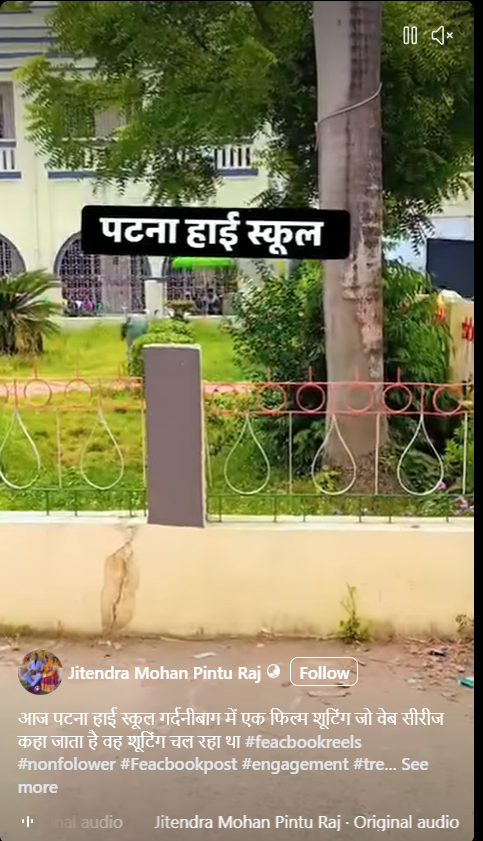
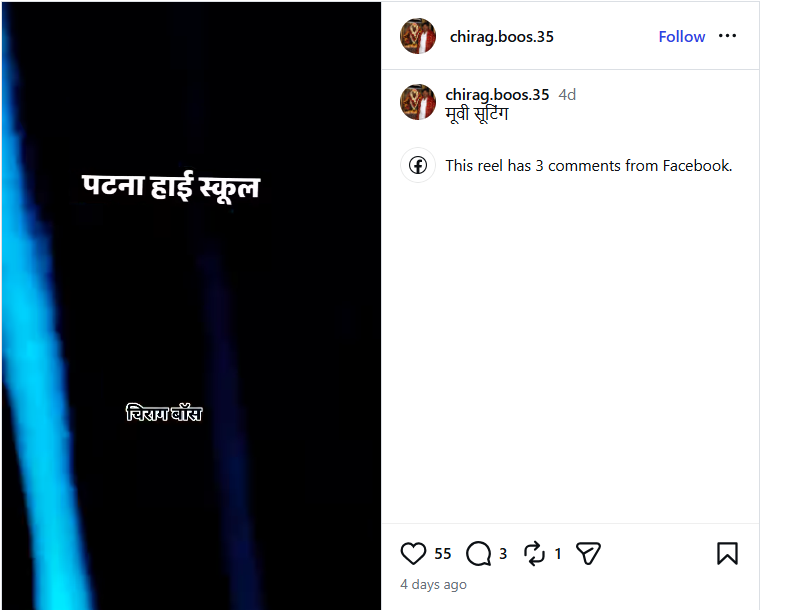
Keyframes from the viral video were analyzed using reverse image search. This led to identical videos uploaded on Facebook and Instagram on June 25, 2026. The captions on both uploads explicitly stated that the footage was from a movie and web series shoot. Furthermore, a closer inspection of the videos revealed professional filmmaking equipment, such as a black flag and a skimmer, visible on the set. https://www.facebook.com/reel/2160248068089642
https://www.instagram.com/p/DaBE0gQglUF/
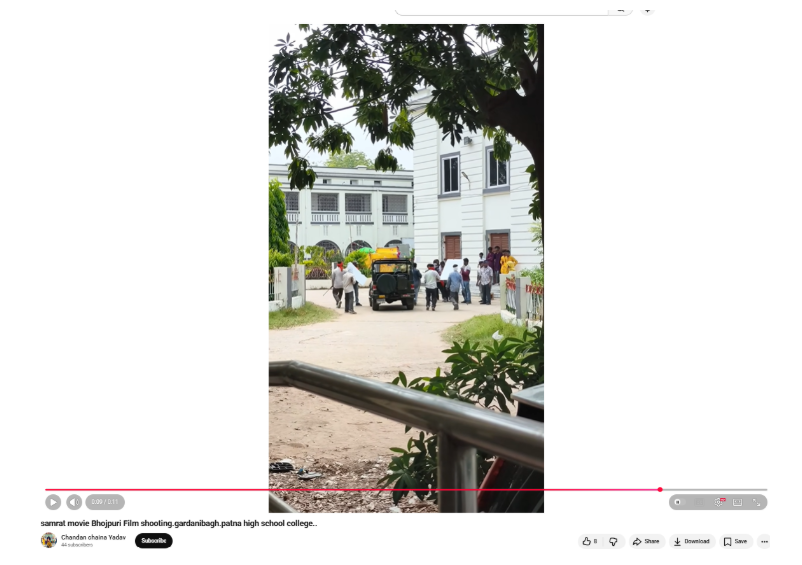
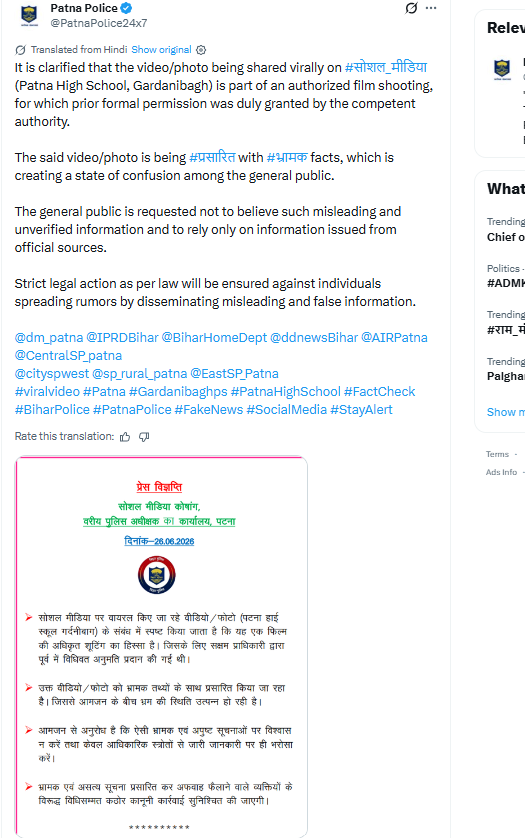
A targeted keyword search led to a YouTube video uploaded on June 20, 2026. The visuals in this video perfectly matched the viral footage, and the individuals seen in the viral clip could be spotted wearing the exact same clothes. "Regarding the video/photo being circulated on social media (Patna High School, Gardanibagh), it is clarified that this is part of an authorized film shooting, for which due permission was previously granted by the competent authority."
To verify further, official statements were checked. The Patna Police issued a formal press release on June 26, 2026, completely dismissing the viral rumors. https://x.com/PatnaPolice24x7/status/2070501501529960581
Conclusion
The evidence gathered confirms that there was no shooting incident at Patna High School. The viral video is behind-the-scenes footage from a pre-approved film production.

Related Blogs
Executive Summary
Amid nationwide outrage over the gang-rape of a 13-year-old minor in Sriganganagar, Rajasthan, a video is circulating on social media. The clip shows police officers tying the hands of several accused individuals and parading them publicly on the streets. Users sharing the video claim that these are the culprits from the Sriganganagar case being beaten by the police.
A fact-check by the CyberPeace Research Wing found this claim to be misleading. The viral video has no connection to the Rajasthan incident; it actually depicts a separate event from Patan, Gujarat, dating back to March 2026.
The Claim
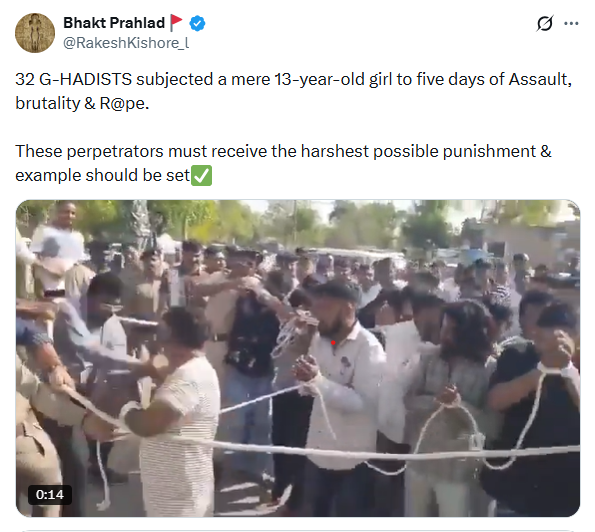
On July 7, 2026, a user on X (formerly Twitter) shared the video with the caption: "32 jihadis assaulted, brutalized, and raped a 13-year-old girl for five days. These criminals must get the harshest punishment to set an example."
https://x.com/RakeshKishore_l/status/2074400280352084129
Fact Check
To verify the viral claim, keyframes from the video were extracted and analysed using Google Lens for reverse image search. During the research, we found a report published by NDTV on March 19, 2026, which carried visuals matching the viral video. The report link and screenshot are provided below:
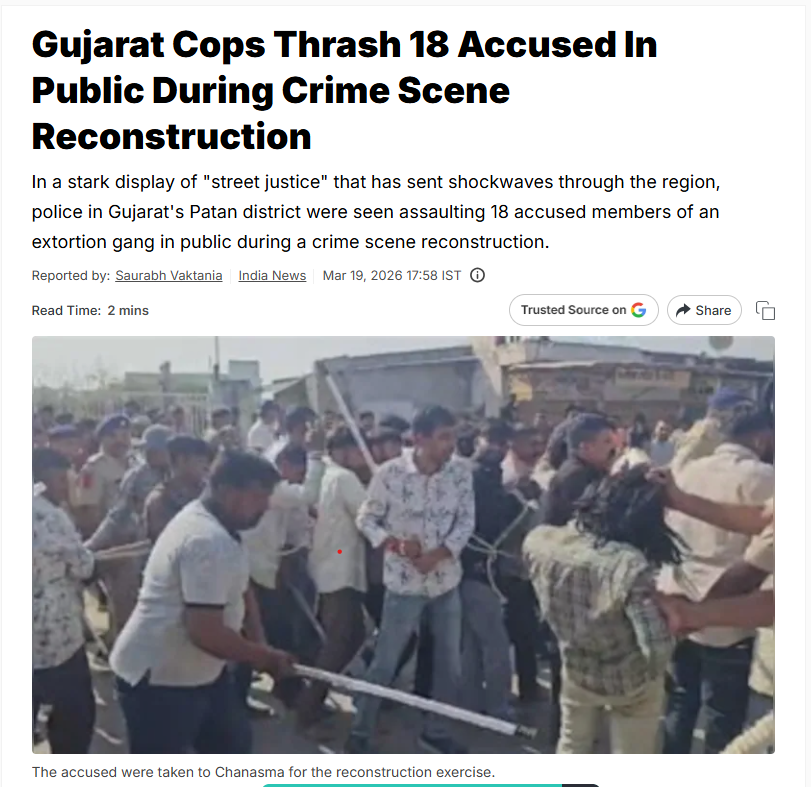
According to the NDTV report, a video showing police personnel publicly assaulting 18 alleged accused persons in Gujarat’s Patan district had surfaced. The incident was reported to have taken place during a crime scene reconstruction exercise.
The report stated that the accused, allegedly linked to an extortion gang, were taken to Chanasma for the reconstruction process. During the exercise, police personnel were seen assaulting them. Witnesses claimed that the accused were paraded through areas where they had allegedly created fear among locals.
The accused were reportedly linked to the alleged Jhiliya gang. The incident occurred days after a violent clash in which members of the same group allegedly attacked a police team, forcing officers to retreat from the spot.
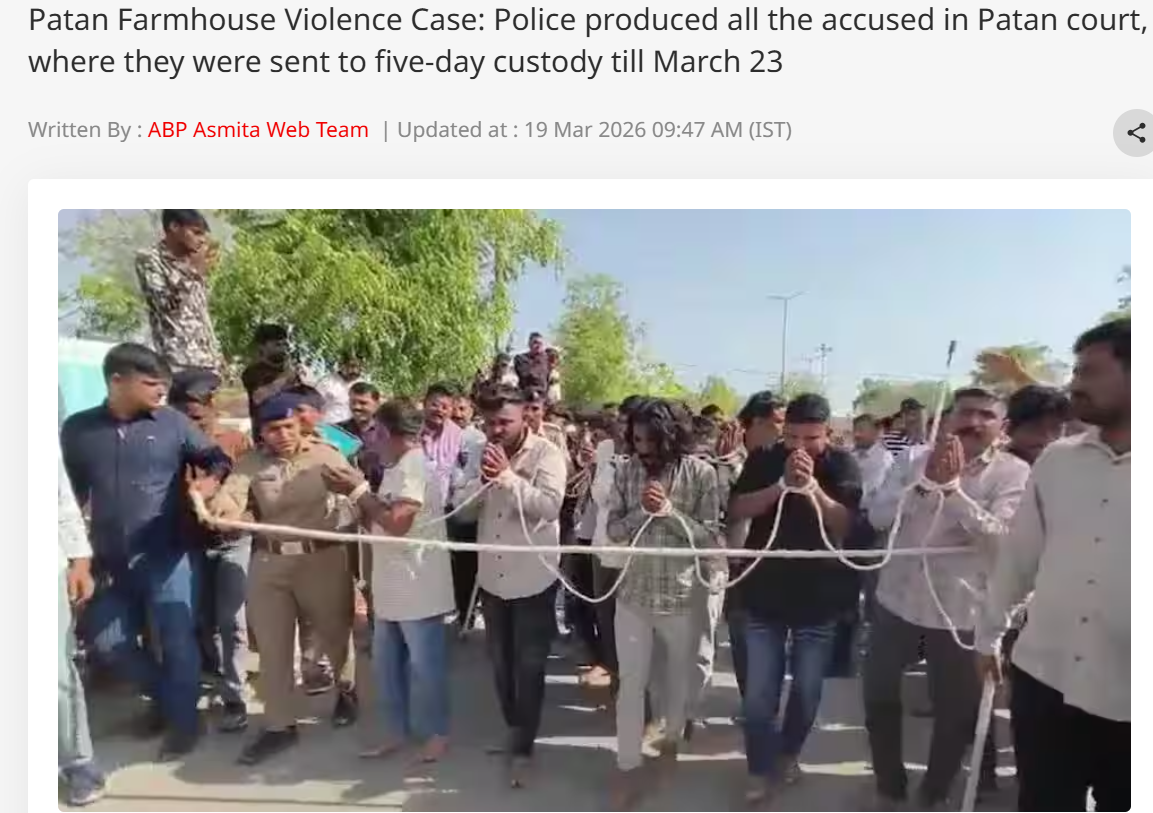
During further research, we found a report published by ABP Asmita on March 19, 2026. According to the report, the incident was linked to an old dispute over temple donations.
The report stated that the accused were produced before a court, which sent them to five days of police custody until March 23, 2026. The report link and screenshot are provided below:
Conclusion
The research found that the viral video is not related to the alleged gang rape case in Sri Ganganagar, Rajasthan. The video is being shared with a false context. The footage actually belongs to a separate incident from Gujarat’s Patan district reported in March 2026.

The Ghibli trend has been in the news for the past couple of weeks for multiple reasons, be it good or bad. The nostalgia that everyone has for the art form has made people turn a blind eye to what the trend means to the artists who painstakingly create the art. The open-source platforms may be trained on artistic material without the artist's ‘explicit permission’ making it so that the rights of the artists are downgraded. The artistic community has reached a level where they are questioning their ability to create, which can be recreated by this software in a couple of seconds and without any thought as to what it is doing. OpenAI’s update on ChatGPT makes it simple for users to create illustrations that are like the style created by Hayao Miyazaki and made into anything from personal pictures to movie scenes and making them into Ghibli-style art. The updates in AI to generate art, including Ghibli-style, may raise critical questions about artistic integrity, intellectual property, and data privacy risks.
AI and the Democratization of Creativity
AI-powered tools have lowered barriers and enable more people to engage with artistic expression. AI allows people to create appealing content in the form of art regardless of their artistic capabilities. The update of ChatGPT has made it so that art has been democratized, and the abilities of the user don't matter. It makes art accessible, efficient and a creative experiment to many.
Unfortunately, these developments also pose challenges for the original artistry and the labour of human creators. The concern doesn't just stop at AI replacing artists, but also about the potential misuse it can lead to. This includes unauthorized replication of distinct styles or deepfake applications. When it is used ethically, AI can enhance artistic processes. It can assist with repetitive tasks, improving efficiency, and enabling creative experimentation.
However, its ability to mimic existing styles raises concerns. The potential that AI-generated content has could lead to a devaluation of human artists' work, potential copyright issues, and even data privacy risks. Unauthorized training of AI models that create art can be exploited for misinformation and deepfakes, making human oversight essential. Few artists believe that AI artworks are disrupting the accepted norms of the art world. Additionally, AI can misinterpret prompts, producing distorted or unethical imagery that contradicts artistic intent and cultural values, highlighting the critical need for human oversight.
The Ethical and Legal Dilemmas
The main dilemma that surrounds trends such as the Ghibli trend is whether it compromises human efforts by blurring the line between inspiration and infringement of artistic freedom. Further, an issue that is not considered by most users is whether the personal content (personal pictures in this case) uploaded on AI models is posing a risk to their privacy. This leads to the issue where the potential misuse of AI-generated content can be used to spread misinformation through misleading or inappropriate visuals.
The negative effects can only be balanced if a policy framework is created that can ensure the fair use of AI in Art. Further, this should ensure that the training of AI models is done in a manner that is fair to the artists who are the original creators of a style. Human oversight is needed to moderate the AI-generated content. This oversight can be created by creating ethical AI usage guidelines for platforms that host AI-generated art.
Conclusion: What Can Potentially Be Done?
AI is not a replacement for human effort, it is to ease human effort. We need to promote a balanced AI approach that protects the integrity of artists and, at the same time, continues to foster innovation. And finally, strengthening copyright laws to address AI-generated content. Labelling AI content and ensuring that this content is disclosed as AI-generated is the first step. Furthermore, there should be fair compensation made to the human artists based on whose work the AI model is trained. There is an increasing need to create global AI ethics guidelines to ensure that there is transparency, ethical use and human oversight in AI-driven art. The need of the hour is that industries should work collaboratively with regulators to ensure that there is responsible use of AI.
References
- https://medium.com/@haileyq/my-experience-with-studio-ghibli-style-ai-art-ethical-debates-in-the-gpt-4o-era-b84e5a24cb60
- https://www.bbc.com/future/article/20241018-ai-art-the-end-of-creativity-or-a-new-movement
Introduction
Imagine receiving a WhatsApp message from your CEO late on a Friday afternoon. The message is urgent: a confidential business deal requires an immediate wire transfer before markets close. The profile picture matches, the tone sounds familiar, and the account it came from has your CEO's name on it. Everything appears legitimate except it is not. This is the essence of the 'Boss Scam,' a sophisticated form of CEO impersonation fraud that has emerged as one of the most financially devastating cybercrime trends of 2025. India's Indian Cyber Crime Coordination Centre (I4C), under the Ministry of Home Affairs, issued an urgent national advisory on this threat in June 2025, warning that organisations across the country are falling victim to an evolved and technically advanced version of executive impersonation fraud that bypasses many traditional cybersecurity safeguards.
Understanding the Boss Scam
What Is CEO Impersonation Fraud?
CEO fraud, also known as Business Email Compromise (BEC) or executive impersonation fraud, is a targeted cyberattack in which criminals assume the digital identity of a high-ranking executive most commonly the Chief Executive Officer to deceive subordinate employees into authorising fraudulent financial transactions or divulging sensitive information. Unlike generic phishing campaigns that cast a wide net, CEO fraud is a precision attack. Cybercriminals invest significant time and resources researching their targets, studying organisational hierarchies, communication styles, and internal financial workflows before executing the scam. The attack is devastatingly effective because it weaponises one of the most powerful forces in any workplace: authority. An instruction that appears to originate from the CEO carries an implicit demand for immediate compliance, often bypassing normal checks and verification procedures. The FBI's Internet Crime Complaint Center (IC3) has consistently identified BEC as one of the most financially destructive categories of cybercrime, with adjusted losses of approximately USD 2.77 billion reported in 2024 alone across the United States.
The New and Evolved Variant: India's I4C Advisory
The variant identified by India's I4C represents a dangerous evolution of traditional CEO fraud. The earlier versions of this scam relied on spoofed email addresses or fake WhatsApp profiles that merely mimicked an executive's account. Employees were trained to spot tell-tale warning signs suspicious domains, unusual sender addresses, or spelling errors in email IDs. The latest
Boss Scam variant eliminates many of these red flags entirely by hijacking the executive's actual and legitimate WhatsApp account. This sophisticated attack begins not with the employee, but with the CEO. Cybercriminals approach senior executives through email or WhatsApp while posing as regulatory authorities in India's context, this includes impersonating officials from the Reserve Bank of India (RBI) or other government bodies. These messages claim an urgent compliance violation or regulatory breach requiring immediate remedial action. The communication contains a compressed ZIP archive, which the executive is prompted to open. Inside the archive are malicious executable (.exe) and Dynamic Link Library (.dll) files that, when run on a Windows system, deploy a Trojan dropper a form of malware capable of establishing persistent access on the device and hijacking active WhatsApp Web session tokens.
Once the session token is compromised, the attacker gains complete control over the executive's WhatsApp account without needing the phone, password, or any two-factor authentication code. The legitimate account is now in criminal hands, and any message sent from it appears entirely authentic to recipients.
How the Boss Scam Operates: A Step-by-Step Breakdown
Stage 1: Targeting the Executive: The operation begins with careful reconnaissance. Attackers study the target organisation's leadership, identify the CEO or a senior executive, and gather publicly available information about their communication patterns, business relationships, and company operations through LinkedIn, corporate websites, and news sources. They then contact the executive under a false regulatory identity, engineering a sense of crisis and urgency.
Stage 2: Malware Deployment:The fraudulent regulatory communication contains a ZIP file disguised as a compliance document, a security patch, or a mandatory software update. Upon execution on a Windows machine, the embedded malware installs itself and begins hijacking the WhatsApp Web session. Critically, in many documented cases, the CEO innocently forwards this regulatory message and the malicious attachment to their own finance officer or IT team, inadvertently widening the attack surface.
Stage 3: Account Takeover and Impersonation:With the CEO's legitimate WhatsApp account now under their control, cybercriminals send highly convincing messages to subordinate staff, particularly those in finance, accounts payable, or treasury functions. These messages carry the full weight of genuine executive authority correct name, profile photo, and account history making them extraordinarily difficult to distinguish from authentic communications.
Stage 4: The Financial Strike:The fraudulent instruction typically requests an urgent, confidential wire transfer to an unfamiliar account, often accompanied by requests for complete secrecy. The employee, believing the instruction to be genuine and fearing the consequences of non-compliance with a directive from their CEO, processes the transaction. By the time the fraud is discovered, the funds have been routed through multiple mule accounts, making recovery extremely difficult.
The Broader Landscape: Scale and Impact
The Boss Scam is not an isolated Indian phenomenon it represents the cutting edge of a global epidemic of executive impersonation fraud. According to the FBI's data, BEC has been the costliest category of cybercrime for several years running, with cumulative global losses that officials have described as exceeding USD 50 billion over the past decade. A 2025 fraud survey found that 90 per cent of U.S. companies experienced attempted cyber-fraud in 2024, with business email compromise and impersonation scams surging by 103 per cent year-on-year. The technological sophistication of these attacks has grown in lockstep with the availability of AI tools. In early 2024, a finance worker at a multinational firm in Hong Kong was tricked into authorising a payment of USD 25 million after attending a video conference in which the CFO and other senior executives were entirely fabricated using deepfake technology. In March 2025, a similar attack unfolded in Singapore, where a finance director authorised nearly USD 499,000 after joining a Zoom call populated entirely by AI-generated deepfakes of company executives. Deepfake attacks against businesses reportedly surged by 3,000 per cent in 2023, and voice cloning fraud rose by 680 per cent the following year. In India, the Telangana Cyber Security Bureau reported over 300 complaints related to the Boss Scam variant alone within a twenty-day period in June 2025. In one prominent case, formerPrime Minister I.K. Gujral's son, Naresh Gujral, reportedly lost approximately Rs 7.8 crorethrough a messaging-app impersonation scheme targeting his company's Chief Financial Officer.
Warning Signs Every Employee Must Recognise
Identifying a Boss Scam attempt requires situational awareness and healthy scepticism. The following red flags should prompt immediate caution:
● Any request for urgent or secret financial transfers received via WhatsApp or email, without prior discussion or formal documentation.
● Instructions to bypass standard approval procedures or to maintain secrecy from colleagues or senior management.
● Compressed files (.zip, .rar) or executable attachments received from any source, including apparently known contacts, claiming to be compliance documents or regulatory updates.
● Messages from executives at unusual hours, particularly those emphasising that a transaction must be completed immediately.
● Claims that a request comes from a government regulator, such as the RBI, delivered through informal channels like WhatsApp.
● Any communication that creates extreme urgency, invokes authority, and simultaneously demands confidentiality the classic triangle of social engineering manipulation. Protective Measures: Defending Against the Boss Scam
For Employees and Finance Teams
The I4C advisory and global cybersecurity authorities recommend several concrete steps that employees can take. The most important is to independently verify any urgent financial instruction through a direct voice call or in-person confirmation before taking action, regardless of how convincing the digital message appears. No financial transaction of significance should be authorised on the basis of a WhatsApp message or email alone.
For Organisations and Leadership
Organisations must implement multi-layered verification protocols for all wire transfers above a defined threshold, making dual authorisation and out-of-band verification mandatory. IT teams should deploy updated malware detection tools, enforce software restriction policies that block unauthorised executable files, and regularly audit devices for signs of compromise. WhatsApp linked devices should be reviewed periodically. Leadership must also commit to regular, mandatory cybersecurity awareness training for all staff, with particular attention to social engineering tactics. The I4C has also emphasised that legitimate regulatory bodies including the RBI , do not distribute software, compliance tools, or security patches via WhatsApp or email attachments. Any such communication must be treated as a potential attack vector and reported immediately.
Conclusion
The Boss Scam exploits organisational trust and human psychology rather than technical vulnerabilities and with deepfake technology now capable of replicating familiar voices and faces, traditional verification instincts are no longer reliable. The strongest defence is a culture of verification without embarrassment, where questioning an unusual instruction is seen as diligence, not insubordination. Awareness, clear protocols, and scepticism towards urgency remain our most powerful tools. If you've encountered such a scam, contact India's National Cybercrime Helpline at 1930 or report at cybercrime.gov.in.
References
- https://www.cybercrime.gov.in
- https://www.business-standard.com/india-news/boss-scam-ceo-impersonation-fraudgovt- advisory-i4c-126062300353_1.html
- https://www.indiatvnews.com/news/india/boss-scam-all-about-the-new-cyber-fraudtargeting- corporates-and-precautions-listed-by-mha-2026-06-23-1045827
- https://www.freepressjournal.in/business/boss-scam-on-whatsapp-new-ceo-fraudbypasses- traditional-cybersecurity-checks
- https://hyderabadmail.com/tgcsb-warns-boss-scam-ceo-impersonation-fraud-malwarealert/
- https://www.newkerala.com/news/a/rising-boss-scam-threat-targets-senior-executiveswarns- 242.html
- https://www.ic3.gov
- https://www.mcafee.com/learn/is-that-really-your-boss/
- https://abnormal.ai/glossary/ceo-fraud
- https://www.brside.com/blog/deepfake-ceo-fraud-50m-voice-cloning-threat-cfos
- https://www.eftsure.com/blog/cyber-crime/these-7-deepfake-ceo-scams-prove-that-nobusiness- is-safe/
- https://www.knowbe4.com/ceo-fraud
- https://trustpair.com/blog/ceo-fraud-how-to-protect-your-organization-from-fraudsters/
- https://hacked.com/services/executive-impersonation-and-ceo-fraud-protecting-high-networth- individuals/
- https://www.certifid.com/article/ceo-fraud
