
#FactCheck: Viral AI Video Showing Finance Minister of India endorsing an investment platform offering high returns.
Executive Summary:
A video circulating on social media falsely claims that India’s Finance Minister, Smt. Nirmala Sitharaman, has endorsed an investment platform promising unusually high returns. Upon investigation, it was confirmed that the video is a deepfake—digitally manipulated using artificial intelligence. The Finance Minister has made no such endorsement through any official platform. This incident highlights a concerning trend of scammers using AI-generated videos to create misleading and seemingly legitimate advertisements to deceive the public.
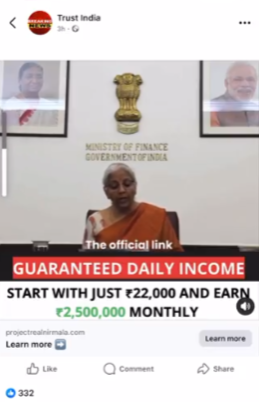
Claim:
A viral video falsely claims that the Finance Minister of India Smt. Nirmala Sitharaman is endorsing an investment platform, promoting it as a secure and highly profitable scheme for Indian citizens. The video alleges that individuals can start with an investment of ₹22,000 and earn up to ₹25 lakh per month as guaranteed daily income.
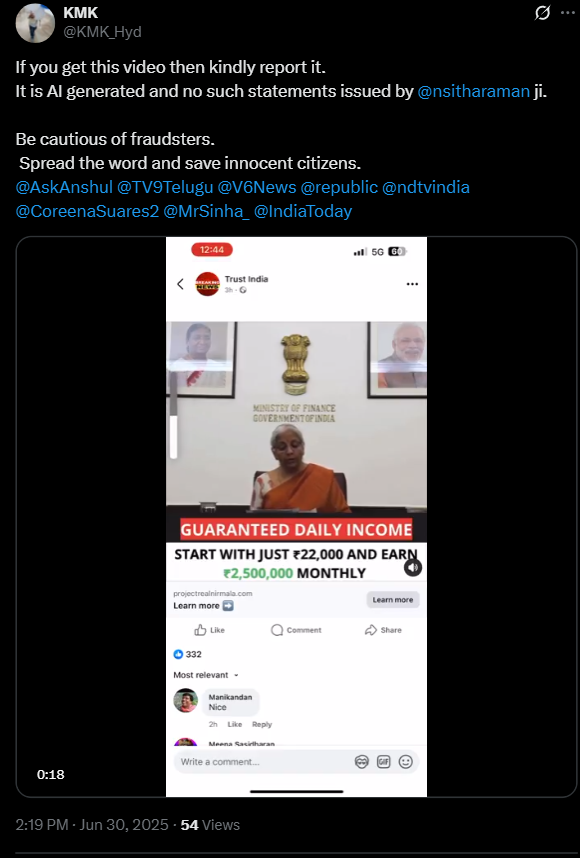
Fact check:
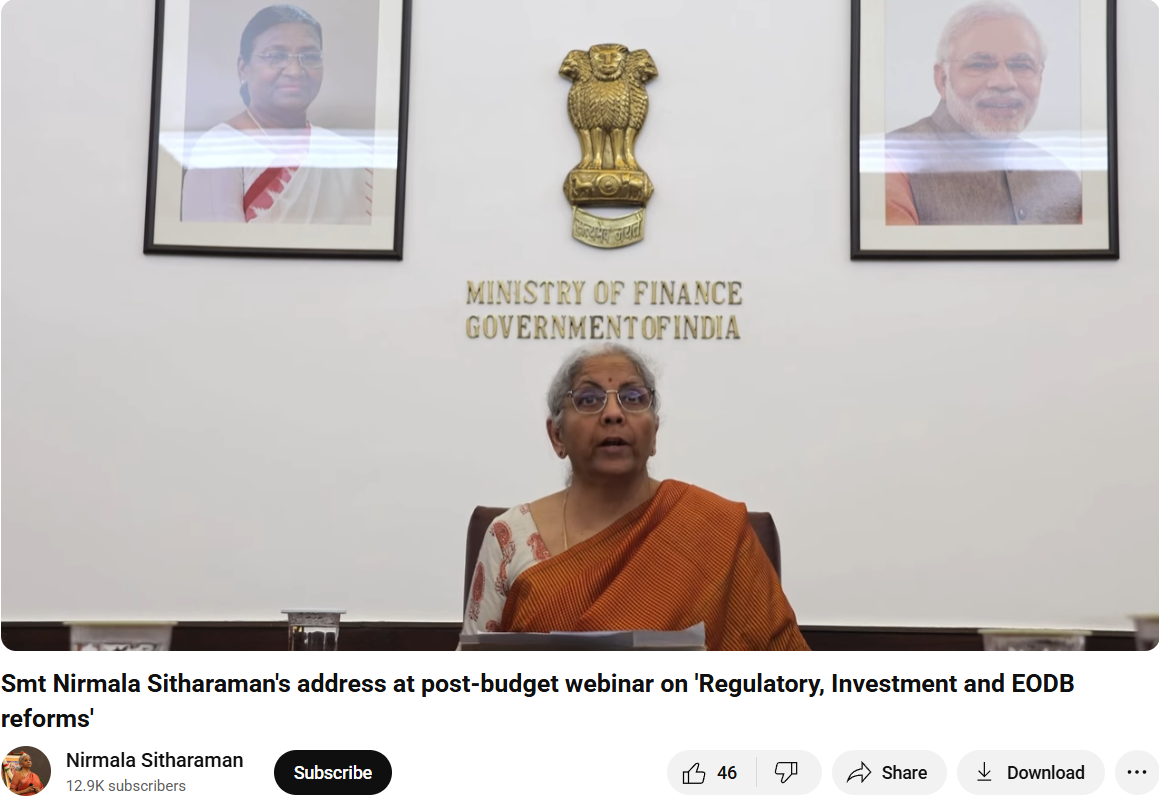
By doing a reverse image search from the key frames of the viral fake video we found an original YouTube clip of the Finance Minister of India delivering a speech on the webinar regarding 'Regulatory, Investment and EODB reforms'. Upon further research we have not found anything related to the viral investment scheme in the whole video.
The manipulated video has had an AI-generated voice/audio and scripted text injected into it to make it appear as if she has approved an investment platform.
The key to deepfakes is that they seem relatively realistic in their facial movement; however, if you look closely, you can see that there are mismatched lip-syncing and visual transitions that are out of the ordinary, and the results prove our point.
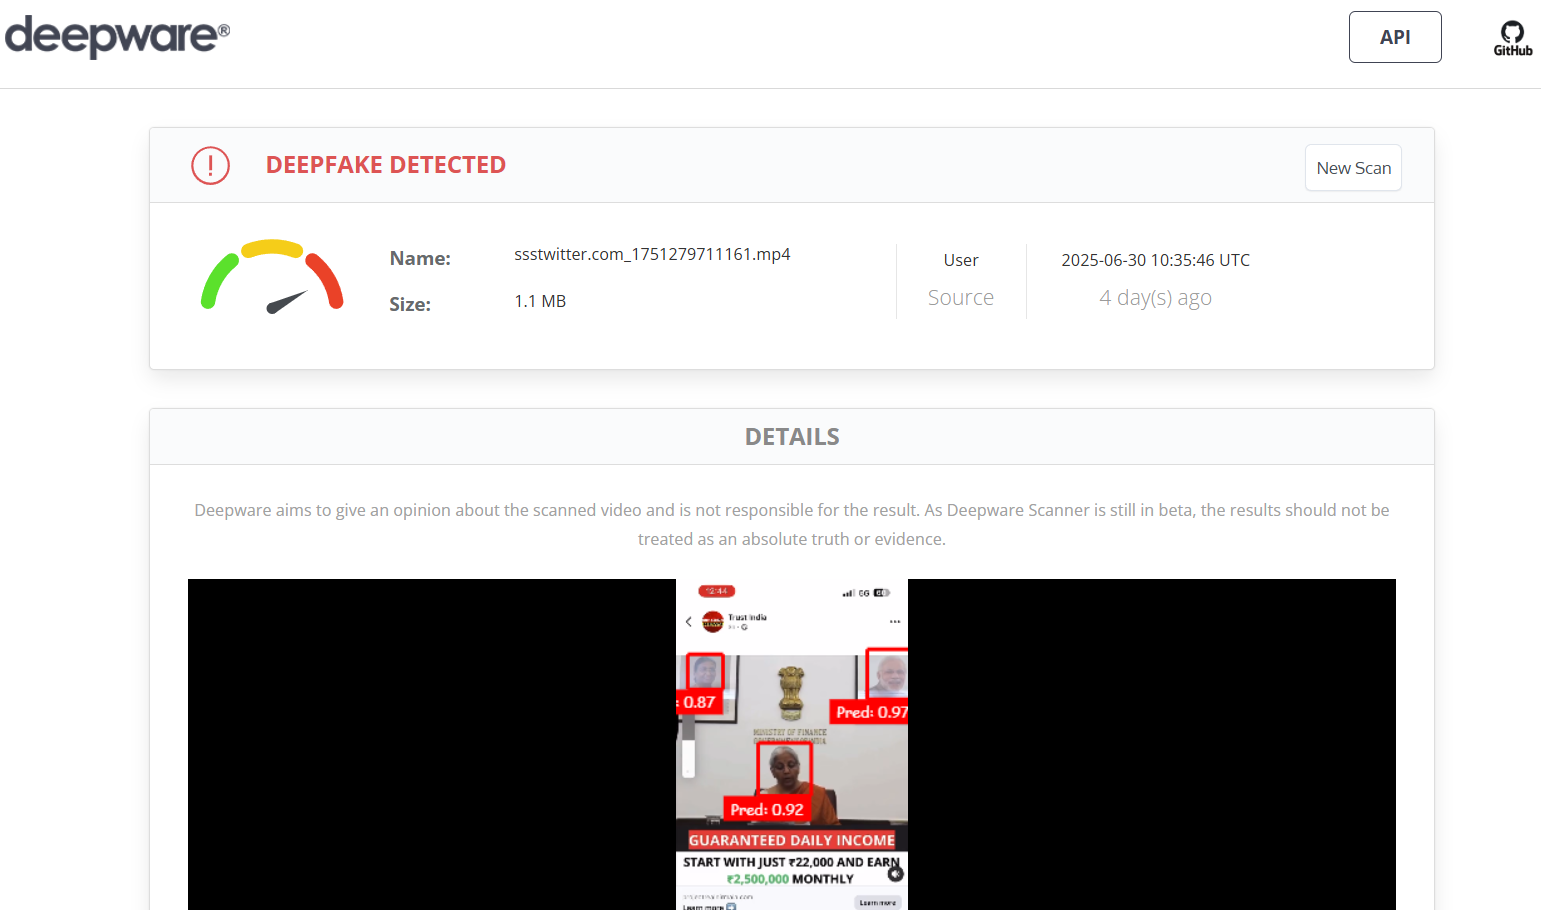
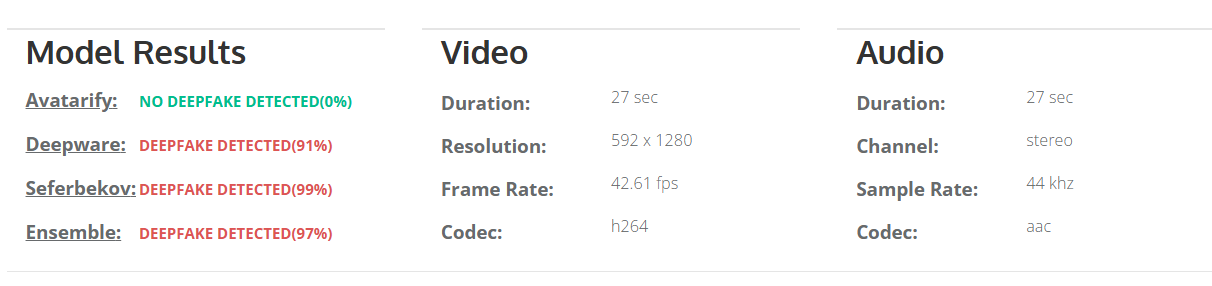
Also, there doesn't appear to be any acknowledgment of any such endorsement from a legitimate government website or a credible news outlet. This video is a fabricated piece of misinformation to attempt to scam the viewers by leveraging the image of a trusted public figure.
Conclusion:
The viral video showing the Finance Minister of India, Smt. Nirmala Sitharaman promoting an investment platform is fake and AI-generated. This is a clear case of deepfake misuse aimed at misleading the public and luring individuals into fraudulent schemes. Citizens are advised to exercise caution, verify any such claims through official government channels, and refrain from clicking on unknown investment links circulating on social media.
- Claim: Nirmala Sitharaman promoted an investment app in a viral video.
- Claimed On: Social Media
- Fact Check: False and Misleading

Related Blogs
Introduction
The digital landscape of the nation has reached a critical point in its evolution. The rapid adoption of technologies such as cloud computing, mobile payment systems, artificial intelligence, and smart infrastructure has led to a high degree of integration between digital systems and governance, commercial activity, and everyday life. As dependence on these systems continues to grow, a wide range of cyber threats has emerged that are complex, multi-layered, and closely interconnected. By 2026, cyber security threats directed at India are expected to include an increasing number of targeted, well-organised, and strategic cyber attacks. These attacks are likely to focus on exploiting the trust placed in technology, institutions, automation, and the fast pace of technological change.
1. Social Engineering 2.0: Hyper-Personalised AI Phishing & Mobile Banking Malware
Cybercriminals have moved from generalised methods to hyper-targeted attacks through AI-based psychological manipulation. In addition to social media profiles, data breaches, and digital/tracking footprints, the latest types of cybercrimes expected in 2026 will involve AI-based analysis of this information to create and increase the use of hyper-targeted phishing emails.
Phishing emails are capable of impersonating banks, employers, and even family members, with all the same regionally or culturally relevant tone, language, and context as would be done if these persons were sending the emails in person.
With malicious applications disguised as legitimate service apps, cybercriminals have the ability to intercept and capture One-Time Passwords (OTPs), hijack user sessions, and steal money from user accounts in a matter of minutes.
These types of attempts or attacks are successful not only because of their technical sophistication, but because they take advantage of human trust at scale, giving them an almost limitless reach into the financial systems of people around the world through their computers and mobile devices.
2. Cloud and Supply Chain Vulnerabilities
As Indian organisations increasingly migrate to cloud infrastructure, cloud misconfigurations are emerging as a major cybersecurity risk. Weak identity controls, exposed storage, and improper access management can allow attackers to bypass traditional network defences. Alongside this, supply chain attacks are expected to intensify in 2026.
In supply chain attacks, cybercriminals compromise a trusted software vendor or service provider to infiltrate multiple downstream organisations. Even entities with strong internal security can be affected through third-party dependencies. For India’s startup ecosystem, government digital platforms, and IT service providers, this presents a systemic risk. Strengthening vendor risk management and visibility across digital supply chains will be essential.
3. Threats to IoT and Critical Infrastructure
By implementing smart cities, digital utilities, and connected public services, IoT has opened itself up to increased levels of operational technology (OT) through India’s initiative. However, there is currently a lack of adequate security in the form of strong authentication, encryption, and update methods available on many IoT devices. By the year 2026, attackers are going to be able to exploit these vulnerabilities much more than they already are.
Cyberattacks on critical infrastructure such as energy, transportation, healthcare, and telecom systems have far-reaching consequences that extend well beyond data loss; they directly affect the provision of essential services, can damage public safety, and raise concerns over national security. Effectively securing critical infrastructure needs to involve dedicated security solutions to deal with the specific needs of critical infrastructure, in contrast to conventional IT security.
4. Hidden File Vectors and Stealth Payload Delivery
SVG File Abuse in Stealth Attacks
Cybercriminals are continually searching for ways to bypass security filters, and hidden file vectors are emerging as a preferred tactic. One such method involves the abuse of SVG (Scalable Vector Graphics) files. Although commonly perceived as harmless image files, SVGs can contain embedded scripts capable of executing malicious actions.
By 2026, SVG-based attacks are expected to be used in phishing emails, cloud file sharing, and messaging platforms. Because these files often bypass traditional antivirus and email security systems, they provide an effective stealth delivery mechanism. Indian organisations will need to rethink assumptions about “safe” file formats and strengthen deep content inspection capabilities.
5. Quantum-Era Cyber Risks and “Harvest Now, Decrypt Later” Attacks
Although practical quantum computers are still emerging, quantum-era cyber risks are already a present-day concern. Adversaries are believed to be intercepting and storing encrypted data now with the intention of decrypting it in the future once quantum capabilities mature—a strategy known as “harvest now, decrypt later.” This poses serious long-term confidentiality risks.
Recognising this threat, the United States took early action during the Biden administration through National Security Memorandum 10, which directed federal agencies to prepare for the transition to quantum-resistant cryptography. For India, similar foresight is essential, as sensitive government communications, financial data, health records, and intellectual property could otherwise be exposed retrospectively. Preparing for quantum-safe cryptography will therefore become a strategic priority in the coming years.
6. AI Trust Manipulation and Model Exploitation
Poisoning the Well – Direct Attacks on AI Models
As artificial intelligence systems are increasingly used for decision-making—ranging from fraud detection and credit scoring to surveillance and cybersecurity—attackers are shifting focus from systems to models themselves. “Poisoning the well” refers to attacks that manipulate training data, feedback mechanisms, or input environments to distort AI outputs.
In the context of India's rapidly growing digital ecosystem, compromised AI models can result in biased decisions, false security alerts or denying legitimate services. The big problem with these types of attacks is they may occur without triggering conventional security measures. Transparency, integrity and continuous monitoring of AI systems will be key to creating and maintaining stakeholder confidence in the decision-making process of the automated systems.
Recommendations
Despite the increasing sophistication of malicious cyber actors, India is entering this phase with a growing level of preparedness and institutional capacity. The country has strengthened its cyber security posture through dedicated mechanisms and relevant agencies such as the Indian Cyber Crime Coordination Centre, which play a central role in coordination, threat response, and capacity building. At the same time, sustained collaboration among government bodies, non-governmental organisations, technology companies, and academic institutions has expanded cyber security awareness, skill development, and research. These collective efforts have improved detection capabilities, response readiness, and public resilience, placing India in a stronger position to manage emerging cyber threats and adapt to the evolving digital environment.
Conclusion
By 2026, complexity, intelligence, and strategic intent will increasingly define cyber threats to the digital ecosystem. Cyber criminals are expected to use advanced methods of attack, including artificial intelligence assisted social engineering and the exploitation of cloud supply chain risks. As these threats evolve, adversaries may also experiment with quantum computing techniques and the manipulation of AI models to create new ways of influencing and disrupting digital systems. In response, the focus of cybersecurity is shifting from merely preventing breaches to actively protecting and restoring digital trust. While technical controls remain essential, they must be complemented by strong cybersecurity governance, adherence to regulatory standards, and sustained user education. As India continues its digital transformation, this period presents a valuable opportunity to invest proactively in cybersecurity resilience, enabling the country to safeguard citizens, institutions, and national interests with confidence in an increasingly complex and dynamic digital future.
References
- https://www.seqrite.com/india-cyber-threat-report-2026/
- https://www.uscsinstitute.org/cybersecurity-insights/blog/ai-powered-phishing-detection-and-prevention-strategies-for-2026
- https://www.expresscomputer.in/guest-blogs/cloud-security-risks-that-should-guide-leadership-in-2026/130849/
- https://www.hakunamatatatech.com/our-resources/blog/top-iot-challenges
- https://csrc.nist.gov/csrc/media/Presentations/2024/u-s-government-s-transition-to-pqc/images-media/presman-govt-transition-pqc2024.pdf
- https://www.cyber.nj.gov/Home/Components/News/News/1721/214

Executive Summary:
A video gone viral on Facebook claims Union Finance Minister Nirmala Sitharaman endorsed the government’s new investment project. The video has been widely shared. However, our research indicates that the video has been AI altered and is being used to spread misinformation.

Claim:
The claim in this video suggests that Finance Minister Nirmala Sitharaman is endorsing an automotive system that promises daily earnings of ₹15,00,000 with an initial investment of ₹21,000.
Fact Check:
To check the genuineness of the claim, we used the keyword search for “Nirmala Sitharaman investment program” but we haven’t found any investment related scheme. We observed that the lip movements appeared unnatural and did not align perfectly with the speech, leading us to suspect that the video may have been AI-manipulated.
When we reverse searched the video which led us to this DD News live-stream of Sitharaman’s press conference after presenting the Union Budget on February 1, 2025. Sitharaman never mentioned any investment or trading platform during the press conference, showing that the viral video was digitally altered. Technical analysis using Hive moderator further found that the viral clip is Manipulated by voice cloning.

Conclusion:
The viral video on social media shows Union Finance Minister Nirmala Sitharaman endorsing the government’s new investment project as completely voice cloned, manipulated and false. This highlights the risk of online manipulation, making it crucial to verify news with credible sources before sharing it. With the growing risk of AI-generated misinformation, promoting media literacy is essential in the fight against false information.
- Claim: Fake video falsely claims FM Nirmala Sitharaman endorsed an investment scheme.
- Claimed On: Social Media
- Fact Check: False and Misleading

Introduction
Digital Arrests are a form of scam that involves the digital restraint of individuals. These restraints can vary from restricting access to the account(s), and digital platforms, to implementing measures to prevent further digital activities or being restrained on video calling or being monitored through video calling. Typically, these scams target vulnerable individuals who are unfamiliar with digital fraud tactics, making them more susceptible to manipulation. These scams often target the victims on allegations of drug trafficking, money laundering, falsified documents, etc. These are serious crimes and these scammers scare the victim into thinking that either their identities were used to commit these crimes or they have committed these crimes. Recently there has been an uptick in the digital fraud scams in India highlighting the growing concerns.
The Legality of Digital Arrests in India
There is no legal provision for law enforcement to conduct ‘arrests’ via video calls or online monitoring. If you receive such calls, it is a clear scam. In fact, recently enacted new criminal laws do not provide for any provision for law enforcement agencies conducting a digital arrest. The law only provides for service of the summons and the proceedings in an electronic mode.
The Bhartiya Nagrik Suraksha Sanhita (BNSS), 2023 provides for the summons to be served electronically under section 63. The section defines the form of summons. It states that every summons served electronically shall be encrypted and bear the image of the seal of the Court or digital signature. Further, according to section 532 of the BNSS, the trial and proceedings may be held in electronic mode, by use of electronic communication or by the use of audio-video electronic means.
Modus Operandi
Under digital arrest scams, the scammer makes a connection via video calls (WhatsApp calls, skype, etc) with the victim over their alleged involvement in crimes (financial, drug trafficking, etc) in bogus charges. The victims are intimidated that the arrest will take place soon and till the time the arresting officers do not reach the victim they are to remain on the call and be under digital surveillance and not contact anyone during the ongoing investigation.
During this period, the scammers start collecting information from the victim to confirm their identity and create an atmosphere in which multiple senior officials are on the victim’s case and they are investigating the case thoroughly. By this time, the victim, scared out of their wits, sits through this arrest and it is then that the scammers posing as law enforcement officials make comments that they can avoid arrest by paying a certain amount of the fines to the accounts that they specify. This monitoring/ surveillance continues till the time the victim makes the transfers to the accounts provided by the scammers. These are the common manipulation tactics used by scammers in digital arrest fraud.
Recent Cyber Arrest Cases
- Recently a 35-year-old NBCC official was duped of Rs 55 lakh in a 'digital arrest' scam. Posing as customs officials, fraudsters claimed her details were linked to intercepted illegal items and a pending arrest. They kept her on video calls, convincing her to transfer Rs 55 lakh to avoid money laundering charges. After the transfer, the scammers vanished. A police investigation traced the funds to a fake company, leading to the arrest of suspects.
- Another recent case involved a neurologist who was duped Rs 2.81 crores in a ‘digital arrest’ scam. Fraudsters claimed her phone number and Aadhaar was linked to accounts transferring funds to an Individual. Under pressure, she was convinced to undergo “verification” and made multiple transactions over two days. The scammers threatened legal consequences for money laundering if she didn’t comply. Now a police investigation is ongoing, and her immense financial loss highlights the severity of this cybercrime.
- One another case took place where the victim was duped of Rs 7.67 crores in a prolonged ‘digital arrest’ scam over three months. Fraudsters posing as TRAI officials claimed complaints against her phone number and threatened to suspend it, alleging illegal use of another number linked to her Aadhaar. Pressured and manipulated through video calls, the victim was coerced into transferring large sums, even taking an Rs 80 lakh loan. The case is under investigation as authorities pursue the cybercriminals behind the massive fraud.
Best Practices
- Do not panic when you get any calls where sudden unexpected news is shared with you. Scammers thrive on the panic that they create.
- Do not share personal details such as Aadhaar number, PAN number etc with unknown or suspect entities. Be cautious of your personal and financial information such as credit card numbers, OTPs, or any other passwords with anyone.
- If individuals contact, claiming to be government officials, always verify their identities by contacting the entity through the proper channels.
- Report and block any fraudulent communications that are received and mark them as Spam. This would further inform other users if they see the caller ID being marked as fraud or spam.
- If you have been defrauded then report about the same to the authorities so that action can be taken and authorities can arrest the fraudsters.
- Do not transfer any money as part of ‘fines’ or ‘dues’ to the accounts that these calls or messages link to.
- In case of any threat, issue or discrepancy, file a complaint at cybercrime.gov.in or helpline number 1930. You can also seek assistance from the CyberPeace helpline at +91 9570000066.
References:
- https://www.cyberpeace.org/resources/blogs/digital-arrest-fraud
- https://www.business-standard.com/india-news/what-is-digital-house-arrest-find-out-how-to-avoid-this-new-scam-124052400799_1.html
- https://www.the420.in/ias-ips-officers-major-generals-doctors-and-professors-fall-victim-to-digital-arrest-losing-crores-stay-alert-read-5-real-cases-inside/
- https://indianexpress.com/article/cities/delhi/senior-nbcc-official-duped-in-case-of-digital-arrest-3-arrested-delhi-police-9588418/#:~:text=Of%20the%20duped%20amount%2C%20Rs,a%20Delhi%20police%20officer%20said (case study 1)
- https://timesofindia.indiatimes.com/city/lucknow/lucknow-sgpgims-professor-duped-of-rs-2-81-crore-in-digital-arrest-scam/articleshow/112521530.cms (case study 2)
- https://timesofindia.indiatimes.com/city/jaipur/bits-prof-duped-of-7-67cr-cops-want-cbi-probe-in-case/articleshow/109514200.cms (case study 3)
