
#Factcheck-Viral Image of Men Riding an Elephant Next to a Tiger in Bihar is Misleading
Executive Summary:
A post on X (formerly Twitter) featuring an image that has been widely shared with misleading captions, claiming to show men riding an elephant next to a tiger in Bihar, India. This post has sparked both fascination and skepticism on social media. However, our investigation has revealed that the image is misleading. It is not a recent photograph; rather, it is a photo of an incident from 2011. Always verify claims before sharing.

Claims:
An image purporting to depict men riding an elephant next to a tiger in Bihar has gone viral, implying that this astonishing event truly took place.

Fact Check:
After investigation of the viral image using Reverse Image Search shows that it comes from an older video. The footage shows a tiger that was shot after it became a man-eater by forest guard. The tiger killed six people and caused panic in local villages in the Ramnagar division of Uttarakhand in January, 2011.

Before sharing viral posts, take a brief moment to verify the facts. Misinformation spreads quickly and it’s far better to rely on trusted fact-checking sources.
Conclusion:
The claim that men rode an elephant alongside a tiger in Bihar is false. The photo presented as recent actually originates from the past and does not depict a current event. Social media users should exercise caution and verify sensational claims before sharing them.
- Claim: The video shows people casually interacting with a tiger in Bihar
- Claimed On:Instagram and X (Formerly Known As Twitter)
- Fact Check: False and Misleading

Related Blogs

Executive Summary:
QakBot, a particular kind of banking trojan virus, is capable of stealing personal data, banking passwords, and session data from a user's computer. Since its first discovery in 2009, Qakbot has had substantial modifications.
C2 Server commands infected devices and receives stolen data, which is essentially the brain behind Qakbot's operations.Qakbot employs PEDLL (Communication Files), a malicious program, to interact with the server in order to accomplish its main goals. Sensitive data, including passwords or personal information, is taken from the victims and sent to the C2 server. Referrer files start the main line of communication between Qakbot and the C2 server, such as phishing papers or malware droppers. WHOIS data includes registration details for this server, which helps to identify its ownership or place of origin.
This report specifically focuses on the C2 server infrastructure located in India, shedding light on its architecture, communication patterns, and threat landscape.
Introduction:
QakBot is also known as Pinkslipbot, QuakBot, and QBot, capable of stealing personal data, banking passwords, and session data from a user's computer. Malware is bad since it spreads very quickly to other networks, affecting them like a worm.,It employs contemporary methods like web injection to eavesdrop on customer online banking interactions. Qakbot is a member of a kind of malware that has robust persistence techniques, which are said to be the most advanced in order to gain access to compromised computers for extended periods of time.
Technical Analysis:
The following IP addresses have been confirmed as active C2 servers supporting Qbot malware activity:

Sample IP's
- 123.201.40[.]112
- 117.198.151[.]182
- 103.250.38[.]115
- 49.33.237[.]65
- 202.134.178[.]157
- 124.123.42[.]115
- 115.96.64[.]9
- 123.201.44[.]86
- 117.202.161[.]73
- 136.232.254[.]46
These servers have been operational in the past 14 days (report created in the month of Nov) and are being leveraged to perpetuate malicious activities globally.
URL/IP: 123.201.40[.]112

- inetnum: 123.201.32[.]0 - 123.201.47[.]255
- netname: YOUTELE
- descr: YOU Telecom India Pvt Ltd
- country: IN
- admin-c: HA348-AP
- tech-c: NI23-AP
- status: ASSIGNED NON-PORTABLE
- mnt-by: MAINT-IN-YOU
- last-modified: 2022-08-16T06:43:19Z
- mnt-irt: IRT-IN-YOU
- source: APNIC
- irt: IRT-IN-YOU
- address: YOU Broadband India Limited
- address: 2nd Floor, Millennium Arcade
- address: Opp. Samarth Park, Adajan-Hazira Road
- address: Surat-395009,Gujarat
- address: India
- e-mail: abuse@youbroadband.co.in
- abuse-mailbox: abuse@youbroadband.co.in
- admin-c: HA348-AP
- tech-c: NI23-AP
- auth: # Filtered
- mnt-by: MAINT-IN-YOU
- last-modified: 2022-08-08T10:30:51Z
- source: APNIC
- person: Harindra Akbari
- nic-hdl: HA348-AP
- e-mail: harindra.akbari@youbroadband.co.in
- address: YOU Broadband India Limited
- address: 2nd Floor, Millennium Arcade
- address: Opp. Samarth Park, Adajan-Hazira Road
- address: Surat-395009,Gujarat
- address: India
- phone: +91-261-7113400
- fax-no: +91-261-2789501
- country: IN
- mnt-by: MAINT-IN-YOU
- last-modified: 2022-08-10T11:01:47Z
- source: APNIC
- person: NOC IQARA
- nic-hdl: NI23-AP
- e-mail: network@youbroadband.co.in
- address: YOU Broadband India Limited
- address: 2nd Floor, Millennium Arcade
- address: Opp. Samarth Park, Adajan-Hazira Road
- address: Surat-395009,Gujarat
- address: India
- phone: +91-261-7113400
- fax-no: +91-261-2789501
- country: IN
- mnt-by: MAINT-IN-YOU
- last-modified: 2022-08-08T10:18:09Z
- source: APNIC
- route: 123.201.40.0/24
- descr: YOU Broadband & Cable India Ltd.
- origin: AS18207
- mnt-lower: MAINT-IN-YOU
- mnt-routes: MAINT-IN-YOU
- mnt-by: MAINT-IN-YOU
- last-modified: 2012-01-25T11:25:55Z
- source: APNIC


IP 123.201.40[.]112 uses the requested URL-path to make a GET request on the IP-address at port 80. "NOT RESPONDED" is the response status code for the request "C:\PROGRAM FILES GOOGLE CHROME APPLICATION CHROME.EXE" that was started by the process.
Programs that retrieve their server data using a GET request are considered legitimate. The Google Chrome browser, a fully functional application widely used for web browsing, was used to make the actual request. It asks to get access to the server with IP 123.201.40[.]112 in order to collect its data and other resources.
Malware uses GET requests to retrieve more commands or to send data back to the command and control servers. In this instance, it may be an attack server making the request to a known IP address with a known port number. Since the server has not replied to the request, the response status "NOT RESPONDED" may indicate that the activity was carried out with malicious intent.
This graph illustrates how the Qakbot virus operates and interacts with its C2 server, located in India and with the IP address 123.201.40[.]112.

Impact
Qbot is a kind of malware that is typically distributed through hacked websites, malicious email attachments, and phishing operations. It targets private user information, including corporate logins or banking passwords. The deployment of ransomware: Payloads from organizations such as ProLock and Egregor ransomware are delivered by Qbot, a predecessor. Network Vulnerability: Within corporate networks, compromised systems will act as gateways for more lateral movement.
Proposed Recommendations for Mitigation
- Quick Action: To stop any incoming or outgoing traffic, the discovered IP addresses will be added to intrusion detection/prevention systems and firewalls.
- Network monitoring: Examining network log information for any attempts to get in touch with these IPs
- Email security: Give permission for anti-phishing programs.
- Endpoint Protection: To identify and stop Qbot infestations, update antivirus definitions.,Install tools for endpoint detection and response.
- Patch management: To reduce vulnerabilities that Qbot exploits, update all operating systems and software on a regular basis.
- Incident Response: Immediately isolate compromised computers.
- Awareness: Dissemination of this information to block the IP addresses of active C2 servers supporting Qbot malware activity has to be carried out.
Conclusion:
The discovery of these C2 servers reveals the growing danger scenario that Indian networks must contend with. To protect its infrastructure from future abuse, organizations are urged to act quickly and put the aforementioned precautions into place.
Reference:
- Threat Intelligence - ANY.RUN
- https://www.virustotal.com/gui
- https://www.virustotal.com/gui/ip-address/123.201.40.112/relations

What are Decentralised Autonomous Organizations (DAOs)?
A Decentralised Autonomous Organisation or a DAO, is a unique take on democracy on the blockchain. It is a set of rules encoded into a self-executing contract (also known as a smart contract) that operates autonomously on a blockchain system. A DAO imitates a traditional company, although, in its more literal sense, it is a contractually created entity. In theory, DAOs have no centralised authority in making decisions for the system; it is a communally run system whereby all decisions (be it for internal governance or for the development of the blockchain system) are voted upon by the community members. DAOs are primarily characterised by a decentralised form of operation, where there is no one entity, group or individual running the system. They are self-sustaining entities, having their own currency, economy and even governance, that do not depend on a group of individuals to operate. Blockchain systems, especially DAOs are characterised by pure autonomy created to evade external coercion or manipulation from sovereign powers. DAOs follow a mutually created, agreed set of rules created by the community, that dictates all actions, activities, and participation in the system’s governance. There may also be provisions that regulate the decision-making power of the community.
Ethereum’s DAO’s White Paper described DAO as “The first implementation of a [DAO Entity] code to automate organisational governance and decision making.” Can be used by individuals working together collaboratively outside of a traditional corporate form. It can also be used by a registered corporate entity to automate formal governance rules contained in corporate bylaws or imposed by law.” The referred white paper proposes an entity that would use smart contracts to solve governance issues inherent in traditional corporations. DAOs attempt to redesign corporate governance with blockchain such that contractual terms are “formalised, automated and enforced using software.”
Cybersecurity threats under DAOs
While DAOs offer increased transparency and efficiency, they are not immune to cybersecurity threats. Cybersecurity risks in DAO, primarily in governance, stem from vulnerabilities in the underlying blockchain technology and the DAO's smart contracts. Smart contract exploits, code vulnerabilities, and weaknesses in the underlying blockchain protocol can be exploited by malicious actors, leading to unauthorised access, fund manipulations, or disruptions in the governance process. Additionally, DAOs may face challenges related to phishing attacks, where individuals are tricked into revealing sensitive information, such as private keys, compromising the integrity of the governance structure. As DAOs continue to evolve, addressing and mitigating cybersecurity threats is crucial to ensuring the trust and reliability of decentralised governance mechanisms.
Centralisation/Concentration of Power
DAOs today actively try to leverage on-chain governance, where any governance votes or transactions are directly taken on the blockchain. But such governance is often plutocratic in nature, where the wealthy hold influences, rather than democracies, since those who possess the requisite number of tokens are only allowed to vote and each token staked implies that many numbers of votes emerge from the same individual. This concentration of power in the hands of “whales” often creates disadvantages for the newer entrants into the system who may have an in-depth background but lack the funds to cast a vote. Voting, presently in the blockchain sphere, lacks the requisite concept of “one man, one vote” which is critical in democratic societies.
Smart contract vulnerabilities and external threats
Smart contracts, self-executing pieces of code on a blockchain, are integral to decentralised applications and platforms. Despite their potential, smart contracts are susceptible to various vulnerabilities such as coding errors, where mistakes in the code can lead to funds being locked or released erroneously. Some of them have been mentioned as follows;
Smart Contracts are most prone to re-entrance attacks whereby an untrusted external code is allowed to be executed in a smart contract. This scenario occurs when a smart contract invokes an external contract, and the external contract subsequently re-invokes the initial contract. This sequence of events can lead to an infinite loop, and a reentrancy attack is a tactic exploiting this vulnerability in a smart contract. It enables an attacker to repeatedly invoke a function within the contract, potentially creating an endless loop and gaining unauthorised access to funds.
Additionally, smart contracts are also prone to oracle problems. Oracles refer to third-party services or mechanisms that provide smart contracts with real-world data. Since smart contracts on blockchain networks operate in a decentralised, isolated environment, they do not have direct access to external information, such as market prices, weather conditions, or sports scores. Oracles bridge this gap by acting as intermediaries, fetching and delivering off-chain data to smart contracts, enabling them to execute based on real-world conditions. The oracle problem within blockchain pertains to the difficulty of securely incorporating external data into smart contracts. The reliability of external data poses a potential vulnerability, as oracles may be manipulated or provide inaccurate information. This challenge jeopardises the credibility of blockchain applications that rely on precise and timely external data.
Sybil Attack: A Sybil attack involves a single node managing multiple active fake identities, known as Sybil identities, concurrently within a peer-to-peer network. The objective of such an attack is to weaken the authority or influence within a trustworthy system by acquiring the majority of control in the network. The fake identities are utilised to establish and exert this influence. A successful Sybil attack allows threat actors to perform unauthorised actions in the system.
Distributed Denial of Service Attacks: A Distributed Denial of Service (DDoS) attack is a malicious attempt to disrupt the regular functioning of a network, service, or website by overwhelming it with a flood of traffic. In a typical DDoS attack, multiple compromised computers or devices, often part of a botnet (a network of infected machines controlled by a single entity), are used to generate a massive volume of requests or data traffic. The targeted system becomes unable to respond to legitimate user requests due to the excessive traffic, leading to a denial of service.
Conclusion
Decentralised Autonomous Organisations (DAOs) represent a pioneering approach to governance on the blockchain, relying on smart contracts and community-driven decision-making. Despite their potential for increased transparency and efficiency, DAOs are not immune to cybersecurity threats. Vulnerabilities in smart contracts, such as reentrancy attacks and oracle problems, pose significant risks, and the concentration of voting power among wealthy token holders raises concerns about democratic principles. As DAOs continue to evolve, addressing these challenges is essential to ensuring the resilience and trustworthiness of decentralised governance mechanisms. Efforts to enhance security measures, promote inclusivity, and refine governance models will be crucial in establishing DAOs as robust and reliable entities in the broader landscape of blockchain technology.
References:
https://www.imperva.com/learn/application-security/sybil-attack/
https://www.linkedin.com/posts/satish-kulkarni-bb96193_what-are-cybersecurity-risk-to-dao-and-how-activity-7048286955645677568-B3pV/ https://www.geeksforgeeks.org/what-is-ddosdistributed-denial-of-service/ Report of Investigation Pursuant to Section 21 (a) of the Securities Exchange Act of 1934: The DAO, Securities and Exchange Board, Release No. 81207/ July 25, 2017
https://www.sec.gov/litigation/investreport/34-81207.pdf https://www.legalserviceindia.com/legal/article-10921-blockchain-based-decentralized-autonomous-organizations-daos-.html
Executive Summary
A post is going viral across various social media platforms claiming that the World Health Organization (WHO) has issued a warning over the issue of adulteration in food products. According to the claim, WHO has warned that milk adulteration is continuously increasing in India and if it continues, 87 percent of Indians will suffer from cancer by 2035. CyberPeace Research Wing’s research found that the viral claim has been circulating on social media for several years. Earlier, the same claim was shared with the year changed to 2025, stating that 87 percent of Indians would suffer from cancer by that year. Now, the year has been changed from 2025 to 2035 and the claim is being circulated again. WHO has repeatedly denied this claim and termed it fake news.
Claim:
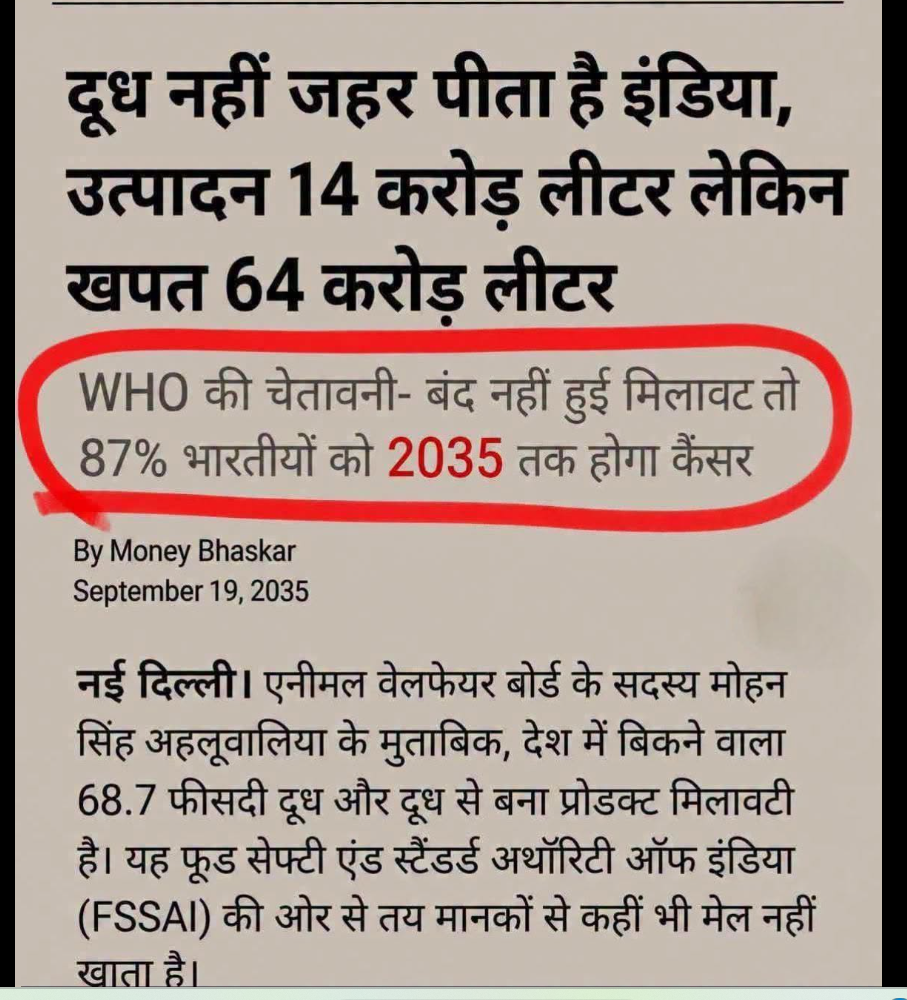
A Facebook user named ‘Vikalp Kuchamancity’ shared the viral post on August 3, 2026, with a caption claiming, “India produces 14 crore litres of milk, but consumption is 64 crore litres. Where does this extra milk come from? WHO has warned that if adulteration is not stopped, 87 percent of Indians may suffer from cancer by 2035.”
https://www.facebook.com/photo/?fbid=968660469565357&set=a.109816988783047
Fact Check:
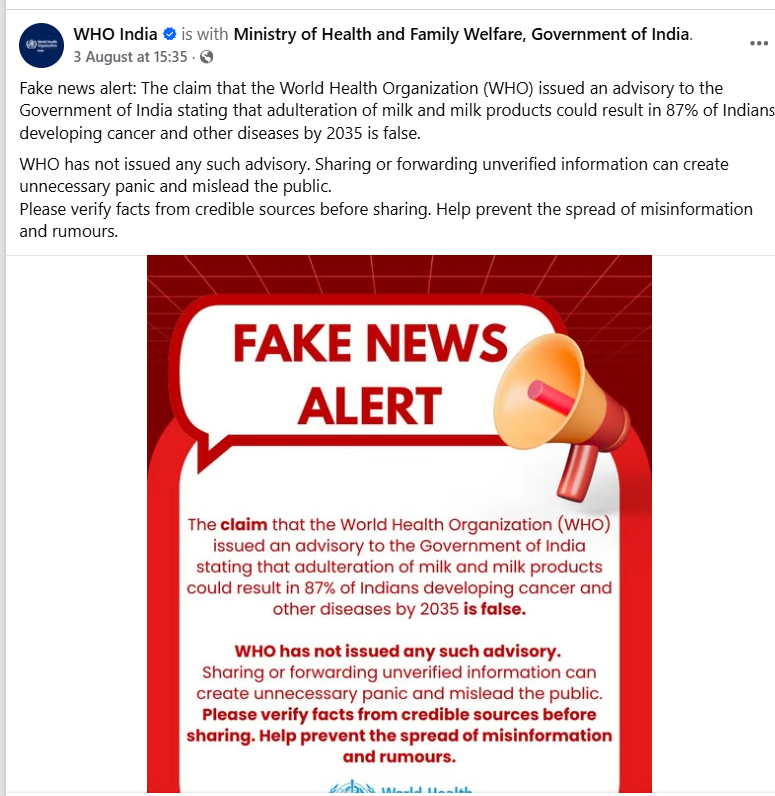
While examining the viral post, we noticed that the report displayed in the image carries the date September 19, 2035, even though the current year is 2026. This raised initial doubts about the authenticity of the claim.To investigate further, we conducted a Google search using relevant keywords. During the search, we found a post from the official Facebook page of WHO India, shared on August 3, 2026. The post denied the viral claim and stated that it is false that WHO issued any advisory to the Indian government warning that adulteration in milk and dairy products could lead to cancer and other diseases among 87 percent of Indians by 2035. WHO clarified that no such advisory has been issued.
WHO India Facebook link:
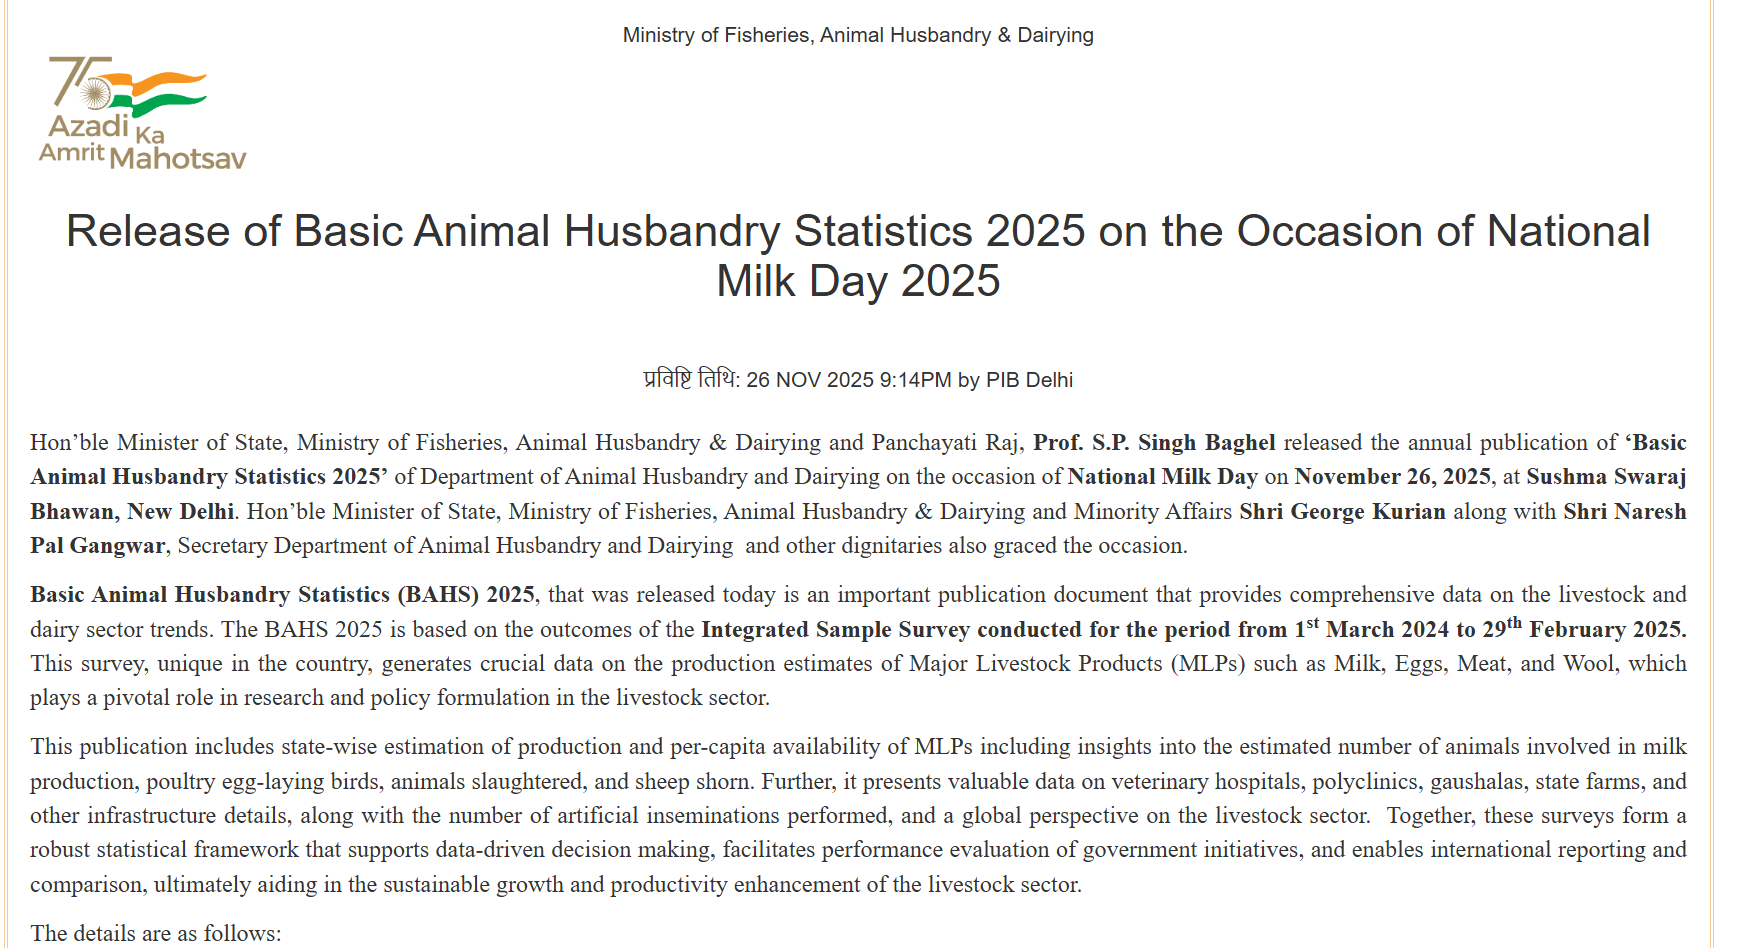
According to data mentioned in a press release issued by the Government of India on November 26, 2025, the country’s total milk production was estimated at 247.87 million tonnes in 2024-25, compared to 239.30 million tonnes in 2023-24. The per capita availability of milk increased from 319 grams per day in 2014-15 to 485 grams per day in 2024-25. The top five milk-producing states are Uttar Pradesh (15.66%), Rajasthan (14.82%), Madhya Pradesh (9.12%), Gujarat (7.78%), and Maharashtra (6.71%). Together, these states contribute 54.09% of India’s total milk production.
https://www.pib.gov.in/PressReleasePage.aspx?PRID=2195049®=3&lang=2
Conclusion:
The research confirmed that there is no evidence of any WHO warning stating that 87 percent of Indians could develop cancer by 2035 due to milk adulteration. WHO has clarified that it has not issued any such advisory. The viral claim is a recycled false claim that has been repeatedly circulated with changed dates.
