
#FactCheck-Old Video From 2023 Palestine Protest Falsely Linked to Ongoing NEET Paper Leak Protest.
Executive Summary
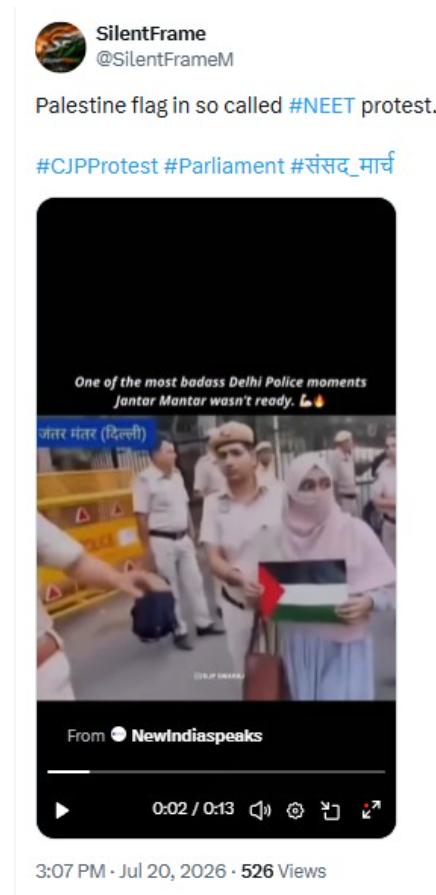
A video showing police personnel allegedly snatching and tearing a Palestine flag from a woman protester is being widely shared on social media. Users are claiming that the video was recorded during the ongoing CJP-led protest at Jantar Mantar demanding the resignation of the Union Education Minister over the NEET paper leak. CyberPeace Research Wing ’s research found that the viral claim is misleading. The video is not related to the ongoing CJP-led protest at Jantar Mantar over the NEET paper leak. The footage dates back to 2023 and is being falsely linked to a recent protest.
Claim:
A social media user shared the viral video claiming that a woman protester arrived at the NEET paper leak protest carrying a Palestine flag.
https://x.com/SilentFrameM/status/2079138742795939907
Fact Check:
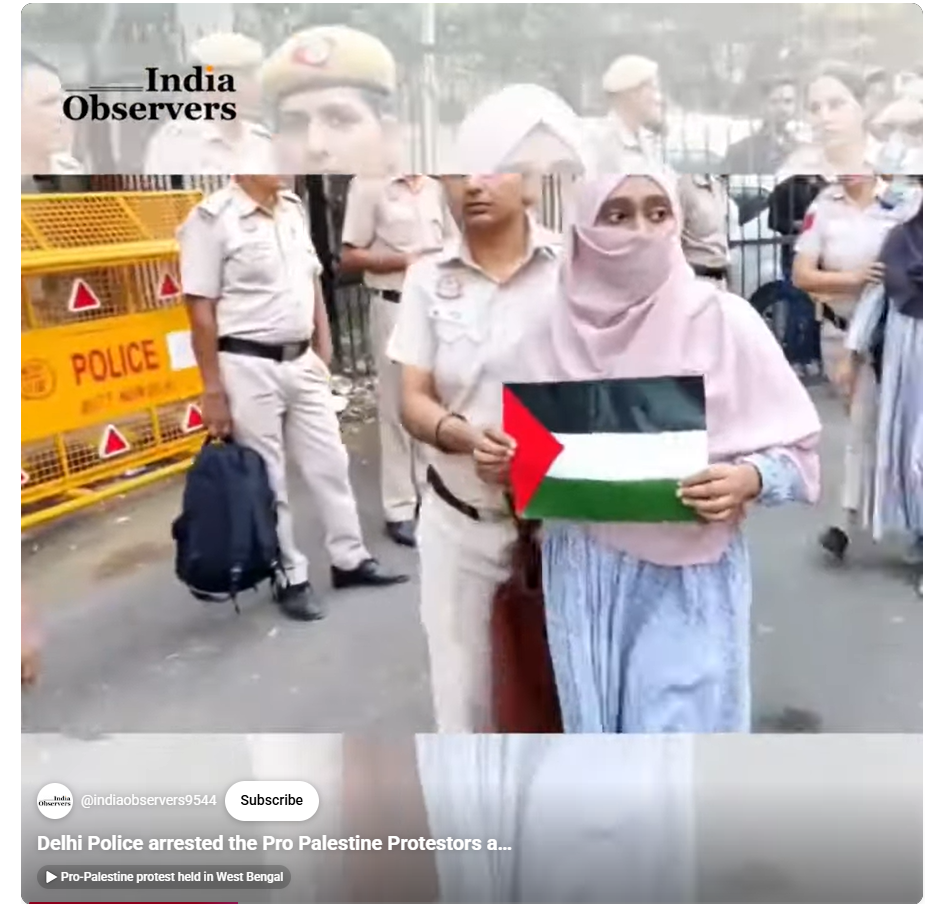
A reverse image search of keyframes from the viral video led us to a YouTube video uploaded by Indian Observer on October 30, 2023, featuring the same visuals. The video description identified the footage as being from a pro-Palestine demonstration held at Jantar Mantar in solidarity with Palestinians.
https://www.youtube.com/shorts/_JhJyZ-Djyw
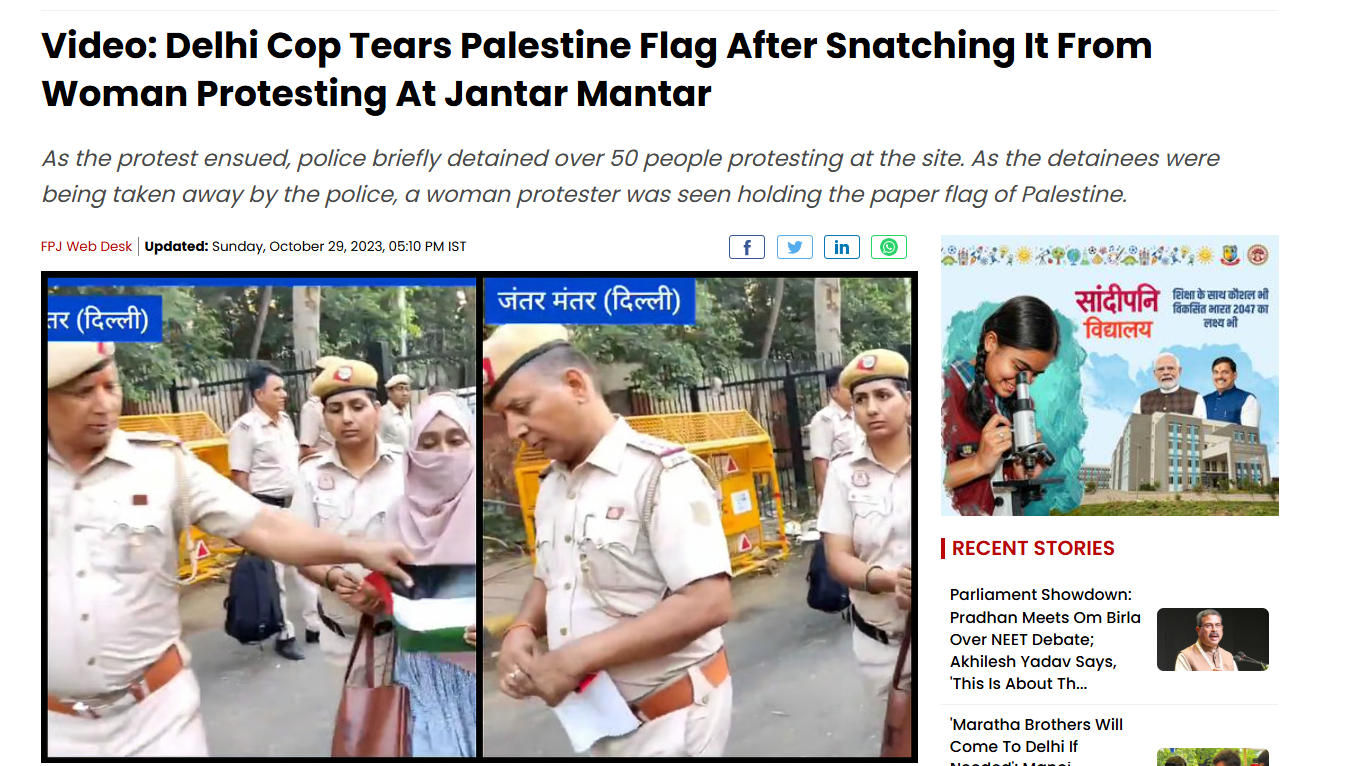
We also found an October 2023 report by Free Press Journal carrying the same visuals. According to the report, several students and civil society members had gathered at Jantar Mantar to protest Israel’s military actions in the Gaza Strip and express solidarity with Palestine. During the protest, Delhi Police briefly detained more than 50 demonstrators. As the detainees were being escorted away, a woman carrying a paper Palestine flag was seen confronting police personnel, who allegedly snatched and tore the flag.
Conclusion:
CyberPeace Research Wing ’s fact check found the viral claim to be misleading. The video is not from the ongoing CJP-led NEET paper leak protest at Jantar Mantar. The footage is from a pro-Palestine demonstration held in October 2023 and has been falsely shared as a recent video from the ongoing protests.

Related Blogs

Executive Summary:
We have identified a post addressing a scam email that falsely claims to offer a download link for an e-PAN Card. This deceptive email is designed to mislead recipients into disclosing sensitive financial information by impersonating official communication from Income Tax Department authorities. Our report aims to raise awareness about this fraudulent scheme and emphasize the importance of safeguarding personal data against such cyber threats.

Claim:
Scammers are sending fake emails, asking people to download their e-PAN cards. These emails pretend to be from government authorities like the Income Tax Department and contain harmful links that can steal personal information or infect devices with malware.
Fact Check:
Through our research, we have found that scammers are sending fake emails, posing as the Income Tax Department, to trick users into downloading e-PAN cards from unofficial links. These emails contain malicious links that can lead to phishing attacks or malware infections. Genuine e-PAN services are only available through official platforms such as the Income Tax Department's website (www.incometaxindia.gov.in) and the NSDL/UTIITSL portals. Despite repeated warnings, many individuals still fall victim to such scams. To combat this, the Income Tax Department has a dedicated page for reporting phishing attempts: Report Phishing - Income Tax India. It is crucial for users to stay cautious, verify email authenticity, and avoid clicking on suspicious links to protect their personal information.

Conclusion:
The emails currently in circulation claiming to provide e-PAN card downloads are fraudulent and should not be trusted. These deceptive messages often impersonate government authorities and contain malicious links that can result in identity theft or financial fraud. Clicking on such links may compromise sensitive personal information, putting individuals at serious risk. To ensure security, users are strongly advised to verify any such communication directly through official government websites and avoid engaging with unverified sources. Additionally, any phishing attempts should be reported to the Income Tax Department and also to the National Cyber Crime Reporting Portal to help prevent the spread of such scams. Staying vigilant and exercising caution when handling unsolicited emails is crucial in safeguarding personal and financial data.
- Claim: Fake emails claim to offer e-PAN card downloads.
- Claimed On: Social Media
- Fact Check: False and Misleading
Introduction
Web applications are essential in various sectors, including online shopping, social networks, banking, and healthcare systems. However, they also pose numerous security threats, including Cross-Site Scripting (XSS), a client-side code injection vulnerability. XSS attacks exploit the trust relationship between users and websites, allowing them to change web content, steal private information, hijack sessions, and gain full control of user accounts without breaking into the core server. This vulnerability is part of the OWASP Top 10 Web Application Security Risks.
What is Cross-Site Scripting (XSS)?
An XSS attack occurs when an attacker injects client-side scripts into web pages viewed by other users. When users visit the affected pages, their browsers naively execute the inserted scripts. The exploit takes advantage of web applications that allow users to submit content without properly sanitising inputs or encoding outputs. These scripts can cause a wide range of damage, including but not limited to stealing session cookies for session hijacking, redirecting users to malicious sites, logging keystrokes to capture credentials, and altering the DOM to display fake or phishing content.
How Does XSS Work?
- Injection: A malicious user submits code through a website input, like a comment or form.
- Execution: The submitted code runs automatically in the browsers of other users who view the page.
- Exploitation:The attacker can steal session information, capture credentials, redirect users, or modify the page content.
The fundamental cause behind the XSS vulnerabilities is the application of:
- Accepting trusted input from the users.
- After users' input, web pages have the strings embedded without any sanitisation.
- Not abiding by security policies like Content Security Policy (CSP).
With such vulnerabilities, attackers can generate malicious payloads like: <script>alert('XSS');</script>
This code might seem simple, but its execution provides the attacker with the possibility to do the following:
- Copy session tokens through hidden HTTP requests.
- From attacker-controlled domains, load attacker scripts.
- Change the DOM structure to show fake login forms for phishing.
Types of XSS Attacks: XSS (Cross-Site Scripting) attacks can occur in three main variations:
- Stored XSS: This type of attack occurs when an attacker injects an administered payload into the database or a message board. The script then runs whenever a user visits the affected board.
- Reflected XSS: In this attack, the danger lies in a parameter of the URL. Its social engineering techniques are attacks, in which it requires tricking people to click on a specially designed link. For example:
- DOM-Based XSS: This technique injects anything harmful without the need for server-side scripts, in contrast to other approaches. It targets JavaScript client-side scripts such as `document.write` and `innerHTML`. Without carrying out any safety checks, these scripts will alter the page's look (DOM stands for Document Object Model). If the hash is given a malicious string, it is run directly within the browser.
What Makes XSS a Threat?
A Cross-Site Scripting attack is only a primary attack vector, and can lead to significant damage that includes the following:
- Statement Hijacking. This uses scripts to steal cookies, which are then used to pose as authorized users.
- Theft of Credentials. Users’ passwords and usernames are wrenched from keystroke trackers.
- Phishing. Users are prompted with deceitful login forms that are used to capture sensitive details.
- Website Vandalism. Modified website material lowers the esteem of the brand.
- Monetary and Legal Consequences. There are compounding effects to GDPR and DPDP Act compliance in case of Data breaches, which incur penalties and fines.
Incidents in the Real World
In 2021, an XSS Stored attack occurred on a famous e-commerce platform eBay, through their product review system. The malicious JavaScript code was set to trigger every time an infected product page was accessed by customers. This caused a lot of problems, including account takeovers, unauthorised purchases, and damage to the company’s reputation. This example further worsens the fact that even reputed platforms can be targeted by XSS attacks.
How to Prevent XSS?
Addressing XSS vulnerabilities demands attention to detail and coordinated efforts across functions, as illustrated in the steps below:
Input Validation and Output Encoding:
- Ensure input validation is in place on the client and server.
- Perform output encoding relative to context: HTML: <, >, &.
- JavaScript: Escape quotes and slashes
Content Security Policy (CSP): CSP allows scripts to be executed only from the verified sources, which helps diminish the odds of harmful scripts running on your website. For example, the Header in the code could look to some degree like this: Content-Security-Policy: script-src 'self';
Unsafe APIs should be dodged: Avoid the use of document.write(), innerHTML, and eval(), and make sure to use:
- TextContent for inserting text.
- CreateElement() and other DOM creation methods for structured content.
Secure Cookies: Apply the HttpOnly and Secure cookie flags to block JavaScript access.
Framework Protections: Use the protective features in frameworks such as:
- React, which escapes data embedded in JSX automatically.
- Angular, which uses context-aware sanitisation.
Periodic Security Assessment:
- Use DAST tools to test the security posture of an application.
- Perform thorough penetration testing and security-oriented code reviews.
Best Practices for Developers: Assume a Secure Development Lifecycle (SDLC) integrating XSS stoppage at each point.
- Educate developers on OWASP secure coding guidelines.
- Automate scanning for vulnerabilities in CI/CD pipelines.
Conclusion:
To reduce the potential danger of XSS, both developers and companies must be diligent in their safety initiatives, ranging from using Content Security Policies (CSP) to verifying user input. Web applications can shield consumers and the company from the subtle but long-lasting threat of Cross-Site Scripting if security controls are implemented during the web application development stage and regular vulnerability scans are conducted.
References
- https://owasp.org/www-community/attacks/xss/
- https://www.paloaltonetworks.com/cyberpedia/xss-cross-site-scripting
- https://developer.mozilla.org/en-US/docs/Glossary/Cross-site_scripting
- https://www.cloudflare.com/learning/security/threats/cross-site-scripting/

Introduction
The increase in consumer demands has resulted in a sharp increase in digital financing in India. As a result, the reputation of the digital lending sector has been impacted, as bad actors increasingly deploy illicit lending platforms such as fraudulent loans and trading apps. As millions of Indians download fast loan applications to help them meet their financial ends, the fraudulent apps result in cyber crimes including financial fraud. Consumers need to be vigilant of dubious trading or loan applications as bad actors frequently use illegitimate apps to trick victims by advertising limited-period offers and applying pressure.
Recently the Indian Cyber Crime Coordination Centre (I4C) led handel CyberDost has issued a cybercrime alert against the ‘CashExpand-U’ finance assistant app, which has been now removed from the Google Play Store. The app was found to be associated with hostile foreign entities, and the app had made it easier to raise small loans. However, such loan apps are seldom credible and may compromise financial information.
Raising cases of Fraudulent Loan Apps
The finance minister had stated that the government is constantly engaged with the Reserve Bank of India and other regulators and stakeholders to control fraudulent loan apps. In FY23, there were 1,062 complaints against such apps, the Finance Minister shared during a Lok Sabha session. Google removed almost 134 fake apps from the Play Store in a single week in September 2023 after multiple complaints were registered against such apps. The Reserve Bank of India (RBI) had also issued regulatory guidelines on digital lending in April 2023 to bring transparency in the digital loan space.
CyberPeace Policy Wing Advisory for Users
- Be cautious of App Permissions
Fake lending apps collect data by fraudulently taking numerous app permissions from consumers and misusing them later. The users must effectively manage their app permissions to avoid denying any extra permissions such as access to contacts, location, and photos. This is because fraudulent digital lenders access users' personal data to extort additional money even after loan repayment.
- Practice Due Diligence
Consumers must exercise care & caution before applying for a loan from digital lending platforms. Before applying for a loan or downloading any such apps, consumers must conduct due diligence by verifying the app's name, rating, reviews, physical address, and contact information. Always double-verify the paperwork before signing any agreement or contract. Always apply for loans from RBI-approved and compliant banking and financial services providers.
- Download from Official Sources
To avoid downloading counterfeit apps, only download lending apps from official stores like Google Play Store or Apple App Store, and avoid downloading apps from web links sent via SMS, email, or social media, even if shared by your known persons.
- Be sceptical of too-good-to-be-true offerings
Be cautious of deals that seem too good to be true, like hassle-free easy loans as they can be fraudulent. If an offer seems too good to be true, it might be a red flag. Hence always conduct your own research to verify the lender and avoid making hasty decisions.
- Reporting Mechanism
In case of facing a scam by such fraudulent apps, victims can file a complaint with the ‘National Cyber Crime Reporting Portal’ or Cyber Crime Helpline ‘1930’, or they can also contact us at CyberPeace Helpline +919570000066 and helpline@cyberpeace.net to get assistance in reporting their cases.
Final Words
Illegitimate loan/trading apps have been raising concerns by defrauding innocent consumers who seek financial assistance. The Center has recently warned against the CashExpand-U app, which has been now removed from the Google Play Store. Users are advised to exercise due care and caution while downloading loan apps and applying for loans to prevent any potential scams. keep up to date with news from concerned authorities about common scams and fraudulent practices in the lending space and stay safe in the online world.
References:
- https://www.livemint.com/news/beware-govt-issues-cybercrime-alert-against-loan-app-cashexpand-u-finance-assistant-11720338996430.html
- https://timesofindia.indiatimes.com/technology/tech-news/government-has-issued-an-important-warning-for-this-loan-app/articleshow/111541577.cms
