
#FactCheck-Old Saudi Arabia Fire Video Falsely Shared as Footage of Recent U.S. Attack on Iran
Executive Summary
As tensions between the United States and Iran continue to escalate in West Asia, a video showing a massive fire engulfing an industrial facility is being widely circulated on social media. Several users claim that the footage shows the aftermath of a recent U.S. strike on Iran. CyberPeace Research Wing’s research found the claim to be false. Our research revealed that the viral video is not related to the current U.S.-Iran conflict. It actually shows a 2022 attack on Saudi Arabia's Aramco petroleum distribution facility in Jeddah, carried out by Yemen's Houthi rebels.
Claim
An X user shared the viral video on July 16, 2026, claiming that it shows a recent American attack on Iran. https://x.com/SonOfBharat7/status/2077823734069826027 , https://perma.cc/RPA9-YZ3C

Fact Check
To verify the claim, we extracted keyframes from the viral video and conducted a reverse image search using Google Lens. During the research, we found that the same video had been uploaded by Reuters on March 26, 2022. According to Reuters, Yemen's Houthi rebels claimed responsibility for attacks on Saudi Arabia's energy facilities. Reuters reported that the Saudi-led coalition confirmed an attack on Saudi Aramco's petroleum products distribution station in Jeddah, where two storage tanks caught fire. The incident caused significant damage but no casualties were reported. https://www.youtube.com/watch?v=-CAxj5tgZ_w

For further verification, we found another video of the same incident uploaded by the Qatar Day Facebook page on March 25, 2022, showing the fire from a different angle. According to the post, a massive blaze broke out at an oil depot in Jeddah, Saudi Arabia, after Yemen's Houthi rebels launched multiple drone and missile attacks targeting Saudi infrastructure. Thick black smoke could be seen rising over the city.

Additionally, The Sun also uploaded the same footage on March 26, 2022, identifying it as the attack on Jeddah, Saudi Arabia. https://www.youtube.com/watch?v=bFj5nDL0y7o

Conclusion
Our research found that the viral video does not show a recent U.S. attack on Iran.Although the United States and Iran have recently exchanged military strikes and attacks on civilian infrastructure have been reported, the viral footage predates the current conflict by several years. It actually shows the March 2022 Houthi attack on Saudi Aramco's petroleum distribution facility in Jeddah, Saudi Arabia. Therefore, the claim linking the video to the ongoing U.S.-Iran conflict is false and misleading.

Related Blogs

Introduction
Over the past few months, cybercriminals have upped the ante with highly complex methods targeting innocent users. One such scam is a new one that exploits WhatsApp users in India and globally. A seemingly harmless picture message is the entry point to stealing money and data. Downloading seemingly harmless images via WhatsApp can unknowingly install malware on your smartphone. This malicious software can compromise your banking applications, steal passwords, and expose your personal identity. With such malware-laced instant messages now making headlines, it is advised for netizens to exercise extreme caution while handling media received on messaging platforms.
How Does the WhatsApp Photo Scam Work?
Cybercriminals began embedding malicious code in images being shared on WhatsApp. Here is how the attack typically works:
- The user receives a WhatsApp message from an unknown number with an image.
- The image may appear harmless—a greeting, meme, or holiday card—but it's packed with hidden malware.
- When the user taps to download the image, the malware gets installed on the phone in silent mode.
- Once installed, the malware is able to capture keystrokes, read messages, swipe banking applications, swipe credentials, and even hijack device functionality.
- Allegedly, in its advanced versions, it can exploit two-factor authentication (2FA) and make unauthorised transactions.
Who Is Being Targeted?
This scam targets both Android and iPhone users, with a focus on vulnerable groups like senior citizens, busy workers during peak seasons, and members of WhatsApp groups flooded with forwarded messages. Experts warn that a single careless click is enough to compromise an entire device.
What Can the Malware Do?
Upon installation, the malware grants hackers a terrifying level of access:
- Track user activity via keylogging or screen capture.
- Pilfer banking credentials and initiate fund transfers automatically.
- Obtain SMS or app-based 2FA codes, evading security layers.
- Clone identity information, such as Aadhaar details, digital wallets, and email access.
- Control device operations, including the camera and microphone.
This level of intrusion can result in not just financial loss but long-term digital impersonation or blackmail.
Safety Measures for WhatsApp Users
- Never Download Media from Suspicious Numbers
Do not download any files or pictures, even if the content appears to be familiar, unless you have faith in the source. Spread this advice among family members, particularly the older generation.
- Turn off Auto-Download in WhatsApp Settings
Navigate to Settings > Storage and Data > Media Auto-Download. Switch off auto-download for mobile data, Wi-Fi, and roaming.
- Install and Update Mobile Security Apps
Ensure your phone is equipped with a good antivirus or mobile security app that is updated from time to time.
- Block and Report Potential Scammers
WhatsApp offers the ability to block and report senders in a straightforward manner. This ensures that it notifies the platform and others as well.
- Educate Your Community
Share your knowledge on cyber hygiene with family, friends, and colleagues. Many people fall victim simply because they aren't aware of the risks, staying informed and spreading the word can make a big difference.
Advisories and Response
The Indian Cybercrime Coordination Centre (I4C) and other state cyber cells have released several alerts on increasing fraud via messaging platforms. Law enforcement agencies are appealing to the public not only to be vigilant but also to report any incident at once through the National Cybercrime Reporting Portal (cybercrime.gov.in).
Conclusion
The WhatsApp photo scam is a stark reminder that not all dangers come with a warning. A picture can now be a Trojan horse, propagating silently from device to device and draining personal money. Do not engage with unwanted media, refresh and update your privacy and security settings. Cyber criminals survive on neglect and ignorance, but through digital hygiene and vigilance, we can fight against these types of emerging threats.
References
- https://www.opswat.com/blog/how-emerging-image-based-malware-attacks-threaten-enterprise-defenses
- https://www.indiatvnews.com/technology/news/whatsapp-photo-scam-alert-downloading-random-images-could-cost-you-big-2025-05-06-988855
- https://www.hindustantimes.com/india-news/what-is-the-whatsapp-image-scam-and-how-can-you-stay-safe-from-it-101744353412848.html
- https://faq.whatsapp.com/898107234497196/?helpref=uf_share
- https://www.welivesecurity.com/en/malware/malware-hiding-in-pictures-more-likely-than-you-think/
- https://faq.whatsapp.com/573786218075805
- https://www.reversinglabs.com/blog/malware-in-images
Introduction
For years, when Meta's automated systems flagged suspected child sexual abuse material on Facebook or Instagram involving an Indian child, that information did not go straight to an Indian police station. It went first to a private, US based nonprofit, the National Center for Missing & Exploited Children (NCMEC), which would then decide how and when to route the relevant details back to law enforcement in the country where the crime actually happened. That indirect chain has now been shortened. In mid September 2026, senior Indian government officials confirmed that Meta had agreed, for the first time among major social media platforms operating in India, to report child sexual abuse cases and details of repeat offenders directly to the cybercrime division of the Indian Cyber Crime Coordination Centre, commonly known as I4C, under the Ministry of Home Affairs. Google followed within days with a similar commitment of its own.
How the reporting actually worked before this
Under US federal law, Meta and every other American headquartered platform is legally obligated to report CSAM instances to NCMEC, facing criminal liability, financial penalties, and the loss of legal safe harbour protections if they fail to do so. NCMEC would then coordinate with law enforcement agencies in the relevant country. In India's case, that meant a 2019 memorandum of understanding between NCMEC and the National Crime Records Bureau, through which more than 69 lakh CyberTipline reports had reportedly been shared with Indian states and union territories by early 2024. The structural problem was not the volume of reports; it was the layer of institutional distance built into every single one of them. As one government official put it plainly, an Indian law enforcement agency was, in effect, made to wait on a private American nonprofit for information about a crime committed on Indian soil against an Indian child, and NCMEC itself has little to no operational presence in India to manage that handoff quickly.
That distance had real, documented costs. Officials directly linked slow data sharing to delayed CSAM investigations, describing situations where exploitation was actively ongoing while Indian agencies remained one step removed from the account level details, IP addresses, and identifying information that could have accelerated a rescue or an arrest.
What actually changed, and why now
This shift did not emerge from a routine policy review. It followed sustained government pressure through 2026, including a formal inquiry launched by the National Commission for Protection of Child Rights into Meta India's child safety policies, multiple summons issued to Meta India head, and a July 2026 controversy in which Meta was found to have run paid Instagram advertisements allegedly directing users toward Telegram channels distributing CSAM.
Union Minister Ashwini Vaishnaw directly raised the direct reporting demand with Meta's Chief of Global Affairs, Joel Kaplan, during a visit to New Delhi in August 2026, and separately questioned whether Meta could still claim to be a "simple intermediary" given that it profits from advertisement placement and exercises systems level control over ad distribution. Under the new arrangement, account level details, including names, associated email addresses, and IP addresses, will now flow directly to I4C, which officials say should meaningfully compress the time between detection and actionable law enforcement response.
Why this is a welcome step, but not a solved problem
There is genuine reason to treat this as meaningful progress. For years, reporting routed through NCMEC meant Indian agencies were effectively once removed from data concerning crimes committed on Indian soil, against Indian children. Direct reporting to I4C shortens that distance and gives investigators quicker access to information that matters most in time sensitive cases, where every day of delay can mean continued access, continued distribution, or a victim who remains unidentified.
That said, this should not be described as a finished problem, and its real value will depend on at least three things.
The first is the depth of data actually shared. Account level details, a name, an email address, an IP address, are a starting point for an investigation, not an end point. Whether the new arrangement includes the kind of contextual detail investigators actually need to build a prosecutable case, rather than simply a faster version of the same limited data packet previously routed through NCMEC, remains to be seen in practice rather than in the announcement itself.
The second is institutional capacity on the receiving end. I4C and state cyber cells will now be positioned to receive a higher volume of reports arriving faster than before, but a faster pipeline only produces better outcomes if the infrastructure receiving it can actually convert that inflow into timely, actionable results on the ground. India's cyber cells have historically been understaffed and unevenly resourced across states, with some districts operating with only a handful of trained personnel handling cybercrime alongside a broad range of other digital offences. A genuinely improved reporting channel could, in that context, simply shift the bottleneck downstream from Washington to a district cyber cell rather than eliminate it, unless the surge in report volume is matched by a corresponding investment in trained staff, forensic capacity, and case management systems capable of prioritising the most time sensitive reports first.
The third is consistency across the industry. Meta and Google have now committed to this model, but whether it extends reliably across every major platform operating in India, rather than remaining an arrangement secured through targeted pressure on one or two companies at a time, will determine whether this becomes a systemic fix or a set of isolated exceptions.
The quieter tension nobody has fully resolved
There is also a more technical reality worth naming honestly. As platforms adopt end to end encryption more broadly, extending it across messaging services and, in some cases, considering it for other content types, the pool of CSAM content that can actually be automatically detected narrows, even as the reporting pipeline for whatever is detected improves. WhatsApp itself has argued in Indian courts, including in its ongoing challenge to the IT Rules' traceability requirements, that end to end encryption and message traceability are close to mutually exclusive, a position echoed by cryptography experts including Signal's Moxie Marlinspike, who has stated plainly that identifying a message's originator at the very least undermines, and likely breaks, the purpose of end to end encryption altogether. Faster reporting channels do not, by themselves, compensate for reduced visibility into content that a platform's own encryption prevents it from scanning in the first place. That tension, between strengthening user privacy through encryption and strengthening child safety through detection, sits underneath this entire announcement and deserves sustained attention from technologists, platforms, and child safety practitioners alike, rather than being treated as resolved simply because reporting speed has improved.
India's National Human Rights Commission has already flagged this directly in its own advisory, recommending that platforms using end to end encryption be required to devise additional protocols or technology specifically to monitor CSAM circulation, an unresolved and technically difficult ask that sits alongside, rather than instead of, the reporting improvements announced this month.
What this actually represents
The most accurate way to characterise this development is as a meaningful first step in platform accountability toward children in India, not a finish line. Meta agreeing to report directly, rather than through a private American intermediary, closes a real structural gap that officials say genuinely delayed investigations. But the task now shifts to India itself: building the institutional capacity at I4C and in state cyber cells to make full use of what is finally being offered, extending the same commitment across the rest of the industry rather than platform by platform, and confronting the encryption question honestly rather than treating faster reporting as a substitute for solving it.
A judicial note worth remembering
It is worth noting that Indian courts pushed for this same sensitivity well before it became routine practice. The Supreme Court, in Just Rights for Children Alliance v. S. Harish, 2024, directed that the term "child pornography" be replaced with "child sexual abuse and exploitation material" across legal and public usage, holding that the word "pornography" wrongly implies consent and normalises what is, in fact, a recorded act of abuse. That judicial insistence on precise language is a useful reminder that reporting frameworks like this one will ultimately be judged not just on speed, but on whether they treat the material, and the children in it, with the gravity courts have already demanded.
References
- https://www.business-standard.com/industry/news/meta-agrees-to-share-csam-details-with-indian-law-enforcement-agencies-125091500052_1.html
- https://www.business-standard.com/technology/tech-news/google-india-to-share-csam-case-details-with-govt-cybercrime-division-126092101062_1.html
- https://www.storyboard18.com/advertising/ncpcr-summons-meta-india-md-again-over-child-abuse-ads-ws-l-110781.htm
- https://www.superprep.io/current-affairs/meta-report-csam-directly-to-indias-cybercrime-portal
- https://theprint.in/india/specialised-central-police-unit-use-of-technology-to-proactively-detect-csam-nhrc-advisory/1822223/
- https://www.livelaw.in/news-updates/whatsapp-delhi-high-court-traceability-end-to-end-encryption-privacy-risk-174743
- https://www.forbesindia.com/article/take-one-big-story-of-the-day/traceability-and-endtoend-encryption-cannot-coexist-on-digital-messaging-platforms-experts/66969/1
Executive Summary
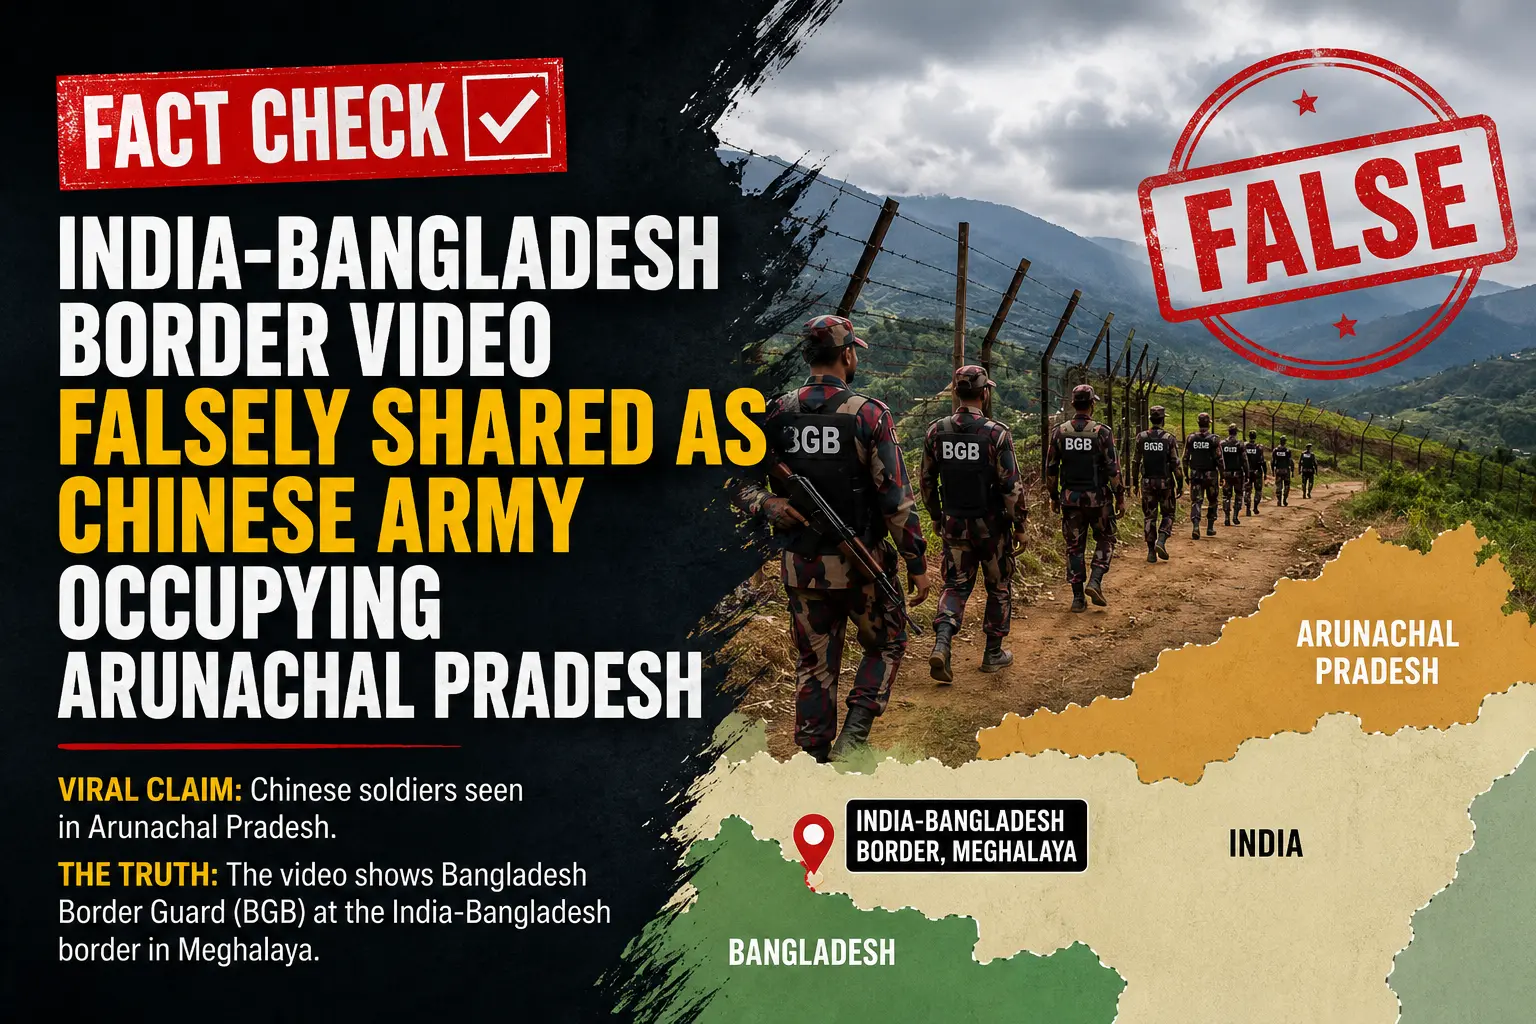
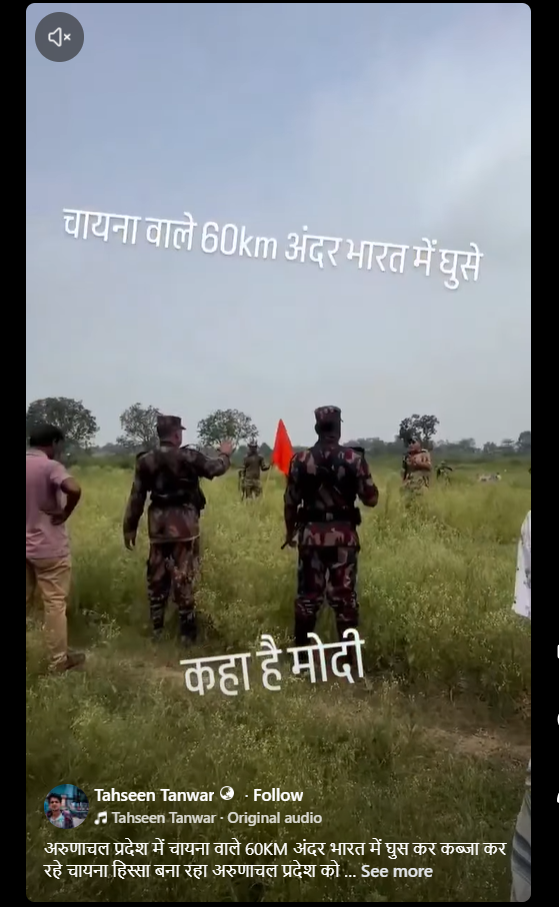
A video is being widely shared on social media with the claim that the Chinese Army has entered 60 kilometres inside Arunachal Pradesh and occupied Indian territory. In the video, a man appears to be recording the situation using his selfie camera, while soldiers can be seen standing face-to-face and arguing with each other in the background. The CyberPeace Research Wing found that the claim is false. The viral video is not from Arunachal Pradesh. It shows a confrontation between India’s Border Security Force (BSF) and Bangladesh’s Border Guard Bangladesh (BGB) along the India-Bangladesh border.
Claim
A Facebook user shared the video with the caption:
"China is entering 60 km inside India and occupying Arunachal Pradesh. China is turning Arunachal Pradesh into its territory. Where are Prime Minister Modi, Defence Minister Rajnath Singh and Home Minister Amit Shah?"
Post link:
https://www.facebook.com/reel/1736825064305394
https://www.facebook.com/reel/1736825064305394
FactCheck
Our research found no credible news report confirming that Chinese troops had entered 60 kilometres inside Arunachal Pradesh or occupied Indian territory.
The people in the viral video can be heard speaking in Bengali, suggesting that the footage could be from the India-Bangladesh border rather than Arunachal Pradesh.
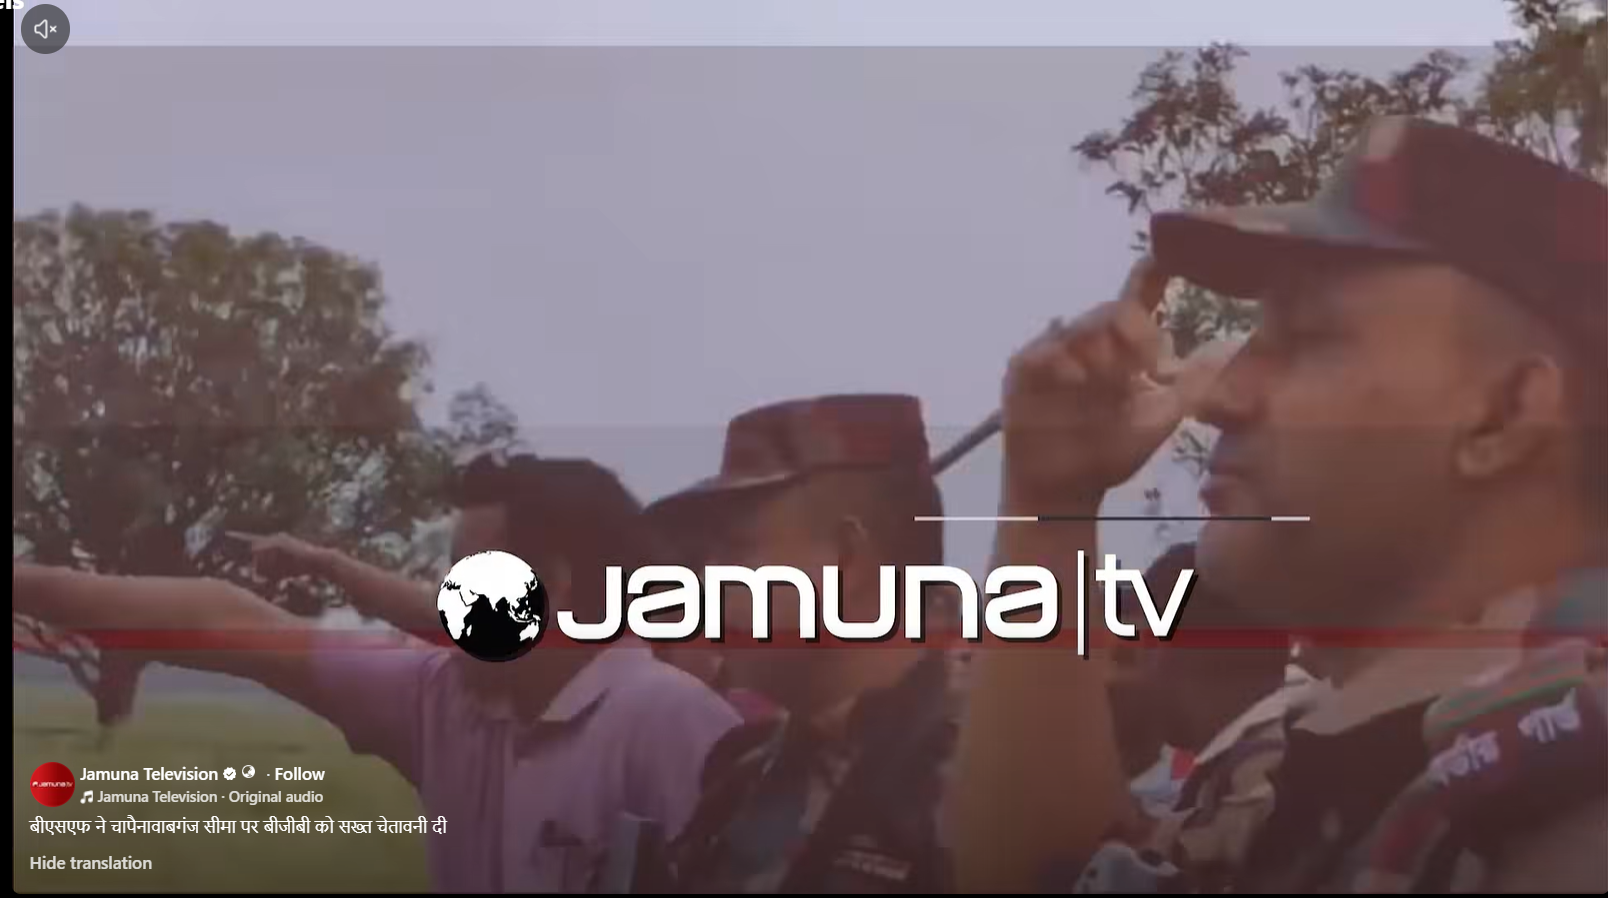
A reverse image search of keyframes from the viral video led us to an identical video posted on the Facebook page of Bangladeshi news channel Jamuna TV on June 20. According to the caption, the incident took place along the Chapainawabganj border in Bangladesh, where personnel of India’s BSF and Bangladesh’s BGB had confronted each other.
https://www.facebook.com/reel/1049262804595610
We also found reports from Bangladeshi media outlet Prothom Alo about the incident. According to the reports, Bangladeshi security personnel had stopped around 20 people who were attempting to return to Bangladesh from India, following which a verbal altercation took place between BSF and BGB personnel.
https://www.prothomalo.com/bangladesh/district/syzkfootaq
Conclusion
The viral claim is false. The video does not show Chinese troops entering or occupying 60 kilometres of territory inside Arunachal Pradesh. It actually shows a confrontation between BSF and BGB personnel along the India-Bangladesh border in the Chapainawabganj area of Bangladesh. The footage is being circulated with a false Arunachal Pradesh-related narrative.
