
#FactCheck: Old Birthday Party Video Falsely Linked to CDS’s Son and Army Residence
Executive Summary
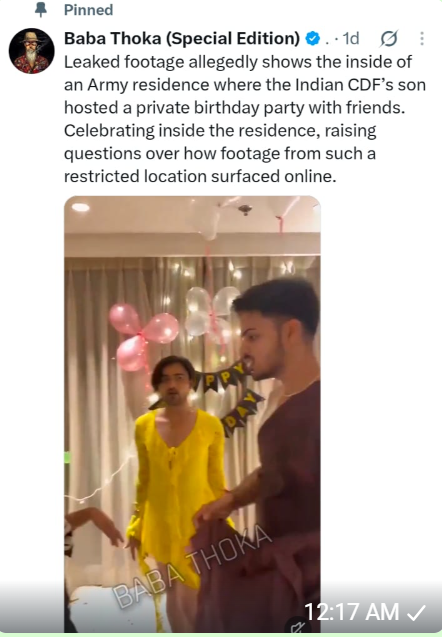
A video is being shared on social media with the claim that it allegedly shows the son of India’s Chief of Defence Staff (CDS) hosting a private birthday party with friends. Several people can be seen wearing women’s clothing in the video and attending what appears to be a birthday celebration. The posts further question how footage from an allegedly restricted Army residence surfaced online. CyberPeace Research found the viral claim to be misleading. Our research found that the video being shared by linking it to an Army residence and the son of the CDS is actually from the birthday celebration of fashion designer Lalit Singh, which was held in Gurugram. Therefore, the claim that the video shows a private birthday party hosted by the CDS’s son inside an Army residence is false.
Claim
A Pakistani handle claimed that the purported leaked footage shows the interior of an Indian Army residence, where the son of India’s CDS allegedly hosted a private birthday party with friends. The handle further questioned how footage from such a restricted location had surfaced online.
https://x.com/OfficialThoka/status/2101591703471988805
Fact Check
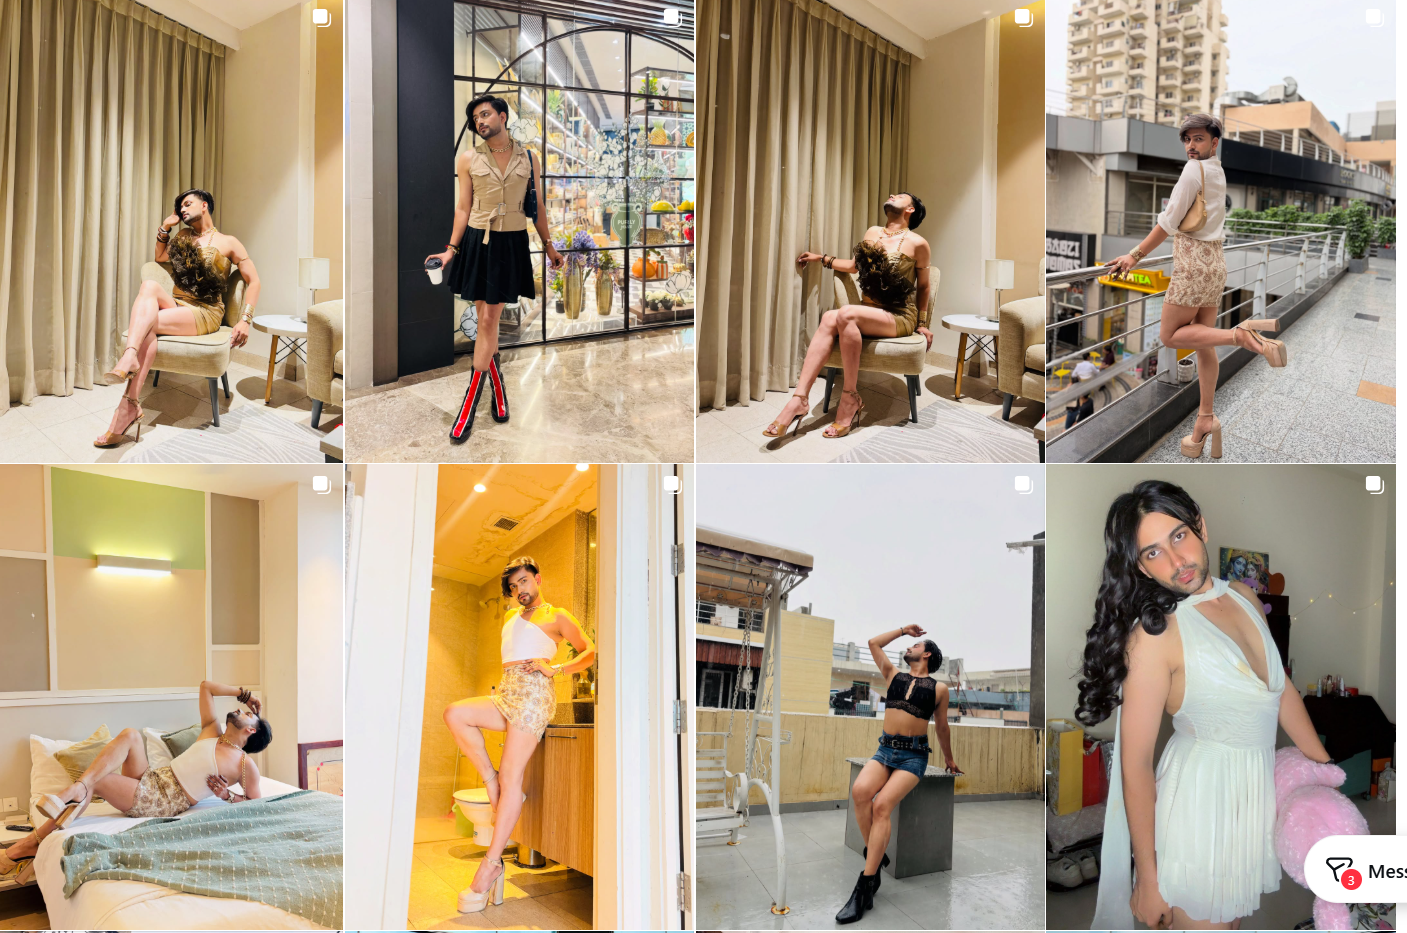
To verify the viral claim, we conducted a Google search using relevant keywords. During the search, we did not find any credible media reports related to the claim. A reverse image search and a search using relevant keywords revealed that the event shown in the video was the birthday celebration of fashion designer Lalit Singh. Lalit Singh had shared several photographs from his birthday celebration held in Gurugram on social media, and the visuals in those photographs matched those seen in the viral video.
https://www.instagram.com/lalitsingh159/
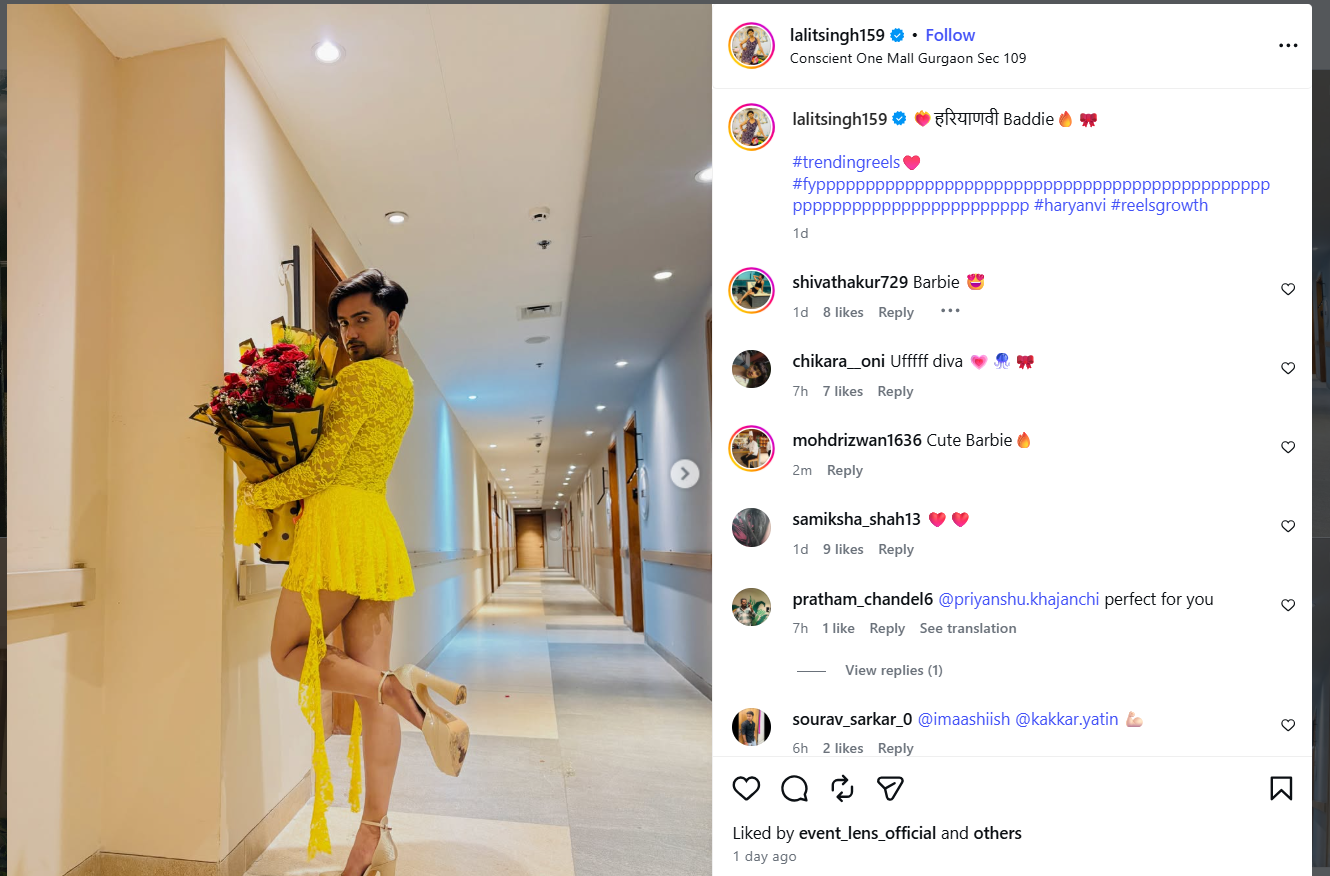
We found photographs of the person seen in the viral video on Instagram. He had identified himself as Lalit Singh.
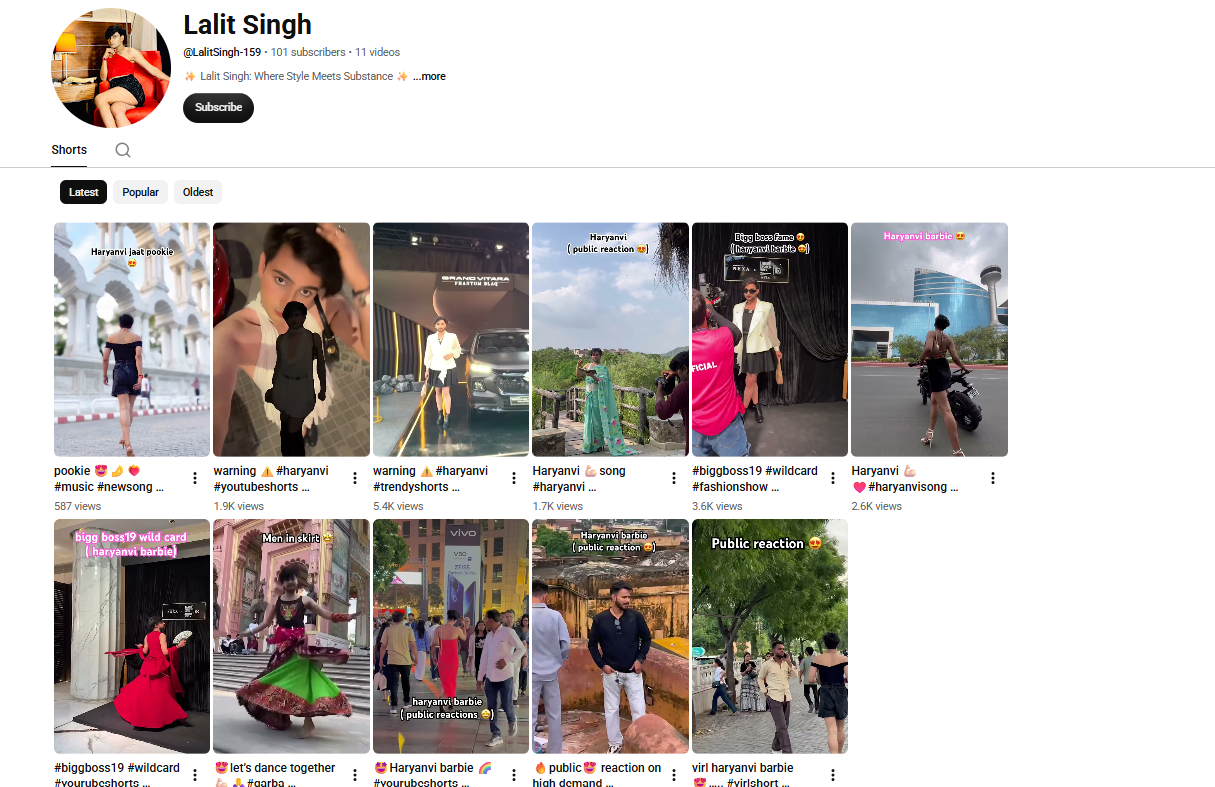
At the end of our research, we also found the YouTube channel of fashion designer Lalit Singh. On the channel, Lalit Singh regularly shares videos related to similar birthday celebrations and other private events. This further confirms that the claim linking the viral video to a birthday party hosted by the son of India’s Chief of Defence Staff is false and fabricated.
https://www.youtube.com/@lalitsingh-159
Conclusion
Our research found that the video being shared on social media with the claim that it shows a birthday party hosted by the son of India’s Chief of Defence Staff (CDS) and footage from an Army residence is being circulated with a false claim. The research revealed that the visuals in the viral video are from the birthday celebration of fashion designer Lalit Singh, which was held in Gurugram. Lalit Singh shared several photographs and videos from the same celebration on his social media accounts. In addition, videos related to similar events are available on his YouTube channel. During our research, we found no credible or official source linking the viral video to the CDS’s son or any Army residence. Therefore, the claim that the viral video shows a private birthday party hosted by the CDS’s son is false and misleading.

Related Blogs

Introduction:
With improved capabilities and evasion strategies, the Vultur banking Trojan has reappeared and is a serious danger to Android users. The virus now employs numerous encrypted payloads, encrypted communication, and poses as legitimate apps. It is transmitted by trojanized dropper programs on the Google Play Store. Vultur targets victims via phone calls and SMS messages. With the help of this updated version of Vultur, attackers may take total control of compromised devices. They can perform a variety of remote control operations like install, remove, upload, and download files, halt the execution of programs, and circumvent the lock screen. The virus is now far more hazardous than it was previously because of its improved capacity to remotely access and manipulate machines.
Overview:
The Android banking malware Vultur is well-known for its ability to record screens. It was first identified by ThreatFabric in March 2021 and targets banking apps for remote control and keylogging.
The malicious apps were hosted on the Google Play Store by the Brunhilda dropper-framework, which was used for its distribution. Initial versions of the program used reputable remote access tools such as ngrok and AlphaVNC.
Hybrid attacks have been used in recent operations to disseminate the Brunhilda dropper via phone calls and SMS. The dropper uses a number of payloads to distribute an upgraded version of Vultur.
41 new Firebase Cloud Messaging (FCM) commands and seven new Command-and-Control (C2) methods are included in the most recent version of Vultur.
With the help of Android's Accessibility Services, these enhancements concentrate on remote access functionality that improves the malware's capacity to communicate with the victim's screen.
Modus operandi of Attack:
Hybrid Attack Method:
- Utilizes a phone call, two SMS messages, and trick users into installing malware.
- First SMS tricks victims into calling a certain number by claiming to have made significant, unlawful transactions, which gives the impression of urgency.
- Although there was no transaction in reality, the urgency motivates victims to act quickly.
Trozonized MacAfee App:
- The victims are told to install a trojanized version of the McAfee Security program from a given link during the phone call.
- This app looks harmless and has features similar to the original McAfee Security app, but it's actually the Brunhilda dropper.
- The victims are misled into assuming that the security software they are installing is authentic.
Execution of Vultur Payloads:
- Three payloads connected to Vultur are decrypted and executed via the Brunhilda dropper.
- Threat actors can carry out a variety of malicious operations, including keylogging and screen recording, on the victim's mobile device thanks to these payloads, which grant them total access over it.
- The infected device of the victim allows the threat actors to launch additional assaults or obtain private data.
Indication of the attack:
The symptoms of a Vultur banking Trojan infection include:
- Remote Access: This malware gives the hacker the ability to remotely use the infected device via clicking, scrolling, and swiping through Android's accessibility services.
- File Management: Through this, the malware is able to copy, share, remove, create, and locate files from devices it has infected.
- App Blocking: For instance; the malicious software can be programmed to stop the victims from opening a certain bunch of apps.
- Custom Notifications: Attackers can embed the malware with the functionality of displaying the customized notifications in the taskbar.
- Keyguard Disabling: The malware may be designed to turn off Screen Lock Guard feature so the lock screen security measure can be easily bypassed.
- Encrypted C2 Communication: The malware chooses AES data encryption, with Base64 text encoding to provide hidden traces for C2 communication.
- Payload Decryption: The malware uses native code, mostly written in C as well as C++, to decode the goods, thus, making a process of reversing more complicated.
- Spying on Financial Apps: The malware uses screen-streaming and keylogging as ways of acquiring facts about the victim’s mobile banking applications.
Indicator of Compromise:
File hash (SHA-256)
- edef007f1ca60fdf75a7d5c5ffe09f1fc3fb560153633ec18c5ddb46cc75ea21
- 89625cf2caed9028b41121c4589d9e35fa7981a2381aa293d4979b36cf5c8ff2
- 1fc81b03703d64339d1417a079720bf0480fece3d017c303d88d18c70c7aabc3
- 4fed4a42aadea8b3e937856318f9fbd056e2f46c19a6316df0660921dd5ba6c5
- 001fd4af41df8883957c515703e9b6b08e36fde3fd1d127b283ee75a32d575fc
- fc8c69bddd40a24d6d28fbf0c0d43a1a57067b19e6c3cc07e2664ef4879c221b
- 7337a79d832a57531b20b09c2fc17b4257a6d4e93fcaeb961eb7c6a95b071a06
- 7f1a344d8141e75c69a3c5cf61197f1d4b5038053fd777a68589ecdb29168e0c
- 26f9e19c2a82d2ed4d940c2ec535ff2aba8583ae3867502899a7790fe3628400
- 2a97ed20f1ae2ea5ef2b162d61279b2f9b68eba7cf27920e2a82a115fd68e31f
- c0f3cb3d837d39aa3abccada0b4ecdb840621a8539519c104b27e2a646d7d50d
- 92af567452ecd02e48a2ebc762a318ce526ab28e192e89407cac9df3c317e78d
- fa6111216966a98561a2af9e4ac97db036bcd551635be5b230995faad40b7607
- dc4f24f07d99e4e34d1f50de0535f88ea52cc62bfb520452bdd730b94d6d8c0e
- 627529bb010b98511cfa1ad1aaa08760b158f4733e2bbccfd54050838c7b7fa3
- f5ce27a49eaf59292f11af07851383e7d721a4d60019f3aceb8ca914259056af
- 5d86c9afd1d33e4affa9ba61225aded26ecaeb01755eeb861bb4db9bbb39191c
- 5724589c46f3e469dc9f048e1e2601b8d7d1bafcc54e3d9460bc0adeeada022d
- 7f1a344d8141e75c69a3c5cf61197f1d4b5038053fd777a68589ecdb29168e0c
- fd3b36455e58ba3531e8cce0326cce782723cc5d1cc0998b775e07e6c2622160
- 819044d01e8726a47fc5970efc80ceddea0ac9bf7c1c5d08b293f0ae571369a9
- 0f2f8adce0f1e1971cba5851e383846b68e5504679d916d7dad10133cc965851
- fb1e68ee3509993d0fe767b0372752d2fec8f5b0bf03d5c10a30b042a830ae1a
- d3dc4e22611ed20d700b6dd292ffddbc595c42453f18879f2ae4693a4d4d925a
- f4d7e9ec4eda034c29b8d73d479084658858f56e67909c2ffedf9223d7ca9bd2
- 7ca6989ccfb0ad0571aef7b263125410a5037976f41e17ee7c022097f827bd74
- c646c8e6a632e23a9c2e60590f012c7b5cb40340194cb0a597161676961b4de0
Command and Control Servers
- safetyfactor[.]online
- cloudmiracle[.]store
- flandria171[.]appspot[.]com (FCM)
- newyan-1e09d[.]appspot[.]com (FCM)
Droppers distribution URL’s
- mcafee[.]960232[.]com
- mcafee[.]353934[.]com
- mcafee[.]908713[.]com
- mcafee[.]784503[.]com
- mcafee[.]053105[.]com
- mcafee[.]092877[.]com
- mcafee[.]582630[.]com
- mcafee[.]581574[.]com
- mcafee[.]582342[.]com
- mcafee[.]593942[.]com
- mcafee[.]930204[.]com
Steps to be taken when your device is compromised?.
- Change the password: Vultur revealed multiple cases where threat actors can gain access to your financial and private information. To safeguard your account, reset passwords on other devices and create secure, unique passwords during the time. Instead of simply storing your password, a reputed password manager is the most secure way of storing information.
- Keep an eye on your transactions and accounts: It is advised that you regularly monitor your online accounts for any unusual or illegal activity. Keep a watch out for any irregularities, and report anything suspicious to the provider or authorities straight immediately.. Also check your credit reports and scores attentively to make sure that your identity or cards are not compromised.
- Make sure you are using identity theft protection: Many pieces of information about your identity are stored in an Android device. Cyber criminals can easily get hold of this data and make major damage to you, including stealing your money and identity. For your own protection, some of the identity theft protection services that monitor all your personal information and notify you on any unusual activity and, as well, helps you to freeze your accounts would be beneficial.
- Immediately get in touch with your banks and credit card companies: Your personal information such as credit card or bank details is of high risk to be exposed to hackers who could use them to make transactions without you knowing. You should inform your credit card and the lending bank about the situation as soon as possible. They would help you if your cards were used for fraudulent charges and your card be either frozen or canceled. Besides, they can get new cards issued.
- Make your contacts alert regarding the fraud you faced: Threat actors may access your social media or email accounts to send phishing messages or spam to people in your contact list, if they gain access to them. Moreover, they may masquerade as you and try to extort cash from you or disclose your personal information. Distributing a message to your contacts stating that they shouldn’t open or reply to any messages that look like they are not from you and look very strange or suspicious, will be a great idea.
- Make a backup and wipe all your device content in factory settings: You can always factory reset your device to ensure it is free of viruses and spyware. In other words, it will refresh Android and leave behind all your data and settings. Back up all the critical data prior to processing it and assure that everything is restored from a trustworthy source only.
Preventive measures to be taken:
- Avoid calling back to the hacker: If a hacker texts you claiming to have approved a sizable bank transaction, refrain from picking up the phone. You can always check by making a call to your own financial intuition. However, never pick up on an unknown number that someone else sends you.
- Avoid sideloading apps and shortened URLs: Try to avoid sideloading apps. That's the moment when you install apps from unofficial sources. Users may be tricked into downloading malware using short URLs.
- Be careful granting permissions: Be cautious when allowing permissions for apps. Think about whether an app really needs access to specific data or device functions.
- Limit the apps you have on your phone: On your phone, having plenty of apps might sometimes make it easier to become infected with malware. Over time, these apps may allow harmful code to enter your system, and the more programs you have to update and monitor, the greater the risk to your Android device. This is how to remove pointless apps from your Android device.
- Download apps from reputable sources: Additionally, make sure the programs you download are from reputable and authorized developers. Do your homework and read reviews before you install.
- Keep your Android device updated: With the help of software and security upgrades, your phone can automatically maintain security. Remember to install them.
- Have good antivirus software on all your devices: The best defense against malware on all of your devices is to install antivirus software. By blocking you from clicking on potentially dangerous links, antivirus software can keep malware off your devices and keep hackers from accessing your personal data.
Conclusion:
Vultur is a terrifying banking Trojan with a great deal of sophistication. It's unsettling that hackers can take complete control of your Android device, which emphasizes how crucial it is that you take precautions. It all starts with a text message in these attacks. You must take the time to independently contact your banking institution to check whether there are any issues. You may prevent having your entire device compromised and your personal information exposed by simply investing an additional few minutes.
Reference:
- https://research.nccgroup.com/2024/03/28/android-malware-vultur-expands-its-wingspan/
- https://www.threatfabric.com/blogs/vultur-v-for-vnc\
- https://www.tomsguide.com/computing/malware-adware/this-nasty-android-banking-trojan-lets-hackers-completely-hijack-your-phone-how-to-stay-safe
- https://thehackernews.com/2024/04/vultur-android-banking-trojan-returns.html?m=1
- https://www.smallbiztechnology.com/archive/2024/04/vultur-trojan-heightens-android-app-security-risks.html/
- https://securityaffairs.com/161320/malware/vultur-banking-trojan-android.html
- https://www.malwarebytes.com/blog/detections/android-trojan-spy-vultur
- https://www.scmagazine.com/brief/updated-vultur-android-banking-trojan-emerges
- https://innovatecybersecurity.com/security-threat-advisory/windows-server-updates-blamed-for-domain-controller-crashes-kb5035855-and-kb5035857/
Introduction
One of the biggest gaming populations in the world today is found in India. Every day, hundreds of millions of young Indians engage with streaming services, immersive digital content, mobile games and e-sports ecosystems. Yet, despite this massive scale of participation, India remains largely absent from the global conversation on original gaming intellectual property. Although the nation produces very few globally significant gaming worlds of its own, it consumes games on an astonishing scale. This paradox highlights a more serious structural issue with the gaming discourse in India. Our national conversation around gaming often begins and ends with regulation i.e., online betting, taxation, fantasy gaming legality, addiction and compliance. Although these worries are valid they have inadvertently obscured a much more crucial query: is India creating a gaming industry or is it just regulating a gaming market? Various subject-matter experts have expressed their views on this issue, like Shailendra Vikram Singh Former Deputy Secretary (Cyber & Information Security), Ministry of Home Affairs who is of the opinion,
“I believe India’s gaming story presents a unique paradox. While we are one of the world’s largest gaming markets, we have yet to fully realize gaming’s potential as a strategic pillar of the AVGC vision. Much of the conversation remains focused on regulation and consumption, whereas the larger opportunity lies in creation, innovation, and global competitiveness.
In my view, gaming should be recognized as a strategic creative and digital industry. It has the potential to generate high-value employment, foster indigenous intellectual property, and strengthen capabilities in design, storytelling, animation, immersive technologies, and emerging digital skills. Beyond its economic value, gaming can also serve as a powerful platform for education, skilling, and public engagement.
I also see gaming as an important medium for bringing India’s rich cultural heritage, historical narratives, and diverse traditions to global audiences through interactive storytelling. As digital experiences increasingly shape how younger generations learn, engage, and understand the world, culturally rooted content can become a source of both creative expression and national soft power.
At the same time, sustainable growth must be built on trust. Strong safeguards for cybersecurity, child protection, user safety, responsible gaming, and data governance are essential to creating a resilient and trusted ecosystem.
To realize the full promise of the AVGC vision, I believe India must aspire to be more than a large gaming market. A nation of gamers must ultimately become a nation of game creators.”
The Misplaced Focus of Regulating Bodies
A country with one of the world’s oldest storytelling civilizations should not remain from the world’s most influential storytelling medium. Examining how other nations viewed gaming as a strategic cultural enterprise highlights the disparity even further. Japan turned gaming into a tool of soft power by exporting global icons like Mario, Pokémon and Zelda. Along with K-pop and digital culture, South Korea incorporated gaming into its larger cultural export sector. With businesses like Tencent and games like Genshin Impact and Black Myth: Wukong, China is now aggressively marketing gaming as a geopolitical and technological impact ecosystem.
Through The Witcher, Poland even showed how local folklore based storytelling may achieve cultural relevance on a worldwide scale. In contrast, India contributes very little to the global gaming imagination despite having one of the strongest civilisational storytelling traditions in human history, including the Mahabharata, Ramayana, Buddhist Narratives, tribal folklore, Indic mythology and regional legends.
Artificial Intelligence and Lore of Lost Opportunities
The arrival of artificial intelligence now changes this equation dramatically. AI is lowering the barriers to creativity in ways previously unimaginable. For character design, procedural storytelling, localisation, environment creation, NPC interactions, voice synthesis and animation pipelines, independent producers and small studios can now use generative AI. Agile creative ecosystems are increasingly able to accomplish what formerly required enormous infrastructure and production teams. This offers India a once-in-a-lifetime chance to overcome conventional developmental barriers in the gaming sector. India may become a global center for AI-assisted storytelling, culturally grounded gaming storylines and scalable independent game production instead of competing just through capital-intensive AAA ecosystems.
The AVGC Promotion Task Force for India’s Digital future explicitly highlighted the significance of intellectual property development, academic integration, skilling and incubation systems. However, India still views gaming more as a compliance industry than as a significant creative economy. Economists use revenue forecasts to discuss gaming. Taxation frameworks are used by policymakers to discuss it. However, narrative ownership, digital culture, creative sovereignty and gaming as a long-term civilisational export are not sufficiently discussed.
Playing Everyone Else’s Game
The actual danger does not lie in the fact India won’t grow into a sizable gaming industry. The change has already taken place. The bigger risk is that, in a global market that is becoming more and more controlled by foreign narratives, foreign engines and foreign platforms, India may permanently remain a consumer ecosystem. Processors and graphic engines won’t be the only factors influencing gaming in the future, cultures that can emotionally engage worlds will also play a significant role. India possesses the depth of civilisation, creative heritage, technical prowess and population size necessary to develop into such a creator economy. It does not, however, have a consistent institutional focus on supporting studios, storytellers, animators and original intellectual property ecosystems.
References
- AVGC Promotion Task Force Report, Government of India
- KPMG India Media & Entertainment Reports
- EY-FICCI Media & Entertainment Industry Reports
- Newzoo Global Games Market Reports
- Lumikai “State of India Gaming” Reports
- UNESCO Reports on Cultural & Creative Industries
- World Economic Forum reports on AI and Creative Economies
Executive Summary
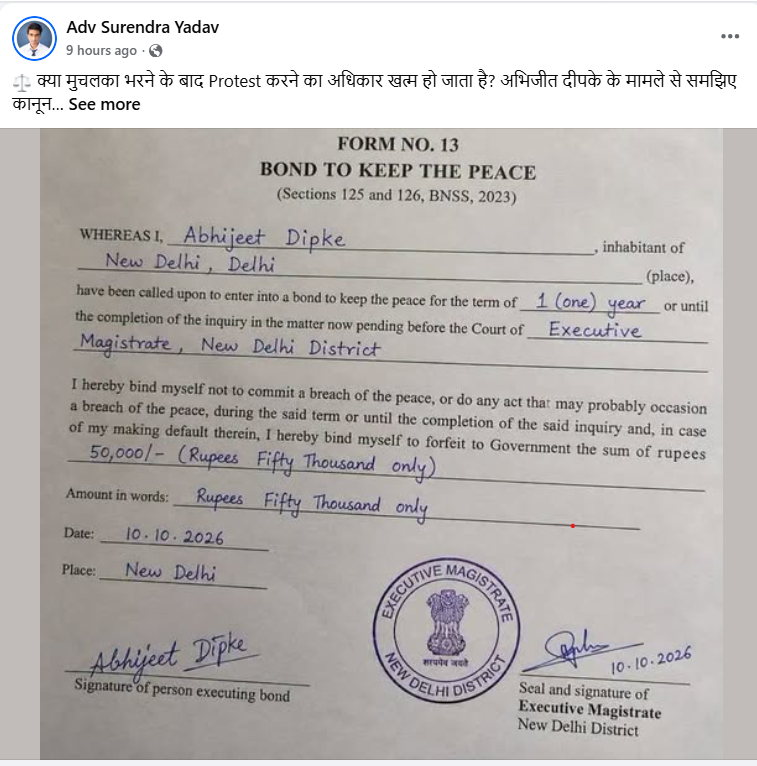
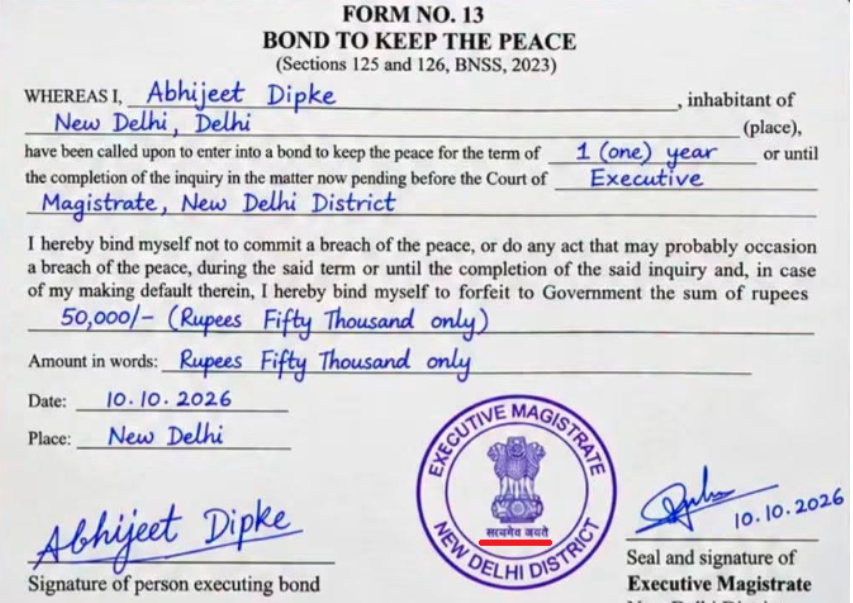
Amid the ongoing protests in Delhi, an image of a bond paper is being widely shared on social media. The image is being shared with the claim that it shows the bond allegedly submitted in court by Cockroach Janata Party (CJP) founder Abhijeet Dipke for his release. The purported bond mentions that Abhijeet Dipke would not participate in any protest in the future and that he had furnished a bail bond of Rs 50,000. CyberPeace Research found that the image of the bond paper being shared in connection with Abhijeet Dipke is not genuine, but was created using AI.
Claim
Amid the ongoing protests in Delhi, an image of a bond paper is being widely shared on social media. It is being claimed that the image shows the bond allegedly submitted in court by Cockroach Janata Party (CJP) founder Abhijeet Dipke for his release. The purported bond mentions that Abhijeet Dipke would not participate in any protest in the future and that he had furnished a bail bond of Rs 50,000.
https://www.facebook.com/photo/?fbid=122133387387390171&set=a.122113963941390171
https://ghostarchive.org/archive/C8SDb
Fact Check
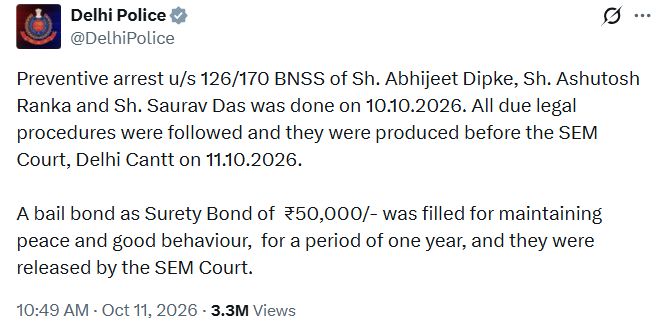
In a post shared on X, the Delhi Police stated that Abhijeet Dipke, Ashutosh Ranka and Saurav Das were taken into preventive custody on October 10, 2026, under Sections 126/170 of the Bharatiya Nagarik Suraksha Sanhita (BNSS). According to the police, all legal procedures were followed, and the three were produced before the SEM court at Delhi Cantt on October 11, 2026. In its post, the Delhi Police also stated that a bail bond (surety bond) of ₹50,000 was furnished for a period of one year to maintain peace and good behaviour.
https://x.com/DelhiPolice/status/2109151954438136069
To verify the viral image of the bond paper, we examined the Delhi Police’s social media handles and searched other media reports. However, we did not find the viral image of the bond paper in any article or X post published by a credible source. We then closely examined the viral bond paper. During our analysis, we noticed a clear error. The spelling of “Satyamev Jayate” on the seal affixed to the document is incorrect. Based on this error, we suspected that the purported image of the bond paper being circulated on social media may have been created using AI.
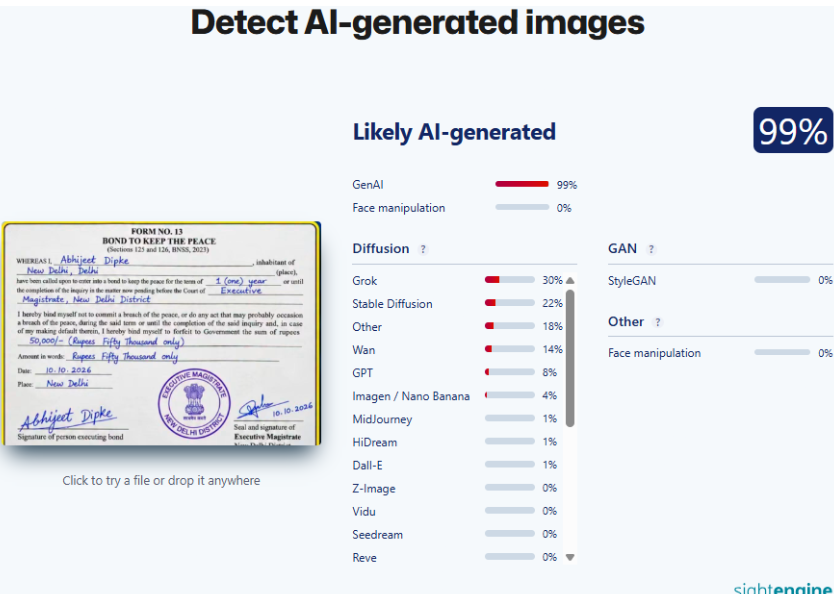
As the next step in our research, we used AI detection tools to analyse the viral image. We scanned the image using Sightengine, which indicated that the viral image is 99% likely to be AI-generated.
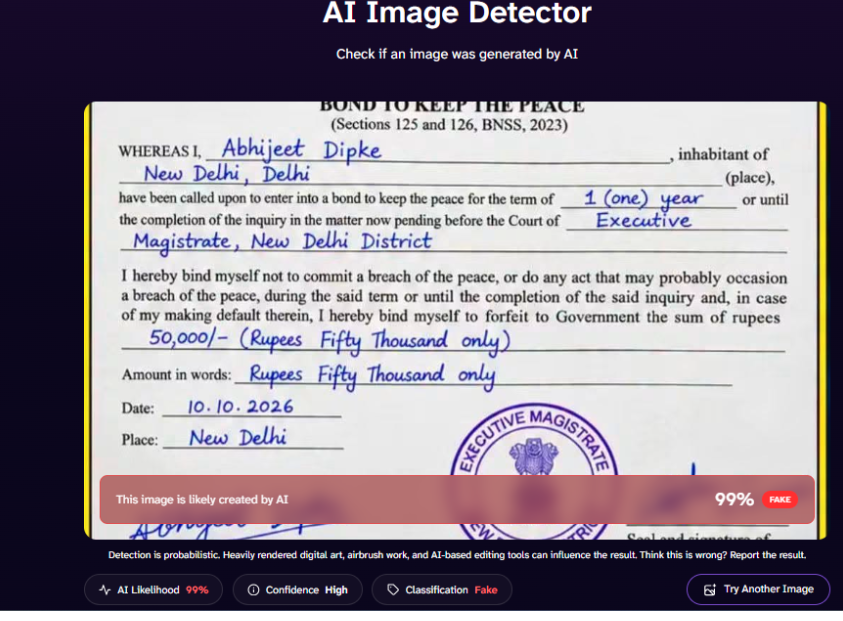
DeepAI, in its analysis, estimated a 99% likelihood that the viral bond paper was created using AI.
Conclusion
Our research found that the image of the bond paper being shared in connection with Abhijeet Dipke is not genuine but was created using AI.
