
#FactCheck-Old Bihar Video Falsely Linked to Jantar Mantar Protest Over NEET Paper Leak
Executive Summary
A video is being widely shared on social media with the claim that a person attempted to set a Thar vehicle on fire during the ongoing protest at Jantar Mantar. CyberPeace Research Wing’s research found that the viral video is not from Jantar Mantar, Delhi. The footage is from Gaya, Bihar, where some people allegedly attempted to set a vehicle on fire after a collision involving a Thar and other vehicles on July 16.
Claim:
A 23-second video is being shared on Facebook claiming to show a person attempting to set a Thar vehicle on fire during the ongoing NEET paper leak protest at Jantar Mantar in Delhi. In the video, a man can be seen trying to ignite the vehicle, while police personnel intervene and stop him. However, the crowd continues to attempt to set the vehicle on fire.
https://www.facebook.com/reel/1575765261002644

Fact Check:
To verify the claim, we extracted keyframes from the viral video and conducted a reverse image search. During the research, we found the same video uploaded on the News18 YouTube channel on July 18, 2026. The caption accompanying the video identified the incident as being from Bihar.
https://www.youtube.com/shorts/fzAPajxyi3A
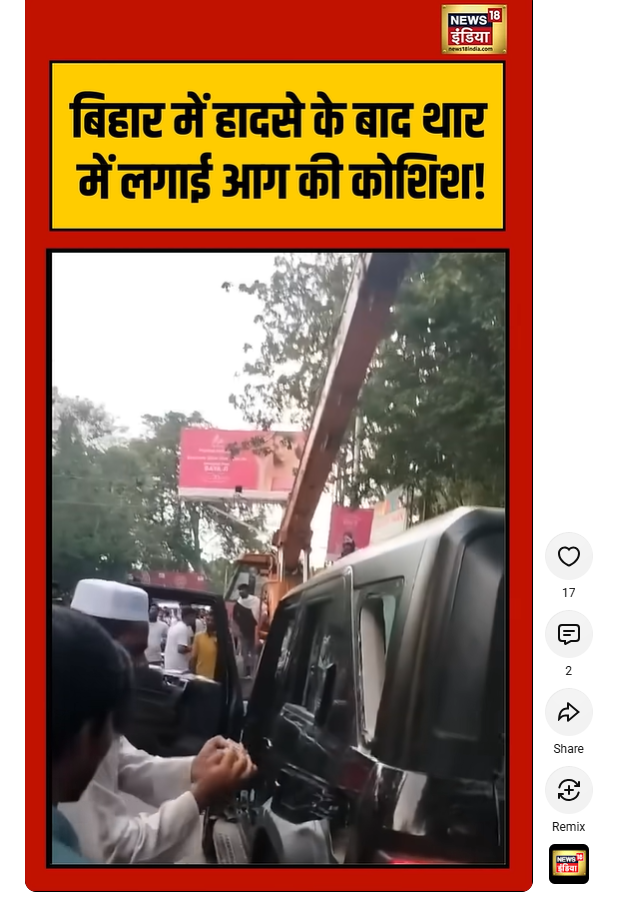
Further, a keyword search led us to a report published by Dainik Bhaskar on July 16, 2026. The report contained visuals matching the viral video, along with the statement of the person seen in the viral footage.

According to the report, the incident took place in Gaya, Bihar, after a collision between a Thar vehicle and other vehicles. Following the accident, some people gathered at the spot and allegedly attempted to set the vehicle on fire.
Conclusion:
CyberPeace Research Wing’s fact check found the viral claim to be misleading. The video does not show an incident from the ongoing Jantar Mantar protest in Delhi. The footage is from Gaya, Bihar, where a Thar vehicle was involved in a collision with other vehicles on July 16, following which some people attempted to set the vehicle on fire.

Related Blogs
Introduction
Not every major breach begins with a sophisticated new exploit. Sometimes it begins with a device nobody remembered to update, and this one began exactly that way, at scale. Security researchers have disclosed a campaign that compromised more than 14,530 internet connected cameras made by Dahua Technology, (one of the world's largest surveillance equipment manufacturers), using a mix of stolen credentials, two long known authentication flaws, and a peer to peer relay technique that let attackers reach devices tucked behind home and office routers. The operation, tracked by researchers at Hunt.io, has been named Operation CameraSwarm. It ran between June 17 and July 22, 2026, and was reconstructed almost entirely from an exposed 407 megabyte working directory the attackers themselves left accessible, containing over 2,600 files, campaign logs, shell history, and tooling. Confirmed compromises were concentrated in Ukraine and Russia, and researchers described the operators/attackers as Russian speaking based on language artifacts found in the recovered material, suggesting the campaign was most plausibly built around surveillance or access relevant to the ongoing conflict between the two countries, though no formal attribution to a named threat actor or state entity has been established or claimed. What makes this worth understanding in detail is not just the scale, though 14,500 compromised cameras is a serious number, but how mundane the actual break in methods were. None of this depended on the attackers discovering some brand new, unknown flaw, the kind of vulnerability security researchers call a ‘zero day’. It depended on something far more ordinary: thousands of devices running years-old software that had never been patched, combined with cheap automated tools that could try weak passwords and known exploits at scale.
What is Dahua, and why does this matter
Dahua Technology, founded in Hangzhou in 2001, is a publicly traded, partially state owned Chinese company and the world's second largest video surveillance manufacturer by revenue, trailing only fellow Chinese firm Hikvision. Its cameras, digital video recorders, and network video recorders are sold in roughly 180 countries through more than 2,100 partners, and the company has shipped tens of millions of devices into homes, retail stores, offices, and public infrastructure worldwide. That scale is precisely what makes any systemic vulnerability in Dahua's product line consequential well beyond a single country or sector.
How the attackers actually got in
Hunt.io attributed the compromises to three distinct attack paths. The largest, by far, was straightforward credential attacks, essentially automated login guessing using weak, default, or previously leaked passwords, which researchers traced to 12,324 unique IP addresses across more than 13,000 recorded campaign attempts. The second path exploited two authentication bypass flaws, catalogued as CVE-2021-33044 and CVE-2021-33045, both rated a severe 9.8 out of 10 on the current CVSS severity scale used by the US National Vulnerability Database. These are not new vulnerabilities. They were publicly disclosed back in 2021, and Dahua issued fixed firmware for them years ago, yet both remain listed today on the US Cybersecurity and Infrastructure Security Agency's Known Exploited Vulnerabilities catalog, a designation reserved specifically for flaws still being actively exploited in the wild despite available patches. The third and most technically interesting path involved a peer to peer, or P2P, relay mechanism built into Dahua's own Easy4IP cloud infrastructure, a system designed to let users remotely access their camera without manually configuring network settings. Security firm ITRES Labs, which documented this exposure separately in 2025, found that on firmware released before mid-2024, simply knowing a device's serial number was enough to establish a connection route through Dahua's relay servers before the camera's own login check ever kicked in, a design gap that let attackers reach devices even when they sat behind network address translation, the technical barrier that normally shields home devices from direct internet exposure. Hunt.io's recovered operator logs claimed an extraordinary 89.4 percent of live serial numbers tested returned an open channel without any authentication at all, though it is worth noting that figure comes solely from the attackers' own recovered data and has not been independently verified by Dahua, ITRES Labs, or any public incident response body as of this writing. Beyond the initial break in, the campaign also planted 1,923 cameras with a persistent account, essentially a backdoor login the operators could return to later, and researchers found evidence suggesting parts of the toolkit may have been built specifically to hand off access to a third party, though no confirmed link to a named threat actor or state sponsor has been established.
Why cameras remain such a persistent target
Internet connected cameras occupy an unusual position in the broader device ecosystem. Unlike a laptop or phone, they are rarely patched by an end user paying regular attention, they are often installed once and forgotten, and many owners never change the default credentials shipped from the factory. A compromised camera also offers an attacker something more than a foothold, live or recorded video feeds of homes, businesses, and sometimes sensitive facilities, which carries value well beyond the kind of access a compromised laptop typically provides.
CyberPeace Advisory | What device owners should do now
For anyone running Dahua surveillance equipment, or any internet connected camera system, several concrete steps meaningfully reduce exposure.
For Dahua device owners specifically:
Two steps address the exact mechanisms this campaign exploited.
- First, check the device's firmware version against Dahua's official download portal and apply the latest available update immediately, since the fixes for both 2021 authentication bypass vulnerabilities have existed for years and simply have not been applied on thousands of devices.
- Second, disable the P2P or Easy4IP remote access feature entirely unless it is actively required, since this is the exact mechanism the third attack path, the serial number based relay, relied on to reach cameras without any login check at all.
For any internet connected camera system, including in India:
The remaining precautions apply regardless of manufacturer, and are worth following on any brand of camera, DVR, or NVR connected to the internet.
- Replace default or weak passwords with strong, unique credentials on every camera and recorder, and remove any unused or unrecognised accounts, since the persistent account technique this campaign used depends entirely on unnoticed access surviving unchecked.
- Place surveillance devices on a segmented network separate from computers and phones, so that a compromised camera cannot become a stepping stone into more sensitive systems.
- Periodically audit which devices on a home or office network are internet facing at all, since many cameras end up exposed simply because remote access was left switched on by default and nobody thought to check.
- And where a device offers the option, disable any built in peer to peer or cloud relay convenience feature unless genuinely needed, since the underlying design pattern this campaign exploited, a remote access shortcut that runs before proper authentication.Is not unique to Dahua and has shown up across other camera brands in the past.
The view from India
This disclosure lands at a particularly relevant moment for India, which enforced sweeping new restrictions on Chinese origin CCTV equipment earlier this year. Since April 1, 2026, internet connected surveillance cameras sold in India have been required to carry Standardisation Testing and Quality Certification under Essential Requirements norms first introduced by the Ministry of Electronics and Information Technology in April 2024, It's a country-of-origin requirement under the Essential Requirements norms (introduced by India's Ministry of Electronics and Information Technology in April 2024), manufacturers must disclose the origin of key components like the System-on-Chip (SoC), and devices using Chinese-origin chipsets are reportedly not being granted approval by certifying authorities. Since Dahua's cameras, like Hikvision's and TP-Link's, generally rely on Chinese-made chipsets, the practical effect is that their products haven't received STQC certification, which functions as a blanket exclusion without the government needing to name any single company in the rule text itself. The stated rationale for that policy, concerns over hidden backdoor access, transmission of data to foreign servers, and deployment near sensitive locations, reads almost like a preview of exactly the kind of exposure Operation CameraSwarm has now documented in the wild. It is worth being precise here: the restriction applies to new sales, not existing installations, and CameraSwarm's confirmed victims were concentrated in Ukraine and Russia rather than India. But the underlying lesson travels well beyond any one country's borders. A camera manufactured with a convenience feature that bypasses its own login check, sitting unpatched for years despite a fix being publicly available, is a vulnerability that does not respect national boundaries, and India's decision to tighten certification requirements before an incident of this scale surfaced looks, in hindsight, considerably more prudent than reactive.
References
- The Hacker News, "Hackers Compromised 14,500+ Dahua Devices Using Credential Attacks, Auth Bypasses, and P2P." August 19, 2026. https://thehackernews.com/2026/08/hackers-compromised-14500-dahua-devices.html
- Hunt.io, "Operation CameraSwarm: Dahua Cameras Compromised." https://hunt.io/blog/operation-cameraswarm-dahua-cameras-compromised
- ITRES Labs, "Dahua Beyond CVE-2025-31702: P2P Relay Exposure." October 29, 2025. https://labs.itresit.es/2025/10/29/dahua-beyond-cve-2025-31702-p2p-relay-exposure?
- Dahua Security, "DHCC-SA-202106-001: Security Advisory - Identity Authentication Bypass Vulnerability Found in Some Dahua Products." https://www.dahuasecurity.com/about-dahua/trust-center/dahua-psirt/dhcc-sa-202106-001%3Asecurity-advisory---identity-authentication-bypass-vulnerability-found-in-some-dahua-products
- National Vulnerability Database, "CVE-2021-33044 Detail." https://nvd.nist.gov/vuln/detail/CVE-2021-33044
- CISA, "Known Exploited Vulnerabilities Catalog." https://www.cisa.gov/known-exploited-vulnerabilities-catalog
- Business Standard, "India to ban Chinese CCTV from Apr 1 as security concerns reshape market." https://www.business-standard.com/industry/news/india-ban-chinese-cctv-government-security-concerns-hikvision-dahua-market-126033000316_1.html
- PTC News, "India CCTV ban 2026: Hikvision, Dahua face STQC block as new security rules begin." https://www.ptcnews.tv/amp/nation/india-cctv-ban-hikvision-dahua-stqc-rules-2026-4422961
- Uyghur Human Rights Project, "Surveillance Tech Series: Dahua's Links to Human Rights Abuses in East Turkistan." https://uhrp.org/report/dahuas-links-to-human-rights-abuses-in-east-turkistan/

Introduction
Search engines have become indispensable in our daily lives, allowing us to find information instantly by entering keywords or phrases. Using the prompt "search Google or type a URL" reflects just how seamless this journey to knowledge has become. With millions of searches conducted every second, and Google handling over 6.3 million searches per minute as of 2023 (Statista), one critical question arises: do search engines prioritise results based on user preferences and past behaviours, or are they truly unbiased?
Understanding AI Bias in Search Algorithms
AI bias is also known as machine learning bias or algorithm bias. It refers to the occurrence of biased results due to human biases that deviate from the original training data or AI algorithm which leads to distortion of outputs and creation of potentially harmful outcomes. The sources of this bias are algorithmic bias, data bias and interpretation bias which emerge from user history, geographical data, and even broader societal biases in training data.
Common biases include excluding certain groups of people from opportunities because of AI bias. In healthcare, underrepresenting data of women or minority groups can skew predictive AI algorithms. While AI helps streamline the automation of resume scanning during a search to help identify ideal candidates, the information requested and answers screened out can result in biased outcomes due to a biased dataset or any other bias in the input data.
Case in Point: Google’s "Helpful" Results and Its Impact
Google optimises results by analysing user interactions to determine satisfaction with specific types of content. This data-driven approach forms ‘filter bubbles’ by repeatedly displaying content that aligns with a user’s preferences, regardless of factual accuracy. While this can create a more personalised experience, it risks confining users to a limited view, excluding diverse perspectives or alternative viewpoints.
The personal and societal impacts of such biases are significant. At an individual level, filter bubbles can influence decision-making, perceptions, and even mental health. On a societal level, these biases can reinforce stereotypes, polarise opinions, and shape collective narratives. There is also a growing concern that these biases may promote misinformation or limit users’ exposure to diverse perspectives, all stemming from the inherent bias in search algorithms.
Policy Challenges and Regulatory Measures
Regulating emerging technologies like AI, especially in search engine algorithms, presents significant challenges due to their intricate, proprietary nature. Traditional regulatory frameworks struggle to keep up with them as existing laws were not designed to address the nuances of algorithm-driven platforms. Regulatory bodies are pushing for transparency and accountability in AI-powered search algorithms to counter biases and ensure fairness globally. For example, the EU’s Artificial Intelligence Act aims to establish a regulatory framework that will categorise AI systems based on risk and enforces strict standards for transparency, accountability, and fairness, especially for high-risk AI applications, which may include search engines. India has proposed the Digital India Act in 2023 which will define and regulate High-risk AI.
Efforts include ethical guidelines emphasising fairness, accountability, and transparency in information prioritisation. However, a complex regulatory landscape could hinder market entrants, highlighting the need for adaptable, balanced frameworks that protect user interests without stifling innovation.
CyberPeace Insights
In a world where search engines are gateways to knowledge, ensuring unbiased, accurate, and diverse information access is crucial. True objectivity remains elusive as AI-driven algorithms tend to personalise results based on user preferences and past behaviour, often creating a biased view of the web. Filter bubbles, which reinforce individual perspectives, can obscure factual accuracy and limit exposure to diverse viewpoints. Addressing this bias requires efforts from both users and companies. Users should diversify sources and verify information, while companies should enhance transparency and regularly audit algorithms for biases. Together, these actions can promote a more equitable, accurate, and unbiased search experience for all users.
References
- https://www.bbc.com/future/article/20241101-how-online-photos-and-videos-alter-the-way-you-think
- https://www.bbc.com/future/article/20241031-how-google-tells-you-what-you-want-to-hear
- https://www.ibm.com/topics/ai-bias#:~:text=In%20healthcare%2C%20underrepresenting%20data%20of,can%20skew%20predictive%20AI%20algorithms

Introduction
Netflix is no stranger to its subscribers being targeted by SMS and email-led phishing campaigns. But the most recent campaign has been deployed at a global scale, affecting paid users in as many as 23 countries according to cybersecurity firm Bitdefender. In this particular campaign, attackers are using the carrot-and-stick tactic of either creating a false sense of urgency or promising rewards to steal financial information and Netflix credentials. For example, users may be contacted via SMS and told that their account is being suspended due to payment failures. A fake website may be shared through a link, encouraging the individual to share sensitive information to restore their account. Once this information has been input, it is now accessible to the attackers. This can create significant stress and even financial loss for its users. Thus, they are encouraged to develop the necessary skills to recognize and respond to these threats effectively.
How The Netflix Scam Works
Users are typically contacted through SMS. Bitdefender reports that these messages may look something like this:
"NETFLIX: There was an issue processing your payment. To keep your services active, please sign in and confirm your details at: https://account-details[.]com"
On clicking the link, the victim is directed to a website designed to mimic an authentic user experience interface, containing Netflix’s logo, color scheme, and grammatically-correct text. The website uses this interface to encourage the victim to divulge sensitive personal information, such as account credentials and payment details. Since this is a phishing website, the user’s personal information becomes accessible to the attacker as soon as it is entered. This information is then sold individually or in bundles on the dark web.
Practical Steps to Stay Safe
- Know Netflix’s Customer Interface: According to Netflix, it will never ask users to share personal information including credit or debit card numbers, bank account details, and Netflix passwords. It will also never ask for payment through a third-party vendor or website.
- Verify Authenticity: Do not open links from unknown sources sent by email or sms. If unsure, access Netflix directly by typing the URL into the browser instead of clicking on links in emails or texts. If the link has been opened, do not enter any information.
- Use Netflix’s Official Support Channels: Confirm any suspicious communication through Netflix’s verified help page or app. Write to phishing@netflix.com with any complaints about such an issue.
- Contact Your Financial Institution: If you have entered your personal information into a phishing website, you should immediately reach out to your bank to block your card and change your Netflix password. Contact the authorities via www.cybercrime.gov.in or by calling the helpline at 1930 in case of loss of funds.
- Use Strong Passwords and Enable MFA/2FA: Users are advised to use a unique, strong password with multiple characters. Enable Multi-Factor Authentication or Two Factor Authentication to your accounts, if available, to add an extra level of security.
Conclusion
Phishing campaigns which are designed to gather customer data through fraudulent means often involve sending links to as many users as possible, with the aim of monetizing stolen information. Attackers exploit user trust in online platforms to steal sensitive personal information, making such campaigns more sophisticated as highlighted above. This underscores the need for users of online platforms to practice good cyber hygiene by verifying information, learning to detect suspicious information and ignoring it, and staying aware of the types of online fraud they may be exposed to.
Sources
- https://www.bitdefender.com/en-gb/blog/hotforsecurity/netflix-scam-stay-safe
- https://help.netflix.com/en/node/65674
- https://timesofindia.indiatimes.com/technology/tech-news/netflix-users-beware-this-netflix-subscription-scam-is-active-in-23-countries-how-to-spot-one-and-stay-safe/articleshow/115820070.cms
