
#FactCheck- Old March Strike Video from Tehran Falsely Linked to Recent Iran–Israel Attacks
Executive Summary
Following recent escalations between Iran and Israel, where both countries reportedly exchanged missile strikes over the weekend, a video is now circulating on social media claiming to show the latest attacks between the two nations. However, CyberPeace Research Wing research found that the viral video is not related to the recent developments. The footage is actually from a March incident involving reported US-Israeli strikes in Tehran’s Jannat Abad area.
Claim
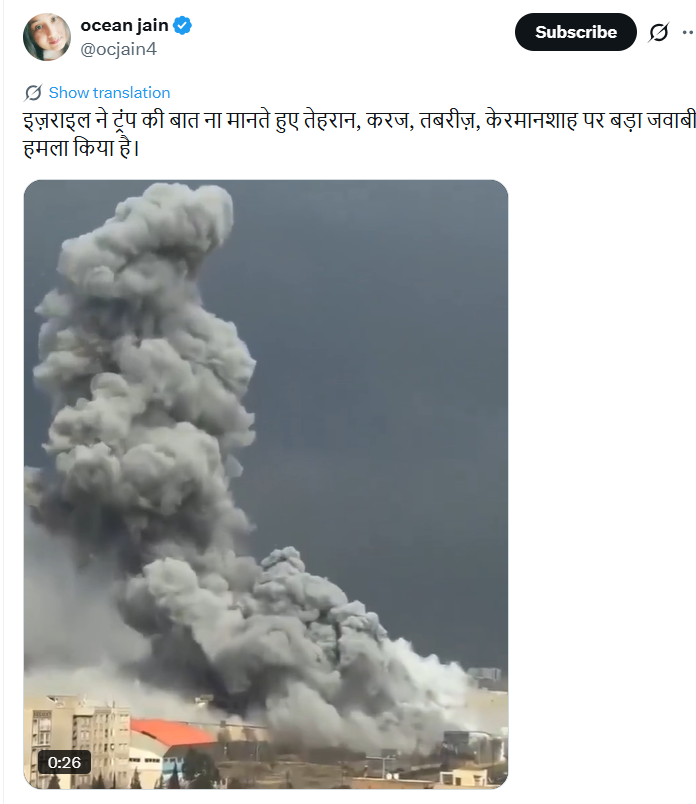
An X (formerly Twitter) user shared the viral video with the caption:“Israel, ignoring Trump’s advice, has carried out a major retaliatory strike on Tehran, Karaj, Tabriz, and Kermanshah.”
https://x.com/ocjain4/status/2063844698138239357?s=20
The video is being widely shared with claims that it shows recent Iran–Israel missile exchanges following Sunday’s reported attacks.
Fact Check
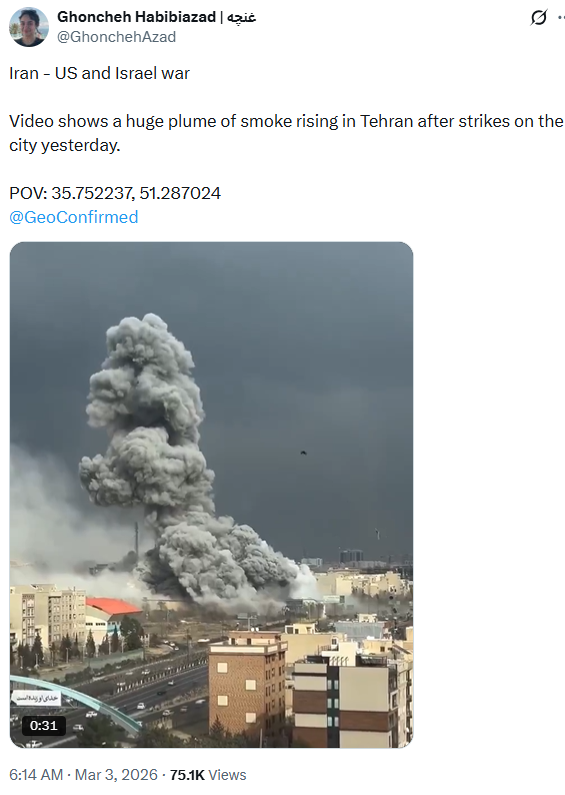
To verify the claim, we extracted keyframes from the viral video and conducted a reverse image search. The research led us to a post from BBC Persian journalist Ghoncheh Habibiazad’s X account dated 3 March. The video was shared with a caption describing it as showing a strike in Tehran attributed to US-Israeli action.
https://x.com/GhonchehAzad/status/2028632595156598874?s=20
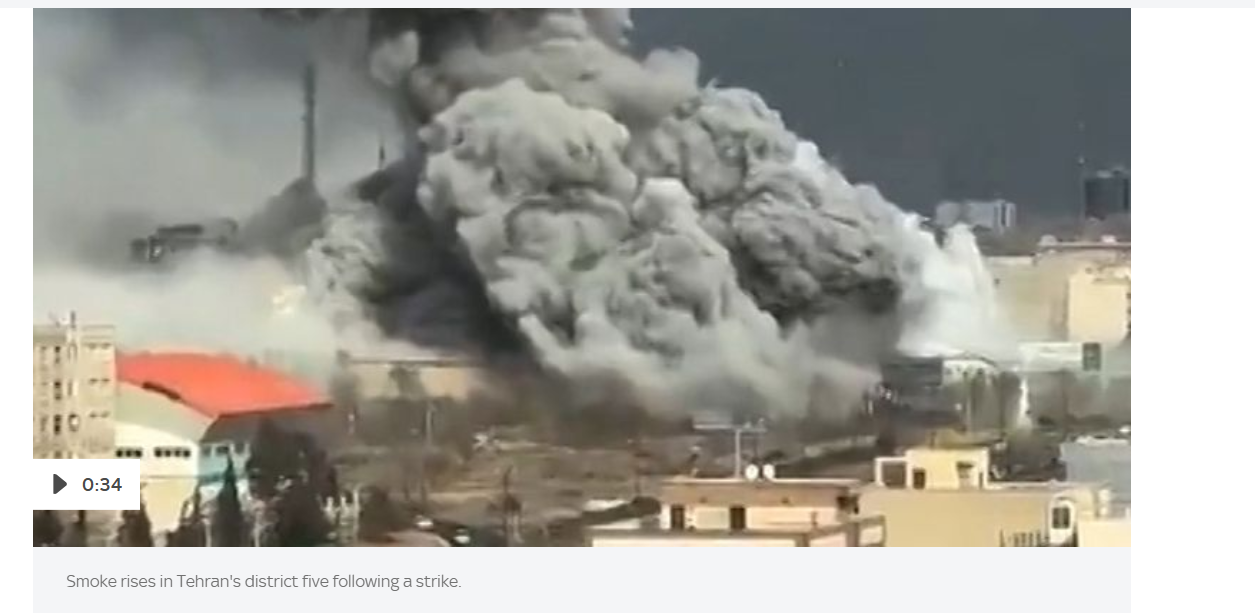
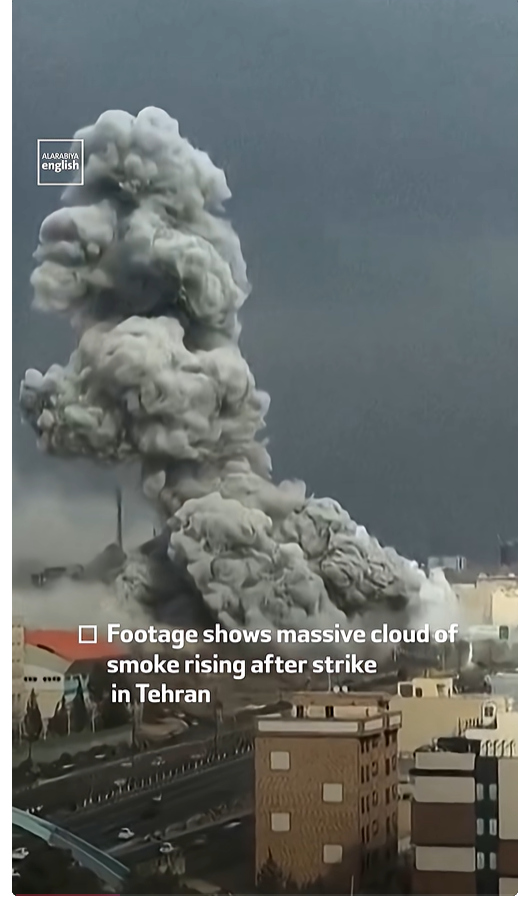
Further verification found the same footage published by Sky News and uploaded on Al Arabiya’s YouTube channel on 3 March 2026. The accompanying descriptions referred to smoke rising from Tehran’s District 5 and near the Hemmat Expressway following the strike.
https://news.sky.com/video/smoke-seen-rising-after-strike-in-tehran-13514731
https://www.youtube.com/shorts/AceFmYiBkuA
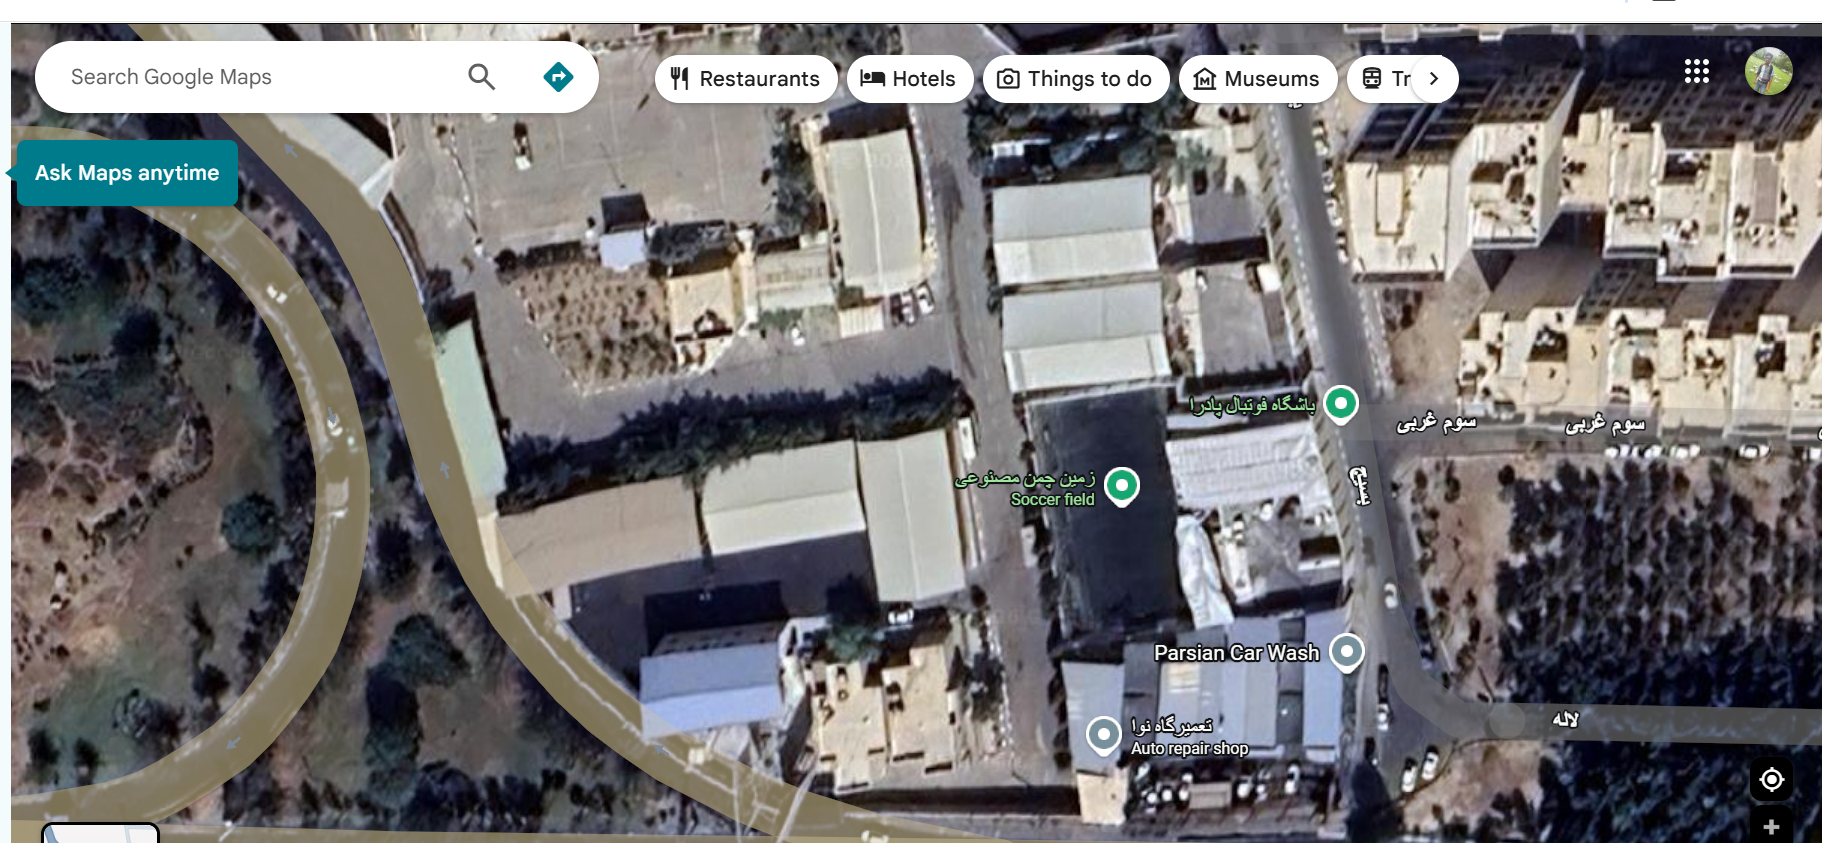
Additionally, a comparison using Google Satellite View confirmed that the location seen in the viral video matches the same area shown in the earlier March footage shared by BBC-affiliated reporting.
Conclusion
Our research confirms that the viral video has no connection to the recent Iran–Israel missile exchanges. The footage is from a March incident showing reported strikes in Tehran’s Jannat Abad area, and is being misleadingly shared as a recent escalation between the two countries.

Related Blogs

Introduction
Cybercrimes have been traversing peripheries and growing at a fast pace. Cybercrime is known to be an offensive action that either targets or operates through a computer, a computer network or a networked device, according to Kaspersky. In the “Era of globalisation” and a “Digitally coalesced world”, there has been an increase in International cybercrime. Cybercrime could be for personal or political objectives. Nevertheless, Cybercrime aims to sabotage networks for motives other than gain and be carried out either by organisations or individuals. Some of the cybercriminals have no national boundaries and are considered a global threat. They are likewise inordinately technically adept and operate avant-garde strategies.
The 2023 Global Risk Report points to exacerbating geopolitical apprehensions that have increased the advanced persistent threats (APTs), which are evolving globally as they are ubiquitous. Christine Lagarde, the president of the European Central Bank and former head of the International Monetary Fund (IMF), in 2020 cautioned that a cyber attack could lead to a severe economic predicament. Contemporary technologies and hazardous players have grown at an exceptional gait over the last few decades. Also, cybercrime has heightened on the agenda of nation-states, establishments and global organisations, as per the World Economic Forum (WEF).
The Role of the United Nations Ad Hoc Committee
In two shakes, the United Nations (UN) has a major initiative to develop a new and more inclusive approach to addressing cybercrime and is presently negotiating a new convention on cybercrime. The following convention seeks to enhance global collaboration in the combat against cybercrime. The UN has a central initiative to develop a unique and more inclusive strategy for addressing cybercrime. The UN passed resolution 74/247, which designated an open-ended ad hoc committee (AHC) in December 2019 entrusted with setting a broad global convention on countering the use of information and Communication Technologies (ICTs) for illicit pursuits.
The Cybercrime treaty, if adopted by the UN General Assembly (UNGA) would be the foremost imperative UN mechanism on a cyber point. The treaty could further become a crucial international legal framework for global collaboration on arraigning cyber criminals, precluding and investigating cybercrime. There have correspondingly been numerous other national and international measures to counter the criminal use of ICTs. However, the UN treaty is intended to tackle cybercrime and enhance partnership and coordination between states. The negotiations of the Ad Hoc Committee with the member states will be completed by early 2024 to further adopt the treaty during the UNGA in September 2024.
However, the following treaty is said to be complex. Some countries endorse a treaty that criminalises cyber-dependent offences and a comprehensive spectrum of cyber-enabled crimes. The proposals of Russia, Belarus, China, Nicaragua and Cuba have included highly controversial recommendations. Nevertheless, India has backed for criminalising crimes associated with ‘cyber terrorism’ and the suggestions of India to the UN Ad Hoc committee are in string with its regulatory strategy in the country. Similarly, the US, Japan, the UK, European Union (EU) member states and Australia want to include core cyber-dependent crimes.
Nonetheless, though a new treaty could become a practical instrument in the international step against cybercrime, it must conform to existing global agencies and networks that occupy similar areas. This convention will further supplement the "Budapest Cybercrime Convention" on cybercrime that materialised in the 1990s and was signed in Budapest in the year 2001.
Conclusion
According to Cyber Security Ventures, global cybercrime is expected to increase by 15 per cent per year over the next five years, reaching USD 10.5 trillion annually by 2025, up from USD 3 trillion in 2015. The UN cybercrime convention aims to be more global. That being the case, next-generation tools should have state-of-the-art technology to deal with new cyber crimes and cyber warfare. The global crevasse in nation-states due to cybercrime is beyond calculation. It could lead to a great cataclysm in the global economy and threaten the political interest of the countries on that account. It is crucial for global governments and international organisations. It is necessary to strengthen the collaboration between establishments (public and private) and law enforcement mechanisms. An “appropriately designed policy” is henceforward the need of the hour.
References
- https://www.kaspersky.co.in/resource-center/threats/what-is-cybercrime
- https://www.cyberpeace.org/
- https://www.interpol.int/en/Crimes/Cybercrime
- https://www.bizzbuzz.news/bizz-talk/ransomware-attacks-on-startups-msmes-on-the-rise-in-india-cyberpeace-foundation-1261320
- https://www.financialexpress.com/business/digital-transformation-cyberpeace-foundation-receives-4-million-google-org-grant-3282515/
- https://www.chathamhouse.org/2023/08/what-un-cybercrime-treaty-and-why-does-it-matter
- https://www.weforum.org/agenda/2023/01/global-rules-crack-down-cybercrime/
- https://www.weforum.org/publications/global-risks-report-2023/
- https://www.imf.org/external/pubs/ft/fandd/2021/03/global-cyber-threat-to-financial-systems-maurer.htm
- https://www.eff.org/issues/un-cybercrime-treaty#:~:text=The%20United%20Nations%20is%20currently,of%20billions%20of%20people%20worldwide.
- https://cybersecurityventures.com/hackerpocalypse-cybercrime-report-2016/
- https://www.coe.int/en/web/cybercrime/the-budapest-convention
- https://economictimes.indiatimes.com/tech/technology/counter-use-of-technology-for-cybercrime-india-tells-un-ad-hoc-group/articleshow/92237908.cms?utm_source=contentofinterest&utm_medium=text&utm_campaign=cppst
- https://consultation.dpmc.govt.nz/un-cybercrime-convention/principlesandobjectives/supporting_documents/Background.pdf
- https://unric.org/en/a-un-treaty-on-cybercrime-en-route/
Executive Summary
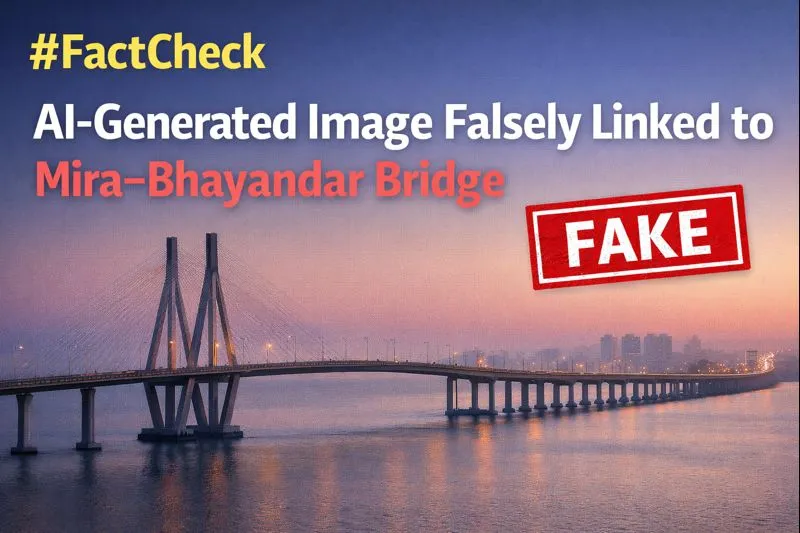
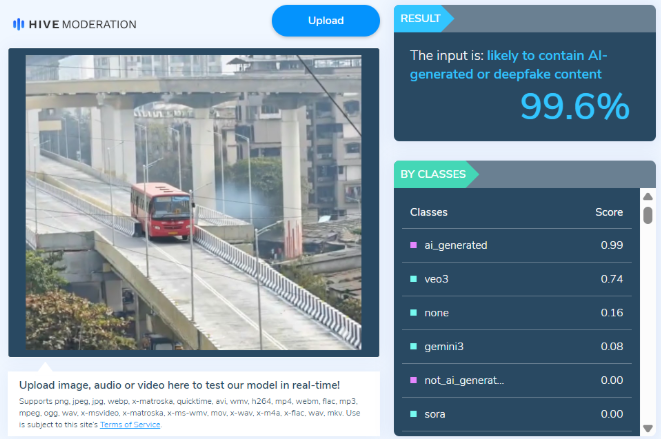
Mumbai’s Mira–Bhayandar bridge has recently been in the news due to its unusual design. In this context, a photograph is going viral on social media showing a bus seemingly stuck on the bridge. Some users are also sharing the image while claiming that it is from Sonpur subdivision in Bihar. However, an research by the CyberPeace has found that the viral image is not real. The bridge shown in the image is indeed the Mira–Bhayandar bridge, which is under discussion because its design causes it to suddenly narrow from four lanes to two lanes. That said, the bridge is not yet operational, and the viral image showing a bus stuck on it has been created using Artificial Intelligence (AI).
Claim
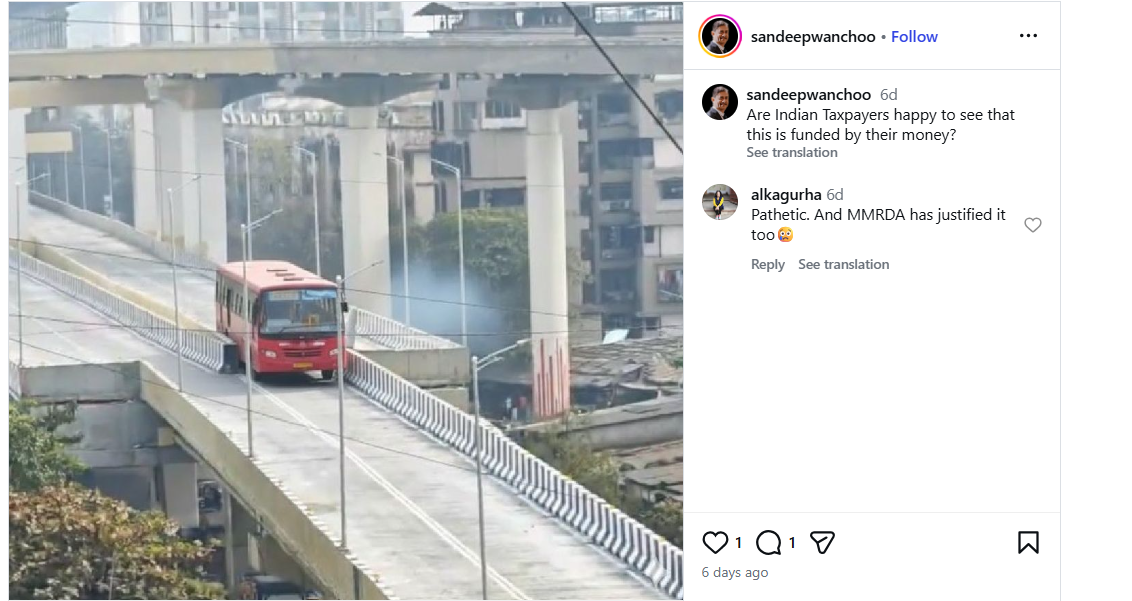
An Instagram user shared the viral image on January 29, 2026, with the caption:“Are Indian taxpayers happy to see that this is funded by their money?” The link, archive link, and screenshot of the post can be seen below.
Fact Check:
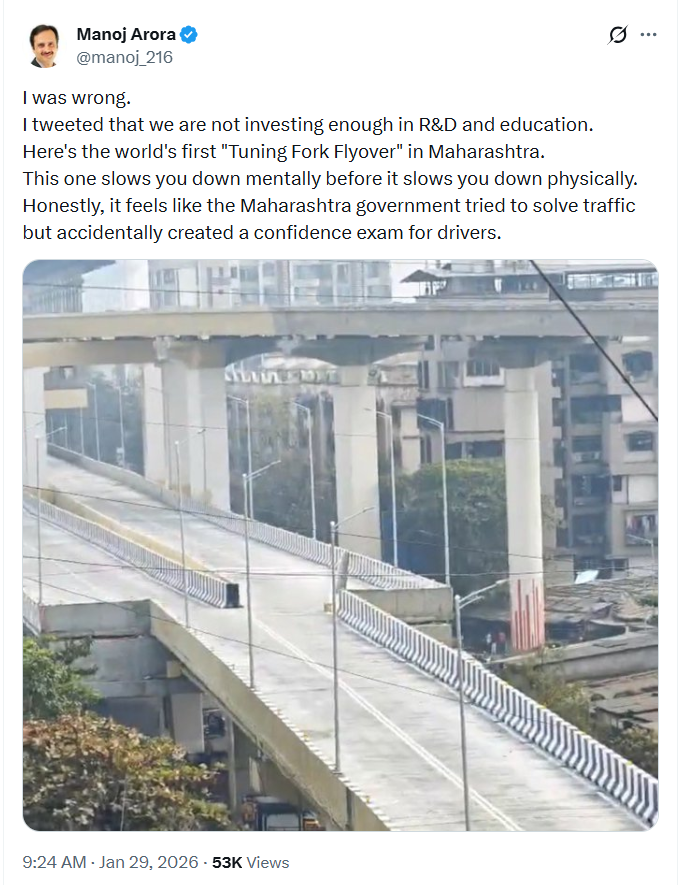
To verify the claim, we first conducted a Google Lens reverse image search. This led us to a post shared by X (formerly Twitter) user Manoj Arora on January 29. While the bridge structure in that image matches the viral photo, no bus is visible in the original post.This raised suspicion that the viral image had been digitally manipulated.
We then ran the viral image through the AI detection tool Hive Moderation, which flagged it as over 99% likely to be AI-generated
Conclusion
The CyberPeace research confirms that while the Mira–Bhayandar bridge is real and has been in the news due to its design, the viral image showing a bus stuck on the bridge has been created using AI tools. Therefore, the image circulating on social media is misleading.

Overview:
‘Kia Connect’ is the application that is used to connect ‘Kia’ cars which allows the user control various parameters of the vehicle through the application on his/her smartphone. The vulnerabilities found in most Kias built after 2013 with but little exception. Most of the risks are derived from a flawed API that deals with dealer relations and vehicle coordination.
Technical Breakdown of Exploitation:
- API Exploitation: The attack uses the vulnerabilities in Kia’s dealership network. The researchers also noticed that, for example, the logs generated while impersonating a dealer and registering on the Kia dealer portal would be sufficient for deriving access tokens needed for next steps.
- Accessing Vehicle Information: The license plate number allowed the attackers to get the Vehicle Identification Number (VIN) number of their preferred car. This VIN can then be used to look up more information about the car and is an essential number to determine for the shared car.
- Information Retrieval: Having the VIN number in hand, attackers can launch a number of requests to backends to pull more sensitive information about the car owner, including:
- Name
- Email address
- Phone number
- Geographical address
- Modifying Account Access: With this information, attackers could change the accounts settings to make them a second user on the car, thus being hidden from the actual owner of the account.
- Executing Remote Commands: Once again, it was discovered that attackers could remotely execute different commands on the vehicle, which includes:some text
- Unlocking doors
- Starting the engine
- Monitoring the location of the vehicle in terms of position.
- Honking the horn
Technical Execution:
The researchers demonstrated that an attacker could execute a series of four requests to gain control over a Kia vehicle:
- Generate Dealer Token: The attacker sends an HTTP request in order to create a dealer token.
- Retrieve Owner Information: As indicated using the generated token, they make another request to another endpoint that returns the owner’s email address and phone number.
- Modify Access Permissions: The attacker takes advantage of the leaked information (email address and VIN) of the owner to change between users accounts and make himself the second user.
- Execute Commands: As the last one, they can send commands to perform actions on the operated vehicle.
Security Response and Precautionary Measures for Vehicle Owners
- Regular Software Updates: Car owners must make sure their cars receive updates on the recent software updates provided by auto producers.
- Use Strong Passwords: The owners of Kia Connect accounts should develop specific and complex passwords for their accounts and then update them periodically. They should avoid using numbers like the birth dates, vehicle numbers and simple passwords.
- Enable Multi-Factor Authentication: For security, vehicle owners should turn on the use of the secondary authentication when it is available to protect against unauthorized access to an account.
- Limit Personal Information Sharing: Owners of vehicles should be careful with the details that are connected with the account on their car, like the e-mail or telephone number, sharing them on social networks, for example.
- Monitor Account Activity: It is also important to monitor the account activity because of change or access attempts that are unauthorized. In case of any abnormality or anything suspicious felt while using the car, report it to Kia customer support.
- Educate Yourself on Vehicle Security: Being aware of cyber threats that are connected to vehicles and learning about how to safeguard a vehicle from such threats.
- Consider Disabling Remote Features When Not Needed: If remote features are not needed, then it is better to turn them off, and then turn them on again when needed. This can prove to help diminish the attack vector for would-be hackers.
Industry Implications:
The findings from this research underscore broader issues within automotive cybersecurity:
- Web Security Gaps: Most car manufacturers pay more attention to equipment running in automobiles instead of the safety of the websites that the car uses to operate thereby exposing automobiles that are connected very much to risks.
- Continued Risks: Vehicles become increasingly connected to internet technologies. Auto makers will have to carry cyber security measures in their cars in the future.
Conclusion:
The weaknesses found in Kia’s connected car system are a key concern for Automotive security. Since cars need web connections for core services, suppliers also face the problem of risks and need to create effective safeguards. Kia took immediate actions to tighten the safety after disclosure; however, new threats will emerge as this is a dynamic domain involving connected technology. With growing awareness of these risks, it is now important for car makers not only to put in proper security measures but also to maintain customer communication on how it safeguards their information and cars against cyber dangers. That being an incredibly rapid approach to advancements in automotive technology, the key to its safety is in our capacity to shield it from ever-present cyber threats.
Reference:
- https://timesofindia.indiatimes.com/auto/cars/hackers-could-unlock-your-kia-car-with-just-a-license-plate-is-yours-safe/articleshow/113837543.cms
- https://www.thedrive.com/news/hackers-found-millions-of-kias-could-be-tracked-controlled-with-just-a-plate-number
- https://www.securityweek.com/millions-of-kia-cars-were-vulnerable-to-remote-hacking-researchers/
- https://news24online.com/auto/kia-vehicles-hack-connected-car-cybersecurity-threat/346248/
- https://www.malwarebytes.com/blog/news/2024/09/millions-of-kia-vehicles-were-vulnerable-to-remote-attacks-with-just-a-license-plate-number
- https://informationsecuritybuzz.com/kia-vulnerability-enables-remote-acces/
- https://samcurry.net/hacking-kia
