
#FactCheck: Viral Video Falsely Linked to Delhi Police Assault on Female Journalist Is From a Movie Shoot
Executive Summary
A video is being widely shared on social media with the claim that a female journalist was assaulted by the Delhi Police. The video is being shared with the claim that a female police officer from the Delhi Police is seen assaulting and misbehaving with a female journalist. In the video, a woman wearing a police uniform can be seen allegedly assaulting another woman. Research by the Research Wing of CyberPeace found that the video is actually from a movie shoot. Social media users are sharing it with a misleading claim.
Claim
Social media users shared the video with the caption: “A female journalist is being beaten up by the Delhi Police. What will happen to ordinary people?”
https://www.facebook.com/reel/1599067985010003
https://archive.ph/mgCqt

Fact Check
While investigating the video being shared with the claim that a female journalist was assaulted by the Delhi Police, we conducted a reverse image search of its keyframes. During the search, we found the same video on a Facebook page called ‘CineEdge Media-Behind the Scenes’. The video was uploaded on the page on June 26, 2026. The description and hashtags used with the video indicate that it is not footage of an actual police action, but is related to a film shoot.
https://www.facebook.com/reel/1542614027395118

In addition, the bio of the aforementioned Facebook page states that it posts videos featuring film acting sequences, action thrillers, and behind-the-scenes footage from movies
https://www.facebook.com/profile.php?id=61578948364025&sk=reels_tab
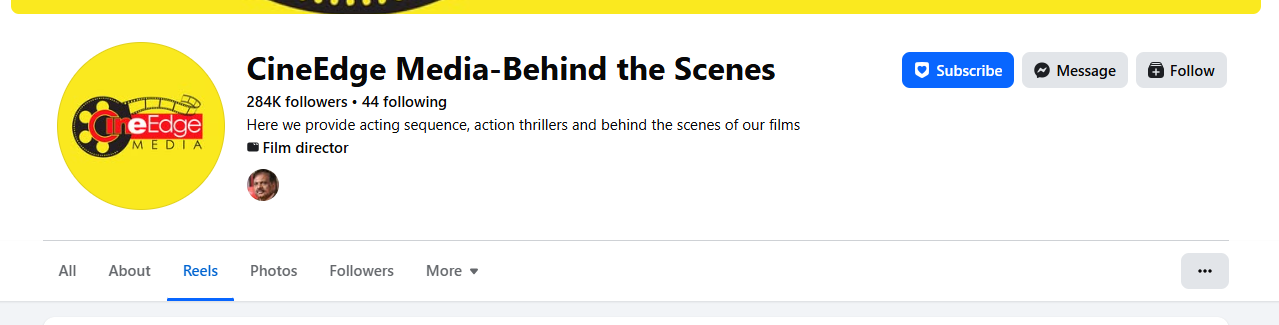
As part of the research, we also examined the CineEdge Media YouTube account. We found that the account has uploaded videos related to films and acting

Conclusion
The evidence gathered during our research makes it clear that the video being shared with the claim that a female journalist was assaulted by the Delhi Police is actually footage from a movie shoot. The video was found on a social media page that shares film-related content, including acting sequences, action scenes and behind-the-scenes footage. Therefore, the claim that the video shows a female journalist being assaulted by the Delhi Police is misleading.

Related Blogs

Introduction
As the sun rises on a new chapter in the Indian telecommunications narrative, the corridors of power in New Delhi are abuzz with palpable excitement and a hint of solemnity. Here, a groundbreaking proposal stands before the lawmakers of the Lok Sabha, not simply a proposed amendment or update to an existing statute, but the cornerstone of a reimagined communications epoch—the Telecommunications Bill of 2023. In every sense, this legislative masterpiece embodies a country at the intersection of tradition and innovation, eager to part ways with vestiges of colonial infrastructure that have shaped its modern landscape.
The Origins
Steeped in history, India's telecommunications system has persevered through a patchwork of regulations and ad hoc policies, growing somewhat unwieldy under the shadow of the Indian Telegraph Act (1885), the Wireless Telegraphy Act (1933), and the Telegraph Wires (Unlawful Possession) Act (1950). Yet, it is within this context of the old guard, a relic of British administration, that the new Telecommunications Bill seeks to transcend the limitations of the past. It aims to dismantle barriers and create an ecosystem that is fluid, adaptable, and resonant with the rapid cadence of technological advancements and the demands of a population increasingly reliant on digital connectivity.
In crafting this bill, the creators have meticulously knitted together an intricate fabric of vibrant threads, each signifying a pillar of progress. To herald an era of unparalleled growth and dynamism, the bill looks beyond the scope of traditional telecommunication services, boldly embracing the convergence of digital mediums such as wire, radio, and optical fibers, aligning with the modalities of 21st-century communication. The bill’s very essence is innovation, etching a new paradigm through its provisions and signalling India's readiness to interface with the ever-expanding digital frontier.
The Defining Features
A novel and defining feature of this bill is its departure from a rigid licensing regime. It forges ahead with 'authorizations'—a signifier that resonates with flexibility, adaptability, and a regulatory approach that isn't mired in bureaucratic inertia but is rather an enabler of swift technological adoption and market responsiveness. This transformative philosophy signifies a departure from the byzantine processes of yore, orbiting instead toward an agile governance model that is both responsive to current needs and anticipative of future trends.
The introduction of mandatory biometric authentication for telecom customers articulates an unyielding stance against the rampant misuse of communication networks. Indeed, this measure draws a fine line between the right to privacy and the exigencies of data protection, posing ethical questions that animate public discourse. This balance seeks to thwart unsolicited commercial communication, exemplifying the state's vigil on the sanctuaries of personal space and tranquility.
In addition, the forward-looking bill tactically addresses the strategic use of spectrum resources with an undercurrent of prescience. By granting ‘spectrum assets’ legislative stature through the National Frequency Allocation Plan and enabling operators to adapt through 'refarming', the bill forms a visionary blueprint for resource optimization. It inherently recognizes that bandwidth is not simply a commercial commodity but one that serves the wider canvas of national imperatives, connectivity goals, and developmental aspirations.
Further embodying the dual themes of openness and vigilance, the bill incorporates provisions for interception and the implementation of a 'trusted sources' regime, a tacit acknowledgement of the cybersecurity challenges that loom on the horizon amidst increasing geopolitical strains. These measures exemplify the act of walking a tightrope between the democratic ideals of transparency and the unyielding requirements of state security.
Looking to the skies, the bill embraces satellite technologies, foreseeing their potential in unshackling the remote and marginalized areas from the constraints of terrestrial infrastructure and thus forging a digitally inclusive society. Acknowledging the expanse of the Indian subcontinent, the bill paves the way for an interconnected, digital hinterland via thoughtful satellite spectrum allocations.
Emphasizing the human thread in the digital weave, the reformulation of the Universal Service Obligation Fund into 'Digital Bharat Nidhi' underscores an unwavering commitment to reaching the unreached. It's the crystallization of a promise that every Indian, regardless of geographical and socio-economic divides, will be privy to the lenses of opportunity presented by the digital revolution.
The Watershed Moment
The introduction of the Telecommunications Bill of 2023 is a watershed moment, a convergence where history and opportunity coalesce, propelling a nation forward with the ambitions of a burgeoning superpower replacing the Indian Telegraph Act (1885), the Wireless Telegraphy Act (1933), and the Telegraph Wires (Unlawful Possession) Act (1950). It carries within its articles and clauses the anticipation of a billion dreams, the catalyst to a regulatory environment that nurtures innovation, equality, and a forward leap into the future.
Conclusion
Through its comprehensive scope and visionary approach, the bill writes a fresh chapter in India's digital saga. It is an unfolding story, pregnant with the possibilities of a nascent digital age, charting a trajectory for an India poised to define its own digital dome of the sky, under which its citizens will thrive for generations to come. With every legislative step, India crafts its legacy, a narrative of evolution, a tableau that reflects the aspirations of its people and their resolve to embrace the force of technology for the collective good. As this bill advances through the legislative labyrinth, it carries the spirit of a digital renaissance nestled in the heart of the world's largest democracy.
References

Introduction
Rapid growth in India’s Digital Economy has opened up various options for companies to utilise digital technology as part of their operations. Examples of these technologies include cloud computing; online payment systems; digitally enabled supply chains; and platforms that facilitate remote working. As small and medium enterprises(SMEs) represent a major part of India’s economy, they have quickly been able to capitalise on the benefits these technologies provide in improving their operational efficiency and developing an increased presence within the market. However, this rapid pace of digitalisation creates an exposure to a much greater breadth of cyber-security threats than ever for SMEs. Today, perhaps the greatest cyber-threat facing SMEs in India is ransomware, an increasing frequent type of cyber-attack that has been increasing on a global scale over the past few years and in response, there have been numerous initiatives by various government agencies, industry organisations, and cyber-security firms designed to educate the general public on the risks of ransomware.
What is Ransomware?
Ransomware is a type of malware, which prevents all users being able to access their file system or access their data until they pay a ransom. In a standard ransomware event an attacker will breach the company's network, and encrypt all critical files so that they are unable to be used. The attacker usually demands payment in bitcoin because it is a difficult trace and promises to provide a key to unlock the data in exchange for the payment. Attackers gain access to company networks by using social engineering techniques such as phishing email, stolen password, or exploiting an unpatched vulnerability in the software that is running on the company's network.
The Rising Threat of Ransomware
Cybercriminals have created one of the most destructive varieties of cybercrimes around the world through ransomware; while experts in the cybersecurity field project losses to global ransomware damage may reach $30 billion by 2025. There has also been a marked increase in SMEs being attacked by ransomware-based cybercriminals throughout India. NASSCOM has done research and found that many SMEs in India have experienced attempted ransomware attacks in the past few years alone. According to incident reports provided through CERT-In, there has been a noticeable increase in the number of cybercrime occurrences throughout different sectors of India’s economy since those reports began. These developments have shown an increase in the size and level of sophistication of ransomware related threats.
Why Indian SMEs Remain Vulnerable Despite Awareness
Despite increased awareness about cyber threats, there is a large number of Indian SMEs that continue to be vulnerable to ransomware. The main reason is financial limitations. Many small businesses typically have limited financial resources and those limited resources more often than not, go towards operations, including production, logistics, and marketing - cybersecurity costs are usually viewed as additional costs.
Another significant problem facing SMEs is a shortage of skilled cybersecurity professionals. Large enterprises typically have dedicated security teams responsible for protecting the enterprise, whereas SMEs will employ IT staff generally without any specific expertise in detecting/countering cyber threats. Human error are also significant contributors to these cyber incursion events. An employee can inadvertently click on an email link or download an infected attachment, or use a weak password - all of which could provide opportunities for cybercriminals to access the company's network. Phishing emails continue to be the most common approach for initiating ransomware.
Furthermore - many SMEs have implemented digital platforms, such as cloud-based applications and payment processing, without appropriately executing cybersecurity planning prior to implementation. Many of the issues that have arisen from such rapid digitisation are due to a lack of sufficient planned cybersecurity measures as part of the implementation process. This has also resulted in a situation where technological advancements such as Ransomware as a Service (RaaS) have created an even larger pool of potential perpetrators (cybercriminals) with little-to-no expertise being able to launch a widespread ransomware campaign using readily available/pre-manufactured tools.
Real-World Cyber Incidents Affecting Indian SMEs
As several examples recently demonstrate, Indian SMEs continue to experience significant cyber attack risks. Recently, a logistics firm located in Gurugram found itself locked out of nearly 4,000 shipments due to a ransomware attack, which cost them ₹12 lakhs to fix because they had poor backups and another incident in Gurugram which highlights how vulnerable many SMEs in the country continue to be to ransomware attacks. In the case of a garments company, a hacker compromised the company's server by placing ransomware on its system. The company was forced to shut down its computerised warehouse system as a result of the attack. Only after the company had lost access to its system, did it receive a ransom demand from the hacker, in the form of an email requesting payment of 15 bitcoins (approximately ₹25 lakh), in order for the hacker to restore the company's access to the system. The hacker also threatened to delete the company's financial and banking records if the ransom were not paid. Gurgaon Police's Cyber Cell received the report of the incident, and registered a first information report (FIR) against unknown hackers. The case represents an opportunity for SMEs to evaluate the risks associated with ransomware.
Bridging the Gap Between Awareness and Implementation
Although awareness campaigns can show organisations what types of cybersecurity risks they’re exposed to, these campaigns will not keep businesses from being victims of a ransomware attack by themselves.. The most critical step forward is the implementation of the principles of cybersecurity from an understanding viewpoint to that of an active action. Organisations need to go beyond being aware of the risks related to cyber and then put measures in place to mitigate those risks.
To improve cybersecurity, organisations may need to spend money on developing and maintaining systems; set up regular training for employees on handling cyber threats and implementing an incident response plan to address security incidents; back up data regularly; maintain the hardware and software used in the organisation's computer systems at least once a month (or more often if necessary); and monitor all aspects of its computer systems continuously for weaknesses or problems.
The Way Forward: Strengthening SME Cybersecurity
In order to truly address the ransomware threat, collaboration by businesses, government agencies and cyber security professionals is mandatory. One of the biggest roles in this collaboration is through governmental initiatives to enhance the overall level of awareness of digital security among SMEs (small to medium-sized enterprises). Improved SME understanding of cyber risks will be based on the availability of affordable security solutions that are specifically tailored for small businesses.
Industry partnerships as well as public-private partnerships also aid the sharing of threat intelligence to strengthen collaborative defense against all cybercriminal activity.
Conclusion
Despite Indian SMEs being aware of cyber threats, they have been unable to implement safeguards or Cyber Security plans due to limited financial resources, insufficient qualified personnel, human errors, and the rapid pace at which digital technology is being adopted without adequate Cyber Security measures. In order to respond effectively to the growing threat of Ransomware, Indian SMEs must evolve from being aware of cyber threats to proactively developing Cyber Security strategies that will allow them to prevent, prepare for, and recover from the increased cyber threat posed by the rapidly growing digitalisation of business within an increasingly globalised economy.
References
- https://www.ibm.com/think/topics/ransomware
- https://primeinfoserv.com/indias-sme-cybersecurity-crisis-real-incidents-real-lessons-2024-2025/
- https://timesofindia.indiatimes.com/city/gurgaon/ransomware-attack-on-apparel-firm-all-data-lost/articleshow/59496777.cms#
- https://ciso.economictimes.indiatimes.com/news/cybercrime-fraud/indian-businesses-face-nearly-700-ransomware-attacks-per-day-kaspersky/120471668
- https://smestreet.in/msmenews/indian-smes-remain-alarmingly-exposed-to-ransomware-threats-sophos-report-2025-9456628
- https://m.economictimes.com/news/how-to/how-can-indian-smes-combat-ransomware-attacks/articleshow/108047111.cms

Introduction
The unprecedented cyber espionage attempt on the Indian Air Force has shocked the military fraternity in the age of the internet where innovation is vital to national security. The attackers have shown a high degree of expertise in their techniques, using a variant of the infamous Go Stealer and current military acquisition pronouncements as a cover to obtain sensitive information belonging to the Indian Air Force. In this recent cyber espionage revelation, the Indian Air Force faces a sophisticated attack leveraging the infamous Go Stealer malware. The timing, coinciding with the Su-30 MKI fighter jets' procurement announcement, raises serious questions about possible national security espionage actions.
A sophisticated attack using the Go Stealer malware exploits defense procurement details, notably the approval of 12 Su-30 MKI fighter jets. Attackers employ a cunningly named ZIP file, "SU-30_Aircraft_Procurement," distributed through an anonymous platform, Oshi, taking advantage of heightened tension surrounding defense procurement.
Advanced Go Stealer Variant:
The malware, coded in Go language, introduces enhancements, including expanded browser targeting and a unique data exfiltration method using Slack, showcasing a higher level of sophistication.
Strategic Targeting of Indian Air Force Professionals:
The attack strategically focuses on extracting login credentials and cookies from specific browsers, revealing the threat actor's intent to gather precise and sensitive information.
Timing Raises Espionage Concerns:
The cyber attack coincides with the Indian Government's Su-30 MKI fighter jets procurement announcement, raising suspicions of targeted attacks or espionage activities.
The Deceitful ZIP ArchiveSU-30 Aircraft Acquisition
The cyberattack materialised as a sequence of painstakingly planned actions. Using the cleverly disguised ZIP file "SU-30_Aircraft_Procurement," the perpetrators took benefit of the authorisation of 12 Su-30 MKI fighter jets by the Indian Defense Ministry in September 2023. Distributed via the anonymous file storage network Oshi, the fraudulent file most certainly made its way around via spam emails or other forms of correspondence.
The Spread of Infection and Go Stealer Payload:
The infiltration procedure progressed through a ZIP file to an ISO file, then to a.lnk file, which finally resulted in the Go Stealer payload being released. This Go Stealer version, written in the programming language Go, adds sophisticated capabilities, such as a wider range of browsing focussed on and a cutting-edge technique for collecting information using the popular chat app Slack.
Superior Characteristics of the Go Stealer Version
Different from its GitHub equivalent, this Go Stealer version exhibits a higher degree of complexity. It creates a log file in the machine owned by the victim when it is executed and makes use of GoLang utilities like GoReSym for in-depth investigation. The malware focuses on cookies and usernames and passwords from web browsers, with a particular emphasis on Edge, Brave, and Google Chrome.
This kind is unique in that it is more sophisticated. Its deployment's cyber enemies have honed its strengths, increasing its potency and detection resistance. Using GoLang tools like GoReSym for comprehensive evaluation demonstrates the threat actors' careful planning and calculated technique.
Go Stealer: Evolution of Threat
The Go Stealer first appeared as a free software project on GitHub and quickly became well-known for its capacity to stealthily obtain private data from consumers who aren't paying attention. Its effectiveness and stealthy design rapidly attracted the attention of cyber attackers looking for a sophisticated tool for clandestine data exfiltration. It was written in the Go programming language.
Several cutting-edge characteristics distinguish the Go Stealer from other conventional data thieves. From the beginning, it showed a strong emphasis on browser focusing on, seeking to obtain passwords and login information from particular websites including Edge, Brave, and Google Chrome.The malware's initial iteration was nurtured on the GitHub database, which has the Go Stealer initial edition. Threat actors have improved and altered the code to serve their evil goals, even if the basic structure is freely accessible.
The Go Stealer version that has been discovered as the cause of the current internet spying by the Indian Air Force is not limited to its GitHub roots. It adds features that make it more dangerous, like a wider range of browsers that may be targeted and a brand-new way to exfiltrate data via Slack, a popular messaging app.
Secret Communications and Information Expulsion
This variation is distinguished by its deliberate usage of the Slack API for secret chats. Slack was chosen because it is widely used in company networks and allows harmful activity to blend in with normal business traffic. The purpose of the function "main_Vulpx" is specifically to upload compromised information to the attacker's Slack route, allowing for covert data theft and communication.
The Time and Strategic Objective
There are worries about targeted assaults or espionage activities due to the precise moment of the cyberattack, which coincides with the Indian government's declaration of its acquisition of Su-30 MKI fighter fighters. The deliberate emphasis on gathering cookies and login passwords from web browsers highlights the threat actor's goal of obtaining accurate and private data from Indian Air Force personnel.
Using Caution: Preventing Possible Cyber Espionage
- Alertness Against Misleading Techniques: Current events highlight the necessity of being on the lookout for files that appear harmless but actually have dangerous intent. The Su-30 Acquisition ZIP file is a stark illustration of how these kinds of data might be included in larger-scale cyberespionage campaigns.
- Potentially Wider Impact: Cybercriminals frequently plan coordinated operations to target not just individuals but potentially many users and government officials. Compromised files increase the likelihood of a serious cyber-attack by opening the door for larger attack vectors.
- Important Position in National Security: Recognize the crucial role people play in the backdrop of national security in the age of digitalisation. Organised assaults carry the risk of jeopardising vital systems and compromising private data.
- Establish Strict Download Guidelines: Implement a strict rule requiring file downloads to only come from reputable and confirmed providers. Be sceptical, particularly when you come across unusual files, and make sure the sender is legitimate before downloading any attachments.
- Literacy among Government Employees: Acknowledge that government employees are prime targets as they have possession of private data. Enable people by providing them with extensive cybersecurity training and awareness that will increase their cognition and fortitude.
Conclusion
Indian Air Force cyber surveillance attack highlights how sophisticated online dangers have become in the digital era. Threat actors' deliberate and focused approach is demonstrated by the deceptive usage of a ZIP archive that is camouflaged and paired with a sophisticated instance of the Go Stealer virus. An additional level of complication is introduced by integrating Slack for covert communication. Increased awareness, strict installation guidelines, and thorough cybersecurity education for government employees are necessary to reduce these threats. In the digital age, protecting national security necessitates ongoing adaptation as well as safeguards toward ever-more potent and cunning cyber threats.
References
- https://www.overtoperator.com/p/indianairforcemalwaretargetpotential
- https://cyberunfolded.in/blog/indian-air-force-targeted-in-sophisticated-cyber-attack-with-su-30-procurement-zip-file#go-stealer-a-closer-look-at-its-malicious-history
- https://thecyberexpress.com/cyberattack-on-the-indian-air-force/https://therecord.media/indian-air-force-infostealing-malware
