
#FactCheck - Old Rajnath Singh Video Falsely Linked To NEET-UG 2026 Paper Leak Controversy
Executive Summary
The Central Bureau of research (CBI) is currently probing the alleged leak of the NEET-UG 2026 examination paper, and several accused persons have already been arrested in connection with the case. Amid this, a video of senior BJP leader and Defence Minister Rajnath Singh is being widely shared on social media. In the clip, he is heard saying, “There will be no resignations. This is not a UPA government, this is an NDA government.” Several users linked the video to the NEET controversy and claimed that Rajnath Singh made the remark while responding to demands for Education Minister Dharmendra Pradhan’s resignation over the alleged paper leak. However, research by the CyberPeace Research Wing found the viral claim to be false. An old video of Rajnath Singh is being misleadingly shared with a false context.
Claim
A Facebook user named “Ravi Kumar Huddi Baba” shared the viral clip on May 13, 2026, claiming that Rajnath Singh was defending the Modi government over demands for the resignation of the education minister in the NEET-UG paper leak case.

Fact Check
To verify the claim, relevant keyword searches were carried out using Google Open Search tools. No credible news reports were found confirming that Rajnath Singh had made any such statement regarding the NEET controversy or demands for Dharmendra Pradhan’s resignation. Had such a statement been made recently, it would likely have been widely reported by mainstream media outlets. A review of Rajnath Singh’s official social media accounts also yielded no such statement or video related to the NEET issue.
During the research, the full version of the viral clip was traced to an old press conference held on June 24, 2015, where Rajnath Singh and then Union Minister Ravi Shankar Prasad were briefing the media about Cabinet decisions. During the interaction, a journalist questioned them regarding resignations linked to controversies at the time. Responding to the question, Rajnath Singh made the now-viral remark. The complete press conference video is available on the BJP’s official YouTube channel and was streamed on June 24, 2015 itself. The viral portion can be heard after the 23-minute mark in the video.

Further searches led to an old report published by Navbharat Times on June 24, 2015. The report stated that Rajnath Singh had made the “NDA, not UPA” remark while responding to questions regarding ministers embroiled in controversies at that time.
Conclusion
The viral claim is false. Rajnath Singh has not made any recent statement linking the NEET-UG 2026 paper leak case with demands for the education minister’s resignation. The viral clip is actually from a 2015 press conference and is being shared with misleading and false context.

Related Blogs
Introduction
For years, Indian companies could get away with vague privacy promises. That window closed on 13 November 2025, when the government notified the Digital Personal Data Protection Rules, giving teeth to the broad principles Parliament had passed back in 2023 under the DPDP Act. The Rules turned soft commitments into specific, auditable duties, and a lot of organisations are only now realising how much that actually changes.
Start with Section 8(4). It requires every Data Fiduciary to put "appropriate technical and organisational measures" in place. Most readers skim past "organisational" and focus on the technical half, but that's a mistake, because the word is doing real work. It's asking for defined roles, written policies, staff training, and someone actually watching whether any of it holds up over time, not just firewalls and encryption keys. Section 8(5) goes further, demanding reasonable security safeguards against breaches, and Rule 6 spells out exactly what that phrase means in practice: encrypt data at rest and in transit, restrict access on a need to know basis, require multi factor authentication, log and monitor activity, run regular vulnerability checks, bind your data processors contractually to the same standard, and keep relevant logs for at least a year.
Then there's Rule 7, and this is where the clock starts running. Once a Data Fiduciary becomes aware of a breach, the Data Protection Board must be told without delay, and a full report has to follow within 72 hours covering what happened, when, why, what's being done about it, and confirmation that affected individuals were notified. Unlike GDPR, there's no minimum severity threshold here. A breach affecting ten people triggers the same obligation as one affecting ten million. And CERT-In's existing six hour reporting window under its 2022 Directions still applies separately, which means a serious incident can trigger two overlapping regulatory clocks running side by side.
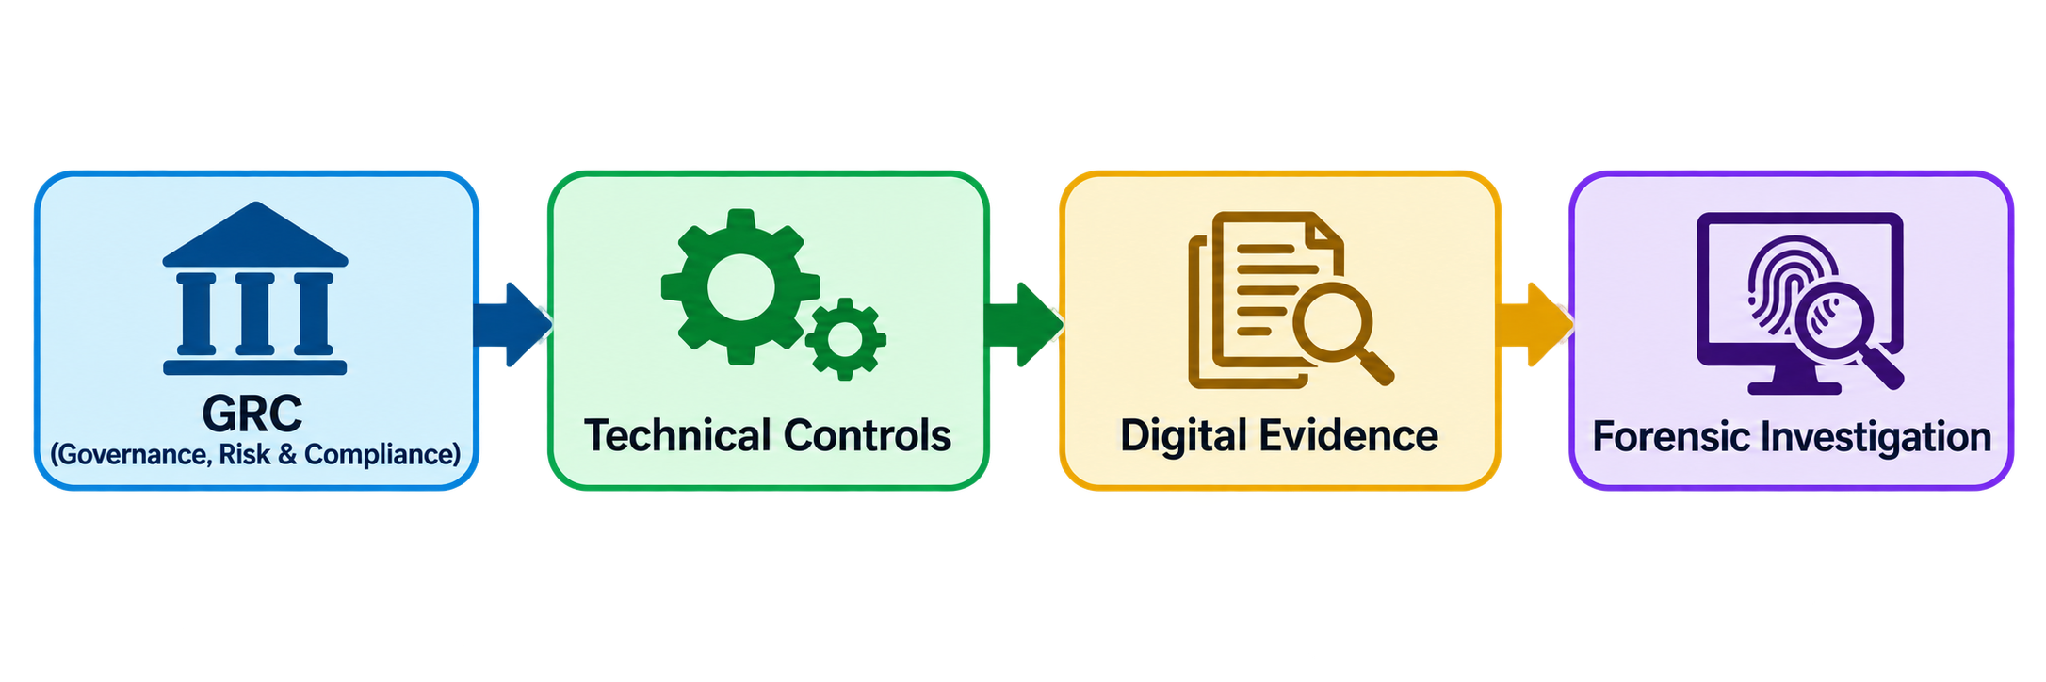
Put all of this together and a pattern emerges. The law assumes an organisation already knows what it's protecting, has actually protected it, kept usable records the whole way through, and can explain clearly what happened the moment something breaks. That coordination job belongs to Governance, Risk and Compliance, or GRC for short. GRC decides who's accountable, which risks actually matter, which controls address them, and how anyone checks whether compliance is real rather than assumed. Skip that structure and security work tends to splinter into a pile of disconnected tasks nobody truly owns.
GRC gives a legal duty somewhere to live. Forensic readiness is what lets an organisation prove, months or years later, that the duty was actually being met.
The Role of Governance, Risk and Compliance
On paper, most cybersecurity programmes look fine. There's an incident response plan somewhere, access control rules exist, logging is "in place," and someone has a title that says they're responsible for security. None of that gets tested until something actually breaks. A phishing compromise, a ransomware infection, a leaked database, a hijacked admin account, whatever the trigger, the questions that follow are always the same, and they're not comfortable ones. What happened, exactly, and when did it start? Which systems, which data, were actually touched? Were the controls the organisation claims to run genuinely functioning at that moment, or just described in a slide deck somewhere? And can anyone produce records solid enough to answer those questions with confidence rather than a shrug?
This is the exact seam where GRC and digital forensics meet. GRC lays out what's expected, who's responsible, and what evidence a control should be generating in the background. Digital forensics is the craft of taking whatever technical traces actually exist and turning them into an account of events that will hold up to scrutiny. Passing an audit was never really the point. Being able to stand in front of a regulator, mid incident, and show that the processes described on paper were real, active, and generating trustworthy evidence, that's the actual bar.
Why Compliance Alone Falls Short
Compliance, in the narrow sense, just means meeting whatever legal, contractual, or internal requirement applies. But a policy sitting in a document repository proves nothing about what actually happens on a Tuesday afternoon when someone requests admin access. A written incident response plan says nothing about whether the team can actually execute it under real pressure, at 2am, with a ransomware note on every screen. A logging policy is close to worthless if the logs it promises were switched off somewhere along the way, or overwritten, or scattered across systems that were never synchronised to the same clock.
NIST's Cybersecurity Framework 2.0 essentially built this concern into its core structure, placing "Govern" alongside Identify, Protect, Detect, Respond, and Recover as one of five equal functions rather than background paperwork sitting off to the side. India's own regulatory posture pushes in the same direction. CERT-In's 2022 Directions require certain incidents to be reported within six hours of discovery, and its guidance for government entities leans heavily on documented incident handling and disciplined evidence practices. The underlying message from both is identical: figure out, before anything goes wrong, whether the evidence you'll eventually need is actually going to exist when someone asks for it.
Where GRC and Forensics Actually Connect
A good GRC programme spells out what's supposed to happen. Forensic readiness is what lets you later prove what actually did.
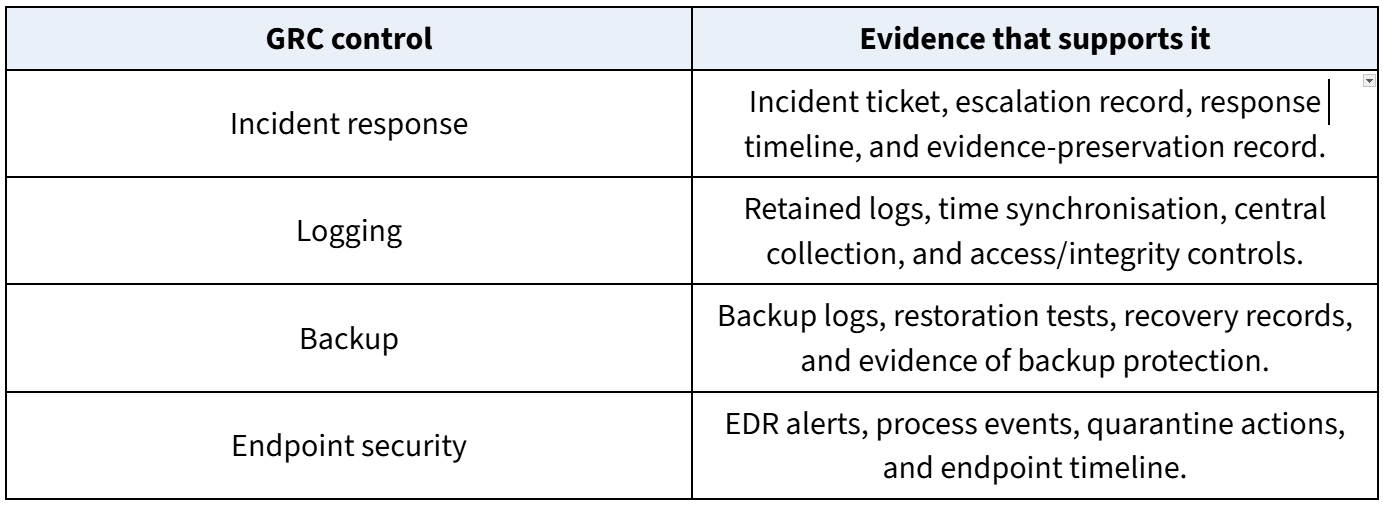
Access control is a useful example here. On the GRC side, an organisation might require least privilege access, multi factor authentication, periodic reviews of who holds privileged accounts, and prompt removal of access once someone leaves or changes roles. On the forensic side, none of that means anything without the underlying records that let investigators actually test it, authentication logs, MFA usage history, privilege change records, and account activity trails. The table below lines up a few common GRC controls against the specific evidence needed to show they were genuinely operating.
A Practical Scenario: After a Ransomware Incident
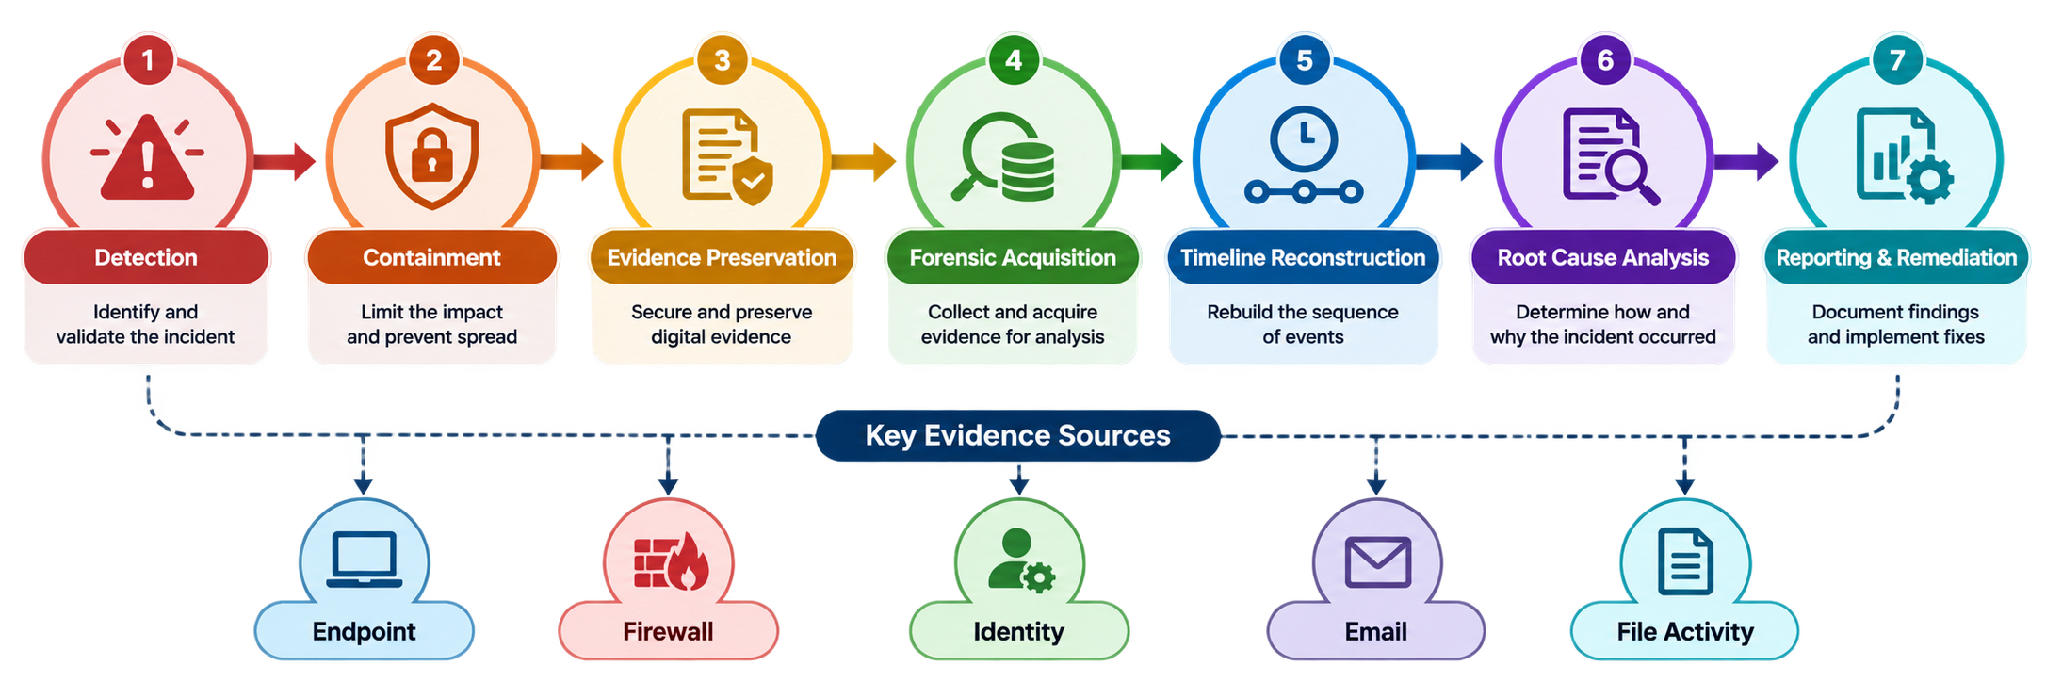
Picture a mid-sized company waking up to find half its file servers encrypted. There's an incident response plan somewhere in the shared drive, technically, but nobody's actually run through it in over a year. The security team isolates the obviously compromised endpoint and starts escalating. Now the forensic side of the house has to reconstruct what happened, working backward through endpoint telemetry, authentication logs, firewall events, email traffic, and file activity, hunting for the original point of entry, how the attacker escalated privileges, how they moved sideways through the network, what data they actually touched, and finally how the ransomware got deployed.
This is where the quality of everything collected beforehand suddenly matters a great deal. If server clocks were never properly synchronised, the timeline investigators build might not line up cleanly enough to trust. If logs only ever lived locally on individual machines rather than being pulled centrally, some of them are probably gone by now. If nobody ever bothered logging administrator actions, there are going to be real, unexplained gaps in the story. And if whatever evidence does exist wasn't collected the right way, its integrity can be challenged later, sometimes fatally, in a legal or regulatory proceeding. CERT-In actually ran a programme on exactly this in July 2026, "Inside the Breach," covering system artefacts, investigative technique, and chain of custody requirements, precisely because this is where real investigations tend to succeed or quietly fall apart.
Building a Forensic Ready GRC Programme
For an organisation starting more or less from scratch, forensic readiness doesn't need to be bolted on as some separate initiative. It can be built straight into the GRC programme that already exists. Start by identifying the systems, applications, cloud services, and privileged accounts that actually matter. Map the real risks and regulatory requirements onto the controls meant to address them. Then get specific about what evidence each control should be generating, and how that evidence gets protected and kept over time. Time synchronisation, centralised logging, tightly controlled access to security records, and clear ownership of preservation, escalation, and investigation all need to exist well before an incident, not be improvised during one. And none of it means much until it's actually been tested, through tabletop exercises and simulated incidents rather than assumed to work because it's written down somewhere. NIST SP 800-61 Revision 3 frames incident response as one continuous loop of preparation, detection, response, recovery, and improvement, rather than a series of separate boxes to check.
There's one question worth asking of every important control an organisation runs: could you actually prove this was working at the moment an incident happened? If the honest answer is no, what you have is a compliance process on paper, and a forensic readiness gap sitting quietly underneath it.
Conclusion
Cyber readiness was never really about how many policies sit in a binder or how many boxes get ticked in an audit. It shows up, or doesn't, in the hours right after something breaks, when an organisation has to move fast, preserve evidence that can actually stand up to scrutiny, explain clearly what happened, and prove that governance and technical controls were genuinely working together rather than just coexisting on paper. GRC sets the direction, the accountability, the risk priorities, and the compliance expectations. Digital forensics does the work of preserving and interpreting the technical evidence once something actually happens. Forensic readiness sits in between the two, making sure they're actually talking to each other long before an incident forces the conversation. The practical task for most organisations comes down to something simple to say, if not always simple to build: design controls that hold up under real incident response, not just an auditor's checklist. The strongest compliance posture was never the one with the thickest binder. It's the one that can back every document up with evidence, on the day it actually matters.
References
- Digital Personal Data Protection Act, 2023, Sections 8(4), 8(5), 8(6). https://www.meity.gov.in/writereaddata/files/Digital%20Personal%20Data%20Protection%20Act%202023.pdf
- Digital Personal Data Protection Rules, 2025, Rules 6 and 7, notified 13 November 2025. https://www.meity.gov.in
- National Institute of Standards and Technology, The NIST Cybersecurity Framework (CSF) 2.0, CSWP 29, 2024. https://csrc.nist.gov/pubs/cswp/29/the-nist-cybersecurity-framework-csf-20/final
- Indian Computer Emergency Response Team (CERT-In), Directions under Section 70B of the Information Technology Act, 2000, dated 28 April 2022. https://www.cert-in.org.in/Directions70B.jsp
- Indian Computer Emergency Response Team (CERT-In), Guidelines on Information Security Practices for Government Entities. https://www.cert-in.org.in/Downloader?fileName=CIPS-2026-0014.pdf&pageid=5&type=2
- National Institute of Standards and Technology, SP 800-86: Guide to Integrating Forensic Techniques into Incident Response, 2006. https://csrc.nist.gov/pubs/sp/800/86/final
- International Organization for Standardization, ISO/IEC 27037:2012, Guidelines for identification, collection, acquisition and preservation of digital evidence. CERT-In, "Inside the Breach: Advanced Cyber Forensics & Incident Investigation," 31 July 2026. https://www.cert-in.org.in/s2cMainServlet?pageid=PRSTNVIEW03&reCode=CIWS-2026-3569
- National Institute of Standards and Technology, SP 800-61 Rev. 3: Incident Response Recommendations and Considerations for Cybersecurity Risk Management, 2025. https://csrc.nist.gov/pubs/sp/800/61/r3/final
- Matters.ai, "DPDP Breach Notification: 72-Hour Rule & ₹200 Cr Penalty." https://www.matters.ai/article/dpdp-breach-notification MediaNama, "Data Breach Reporting Timeline of DPDP Rules 2025 Explained." https://www.medianama.com/2025/11/223-data-breach-reporting-timeline-of-dpdp-rules-2025-explained/

Introduction
The digital ecosystem has undergone a profound transformation due to the rapid growth of artificial intelligence, especially through its generative applications. While this progress has introduced innovative technologies, it has also intensified the risks of deepfakes, misinformation, and identity theft. The Information Technology (Intermediary Guidelines and Digital Media Ethics Code) Amendment Rules, 2026, introduced by the Government of India, mark an important step toward stronger digital governance and greater oversight of online activities. These latest amendments establish new regulatory standards and represent India’s most comprehensive effort so far to address synthetically generated information, including AI created audio, video, and images that closely imitate reality.
Understanding the Core Shift: From Reactive to Proactive Regulation
The 2026 amendment establishes its main characteristic through its shift from a reactive compliance system to a proactive due diligence system. Intermediaries must now operate as active participants who take responsibility for detecting, marking and controlling dangerous material instead of functioning as neutral channels. The rules establish an official definition for stands for Synthetically Generated Information(SGI), which they protect through legal regulations, while they address issues such as impersonation scams, election manipulation and non-consensual deepfake content. The current transition represents a worldwide pattern that shows that governments are starting to make online platforms responsible for the material they display.
Key Provisions of the IT Amendment Rules, 2026
1. Mandatory Labelling of AI-Generated Content
Platforms must ensure that all AI-generated content is clearly labelled or watermarked to distinguish it from authentic media. Users must reveal their uploaded content's synthetic origin while platforms must confirm the information.
2. The 3-Hour Takedown Rule
The most contentious aspect of this regulation establishes new rules that require content removal to be processed within much shorter timeframes.:
- The government and courts grant three-hour time limits for removing unlawful content.
- The two-hour deadline applies to media that includes non-consensual intimate imagery.
The current time frame allows content removal within three hours, which represents a major decrease from the previous content removal time, which lasted between 24 and 36 hours, because online misinformation needs urgent attention.
3. Traceability and Metadata Requirements
The rules require AI-generated content to include both digital fingerprints and metadata, which enables traceability and accountability through their embedded digital fingerprints. The provision serves as an essential tool for law enforcement to investigate cases while it helps identify which parties generated harmful content.
4. Safe Harbour Conditionality
Intermediaries who do not meet the following three conditions risk losing their safe harbour protection through Section 79 of the IT Act:
- The first requirement demands that intermediaries must implement proper labelling.
- The second requirement demands that intermediaries must complete their takedown responsibilities within specific timeframes
- The third requirement demands that intermediaries must complete their due diligence tasks.
This development represents a major transition for digital platforms, which will face increased responsibility for their actions.
5. Strengthened Grievance Redressal
The amendment establishes two new requirements for platforms. The amendment requires platforms to create systems that operate at all times to monitor their compliance with regulations.
Significance: Why These Rules Matter
The 2026 amendments are significant for multiple reasons:
- The rules require labelling and rapid content removal, which helps to stop the viral dissemination of misleading information.
- The framework provides better identity protection, defamation defence and protection against non-consensual imagery.
- The new rules make intermediaries responsible for their own compliance failures.
- The regulation of AI-generated misinformation protects democratic processes during electoral periods and public discussions.
The rules demonstrate India's goal to establish international standards for AI governance and digital responsibility.
Challenges and Concerns
The amendments present key issues that exist despite their positive aspects:
- The process of removing content at high speed creates risks for legitimate expression because safeguards need to be established through careful planning.
- The technical and infrastructural requirements governing compliance create financial burdens for smaller platforms that operate as intermediaries.
The existing challenges demonstrate the necessity for a solution that protects both human rights and security needs.
Conclusion
The IT Amendment Rules, 2026, establish a critical turning point for India's progress toward digital governance. The framework aims to establish a more secure digital environment through its solution of AI-generated content and deepfake detection problems, which create transparency and accountability issues. The rules will achieve their goals through proper implementation, which requires creating quick enforcement methods that protect both legal processes and free speech rights. The ongoing development of AI technology requires regulatory systems to keep changing while including all citizens and upholding democratic principles.
References
- https://vajiramandravi.com/current-affairs/it-rules-amendment-2026
- https://indianexpress.com/article/legal-news/indias-new-3-hour-deepfake-removal-rule-experts-urge-strict-compliance-10528122
- https://timesofindia.indiatimes.com/technology/tech-news/governments-new-it-rules-make-ai-content-labelling-mandatory-give-google-youtube-instagram-and-other-platforms-3-hours-for-takedowns/articleshow/128157496.cms
- https://www.drishtiias.com/daily-updates/daily-news-analysis/information-technology-amendment-rules-2026
- https://visionias.in/current-affairs/news-today/2026-02-11/science-and-technology/government-notified-the-information-technology-intermediary-guidelines-and-digital-media-ethics-code-amendment-rules-2026

Executive Summary
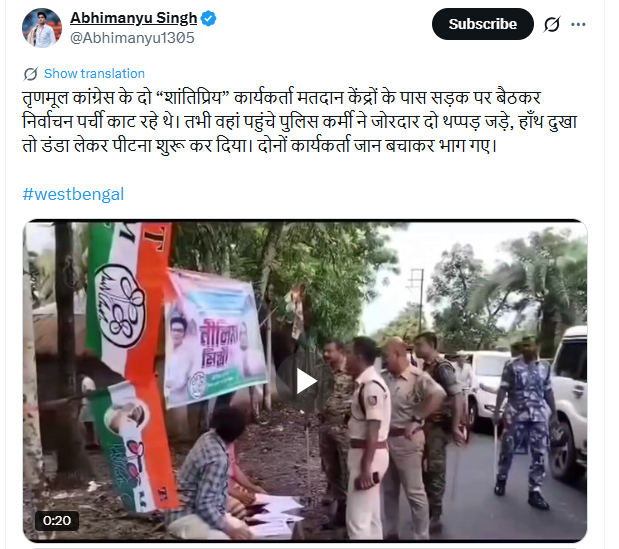
A video is being widely shared on social media showing two men seated on chairs when police personnel arrive and begin assaulting them. A flag of West Bengal Chief Minister Mamata Banerjee’s party, the Trinamool Congress (TMC), can also be seen in the footage. The video is being circulated with the claim that during the first phase of polling held on April 23, 2026, two TMC workers were issuing voter slips near a polling booth when security forces reached the spot and beat them. However, research by the CyberPeace Research Wing found the claim to be false. The footage is not recent and has no connection to the 2026 West Bengal Assembly elections.
Claim:
Social media users alleged that police assaulted TMC workers during the 2026 West Bengal Assembly elections. An X user, Abhimanyu Singh, shared the clip claiming that two “peaceful” TMC workers were sitting near polling stations issuing voter slips when a policeman slapped and beat them with a baton, forcing them to flee.
- https://x.com/Abhimanyu1305/status/2047317736825790549
- https://archive.ph/0ceXH
Fact Check:
To verify the claim, keyframes from the viral video were subjected to a reverse image search. This led to the same video being found on a Facebook page named Canning News, where it had been uploaded in 2023. The caption stated: “Take a look at the situation in Basanti, Canning, on election day.”
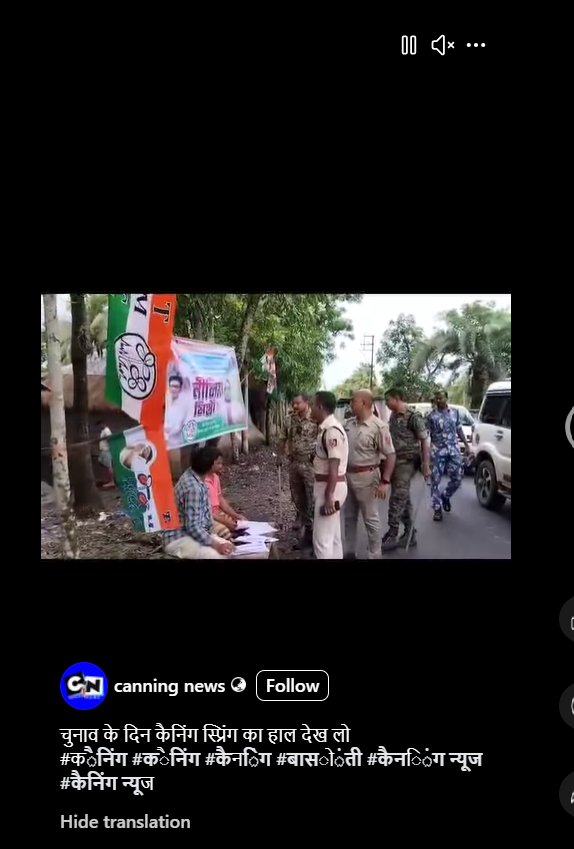
Further searches found the clip published by News18 Bangla on July 6, 2023. The report described unrest during the 2023 Panchayat elections, stating that allegations of bomb throwing had surfaced in Basanti the previous night. On the morning of polling, a bomb was reportedly recovered from the roadside, creating panic in the area.

According to the report, police intervened to control the situation and took action wherever crowds had gathered. The footage showed police dispersing people with batons and, at times, physically confronting individuals.
Conclusion:
The viral claim is misleading. The video is from the 2023 Panchayat elections in West Bengal and is being falsely linked to the recent 2026 Assembly elections.
