
#FactCheck -AI-Generated Video Falsely Shows Car Stuck on Delhi–Jaipur Highway Signboard
Executive Summary
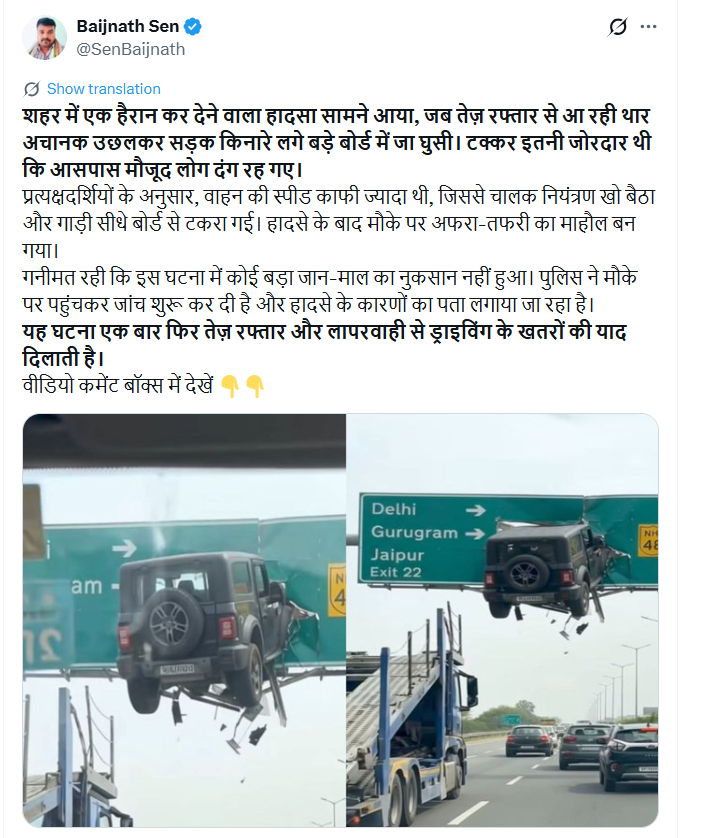
A shocking video showing a car hanging from a highway signboard is going viral on social media. The clip allegedly shows a black Mahindra Thar stuck on an overhead direction signboard on the Delhi–Jaipur Highway (NH-48). Social media users are widely sharing the video, claiming it shows a real road accident. However, a research by CyberPeace found the viral claim to be false. Our findings reveal that the circulating video is not real but AI-generated.
Claim
Social media users are sharing the clip as footage of an actual road accident. A viral post on X (formerly Twitter) claims that the incident took place on the Delhi–Jaipur Highway, showing a black Mahindra & Mahindra Thar lodged in a highway signboard.
- https://x.com/SenBaijnath/status/2024098520006029504
- https://archive.ph/cmr5e
Fact Check
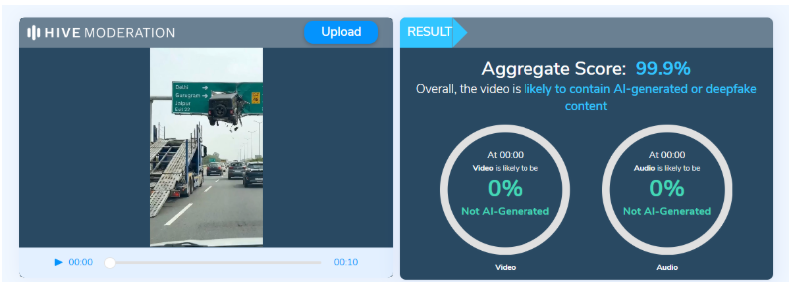
On closely examining the viral video, several inconsistencies were observed that are commonly associated with AI-generated content. For instance, it appears highly improbable for a heavy vehicle to get stuck precisely at the center of a signboard at such a height. Despite the scale of the alleged incident, traffic on the highway below continues moving normally without any disruption. Additionally, the text visible on the right side of the signboard appears distorted and unusually written. To further verify the authenticity of the video, we analysed it using the AI detection tool Hive Moderation, which indicated a 99.9% probability that the video was AI-generated.
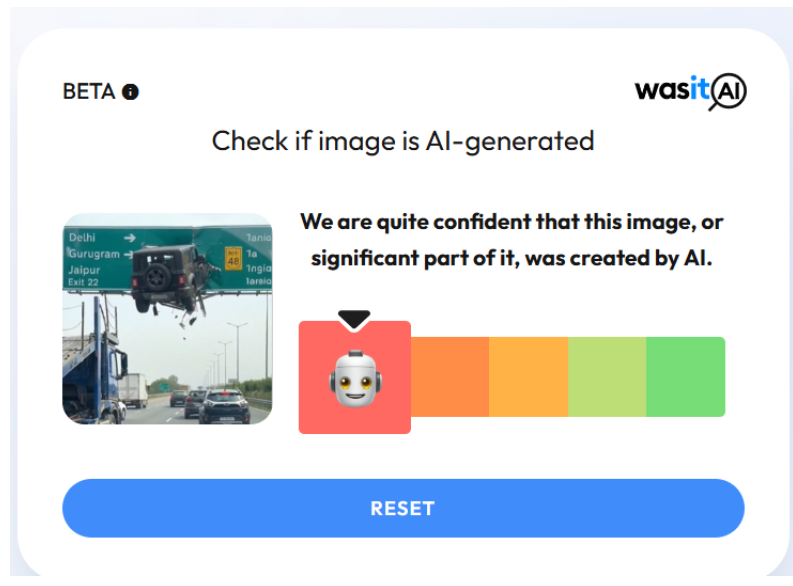
Another AI image detection tool, WasitAI, also found that the visuals in the viral clip were largely AI-generated.
Conclusion
Based on our research and available evidence, it is clear that the viral video showing a Mahindra Thar hanging from a highway signboard is not real but AI-generated.

Related Blogs
Executive Summary
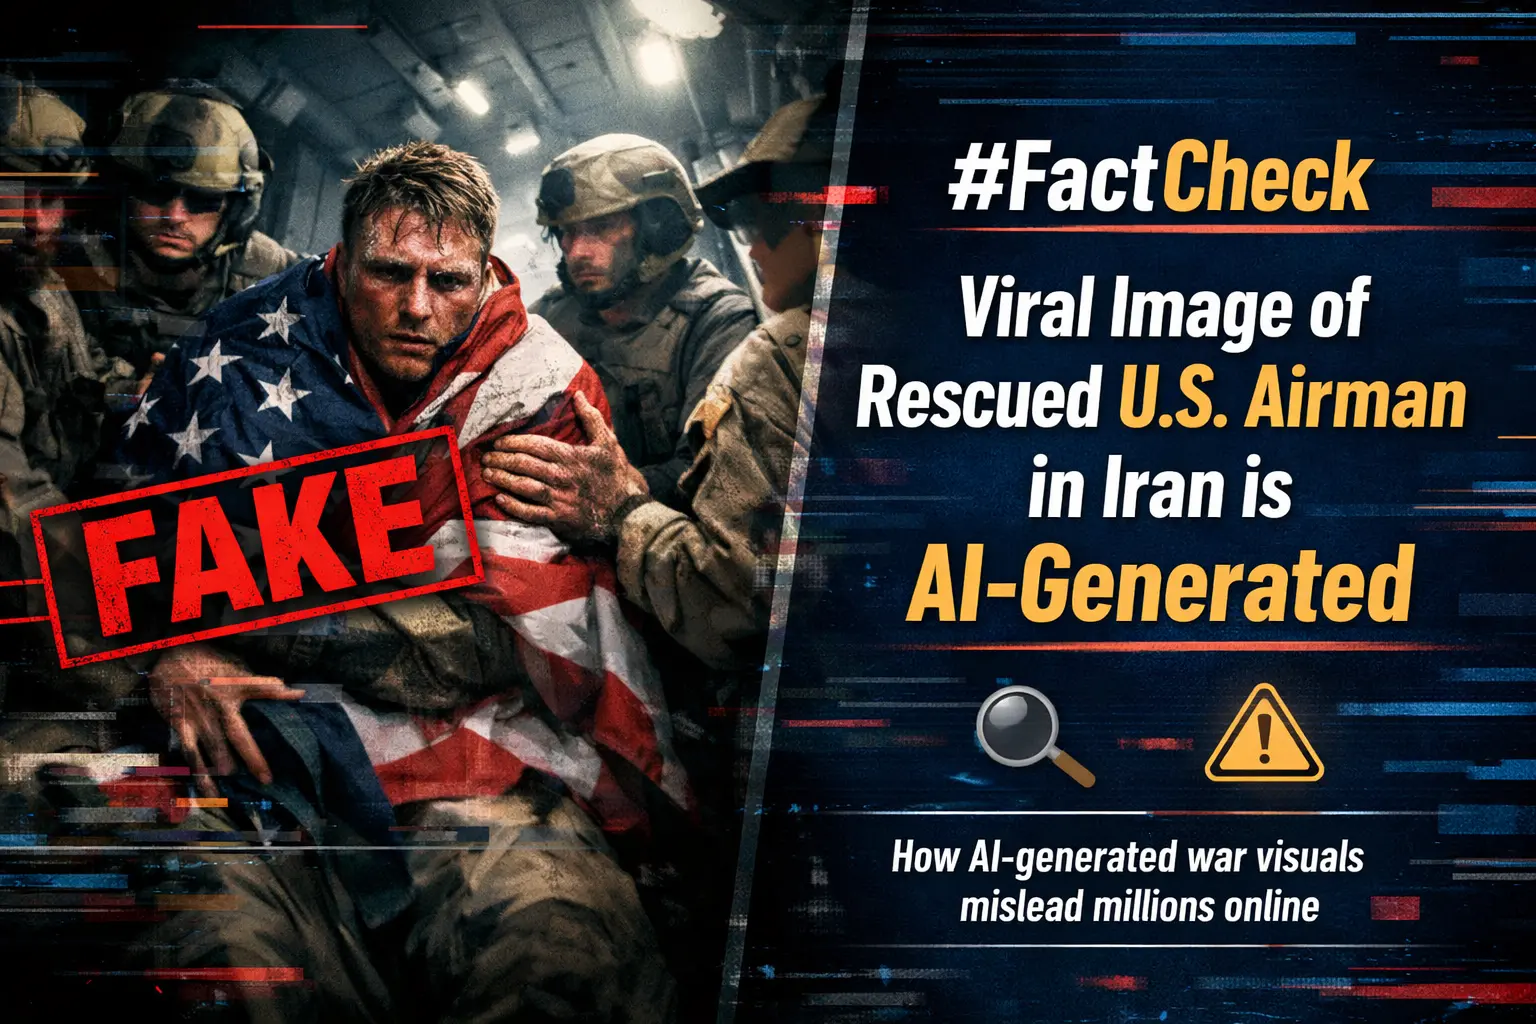
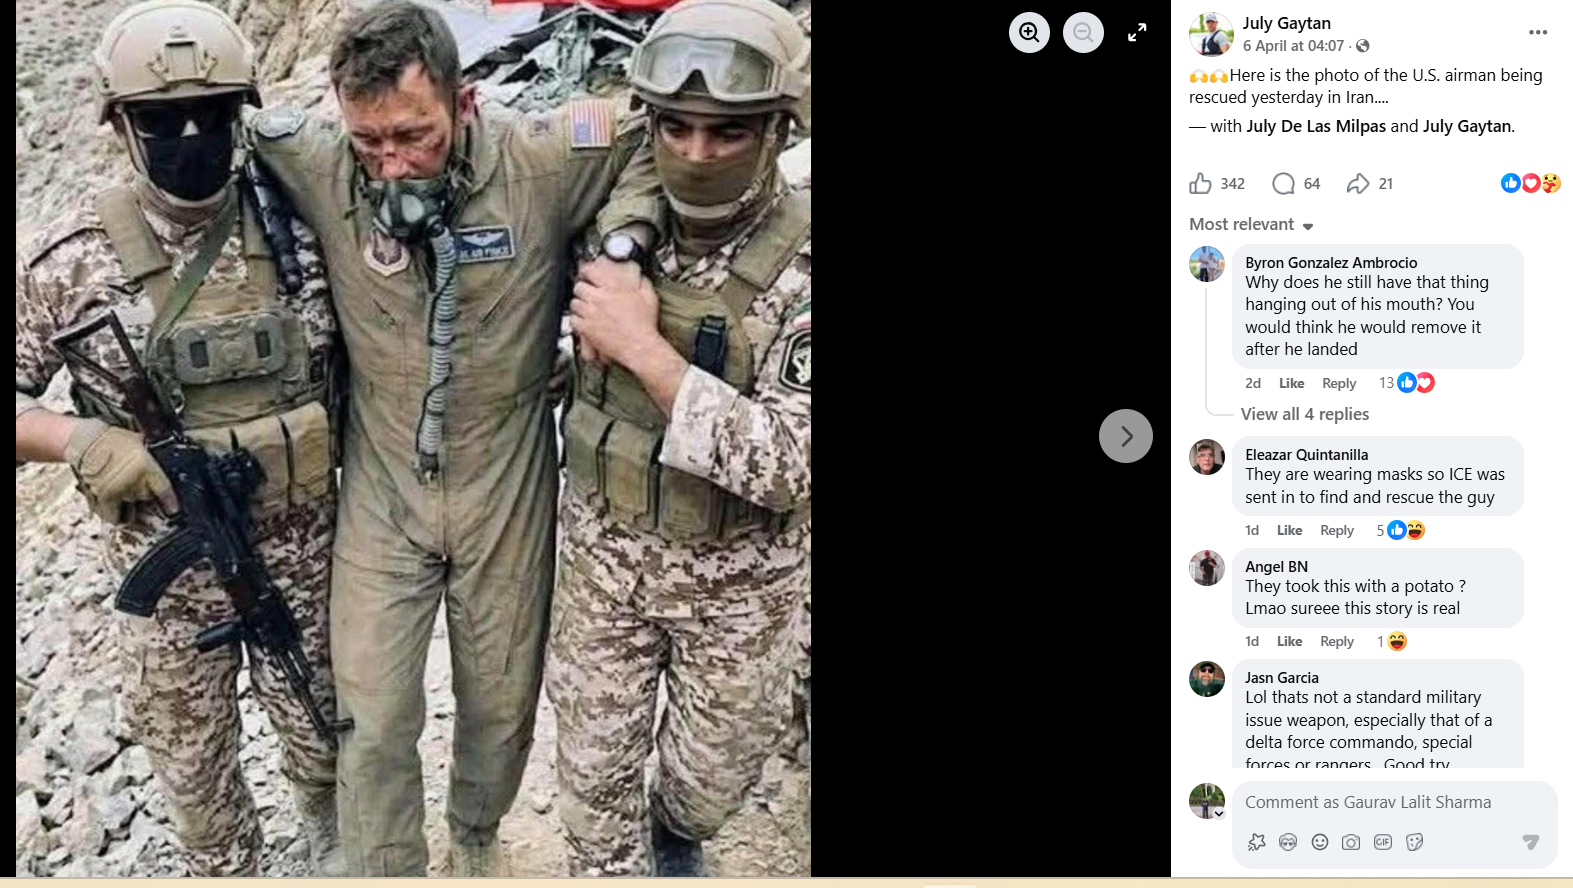
A claim is circulating on social media that the U.S. military successfully rescued a missing crew member of an F-15E fighter jet in Iran. Along with this claim, a photo is being widely shared, allegedly showing the rescued U.S. airman after the high-risk operation. However, researches reveal that the viral image is not authentic and has been generated using artificial intelligence tools.
The Claim
On April 6, 2026, a social media user named “July Gaytan” shared the viral image with the caption: “Here is the photo of the U.S. airman being rescued yesterday in Iran.”
The post quickly gained traction, with many users believing it to be genuine.
- https://www.facebook.com/photo/?fbid=1724007721903888&set=a.116284172676259
- https://perma.cc/URM4-KEJA
Fact Check
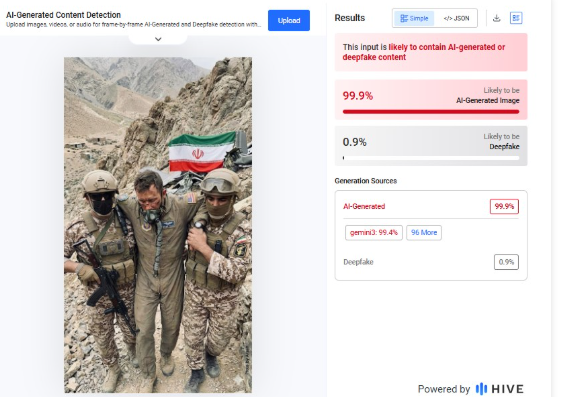
Despite extensive searches, no credible media report or official source has published any real image of the rescued crew members. This raised suspicion about the authenticity of the viral photo. Hive Moderation analysis indicated a 100% probability that the image was generated using Google’s Gemini AI.
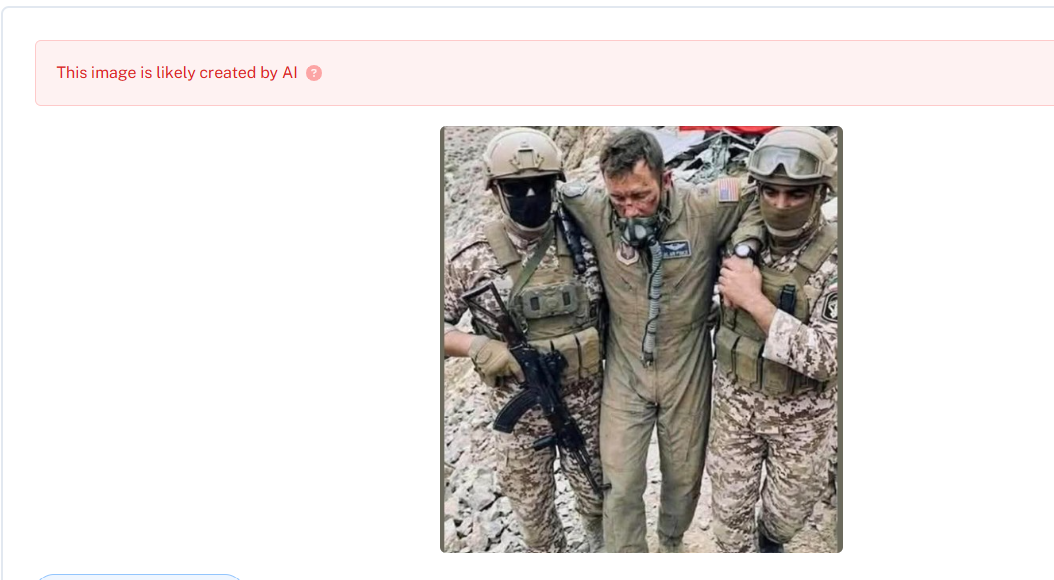
A second scan using Undetectable AI also concluded that the image is AI-generated.
Reports indicate that a U.S. Air Force F-15E Strike Eagle was shot down in Iran. The aircraft had two crew members on board: a pilot and a Weapon Systems Officer (WSO).
- The pilot was rescued shortly after the incident.
- The WSO was initially missing and remained inside Iranian territory in an injured condition.
- The U.S. later carried out a high-risk rescue operation and successfully evacuated the WSO from Iran.
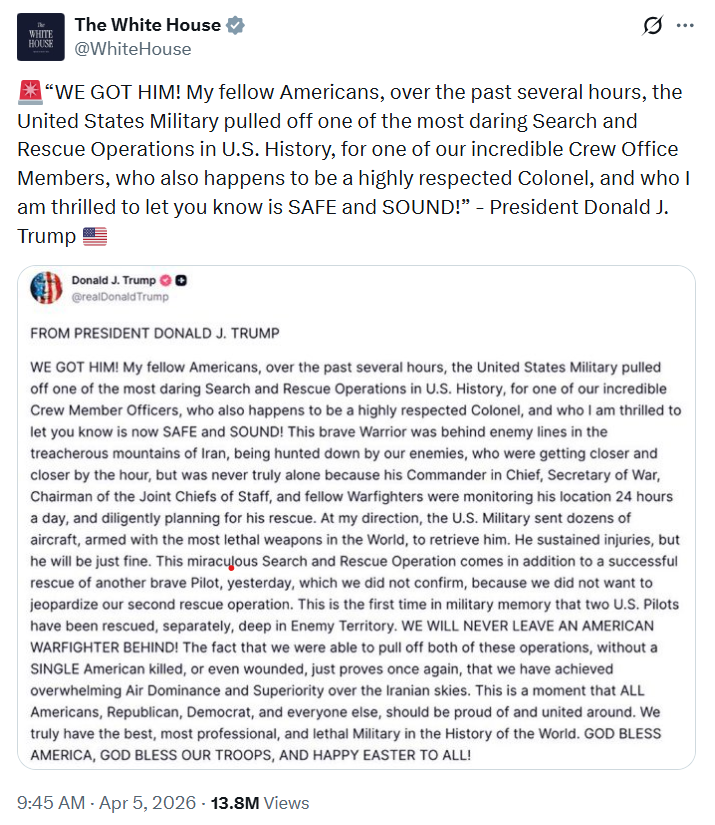
U.S. President Donald Trump also confirmed the “brave and risky” rescue mission in a detailed post on his platform, Truth Social. The statement was further shared by the official White House account.
- https://x.com/WhiteHouse/status/2040644451513598220?s=20
Conclusion
The viral image claiming to show a rescued U.S. airman in Iran is not real. It has been created using AI tools, likely Google’s Gemini. While it is true that the U.S. conducted a high-risk operation to rescue the missing crew member, no authentic image of the rescue or the personnel has been publicly released.
BharOS’s successful testing grabbed massive online attention after Ashwini Vaishnaw, Minister of Communications and Electronics & IT, and Union Education Minister Dharmendra Pradhan unveiled the new mobile operating system. On Data Privacy Day, January 28, it’s appropriate to discuss the safety factors.
The OS is developed by JandKops, which has been incubated by IIT Madras Pravartak Technologies Foundation. It is claimed that BharOS will ensure the prevention of the “execution of any malware” and “execution of any malicious application”.
Even though it is called a Made in India OS, there are many people who disagree with this. It is because the OS is based on an AOSP (Android Open Source Project). It includes similar methodologies, functionalities, and basics used in Google Android.
Global safety factor
Security and data safety has been worldwide issue. A few years ago, Alphabet CEO Sundar Pichai also testified in front of US Congress while facing questions related to privacy, data collection, and location tracking.
While experts say that Android’s app ecosystem is a privacy and security disaster, a study that examined 82,501 apps pre-installed on 1,742 Android smartphones sold by 214 vendors concluded that users are woefully unaware of the significant security and privacy risks posed by pre-installed applications.
Even Apple, which takes cybersafety issues as a top priority, sometimes finds itself in a vulnerable situation. For example, last year Apple users were advised to update their devices to protect against a pair of security flaws that could allow attackers to take complete control.
It was said that one of the software flaws affected the kernel, the deepest layer of the OS shared by all Apple devices, while the other had an impact on WebKit, the technology that powers the Safari web browser.
Security researchers, including NordVPN, said that Apple’s closed development OS makes it more difficult for hackers to develop exploits, while Android raises the threat level since anyone can see its source code to develop exploits.
BharOS is not like iOS but it is kind of similar to Android and based on AOSP. So the question is, how safe would this OS be?
‘Security blanket’
Sandip Kumar Panda, Co-founder and CEO of InstaSafe, told News18: “BharOS acts as a security blanket for devices. The framework is designed in a manner that it prevents the execution of any malicious app and verifies each app on the devices before making it live on the BharOS platform.”
There are no apps without any vulnerabilities, he said. “As the app development progresses, vulnerabilities get introduced either in the form of insecure coding practices or third-party software vulnerabilities integrated with the platform. Since several Android vulnerabilities were discovered over the years, all those bugs would have been fixed now and updates would already have been for AOSP, which will be much more mature now,” he added.
Vineet Kumar, Founder and President of CyberPeace Foundation, believes that “the use of AOSP as the foundation for BharOS is a positive step” as it is a robust platform.
But according to him, it is important to note that no OS can be completely immune to all forms of cyber threats. “The key to staying safe online is to stay vigilant, use security software, keep your software updated, and be mindful of the apps you install and the websites you visit,” he said,
Furthermore, the expert stated that it is possible to make an OS more secure by implementing a variety of security features and technologies such as sandboxing, whitelisting, and application control, as well as rigorous testing and code review processes.
Kumar said: “It would be important for an independent, reputable security firm to evaluate BharOS and test its security features before it can be stated with certainty that it is more secure than other OSs.”
It is difficult to say whether the BharOS will be free of cybersecurity issues without more information about the specific features and security measures that have been implemented, he noted while adding that this OS has to go through a rigorous testing and certification process.
“It will be important to see how it measures up against established security standards and how well it can withstand real-world attacks,” the expert stated.
Reference Link : https://www.news18.com/amp/news/tech/data-privacy-day-how-safe-is-bharos-what-do-cybersecurity-experts-say-you-are-about-to-find-out-6932521.html

Introduction
In today's digital economy, data is not only a business asset but also the fuel for innovation, decision-making, and consumer trust. However, the digitisation of services has made personal or sensitive data a top target for cybercriminals. The stakes are high: a data breach can cost millions of fines, cause damage to reputation and devastate the confidence of consumers. Therefore, regulatory compliance and data protection have become a strategic imperative.
From the General Data Protection Regulation (GDPR) in the EU to the Digital Personal Data Protection (DPDP) Act of India, various sector-specific regulations like HIPAA for healthcare in the US, companies are now subject to a web of data protection and compliance laws. The challenge is to balance compliance efforts with strong security, a balance that demands both policy restraint and technical resilience. This blog examines pivotal pillars, shifting trends and actionable best practices for dominating data protection and compliance in 2025 and beyond.
Why Data Protection and Compliance Matter More Than Ever
Data protection isn't just about keeping fines at bay, it's about preserving the relationship with customers, partners and regulators. A 2024 IBM report says the average data-breach cost has now exceeded USD 4.5 million, with regulatory fines constituting a large portion of the cost. In addition to economics, breaches tend to result in intellectual property loss, customer loss and long-term brand attenuation. Compliance ensures organisations remain within certain legislative necessities for collecting, holding, transferring and setting of personal and sensitive information. Failure to conformity can lead to serious penalties: under GDPR, fines could be up to 4% of the company's annual turnover or €20 million, whichever is higher. In regulated sectors like banking and healthcare, compliance breaches can also lead to the suspension of licenses.
Important Regulatory Frameworks Informing 2025
- GDPR and Its Global Ripple Effect
GDPR was enacted in 2018 and continues to have a ripple effect on privacy legislation worldwide. Its tenets of lawfulness, transparency, data minimisation and purpose limitation have been replicated in many jurisdictions such as Brazil's LGPD and South Korea's PIPA.
- India's DPDP Act
The DPDP Act, 2023, gives high importance to consent-based processing of data, transparent notice rules and fiduciary responsibilities for data. With a penalty for default of up to INR 250 crore, it's amongst the most impactful laws for digital personal data protection.
- Sectoral Regulations
- HIPAA for healthcare information in the US.
- PCI DSS for payment card security.
- DORA (Digital Operational Resilience Act) in the EU for financial organisations.
- These industry-specific models generate overlapping compliance responsibilities, making cross-enterprise compliance programs vital.
Key Pillars of a Sound Data Protection & Compliance Program
- Data Governance and Classification
Having insight into what data you have to store, where it is stored and who can have access to it is the keystone of compliance. Organisations need to have data classification policies in place to group information based on sensitivity and impose more rigorous controls on sensitive data.
- Security Controls and Privacy by Design
Strong technical defences, encryption, multi-factor authentication, and intrusion detection are the initial defences. Privacy by design integrated in product development guarantees compliance is thought through from the initial stage, not added on afterwards.
- Consent and Transparency
Contemporary data legislation highlights informed consent. This entails simple, non-technical privacy notices, detailed opt-in choices, and straightforward withdrawal options. Transparency produces trust and lessens legal danger.
- Incident Response and Breach Notification
Most laws demand timely breach notifications, and GDPR insists on reporting within 72 hours. Having a documented incident response plan maintains legal deadlines and reduces harm.
- Employee Training and Awareness
Human mistake is the top source of data breaches. Ongoing training in prevention of phishing, password management, basic cyber hygiene and compliance requirements is crucial.
Upcoming Trends in 2025
- AI-Powered Compliance Monitoring
Organisations are embracing AI-powered solutions to systematically monitor data flows, identify policy breaches and auto-create compliance reports. The solutions assist in closing the loop between IT security teams and compliance officers.
- Cross-Border Data Transfer Mechanisms
With increasingly severe regulations, companies are spending more on secure cross-border data transfer frameworks like Standard Contractual Clauses (SCCs) and Binding Corporate Rules (BCRs).
- Privacy-Enhancing Technologies (PETs)
Methods such as homomorphic encryption and differential privacy are picking up steam, enabling organisations to sift through datasets without revealing sensitive personal data.
- ESG and Data Ethics
Data handling is increasingly becoming a part of Environmental, Social and Governance (ESG) reporting. Ethical utilisation of customer data, not just compliance, has become a reputational differentiator.
Challenges in Implementation
Despite having transparent frameworks, data protection plans encounter challenges like jurisdictions having competing needs, and global compliance is becoming expensive. The emerging technologies, such as generative AI, often bring privacy threats that haven’t been fully covered by legislation. Small and micro enterprises have neither the budget nor the skills to implement enterprise-level compliance programs. Qualifying these challenges often needs a risk-based strategy, allocations of resources to top areas of impact and automating the compliance chores wherever possible.
Best Practices for 2025 and Beyond
In 2025, regulatory compliance and data protection are no longer a precaution or a response to a breach but are strategic drivers of resilience and trust. As regulatory analysis rises, cyber threats evolve, and consumer expectations grow, administrations need to integrate compliance into the very fabric of their actions. By bringing governance and technology together, organisations can break free from a "checklist" mentality and instead adopt a proactive and risk-sensitive approach. Eventually, data protection is not just about not getting in trouble; it's about developing a kind that succeeds in the digital era.
References
- GDPR – Official EU Regulation Page: https://gdpr.eu
- India’s DPDP Act Overview – MeitY: https://www.meity.gov.in/data-protection-framework
- HIPAA – US Department of Health & Human Services: https://www.hhs.gov/hipaa
- PCI DSS Standards: https://www.pcisecuritystandards.org
- IBM Cost of a Data Breach Report 2024: https://www.ibm.com/reports/data-breach
- OECD – Privacy Guidelines: https://www.oecd.org/sti/privacy-guidelines
