
#FactCheck - Manipulated Image Alleging Disrespect Towards PM Circulates Online
Executive Summary:
A manipulated image showing someone making an offensive gesture towards Prime Minister Narendra Modi is circulating on social media. However, the original photo does not display any such behavior towards the Prime Minister. The CyberPeace Research Team conducted an analysis and found that the genuine image was published in a Hindustan Times article in May 2019, where no rude gesture was visible. A comparison of the viral and authentic images clearly shows the manipulation. Moreover, The Hitavada also published the same image in 2019. Further investigation revealed that ABPLive also had the image.

Claims:
A picture showing an individual making a derogatory gesture towards Prime Minister Narendra Modi is being widely shared across social media platforms.


Fact Check:
Upon receiving the news, we immediately ran a reverse search of the image and found an article by Hindustan Times, where a similar photo was posted but there was no sign of such obscene gestures shown towards PM Modi.

ABP Live and The Hitavada also have the same image published on their website in May 2019.


Comparing both the viral photo and the photo found on official news websites, we found that almost everything resembles each other except the derogatory sign claimed in the viral image.

With this, we have found that someone took the original image, published in May 2019, and edited it with a disrespectful hand gesture, and which has recently gone viral across social media and has no connection with reality.
Conclusion:
In conclusion, a manipulated picture circulating online showing someone making a rude gesture towards Prime Minister Narendra Modi has been debunked by the Cyberpeace Research team. The viral image is just an edited version of the original image published in 2019. This demonstrates the need for all social media users to check/ verify the information and facts before sharing, to prevent the spread of fake content. Hence the viral image is fake and Misleading.
- Claim: A picture shows someone making a rude gesture towards Prime Minister Narendra Modi
- Claimed on: X, Instagram
- Fact Check: Fake & Misleading

Related Blogs

Executive Summary:
A new threat being uncovered in today’s threat landscape is that while threat actors took an average of one hour and seven minutes to leverage Proof-of-Concept(PoC) exploits after they went public, now the time is at a record low of 22 minutes. This incredibly fast exploitation means that there is very limited time for organizations’ IT departments to address these issues and close the leaks before they are exploited. Cloudflare released the Application Security report which shows that the attack percentage is more often higher than the rate at which individuals invent and develop security countermeasures like the WAF rules and software patches. In one case, Cloudflare noted an attacker using a PoC-based attack within a mere 22 minutes from the moment it was released, leaving almost no time for a remediation window.
Despite the constant growth of vulnerabilities in various applications and systems, the share of exploited vulnerabilities, which are accompanied by some level of public exploit or PoC code, has remained relatively stable over the past several years and fluctuates around 50%. These vulnerabilities with publicly known exploit code, 41% was initially attacked in the zero-day mode while of those with no known code, 84% was first attacked in the same mode.
Modus Operandi:
The modus operandi of the attack involving the rapid weaponization of proof-of-concept (PoC) exploits is characterized by the following steps:
- Vulnerability Identification: Threat actors bring together the exploitation of a system vulnerability that may be in the software or hardware of the system; this may be a code error, design failure, or a configuration error. This is normally achieved using vulnerability scanners and test procedures that have to be performed manually.
- Vulnerability Analysis: After the vulnerability is identified, the attackers study how it operates to determine when and how it can be triggered and what consequences that action will have. This means that one needs to analyze the details of the PoC code or system to find out the connection sequence that leads to vulnerability exploitation.
- Exploit Code Development: Being aware of the weakness, the attackers develop a small program or script denoted as the PoC that addresses exclusively the identified vulnerability and manipulates it in a moderated manner. This particular code is meant to be utilized in showing a particular penalty, which could be unauthorized access or alteration of data.
- Public Disclosure and Weaponization: The PoC exploit is released which is frequently done shortly after the vulnerability has been announced to the public. This makes it easier for the attackers to exploit it while waiting for the software developer to release the patch. To illustrate, Cloudflare has spotted an attacker using the PoC-based exploit 22 minutes after the publication only.
- Attack Execution: The attackers then use the weaponized PoC exploit to attack systems which are known to be vulnerable to it. Some of the actions that are tried in this context are attempts at running remote code, unauthorized access and so on. The pace at which it happens is often much faster than the pace at which humans put in place proper security defense mechanisms, such as the WAF rules or software application fixes.
- Targeted Operations: Sometimes, they act as if it’s a planned operation, where the attackers are selective in the system or organization to attack. For example, exploitation of CVE-2022-47966 in ManageEngine software was used during the espionage subprocess, where to perform such activity, the attackers used the mentioned vulnerability to install tools and malware connected with espionage.
Precautions: Mitigation
Following are the mitigating measures against the PoC Exploits:
1. Fast Patching and New Vulnerability Handling
- Introduce proper patching procedures to address quickly the security released updates and disclosed vulnerabilities.
- Focus should be made on the patching of those vulnerabilities that are observed to be having available PoC exploits, which often risks being exploited almost immediately.
- It is necessary to frequently check for the new vulnerability disclosures and PoC releases and have a prepared incident response plan for this purpose.
2. Leverage AI-Powered Security Tools
- Employ intelligent security applications which can easily generate desirable protection rules and signatures as attackers ramp up the weaponization of PoC exploits.
- Step up use of artificial intelligence (AI) - fueled endpoint detection and response (EDR) applications to quickly detect and mitigate the attempts.
- Integrate Artificial Intelligence based SIEM tools to Detect & analyze Indicators of compromise to form faster reaction.
3. Network Segmentation and Hardening
- Use strong networking segregation to prevent the attacker’s movement across the network and also restrict the effects of successful attacks.
- Secure any that are accessible from the internet, and service or protocols such as RDP, CIFS, or Active directory.
- Limit the usage of native scripting applications as much as possible because cyber attackers may exploit them.
4. Vulnerability Disclosure and PoC Management
- Inform the vendors of the bugs and PoC exploits and make sure there is a common understanding of when they are reported, to ensure fast response and mitigation.
- It is suggested to incorporate mechanisms like digital signing and encryption for managing and distributing PoC exploits to prevent them from being accessed by unauthorized persons.
- Exploits used in PoC should be simple and independent with clear and meaningful variable and function names that help reduce time spent on triage and remediation.
5. Risk Assessment and Response to Incidents
- Maintain constant supervision of the environment with an intention of identifying signs of a compromise, as well as, attempts of exploitation.
- Support a frequent detection, analysis and fighting of threats, which use PoC exploits into the system and its components.
- Regularly communicate with security researchers and vendors to understand the existing threats and how to prevent them.
Conclusion:
The rapid process of monetization of Proof of Concept (POC) exploits is one of the most innovative and constantly expanding global threats to cybersecurity at the present moment. Cyber security experts must react quickly while applying a patch, incorporate AI to their security tools, efficiently subdivide their networks and always heed their vulnerability announcements. Stronger incident response plan would aid in handling these kinds of menaces. Hence, applying measures mentioned above, the organizations will be able to prevent the acceleration of turning PoC exploits into weapons and the probability of neutral affecting cyber attacks.
Reference:
https://www.mayrhofer.eu.org/post/vulnerability-disclosure-is-positive/
https://www.uptycs.com/blog/new-poc-exploit-backdoor-malware
https://www.balbix.com/insights/attack-vectors-and-breach-methods/
https://blog.cloudflare.com/application-security-report-2024-update
Executive Summary
A video showing a massive fire in a high-rise building is being widely shared on social media. The footage shows a tall building engulfed in flames with thick smoke rising from it. Users are circulating the video with multiple claims. Some social media users claim that the video is from Tehran, Iran, where Israel allegedly carried out an attack on the headquarters of the Islamic Revolutionary Guard Corps (IRGC). Others are sharing the same video as an alleged strike by the United States Air Force on the IRGC headquarters. CyberPeace Research Wing’s research found the claim to be misleading. The video is not related to any Israeli or U.S. military strike on Iran’s IRGC. In reality, it shows a massive fire that broke out in a skyscraper in Changsha, China, in 2022.
Claim
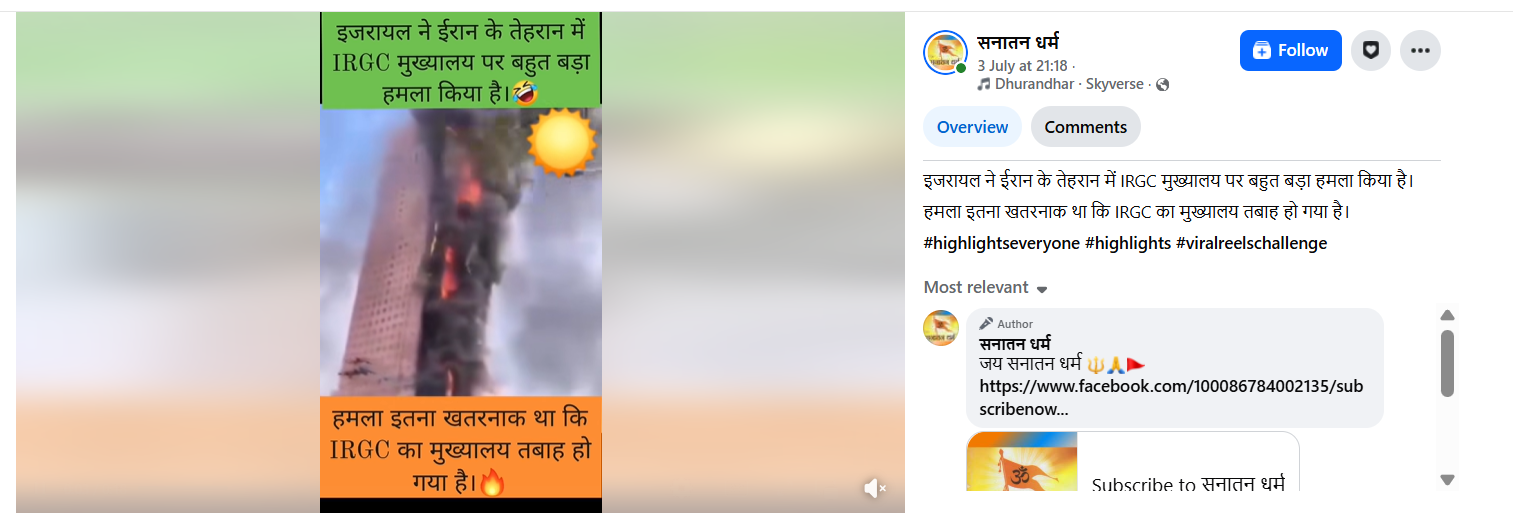
On Facebook, a user shared the viral video on 3 July 2026, claiming: “Israel has carried out a massive attack on IRGC headquarters in Tehran, Iran. The headquarters has been destroyed in the strike.” The post link, archive link, and screenshots are provided below.
https://archive.ph/7BknH
https://www.facebook.com/watch/?v=1530020795436530
Fact Check
During verification, we extracted keyframes from the viral video and performed a reverse image search using Google Lens. The research led us to the same footage uploaded on the official YouTube channel of Hindustan Times on 16 September 2022. According to the video description, the incident shows a massive fire at a high-rise building in Changsha, China, not any military strike in Iran.
https://www.youtube.com/watch?v=Cphle9wkjCE
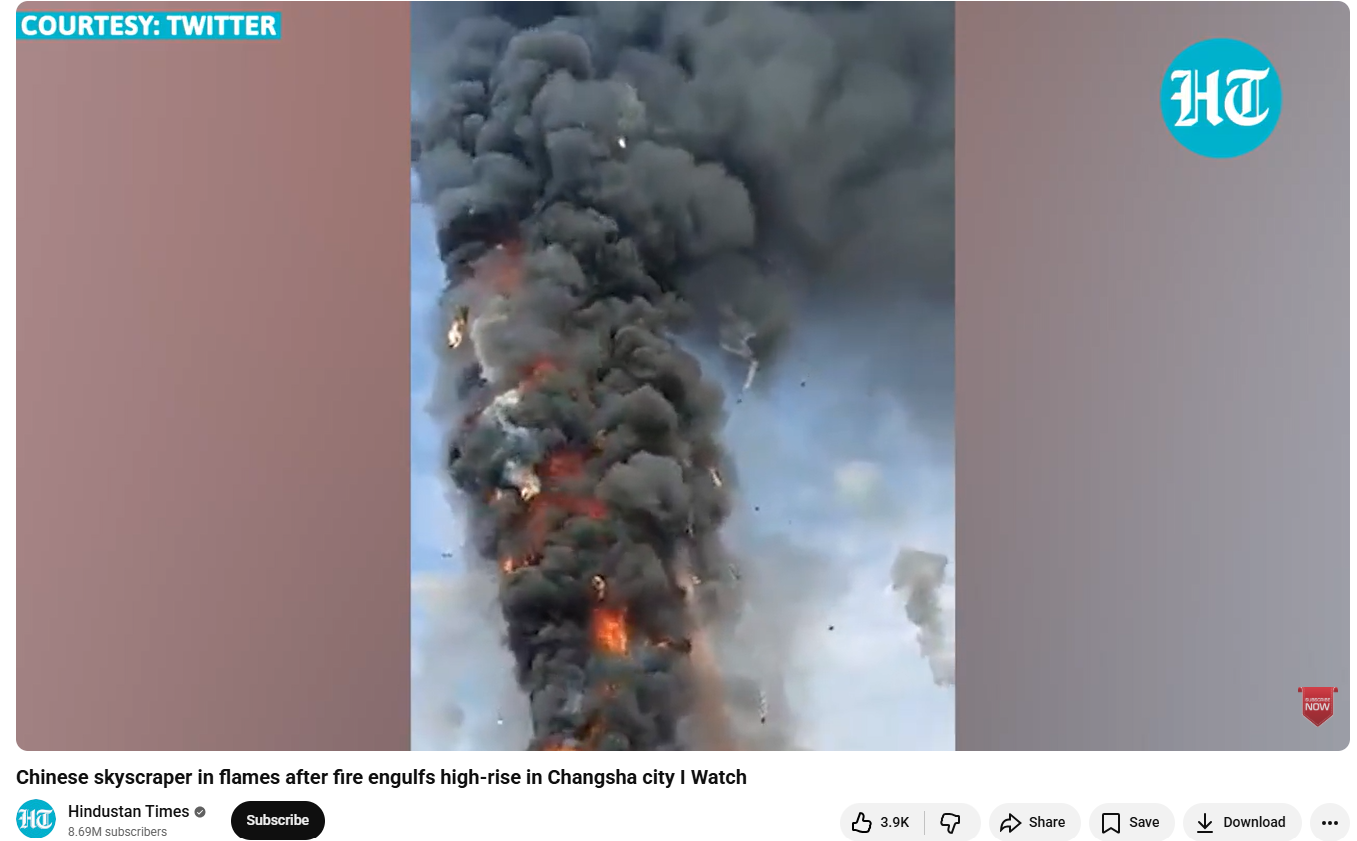
The video description states that the incident took place in a 42-storey building in Changsha, which housed the offices of the state-owned telecommunications company China Telecom. Authorities had initially confirmed that no casualties were reported. Further research led us to a report published on The Guardian website three years ago, which also contained visuals matching the viral footage.
https://www.theguardian.com/world/2022/sep/16/major-fire-breaks-out-at-skyscraper-in-changsha-china
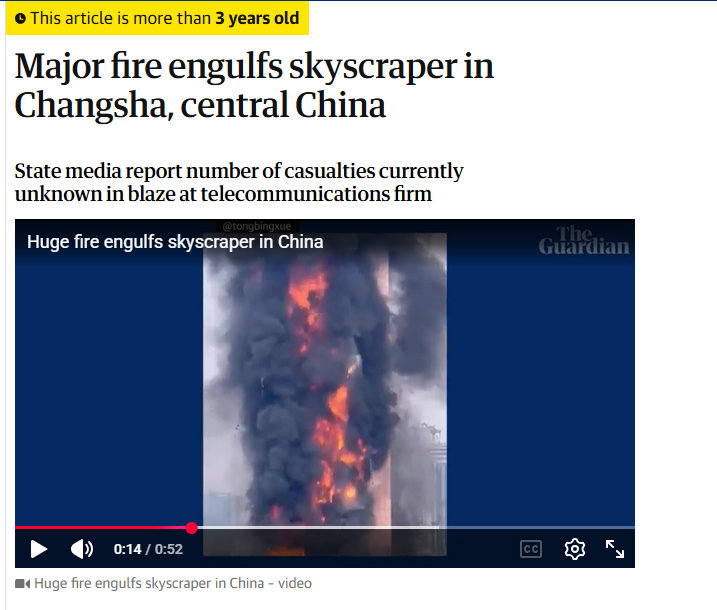
According to The Guardian report, the 42-storey, 218-metre-high building was constructed in 2000 and is located near a major ring road. The report also confirmed that there were no reported fatalities in the incident.
Conclusion
The research clearly found that the viral video does not show an Israeli or U.S. attack on Iran’s IRGC headquarters. The footage is from a massive fire that broke out in a skyscraper in Changsha, China, in 2022. Therefore, the claim being circulated on social media is false and misleading.

Introduction
As AI becomes more deeply integrated into everyday life and industries, Google Cloud is increasing its investment in AI-ready data centres worldwide, with India emerging as a key part of its expansion plans. Thomas Kurian’s latest India visit highlighted Google Cloud’s expanding ambitions in the country. Beyond the $15 billion, 1GW Visakhapatnam data centre announced in October 2025, Google is planning a larger multi-year AI infrastructure push, backed by partnerships with major enterprises across banking, healthcare, and digital services. This reflects a shift where countries are not only competing to create advanced AI technologies but also to build the infrastructure needed to support and lead the future AI economy. But it's worth being precise about what "building infrastructure" actually means here because it is private, foreign-headquartered capital constructing facilities on Indian soil, under terms that remain largely opaque to the public that will depend on them. That distinction matters more than the investment headline suggests.
The Promise and Pressure of Google’s Full-Stack AI Strategy
For decades, data centres were mainly built to store information, host websites, and support cloud applications. The rise of generative AI has completely changed that role. Today's systems need massive computing power both to train models on huge datasets and to run them every time someone generates content or automates a task. It is distinguished from traditional workloads mainly due to relying on proprietary technologies like GPU or TPU, alongside advanced networking and dynamic storage systems that complement each other and work in unison. The efforts of Google to create its own TPUs are understandable as they played a vital role in a number of achievements made by Google DeepMind. Today, the companies, government entities, and people turning to AI solutions put enormous pressure on the processing of data.
The companies that are building this infrastructure are shaping ecosystems on which others will depend on. Google’s “full stack” approach that infers controlling everything from chips and AI models to cloud platforms and applications which may improve efficiency and reduce costs, but it also creates deeper dependence on a single provider. Like a hospital adopting an AI platform is not just purchasing software; over time, its data systems, workflows, and operations can become closely tied to the underlying cloud ecosystem.
This concern when viewed against the concentration of the global cloud market: Amazon Web Services, Microsoft Azure, and Google Cloud together control roughly two-thirds of global cloud infrastructure, making them the dominant gatekeepers of enterprise computing. As these same companies move upward into AI models and applications while controlling the compute layer beneath them, the debate is no longer only about market share, it is about control over the entire AI value chain.
Why Location Matters and Why It Isn't Enough
In traditional internet services, a delay of a few milliseconds rarely mattered. However, future AI applications like autonomous vehicles, AI-assisted diagnostics, automated factory robotics will demand near-instant decision-making and cannot always depend on servers thousands of kilometres away. Regional data centres reduce that latency, which matters especially for India, where hundreds of millions are expected to interact with AI-powered services in the coming years. There is also the question of data sovereignty, and this is where the infrastructure narrative gets ahead of the regulatory reality. Governments worldwide are increasingly concerned about where citizens' and companies' data is stored and processed and local data centres are presented as the answer, but physical proximity does not automatically translate into legal accountability. Google has acknowledged that it bills cloud revenue through whichever global entity corresponds to the data centre being accessed which means an Indian client's spending on Google Cloud infrastructure inside India may still not be booked, taxed, or contractually governed as an Indian transaction. Google Cloud India Pvt. Ltd reported just ₹2,065.4 crore in FY25 revenue, strikingly disconnected from the scale of a $15 billion facility and its roster of major Indian clients. Servers on Indian soil do not by themselves guarantee that India captures the tax base, the leverage, or the oversight that "data sovereignty" implies.
This gap is widened by where India's own data protection framework stands. The Digital Personal Data Protection (DPDP) Act, 2023 leaves retention periods and purpose limitation loosely specified under Sections 8(7) and 12, and its enforcement rules are still being finalised. When hospitals or banks process data through a foundation-model platform like Gemini Enterprise, questions like where processing occurs and what audit trail exists for cross-border flows are not resolved by a local data centre's presence. At present, they rely mostly on vendor assurance rather than independent verification.
Economic Opportunities: More Than Just Servers
AI data centres are often imagined as buildings filled with computers, but their economic impact extends further, into energy systems, construction, engineering, semiconductor supply chains, and skilled technical work. Countries hosting these facilities can benefit from investment and job creation, while local businesses gain access to AI tools without building expensive infrastructure of their own.
For India, expanded AI infrastructure could support ambitions to become a global technology hub, and could narrow the gap in access to high-performance computing that has historically disadvantaged smaller companies and researchers. That potential is real. But it should be weighed against the terms on which it arrives, whether the economic value generated is captured domestically through tax revenue and enforceable local accountability, or whether India functions primarily as a hosting site while value accrues elsewhere. The current revenue-booking structure suggests the latter is, at minimum, a live risk rather than a settled question.
The Environmental Challenge of AI Expansion
However, what remains less discussed is the environmental cost behind this expansion from its impact on the power grid and water required for cooling to clearing use of renewable energy. A 1GW facility, the scale for the Visakhapatnam project is comparable to the output of a mid-sized power plant dedicated entirely to compute demand. As models grow larger and adoption accelerates, this level of energy and water consumption has become one of the central concerns of the global AI infra. As much attention as the investment figures receive, the sustainability issue behind such large-scale infrastructure deserves equal visibility.
The Future: AI Infrastructure as National Infrastructure
The expansion of Google Cloud's AI data centres show a change in how the world views computing. Data centres are no longer invisible facilities operating in the background; they are becoming strategic infrastructure comparable to power grids and telecom networks. That comparison should prompt that infrastructure this consequential is usually made subject to public oversight, licensing conditions, and accountability mechanisms proportionate to its importance which is missing so far. Google Cloud's investment and the compute capacity it brings will lower barriers for Indian enterprises and researchers who have long lacked access to frontier-scale infrastructure. Against this backdrop, India needs to develop the regulatory, tax, and competition frameworks to ensure that the foundation serves the country hosting it, rather than the company that owns it.
Beyond Compute: The Emerging Question of AI Sovereignty
The next phase of the AI race may not be defined only by who builds the most capable models, but by who governs the infrastructure, standards, and decision making systems that those models depend upon. As advances in artificial general intelligence and discussions around superintelligence move from research laboratories into policy circles, control over compute resources is becoming a matter of strategic importance comparable to control over energy reserves or communication networks. Nations that rely entirely on external providers for advanced AI infrastructure may eventually find themselves dependent not merely for technology services, but for economic productivity, public administration, healthcare delivery, and national security capabilities. For India, the challenge is therefore larger than attracting investment. It is about ensuring meaningful domestic participation in ownership, governance, talent development, and oversight so that the intelligence systems shaping the future remain aligned with national priorities and public interest.
References
