
#FactCheck- AI-Generated Train Video Falsely Shows Muslims Praying in Japan A video purportedly showing
Executive Summary
Muslims offering prayers inside a crowded train in Japan is being widely shared on social media, amid ongoing discussions around the country’s alleged rise in anti-immigration sentiment. The clip is being presented as a recent and real incident. However, an research reveals that the video is not authentic. Experts noted that the prayer postures shown in the clip do not align with standard Islamic practices, raising doubts about its credibility. Further analysis indicates that the video has been generated using artificial intelligence (AI).
Claim
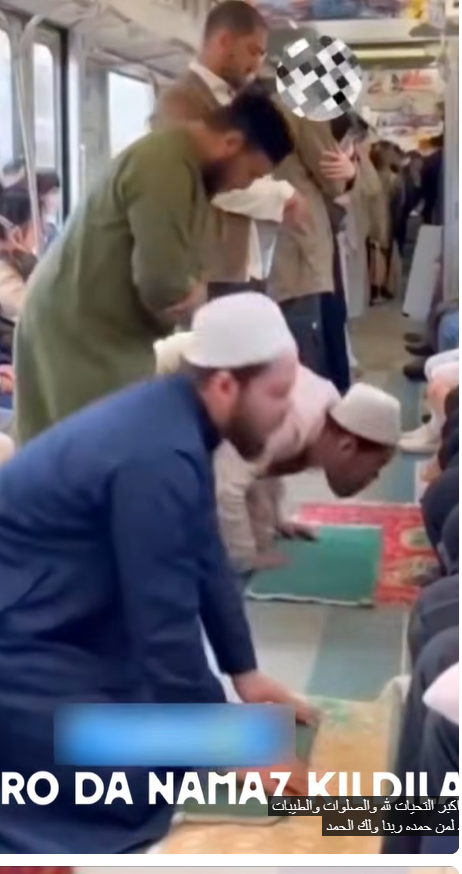
A user shared the viral video on YouTube, showing a group of men—mostly dressed in long tunics and skullcaps—appearing to offer prayers inside a moving subway train. Passengers can be seen seated on both sides of the carriage. In the clip, two men are kneeling on the floor and bowing their heads onto a small mat placed in front of them, with their heads coming very close to the knees of seated passengers. Another man is seen bending forward at the waist while standing, and a fourth appears to be standing upright with his eyes closed.
- Link: https://www.youtube.com/shorts/cZHMCUgbDIA
,
Fact Check
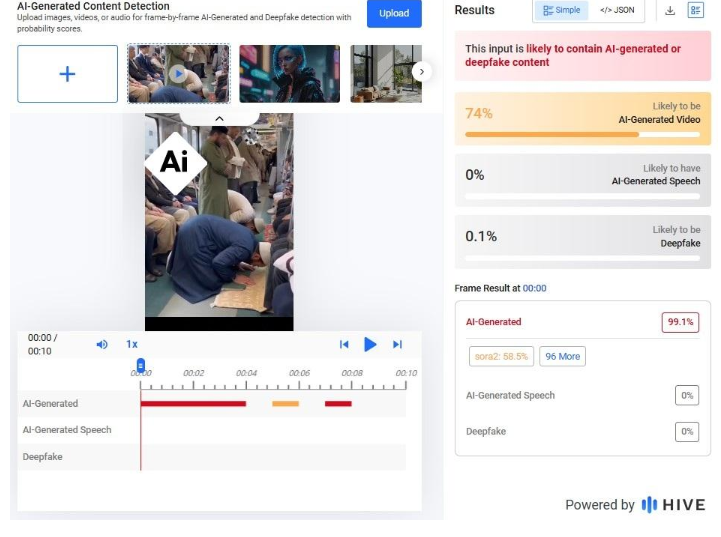
A closer examination of the video reveals several visual inconsistencies. One passenger appears to be fused with the seat rails, creating a distorted overlap. Others seem to be seated in areas where seats do not normally exist, such as directly in front of a door. Additionally, an advertisement visible in the background appears blurred and oddly shaped—another common indicator of AI-generated content. An analysis conducted using the Hive Moderation tool found that the video is “likely to contain AI-generated or deepfake content.”
Conclusion
The viral claim is misleading. The video does not depict a real incident in Japan. Instead, it is likely AI-generated content being circulated with a false narrative, misrepresenting both the context and religious practices shown in the clip.

Related Blogs

Introduction
In the era of digitalisation, social media has become an essential part of our lives, with people spending a lot of time updating every moment of their lives on these platforms. Social media networks such as WhatsApp, Facebook, and YouTube have emerged as significant sources of Information. However, the proliferation of misinformation is alarming since misinformation can have grave consequences for individuals, organisations, and society as a whole. Misinformation can spread rapidly via social media, leaving a higher impact on larger audiences. Bad actors can exploit algorithms for their benefit or some other agenda, using tactics such as clickbait headlines, emotionally charged language, and manipulated algorithms to increase false information.
Impact
The impact of misinformation on our lives is devastating, affecting individuals, communities, and society as a whole. False or misleading health information can have serious consequences, such as believing in unproven remedies or misinformation about some vaccines can cause serious illness, disability, or even death. Any misinformation related to any financial scheme or investment can lead to false or poor financial decisions that could lead to bankruptcy and loss of long-term savings.
In a democratic nation, misinformation plays a vital role in forming a political opinion, and the misinformation spread on social media during elections can affect voter behaviour, damage trust, and may cause political instability.
Mitigating strategies
The best way to minimise or stop the spreading of misinformation requires a multi-faceted approach. These strategies include promoting media literacy with critical thinking, verifying information before sharing, holding social media platforms accountable, regulating misinformation, supporting critical research, and fostering healthy means of communication to build a resilient society.
To put an end to the cycle of misinformation and move towards a better future, we must create plans to combat the spread of false information. This will require coordinated actions from individuals, communities, tech companies, and institutions to promote a culture of information accuracy and responsible behaviour.
The widespread spread of false information on social media platforms presents serious problems for people, groups, and society as a whole. It becomes clear that battling false information necessitates a thorough and multifaceted strategy as we go deeper into comprehending the nuances of this problem.
Encouraging consumers to develop media literacy and critical thinking abilities is essential to preventing the spread of false information. Being educated is essential for equipping people to distinguish between reliable sources and false information. Giving individuals the skills to assess information critically will enable them to choose the content they share and consume with knowledge. Public awareness campaigns should be used to promote and include initiatives that aim to improve media literacy in school curriculum.
Ways to Stop Misinformation
As we have seen, misinformation can cause serious implications; the best way to minimise or stop the spreading of misinformation requires a multifaceted approach; here are some strategies to combat misinformation.
- Promote Media Literacy with Critical Thinking: Educate individuals about how to critically evaluate information, fact check, and recognise common tactics used to spread misinformation, the users must use their critical thinking before forming any opinion or perspective and sharing the content.
- Verify Information: we must encourage people to verify the information before sharing, especially if it seems sensational or controversial, and encourage the consumption of news or any information from a reputable source of news that follows ethical journalistic standards.
- Accountability: Advocate for social media networks' openness and responsibility in the fight against misinformation. Encourage platforms to put in place procedures to detect and delete fraudulent content while boosting credible sources.
- Regulate Misinformation: Looking at the current situation, it is important to advocate for policies and regulations that address the spread of misinformation while safeguarding freedom of expression. Transparency in online communication by identifying the source of information and disclosing any conflict of interest.
- Support Critical Research: Invest in research and study on the sources, impacts, and remedies to misinformation. Support collaborative initiatives by social scientists, psychologists, journalists, and technology to create evidence-based techniques for countering misinformation.
Conclusion
To prevent the cycle of misinformation and move towards responsible use of the Internet, we must create strategies to combat the spread of false information. This will require coordinated actions from individuals, communities, tech companies, and institutions to promote a culture of information accuracy and responsible behaviour.
Executive Summary
The U.S. Department of Justice recently released nearly three million pages of documents, along with thousands of videos and photographs, related to its research into convicted offender Jeffrey Epstein. Meanwhile, a video showing a massive crowd protesting on a street is going viral on social media The video, which had earlier circulated with false claims linking it to anti-government protests in Iran, is now being shared by several users who claim that the protest took place in the United States after the release of the Epstein files. Research by CyberPeace found the viral claim to be false. The video being linked to protests in the United States following the release of the Epstein files is not real and was generated using artificial intelligence (AI).
Claim:
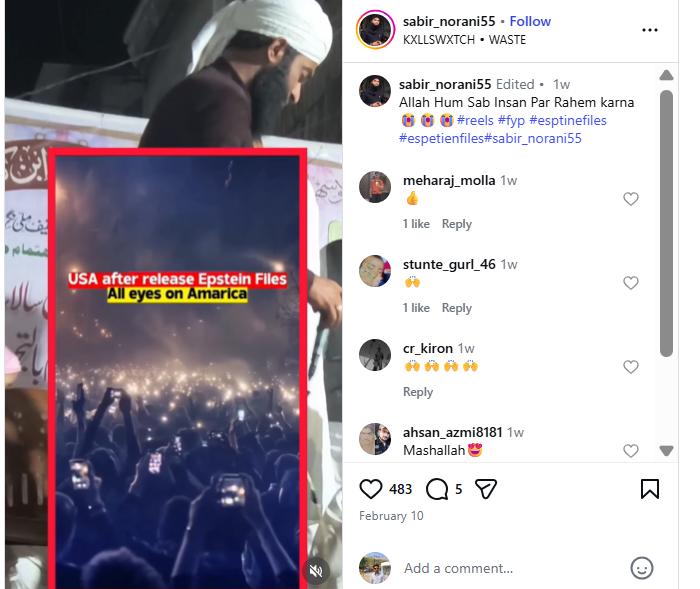
An Instagram user uploaded the viral video on February 9, 2026, with the caption: “After Epstein files released in America. All eyes on America.”
- https://www.instagram.com/reel/DUjLe-XE5lA
- https://ghostarchive.org/archive/tkP6W
Fact Check:
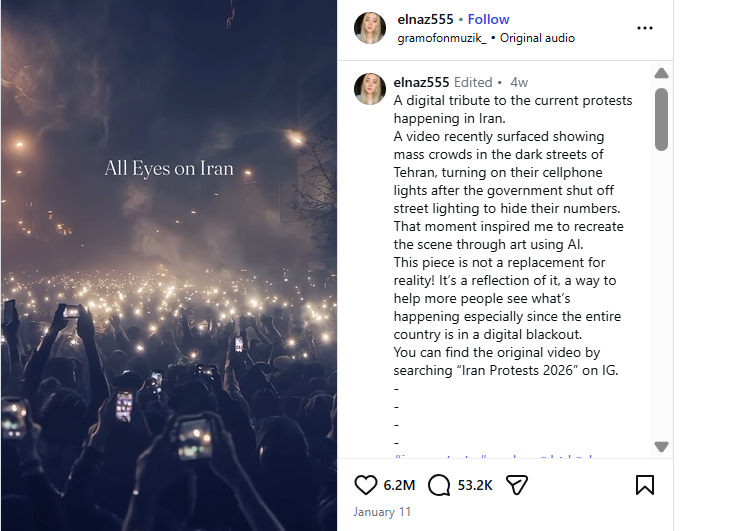
To verify the claim, we first conducted a reverse search of the viral video using Google Lens. The same video was found posted on January 10, 2026, by an Instagram account named “elnaz555,” where it was shared in the context of recent protests in Iran. The post also mentioned that the video was created using AI.
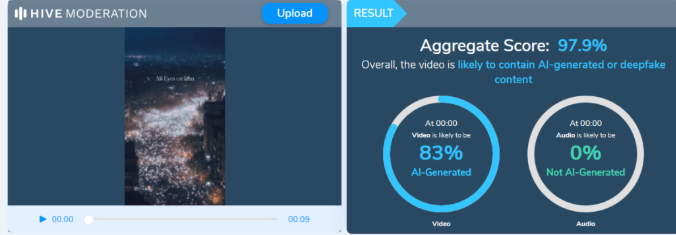
Based on this lead, we further analyzed a higher-quality version of the viral video using Hive Moderation, a tool used to detect AI-generated images and videos. The analysis indicated a 97.9% probability that the video was generated using artificial intelligence. The research clearly shows that the video is not authentic and has been falsely linked to protests in the United States after the release of the Epstein files.
Conclusion:
The claim circulating on social media is false. The viral video allegedly showing protests in the United States following the release of the Epstein files is AI-generated and not related to any real event.
On 12 August 2026, President Donald Trump signed a National Security Presidential Memorandum titled Expanding Capabilities to Combat Transnational Cyber Enabled Crime. Stripped of its bureaucratic packaging, the document does something American law has resisted for three decades: it lets private companies, under close federal supervision, break into the systems of foreign criminal networks and, in some cases, disrupt or damage them.
That is a genuinely large policy shift, even if the memorandum itself is careful, almost defensive, about how it frames the shift. Understanding why requires separating what the text actually authorizes from the "hack back" headline that has attached itself to the story within days of signing.
The problem the memo says it is solving
The White House frames this as a response to scale, not ideology. Americans reported losing more than 20.8 billion dollars to cyber enabled crime in 2025, a sharp jump from the roughly 12.5 billion dollar figure cited when the administration's earlier March 2026 executive order on cybercrime, fraud, and predatory schemes was signed. Ransomware, phishing, financial fraud, sextortion, and impersonation scams sit at the center of that number, and the administration's own supporting material points to a grim detail buried in the numbers: one in seven young people who experienced sextortion as a minor reported harming themselves as a result.
Those crimes, the memorandum argues, are increasingly the work of organized, transnational groups operating from jurisdictions the FBI simply cannot reach. Domestic law enforcement, built for domestic crime, is structurally mismatched to a threat that lives across borders and inside encrypted infrastructure. The administration's answer is to formally recruit the resource it says is best positioned to close that gap: the American cybersecurity industry itself, which the memo describes as "the most innovative and technologically advanced in the world."
What the Program actually authorizes
The memorandum directs the National Coordination Center, a body first stood up under a 2025 executive order, to build a formal Program through which vetted Participating Companies can conduct two categories of activity against foreign Cyber Enabled Transnational Criminal Organizations, defined in the text as CE TCOs.
Cyber Surveillance Operations cover unauthorized access to a target's systems for the primary purpose of collecting information or intelligence, undertaken with the intent to remain undetected. Cyber Effects Operations go further: manipulating, disrupting, denying, degrading, or destroying information systems, the infrastructure those systems control, or the data resident on them.
Crucially, CE TCOs are defined narrowly. A foreign group only counts if it targets the US government, US persons, or US interests, and it must not be an institutional arm of a foreign state or wholly directed by one. The memo builds in a presumption of innocence at the state level too: a group is assumed not to be state controlled unless clear intelligence establishes otherwise. That distinction matters enormously, because it is the line meant to separate this Program from anything resembling private warfare against a nation state.
No operation happens unilaterally. Every proposed action must be approved in writing by two Program Executive Directors, one designated by the Attorney General and one by the Secretary of Homeland Security, coordinating with each other before signing off. Participating Companies must pass what the memo calls rigorous vetting, sign contractual agreements with DOJ or DHS, and in many cases post a bond or escrow of at least one million dollars, forfeited if they breach their agreement. Within 60 days of the memo's signing, the Program Executive Directors must publish detailed operating procedures covering everything from target adjudication to what happens if an operation accidentally hits a US person's system, in which case the company must stop, run minimization procedures, and immediately notify the Center.
There is also a hard ceiling built into the design. Operations expected to cause loss of life, serious injury, or conduct that would rise to the level of a use of force or armed attack under international law, termed Critical Outcomes in the text, cannot be approved by the Program Executive Directors at all. That ceiling is the memo's clearest attempt to keep this inside the bounds of law enforcement rather than sliding into something closer to conflict.
Multiple law firms tracking the rollout, including Wiley, have been explicit on one point worth repeating because so much coverage has blurred it: this is not a green light for companies to hack back on their own initiative. Every operation remains, on paper, an act of the federal government, merely executed through a contracted private hand.
Why experts are not popping champagne
Legal caution has not stopped a wave of professional anxiety. Cyber policy veterans interviewed by outlets like CyberScoop describe the memo as a genuine philosophical break in how Washington thinks about offense in cyberspace, and the debate that followed split fairly evenly between cautious optimism and open alarm.
The core worry, echoed across nearly every serious critique, is attribution. Cyber operations are hard to trace precisely because criminals exploit shared infrastructure, proxies, and compromised third party systems to hide, and that same fog does not lift just because a government contract sits behind the operator. A former senior CISA official, Michael Garcia, put the risk plainly: pressure to attribute quickly could push companies toward lower certainty judgments about who they are actually striking, with a realistic chance of hitting the wrong server, or worse, infrastructure tied to a foreign government rather than a criminal gang. A former Cyber Command official was blunter still, describing parts of the memo on social media as a structure that could reward companies for manufacturing billable threats rather than resolving them efficiently.
Paul Rosenzweig, a former DHS policy official, raised a separate and arguably more durable problem: jurisdiction. Whatever this memo authorizes under American law, the systems being accessed usually sit inside someone else's sovereign territory, governed by that country's own criminal statutes. Washington cannot legislate away a foreign hacking law simply by calling the American company that broke it a Participating Company.
None of this makes the memo indefensible. Supporters point out, correctly, that the private sector already does enormous amounts of active defense and threat disruption work informally, through botnet takedown litigation and coordinated infrastructure seizures, and that formalizing federal oversight over that activity is arguably safer than the current improvisation. The honest position, and probably the fair one, is that the memo trades one set of risks for another, and which set turns out worse will depend entirely on the operating procedures due inside sixty days, procedures the public has not yet seen.
CyberPeace Insights: what this means beyond America's borders
A significant share of the CE-TCO activity this memo is built to target, the ransomware crews, romance investment fraud operations, and sextortion rings running out of Southeast Asia, does not victimize Americans in isolation. The scam compounds clustered along the Myanmar, Cambodia, and Laos borders, repeatedly raided over the past two years, have held thousands of trafficked workers of dozens of nationalities, Indians consistently among the largest groups rescued, alongside Chinese, Filipino, and Malaysian nationals. India has run its own repatriation efforts out of Mae Sot in Thailand, bringing citizens home several hundred at a time, and has built its own institutional response to this threat through the Indian Cyber Crime Coordination Centre, which coordinates cybercrime enforcement across states and increasingly across borders.
That shared exposure gives India and the United States real common ground here. The criminal infrastructure this American Program is designed to disrupt is, in significant part, the same infrastructure that has trafficked and defrauded Indian citizens, which gives New Delhi genuine reason to watch this experiment closely and constructively. At the same time, the Program's underlying model, private companies conducting cross-border operations under one nation's legal authorization, is a genuinely new template in international cyber governance, and how it performs over its first year will likely shape how other major digital economies, India included, think about calibrating their own frameworks for public-private cooperation against transnational cybercrime. India and other nations should closely watch whether this becomes a template worth adapting or a cautionary tale worth avoiding.
It is pertinent to note that Justice and Homeland Security departments have 60 days to write detailed operating procedures covering everything from a target-vetting rubric to a classified operational workflow and 180 days to deliver the first status report to the White House.
References
- The White House. "Expanding Capabilities to Combat Transnational Cyber Enabled Crime." 12 August 2026. https://www.whitehouse.gov/presidential-actions/2026/08/expanding-capabilities-to-combat-transnational-cyber-enabled-crime/
- Wiley Rein LLP. "Navigating the New Presidential Memorandum on Transnational Cyber Enabled Crime." August 2026. https://www.wiley.law/alert-Navigating-the-New-Presidential-Memorandum-on-Transnational-Cyber-Enabled-Crime
- SecureWorld. "Trump Memo Lets Private Firms Hack Back at Cybercriminals." August 2026. https://www.secureworld.io/industry-news/trump-authorizes-private-firms-offensive-cyber-operations
- CyberScoop. "A bold new strategy or a dangerous precedent? Experts are divided on Trump's memo." August 2026. https://cyberscoop.com/private-sector-hacking-presidential-memo-cybersecurity/
- CyberScoop. "Trump turns to private sector in offensive hacking operations memo." August 2026. https://cyberscoop.com/trump-memo-private-sector-offensive-hacking/
- CNN Politics. "Cyber privateers: Trump issues order allowing US companies to hack overseas groups under certain conditions." August 2026. https://www.cnn.com/2026/08/13/politics/cyber-privateers-trump-order-overseas-groups-hacking
- NPR. "Trump administration wants to allow companies to hack foreign cybercriminals." August 2026. https://www.npr.org/2026/08/15/nx-s1-5930311/trump-companies-hack-foreign-cybercriminals
- The Next Web. "President Donald Trump signs memo letting US agencies hack transnational crime groups abroad." August 2026. https://thenextweb.com/news/trump-cyber-memo-transnational-crime
- Machine News. "Security firms hit back at Trump's call to hack back against international crime gangs." August 2026. https://www.machine.news/security-firms-hit-back-at-trumps-call-to-hack-back-against-international-crime-gangs/
- Lawfare. "Trump Admin Cyber Strategy Centers Private Sector in Offensive Cyber Operations." March 2026. https://www.lawfaremedia.org/article/trump-admin-cyber-strategy-centers-private-sector-in-offensive-cyber-operations
- Lawfare. "Partners or Provocateurs? Private Sector Involvement in Offensive Cyber Operations." July 2025. https://www.lawfaremedia.org/article/partners-or-provocateurs--private-sector-involvement-in-offensive-cyber-operations
- Global Indian Network. "Pig Butchering Scams in India: The Dark Intersection of Social Media, AI, and Emotional Manipulation." January 2026. https://globalindiannetwork.com/pig-butchering-scams-in-india/
- The Tribune. "India brings home scammed 549 nationals from Myanmar in 2 days." 2025. https://www.tribuneindia.com/news/india/india-brings-home-scammed-549-nationals-from-myanmar-in-2-days
- Malay Mail. "India to repatriate 500 nationals fleeing Myanmar's cyber scam hub, says Thai PM." October 2025. https://www.malaymail.com/amp/news/world/2025/10/29/india-to-repatriate-500-nationals-fleeing-myanmars-cyber-scam-hub-says-thai-pm/196399
- NBC News. "260 foreigners rescued from virtual slavery in Myanmar's online scam centers are being repatriated." 2025. https://www.nbcnews.com/news/world/260-foreigners-rescued-virtual-slavery-myanmars-online-scam-centers-ar-rcna192180
- CyberPeace Foundation. "About Us." https://cyberpeace.org/about-us
Contributors
- Maj. Vineet Kumar, Founder & Global President, CyberPeace
- Mr. Neeraj Soni, Senior Research Analyst, Policy & Advocacy, CyberPeace
List of Abbreviations
- CE‑TCO — Cyber Enabled Transnational Criminal Organization
- DOJ — Department of Justice
- DHS — Department of Homeland Security
- FBI — Federal Bureau of Investigation
- CISA — Cybersecurity and Infrastructure Security Agency
- I4C — Indian Cyber Crime Coordination Centre
- US — United States
- IT — Information Technology
