
#FactCheck - Fake Quote Attributed To Manoj Tiwari On Rupee-Dollar Value Goes Viral Online
Executive Summary
A postcard featuring BJP leader Manoj Tiwari is being widely shared on social media with a purported statement attributed to him. The viral postcard claims that Tiwari suggested that if people stopped using the ₹1 coin and treated ₹2 as ₹1, the value of the dollar would automatically come down to ₹45. Users are sharing the post claiming that the BJP leader made the bizarre suggestion to strengthen the Indian rupee against the US dollar.
However, research by the CyberPeace Research Wing found the claim to be false. Manoj Tiwari never made any such statement regarding the rupee and the dollar. The BJP MP himself has dismissed the viral claim as fake.
Claim
TMC leader Kirti Azad shared the viral postcard on X and wrote, “As received on X, forwarded as it is. India is truly blessed with such brilliant minds.”
https://x.com/KirtiAzaad/status/2055905987115233473?s=20

Fact Check
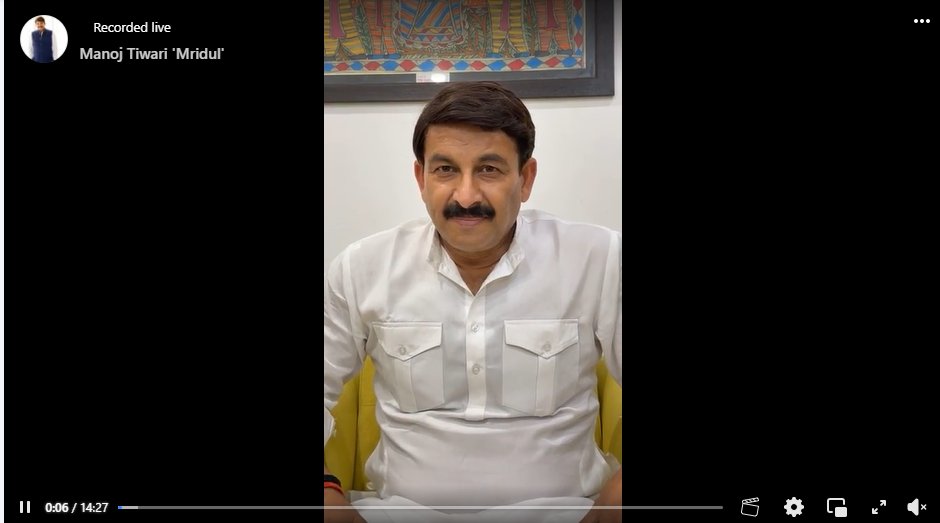
A keyword search on Google did not yield any credible media reports suggesting that Manoj Tiwari had made such a statement. No reliable source was found to support the viral claim. Further research led to a clarification posted on Manoj Tiwari’s official Facebook page. In the video statement, Tiwari categorically denied making any such remark about the rupee and the dollar. He stated that the viral claim being circulated in his name was completely fake.
Manoj Tiwari’s clarification video on Facebook
Conclusion
The viral claim is false. Manoj Tiwari never made any statement suggesting that stopping the use of ₹1 and treating ₹2 as ₹1 would strengthen the rupee against the dollar. He has himself denied the claim and called it fake.

Related Blogs
Executive Summary
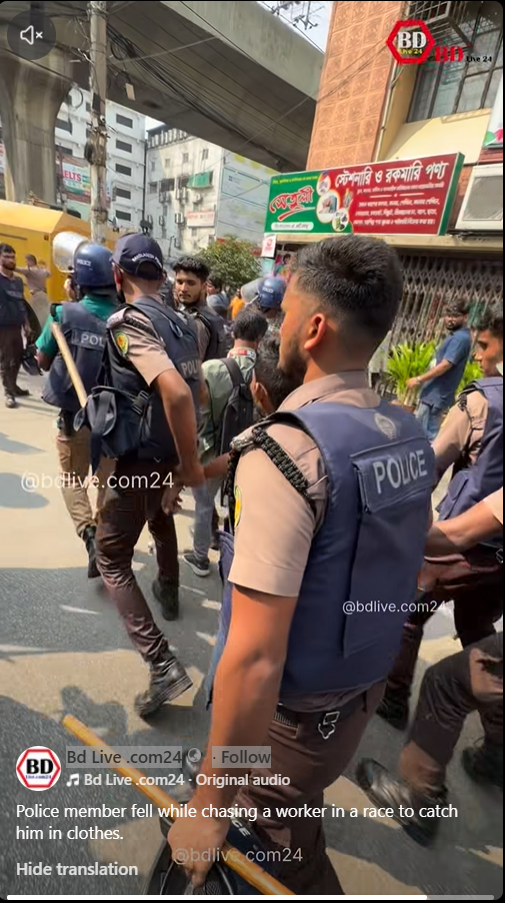
A video is being shared on social media claiming to be from Tripura. It is claimed that police chased and thrashed those accused of attacking BSF personnel. The video shows police personnel chasing and beating a group of people. During the incident, a young man falls onto the road. CyberPeace Research found the viral claim to be misleading. Our research revealed that the video is not from Tripura but from Bangladesh.
Claim
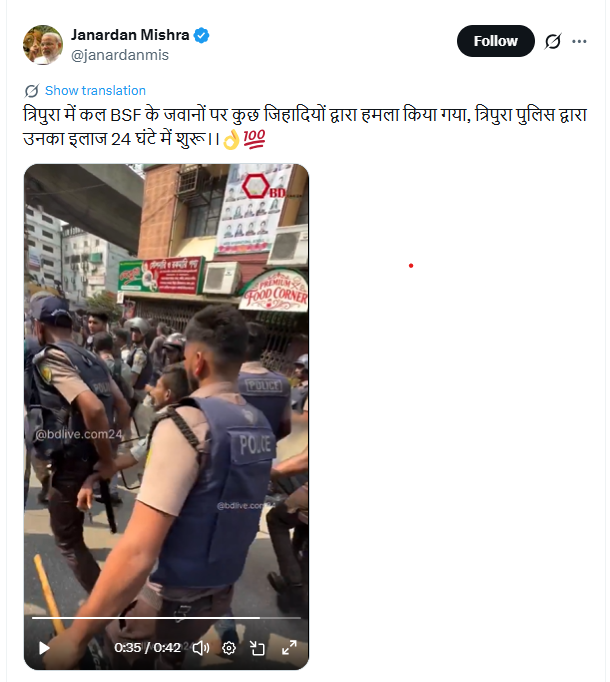
A user on social media platform X shared the viral video on November 4, 2026, with the caption: “Some jihadis attacked BSF personnel in Tripura yesterday, and the Tripura Police began treating them within 24 hours.” The post link, archive link and screenshot are provided below.
https://x.com/janardanmis/status/2117985963519693257
Fact Check
To verify the authenticity of the viral claim, we conducted a reverse image search of the video. During the search, we found the video on a YouTube channel named ‘bbpatrikabd’, where it was identified as being from Dhaka.According to the video caption, it shows police baton-charging workers during a protest in Mirpur, Dhaka. The video captures the tense situation at the protest site and the police action against the demonstrators.
https://www.youtube.com/shorts/1GN_0naBhuM
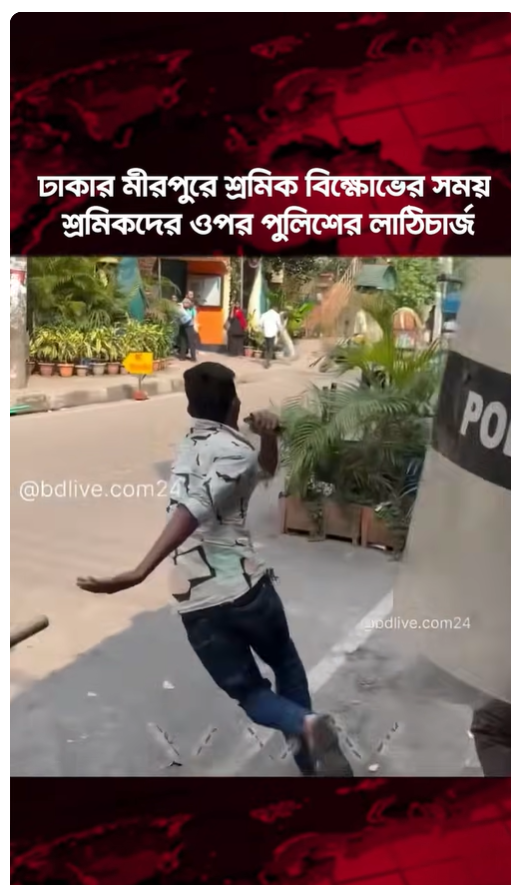
Further research led us to the same video on a Facebook page named ‘Bd Live .com24’, where it was also identified as being from Dhaka.
https://www.facebook.com/reel/39671225852493290
Conclusion
Our research established that the viral video is not related to any incident in Tripura involving an attack on BSF personnel. The video actually shows police baton-charging workers during a protest in Mirpur, Dhaka, Bangladesh. Therefore, the video is being shared with a misleading claim linking it to the alleged attack on BSF personnel in Tripura.
Introduction
For years, the story of terror recruitment in Jammu & Kashmir followed a familiar arc: physical infiltration across the Line of Control, local Over Ground Workers (OGWs) acting as couriers, and recruitment pitches on mainstream apps like WhatsApp and Facebook Messenger. Indian security agencies built entire surveillance architectures around that arc. Now, officials say, the architecture is being outflanked in a way few anticipated: through pornography and dating platforms.
The New Front: Chat Rooms Nobody Is Watching
According to officials cited in recent reporting, Pakistan-based terror handlers working in coordination with Pakistan's ISI have begun exploiting the real-time chat features built into pornography and dating websites to reach recruits in Jammu & Kashmir. These pornography platforms feature real-time chat tools that operate under the guise of helping users find dates nearby, and handlers are exploiting that feature to broadcast messages and coordinate activities. It's a strikingly mundane pivot for an organisation engaged in violent extremism, but that is precisely the point that nobody expects a counter-terror dragnet to be watching a dating chatbox.
Officials say the tactic is designed to evade the surveillance that has become standard on conventional social media platforms, allowing handlers to convey instructions to recruits while staying off the radar of established monitoring tools. WhatsApp, Signal and Facebook Messenger have all, in various ways, become known quantities to Indian intelligence subject to legal intercepts, metadata analysis and years of institutional familiarity. A chat window buried inside an adult content site is not.
Tor, Encrypted Nodes, and Apps Built to Disappear
Other than porn sites, investigators have also flagged a cluster of niche, privacy-first messaging apps that route traffic through Tor-based, encrypted nodes to mask user identity. Security agencies have placed a wide array of specialised digital tools under scrutiny, with terror handlers relying on Tor-based messaging applications like Coatex and Conion to route data through encrypted nodes and obscure user identities. Access to at least one of these apps' installation files is reportedly already restricted within India, though enforcement against sideloaded Android packages remains an uphill battle.
What makes these platforms attractive to handlers isn't unique code so much as the design philosophy behind privacy-first messaging generally. Some of these apps offer only basic encryption, while others go further with end-to-end encryption, self-destructing messages, and strong on-device encryption algorithms that keep data processing off any third-party server. Several reportedly allow account creation without a phone number or SIM verification, stripping away one of the most basic identity anchors that Indian telecom-linked surveillance depends on.
There's also an operational, almost logistical, reason for the shift: connectivity. Officials note that some of these applications provide end-to-end encryption, self-destructing messages and registration without a phone number or email, making it difficult for security agencies to trace users, even as terror networks also shift away from commonly used platforms. In the hilly, forested and often poorly connected terrain of Jammu's border districts, apps engineered to function on weak 2G or EDGE networks have an obvious tactical advantage over data-hungry mainstream platforms.
VPNs, Banned Apps, and a Cat-and-Mouse Game
Virtual Private Networks add another layer of obfuscation, letting operatives access apps banned in India and mask the geographic origin of their traffic. This isn't new tradecraft, but its pairing with adult-content chat infrastructure and Tor-routed messaging represents a genuinely novel combination in the Kashmir context, according to the officials describing the pattern to reporters.
The broader trend line, officials say, is a steady migration away from platforms Indian agencies have learned to monitor. Terror networks are increasingly moving away from mainstream, commonly used platforms in favour of more obscure alternatives, forcing intelligence agencies into a perpetual game of catch-up: each time a monitoring capability matures against one platform, handlers migrate to the next.
This is not the first time investigators have flagged this cat-and-mouse dynamic. Reporting on a recent case in Jammu's Bathindi area described a 19-year-old allegedly radicalised through the encrypted app. Session the same platform reportedly linked to suspects in a Delhi bomb plot investigation after months of contact with Pakistan-based handlers. Investigators in that case noted that terror organisations have increasingly turned to multi-layered encrypted messaging services specifically to evade monitoring by intelligence agencies.
The Virtual SIM Problem
Alongside app-layer evasion, foreign-issued virtual SIM cards remain a persistent headache for investigators. The most cited example remains the 2019 Pulwama attack investigation, in which agencies reportedly traced more than 40 virtual SIM cards to the Jaish-e-Mohammed suicide bomber and his network numbers that could be provisioned and abandoned without ever touching an Indian telecom's KYC system. That case became something of a template for how virtual and foreign-registered numbers can be used to build communication chains that are extremely difficult to map after the fact, since there is no physical SIM, no retail purchase record, and often no domestic carrier data trail at all.
More recent J&K cases echo the same pattern in a different form. Police investigating a cross-border radicalisation network noted that intelligence agencies now suspect unauthorised SIM card distribution is being used by terrorists to communicate with handlers across the border, part of a broader push to choke off the logistical and communication backbone that keeps sleeper modules alive even when direct physical contact with a local handler is minimal or non-existent.
How Agencies Are Responding
To their credit, security agencies aren't standing still. Officials say cyber-surveillance frameworks are actively being redesigned to map and intercept these "off-grid" communication channels, a phrase that itself signals how far outside traditional monitoring territory this recruitment method has moved. Agencies say they continue to adapt their cyber-surveillance frameworks specifically to map and intercept these off-grid communication channels. That has included moving to restrict access to specific APKs, tightening scrutiny of virtual number providers, and, as seen in recent CIK (Counter Intelligence Kashmir) operations, proactively disrupting online propaganda networks before recruitment pitches can mature into operational plots. One recent CIK operation, for instance, intercepted attempts to recruit two teenage boys who were allegedly being fed terror content in the direction of a Pakistan-based handler, underlining how young the target pool for these campaigns has become.
Conclusion
What this episode really illustrates isn't a single clever trick but a structural truth about counter-terror surveillance: it is inherently reactive. Every time agencies build competence around a platform, handlers find a low-attention, high-friction-to-monitor alternative: first fringe messaging apps, then Tor-routed clients, and now the sprawling, largely unregulated back-end of adult content platforms, which few people would ever think to associate with national security. It's a reminder that the fight against radicalisation online is no longer confined to obviously "extremist" corners of the internet; it can hide in plain sight, inside the most ordinary-looking corners of the web.
Sources
- New J-K terror tactic: Pornography apps, Tor network used for secret messaging — The Tribune
- New J&K terror tactic: Handlers turn to porn sites, encrypted apps to contact recruits — Deccan Herald
- Terrorists using porn website, encrypted apps for chats with recruits — Organiser
- New J&K Terror Tactic: Pornography Apps, Tor Network Used For Secret Messaging — Kashmir Dot Com
- From WhatsApp to Porn Sites: Terror Groups Adopt New Digital Tactic in J&K — Jammu Kashmir Now
- Jammu teenager's arrest exposes cross-border radicalisation network — The Tribune
- After OGW network, J&K cops target communication channel of terrorists — The Tribune
- CIK busts online radical network, foils recruitment of two minors — The Tribune

Introduction
Law grows by confronting its absences, it heals through its own gaps. States often find themselves navigating a shared frontier without a mutual guide or lines of law in an era of expanding digital boundaries and growing cyber damages. The United Nations General Assembly ratified the United Nations Convention against Cybercrime on December 24, 2024, and more than sixty governments were in attendance in the signing ceremony on 24th & 25th October this year, marking a moment of institutional regeneration and global commitment.
A new Lexicon for Global Order
The old liberal order is being strained by growing nationalism, economic fracturing, populism, and great-power competition as often emphasised in the works of scholars like G. John Iken berry and John Mearsheimer. Multilateral arrangements become more brittle in such circumstances. Therefore, the new cybercrimes convention represents not only a legal tool but also a resurgence of international promise, a significant win for collective governance in an uncertain time. It serves as a reminder that institutions can be rebuilt even after they have been damaged.
In Discussion: The Fabric of the Digital Polis
The digital sphere has become a contentious area. On the one hand, the US and its allies support stakeholder governance, robust individual rights, and open data flows. On the other hand, nations like China and Russia describe a “post-liberal cyber order” based on state mediation, heavily regulated flows, and sovereignty. Instead of focusing on ideological dichotomies, India, which is positioned as both a rising power and a voice of the Global South, has offered a viewpoint based on supply-chain security, data localisation, and capacity creation. Thus, rather than being merely a regulation, the treaty arises from a framework of strategic recalibration.
What Changed & Why it Matters
There have been regional cybercrime accords up to this point, such as the Budapest Convention. The goal of this new international convention, which is accessible to all UN members, is to standardise definitions, evidence sharing and investigation instruments. 72 states signed the Hanoi signature event in October, 2025, demonstrating an unparalleled level of scope and determination. In addition to establishing structures for cooperative investigations, extradition, and the sharing of electronic evidence, it requires signatories to criminalise acts such as fraud, unlawful access to systems, data interference, and online child exploitation.
For the first time, a legally obligatory global architecture aims to harmonise cross-border evidence flows, mutual legal assistance, and national procedural laws. Cybercrime offers genuine promise for community defence at a time when it is no longer incidental but existential, attacks on hospitals, schools and infrastructure are now common, according to the Global Observatory.
Holding the Line: India’s Deliberate Path in the Age of Cyber Multilateralism
India takes a contemplative rather than a reluctant stance towards the UN Cybercrime Treaty. Though it played an active role during the drafting sessions and lent its voice to the shaping of global cyber norms, New Delhi is yet to sign the convention. Subtle but intentional, the reluctance suggests a more comprehensive reflection, an evaluation of how international obligations correspond with domestic constitutional protections, especially the right to privacy upheld by the Supreme Court in Puttaswamy v. UOI (2017).
Prudence is the reason for this halt. Policy circles speculate that the government is still assessing the treaty’s consequences for national data protection, surveillance regimes, and territorial sovereignty. Officials have not provided explicit justifications for India’s refusal to join. India’s position has frequently been characterised by striking a careful balance between digital sovereignty and taking part in cooperative international regimes. In earlier negotiations, India had even proposed including clauses to penalise “offensive messages” on social media, echoing the erstwhile Section 66A of the IT Act, 2000, but the suggestion found little international traction.
Advocates for digital rights such as Raman Jit Singh Chima of Access Now have warned that ensuring that the treaty’s implementation upholds constitutional privacy principles may be necessary for India to eventually endorse it. He contends that the treaty’s wording might not entirely meet India’s legal requirements in the absence of such voluntary pledges.
UN Secretary-General Antonio Guterres praised the agreement as “a powerful, legally binding instrument to strengthen our collective defences against “cybercrime” during its signing in Hanoi. The issue for India is to make sure that multilateral collaboration develops in accordance with constitutional values rather than to reject that vision. Therefore, the path forward is one of assertion rather than absence, careful march towards a cyber future that protects freedom and sovereignty.
