
#FactCheck - Deepfake Video Falsely Links Shah Rukh Khan to Rajpal Yadav Case
Executive Summary
A video featuring popular comedian Rajpal Yadav has recently gone viral on social media, claiming that he is currently lodged in Tihar Jail in connection with a loan default and cheque bounce case. In connection with this, another video showing Bollywood superstar Shah Rukh Khan is being widely shared online. In the viral clip, Khan is purportedly seen saying that he would help Rajpal Yadav get out of jail and also offer him a role in his upcoming film. However, research by the CyberPeace found the viral video to be fake. The clip is a deepfake, in which the audio has been manipulated using artificial intelligence. In the original video, Shah Rukh Khan is speaking about his life and personal experiences. Although several prominent Bollywood personalities have expressed support for Rajpal Yadav, the claims made in the viral video are misleading.
Claim
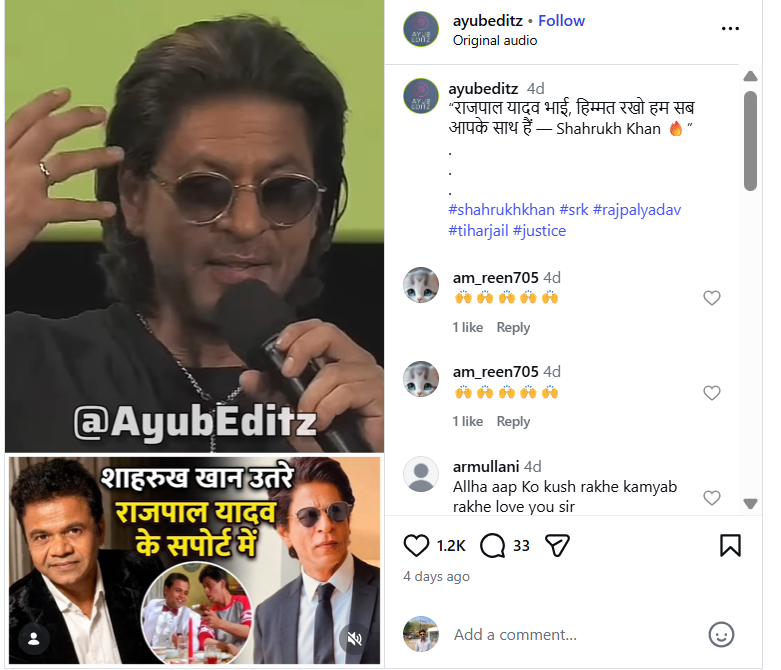
An Instagram user named “ayubeditz” shared the viral video on February 11, 2026, with the caption: “Rajpal Yadav bhai, stay strong, we are all with you — Shah Rukh Khan.” The link to the post and its archived version are provided below.
Fact Check
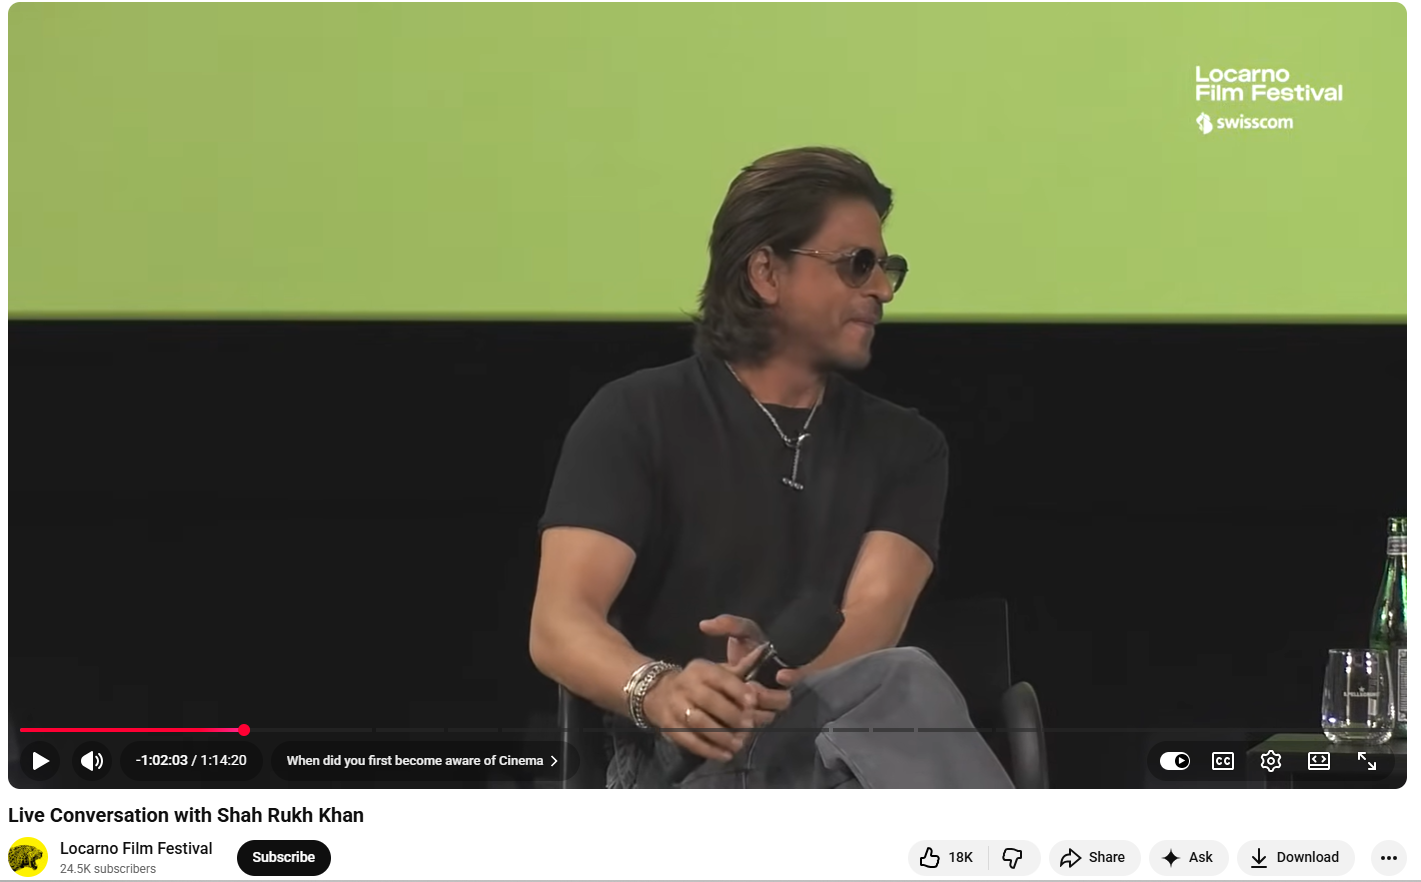
To verify the claim, we extracted key frames from the viral video and conducted a Google reverse image search. This led us to the original video uploaded on a YouTube channel titled “Locarno Film Festival” on August 11, 2024. According to the available information, Shah Rukh Khan was sharing insights about his life and career during a conversation with the festival’s Artistic Director, Giona A. Nazzaro. This raised strong suspicion that the viral video had been edited using AI.
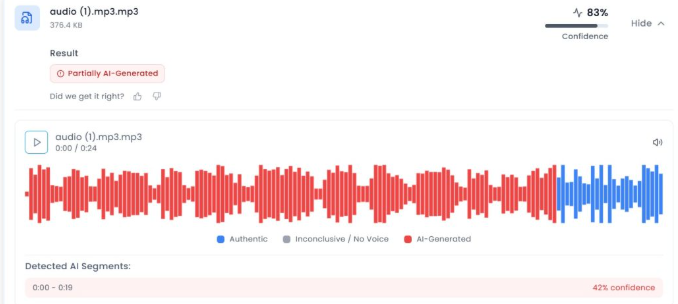
To further examine the authenticity of the audio, we analysed it using AI detection tools. The audio was first checked using Aurigin.ai, which indicated an 83 percent probability that the voice in the viral clip was AI-generated.
Conclusion
The CyberPeace’s research confirmed that the claim associated with Shah Rukh Khan’s viral video is false. The video is a deepfake in which the audio has been altered using artificial intelligence. In the original footage, Khan was discussing his life and experiences, and he did not make any statement about helping Rajpal Yadav.

Related Blogs

Introduction
In the vast, cosmic-like expanse of international relations, a sphere marked by the gravitational pull of geopolitical interests, a singular issue has emerged, casting a long shadow over the fabric of Indo-Canadian diplomacy. It is a narrative spun from an intricate loom, interlacing the yarns of espionage and political machinations, shadowboxing with the transient, yet potent, specter of state-sanctioned violence. The recent controversy undulating across this geopolitical landscape owes its origins to the circulation of claims which the Indian Ministry of External Affairs (MEA) vehemently dismisses as a distorted tapestry of misinformation—a phantasmagoric fable divorced from reality.
This maelstrom of contention orbits around the alleged existence of a 'secret memo', a document reportedly dispatched with stealth from the helm of the Indian government to its consulates peppered across the vast North American continent. This mysterious communique, assuming its spectral presence within the report, was described as a directive catalyzing a 'sophisticated crackdown scheme' against specific Sikh diaspora organizations. A proclamation that MEA has repudiated with adamantine certainty, branding the report as a meticulously fabricated fiction.
THE MEA Stance
The official statement from the Indian Ministry of External Affairs (MEA) emerged as a paragon of clarity cutting through the dense fog of accusations, 'We strongly assert that such reports are fake and emphatically concocted. The referenced memo is non-existent. This narrative is a chapter in the protracted saga of a disinformation campaign aimed against India.' The outlet responsible for airing this contentious story, as per the Indian authorities, has a historical penchant for circulating narratives aligned with the interests of rival intelligence agencies, particularly those associated with Pakistani strategic circles—a claim infusing yet another complex layer to the situation at hand.
The report that catapulted itself onto the stage with the force of an untamed tempest insists the 'secret memo' was decked with several names—all belonging to individuals under the hawk-like gaze of Indian intelligence.
The Plague of Disinformation
The profoundly intricate confluence of diplomacy is one that commands grace, poise, and an acute sense of balance—nations effortlessly tip-toeing around sensitivities, proffering reciprocity and an equitable stance within the grand ballroom of international affairs. Hence, when S. Jaishankar, India's Minister of External Affairs, found himself fielding inquiries on the perceived inconsistent treatment afforded to Canada compared to the US—despite similar claims emanating from both—his response was the embodiment of diplomatic discretion: 'As far as Canada is concerned, there was a glaring absence of specific evidence or inputs provided to us. The robust question of equitable treatment between two nations, where only one has furnished substantive input and the other has not, is naturally unmerited.'
The articulation from the Ministry's spokesperson, Arindam Bagchi, further solidified India's stance. He calls into question the credibility of The Intercept—the publication that initially disseminated the report—accusing it of acting as a vessel for 'invented narratives' propagated under the auspices of Pakistani intelligence interests.
Conclusion
In the grand theater of international politics, the distinction between reality and deception is frequently obscured by the heavy drapes of secrecy and diplomatic guile. The persistent denial by the Indian government of any 'secret memo' serves as a critical reminder of the blurred lines between narrative and counter-narrative in the global concert of power and persuasion. As observant spectators within the arena of world politics, we are endowed with the unenviable task of untangling the convoluted web of claims and counterclaims, hoping to uncover the enduring truths that linger therein. In this domain of authentic and imaginary tales, the only unwavering certainty is the persistent rhythm of diplomatic interplay and the subtle shadows it casts upon the international stage. The Ministry of External Affairs fact-checked a claim on the secret memo, rubbishing it as fake and fabricated. The government has said there is a deliberate disinformation campaign that has been on against India.
References
- https://timesofindia.indiatimes.com/india/mea-denies-report-it-issued-secret-memo-on-nijjar-to-missions/articleshow/105884217.cms?from=mdr
- https://www.hindustantimes.com/india-news/india-denies-secret-memo-against-nijjar-report-peddled-by-pak-intelligence-101702229753576.html
Executive Summary
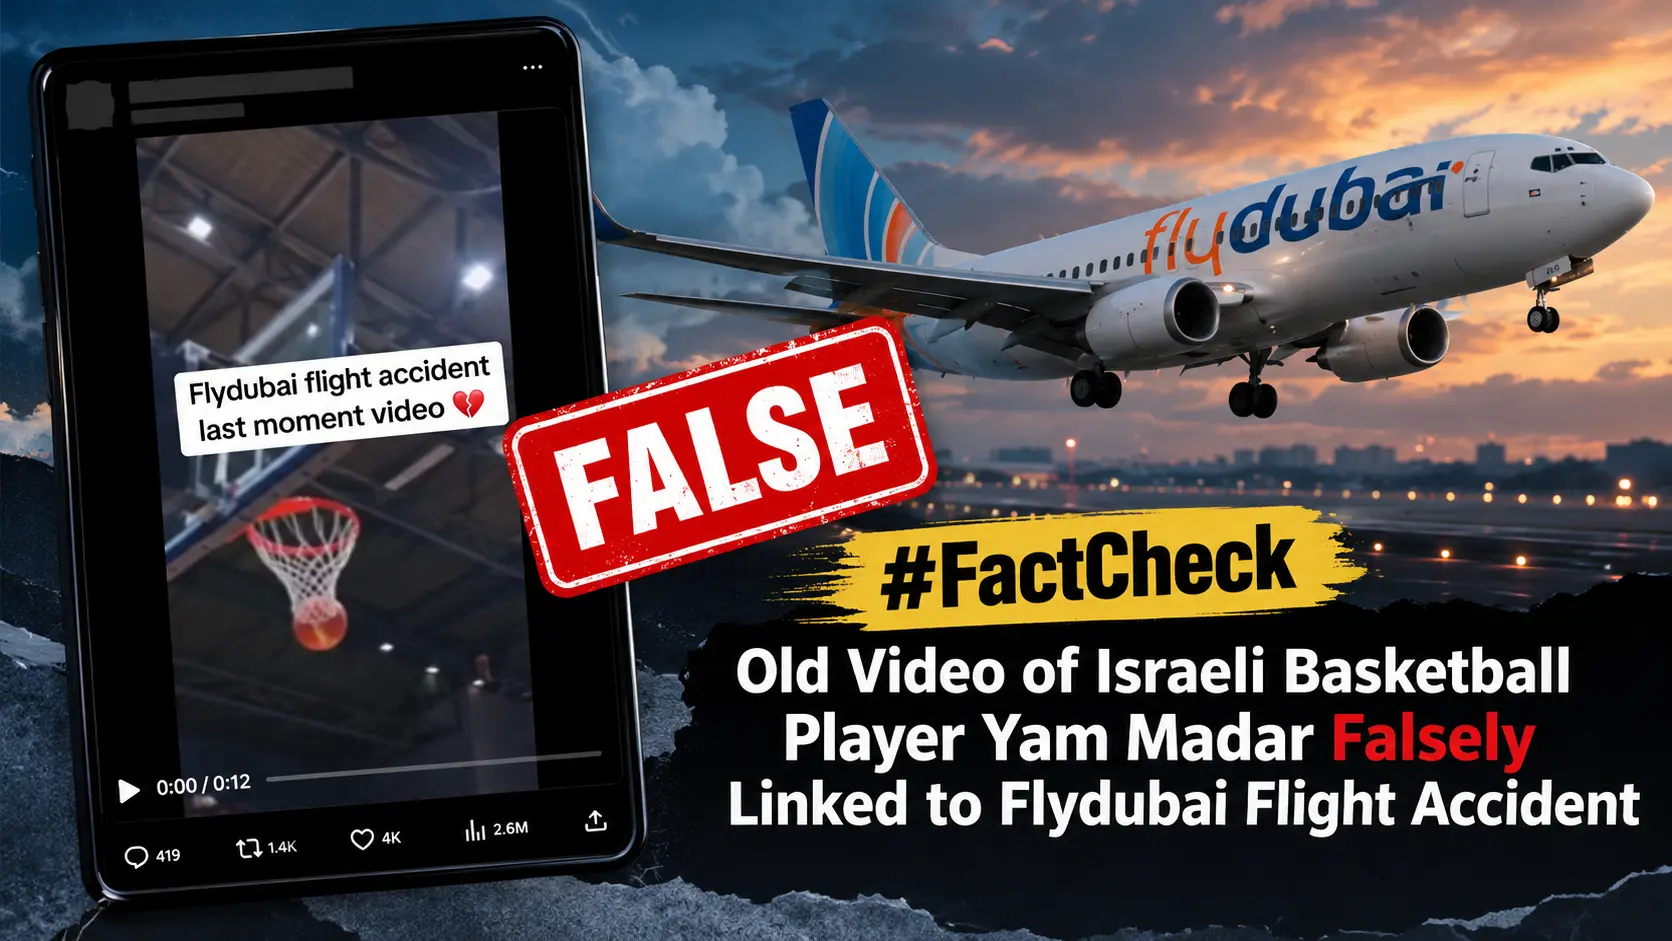
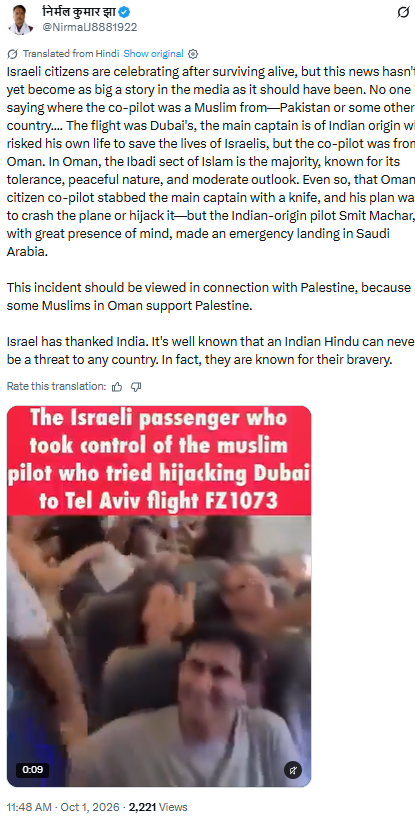
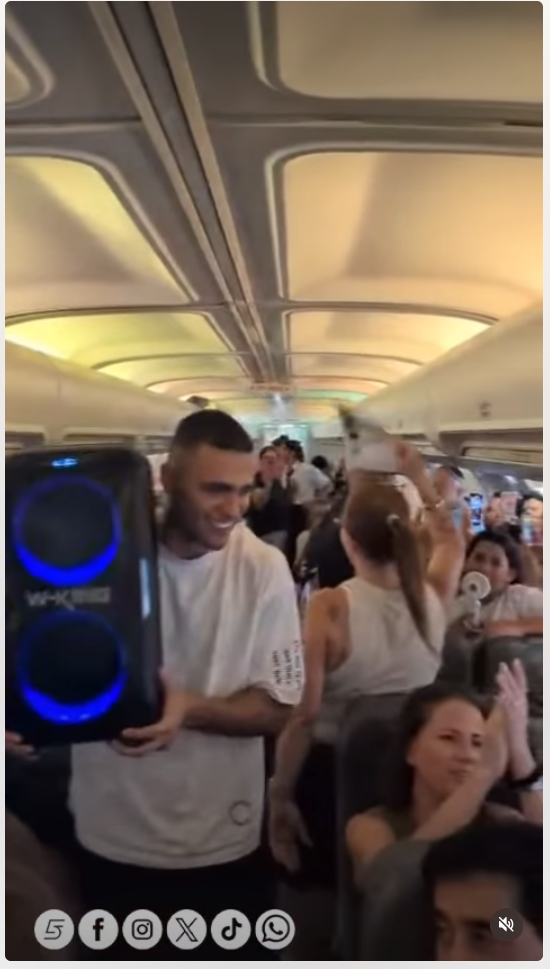
A video showing people dancing inside an aircraft with a speaker playing music is being shared on social media with the claim that they were celebrating after surviving an accident involving a flydubai flight travelling from Dubai to Tel Aviv. However, CyberPeace Research found that the video was actually shared by an Israeli sports media outlet in August 2025, and shows Israeli basketball player Yam Madar playing music through a speaker inside a flight.
Claim
A video is going viral on social media showing a person playing music through a speaker inside an aircraft, while other passengers can be seen dancing to the song being played.
https://x.com/NirmalJ8881922/status/2105542863278973186
Fact Check:
We began our research into the viral video using the InVID tool and extracted several keyframes from it. During this process, we found the same video on the Instagram account of Israeli sports media channel Sports 5, where it was uploaded on August 18, 2025. The video was accompanied by a caption in Hebrew, which translates into Hindi as: “Don’t take a sleeping pill: This is what it’s like to be on a flight with Yam Madar.”
https://www.instagram.com/reels/DNgQrgLsW11/
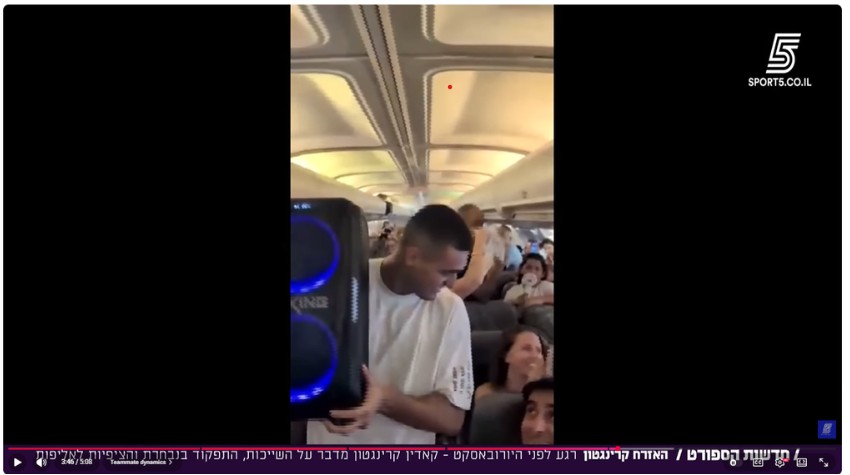
During our research, we also found an interview with another player from the Israeli basketball team, Khadeen Carrington, uploaded on Sports 5’s YouTube channel on August 26, 2025. During the interview, when Carrington was asked about his relationship with the other members of the team, he referred to the aforementioned video featuring Yam Madar.
https://www.youtube.com/watch?v=k_0AzSWlvJw
Conclusion
The evidence gathered during our research makes it clear that the video being linked to the flydubai flight accident is old. The person seen in the video is Yam Madar, a member of the Israeli basketball team.
Executive Summary:
New Linux malware has been discovered by a cybersecurity firm Volexity, and this new strain of malware is being referred to as DISGOMOJI. A Pakistan-based threat actor alias ‘UTA0137’ has been identified as having espionage aims, with its primary focus on Indian government entities. Like other common forms of backdoors and botnets involved in different types of cyberattacks, DISGOMOJI, the malware allows the use of commands to capture screenshots, search for files to steal, spread additional payloads, and transfer files. DISGOMOJI uses Discord (messaging service) for Command & Control (C2) and uses emojis for C2 communication. This malware targets Linux operating systems.
The DISCOMOJI Malware:
- The DISGOMOJI malware opens a specific channel in a Discord server and every new channel corresponds to a new victim. This means that the attacker can communicate with the victim one at a time.
- This particular malware connects with the attacker-controlled Discord server using Emoji, a form of relay protocol. The attacker provides unique emojis as instructions, and the malware uses emojis as a feedback to the subsequent command status.
- For instance, the ‘camera with flash’ emoji is used to screenshots the device of the victim or to steal, the ‘fox’ emoji cracks all Firefox profiles, and the ‘skull’ emoji kills the malware process.
- This C2 communication is done using emojis to ensure messaging between infected contacts, and it is almost impossible for Discord to shut down the malware as it can always change the account details of Discord it is using once the maliciou server is blocked.
- The malware also has capabilities aside from the emoji-based C2 such as network probing, tunneling, and data theft that are needed to help the UTA0137 threat actor in achieving its espionage goals.
Specific emojis used for different commands by UTA0137:
- Camera with Flash (📸): Captures a picture of the target device’s screen as per the victim’s directions.
- Backhand Index Pointing Down (👇): Extracts files from the targeted device and sends them to the command channel in the form of attachments.
- Backhand Index Pointing Right (👉): This process involves sending a file found on the victim’s device to another web-hosted file storage service known as Oshi or oshi[. ]at.
- Backhand Index Pointing Left (👈): Sends a file from the victim’s device to transfer[. ]sh, which is an online service for sharing files on the Internet.
- Fire (🔥): Finds and transmits all files with certain extensions that exist on the victim’s device, such as *. txt, *. doc, *. xls, *. pdf, *. ppt, *. rtf, *. log, *. cfg, *. dat, *. db, *. mdb, *. odb, *. sql, *. json, *. xml, *. php, *. asp, *. pl, *. sh, *. py, *. ino, *. cpp, *. java,
- Fox (🦊): This works by compressing all Firefox related profiles in the affected device.
- Skull (💀): Kills the malware process in windows using ‘os. Exit()’
- Man Running (🏃♂️): Execute a command on a victim’s device. This command receives an argument, which is the command to execute.
- Index Pointing up (👆) : Upload a file to the victim's device. The file to upload is attached along with this emoji
Analysis:
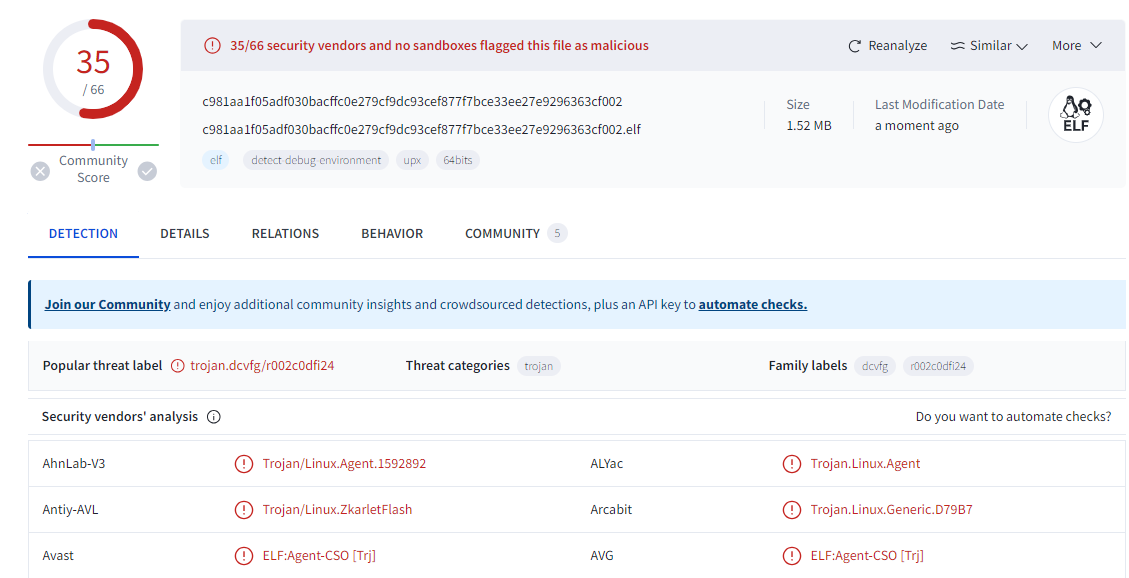
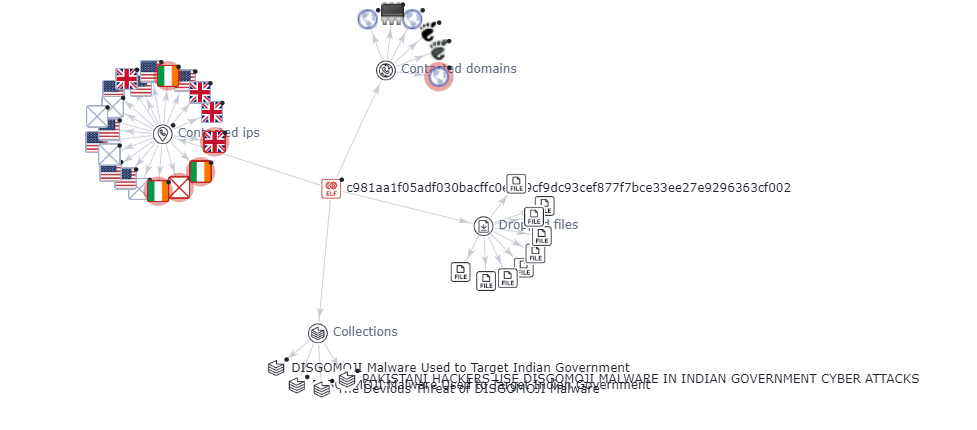
The analysis was carried out for one of the indicator of compromised SHA-256 hash file- C981aa1f05adf030bacffc0e279cf9dc93cef877f7bce33ee27e9296363cf002.
It is found that most of the vendors have marked the file as trojan in virustotal and the graph explains the malicious nature of the contacted domains and IPs.
Discord & C2 Communication for UTA0137:
- Stealthiness: Discord is a well-known messaging platform used for different purposes, which means that sending any messages or files on the server should not attract suspicion. Such stealthiness makes it possible for UTA0137 to remain dormant for greater periods before launching an attack.
- Customization: UTA0137 connected to Discord is able to create specific channels for distinct victims on the server. Such a framework allows the attackers to communicate with each of the victims individually to make a process more accurate and efficient.
- Emoji-based protocol: For C2 communication, emojis really complicates the attempt that Discord might make to interfere with the operations of the malware. In case the malicious server gets banned, malware could easily be recovered, especially by using the Discord credentials from the C2 server.
- Persistence: The malware, as stated above, has the ability to perpetually exist to hack the system and withstand rebooting of systems so that the virus can continue to operate without being detected by the owner of the hacked system.
- Advanced capabilities: Other features of DISGOMOJI are the Network Map using Nmap scanner, network tunneling through Chisel and Ligolo and Data Exfiltration by File Sharing services. These capabilities thus help in aiding the espionage goals of UTA0137.
- Social engineering: The virus and the trojan can show the pop-up windows and prompt messages, for example the fake update for firefox and similar applications, where the user can be tricked into inputting the password.
- Dynamic credential fetching: The malware does not write the hardcoded values of the credentials in order to connect it to the discord server. This also inconveniences analysts as they are unable to easily locate the position of the C2 server.
- Bogus informational and error messages: They never show any real information or errors because they do not want one to decipher the malicious behavior easily.
Recommendations to mitigate the risk of UTA0137:
- Regularly Update Software and Firmware: It is essential to regularly update all the application software and firmware of different devices, particularly, routers, to prevent hackers from exploiting the discovered and disclosed flaws. This includes fixing bugs such as CVE-2024-3080 and CVE-2024-3912 on ASUS routers, which basically entails solving a set of problems.
- Implement Multi-Factor Authentication: There are statistics that show how often user accounts are attacked, it is important to incorporate multi-factor authentication to further secure the accounts.
- Deploy Advanced Malware Protection: Provide robust guard that will help the user recognize and prevent the execution of the DISGOMOJI malware and similar threats.
- Enhance Network Segmentation: Utilize stringent network isolation mechanisms that seek to compartmentalize the key systems and data from the rest of the network in order to minimize the attack exposure.
- Monitor Network Activity: Scanning Network hour to hour for identifying and handling the security breach and the tools such as Nmap, Chisel, Ligolo etc can be used.
- Utilize Threat Intelligence: To leverage advanced threats intelligence which will help you acquire knowledge on previous threats and vulnerabilities and take informed actions.
- Secure Communication Channels: Mitigate the problem of the leakage of developers’ credentials and ways of engaging with the discord through loss of contact to prevent abusing attacks or gaining control over Discord as an attack vector.
- Enforce Access Control: Regularly review and update the user authentication processes by adopting stricter access control measures that will allow only the right personnel to access the right systems and information.
- Conduct Regular Security Audits: It is important to engage in security audits periodically in an effort to check some of the weaknesses present within the network or systems.
- Implement Incident Response Plan: Conduct a risk assessment, based on that design and establish an efficient incident response kit that helps in the early identification, isolation, and management of security breaches.
- Educate Users: Educate users on cybersecurity hygiene, opportunities to strengthen affinity with the University, and conduct retraining on threats like phishing and social engineering.
Conclusion:
The new threat actor named UTA0137 from Pakistan who was utilizing DISGOMOJI malware to attack Indian government institutions using embedded emojis with a command line through the Discord app was discovered by Volexity. It has the capability to exfiltrate and aims to steal the data of government entities. The UTA0137 was continuously improved over time to permanently communicate with victims. It underlines the necessity of having strong protection from viruses and hacker attacks, using secure passwords and unique codes every time, updating the software more often and having high-level anti-malware tools. Organizations can minimize advanced threats, the likes of DISGOMOJI and protect sensitive data by improving network segmentation, continuous monitoring of activities, and users’ awareness.
References:
https://otx.alienvault.com/pulse/66712446e23b1d14e4f293eb
https://thehackernews.com/2024/06/pakistani-hackers-use-disgomoji-malware.html?m=1
https://cybernews.com/news/hackers-using-emojis-to-command-malware/
https://www.volexity.com/blog/2024/06/13/disgomoji-malware-used-to-target-indian-government/
