
#FactCheck: Viral image shows the Maldives mocking India with a "SURRENDER" sign on photo of Prime Minister Narendra Modi
Executive Summary:
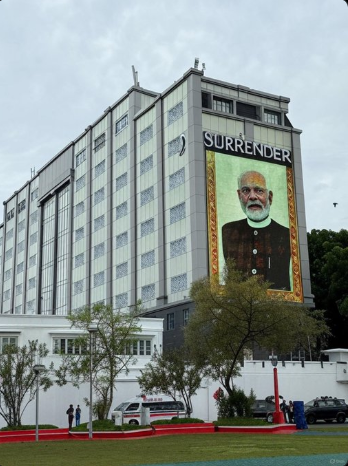
A manipulated viral photo of a Maldivian building with an alleged oversized portrait of Indian Prime Minister Narendra Modi and the words "SURRENDER" went viral on social media. People responded with fear, indignation, and anxiety. Our research, however, showed that the image was manipulated and not authentic.
Claim:
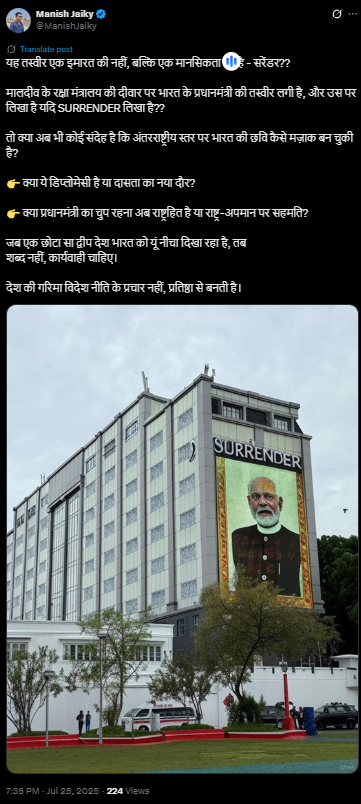
A viral image claims that the Maldives displayed a huge portrait of PM Narendra Modi on a building front, along with the phrase “SURRENDER,” implying an act of national humiliation or submission.
Fact Check:
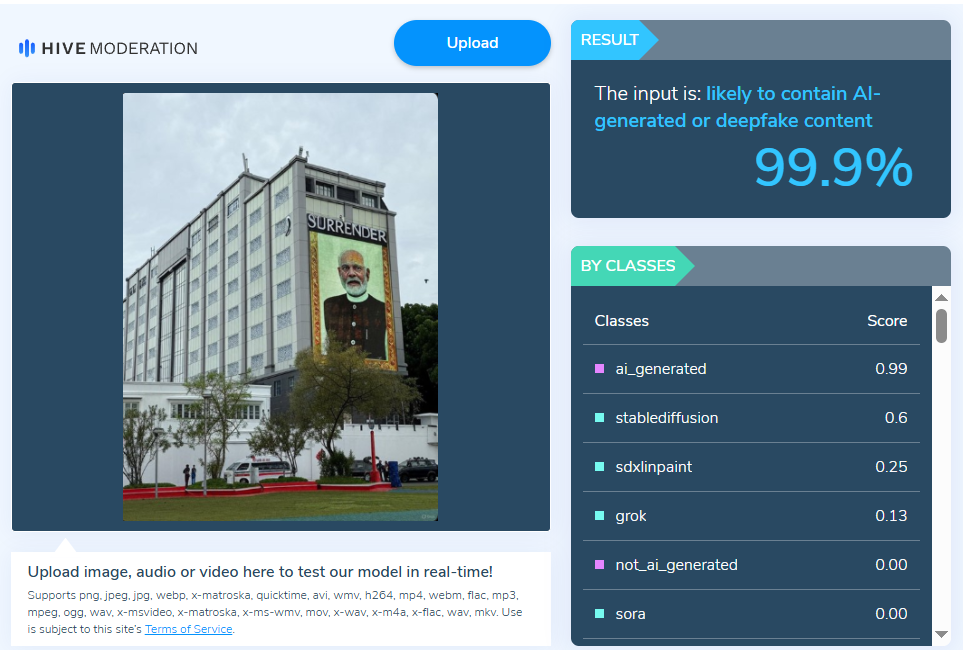
After a thorough examination of the viral post, we got to know that it had been altered. While the image displayed the same building, it was wrong to say it included Prime Minister Modi’s portrait along with the word “SURRENDER” shown in the viral version. We also checked the image with the Hive AI Detector, which marked it as 99.9% fake. This further confirmed that the viral image had been digitally altered.
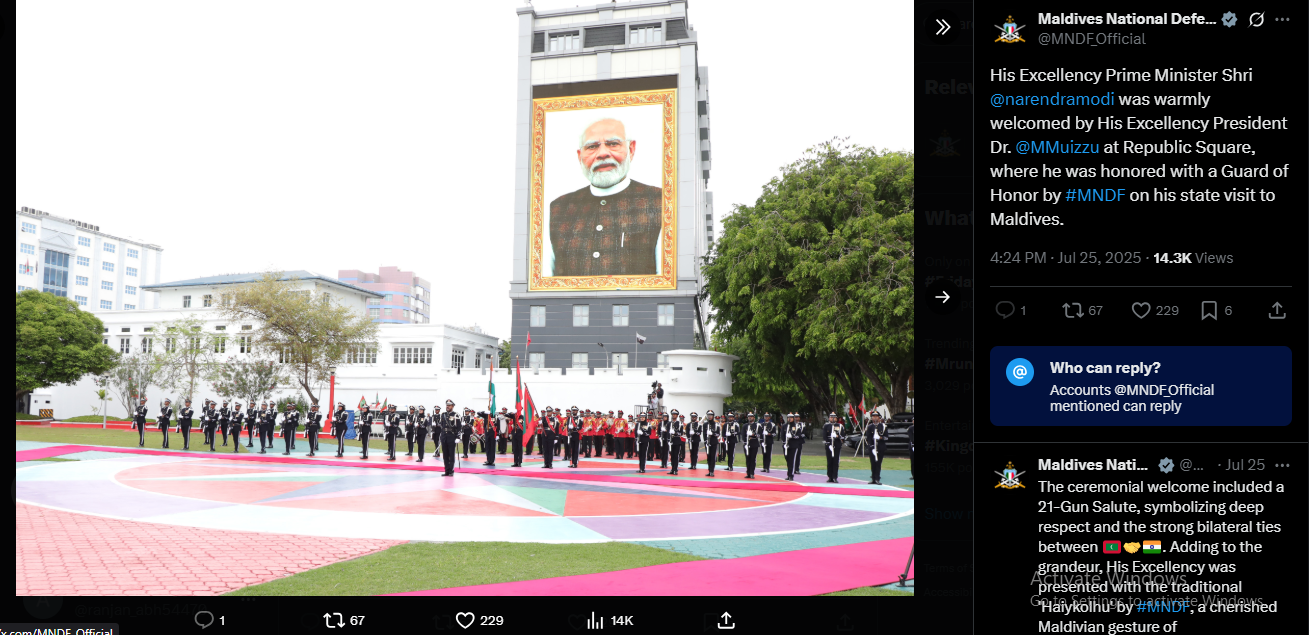
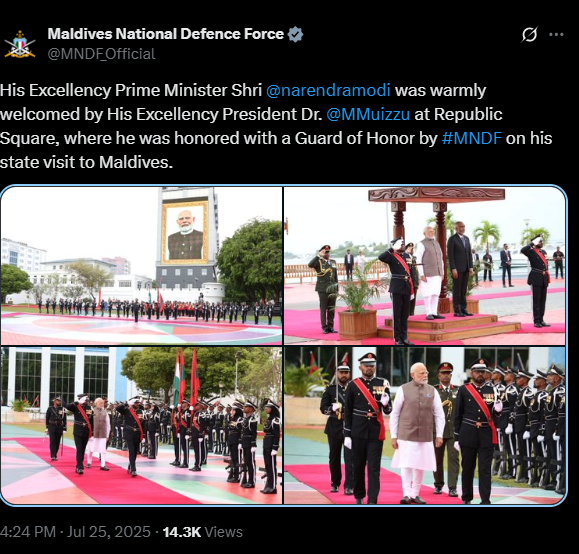
During our research, we also found several images from Prime Minister Modi’s visit, including one of the same building displaying his portrait, shared by the official X handle of the Maldives National Defence Force (MNDF). The post mentioned “His Excellency Prime Minister Shri @narendramodi was warmly welcomed by His Excellency President Dr.@MMuizzu at Republic Square, where he was honored with a Guard of Honor by #MNDF on his state visit to Maldives.” This image, captured from a different angle, also does not feature the word “surrender.
Conclusion:
The claim that the Maldives showed a picture of PM Modi with a surrender message is incorrect and misleading. The image is altered and is being spread to mislead people and stir up controversy. Users should check the authenticity of photos before sharing.
- Claim: Viral image shows the Maldives mocking India with a surrender sign
- Claimed On: Social Media
- Fact Check: False and Misleading

Related Blogs

Executive Summary:
This report discloses a new cyber threat contributing to the list of threats targeting internet users in the name of "Aarong Ramadan Gifts". The fraudsters are imitating the popular Bangladeshi brand Aarong, which is known for its Bengali ethnic wear and handicrafts, and allure the victims with the offer of exclusive gifts for Ramadan. The moment when users click on the link, they are taken through a fictitious path of quizzes, gift boxes, and social proof, that simply could damage their personal information and system devices. Through knowing how this is done we can educate users to take caution and stop themselves from falling into cyber threats.
False Claim:
The false message accompanied by a link on social media, claims that Aarong, one of the most respected brands in Bangladesh for their exquisite ethnic wear and handicrafts, is providing Ramadan gifts exclusively through online promotion. And while that may be the facade of the scam, its real aim is to lead users to click on harmful links that may end up in their personal data and devices being compromised.

The Deceptive Journey:
- The Landing page starts with a salutation and a catchy photo of Aarong store, and later moves ahead encouraging the visitors to take a part of a short quiz to claim the gift. This is designed for the purpose of creating a false image of authenticity and trustworthiness.
- A certain area at the end of the page looks like a social media comment section, and users are posting the positive impacts the claim has on them. This is one of the techniques to build the image of a solid base of support and many partakers.
- The quiz starts with a few easy questions on how much the user knows about Aarong and their demographics. This data is vital in the development of more complex threats and can be used to address specific targets in the future.
- After the user hits the OK button, the screen displays a matrix of the Gift boxes, and the user then needs to make at least 3 attempts to attain the reward. This is a commonly used approach which allows the scammer to keep users engaged longer and increases the chances of making them comply with the fraudulent scheme.
- The user is instructed to share the campaign on WhatsApp from this point of the campaign, and the user must keep clicking the WhatsApp button until the progress bar is complete. This is a way to both expand and perpetuate the scam, affecting many more users.
- After completing the steps, the user is shown instructions on how to claim the prize.
The Analysis:
- The home page and quiz are structured to maintain a false impression of genuineness and proficiency, thus allowing the victims to partake in the fraudulent design. The compulsion to forward the message in WhatsApp is the way they inspire more and more users and eventually get into the scam.
- The final purpose of the scam could be to obtain personal data from the user and eventually enter their devices, which could lead to a higher risk of cyber threats, such as identity theft, financial theft, or malware installation.
- We have also cross-checked and as of now there is no well established and credible source or any official notification that has confirmed such an offer advertised by Aarong.
- The campaign is hosted on a third party domain instead of the official Website, this raised suspicion. Also the domain has been registered recently.
- The intercepted request revealed a connection to a China-linked analytical service, Baidu in the backend.

- Domain Name: apronicon.top
- Registry Domain ID: D20231130G10001G_13716168-top
- Registrar WHOIS Server: whois.west263[.]com
- Registrar URL: www.west263[.]com
- Updated Date: 2024-02-28T07:21:18Z
- Creation Date: 2023-11-30T03:27:17Z (Recently created)
- Registry Expiry Date: 2024-11-30T03:27:17Z
- Registrar: Chengdu west dimension digital
- Registrant State/Province: Hei Long Jiang
- Registrant Country: CN (China)
- Name Server: amos.ns.cloudflare[.]com
- Name Server: zara.ns.cloudflare[.]com
Note: Cybercriminal used Cloudflare technology to mask the actual IP address of the fraudulent website.
CyberPeace Advisory:
- Do not open those messages received from social platforms in which you think that such messages are suspicious or unsolicited. In the beginning, your own discretion can become your best weapon.
- Falling prey to such scams could compromise your entire system, potentially granting unauthorized access to your microphone, camera, text messages, contacts, pictures, videos, banking applications, and more. Keep your cyber world safe against any attacks.
- Never, in any case, reveal such sensitive data as your login credentials and banking details to entities you haven't validated as reliable ones.
- Before sharing any content or clicking on links within messages, always verify the legitimacy of the source. Protect not only yourself but also those in your digital circle.
- For the sake of the truthfulness of offers and messages, find the official sources and companies directly. Verify the authenticity of alluring offers before taking any action.
Conclusion:
Aarong Ramadan Gift scam is a fraudulent act that takes advantage of the victims' loyalty to a reputable brand. The realization of the mechanism used to make the campaign look real, can actually help us become more conscious and take measures to our community not to be inattentive against cyberthreats. Be aware, check the credibility, and spread awareness to others wherever you can, to contribute in building a security conscious digital space.
Introduction
On September 1–2, 2026, the G20 Innovation Ministerial was held at the Carolina Inn in Chapel Hill, North Carolina. This gathering of ministers, senior officials, and high-profile technology executives marked the first sectoral ministerial of the G20 presidency held by the U.S. government this year. The two consensus documents that resulted from the meeting, the G20 Innovation Ministerial Statement and the Carolina Principles, are expected to dictate how the largest world economies regulate AI for many years. In this post, the content of the two documents will be discussed along with their role in the larger context of the U.S. G20 presidency that will culminate in the leaders’ summit in Miami scheduled for December and the response of the tech community, allied governments, and civil society to the framework.
The U.S. Presidency and the Road to Chapel Hill
The United States assumed the rotating G20 presidency on December 1, 2025, and immediately signalled a departure from the priorities pursued by South Africa, the previous chair, whose 2025 Johannesburg summit had emphasised climate finance and debt sustainability for developing economies, a summit the U.S. ultimately boycotted. In its opening statement, the State Department announced that the American presidency would organise the year around three themes: reducing regulatory burdens on economic growth, securing affordable and reliable energy supply chains, and "pioneering new technologies and innovations". The Innovation Ministerial in Chapel Hill was the clearest single expression of that third pillar, and it was scheduled ahead of the finance ministers' meetings in Asheville and the foreign ministers' meetings in Atlanta, with the full cycle set to close at the Leaders' Summit at Trump National Doral in Miami on December 14–15, 2026.
Symbolism was deliberately built into the choice of venue. White House science and technology advisor Michael Kratsios, who chaired the ministerial, argued that North Carolina's Research Triangle and its status as home to the nation's first public university made Chapel Hill an apt backdrop for a statement about translating research into commercial and public benefit. The venue also produced the framework's name: the Carolina Principles.
The Innovation Ministerial Statement: Six Pillars
The Innovation Ministerial Statement is organised around six pillars:
pro-innovation policy frameworks; technology for opportunity and prosperity (chiefly AI adoption in public services);
- skilled technical workforce development;
- intellectual property policy for AI;
- standards that support both AI-enabled standards development and standards for AI systems; and
- industrial innovation and supply-chain resilience.
All six ideas run together in one concept: "Old-fashioned or too rigid regulatory systems can limit innovation in an unintended way," and successful policymaking, short of restricting entrepreneurial initiatives, consists of creating the type of regulatory framework which is effective and flexible. The language is also marked by sensitivity to sovereignty, stating repeatedly that countries have the right "to formulate their policies and express their sovereignty on issues of emerging technology governance" and thus make it possible for twenty countries with different legislative customs to agree upon one text.
On IP, the statement treats the copyright-AI interface as unresolved by design, noting that questions about how doctrines such as prior consent and fair-use-style exceptions apply to AI training "remain appropriately resolved through each member's established legal processes" rather than through a harmonised international rule. On standards, it frames AI itself as a tool for regulatory efficiency for comparing safety and performance data across jurisdictions and reducing duplicative testing while affirming that market competition, not government selection, should determine which AI models succeed.
The Carolina Principles: Structuring the Technology Lifecycle
Where the Ministerial Statement sets out aspirations, the Carolina Principles operationalise them across the "science and technology development lifecycle". The document is structured in three parts. The first, Advancing Discovery and Strengthening Technology Development, calls for sustained public investment in foundational research, blended public-private financing across technology readiness levels, and streamlined administrative processes for R&D funding. The second, Accelerating Validation and Commercialisation, is the most operationally specific section, endorsing regulatory sandboxes, results-based funding mechanisms, and innovation-orientated public procurement to help technologies cross the gap from laboratory to market. The third, Enabling Technology Adoption, is the section that has drawn the most political attention: it commits members to apply existing sector-specific regulatory frameworks to AI wherever possible and to reserve new rulemaking only for "novel considerations that existing legal frameworks cannot adequately address" as defined in The Carolina Principles for Emerging Technologies, 2026, Section III.
That last commitment is the crux of what commentary has called the U.S.'s "light-touch" pitch to the world. Rather than proposing a new international AI regulator, the Carolina Principles ask governments to extend the jurisdiction of existing sector regulators and financial supervisors handling AI in finance and health authorities handling AI in medical devices and to treat novel, cross-cutting AI regulation as an exception rather than a default. Commerce Secretary Howard Lutnick announced that all twenty G20 members, including China, endorsed the framework, calling it a product of "an enormous amount of work" given the divergent starting positions in the room. The timing was pointed: the framework was finalised roughly a month after the European Union's AI Act reached its most consequential enforcement milestone, with binding obligations for high-risk AI systems taking effect on August 2, 2026, a contrast Elon Musk, participating in the ministerial, invoked directly in criticising EU-style regulation.
Reception: Consensus Inside, Scepticism Outside
Inside the Carolina Inn, the mood among industry leaders was buoyant. In a fireside conversation with Secretary Lutnick, OpenAI's Sam Altman described AI as "incredible magic of intelligence in a bottle" while warning that continued infrastructure build-out, more data centres, and more compute would be necessary to keep costs manageable. Nvidia's Jensen Huang and Palantir's Alex Karp offered similarly optimistic assessments, and Anthropic's participation in a voluntary model-testing arrangement with the U.S. government's safety and security institute was cited by OSTP Director Kratsios as evidence that industry-government cooperation, rather than statutory mandate, could deliver trustworthy AI.
Outside the security perimeter, several hundred demonstrators, like students, faculty, and local organisers, gathered to protest what they characterised as an unaccountable alliance between government and AI capital, chanting slogans against both the technology's labour-market effects and the data centre buildout it requires. The juxtaposition captured a tension that runs beneath the consensus text itself: a framework designed to secure the broadest possible international agreement necessarily says less about how risks Labour displacement, energy demand, and algorithmic harm will be managed than it does about how innovation will be accelerated.
Conclusion
The Carolina Principles represent a coherent and, by G20 standards, unusually specific attempt to answer a question that has vexed multilateral technology governance for a decade: how do twenty economies with incompatible regulatory philosophies agree on anything regarding AI? The answer Chapel Hill produced was to agree on process rather than on substantive limits. Whether that process-based consensus proves durable will depend on what happens between now and the Miami Leaders' Summit in December, when heads of state, rather than ministers, will decide whether to elevate the Carolina Principles into the G20's broader economic agenda or treat them as a single ministerial's contribution to a much longer conversation.
References
- https://assets.publishing.service.gov.uk/media/6a996786f5b35599aec19180/g20-innovation-ministerial
- https://www.commerce.gov/sites/default/files/2026-09/THE-CAROLINA-PRINCIPLES-FOR-EMERGING-TE
- https://www.commerce.gov/news/press-releases/2026/09/g20-innovation-ministerial-concludes-conseNSUS statement
- https://www.whitehouse.gov/releases/2026/09/g20-innovation-ministerial-concludes-with-consensus-sstatement/
- https://www.state.gov/policy-issues/g20/feed/
- https://g20.org/g20-united-states/
- https://dailytarheel.com/480187/university/university-g20-event-1/
- https://qz.com/g20-us-light-touch-ai-framework-chapel-hill-090326
- https://explainx.ai/blog/g20-carolina-principles-ai-regulation-chapel-hill-2026
- https://enterprisedna.co/resources/news/us-g20-carolina-principles-ai-regulation-enterprise-september-2026/
- https://www.cnbc.com/2026/09/02/g20-innovation-ministerial-live-updates.html
- https://fortune.com/2026/09/05/tech-ceos-ai-data-centers-g20-protests-sam-altman-nvidia-jensen-huang-palantir-alex-karp-chapel-hill-north-carolina-ai-backlash/
- https://www.wunc.org/education/2026-09-02/protest-chapel-hill-unc-g20-innovation-technology-sam-a
- https://www.cfr.org/articles/us-g20-presidency-narrow-agenda-2026

Introduction
India’s telecom regulator, the Telecom Regulatory Authority of India (TRAI), has directed telcos to block all unverified headers and message templates within 30 and 60 days, respectively, according to a press release. The regulator observed that telemarketers were ‘misusing’ headers and message templates of registered parties and asked telcos to reverify all registered headers & message templates on the DLT (Distributed Ledger Technology) platform. All telecom service providers (TSP) have to comply with these directions, issued under the Telecom Commercial Communication Customer Preference Regulations, 2018, within a month, TRAI said in its release. The directions were issued after TRAI held a meeting with telcos on February 17, 2023, to discuss quality of service (QoS) improvements, review of QoS standards, QoS of 5G services and unsolicited commercial communications”, as per its press release.
Why it matters?
It may be useful as it can ensure that all promotional messages are sent through registered telemarketers using only approved templates. It is no secret that the spam problem has been difficult to rein in, so the measure can restrict its proliferation and filter out telemarketers resorting to misuse.
Details about TRAI’s orders
The release said that telcos have to ensure that temporary headers are deactivated immediately after the time duration for which such headers were created. The telcos also have to ensure that there is no space to insert unwanted content in the template of a message where one can add content to be sent to people. Message recipients should not be confused, so telcos must ensure that they register no lookalike headers in the names of different senders.
Measures to check unregistered telemarketers
The release ordered telcos to bar telemarketers not registered on its DLT platform from accessing message templates and scrubbing them to deliver spam messages to recipients on the telco’s network. The telcos have been directed not to allow promotional messages to be sent by unregistered telemarketers or telemarketers using 10-digit telephone numbers. It added that telcos have to take action against erring telemarketers and share details of these telemarketers with other telcos, which will then be responsible for stopping these entities from sending commercial communications through their networks.
How big is the problem of spam?
A survey conducted by LocalCircles said that two out of every three people (66 per cent) in India get three or more spam calls daily. It added that not one person among thousands of respondents checked the box of ‘no spam’.
The platform said that it was a national survey which gathered over 56,000 responses from Indians located in 342 districts. It also found that 92 % of responders said they continue receiving spam despite opting for DND. The DND list is a feature where mobile subscriber can register their number to avoid getting unsolicited commercial communication (UCC).
Addressing the problem of spam
The regulatory body recently released a consultation paper that proposed the idea of providing the real name identity of callers to people receiving calls. The paper said that it would use a database containing each subscriber’s correct name to implement the caller name presentation (CNAP) service. The regulator wants to use details acquired by telecom service providers via customer acquisition forms (CAF).
TRAI formed a joint committee to look at the issue of phishing and cyber fraud in 2022. It included officials from the Reserve Bank of India (RBI) and the Securities and Exchange Board of India (SEBI). The telecom watchdog had laid out a plan to combat SMS and call spam using blockchain technology (DLT). It saw telecom companies and TRAI to build an encrypted and distributed database that will record user consent to be included in SMS or call send-out lists.
According to a press release, the Telecom Regulatory Authority of India (TRAI), the telecom regulator in India, has ordered carriers to block any unverified headers and message templates within 30 and 60 days, respectively.
The regulator saw that telemarketers were “misusing” registered parties’ headers and message templates. Thus, they requested that telecoms validate all of the registered headers and message templates on the DLT (Distributed Ledger Technology) platform.
According to TRAI’s statement, all telecom service providers (TSP) must adhere to these directives within one month under the 2018 Telecom Commercial Communication Consumer Preference Rules. The guidelines were released following a conference with telcos convened by TRAI on February 17, 2023, to discuss quality of service (QoS) enhancements, a review of QoS standards, the QoS of 5G services, and unsolicited commercial communications.
Why it matters?
Requiring that only registered telemarketers send promotional communications using approved templates may prove to be a beneficial safeguard. It is no secret that the spam problem has been challenging to control, so the measure can limit its spread and screen out telemarketers that employ abusive tactics.
Information on the TRAI order
According to the press release, telecoms must ensure that temporary headers are deactivated as soon as the time period they were established has passed. The telecoms must also ensure that there is no room in the message template where one can add content to be sent to recipients for unwanted content. There should be no room for uncertainty among message recipients. Thus, telecoms must ensure that no similar-looking headers are registered under the identities of various senders.
Taking action against unregistered telemarketers In accordance with the directive, telcos must prevent telemarketers who are not registered on their DLT platform from obtaining message templates and using them to send spam to subscribers on their network. Telemarketers who are not registered or who use 10-digit phone numbers cannot send promotional messages, according to instructions given to telecoms. Telcos must take action against misbehaving telemarketers, it was noted, and divulge their information to other telecoms, who would be in charge of preventing these companies from transmitting commercial messages.
How widespread is the spam issue?
According to a LocalCircles poll, three or more spam calls are received every day by two out of every three Indians (66%) on average. It further stated that not a single one of the thousands of responses clicked the “no-spam” box. According to the platform, the survey was conducted nationally and received over 56,000 responses from Indians in 342 districts. Moreover, 92 % of respondents reported that even after choosing DND, they still receive spam. A mobile subscriber can register their number on the DND list to prevent receiving unsolicited commercial communication (UCC).
consultation document recently in which it recommended the concept of providing the genuine name identify of callers to persons receiving calls. The paper indicated that it would employ a database containing each subscriber’s correct name to implement the caller name presentation (CNAP) service. The regulator wants to use information collected by telecom service providers through client acquisition forms (CAF).
Conclusion
TRAI established a joint committee to examine the problem of phishing and cyber scams in 2022. Officials from the Securities and Exchange Board of India (SEBI) and Reserve Bank of India (RBI) were present (SEBI).
The telecom watchdog had outlined a strategy for leveraging blockchain technology to combat SMS and call spam (DLT).
