
#FactCheck: Viral video claims Ahmedabad plane crash but actually a Hollywood Movie Clip
Executive Summary:
A viral video claiming the crash site of Air India Flight AI-171 in Ahmedabad has misled many people online. The video has been confirmed not to be from India or a recent crash, but was filmed at Universal Studios Hollywood on a TV or movie set meant to look like a plane crash set piece for a movie.

Claim:
A video that purportedly shows the wreckage of Air India Flight AI-171 after crashing in Ahmedabad on June 12, 2025, has circulated among social media users. The video shows a large amount of aircraft wreckage as well as destroyed homes and a scene reminiscent of an emergency, making it look genuine.

Fact check:
In our research, we took screenshots from the viral video and used reverse image search, which matched visuals from Universal Studios Hollywood. It became apparent that the video is actually from the most famous “War of the Worlds" set, located in Universal Studios Hollywood. The set features a 747 crash scene that was constructed permanently for Steven Spielberg's movie in 2005. We also found a YouTube video. The set has fake smoke poured on it, with debris scattered about and additional fake faceless structures built to represent a scene with a larger crisis. Multiple videos on YouTube here, here, and here can be found from the past with pictures of the tour at Universal Studios Hollywood, the Boeing 747 crash site, made for a movie.


The Universal Studios Hollywood tour includes a visit to a staged crash site featuring a Boeing 747, which has unfortunately been misused in viral posts to spread false information.

While doing research, we were able to locate imagery indicating that the video that went viral, along with the Universal Studios tour footage, provided an exact match and therefore verified that the video had no connection to the Ahmedabad incident. A side-by-side comparison tells us all we need to know to uncover the truth.


Conclusion:
The viral video claiming to show the aftermath of the Air India crash in Ahmedabad is entirely misleading and false. The video is showing a fictitious movie set from Universal Studios Hollywood, not a real disaster scene in India. Spreading misinformation like this can create unnecessary panic and confusion in sensitive situations. We urge viewers to only trust verified news and double-check claims before sharing any content online.
- Claim: Massive explosion and debris shown in viral video after Air India crash.
- Claimed On: Social Media
- Fact Check: False and Misleading

Related Blogs
Executive Summary
A video of Russian President Vladimir Putin and Chinese President Xi Jinping is being shared on social media. In the video, the two leaders can be seen cooking together and interacting with each other.The video is being linked to the BRICS Summit held at Bharat Mandapam in Delhi on September 12 and 13, 2026, with the claim that Putin and Xi Jinping were seen in this manner during the summit. The viral claim was found to be false in CyberPeace Research Wing’s research. Our research revealed that the video being shared on social media is not recent. The video dates back to 2018, when Russian President Vladimir Putin and Chinese President Xi Jinping cooked together during the Eastern Economic Forum held in Vladivostok, Russia.
Claim:
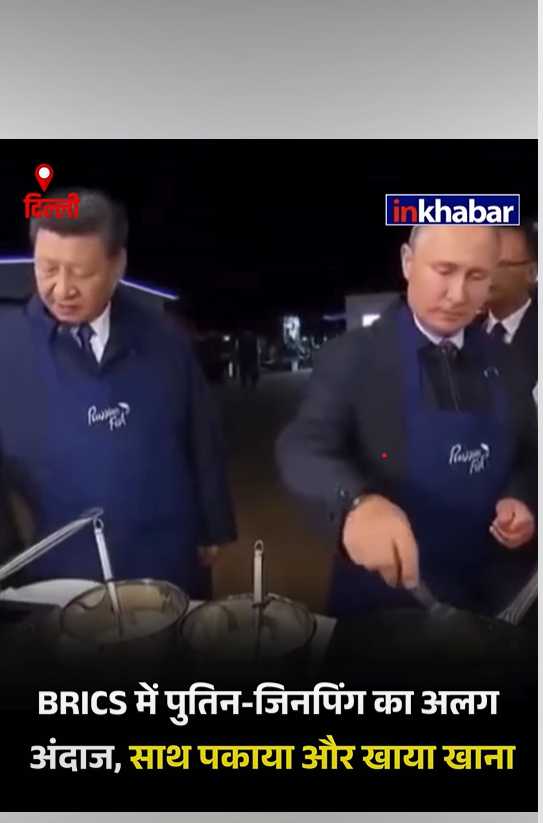
A Facebook user shared the viral video with the caption: “Russian President Vladimir Putin and Chinese President Xi Jinping enjoyed cooking and sharing a meal together in India. The special camaraderie between the two leaders was on display during the BRICS Summit.” The link to the post, along with an archive link and screenshot, is provided below.
https://www.instagram.com/reels/DdOFovfkelC/
Factcheck
To verify the authenticity of the viral claim, we conducted a reverse image search of the keyframes from the video. During the search, we found visuals matching the video on the Armenpress website, published on September 12, 2018. The link to the post and the screenshot are provided below.
https://armenpress.am/en/article/946878
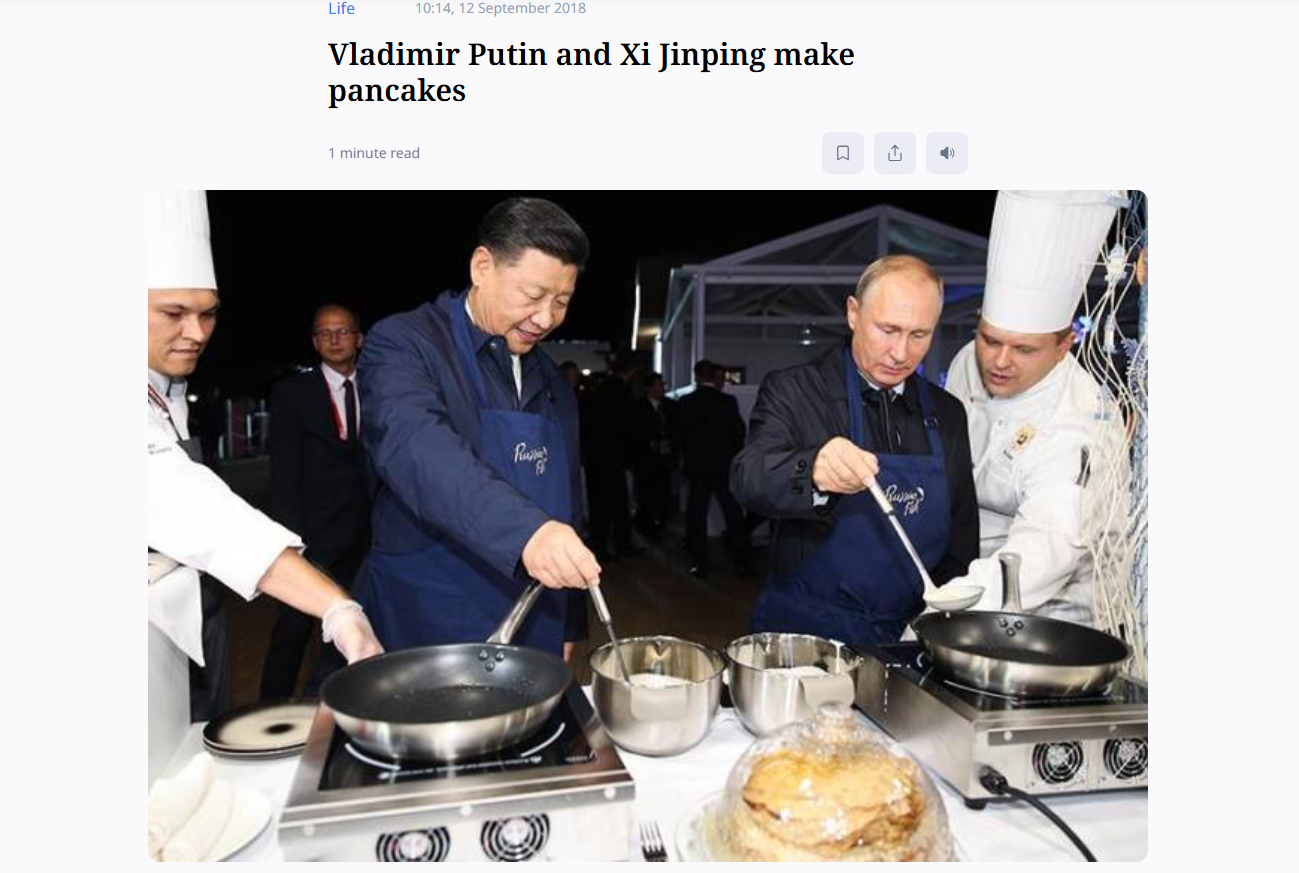
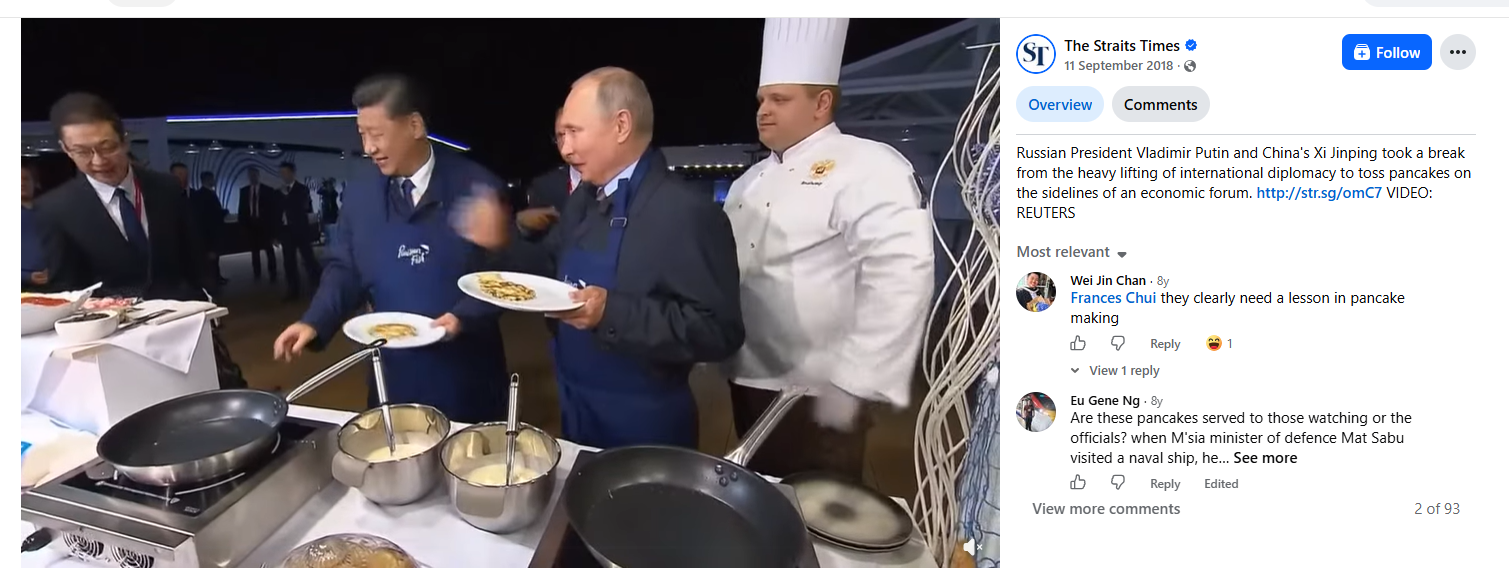
According to the report, Russian President Vladimir Putin and Chinese President Xi Jinping took a break from the hectic schedule of international diplomacy on Tuesday to make pancakes on the sidelines of an economic forum. Chinese President Xi Jinping was among the prominent leaders attending the event in Russia’s Far Eastern city of Vladivostok. The forum primarily focused on economic ties and issues related to North Korea.During the event, the two leaders made blini, a traditional Russian pancake, together at an exhibition called “Far East Street”, which showcased the region’s cultural and economic achievements. Photographs showed Putin and Xi Jinping wearing blue aprons as they poured pancake batter onto a griddle and flipped the pancakes. They later enjoyed the pancakes with caviar and vodka. As we continued our research, we found the same video on The Straits Times’ Facebook page, where it was published on September 11, 2018. According to the information provided with the video, Russian President Vladimir Putin and Chinese President Xi Jinping took a break from the hectic schedule of international diplomacy to make pancakes together on the sidelines of an economic forum. The link to the post and the screenshot are provided below.
https://www.facebook.com/watch/?v=1915270415222092
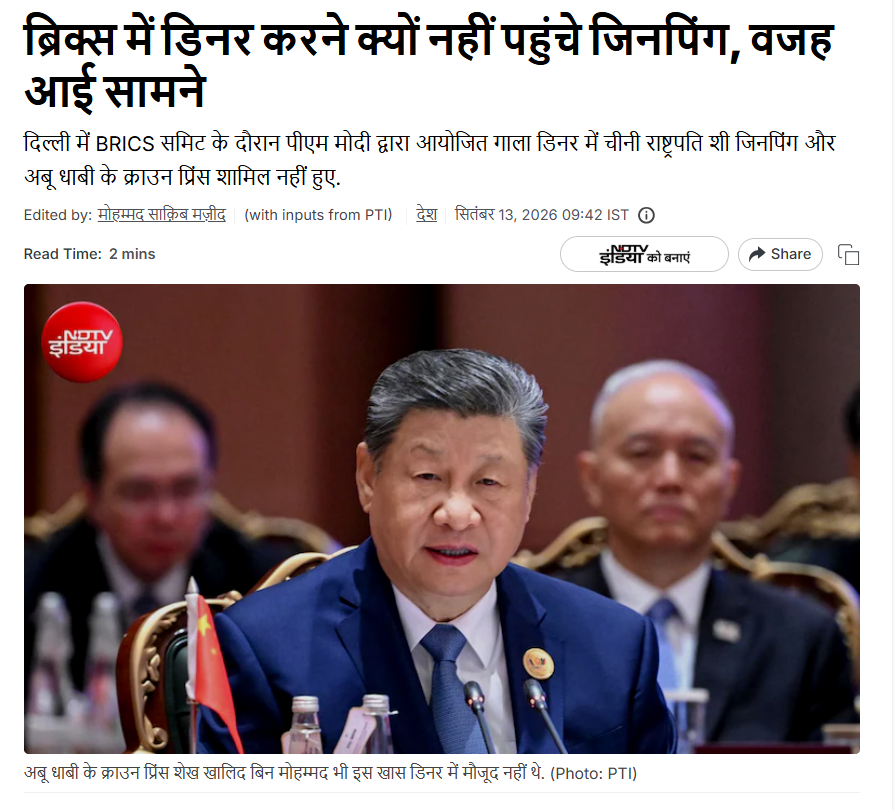
Meanwhile, for context, according to a report by a news agency, the BRICS Summit was underway in Delhi. Saturday was an important day of the summit, and Prime Minister Narendra Modi hosted a dinner for several heads of state, including Chinese President Xi Jinping. Several leaders, including Russian President Vladimir Putin, attended the special dinner. However, Chinese President Xi Jinping was not present. According to sources cited by the news agency, Xi Jinping did not attend the dinner.
https://ndtv.in/india/chinese-president-xi-jinping-skips-brics-gala-dinner-what-reason-12039666
Conclusion
Our research found that the video showing Russian President Vladimir Putin and Chinese President Xi Jinping making pancakes together is not recent and has no connection with the 2026 BRICS Summit held in Delhi. The claim circulating on social media is therefore false and misleading. Further research established that the video dates back to 2018, when Putin and Xi participated in the Eastern Economic Forum in Vladivostok, Russia. During the event, the two leaders were seen preparing traditional Russian pancakes, or blini, together at an exhibition showcasing the cultural and economic achievements of Russia’s Far East region. Therefore, the video is being shared with a false context by linking an old 2018 event to the recently held BRICS Summit.

Introduction
Digital Public Infrastructure (DPI) serves as the backbone of e-governance, enabling governments to deliver services more efficiently, transparently, and inclusively. By leveraging information and communication technology (ICT), digital governance systems reconfigure traditional administrative processes, making them more accessible and citizen-centric. However, the successful implementation of such systems hinges on overcoming several challenges, from ensuring data security to fostering digital literacy and addressing infrastructural gaps.
This article delves into the key enablers that drive effective DPI and outlines the measures already undertaken by the government to enhance its functionality. Furthermore, it outlines strategies for their enhancement, emphasizing the need for a collaborative, secure, and adaptive approach to building robust e-governance systems.
Key Enablers of DPI
Digital Public Infrastructure (DPI), the foundation for e-governance, relies on common design, robust governance, and private sector participation for efficiency and inclusivity. This requires common principles, frameworks for collaboration, capacity building, and the development of common standards. Some of the key measures undertaken by the government in this regard include:
- Data Protection Framework: The Digital Personal Data Protection (DPDP) Act of 2023 establishes a framework to ensure consent-based data sharing and regulate the processing of digital personal data. It delineates the responsibilities of data fiduciaries in safeguarding users' digital personal data.
- Increasing Public-Private Partnerships: Refining collaboration between the government and the private sector has accelerated the development, maintenance, expansion, and trust of the infrastructure of DPIs, such as the AADHAR, UPI, and Data Empowerment and Protection Architecture (DEPA). For example, the Asian Development Bank attributes the success of UPI to its “consortium ownership structure”, which enables the wide participation of major financial stakeholders in the country.
- Coordinated Planning: The PM-Gati Shakti establishes a clear coordination framework involving various inter-governmental stakeholders at the state and union levels. This aims to significantly reduce project duplications, delays, and cost escalations by streamlining communication, harmonizing project appraisal and approval processes, and providing a comprehensive database of major infrastructure projects in the country. This database called the National Master Plan, is jointly accessible by various government stakeholders through APIs.
- Capacity Building for Government Employees: The National e-Governance Division of the Ministry of Electronics and Information Technology routinely rolls out multiple training programs to build the technological and managerial skills required by government employees to manage Digital Public Goods (DPGs). For instance, it recently held a program on “Managing Large Digital Transformative Projects”. Additionally, the Ministry of Personnel, Public Grievances, and Pensions has launched the Integrated Government Online Training platform (iGOT) Karmayogi for the continuous learning of civil servants across various domains.
Digital Governance; Way Forward
E-governance utilizes information and communication technology (ICT) such as Wide Area Networks, the Internet, and mobile computing to implement existing government activities, reconfiguring the structures and processes of governance systems. This warrants addressing certain inter-related challenges such as :
- Data Security: The dynamic and ever-changing landscape of cyber threats necessitates regular advancements in data and information security technologies, policy frameworks, and legal provisions. Consequently, the digital public ecosystem must incorporate robust data cybersecurity measures, advanced encryption technologies, and stringent privacy compliance standards to safeguard against data breaches.
- Creating Feedback Loops: Regular feedback surveys will help government agencies improve the quality, efficiency, and accessibility of digital governance services by tailoring them to be more user-friendly and enhancing administrative design. This is necessary to build trust in government services and improve their uptake among beneficiaries. Conducting the decennial census is essential to gather updated data that can serve as a foundation for more informed and effective decision-making.
- Capacity Building for End-Users: The beneficiaries of key e-governance projects like Aadhar and UPI may have inadequate technological skills, especially in regions with weak internet network infrastructure like hilly or rural areas. This can present challenges in the access to and usage of technological solutions. Robust capacity-building campaigns for beneficiaries can provide an impetus to the digital inclusion efforts of the government.
- Increasing the Availability of Real-Time Data: By prioritizing the availability of up-to-date information, governments and third-party enterprises can enable quick and informed decision-making. They can effectively track service usage, assess quality, and monitor key metrics by leveraging real-time data. This approach is essential for enhancing operational efficiency and delivering improved user experience.
- Resistance to Change: Any resistance among beneficiaries or government employees to adopt digital governance goods may stem from a limited understanding of digital processes and a lack of experience with transitioning from legacy systems. Hand-holding employees during the transitionary phase can help create more trust in the process and strengthen the new systems.
Conclusion
Digital governance is crucial to transforming public services, ensuring transparency, and fostering inclusivity in a rapidly digitizing world. The successful implementation of such projects requires addressing challenges like data security, skill gaps, infrastructural limitations, feedback mechanisms, and resistance to change. Addressing these challenges with a strategic, multi-stakeholder approach can ensure the successful execution and long-term impact of large digital governance projects. By adopting robust cybersecurity frameworks, fostering public-private partnerships, and emphasizing capacity building, governments can create efficient and resilient systems that are user-centric, secure, and accessible to all.
References
- https://www.adb.org/sites/default/files/publication/865106/adbi-wp1363.pdf
- https://www.jotform.com/blog/government-digital-transformation-challenges/
- https://aapti.in/wp-content/uploads/2024/06/AaptixONI-DPIGovernancePlaybook_compressed.pdf
- https://community.nasscom.in/sites/default/files/publicreport/Digital%20Public%20Infrastructure%2022-2-2024_compressed.pdf
- https://proteantech.in/articles/Decoding-Digital-Public-Infrastructure-in-India/
Introduction
On June 2nd, 2026, even as thousands of Class 12 students across the nation flocked to submit re-evaluation and verification applications on the CBSE’s newly rolled-out On-Screen Marking (OSM) portal, a decidedly different kind of visitor had logged in an attacker carrying automation scripts, botnet traffic, and malicious intentions to either shut the system down or steal its contents. The attack, which CBSE then openly reported on its official X account, flooded the portal with 1.5 million hits in two minutes and sent over a lakh unauthorized file access attempts.
Understanding the Attack Architecture: The Two-Pronged Operation
The CBSE cyberattack was actually not a single exploit but rather a layered, orchestrated attack. The attack can be understood in two prongs:
- The DoS Attack:Firstly, attackers initiated a large-scale DoS (Denial of Service) attack, producing approximately 1.5 million requests in 120 seconds, or approximately 12,500 per second, in order to saturate the server. By overloading the systems with bogus requests, the attackers sought not just to disable the site but also to throw off security personnel from their primary task of stabilizing the portal during its launch period.
The File Probing: These attacks usually include the following methods:
- Path Traversal Attacks - Attackers will attempt to navigate outside of the current directory by supplying inputs such as "../../etc/passwd" in URL parameters or in a file upload.
- Forced Browsing / Directory Enumeration - An attacker may have used tools to attempt to find vulnerable files and directories like answer sheets, exam scans, student identification documents, and admin-related files by systematically guessing names.
- API Endpoint Fuzzing: If any REST or GraphQL API was present for the portal, the attacker may have tried sending a various number of inputs to parameters to attempt to retrieve records, find IDORs, or escalate privileges.
- Session Token Harvesting - For high-load environments, some systems may use insecure session management. Attackers would attempt to predict or guess the token to hijack another student's or administrator's session.
Why Are Educational Portals High-Value Targets?
Here's why the Indian education sector is an attractive target for cyber-attacks:
- Concentrated PII: Millions of students are present on these education portals, and their data (names, birth dates, Aadhaar linkage information, parents' details, address, education profiles, etc.) is of the highest value on the dark web and can be used for identity theft, financial fraud, credential reuse, and targeting.
- Low Investment Relative to the Data Value: The education system is chronically under-invested in cybersecurity. Many of these systems were built for a function/scale, rather than security by design, and are highly vulnerable.
- High-Pressure Launches: Launching a massive, public-facing system like the CBSE OSM verification site that needs to service millions of students on day 1 often requires time constraints that preclude proper penetration testing, stress testing, security auditing, or staged deployment; these launches often launch with numerous known security flaws.
- Large Attack Surface: The education ecosystem is comprised of many integrated systems, APIs, cloud instances, third-party systems, and authentication infrastructure. Each dependency increases the overall attack surface and provides multiple potential avenues to compromise these systems, such as IDOR, API abuse, or credential-based attacks.
- Geopolitical Motivation: Following the Op Sindoor attack in 2025, there was a significant increase in public institutions targeted by cyber-attacks with prolonged DDoS against critical systems. Highly visible, public-facing student portals catering to more than 35 million students make a tantalizing target for both nation-state attackers and hacktivist groups to cause disruption or gather intelligence.
The CBSE's Response
A balanced perspective on CBSE's public response is necessary:
- The portal did not go down and served about 14000 users at any point during the attack and had over 28000 successful submissions by 10pm June 2nd.
- In real-time, sessions are continuously being optimized for the students, and session timeouts are being extended.
- Management was on top of the situation and maintained good communication through social media.
To withstand a sustained attack volume of roughly 12,500 requests per second, CBSE would surely need more than one security control implemented on its infrastructure. In all probability, rate limiting was the primary reason it could sustain this attack volume by limiting the requests from an IP or client over a certain period of time and automatically aborting requests from systems sending automated data. This, coupled with perhaps load balancing, will distribute the attack across several systems, none of which will have become bottlenecks. Finally, it is possible that traffic could have also been routed via a Content Delivery System (CDN) or dedicated DDoS mitigation service capable of detecting and cleaning requests of malicious code before they even reach the origin servers.
Technical Recommendations
It is not sustainable for India's exam infrastructure to continue operating in a post-breach, patching-in mode forever. The systems need to embrace Privacy By Design (PBD) as an integral part of their DNA. Here are suggestions for short-term hardening and long-term resilience:
- Deploy a zero-trust file access architecture: Each request to access any file should be authenticated, authorized using role-based access control (RBAC), and logged in an immutable audit trail. Direct access to file paths should not be permissible; rather, pre-signed, time-limited tokens are recommended to control file access.
- Implement a multi-layered DDoS mitigation architecture: A combination of network edge traffic scrubbing (CDNs & DDoS mitigation services) along with rate limiting at the application layer via WAF is necessary. An Anycast-based multi-PoP architecture and pre-provisioning scrubbing capacity may further increase resiliency
- Conduct pre-launch penetration testing and red teaming exercises: Penetration testing with OWASP Top 10 audits, API security reviews, and load-based penetration testing should be conducted by CERT-In empanelled auditors prior to the launch of the examination. The red team exercise should simulate blended DoS and file-probing attacks.
- Secure Payments: The secure payment surface should support PCI-DSS Level 1 certified payments and tokenisation and employ velocity checks against automated abuse and support 3D Secure 2.0 (3DS2) on card payments.
- Implement SOC: Security operations centers (SOCs) should have real-time access to CERT-In threat feeds and ISAC intelligence, allowing them to act quickly on emerging attack vectors before anything malicious can be exploited.
- Encryption: Students' data should be encrypted with AES-256; keys should be stored separately in a Hardware Security Module (HSM) system and not co-located with the data storage system. Student data must also support the data minimisation principle, while storing it should be encrypted with AES-256 and keys should be stored securely in HSM.
- Monitoring: 24/7 SOC monitoring, ongoing vulnerability scanning on all pipelines, anomalous detection baselining, and frequent tabletop exercises for cyber resilience at 24x7 and post-examination activities.
Beyond the Breach: Governance, Accountability, and the Growing Cyber Threat to India's Education Sector
The CBSE attack is merely one example of a wider truth, a truth that extends beyond an isolated security event and highlights security as not only an issue of governance but of national security. Although it was during a period in which there was considerable change in leadership within the CBSE (some officials had been removed from their positions), and although it may be impossible to prevent administrative change, security vulnerability is an inherent risk when it cannot be ensured that the new incumbents have had knowledge transferred from the previous administration in terms of system design, vendor management, configuration, and incident response procedures. It has become apparent that a requirement for digital system governance must be considered to be just as serious a requirement as an academic and administrative governance requirement.
The attack is also indicative of a wider problem, and in 2025 there were in excess of 265 million cyber-attacks, and increasingly, critical infrastructure is being attacked by all manner of actors, including criminals, hacktivists, and state-sponsored groups. Educational institutions offer a prime target due to the amount of personal data held within their systems and the historically low security investment they tend to have. Worldwide trends that support the similar narrative of "data of immense value protected by under-resourced programs" (universities hit by ransomware and mass student data breaches included) are being constantly illustrated. For an examining body of tens of millions of students, cybersecurity cannot be an afterthought and needs to be clearly addressed within the governance and risk-management framework of the institution and, therefore, become a fundamental pillar of public trust.
Conclusion
The June 2026 cyberattack on the CBSE's OSM portal both illustrated the advancing capabilities of today's threat actors and highlighted the critical role cyber resilience must play in India's education sector. A high-volume DoS attack combined with over 100,000 file access attempts indicates a concerted and strategic operation both for disruption and the opportunity for data theft. Though the CBSE's infrastructure did hold, the attack should not offer comfort. Educational institutions are responsible for a significant amount of sensitive personal data, and they are major targets to state-sponsored and financially motivated attackers. Attacks are bound to continue. It is essential that cybersecurity become a fundamental pillar of the governance and trustworthiness of education and not a technical afterthought.
References
- CBSE Official Statement on Cyberattack, X (formerly Twitter), @cbseindia29, June 2, 2026.
- Indian Express, "CBSE OSM Row: Portal attack was a 'coordinated, two-pronged operation' says cybersecurity expert," June 3, 2026.
- Srinivas L, Joint MD & Joint CEO, 63SATS Cybertech (subsidiary of 63 moons technologies limited), was quoted in Indian Express, June 3, 2026.
- The Federal, "CBSE re-evaluation portal faces cyberattack, records 1.5 million hits in two minutes," June 2, 2026. https://thefederal.com
- CERT-In (Indian Computer Emergency Response Team), Empanelled Security Auditor Framework. https://www.cert-in.org.in
- OWASP Top 10 Web Application Security Risks, 2021 edition. https://owasp.org/www-project-top-ten/
- National Institute of Standards and Technology (NIST), Zero Trust Architecture (SP 800-207), August 2020. https://doi.org/10.6028/NIST.SP.800-207
- Indian Express, "What CBSE ignored: Its own panel found glitches in dry run, said delay OSM by a year," June 3, 2026.
- Asianet Newsable, "CBSE Class 12 re-evaluation portal withstands major DoS cyberattack," June 2, 2026. https://newsable.asianetnews.com
