
#FactCheck-Viral Fire Video Falsely Linked to Hezbollah Strike on Israeli Military HQ
Executive Summary
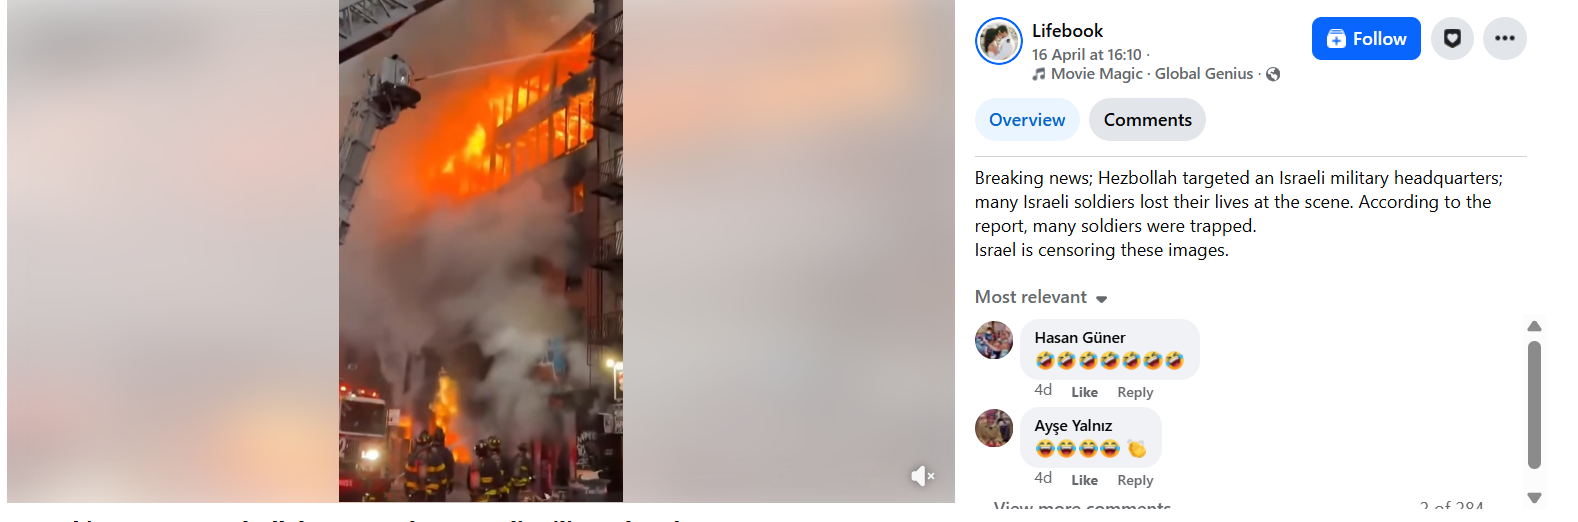
Despite a truce announced in mid-April, sporadic violence has continued between Israel and the Iran-backed Hezbollah in Lebanon. Meanwhile, a video circulating widely on social media shows a multi-storey building engulfed in flames, with users falsely linking it to the ongoing conflict. Posts sharing the clip claim it depicts a Hezbollah strike on an Israeli military headquarters, alleging that several soldiers were killed and that Israel is censoring visuals from the incident. However, research by the CyberPeace Research Wing found the claim to be misleading. The video is unrelated to the Israel-Hezbollah conflict. Verification shows that the footage actually captures a fire at an apartment building in New York City. Firefighters can be seen at the scene attempting to control the blaze.
Claim
A Facebook post shared on April 16, 2026, read: “Breaking news; Hezbollah targeted an Israeli military headquarters; many Israeli soldiers lost their lives at the scene… Israel is censoring these images.” The video has garnered more than 240,000 views.
- https://perma.cc/BQ6X-4LAT
- https://www.facebook.com/watch/?v=1283830349750737
Fact Check
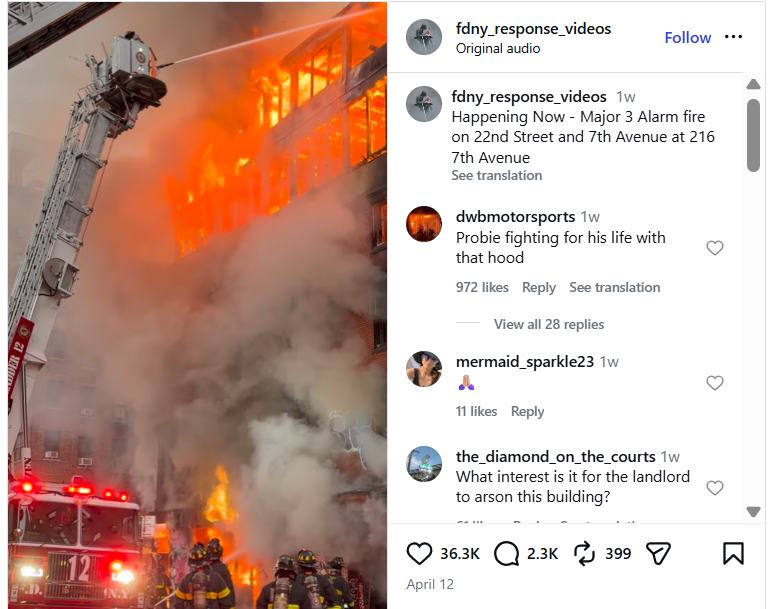
A reverse image search using keyframes from the viral clip led to a higher-quality version posted on April 12, 2026, by an Instagram account titled “FDNY response video.” The caption stated: “Happening now — Major 3 alarm fire on 22nd Street and 7th Avenue at 216 7th Avenue.”
- https://www.instagram.com/p/DXB0ePqjgGD/
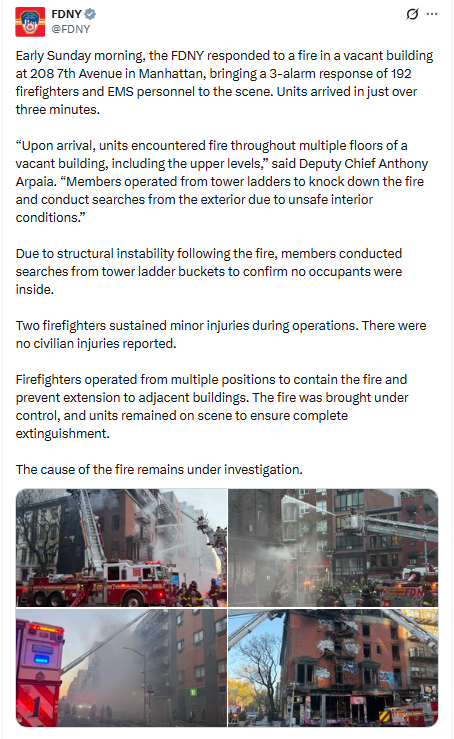
Further verification found that images of the same incident were shared on April 13, 2026, by the official X account of the New York City Fire Department. According to the post, no civilians were injured in the fire, although two firefighters sustained minor injuries while battling the blaze.
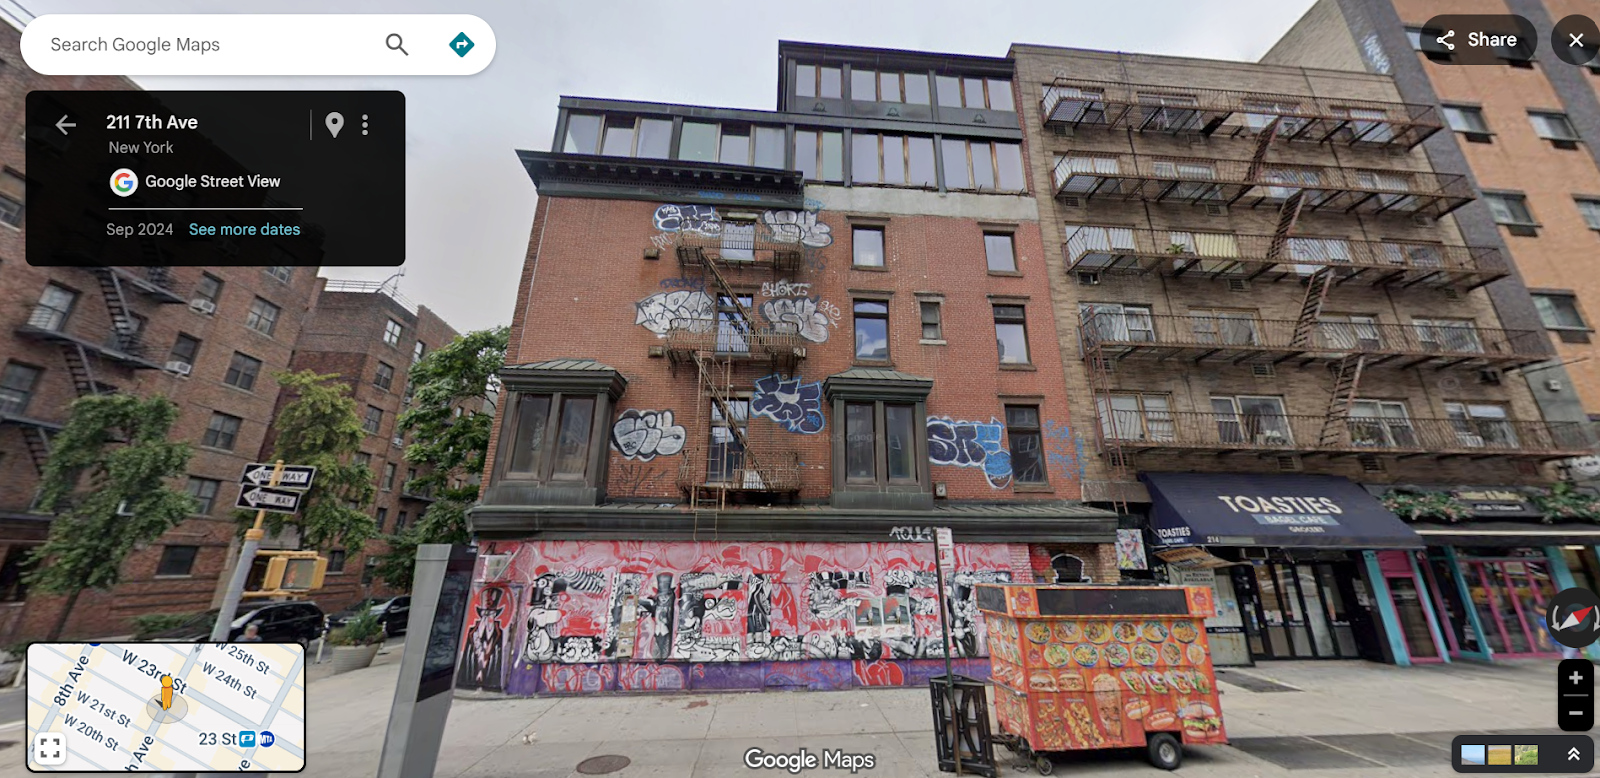
Using the location details mentioned in the posts, visible structures in the video were matched with Google Maps street imagery, confirming that the footage was indeed filmed in New York City.
Conclusion
The research establishes that the viral video is being shared with a false claim. It does not show any attack on an Israeli military facility but rather a residential building fire in New York City.

Related Blogs
Introduction
Recently in July 2026, India's Cyber Crime Coordination Centre (I4C) under the Ministry of Home Affairs quietly tried to do something almost no government has managed before: switch off an app that doesn't need the internet to work. On July 23, 2026, I4C sent takedown notices to Google, Apple and GitHub, ordering them to pull three offline messaging apps – like BitChat, Briar and Bridgefy – from the Play Store, App Store and GitHub's code repository, respectively, giving a three-hour deadline. The notices followed a period of student-led demonstrations at Jantar Mantar, New Delhi, associated with a group "Cockroach Janata Party," a period that also saw a mobile internet shutdown in parts of central Delhi. When Twitter co-founder Jack Dorsey, who built and open-sourced BitChat, publicised the GitHub notice on X, the episode made international news. Google and Apple got near-identical orders the same night, and telecom operators were reportedly told, and then just as quickly untold, to block the apps at the network level. By July 29, all three apps were still live on both app stores, and BitChat's code was still on GitHub. This incident is worth unpacking carefully, because it sits at the intersection of three things most people care about but rarely see explained together: how this technology actually works, what the law actually allows, and why an app can be "banned" on paper while still working perfectly on your phone.
What makes these apps different
Ordinary apps like WhatsApp or Telegram are centralised: your message travels from your phone to a company's server, and then to the recipient's phone. Block or seize the server, and communication stops. BitChat, Briar and Bridgefy are built differently. They use Bluetooth mesh networking, a system where nearby phones talk directly to each other, and each device also relays messages onwards to phones further away, like a bucket brigade. No message ever touches a central server. Briar adds a further layer by routing traffic over Tor, an anonymity network, when internet access is available, and falls back to Bluetooth or Wi-Fi Direct when it isn't. Bridgefy is tuned for larger crowds, useful during concerts, natural disasters, or protests where thousands of phones are packed into a small area and cellular networks buckle under the load. This design, often called decentralised or peer-to-peer communication, is precisely why these apps are useful during disasters and precisely why they worry law enforcement: they keep working when the internet doesn't, whether that's because a cyclone knocked out cell towers or because the government itself ordered a shutdown.
The legal machinery behind a takedown notice
India's power to block online content mainly comes from Section 69A of the Information Technology Act, 2000, which lets the central government order blocking on grounds like sovereignty, public order or preventing incitement to an offence but only through a defined process set out in the IT (Blocking) Rules, 2009: a designated officer, a review committee, and recorded written reasons. The Supreme Court examined this exact provision in its landmark 2015 ruling, Shreya Singhal v. Union of India. While the judgement is best remembered for striking down the vague "offensive speech" law under Section 66A, it separately upheld Section 69A specifically because it came with procedural guardrails, a reasoned order, an opportunity to be heard, and the possibility of judicial review that stopped it from becoming an unchecked censorship tool. The July 23 notices, however, reportedly leaned on a different lever: Section 79(3)(b) of the IT Act, read with Rule 3(1)(d) of the IT Intermediary Guidelines and Digital Media Ethics Code Rules, 2021. That provision governs when an intermediary loses its legal immunity ("safe harbour") for user content if it fails to act on a government or court order, a mechanism built for content takedowns, not necessarily for pulling an entire app off a store shelf within three hours. Legal commentators have flagged this as significant, since Shreya Singhal itself read down Section 79(3)(b) to require action only pursuant to a court order or a properly authorised government direction, not an informal notice. This isn't the first time a mesh-messaging app has run into this machinery. In 2023, following an I4C request, the government blocked Briar and thirteen other apps in Jammu and Kashmir under Section 69A, citing use, the first known instance of Section 69A being used for a regional block. Briar's developers challenged this in the Delhi High Court; in 2024, the court dismissed the challenge, holding that principles of natural justice can give way in matters of national security.
Why you can't easily switch off a mesh network
Here's the technical wrinkle that made the July order largely symbolic: removing an app from the Play Store stops new downloads, but it does nothing to phones that already have it installed, and it does nothing at all to the Bluetooth radios exchanging messages between those phones. Unlike an internet shutdown, which works by controlling the pipes that all traffic must pass through, a mesh network has no chokepoint, no server to seize, no IP address to blacklist, and no single company to compel.
GitHub, for its part, said it followed its standard process of notifying the account holder and offering an appeal before taking any action, which is one reason BitChat's source code stayed publicly accessible throughout. Within a day, officials reportedly told the companies orally that enforcement wasn't necessary after all, though no public clarification or official document has been released explaining why the notices were issued or withdrawn.
Two legitimate, competing interests
None of this means the government's underlying worry is baseless. Law enforcement agencies genuinely lose visibility when communication moves off networks they can lawfully intercept, and coordination of unlawful assembly or violence is a real concern during volatile protests.
The transparency gap
The single biggest problem with how this played out isn't the underlying concern it's the absence of a public, reasoned order. Under the blocking rules, disclosure is restricted, and courts, including the Supreme Court in Anuradha Bhasin v. Union of India, have said that when access is restricted, reasons must be recorded and, where possible, made available. A three-hour notice, issued and then informally withdrawn without explanation, sits uneasily with that standard. A more durable approach, one that CyberPeace and other digital-rights researchers have called for, would combine clearly identified statutory authority; published (even if redacted) reasoning; proportionality review; and investment in lawful digital forensics, rather than blanket app-store takedowns that decentralised technology is, by design, built to survive.
CyberPeace's policy recommendations
Alongside the legal analysis above, CyberPeace puts forward a ten-point framework for how India should approach decentralised communication technologies going forward, instead of defaulting to blanket takedowns:
- Strengthen transparency in blocking decisions
- Ensure statutory clarity
- Apply legality, necessity and proportionality
- Differentiate technology from misuse
- Invest in advanced investigative capabilities
- Establish a multi-stakeholder advisory mechanism
- Develop a framework for emerging decentralised technologies
- Promote responsible innovation
- Enhance public awareness
- Foster international cooperation
Conclusion
The referred incident illustrates that regulating decentralised technologies requires more than swift takedown notices. As communication networks become increasingly resilient and distributed, effective governance must combine legal certainty, technical realism, transparency, and proportionate enforcement. India's challenge is not simply to regulate emerging technologies but to develop a kind of regulatory framework that safeguards national security and the constitutional values of privacy, free expression, and due process.
Sources
- MediaNama — Bitchat was not the only mesh-messaging app targeted by a government takedown notice
- Outlook Business — Beyond GitHub, Govt Also Directed Google To Take Down Bitchat, Briar And Bridgefy
- The Wire — Government Asks GitHub to Remove Bluetooth Messaging App Bitchat Over Concerns of 'Misuse'
- The Tech Trace (Substack) — The Indian govt's crackdown on Bluetooth-enabled messaging apps that wasn't?
- Bar and Bench — Section 69A IT Act and the expanding architecture of digital censorship in India
- Supreme Court Observer — X relies on 'Shreya Singhal' in arbitrary content-blocking case in Karnataka HC
- LiveLaw — Internet Freedom, Shreya Singhal v Union of India, IT Act, Blocking Rules 2009
- Manupatra — Full text, Shreya Singhal v. Union of India (2015) 5 SCC 1
- Open Magazine — CJP Protests at Jantar Mantar: How Offline Mesh Messaging Apps Powered a Network of Resistance

Introduction
A disturbing trend of courier-related cyber scams has emerged, targeting unsuspecting individuals across India. In these scams, fraudsters pose as officials from reputable organisations, such as courier companies or government departments like the narcotics bureau. Using sophisticated social engineering tactics, they deceive victims into divulging personal information and transferring money under false pretences. Recently, a woman IT professional from Mumbai fell victim to such a scam, losing Rs 1.97 lakh.
Instances of courier-related cyber scams
Recently, two significant cases of courier-related cyber scams have surfaced, illustrating the alarming prevalence of such fraudulent activities.
- Case in Delhi: A doctor in Delhi fell victim to an online scam, resulting in a staggering loss of approximately Rs 4.47 crore. The scam involved fraudsters posing as representatives of a courier company. They informed the doctor about a seized package and requested substantial money for verification purposes. Tragically, the doctor trusted the callers and lost substantial money.
- Case in Mumbai: In a strikingly similar incident, an IT professional from Mumbai, Maharashtra, lost Rs 1.97 lakh to cyber fraudsters pretending to be officials from the narcotics department. The fraudsters contacted the victim, claiming her Aadhaar number was linked to the criminals’ bank accounts. They coerced the victim into transferring money for verification through deceptive tactics and false evidence, resulting in a significant financial loss.
These recent cases highlight the growing threat of courier-related cyber scams and the devastating impact they can have on unsuspecting individuals. It emphasises the urgent need for increased awareness, vigilance, and preventive measures to protect oneself from falling victim to such fraudulent schemes.
Nature of the Attack
The cyber scam typically begins with a fraudulent call from someone claiming to be associated with a courier company. They inform the victim that their package is stuck or has been seized, escalating the situation by involving law enforcement agencies, such as the narcotics department. The fraudsters manipulate victims by creating a sense of urgency and fear, convincing them to download communication apps like Skype to establish credibility. Fabricated evidence and false claims trick victims into sharing personal information, including Aadhaar numbers, and coercing them to make financial transactions for verification purposes.
Best Practices to Stay Safe
To protect oneself from courier-related cyber scams and similar frauds, individuals should follow these best practices:
- Verify Calls and Identity: Be cautious when receiving calls from unknown numbers. Verify the caller’s identity by cross-checking with relevant authorities or organisations before sharing personal information.
- Exercise Caution with Personal Information: Avoid sharing sensitive personal information, such as Aadhaar numbers, bank account details, or passwords, over the phone or through messaging apps unless necessary and with trusted sources.
- Beware of Urgency and Threats: Scammers often create a sense of urgency or threaten legal consequences to manipulate victims. Remain vigilant and question any unexpected demands for money or personal information.
- Double-Check Suspicious Claims: If contacted by someone claiming to be from a government department or law enforcement agency, independently verify their credentials by contacting the official helpline or visiting the department’s official website.
- Educate and Spread Awareness: Share information about these scams with friends, family, and colleagues to raise awareness and collectively prevent others from falling victim to such frauds.
Legal Remedies
In case of falling victim to a courier-related cyber scam, individuals can sort to take the following legal actions:
- File a First Information Report (FIR): In case of falling victim to a courier-related cyber scam or any similar online fraud, individuals have legal options available to seek justice and potentially recover their losses. One of the primary legal actions that can be taken is to file a First Information Report (FIR) with the local police. The following sections of Indian law may be applicable in such cases:
- Section 419 of the Indian Penal Code (IPC): This section deals with the offence of cheating by impersonation. It states that whoever cheats by impersonating another person shall be punished with imprisonment of either description for a term which may extend to three years, or with a fine, or both.
- Section 420 of the IPC: This section covers the offence of cheating and dishonestly inducing delivery of property. It states that whoever cheats and thereby dishonestly induces the person deceived to deliver any property shall be punished with imprisonment of either description for a term which may extend to seven years and shall also be liable to pay a fine.
- Section 66(C) of the Information Technology (IT) Act, 2000: This section deals with the offence of identity theft. It states that whoever, fraudulently or dishonestly, makes use of the electronic signature, password, or any other unique identification feature of any other person shall be punished with imprisonment of either description for a term which may extend to three years and shall also be liable to pay a fine.
- Section 66(D) of the IT Act, 2000 pertains to the offence of cheating by personation by using a computer resource. It states that whoever, by means of any communication device or computer resource, cheats by personating shall be punished with imprisonment of either description for a term which may extend to three years and shall also be liable to pay a fine.
- National Cyber Crime Reporting Portal- One powerful resource available to victims is the National Cyber Crime Reporting Portal, equipped with a 24×7 helpline number, 1930. This portal serves as a centralised platform for reporting cybercrimes, including financial fraud.
Conclusion:
The rise of courier-related cyber scams demands increased vigilance from individuals to protect themselves against fraud. Heightened awareness, caution, and scepticism when dealing with unknown callers or suspicious requests are crucial. By following best practices, such as verifying identities, avoiding sharing sensitive information, and staying updated on emerging scams, individuals can minimise the risk of falling victim to these fraudulent schemes. Furthermore, spreading awareness about such scams and promoting cybersecurity education will play a vital role in creating a safer digital environment for everyone.

Executive Summary:
A viral image circulating on social media claims it to be a natural optical illusion from Epirus, Greece. However, upon fact-checking, it was found that the image is an AI-generated artwork created by Iranian artist Hamidreza Edalatnia using the Stable Diffusion AI tool. CyberPeace Research Team found it through reverse image search and analysis with an AI content detection tool named HIVE Detection, which indicated a 100% likelihood of AI generation. The claim of the image being a natural phenomenon from Epirus, Greece, is false, as no evidence of such optical illusions in the region was found.

Claims:
The viral image circulating on social media depicts a natural optical illusion from Epirus, Greece. Users share on X (formerly known as Twitter), YouTube Video, and Facebook. It’s spreading very fast across Social Media.

Similar Posts:


Fact Check:
Upon receiving the Posts, the CyberPeace Research Team first checked for any Synthetic Media detection, and the Hive AI Detection tool found it to be 100% AI generated, which is proof that the Image is AI Generated. Then, we checked for the source of the image and did a reverse image search for it. We landed on similar Posts from where an Instagram account is linked, and the account of similar visuals was made by the creator named hamidreza.edalatnia. The account we landed posted a photo of similar types of visuals.

We searched for the viral image in his account, and it was confirmed that the viral image was created by this person.

The Photo was posted on 10th December, 2023 and he mentioned using AI Stable Diffusion the image was generated . Hence, the Claim made in the Viral image of the optical illusion from Epirus, Greece is Misleading.
Conclusion:
The image claiming to show a natural optical illusion in Epirus, Greece, is not genuine, and it's False. It is an artificial artwork created by Hamidreza Edalatnia, an artist from Iran, using the artificial intelligence tool Stable Diffusion. Hence the claim is false.
