
#FactCheck: Photo of President’s ADC Sorab S. Nair Falsely Shared as Saurabh Tomar, Who Was Shot in Baghpat
Executive Summary
A photograph is going viral on social media claiming to show Saurabh Tomar, a member of the President’s Bodyguard deployed at Rashtrapati Bhavan, who was shot dead in Baghpat on Diwali night. However, CyberPeace Research found that the officer seen with President Droupadi Murmu in the photograph is not Saurabh Tomar but Sorab S. Nair, who serves as the President’s Aide-de-Camp (ADC). Meanwhile, Saurabh Tomar, who was involved in the Baghpat incident, serves in the President’s Bodyguard.
Claim:
A photograph is going viral on social media showing an officer with President Droupadi Murmu on a basketball court. The officer in the photograph is being identified as Saurabh Tomar.
https://www.facebook.com/photo/?fbid=1054488464316746&set=a.115259804906288
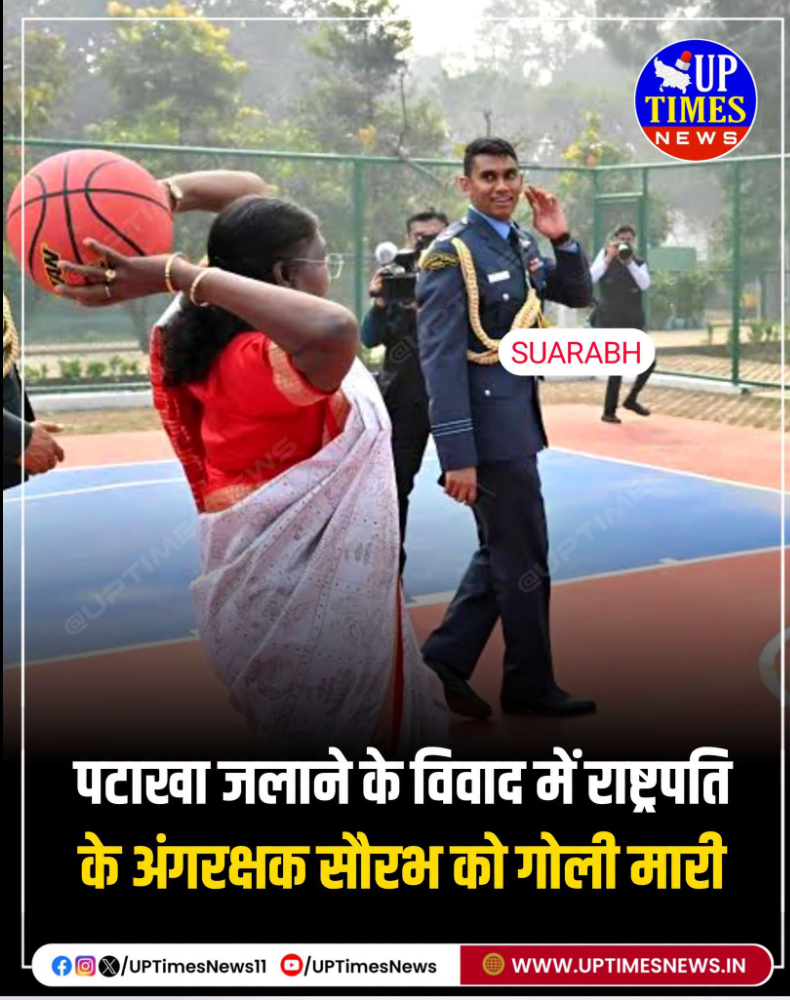
Fact Check
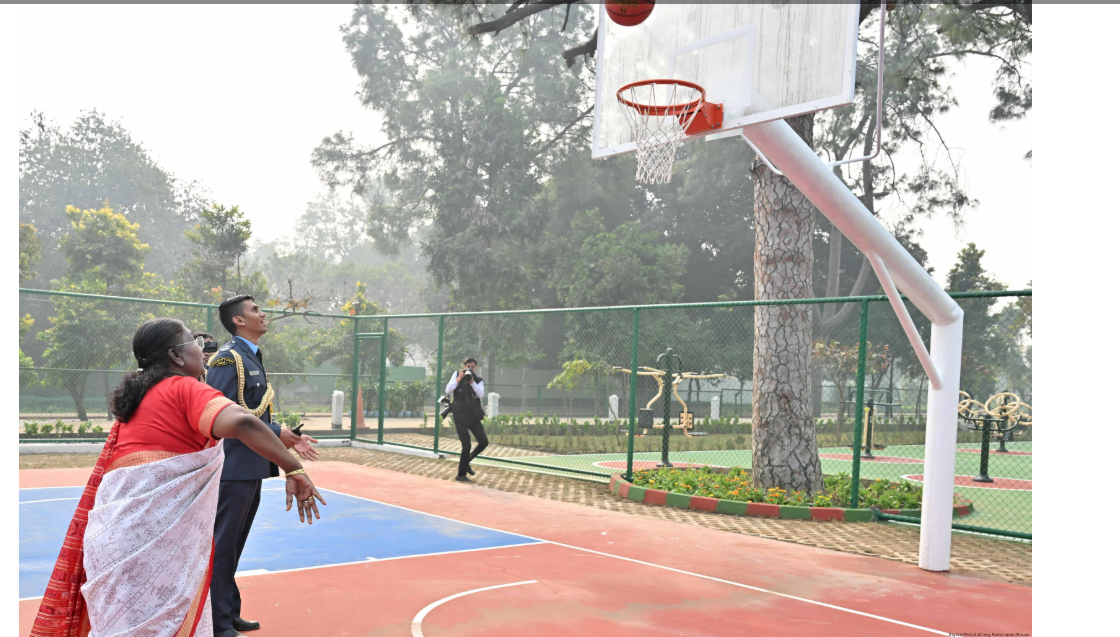
To verify the authenticity of the photograph being circulated as that of Saurabh Tomar, a member of the President’s Bodyguard deployed at Rashtrapati Bhavan, we first conducted a reverse image search. During the search, we found the photograph on the official photo gallery website of Rashtrapati Bhavan, where it was uploaded on February 1, 2025. However, the caption accompanying the photograph did not provide any information about the officer seen in it.
https://dpl.rashtrapatibhavan.gov.in/view_datails/MjU0NjM=
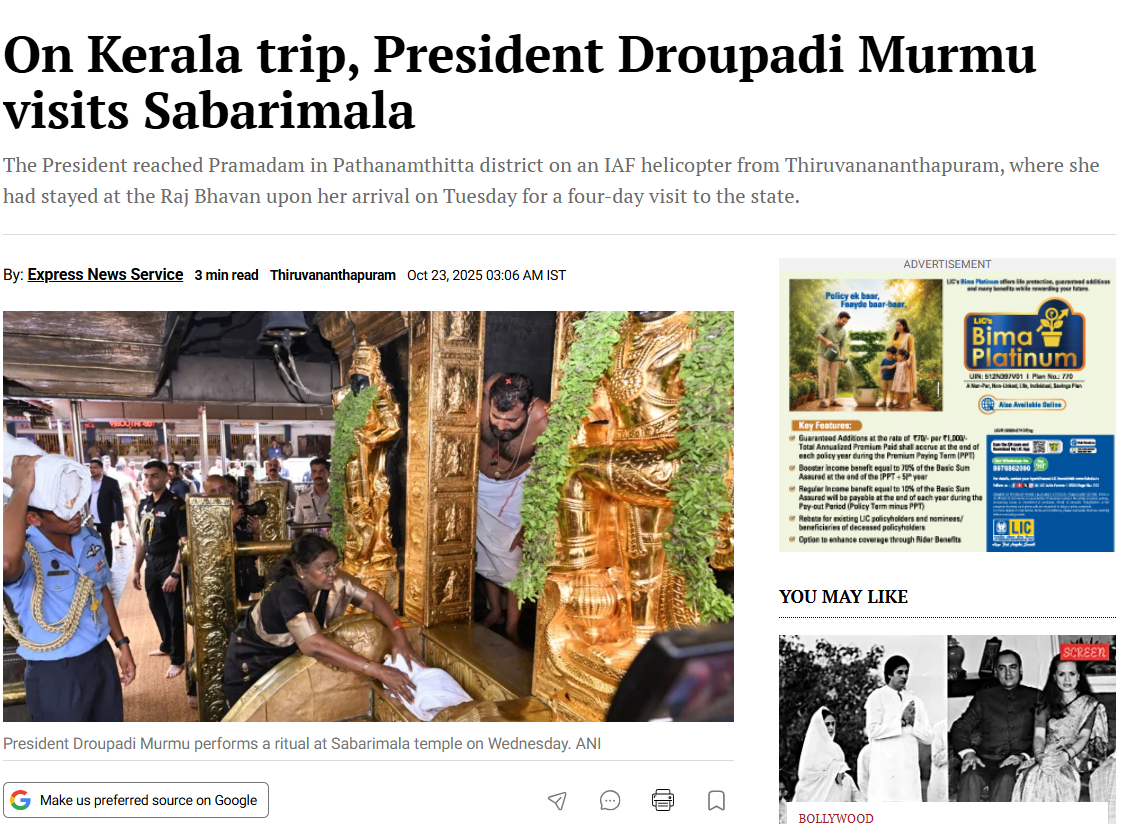
During our research, we also found several news reports identifying Sorab S. Nair as the Aide-de-Camp (ADC) to President Droupadi Murmu. According to these media reports, the President has a total of five ADCs, three from the Indian Army and one each from the Indian Navy and the Indian Air Force.
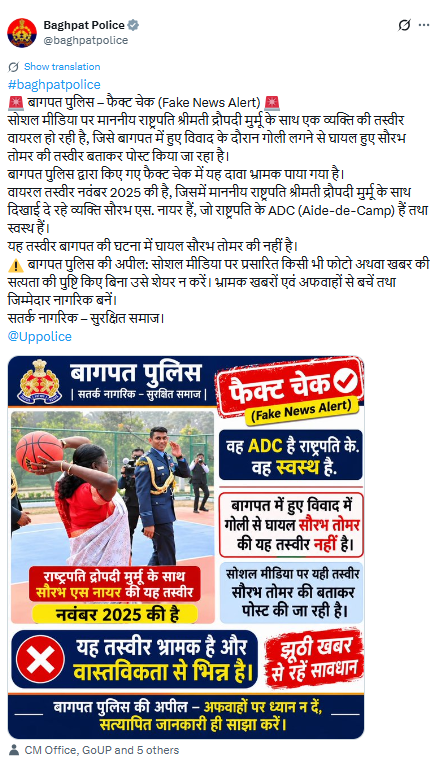
Additionally, we found an X post by Baghpat Police identifying the officer seen in the viral photograph as Sorab S. Nair. The post also stated that the photograph was being misleadingly circulated on social media as that of Saurabh Tomar.
https://x.com/baghpatpolice/status/2120401831478329418
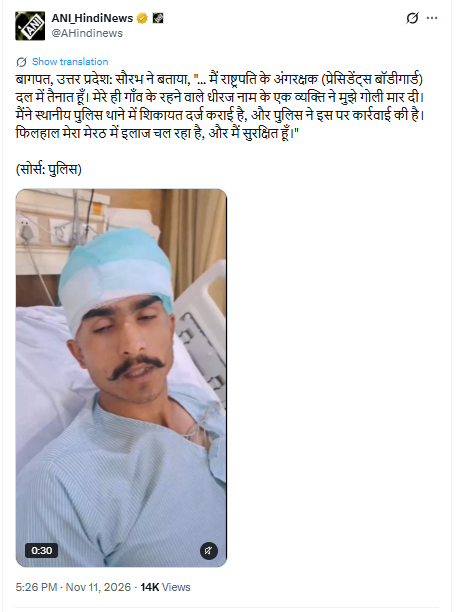
During our research, we also found a video posted on the X account of news agency ANI Hindi, featuring a statement by Saurabh Tomar, who serves in the President’s Bodyguard and was injured in the incident. In the approximately 30-second video, he identifies himself as Saurabh and says, “I serve in the President’s Bodyguard, and Dheeraj, who is from my village, shot me. The police are taking action in this matter.”
https://x.com/AHindinews/status/2120485882314764671
Conclusion
Our research found that the viral post is misleading. The person seen in the photograph with the President was not the one who was shot. He has been identified as Sorab S. Nair, who serves as the President’s Aide-de-Camp (ADC).The person who was shot during a dispute is Saurabh Tomar, who serves in the President’s Bodyguard.

Related Blogs

Introduction
Generative AI models are significant consumers of computational resources and energy required for training and running models. While AI is being hailed as a game-changer, however underneath the shiny exterior, cracks are present which significantly raises concerns for its environmental impact. The development, maintenance, and disposal of AI technology all come with a large carbon footprint. The energy consumption of AI models, particularly large-scale models or image generation systems, these models rely on data centers powered by electricity, often from non-renewable sources, which exacerbates environmental concerns and contributes to substantial carbon emissions.
As AI adoption grows, improving energy efficiency becomes essential. Optimising algorithms, reducing model complexity, and using more efficient hardware can lower the energy footprint of AI systems. Additionally, transitioning to renewable energy sources for data centers can help mitigate their environmental impact. There is a growing need for sustainable AI development, where environmental considerations are integral to model design and deployment.
A breakdown of how generative AI contributes to environmental risks and the pressing need for energy efficiency:
- Gen AI during the training phase has high power consumption, when vast amounts of computational power which is often utilising extensive GPU clusters for weeks or at times even months, consumes a substantial amount of electricity. Post this phase, the inference phase where the deployment of these models takes place for real-time inference, can be energy-extensive especially when we take into account the millions of users of Gen AI.
- The main source of energy used for training and deploying AI models often comes from non-renewable sources which then contribute to the carbon footprint. The data centers where the computations for Gen AI take place are a significant source of carbon emissions if they rely on the use of fossil fuels for their energy needs for the training and deployment of the models. According to a study by MIT, training an AI can produce emissions that are equivalent to around 300 round-trip flights between New York and San Francisco. According to a report by Goldman Sachs, Data Companies will use 8% of US power by 2030, compared to 3% in 2022 as their energy demand grows by 160%.
- The production and disposal of hardware (GPUs, servers) necessary for AI contribute to environmental degradation. Mining for raw materials and disposing of electronic waste (e-waste) are additional environmental concerns. E-waste contains hazardous chemicals, including lead, mercury, and cadmium, that can contaminate soil and water supplies and endanger both human health and the environment.
Efforts by the Industry to reduce the environmental risk posed by Gen AI
There are a few examples of how companies are making efforts to reduce their carbon footprint, reduce energy consumption and overall be more environmentally friendly in the long run. Some of the efforts are as under:
- Google's TPUs in particular the Google Tensor are designed specifically for machine learning tasks and offer a higher performance-per-watt ratio compared to traditional GPUs, leading to more efficient AI computations during the shorter periods requiring peak consumption.
- Researchers at Microsoft, for instance, have developed a so-called “1 bit” architecture that can make LLMs 10 times more energy efficient than the current leading system. This system simplifies the models’ calculations by reducing the values to 0 or 1, slashing power consumption but without sacrificing its performance.
- OpenAI has been working on optimizing the efficiency of its models and exploring ways to reduce the environmental impact of AI and using renewable energy as much as possible including the research into more efficient training methods and model architectures.
Policy Recommendations
We advocate for the sustainable product development process and press the need for Energy Efficiency in AI Models to counter the environmental impact that they have. These improvements would not only be better for the environment but also contribute to the greater and sustainable development of Gen AI. Some suggestions are as follows:
- AI needs to adopt a Climate justice framework which has been informed by a diverse context and perspectives while working in tandem with the UN’s (Sustainable Development Goals) SDGs.
- Working and developing more efficient algorithms that would require less computational power for both training and inference can reduce energy consumption. Designing more energy-efficient hardware, such as specialized AI accelerators and next-generation GPUs, can help mitigate the environmental impact.
- Transitioning to renewable energy sources (solar, wind, hydro) can significantly reduce the carbon footprint associated with AI. The World Economic Forum (WEF) projects that by 2050, the total amount of e-waste generated will have surpassed 120 million metric tonnes.
- Employing techniques like model compression, which reduces the size of AI models without sacrificing performance, can lead to less energy-intensive computations. Optimized models are faster and require less hardware, thus consuming less energy.
- Implementing scattered learning approaches, where models are trained across decentralized devices rather than centralized data centers, can lead to a better distribution of energy load evenly and reduce the overall environmental impact.
- Enhancing the energy efficiency of data centers through better cooling systems, improved energy management practices, and the use of AI for optimizing data center operations can contribute to reduced energy consumption.
Final Words
The UN Sustainable Development Goals (SDGs) are crucial for the AI industry just as other industries as they guide responsible innovation. Aligning AI development with the SDGs will ensure ethical practices, promoting sustainability, equity, and inclusivity. This alignment fosters global trust in AI technologies, encourages investment, and drives solutions to pressing global challenges, such as poverty, education, and climate change, ultimately creating a positive impact on society and the environment. The current state of AI is that it is essentially utilizing enormous power and producing a product not efficiently utilizing the power it gets. AI and its derivatives are stressing the environment in such a manner which if it continues will affect the clean water resources and other non-renewable power generation sources which contributed to the huge carbon footprint of the AI industry as a whole.
References
- https://cio.economictimes.indiatimes.com/news/artificial-intelligence/ais-hunger-for-power-can-be-tamed/111302991
- https://earth.org/the-green-dilemma-can-ai-fulfil-its-potential-without-harming-the-environment/
- https://www.technologyreview.com/2019/06/06/239031/training-a-single-ai-model-can-emit-as-much-carbon-as-five-cars-in-their-lifetimes/
- https://www.scientificamerican.com/article/ais-climate-impact-goes-beyond-its-emissions/
- https://insights.grcglobalgroup.com/the-environmental-impact-of-ai/
Introduction
India is reaching a turning point in its technological development when the AI Impact Summit 2026 is held in New Delhi. Artificial Intelligence (AI)is transforming economies, labour markets, governance structures and even the grammar of public discourse. It is no longer a frontier of speculation. The challenge facing the Summit is not whether AI will change our societies, it has already done so but rather whether inclusiveness and human dignity will serve as the foundation for this change.
India’s AI journey is defined by scale. The nation has one of the biggest user bases for cutting edge AI systems worldwide. According to projections, AI may create millions of new technology-driven occupations by 2030 and change the nature of millions more. This is a structural reconfiguration rather than an incremental alteration. The stakes are high for a country with a large youth population and diverse socioeconomic diversity.
India’s Tryst with Artificial Intelligence
India’s tryst with AI is a developmental imperative occurring at a civilisational scale not a show put on for a western favour. AI is still portrayed in many international storylines as a competition between China’s state backed rapidity, Europe’s sophisticated regulations and Silicon Valley’s capital. India is far too frequently a huge consumer market rather than a significant force behind the AI era. Such evaluations undervalue a nation that has already proven its capacity to implement technology at a democratic scale through its digital public infrastructure. AI in India is about more than just improving algorithms, it’s about giving millions more people access to social safety, healthcare, agriculture and education.
The scepticism overlooks a deeper truth, India innovates not from abundance but from urgency. India remains certain that technical advancement must be in line with social justice and inclusive growth. The recollections from history suggest that India’s greatest technological strides have often followed underestimation.
A Conclave of Contagious Ideas
India has long been the favourite underestimation of certain western observers, a nation of 1.4 billion people, the world’s fifth largest economy, a noisy democracy with inconvenient geopolitical realities, often assessed by counterparts governing populations smaller than many of its states. Advice follows in spades, sometimes from cities that mastered the art of strategic improvisation long before they preached restraint and sometimes with lectures on innovation, governance and order.
However, there are times when hierarchies need to be rearranged. It was hard to overlook the symbolism when Ranvir Sachdeva, the youngest keynote speaker at the AI Impact Summit, 2026, took the stage, “I’m here as the youngest keynote speaker at the Indian AI Impact Summit,” he said, discussing how he’s connecting ancient Indian beliefs to contemporary technology and the various strategies that other countries are doing to develop AI. In that simple articulation lay a quiet rebuttal, a civilization that once debated metaphysics under banyan trees is now debating ethics in plenary halls. History constantly demonstrates that India’s permanent address has never been underestimation.
From New Delhi to Geneva: The Global Arc of AI Governance
Now that the AI Impact Summit, 2026 is coming to an end, what’s left is not just the recollection of its size but also the form of new international dialogue. The New Delhi Declaration, a remarkable highlight of the Summit, was signed by eighty-eight nations and international organisations to support the democratic spread of AI.
The increasing complexity of the AI order was also made clear by the Summit. Pledges for investments totalled hundred of billions. The U.S. led Pax Silica effort was joined by India. SovereignLLMs in the country were introduced. At the same time, spectators were reminded that the politics of AI are inextricably linked to its promise via logistical challenges, protest disruptions and business rivalries. Although nations are not bound by the New Delhi Declaration it does represent a growing consensus that acceleration must be accompanied by governance.
The revelation that the 2027 AI Impact Summit will be in Geneva represents a significant shift in this regard. Guy Parmelin, the president of Switzerland, described the upcoming chapter as one that is primarily concerned with international law and good governance in an attempt to guarantee that the future of AI is not entirely in the hands of powerful nations. From scale and ambition in New Delhi to normative consolidation in Europe, Geneva, longtime hotbed of multilateral diplomacy, provides symbolic continuity.
Concluding Confluence
It is tempting to view the Global CyberPeace Summit (GCS), a Pre-Summit Event of AI Impact Summit held in close succession at Bharat Mandapam on 10th February, 2026. They formed a strong intellectual arc. At GCS, inclusion was not ornamental. A deeper message was conveyed by India Signing Hands’ involvement and purposeful emphasis on accessibility, digital systems must be created with, not just for, those on margins. Resilience must start at the economic level, according to the AI-enabled cybersecurity engagement for MSMEs. Participants were reminded during the talks on Technology Facilitated Gender-Based Violence (TFGBV), CSAM prevention and child safety that technological arguments only gain significance when they are connected to real-world outcomes.
When Geneva takes over in 2027, the issue will not just be how AI should be regulated, but also what ethical foundation that governance is built upon. New Delhi’s belief that wisdom and power must coexist may be its contribution to this developing narrative. That persistence has content than spectacle, as well as possibly the faint form of technical conscience.

Recent Incidents:
Recent reports are revealing a significant security threat linked to a new infostealer based malware campaign known to solely target gaming accounts. This attack has affected users of Activision and other gaming websites. The sophisticated software has captured millions of login credentials, notably from the cheats and players. The officials at Activision Blizzard, an American video game holding company, are still investigating the matter and collaborating with cheated developers to minimize the impact and inform the accounts’ residents of appropriate safety measures.
Overview:
Infostealer, also known as information stealer, is a type of malware designed in the form of a Trojan virus for stealing private data from the infected system. It can have a variety of incarnations and collect user data of various types such as browser history, passwords, credit card numbers, and login details and credentials to social media, gaming platforms, bank accounts, and other websites. Bad actors use the log obtained as a result of the collection of personal records to access the victim’s financial accounts, appropriate the victim’s online identity, and perform fraudulent actions on behalf of the victim.
Modus Operandi:
- Infostealer is a malicious program created to illegally obtain people's login details, like usernames and passwords. Its goal is to enable cyberattacks, sell on dark web markets, or pursue malicious aims.
- This malware targets both personal devices and corporate systems. It spreads through methods like phishing emails, harmful websites, and infected public sites.
- Once inside a device, Infostealer secretly gathers sensitive data like passwords, account details, and personal information. It's designed to infiltrate systems being undetected. The stolen credentials are compiled into datalogs. These logs are then sold illegally on dark web marketplaces for profit.
Analysis:


Basic properties:
- MD5: 06f53d457c530635b34aef0f04c59c7d
- SHA-1: 7e30c3aee2e4398ddd860d962e787e1261be38fb
- SHA-256: aeecc65ac8f0f6e10e95a898b60b43bf6ba9e2c0f92161956b1725d68482721d
- Vhash: 145076655d155515755az4e?z4
- Authentihash: 65b5ecd5bca01a9a4bf60ea4b88727e9e0c16b502221d5565ae8113f9ad2f878
- Imphash: f4a69846ab44cc1bedeea23e3b680256
- Rich PE header hash: ba3da6e3c461234831bf6d4a6d8c8bff
- SSDEEP: 6144:YcdXHqXTdlR/YXA6eV3E9MsnhMuO7ZStApGJiZcX8aVEKn3js7/FQAMyzSzdyBk8:YIKXd/UgGXS5U+SzdjTnE3V
- TLSH:T1E1B4CF8E679653EAC472823DCC232595E364FB009267875AC25702D3EFBB3D56C29F90
- File type: Win32 DLL executable windows win32 pepe dll
- Magic: PE32+ executable (DLL) (GUI) x86-64, for MS Windows
- File size: 483.50 KB (495104 bytes)
Additional Hash Files:
- 160389696ed7f37f164f1947eda00830
- 229a758e232aeb49196c862655797e12
- 23e4ac5e7db3d5a898ea32d27e8b7661
- 3440cced6ec7ab38c6892a17fd368cf8
- 36d7da7306241979b17ca14a6c060b92
- 38d2264ff74123f3113f8617fabc49f6
- 3c5c693ba9b161fa1c1c67390ff22c96
- 3e0fe537124e6154233aec156652a675
- 4571090142554923f9a248cb9716a1ae
- 4e63f63074eb85e722b7795ec78aeaa3
- 63dd2d927adce034879b114d209b23de
- 642aa70b188eb7e76273130246419f1d
- 6ab9c636fb721e00b00098b476c49d19
- 71b4de8b5a1c5a973d8c23a20469d4ec
- 736ce04f4c8f92bda327c69bb55ed2fc
- 7acfddc5dfd745cc310e6919513a4158
- 7d96d4b8548693077f79bc18b0f9ef21
- 8737c4dc92bd72805b8eaf9f0ddcc696
- 9b9ff0d65523923a70acc5b24de1921f
- 9f7c1fffd565cb475bbe963aafab77ff
Indicators of Compromise:
- Unusual Outbound Network Traffic: An increase in odd or questionable outbound network traffic may be a sign that infostealer malware has accessed more data.
- Anomalies in Privileged User Account Activity: Unusual behavior or illegal access are two examples of irregular actions that might indicate a breach in privileged user accounts.
- Suspicious Registry or System File Changes: Infostealer malware may be trying to alter system settings if there are any unexpected changes to system files, registry settings, or configurations.
- Unusual DNS queries: When communicating with command and control servers or rerouting traffic, infostealer malware may produce strange DNS queries.
- Unexpected System Patching: Unexpected or unauthorized system patching by unidentified parties may indicate that infostealer malware has compromised the system and is trying to hide its footprint or become persistent.
- Phishing emails and social engineering attempts: It is a popular strategy employed by cybercriminals to get confidential data or implant malicious software. To avoid compromise, it is crucial to be wary of dubious communications and attempts of social engineering.
Recommendations:
- Be Vigilant: In today's digital world, many cybercrimes threaten online safety, Phishing tricks, fake web pages, and bad links pose real dangers. Carefully check email sources. Examine websites closely. Use top security programs. Follow safe browsing rules. Update software often. Share safety tips. These steps reduce risks. They help keep your online presence secure.
- Regular use of Anti-Virus Software to detect the threats: Antivirus tools are vital for finding and stopping cyber threats. These programs use signature detection and behavior analysis to identify known malicious code and suspicious activities. Updating virus definitions and software-patches regularly, improves their ability to detect new threats. This helps maintain system security and data integrity.
- Provide security related training to the employees and common employees: One should learn Cybersecurity and the best practices in order to keep the office safe. Common workers will get lessons on spotting risks and responding well, creating an environment of caution.
- Keep changing passwords: Passwords should be changed frequently for better security. Rotating passwords often makes it harder for cyber criminals to compromise and make it happen or confidential data to be stolen. This practice keeps intruders out and shields sensitive intel.
Conclusion:
To conclude, to reduce the impact and including the safety measures, further investigations and collaboration are already in the pipeline regarding the recent malicious software that takes advantage of gamers and has stated that about millions of credentials users have been compromised. To protect sensitive data, continued usage of antivirus software, use of trusted materials and password changes are the key elements. The ways to decrease risks and safely protect sensitive information are to develop improved Cybersecurity methods such as multi-factor authentication and the conduct of security audits frequently. Be safe and be vigilant.
Reference:
- https://techcrunch.com/2024/03/28/activision-says-its-investigating-password-stealing-malware-targeting-game-players/
- https://www.bleepingcomputer.com/news/security/activision-enable-2fa-to-secure-accounts-recently-stolen-by-malware/
- https://cyber.vumetric.com/security-news/2024/03/29/activision-enable-2fa-to-secure-accounts-recently-stolen-by-malware/
- https://www.virustotal.com/
- https://otx.alienvault.com/
