
#FactCheck: Fake Phishing link on Modi Government is giving ₹5,000 to all Indian citizens via UPI
Executive Summary:
A viral social media message claims that the Indian government is offering a ₹5,000 gift to citizens in celebration of Prime Minister Narendra Modi’s birthday. However, this claim is false. The message is part of a deceptive scam that tricks users into transferring money via UPI, rather than receiving any benefit. Fact-checkers have confirmed that this is a fraud using misleading graphics and fake links to lure people into authorizing payments to scammers.

Claim:
The post circulating widely on platforms such as WhatsApp and Facebook states that every Indian citizen is eligible to receive ₹5,000 as a gift from the current Union Government on the Prime Minister’s birthday. The message post includes visuals of PM Modi, BJP party symbols, and UPI app interfaces such as PhonePe or Google Pay, and urges users to click on the BJP Election Symbol [Lotus] or on the provided link to receive the gift directly into their bank account.


Fact Check:
Our research indicates that there is no official announcement or credible article supporting the claim that the government is offering ₹5,000 under the Pradhan Mantri Jan Dhan Yojana (PMJDY). This claim does not appear on any official government websites or verified scheme listings.

While the message was crafted to appear legitimate, it was in fact misleading. The intent was to deceive users into initiating a UPI payment rather than receiving one, thereby putting them at financial risk.
A screen popped up showing a request to pay ₹686 to an unfamiliar UPI ID. When the ‘Pay ₹686’ button was tapped, the app asked for the UPI PIN—clearly indicating that this would have authorised a payment straight from the user’s bank account to the scammer’s.

We advise the public to verify such claims through official sources before taking any action.
Our research indicated that the claim in the viral post is false and part of a fraudulent UPI money scam.

Clicking the link that went with the viral Facebook post, it took us to a website
https://wh1449479[.]ispot[.]cc/with a somewhat odd domain name of 'ispot.cc', which is certainly not a government-related or commonly known domain name. On the website, we observed images that featured a number of unauthorized visuals, including a Prime Minister Narendra Modi image, a Union Minister and BJP President J.P. Nadda image, the national symbol, the BJP symbol, and the Pradhan Mantri Jan Dhan Yojana logo. It looked like they were using these visuals intentionally to convince users that the website was legitimate.
Conclusion:
The assertion that the Indian government is handing out ₹5,000 to all citizens is totally false and should be reported as a scam. The message uses the trust related to government schemes, tricking users into sending money through UPI to criminals. They recommend that individuals do not click on links or respond to any such message about obtaining a government gift prior to verification. If you or a friend has fallen victim to this fraud, they are urged to report it immediately to your bank, and report it through the National Cyber Crime Reporting Portal (https://cybercrime.gov.in) or contact the cyber helpline at 1930. They also recommend always checking messages like this through their official government website first.
- Claim: The Modi Government is distributing ₹5,000 to citizens through UPI apps
- Claimed On: Social Media
- Fact Check: False and Misleading

Related Blogs

Introduction
With the increasing frequency and severity of cyber-attacks on critical sectors, the government of India has formulated the National Cyber Security Reference Framework (NCRF) 2023, aimed to address cybersecurity concerns in India. In today’s digital age, the security of critical sectors is paramount due to the ever-evolving landscape of cyber threats. Cybersecurity measures are crucial for protecting essential sectors such as banking, energy, healthcare, telecommunications, transportation, strategic enterprises, and government enterprises. This is an essential step towards safeguarding these critical sectors and preparing for the challenges they face in the face of cyber threats. Protecting critical sectors from cyber threats is an urgent priority that requires the development of robust cybersecurity practices and the implementation of effective measures to mitigate risks.
Overview of the National Cyber Security Policy 2013
The National Cyber Security Policy of 2013 was the first attempt to address cybersecurity concerns in India. However, it had several drawbacks that limited its effectiveness in mitigating cyber risks in the contemporary digital age. The policy’s outdated guidelines, insufficient prevention and response measures, and lack of legal implications hindered its ability to protect critical sectors adequately. Moreover, the policy should have kept up with the rapidly evolving cyber threat landscape and emerging technologies, leaving organisations vulnerable to new cyber-attacks. The 2013 policy failed to address the evolving nature of cyber threats, leaving organisations needing updated guidelines to combat new and sophisticated attacks.
As a result, an updated and more comprehensive policy, the National Cyber Security Reference Framework 2023, was necessary to address emerging challenges and provide strategic guidance for protecting critical sectors against cyber threats.
Highlights of NCRF 2023
- Strategic Guidance: NCRF 2023 has been developed to provide organisations with strategic guidance to address their cybersecurity concerns in a structured manner.
- Common but Differentiated Responsibility (CBDR): The policy is based on a CBDR approach, recognising that different organisations have varying levels of cybersecurity needs and responsibilities.
- Update of National Cyber Security Policy 2013: NCRF supersedes the National Cyber Security Policy 2013, which was due for an update to align with the evolving cyber threat landscape and emerging challenges.
- Different from CERT-In Directives: NCRF is distinct from the directives issued by the Indian Computer Emergency Response Team (CERT-In) published in April 2023. It provides a comprehensive framework rather than specific directives for reporting cyber incidents.
- Combination of robust strategies: National Cyber Security Reference Framework 2023 will provide strategic guidance, a revised structure, and a proactive approach to cybersecurity, enabling organisations to tackle the growing cyberattacks in India better and safeguard critical sectors.
Rising incidents of malware attacks on critical sectors
In recent years, there has been a significant increase in malware attacks targeting critical sectors. These sectors, including banking, energy, healthcare, telecommunications, transportation, strategic enterprises, and government enterprises, play a crucial role in the functioning of economies and the well-being of societies. The escalating incidents of malware attacks on these sectors have raised concerns about the security and resilience of critical infrastructure.
- Banking: The banking sector handles sensitive financial data and is a prime target for cybercriminals due to the potential for financial fraud and theft.
- Energy: The energy sector, including power grids and oil companies, is critical for the functioning of economies, and disruptions can have severe consequences for national security and public safety.
- Healthcare: The healthcare sector holds valuable patient data, and cyber-attacks can compromise patient privacy and disrupt healthcare services. Malware attacks on healthcare organisations can result in the theft of patient records, ransomware incidents that cripple healthcare operations, and compromise medical devices.
- Telecommunications: Telecommunications infrastructure is vital for reliable communication, and attacks targeting this sector can lead to communication disruptions and compromise the privacy of transmitted data. The interconnectedness of telecommunications networks globally presents opportunities for cybercriminals to launch large-scale attacks, such as Distributed Denial-of-Service (DDoS) attacks.
- Transportation: Malware attacks on transportation systems can lead to service disruptions, compromise control systems, and pose safety risks.
- Strategic Enterprises: Strategic enterprises, including defence, aerospace, intelligence agencies, and other sectors vital to national security, face sophisticated malware attacks with potentially severe consequences. Cyber adversaries target these enterprises to gain unauthorised access to classified information, compromise critical infrastructure, or sabotage national security operations.
- Government Enterprises: Government organisations hold a vast amount of sensitive data and provide essential services to citizens, making them targets for data breaches and attacks that can disrupt critical services.
Conclusion
The sectors of banking, energy, healthcare, telecommunications, transportation, strategic enterprises, and government enterprises face unique vulnerabilities and challenges in the face of cyber-attacks. By recognising the significance of safeguarding these sectors, we can emphasise the need for proactive cybersecurity measures and collaborative efforts between public and private entities. Strengthening regulatory frameworks, sharing threat intelligence, and adopting best practices are essential to ensure our critical infrastructure’s resilience and security. Through these concerted efforts, we can create a safer digital environment for these sectors, protecting vital services and preserving the integrity of our economy and society. The rising incidents of malware attacks on critical sectors emphasise the urgent need for updated cybersecurity policy, enhanced cybersecurity measures, a collaboration between public and private entities, and the development of proactive defence strategies. National Cyber Security Reference Framework 2023 will help in addressing the evolving cyber threat landscape, protect critical sectors, fill the gaps in sector-specific best practices, promote collaboration, establish a regulatory framework, and address the challenges posed by emerging technologies. By providing strategic guidance, this framework will enhance organisations’ cybersecurity posture and ensure the protection of critical infrastructure in an increasingly digitised world.
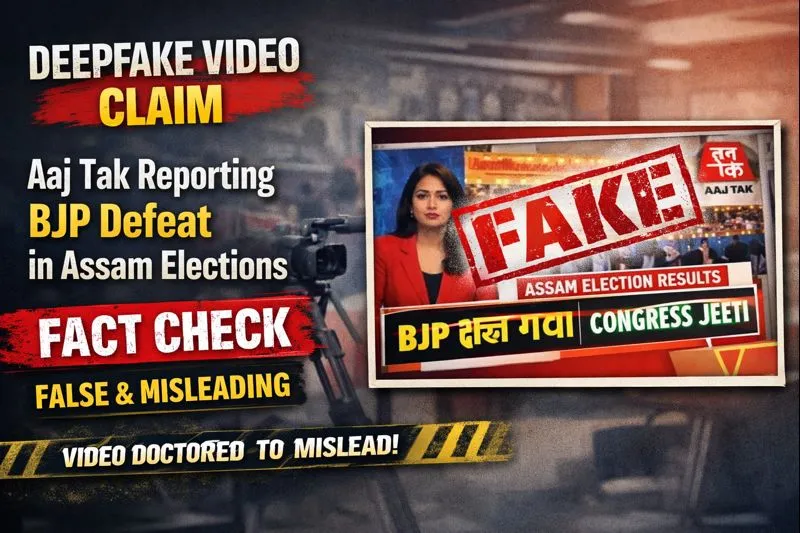
Assembly elections are due to be held in Assam later this year, with polling likely in April or May. Ahead of the elections, a video claiming to be an Aaj Tak news bulletin is being widely circulated on social media.
In the viral video, Aaj Tak anchor Rajiv Dhoundiyal is allegedly seen stating that a leaked intelligence report has issued a warning for the ruling Bharatiya Janata Party (BJP) in Assam. The clip claims that according to this purported report, the BJP may suffer significant losses in the upcoming Assembly elections. Several social media users sharing the video have also claimed that the alleged intelligence report signals the possible removal of Assam Chief Minister Himanta Biswa Sarma from office.
However, an investigation by the Cyber Peace Foundation found the viral claim to be false. Our probe clearly established that no leaked intelligence report related to the Assam Assembly elections exists.
Further, Aaj Tak has neither published nor broadcast any such report on its official television channel, website, or social media platforms. The investigation also revealed that the viral video itself is not authentic and has been created using deepfake technology.
Claim
On social media platform Facebook, a user shared the viral video claiming that the BJP has been pushed on the back foot following organisational changes in the Congress—appointing Priyanka Gandhi Vadra as chairperson of the election screening committee and Gaurav Gogoi as the Assam Pradesh Congress Committee president. The post further claims that an Intelligence Bureau report predicts that the current Assam government will not return to power.
(Link to the post, archive link, and screenshots are available.)
FactCheck:
To verify the claim, we first searched for reports related to any alleged leaked intelligence assessment concerning the Assam Assembly elections using relevant keywords. However, no credible or reliable reports supporting the claim were found. We then reviewed Aaj Tak’s official website, social media pages, and YouTube channel. Our examination confirmed that no such news bulletin has been published or broadcast by the network on any of its official platforms.
- https://www.facebook.com/aajtak/?locale=hi_IN
- https://www.instagram.com/aajtak/
- https://x.com/aajtak
- https://www.youtube.com/channel/UCt4t-jeY85JegMlZ-E5UWtA
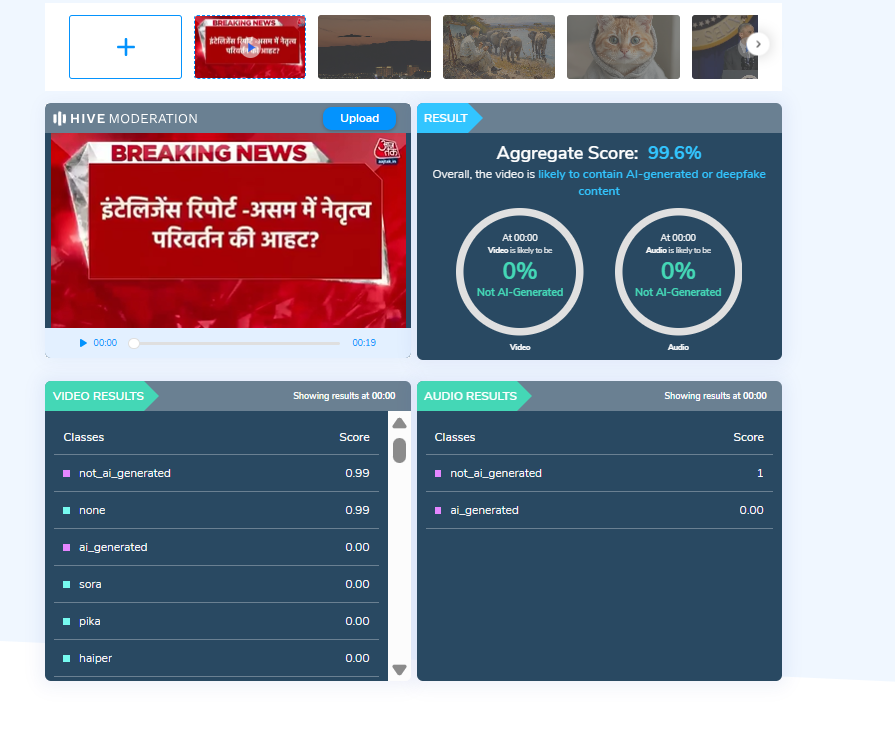
To further verify the authenticity of the video, its audio was scanned using the deepfake voice detection tool HIVE Moderation.
The analysis revealed that the voice heard in the video is 99 per cent AI-generated, clearly indicating that the audio is not genuine and has been artificially created using artificial intelligence.
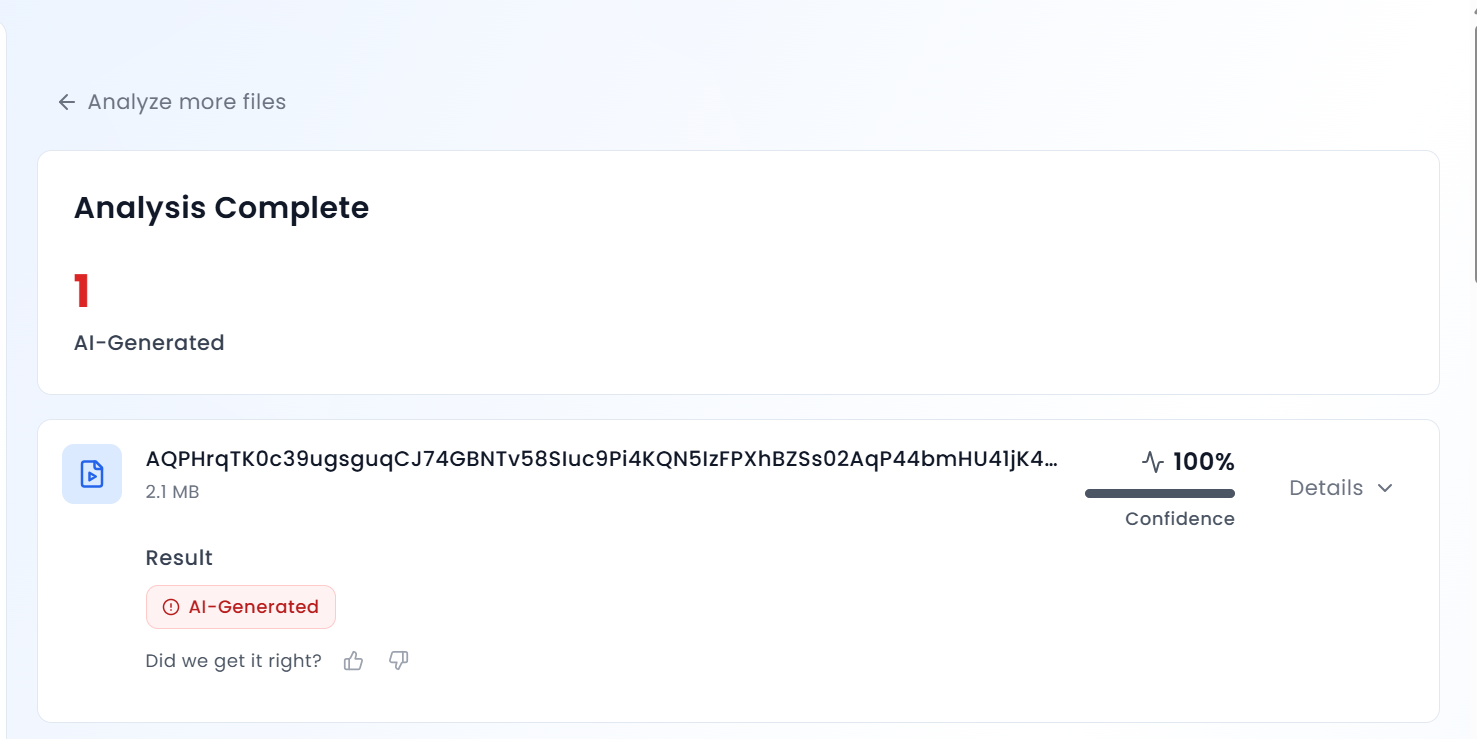
Additionally, the video was analysed using another AI detection tool, Aurigin AI, which also identified the viral clip as AI-generated.
Conclusion:
The investigation clearly establishes that there is no leaked intelligence report predicting BJP’s defeat in the Assam Assembly elections. Aaj Tak has not published or broadcast any such content on its official platforms. The video circulating on social media is not authentic and has been created using deepfake technology to mislead viewers.
Introduction
Meta smart glasses are now banned from courts across England and Wales. His Majesty's Courts and Tribunals Service (HMCTS), the body responsible for criminal, civil, and family courts throughout the jurisdiction, has confirmed that anyone entering a court building wearing the devices will have them confiscated at the door and returned only when they leave. The decision follows a comparable restriction introduced by New York's court system weeks earlier, and it lands at a moment when Meta's artificial intelligence (AI) powered eyewear, now sold in more than seven million pairs worldwide, has already been turned away from a wide range of British venues, from pubs and restaurants to theatres and members' clubs, over the same underlying worry: that a camera built into an ordinary looking pair of glasses can record people who have no way of knowing it is happening. Courts occupy a category of their own in this debate. Photography and recording inside a courtroom have been prohibited for the better part of a century, precisely because the integrity of witness testimony, jury deliberation, and the dignity of the proceedings depend on people being able to speak and be observed only by those the law intends. Smart glasses do not just test that rule. They expose a gap in how it was ever meant to be enforced.
What actually changed, and why smartphones were never the real problem
Unauthorised filming inside a courtroom can be prosecuted as contempt of court. Smartphones, despite carrying multiple cameras, have always been let through security on a kind of implicit social contract: everyone understands that the device could record, everyone understands that using it to do so is a punishable offence, and the visible act of holding a phone up to film someone is itself a signal that can be seen and stopped. As per reports citing an HMCTS spokesperson, "There are clear restrictions on taking images or videos within courts and tribunals which is why the use of Meta glasses is prohibited."
Smart glasses dissolve that social contract. A person wearing them looks, to everyone around them, exactly like a person not recording anything at all.
The wider pattern this fits into
England and Wales did not act in isolation. New York's court system introduced a comparable restriction weeks earlier, following an incident during a trial in which a presiding judge warned Meta's own legal team, present in court wearing the company's glasses, that recording proceedings would be treated as contempt. Reports note that the same device has already been shut out of a striking range of everyday venues across Britain, including a major pub chain, high end restaurants, private members' clubs, theatres, music venues, and comic book conventions, with critics giving the product the unflattering nickname "pervert glasses" well before any court got involved.
That pattern matters analytically because it shows this is not really a story about courts distrusting one particular gadget. It is a story about physical spaces everywhere recalibrating what "no recording" can plausibly mean once recording no longer requires a visible object pointed at someone. Meta, for its part, has said the glasses carry a pulsing light-emitting diode (LED) indicator that activates during recording and tamper detection technology intended to stop wearers covering the light, and the company has shipped more than seven million pairs, commanding, according to reports, more than 80 percent of the global AI eyewear market. None of that changes how the device is experienced by the person being recorded, who typically has no reliable way of noticing a small light on the side of someone's face across a room.
There is a genuine innovation story sitting underneath this controversy, and it deserves to be told honestly rather than dismissed. Wearable AI devices that layer translation, navigation, accessibility support, and hands free computing onto ordinary looking eyewear represent one of the more interesting consumer hardware categories to emerge in years, and the underlying engineering, fitting a camera, microphones, speakers, and AI processing into frames that look like Ray-Bans, is a legitimate technical achievement. The court ban is not a verdict on that achievement. It is a verdict on a specific gap between what the hardware makes physically possible and what existing social and legal norms were designed to detect and police. Those are two different conversations, and collapsing them into one tends to produce worse policy on both sides.
Reading the legal architecture underneath the ban
What HMCTS has effectively done is draw a bright line around function rather than form. Smartphones stay in because the courts are relying on deterrence, the near certainty of visible detection and prosecution if someone is caught filming, to manage the risk they pose. Smart glasses are excluded because that deterrence model breaks down when the recording apparatus is invisible by design. Clara Westbrook, a privacy law partner quoted in coverage of the decision, framed the underlying issue as a gap between the technology and the rules meant to govern it, rather than a simple case of institutional overreaction. That framing holds up under scrutiny. Courtroom rules were written for an era in which recording devices announced themselves. Smart glasses were engineered, whatever the stated intent, to do the opposite.
The view from India
Photography and videography are already prohibited inside Indian court premises as a general rule. Filming inside courtrooms has long been treated as a threat to witness candour, judicial dignity, and the orderly conduct of proceedings, and the principle has been reinforced recently. The Supreme Court, in a circular issued in September 2025, imposed a strict ban on photography, videography, and the creation of social media content within its High Security Zone, prohibiting mobile phones, cameras, tripods, and similar equipment except for official use. More recently, in an interim order passed in 2026, the Court went further, restricting the extraction, editing, and re-dissemination of audio-video recordings of judicial proceedings on social media or digital platforms without prior written permission from the Registrar General of the concerned High Court or the Secretary General of the Supreme Court.
Read together, these rules already prohibit the underlying act that smart glasses would enable inside a courtroom, unauthorized capture and circulation of what happens during a hearing. In that sense, Meta glasses are indirectly covered the moment someone wears a pair inside an Indian court, since using them to record would fall squarely within conduct the existing circulars already forbid. What has not happened, and this distinction matters, is any explicit order naming smart glasses as a class of device to be confiscated or barred at entry, the way HMCTS has now done in England and Wales. Indian courts have regulated the act of recording. They have not yet regulated the device that makes covert recording structurally easier to commit without detection.
It remains to be seen whether Indian courts will explicitly name and ban Meta glasses, rather than relying on existing photography rules to cover them indirectly. If that happens, the reasoning will be drawn on constitutional privacy jurisprudence or courtroom security concerns already in play.
Conclusion
What courts owe the people who appear before them is not hostility toward innovation, but a firm defence of the trust a courtroom is built on, that witnesses can speak freely, that proceedings remain what they are meant to be, and that privacy inside those walls is not negotiable. The question worth asking is not what smart glasses can see, but what courts must protect. Innovation earns its place by respecting the spaces it enters, not by outrunning their rules.
References
- The Guardian, "Meta glasses banned from courts in England and Wales," 11 August 2026 https://www.theguardian.com/technology/2026/aug/11/meta-glasses-banned-from-courts-in-england-and-wales
- Engadget, "England and Wales ban Meta Glasses from courtrooms.” https://www.engadget.com/2234606/england-and-wales-ban-meta-glasses-from-courtrooms/
- TechRepublic, "England and Wales Courts Ban Meta Smart Glasses Over Recording Risks." https://www.techrepublic.com/article/news-meta-smart-glasses-ban-england-wales-courts/
- BM Magazine, "Meta glasses banned from courts across England and Wales." https://bmmagazine.co.uk/legal/meta-glasses-banned-courts-england-wales/
- IBTimes UK" UK Court Service Bans Meta Smart Glasses After Restaurants, Theatres and Pubs Lead 'Spyware' Privacy Push." https://www.ibtimes.co.uk/uk-courts-ban-meta-smart-glasses-privacy-concerns-18141
- 97 Boing Boing, "English courts ban Meta glasses and other spyware." https://boingboing.net/2026/08/11/english-courts-ban-meta-glasses-and-other-spywear.html
- MediaPost, "Meta Smart Glasses Banned In England, Wales Courtrooms." https://www.mediapost.com/publications/article/417180/meta-smart-glasses-banned-in-england-wales-courtr.html
- LiveLaw, "When Seeing Becomes Recording: Invisible Bystander And Limits Of Indian Privacy Law." https://www.livelaw.in/lawschool/articles/invisible-bystander-limits-indian-privacy-law-545517
- PCQuest "B by Lenskart AI Glasses: India's Privacy Laws May Not Be Ready." https://www.pcquest.com/tech-trends/b-by-lenskart-ai-smart-glasses-india-privacy-dpdp-act-12141827
- MediaNama, "Meta tightens AI glasses security as questions over bystander privacy persist." https://www.medianama.com/2026/07/223-meta-tightens-ai-glasses-security-questions-bystander-privacy-persist/
- India Legal, "The State Of Surveillance." https://indialegallive.com/cover-story-articles/il-feature-news/surveillance-jantar-mantar-protests-delhi-police-wearable-recording-devices/
- Feminism In India, "AI Glasses: Is India Ready To Handle The Privacy Implications?" https://feminisminindia.com/2026/07/29/is-india-ready-to-handle-ai-glasses-social-ethical-and-regulatory-governance/
- LiveLaw, "Supreme Court Bans Photography, Videography In Court's High Security Zone." https://www.livelaw.in/top-stories/supreme-court-bans-photography-videography-in-courts-high-security-zone-after-bars-concerns-over-reels-selfies-in-court-premises-303682
- LiveLaw, "Supreme Court Bans Uploading and Sharing Of Audio-Video Recordings Of Court Hearings Without Prior Permission." https://www.livelaw.in/amp/top-stories/breaking-supreme-court-bans-uploading-sharing-of-audio-video-recordings-of-court-hearings-without-prior-permission-542719
- Deccan Herald, "SC bans clicking photos, making reels in its high security zone." https://www.deccanherald.com/amp/story/india%2Fdelhi%2Fsc-bans-clicking-photos-making-reels-in-its-high-security-zone-3724668
