
#FactCheck: Fake Claim that US has used Indian Airspace to attack Iran
Executive Summary:
An online claim alleging that U.S. bombers used Indian airspace to strike Iran has been widely circulated, particularly on Pakistani social media. However, official briefings from the U.S. Department of Defense and visuals shared by the Pentagon confirm that the bombers flew over Lebanon, Syria, and Iraq. Indian authorities have also refuted the claim, and the Press Information Bureau (PIB) has issued a fact-check dismissing it as false. The available evidence clearly indicates that Indian airspace was not involved in the operation.
Claim:
Various Pakistani social media users [archived here and here] have alleged that U.S. bombers used Indian airspace to carry out airstrikes on Iran. One widely circulated post claimed, “CONFIRMED: Indian airspace was used by U.S. forces to strike Iran. New Delhi’s quiet complicity now places it on the wrong side of history. Iran will not forget.”

Fact Check:
Contrary to viral social media claims, official details from U.S. authorities confirm that American B2 bombers used a Middle Eastern flight path specifically flying over Lebanon, Syria, and Iraq to reach Iran during Operation Midnight Hammer.

The Pentagon released visuals and unclassified briefings showing this route, with Joint Chiefs of Staff Chair Gen. Dan Caine explained that the bombers coordinated with support aircraft over the Middle East in a highly synchronized operation.

Additionally, Indian authorities have denied any involvement, and India’s Press Information Bureau (PIB) issued a fact-check debunking the false narrative that Indian airspace was used.

Conclusion:
In conclusion, official U.S. briefings and visuals confirm that B-2 bombers flew over the Middle East not India to strike Iran. Both the Pentagon and Indian authorities have denied any use of Indian airspace, and the Press Information Bureau has labeled the viral claims as false.
- Claim: Fake Claim that US has used Indian Airspace to attack Iran
- Claimed On: Social Media
- Fact Check: False and Misleading

Related Blogs
CyberPeace | Automotive Cybersecurity & Digital Forensics
Introduction
After a crash, the story usually comes from the driver, a witness or a police report. But a modern vehicle can leave another version behind - a digital one. An Event Data Recorder (EDR), commonly called a car's black box, can preserve selected information from the seconds around a crash. NHTSA describes EDRs as recording vehicle dynamics, driver inputs, crash characteristics, restraint status and some post-crash information.[1] The exact fields depend on the vehicle. A black box is not a magical device that records everything; it is one evidence source inside a much larger vehicle.
A modern vehicle can also contain safety controllers, diagnostic interfaces, ADAS, telematics and software-update systems. For an investigator, the question is what evidence can be linked to the EDR and what that combined record can actually support.
What Is Actually in the Black Box?
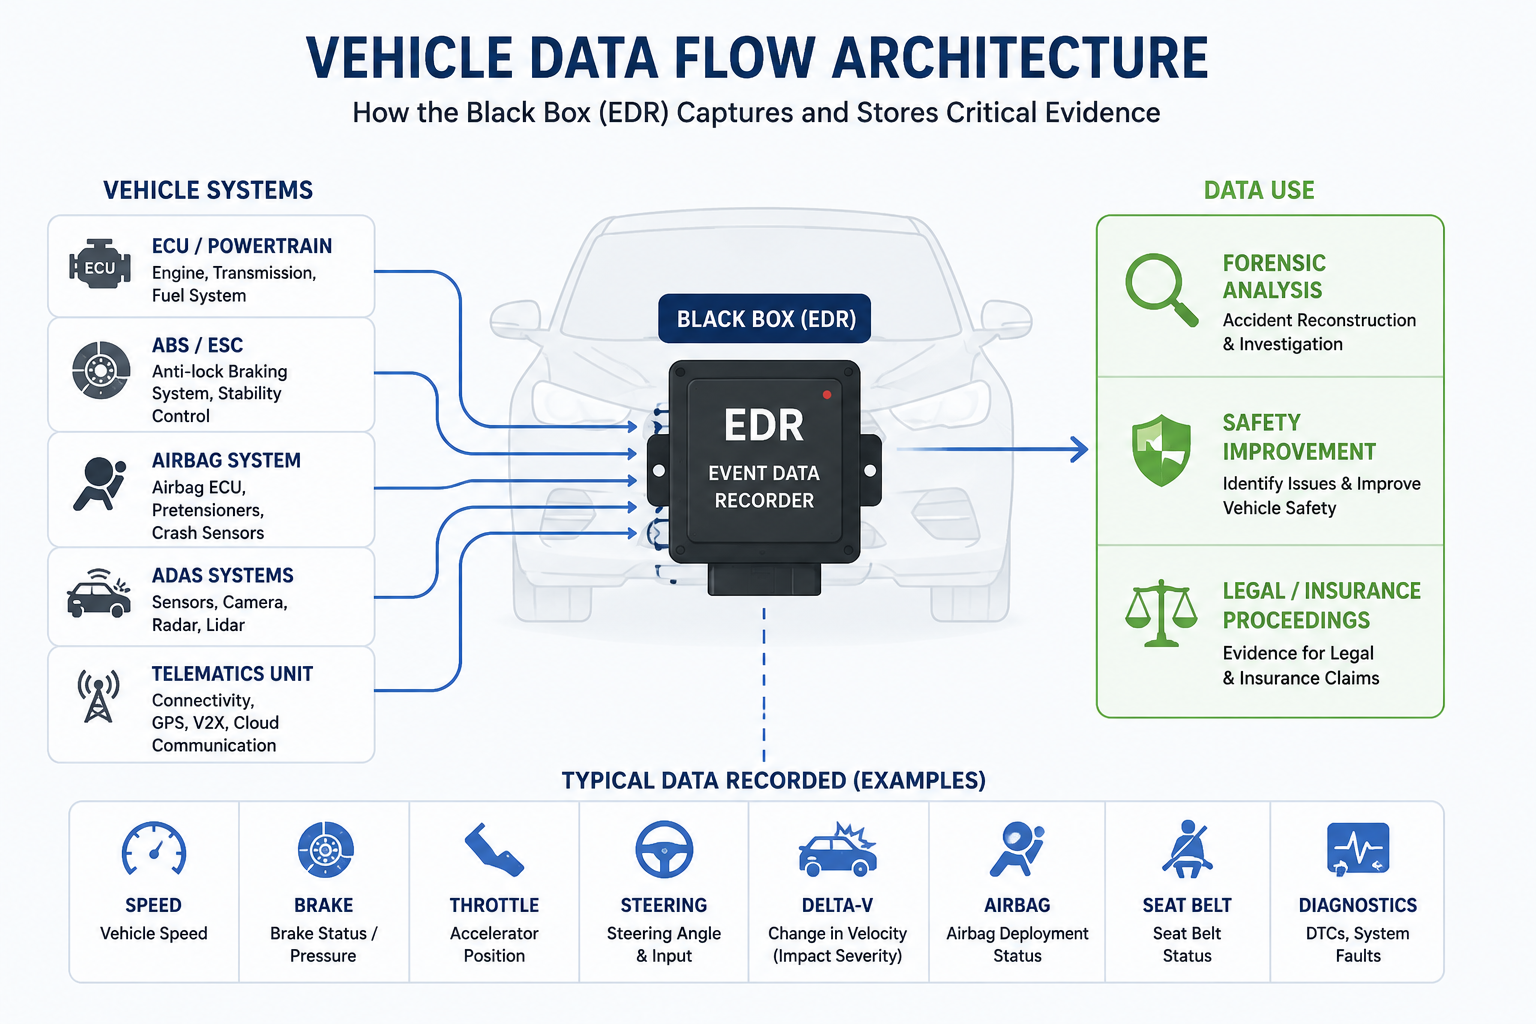
An EDR is best understood as a short event record, not a continuous driving diary. Depending on the vehicle and its configuration, forensic extraction may reveal items such as speed, acceleration, delta-V, engine RPM, throttle position, brake status, steering input, ABS or stability-control activity, seat-belt status and airbag or restraint events. NHTSA's published EDR material shows that data elements can include longitudinal and lateral acceleration, delta-V, vehicle speed, engine speed, throttle, service-brake status, roll/pitch/yaw information and steering input.[2] Do not overread the data: A field that exists in one model should not automatically be assumed to exist in another. A forensic report must identify exactly which module and fields were available and actually recovered.
What Can a Forensic Examination Recover?
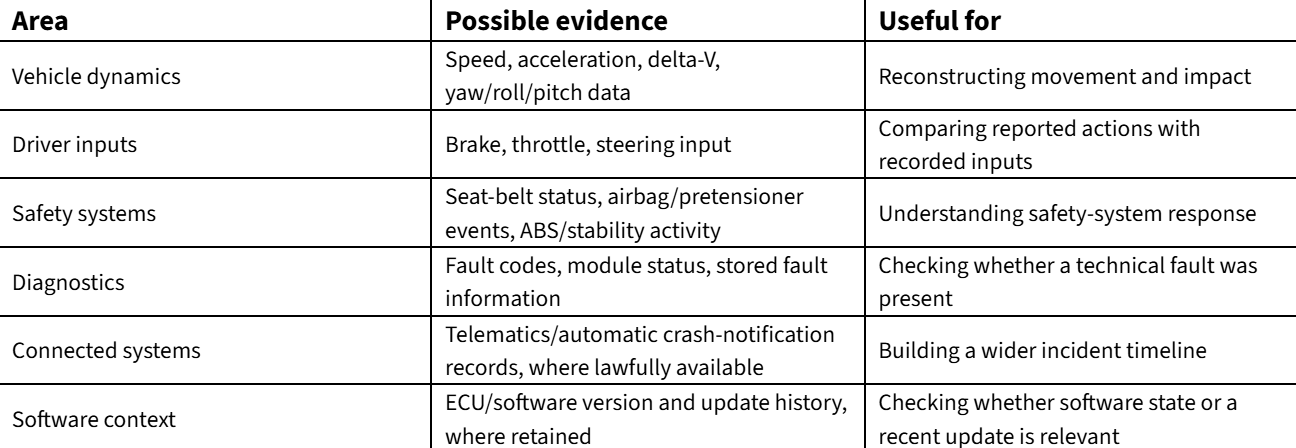
A Brake Failure Example
Consider a driver who reports: “I pressed the brake, but nothing happened.” The statement should be preserved, but a forensic investigation should test it. Was brake status captured? What was the speed before the event? Did ABS activate? What were the acceleration and delta-V patterns? Were there relevant fault codes? Was the vehicle recently repaired or updated? Suppose the recovered records show a brake input, ABS activity and a change in vehicle speed before impact. That does not prove the brakes were mechanically perfect. It does, however, make the sentence “nothing happened” too simple. Conversely, a relevant fault appearing just before the event may give investigators a stronger lead. The important part is the comparison: human account, vehicle record, physical evidence and technical history should be examined together.
Smart Vehicles, Digital Evidence and Cybersecurity Investigation
A connected vehicle can communicate through cellular networks, Bluetooth, Wi-Fi, mobile applications, workshop tools and cloud services. If unusual activity appears around a safety-critical incident, investigators may need to look beyond the EDR. Useful questions include:
• Was there unusual diagnostic or service activity before the incident?
• Was a software update or configuration change recently applied?
• Do timestamps from different modules line up, or is there clock drift?
• Can the extracted record be tied back to the original vehicle and module?
• Is there a non-cyber explanation - such as a hardware fault or software defect - that fits the evidence better?
The mindset matters: A cyberattack should be a conclusion supported by evidence, not the default explanation for strange vehicle behaviour.
The Forensic View: From Data to Evidence
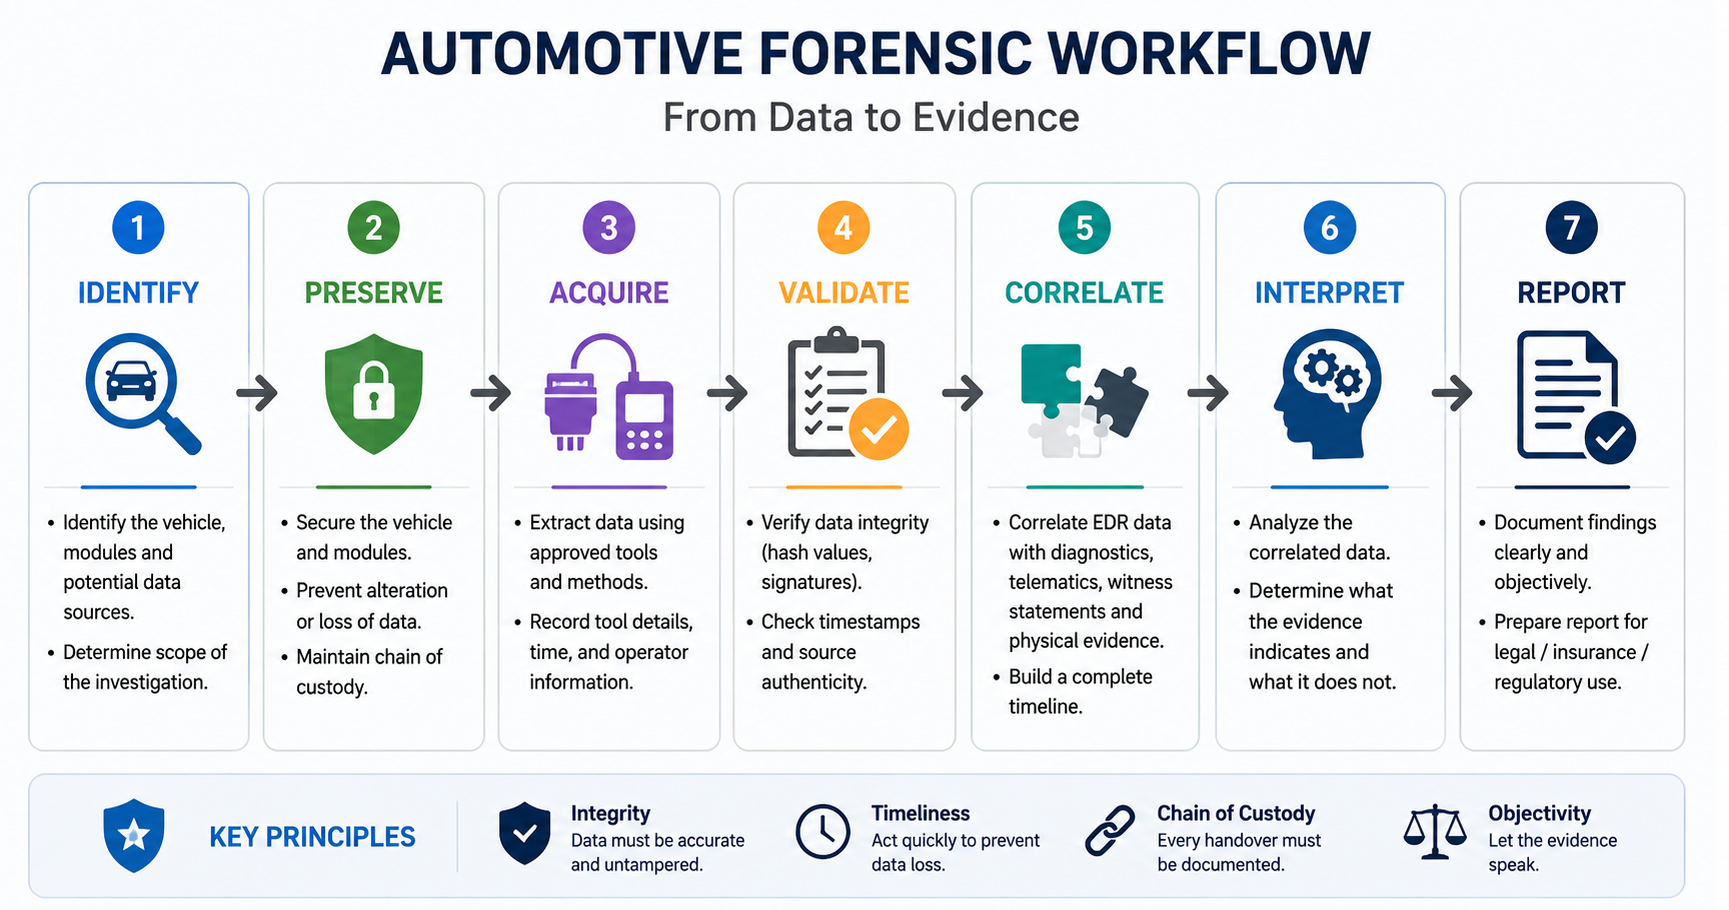
Automotive forensics is not simply plugging in a tool and exporting a report. The investigator should document the vehicle identity, module involved, extraction method, tool version, acquisition time and evidence-preservation steps. The goal is to make the work repeatable and defensible.
• Identify the relevant modules and evidence sources.
• Preserve the vehicle and extracted data against unnecessary alteration.
• Acquire data using a documented and appropriate method.
• Validate provenance, integrity, timestamps and completeness.
• Correlate EDR, diagnostics, software history, connected records and physical evidence.
• Report both findings and uncertainty.
A useful forensic rule: “Recorded” does not mean “proven.” Evidence becomes persuasive when its source, integrity and context are clear.
What the Law and Standards Are Changing
India is moving toward a more formal automotive cybersecurity lifecycle. IS-189 focuses on vehicle cybersecurity and the Cyber Security Management System (CSMS), while AIS-190 deals with software updates and the Software Update Management System (SUMS).[4][5] The wider statutory and type-approval framework is provided by the Motor Vehicles Act, 1988 and the Central Motor Vehicles Rules, 1989. For vehicle prototypes, Rule 126 provides for testing and approval by authorized testing agencies.[6][7]
In June 2026, the Ministry of Road Transport and Highways (MoRTH) came out with draft G.S.R. 503(E). The draft proposes new CMVR Rules 125-T and 125-U covering cybersecurity and software-update requirements. Since G.S.R. 503(E) is still a draft notification, its proposed requirements and the dates from which they may apply should be verified with the latest final notification before treating them as applicable law.[8]
At the international level, UN Regulation No. 155 addresses vehicle cybersecurity, while UN Regulation No. 156 covers software updates and their management.[9][10] This matters to forensics because lifecycle cybersecurity creates an expectation that manufacturers should be able to understand and manage security risks over time. In other words, logs, software-state information, vulnerability records and incident evidence can become part of the security story, not merely post-incident paperwork.
The Real Takeaway
The black box is valuable because it can reduce guesswork. It may tell us how fast the vehicle was moving, whether the driver applied the brake, how the vehicle responded, and what certain safety systems were doing around the event. But it rarely answers the whole case on its own. The strongest investigation is built by joining several pieces: EDR data, diagnostics, software context, connected-system evidence and what was found at the crash scene.
For cybersecurity professionals, the lesson is simple: a secure vehicle should not only resist attacks. It should also leave trustworthy evidence when something goes wrong. Good access controls, reliable timestamps and careful evidence handling help turn “something failed” into a defensible explanation.
Conclusion
The phrase “car black box” sounds simple, but the evidence behind it is not. An EDR can preserve a small but valuable window into a crash. During forensic examination, investigators may also be able to recover diagnostic, safety-system, software and connected-vehicle information, depending on the vehicle and what has been retained. The job is not to collect the largest possible amount of data. It is to collect the right data, preserve it properly and understand what each record can - and cannot - prove.
That is where automotive cybersecurity and digital forensics meet. As vehicles become more connected and software-driven, the ability to reconstruct an incident becomes part of security itself.
References
1. National Highway Traffic Safety Administration (NHTSA), Event Data Recorder (EDR) overview and research resources.
2. NHTSA, Use of Event Data Recorder (EDR) Technology for Highway Crash Data Analysis.
3. NHTSA, Light-Vehicle Event Data Recorder Technologies Update.
4. Automotive Research Association of India (ARAI), AIS-189, Approval of Vehicles with Regards to Cyber Security and Cyber Security Management System, April 2024.
5. Automotive Research Association of India (ARAI), AIS-190, Approval of Vehicles with Regards to Software Update and Software Update Management System, April 2024.
6. Government of India, Motor Vehicles Act, 1988.
7. Government of India, Central Motor Vehicles Rules, 1989, Rule 126.
8. Ministry of Road Transport and Highways, G.S.R. 503(E), 17 June 2026, draft Central Motor Vehicles (Amendment) Rules concerning cybersecurity and software updates.
9. UNECE, UN Regulation No. 155, Cyber Security and Cyber Security Management System.
10. UNECE, UN Regulation No. 156, Software Update and Software Update Management System.
11. NIST, SP 800-86, Guide to Integrating Forensic Techniques into Incident Response.

Introduction
Cyber attacks are becoming increasingly common and most sophisticated around the world. India's Telecom operator BSNL has allegedly suffered a data breach. Reportedly, Hackers managed to steal sensitive information of BSNL customers and the same is now available for sale on the dark web. The leaked information includes names email addresses billing details contact numbers and outgoing call records of BSNL customers victims include both BSNL fibre and landline users. The threat actor using Querel has released a sample data set on a dark web forum and the data set contains 32,000 lines of leaked information the threat actor has claimed that the total number of lines across all databases amounts to approximately 2.9 Million.
The Persistent Threat to Digital Fortresses
As we plunge into the abyssal planes of the internet, where the shadowy tendrils of cyberspace stretch out like the countless arms of some digital leviathan, we find ourselves facing a stark and chilling revelation. At its murky depths lurks the dark web, a term that brings forth images of a clandestine digital netherworld where anonymity reigns supreme and the conventional rules of law struggle to cast their net. It is here, in this murky digital landscape, where the latest trophy of cyber larceny has been flagrantly displayed — the plundered data of Bharat Sanchar Nigam Ltd (BSNL), India's state-owned telecommunications colossus.
This latest breach serves not simply as a singular incident in the tapestry of cyber incursions but as a profound reminder of the enduring fragility of our digital bastions against the onslaught wielded by the ever-belligerent adversaries in cyberspace.
The Breach
Tracing the genesis of this worrisome event, we find a disconcerting story unfold. It began to surface when a threat actor, shrouded in the mystique of the digital shadows and brandishing the enigmatic alias 'Perell,' announced their triumph on the dark web. This self-styled cyber gladiator took to the encrypted recesses of this hidden domain with bravado, professing to have extracted 'critical information' from the inner sanctum of BSNL's voluminous databases. It is from these very vaults that the most sensitive details of the company's fibre network and landline customers originate.
A portion of the looted data, a mere fragment of a more extensive and damning corpus, was brandished like a nefariously obtained banner for all to see on the dark web. It was an ostentatious display, a teaser intended to tantalize and terrify — approximately 32,000 lines of data, a hint of the reportedly vast 2.9 million lines of data that 'Perell' claimed to have sequestered in their digital domain. The significance of this compromised information cannot be overstated; it is not mere bytes and bits strewn about in the cyber-wind. It constitutes the very essence of countless individuals, an amalgamation of email addresses, billing histories, contact numbers, and a myriad of other intimate details that, if weaponized, could set the stage for heinous acts of identity theft, insidious financial fraud, and precisely sculpted phishing schemes.
Ramifications
The ramifications of such a breach extend far beyond individual concerns of privacy invasion. This event signifies an alarming clarion call highlighting the susceptibility of our digital identities. In an era where the strands of our daily lives are ever more entwined with the World Wide Web, such penetrations are not merely an affront to corporate entities; they are a direct assault on the individual's inherent right to security and the implicit trust placed in the institutions that profess to shield their most private information.
Ripples of concern have emanated throughout the cybersecurity community, prompting urgent action from Cert-In, India's cyber security sentinel. Upon notification of this digital transgression, alarms were sounded, and yet, in a disconcerting turn, BSNL has remained enigmatic, adopting a silence that seems to belie the gravity of the situation. This reticence stands in contrast to the urgency for open dialogue and transparency — it is within the anvil of these principles that the foundations of trust are laid and sustained.
Conclusion
The narrative of the BSNL data breach transcends a singular tale of digital larceny or vulnerability; it unfolds as an insistent call to action, demanding a unified and proactive response to the perpetually morphing threat landscape that haunts our technologically dependent world. It is an uncomfortable reminder that in the intricately woven web of our online existence, we each stand as potential targets with our personal data held precariously as the coveted prize for those shadow-walkers and data marauders who dwell in the secretive realms of the internet's darkest corners.
References
Introduction
There has been a recent surge of misinformation all over social media, claiming that every Indian ought to receive an allowance of ₹2,000 under some "Prime Minister's scheme." The message, which has been circulated far and wide on almost all platforms-WhatsApp, Facebook, Telegram, etc.-has urged users to click on an unfamiliar link to claim the allowance in their bank accounts.
It would seem like a very attractive offer, especially at a time when common citizens are coping with rising costs of living. But upon further examination, it turns out to be an outright online scam. NewsMobile fact-checked the claim and confirmed that no such scheme exists. Thus, the message circulating is a scam that aims to mislead common citizens.
Such an incident is not isolated. Over the years, fraudulent posts falsely offering benefits in the name of the government or well-known brands have been on the rise. These scams are not just about misinformation-they take advantage of trust, lure people into clicking, and sharing personal info that poses serious risks to financial and personal security.
Anatomy of the Viral PM Scheme Scam
The viral message received attention and was written in Hindi. It read:
“सभी नागरिकों को PM योजना के तहत दो हज़ार रुपए का भत्ता प्रदान किया गया है अपने bank खाते में प्राप्त करने के लिए click करें."
(English: “All citizens have been provided an allowance of ₹2000 under the PM scheme. Click to receive it in your bank account.”)
Beneath this was an odd link that, upon clicking through investigation, turned out to be not working and invalid. An examination of government sites, official handle accounts, and other such was done and no announcement for any such allowance was found.
This provides a neat explanation of a phishing attempt by which a scammer induces urgency and temptation in order to lure citizens into clicking a malicious link. While the link may no longer be active, it could very well have once redirected users to websites that harvest personal information such as Aadhaar numbers, bank details, or login credentials.
The Broader Problem: Fake Government Scheme Scams
Some scams have been exploiting the hoax gimmick of the ₹2,000 PM scheme into the wider trend. How do the con men work? They leverage the credibility of governmental initiatives to scam citizens. In the past, fake promises were made concerning free gas cylinders, cash allowances, subsidised rations, or even job opportunities.
During the COVID times, for instance, fake vaccination registration links and so-called relief scheme offers went viral, preying on the fears and vulnerabilities of ill-informed citizens. Likewise, false schemes associated with reputed companies such as Amazon, Flipkart, TATA Group, and Hermès have also gone viral, promising free gifts or allowances.
The one thing that makes scams associated with the government very dangerous is the exploitation of people's trust in authority. The common citizen is predisposed to believe the PM scheme or the Government Yojana because of the social credibility accorded to these announcements.
How These Scams Operate
These are scams where the creators intend deception and in the end, gain from defrauding a person. Fraudsters first create clickbait messages that are duly recorded to resemble official communications and often bear the government logos and bear a mix of Hindi-English text with the phrase "Pradhan Mantri Yojana" to make it sound legitimate. The messages then redirect users to bogus websites that really look very much like the government's portals, asking sick persons to enter personal information. Finally, as soon as they have obtained this data, the scammer uses it for identity theft, bank fraud, or sells it on the dark web. Social engineering does play a large role in these scams: here terms of urgency like limited time, last chance, and whatnot get created with the aim of pushing the targets to act on these without thinking. For maximum reach, victims are also asked to forward the message to their friends and family, causing the scammer to go viral across WhatsApp, Facebook, and Telegram.
Risks to Citizens
Risks are serious and manifold to falling prey to these scams. The immediate kind of risk is financial loss: divulging bank account details, an OTP, or credentials may constitute providing attackers the power to drain funds therefrom. Another prevalent kind of identity theft occurs through hijacked Aadhaar, PAN, or personal information that subsequently finds its way into fake loans or SIM activations. Apart from monetary losses, opening malicious links might also make devices infected with spyware or ransomware, thereby invading privacy and security. Victims tend to experience a form of psychological trauma due to feelings of betrayal or humiliation of being deceived, thus discouraging them from reporting, which in turn enables such scams to go undetected.
Best Practices for Prevention
It is prudent to exercise good cyber hygiene and be on the lookout for such scams. The citizens should verify each statement against government-authorised websites like https://www.mygov.in or through press statements of the ministries prior to believing it. One should not click on suspicious links offering money, gifts, or subsidies. Red flags like poor grammar, an unofficial domain name, or too-good-to-be-true offers can enable one to identify the scam in time. Two-factor authentication, antivirus software updates, and securing devices can drastically lower the threat from the technical angle. Equally important is the reporting of issues: always report any suspicious activities to cybercrime.gov.in or to the nearest cyber cell so that the authorities may trace some pattern and issue advisories accordingly. Finally, one can do some good by sharing verified fact checks within their circles to build added strength against misinformation and scams.
Policy and Community Role
While individual awareness is important, collective action must be taken against these fake government scheme scams. Platforms such as WhatsApp, Facebook, and X (Twitter) must tune up fraudsters' message detection mechanisms. In the meantime, Government Bodies must alert citizens periodically on new scams through their official handles/schemes and through community outreach.
Civil society and fact-checking agencies play an important role in dispelling frequently viral hoaxes. This work must be amplified to reach people's consciousness in regional languages for the very reason that in these terrain zones, forwarded messages are much more trusted.
Conclusion
The viral ₹2,000 PM scheme scam is a reminder that everything that is viral online cannot be trusted in toto. The scammers of the day are inventing newer scams to gain trust, spread misinformation, and extort innocent citizens.
The best defence will be awareness and alertness. Citizens must verify any claims through official channels before clicking on a link, sharing their data, or even acting upon it in any way. With proper cyber hygiene and avoiding suspicious messages, we can counterattack by reducing the percentage of impact that these scams may have and collaboratively build a secure digital environment.
As India pushes itself further into a digital ecosystem, both empowering and being resilient to cyber fraud is not a state of individual security, but a national agenda.
References
- https://www.newsmobile.in/nm-fact-checker/fact-check-viral-post-claiming-pm-scheme-offering-rs-2000-allowance-is-a-scam/
- https://timesofindia.indiatimes.com/business/financial-literacy/investing/beware-of-deepfake-scams-fraudsters-using-ai-videos-to-push-schemes-promising-unrealistic-returns-red-flags-to-watch-out-for/articleshow/124085155.cms
- https://www.business-standard.com/finance/personal-finance/invest-rs-21-000-to-earn-rs-20-lakh-monthly-viral-videos-of-fm-are-fake-125082000517_1.html
- https://www.pib.gov.in/PressReleasePage.aspx?PRID=2124728
