
#FactCheck-Air Taxi is a prototype and is not launched to commercial public
Executive Summary:
Recent reports circulating on various social media platforms have falsely claimed that an air taxi prototype is operational and providing services between Amritsar, Chandigarh, Delhi, and Jaipur. These claims, accompanied by images and videos, have been widely shared, leading to significant public attention. However, upon conducting a thorough examination using reverse image search, it has been determined that the information is misleading and inaccurate. These assertions do not reflect the current reality and are not substantiated by credible sources

Claim:
The claim suggests that an air taxi prototype is already operational, servicing routes between Amritsar, Chandigarh, Delhi, and Jaipur. This assertion is accompanied by images of a futuristic aircraft, implying that such technology is currently being used to transport commercial passengers.

Fact Check:
The claim of air taxi and routes between Amritsar, Chandigarh, Delhi, and Jaipur has been found to be misleading. Also, so far, neither the Indian government nor the respective aviation authorities have issued any sort of public declarations nor industry insiders to claim any launch of any air taxi service. Further research followed a keyword-based search that directed us to a news report published in The Times of India on January 20, 2025. A similar post to the one seen in the viral video accompanied the report. It stated that Bengaluru-based aerospace startup Sarla Aviation launched its prototype air taxi called “Shunya” during the Bharat Mobility Global Expo. Under this plan, it looks to initiate electric flying taxis in Bangalore by 2028. This urban air transport program for India will be similar to what they are posting in this regard.

Conclusion:
The viral claim saying that there is an air taxi service in India between Amritsar, Chandigarh, Delhi, and Jaipur is entirely false. The pictures and information going viral are misleading and do not relate to any progress or implementation of air taxi technology in India. To date, there is no official confirmation or credible evidence that supports such a service. Information must be verified from reliable sources before it is believed or shared in order to prevent the spread of misinformation.
- Claim: A viral post claims an air taxi is operational between Amritsar, Chandigarh, Delhi, and Jaipur.
- Claimed On: Social Media
- Fact Check: False and Misleading

Related Blogs
Executive Summary
Israel’s parliament, the Knesset, recently passed a bill allowing military courts to impose the death penalty on Palestinians convicted of killing Israelis. Amid this backdrop, a video has gone viral on social media showing men in black uniforms beating detainees inside a prison, with claims linking it to alleged torture by Israeli forces. However, a research by the CyberPeace found the claim to be false. The viral video is not related to Israel or any real incident, but is actually from an Iraqi television series titled “Beit Umm Layla.”
Claim
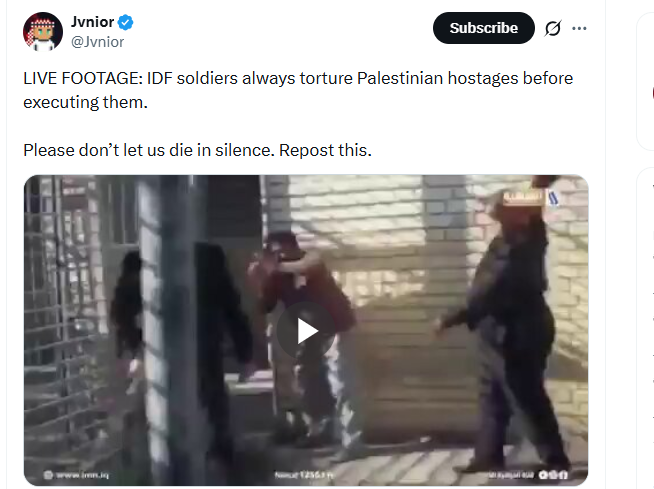
Sharing the video, a user on X (formerly Twitter) wrote:“Live footage: IDF soldiers always torture Palestinian hostages before executing them. Please don’t let us die in silence.”
Fact Check
To verify the claim, we extracted keyframes from the viral video and conducted a reverse image search. This led us to a longer version of the clip posted on March 9 by the Iraqi channel Al-Iraqiya on its Facebook and Instagram pages.
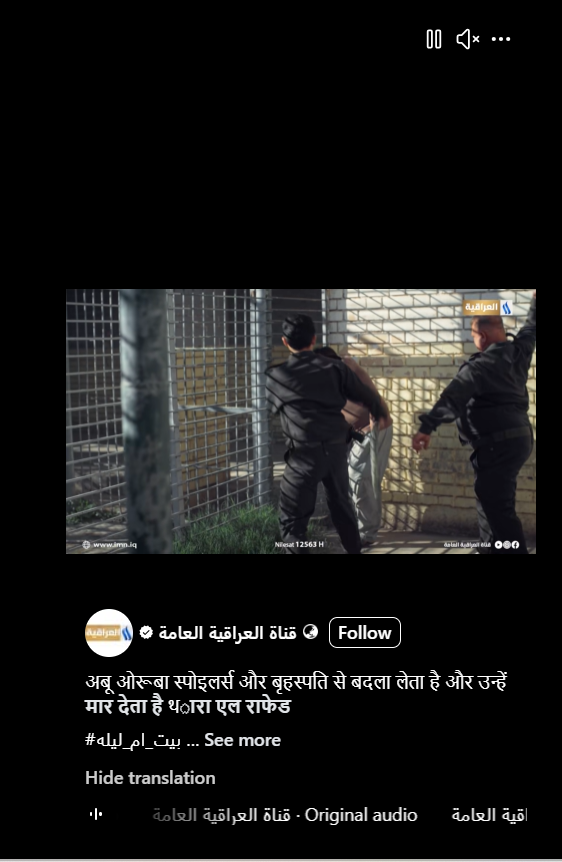
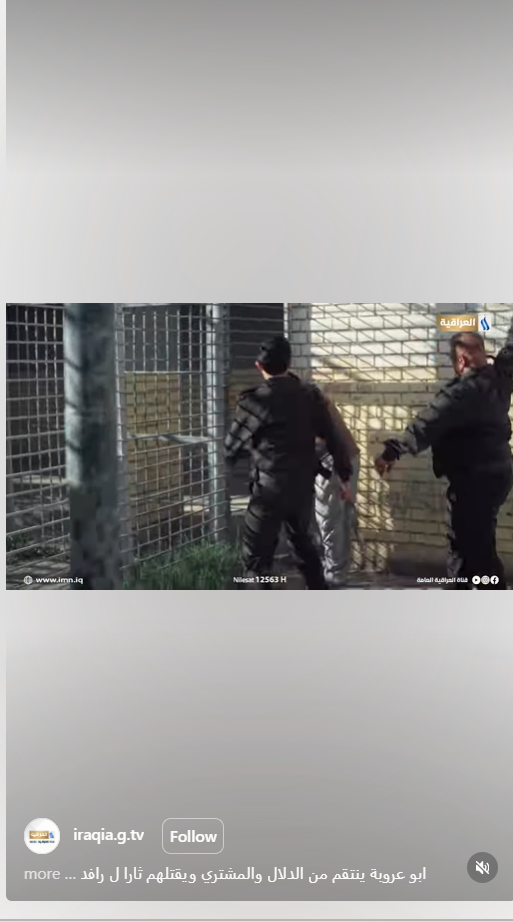
The posts clearly identified the footage as part of “Beit Umm Layla,” a popular Iraqi TV series. Further research showed that the full series is available on Al-Iraqiya’s official YouTube channel, where 25 episodes were uploaded between February 19 and March 20. The viral clip corresponds to Episode 16 of the show.
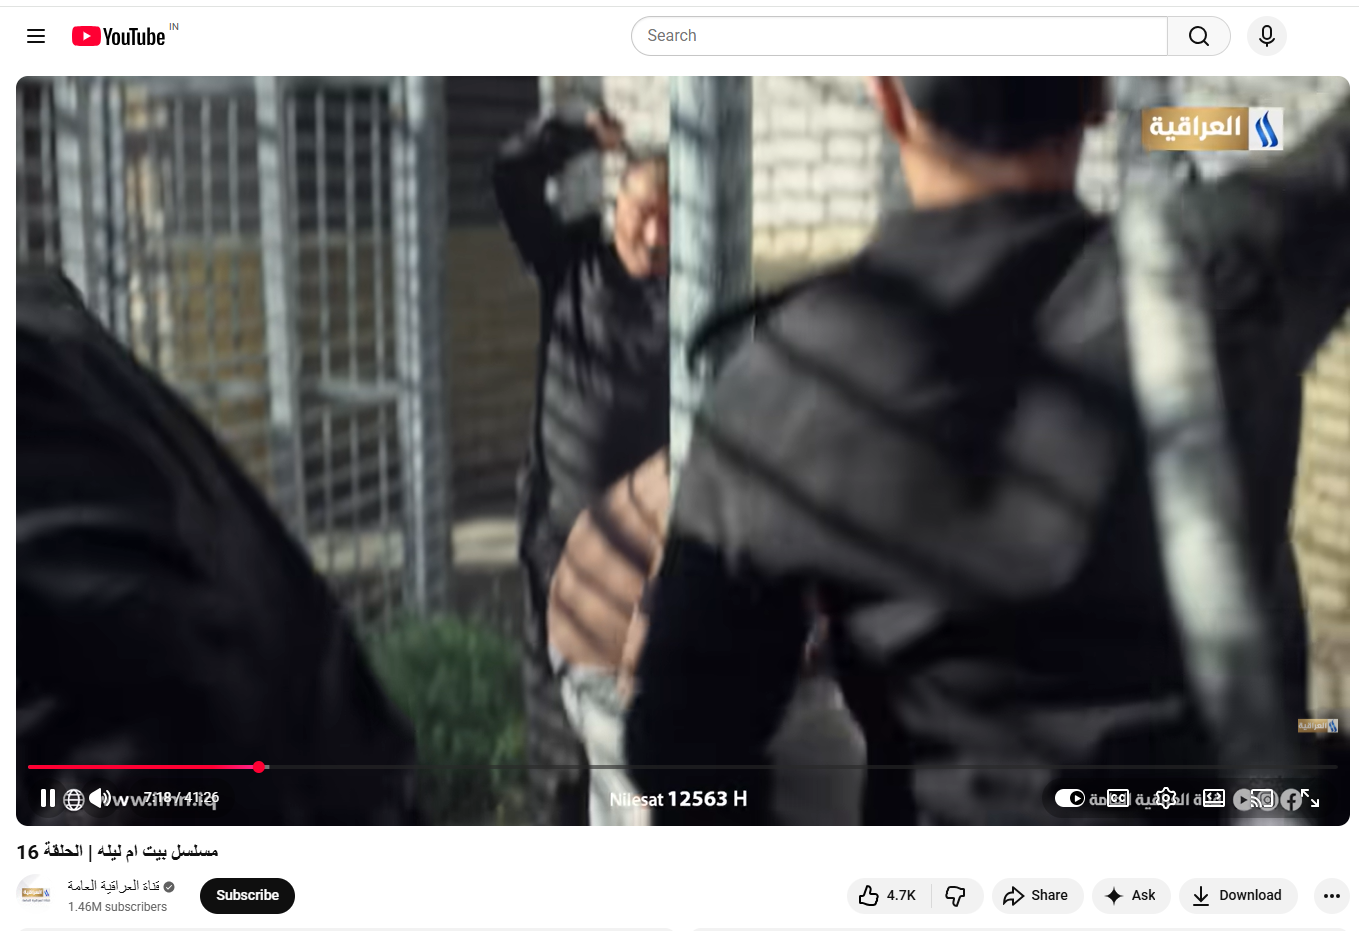
Additionally, information available on the Arabic entertainment website elCinema indicates that the series, released on February 18, is a socio-political drama focusing on prisoners and the psychological struggles faced by them and their families.
Conclusion
The viral claim is false and misleading. The video does not depict any real incident involving Israeli forces or Palestinian detainees. Instead, it is a fictional scene from an Iraqi television drama series.There is no credible evidence to support the claim that the footage shows torture by Israeli soldiers. The clip has been taken out of context and shared with a misleading narrative to provoke emotional reactions.
Introduction
On June 11, 2026, the Ministry of Home Affairs (MHA) India released one of the most critical Indian government advisories concerning cybersecurity by the Indian Cyber Crime Coordination Centre (I4C) under the National Cybercrime Threat Analytics Unit (NCTAU) concerning the immediate and escalating threat posed by the weaponization of generative artificial intelligence to forge synthetic biometric identities capable of bypassing the existing facial verification mechanisms in India. This advisory is arguably one of the most explicit Indian government recognitions of the deep-seated threats associated with AI-generated deepfakes in the country’s digital financial infrastructure. As many Indian financial service providers embrace facial recognition and biometric verification systems for customer onboarding and authentications, the myth that biometric traits are in themselves secure is slowly unraveling.
The advisory states that cybercriminals are deploying sophisticated AI tools to forge such credible digital simulacrums that exhibit such a precise similarity of facial expressions, eye movements, eye blinks, head movements, and voice patterns that they are virtually indistinguishable from the originals for identity verification mechanisms. Such a confluence of easy AI technology, mass onboarding of digital identities, and underdeveloped infrastructure to detect these synthetics requires urgent regulatory, institutional, and technological intervention.
The I4C Advisory: Core Findings and Threat Architecture
In its advisory, NCTAU describes a complex, multi-step attack chain used by scammers to capture biometric information and perpetrate fraud using everyday social interactions. The attackers typically use social media accounts, chat messengers, online job applications, dating applications, or direct phone calls to reach their targets. These interactions are presented as innocuous, such as for video calls, job interviews, identity checks, or just normal conversation with the intention of recording facial and vocal data.
During these interactions, victims may be asked to perform gestures commonly seen in legitimate video calls, such as look directly at the camera, blink, turn their head, or say specific phrases. However, the perpetrators record this video feed without the victim's knowledge and then use deep learning generative AI technologies to process it. Through methods such as Generative Adversarial Networks (GANs) and diffusion models, the scammers create photorealistic synthetic duplicates of the target, capable of mirroring all physical and vocal attributes, such as facial expressions, blinking patterns, head movements, and even voice tones.
The advisory explicitly states that these synthetic identities can be used for a variety of fraudulent activities, such as spoofing face authentication systems, circumventing liveness detection checks, successfully completing video KYC, enabling fraudulent account recovery processes, and illegally accessing bank and financial services. NCTAU also cautions that these voice deepfakes may be paired with facial deepfakes in an attempt to undermine multi-modal authentication methods, and the occurrence of related SIM-swap attacks can eliminate the last layer of security in OTP verification and facilitate a complete account compromise.
The scale of India's Digital Financial Ecosystem
The scale of I4C's detected threat can be better understood by considering India's entire digital financial landscape. In 2025 India has witnessed over 228 billion UPI transactions, with 21.63 billion in December alone, an annual growth rate of 29% from 2024, and an active user base of over 500 million by the beginning of 2026. Furthermore, total e-KYC transactions by April 2025 have exceeded 2,393 crore, and thus, it can be seen the extent to which these aspects of finance (banking, insurance, and credit) are now conducted via remote digital verification. The transformation, although instrumental in increasing financial inclusion, has, according to some analysts, created an attack surface of historic scale. As hundreds of millions more become financially integrated via the very same channels that now form the country's infrastructure and systems of identity, the threat from identity-based fraud becomes astronomically large.
Indian government data further illustrates the extent to which such frauds are a growing concern. Cybercrime cases jumped 42% year-on-year to 2.27 million in 2024, resulting in losses amounting to nearly 228.45 billion. Within that, 1.34 million UPI cases, worth 1,087 crore, occurred in FY2024 alone, while cybercrimes in general soared from 260,000 cases in 2021 to nearly 2.8 million by 2025, totaling cybercrime losses of 22,931 crore.
How Do Deepfakes Defeat Biometric Systems?
Deepfake fraud, in particular, is extremely difficult to counteract due to the direct attack it poses on the assumptions underlying traditional verification systems. Passive techniques for verifying a live person from a static photo or video existed that primarily looked for similarities in textures, lighting, and geometrical properties or challenged subjects to perform an action in real-time. But the generation of real-time face swapping that contains blinks, head motion, and speaking can now be produced on even cheap machines. Cybercriminals can exploit these by using virtual camera drivers to "inject" the false image feed into the live verification session, nullifying any passive liveness checks. Data from the industry clearly shows the extent of this problem: iProov, a leading authenticator, documented a 7.8-fold rise in injection attacks in 2024; Jumio noted an 88% increase in deepfake-induced fraud in 2025; and voice-deepfake attacks on financial call centres saw a 6.8-fold increase in 2024.
Gartner had also predicted that 30% of organizations would have lost trust in facial verification alone by 2026, and work by Kubam (2024) confirmed a lack of multi-factor authentication such as cross-validation of biometric, document, and device integrity signals used within KYC platforms. Such fears have been corroborated by FATF's 2025 Horizon Scan, which classified deepfakes as an emerging threat to the AML/CDD framework and digital identity verification.
Recommendations by I4C
I4C's advisory goes beyond merely warning about threats and lists actionable recommendations to both institutions and citizens. Banks, NBFCs, fintech companies, and onboarding platforms have been advised to incorporate advanced deepfake and synthetic content detection techniques into their verification flows, given that first-generation liveness checks are not enough. They should employ a multi-modal strategy that considers face features along with the device, network signals, behavioral biometrics, and alignment of face and voice. They also have been advised to make a more robust upgrade of their onboarding and verification platforms, as much of the current remote verification architecture was built in a less sophisticated threat context. This aligns with the KYC Master Direction of the RBI that specifies end-to-end encryption, IP-based access controls, geotagging, and technology platforms and systems are to be upgraded frequently. Citizens are advised by I4C to keep their biometric information secure; be careful of unsolicited video calls and online interviews; keep an eye on transaction-related SMS and emails; and report suspicious instances through the National Cybercrime Reporting Portal and through the telephone number 1930. It is clarified that this advisory aims to create awareness of developing AI-based identity fraud schemes, and it is not a declaration that any specific organization, platform, or service is vulnerable.
The Legislative Dimension: India's Evolving Response to Synthetic Media
The problem highlighted by I4C is evolving in a heavily legislated environment, not a legal void. The first-ever legal definition of "synthetic media" in India came into force in the Information Technology Amendment Rules 2026 on February 20, 2026. These rules oblige significant platforms to remove deepfakes and non-consensual intimate media within three hours and two hours, respectively, or lose their safe harbor protection under Section 79 of the IT Act. While the provision focuses on harm stemming from content, this creates a new legal and normative precedent on dealing with AI-induced deception. However, financial frauds facilitated through deepfakes are not content but involve the use of remote identity verification and customer onboarding systems, which require specific technical standards. The overall policy environment when viewed in light of the FATF Horizon Scan, RBI KYC rules, and recent I4C advisory already offers significant scope to define and introduce mandatory deepfake detection and identity assurance standards even before these are explicitly legislated.
Institutional and Technical Recommendations
- For Financial Institutions and Fintech platforms: The existing verification systems (liveness detection) must be replaced with multi-layered deep-fake detection processes, including injection attack detection, behavioral biometrics, cross-modal facial and voice verification, device integrity check, and hardware attestation during onboarding itself.
- For Regulators: The RBI and Ministry of Home Affairs should work together to release technical standards that specify minimum deepfake-detection requirements for video-KYC and remote onboarding systems in line with FATF digital identity guidance and the upcoming EU AI Act.
- For researchers and academia: Dedicated studies on deepfake detection performance across varied demographic, linguistic, and regional populations of India should be prioritized. Current models are mostly trained on Western data.
- For citizens: Face recordings and other biometric information should be treated with the same caution as sensitive financial details. Be wary of unsolicited video calls, remote interviews, or verification requests from unknown people, and report suspicious activities on any account immediately via the National Cybercrime Helpline (1930) or cybercrime.gov.in.
Conclusion
The I4C advisory of June 2026 marks a critical recognition that advances in generative AI have fundamentally challenged the reliability of facial biometric authentication. For a country whose digital financial ecosystem relies heavily on remote identity verification, the implications are significant. The integrity of India's financial inclusion framework now depends on rapidly strengthening identity assurance mechanisms. Addressing this threat will require coordinated action by regulators, financial institutions, technology developers, researchers, and citizens to develop robust technical standards, enhance detection capabilities, and build public awareness at a pace matching the evolution of AI-enabled fraud.
References and Sources
- I4C / NCTAU Advisory, June 2026 — National Cybercrime Threat Analytics Unit, Indian Cyber Crime Coordination Centre, Ministry of Home Affairs, Government of India. Advisory on AI-Enabled Deepfake Identity Fraud. Issued 11 June 2026.
- shuftipro.com/blog/key-takeaways-from-fatf-horizon-scan-report-on-deepfakes
- https://timesofindia.indiatimes.com/india/fraudsters-creating-deepfakes-to-bypass-facial-authentication-i4c/articleshow/131668958.cms
- hyperverge.co/blog/what-is-a-deepfake
- iproov.com/reports/threat-intelligence-report-2026
- arxiv.org/pdf/2601.06241
Executive Summary
A video widely circulated on social media claims to show a confrontation between a Zee News journalist and Chief of Army Staff (COAS) General Upendra Dwivedi during the Indian Army’s Annual Press Briefing 2026. The video alleges that General Dwivedi made sensitive remarks regarding ‘Operation Sindoor’, including claims that the operation was still ongoing and that diplomatic intervention by former US President Donald Trump had restricted India’s military response. Several social media users shared the clip while questioning the Indian Army’s operational decisions and demanding accountability over the alleged remarks. The CyberPeace concludes that the viral video claiming to show a discussion between a Zee News journalist and Chief of Army Staff General Upendra Dwivedi on ‘Operation Sindoor’ is misleading and digitally manipulated. Although the visuals were sourced from the Indian Army’s Annual Press Briefing 2026, the audio was artificially created and added later to misinform viewers. The Army Chief did not make any remarks regarding diplomatic interference or limitations on military action during the briefing.
Claim:
An X (formerly Twitter) user, Abbas Chandio (@AbbasChandio__), shared the video on January 14, asserting that it showed a Zee News journalist questioning the Army Chief about the status and outcomes of ‘Operation Sindoor’ during a recent press conference. In the clip, the journalist is purportedly heard challenging the Army Chief over his earlier statement that the operation was “still ongoing,” while the COAS is allegedly heard responding that diplomatic intervention during the conflict limited the Army’s ability to pursue further military action. Here is the link and archive link to the post, along with a screenshot.
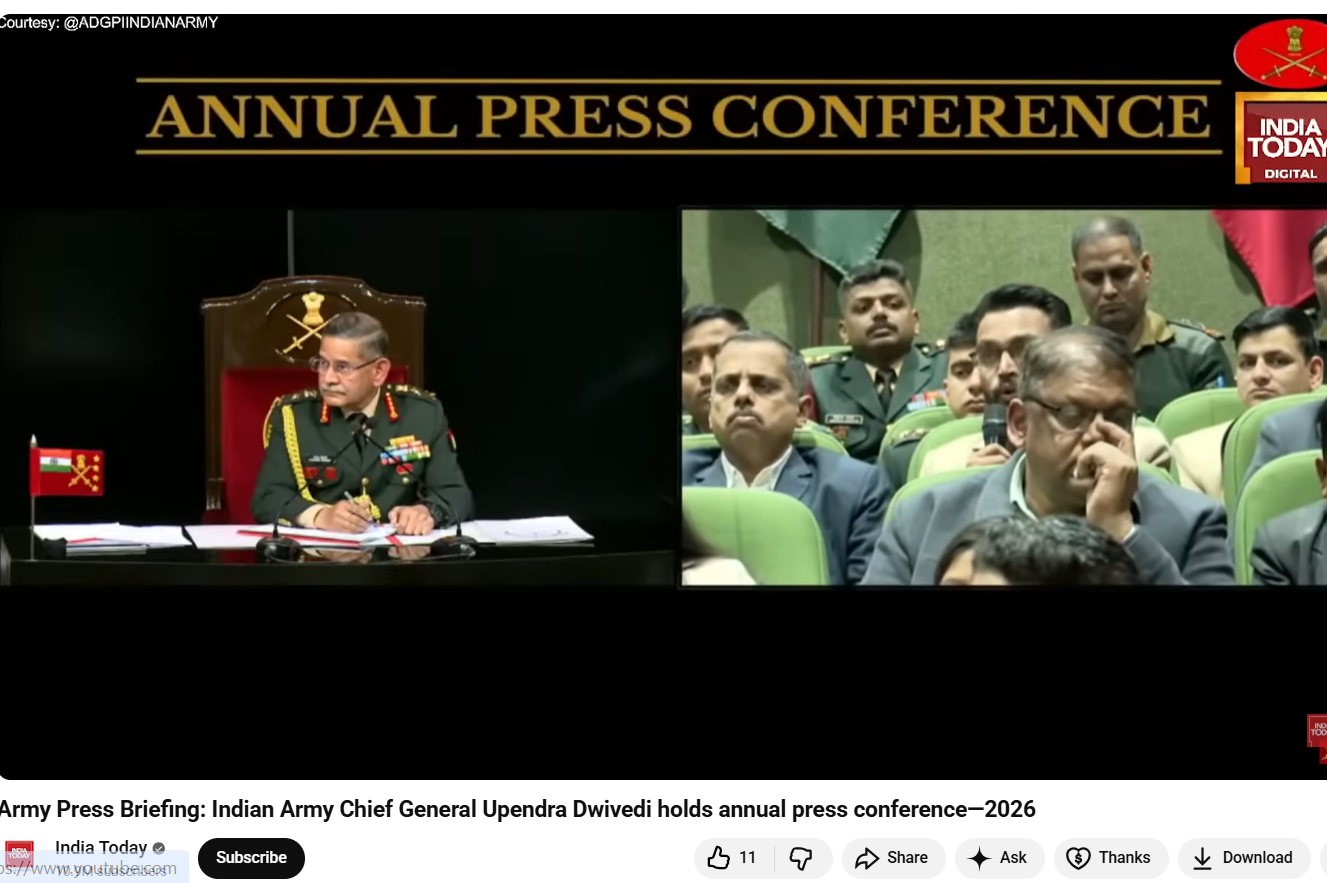
The reverse image search also directed to an extended version of the footage uploaded on the official YouTube channel of India Today. The original video was identified as coverage from the Indian Army’s Annual Press Conference 2026, held on January 13 in New Delhi and addressed by COAS General Upendra Dwivedi. Upon reviewing the original press briefing footage, CyberPeace found no instance where a Zee News journalist questioned the Army Chief about ‘Operation Sindoor’. There was also no mention of the statements attributed to General Dwivedi in the viral clip.
In the authentic footage, journalist Anuvesh Rath was seen raising questions related to defence procurement and modernization, not military operations or diplomatic interventions. Here is the link to the original video, along with a screenshot.
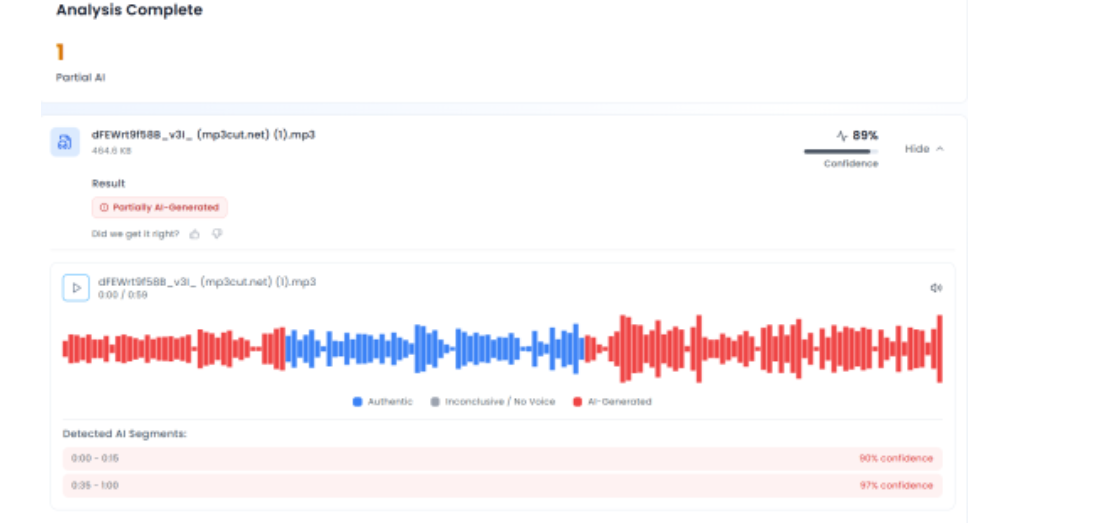
To further verify the claim, CyberPeace extracted the audio track from the viral video and analysed it using the AI-based voice detection tool Aurigin. The analysis revealed that the voice heard in the clip was artificially generated, indicating the use of synthetic or manipulated audio. This confirmed that while genuine visuals from the Army’s official press briefing were used, a fabricated audio track had been overlaid to falsely attribute controversial statements to the Army Chief and a Zee News journalist.
Conclusion
The CyberPeace concludes that the viral video claiming to show a discussion between a Zee News journalist and Chief of Army Staff General Upendra Dwivedi on ‘Operation Sindoor’ is misleading and digitally manipulated. Although the visuals were sourced from the Indian Army’s Annual Press Briefing 2026, the audio was artificially created and added later to misinform viewers. The Army Chief did not make any remarks regarding diplomatic interference or limitations on military action during the briefing. The video is a clear case of digital manipulation and misinformation, aimed at creating confusion and casting doubts over the Indian Army’s official position.
