
#FactCheck- 2019 Fighter Jet Escort Video Falsely Linked to Iran Delegation
Executive Summary
Iran’s official news agencies have denied claims that senior officials, including Foreign Minister Abbas Araghchi and Parliament Speaker Mohammad Bagher Ghalibaf, have arrived in Pakistan for talks. A senior official told Iran’s Tasnim News Agency that Tehran is considering Pakistan’s proposal for peace talks, but any dialogue would depend on the United States fulfilling its commitment to halt military actions on all fronts.
Notably, the United States and Iran had agreed to a two-week ceasefire on April 8, 2026, with discussions reportedly scheduled for April 11 in Islamabad. Amid this backdrop, a video showing fighter jets escorting a large aircraft is being widely circulated on social media. Users claim that Pakistan deployed these jets to escort an Iranian delegation into the country.
However, an research by the CyberPeace found the claim to be false. The viral video is not recent and dates back to 2019.
Claim
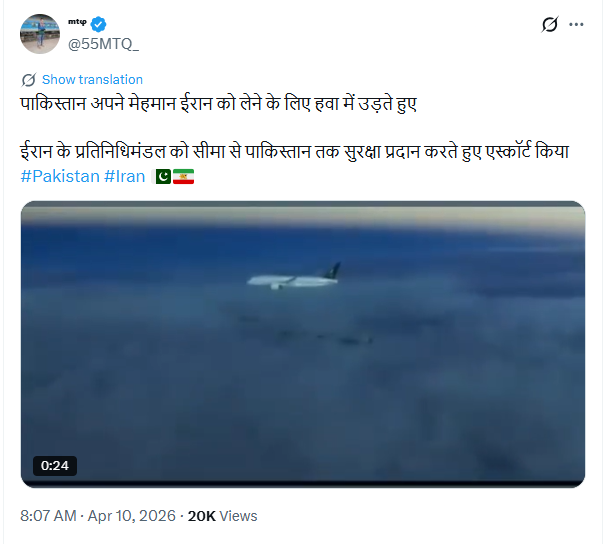
An X (formerly Twitter) user shared the video claiming that Pakistan Air Force jets were escorting an Iranian delegation into Pakistan.
Fact Check
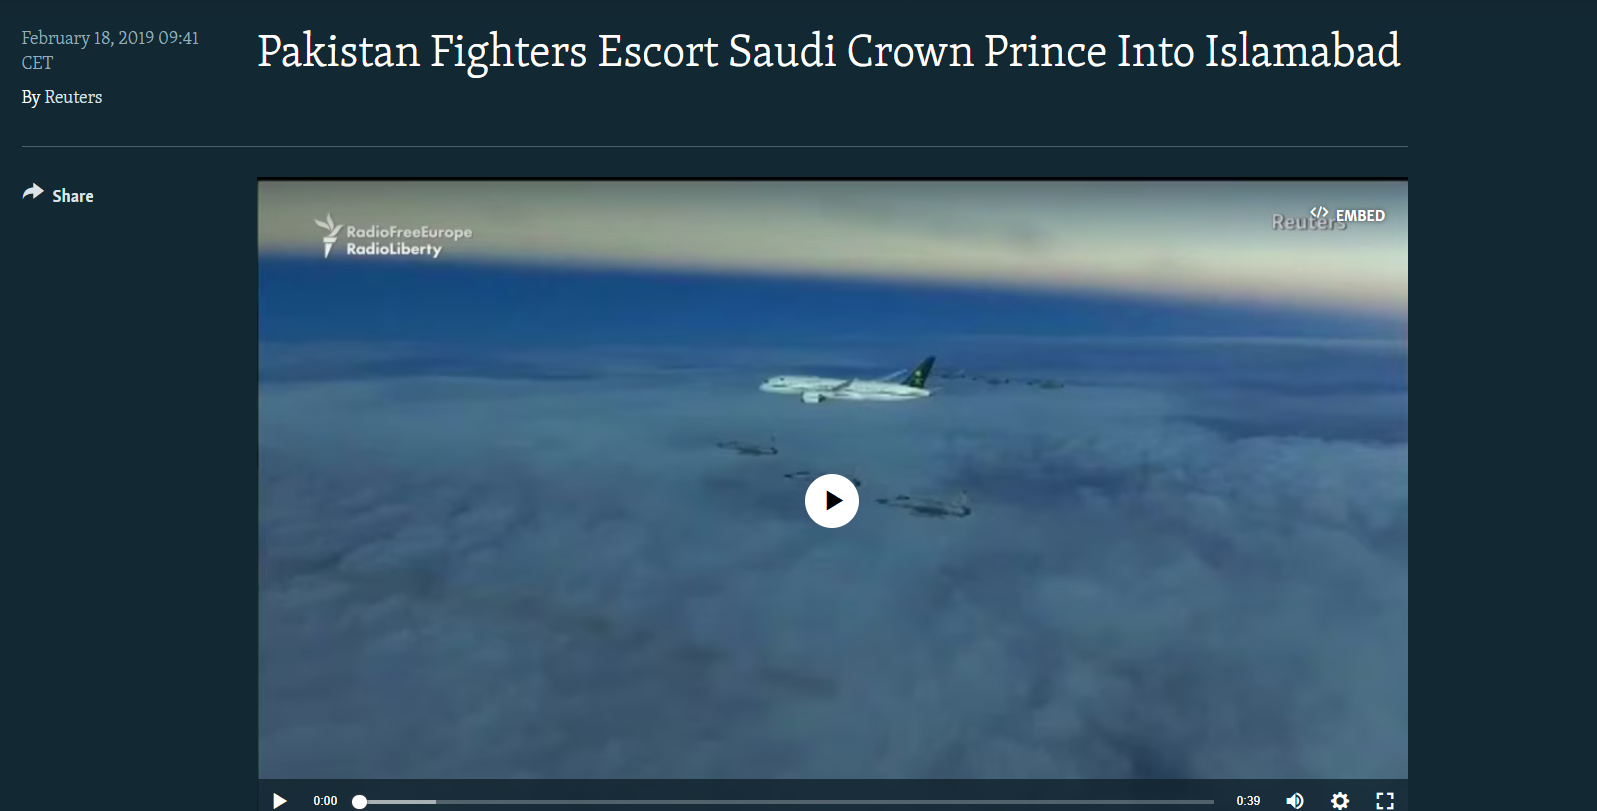
Reverse image search of keyframes from the viral video led us to a February 18, 2019 report by Radio Free Europe/Radio Liberty. The report stated that the fighter jets were deployed by Pakistan to escort the aircraft of Saudi Crown Prince Mohammed bin Salman during his visit to Pakistan on February 17, 2019.
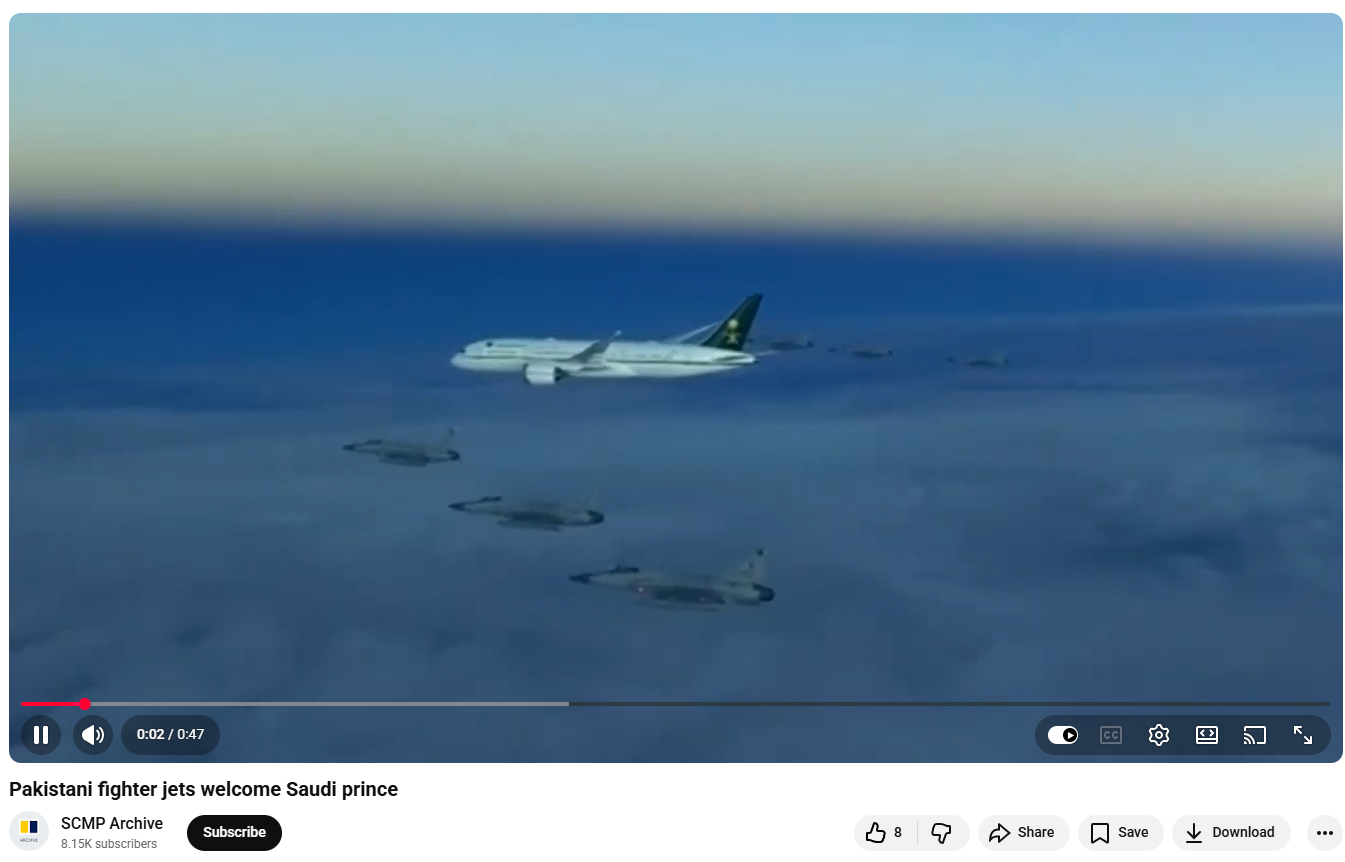
Further verification led us to the same footage uploaded on YouTube by the channel “SCMP Archive” on July 6, 2020. At the time, Pakistan’s Air Force had described the escort as part of a ceremonial welcome tradition for visiting dignitaries.
Conclusion
The viral claim is misleading. The video does not show Pakistani fighter jets escorting an Iranian delegation amid ongoing ceasefire talks. Instead, it is an old clip from 2019, when Pakistan deployed JF-17 fighter jets to welcome Saudi Crown Prince Mohammed bin Salman during his official visit. There is no evidence linking the video to current geopolitical developments involving Iran and Pakistan. The footage has been taken out of context and reshared with a false narrative to mislead viewers.

Related Blogs
Executive Summary
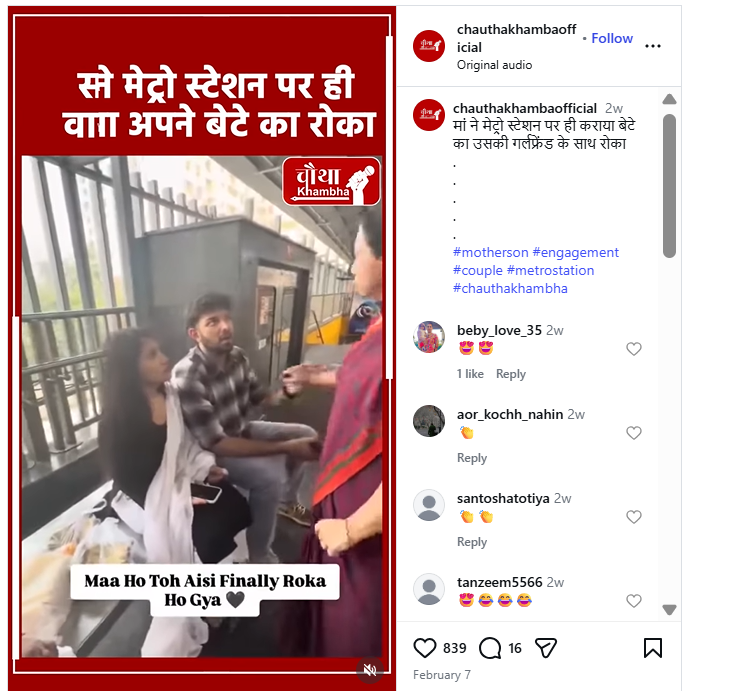
A video is going viral on social media showing a woman performing a pre-wedding ritual called “Roka” for a couple at a metro station. Many users are sharing the clip believing it to be a real incident. CyberPeace found in its research that the viral claim is false. The video is actually scripted.
Claim:
An Instagram user posted the video on February 7, 2026, with the caption, “A mother performed her son’s Roka with his girlfriend at a metro station.”
Fact Check:
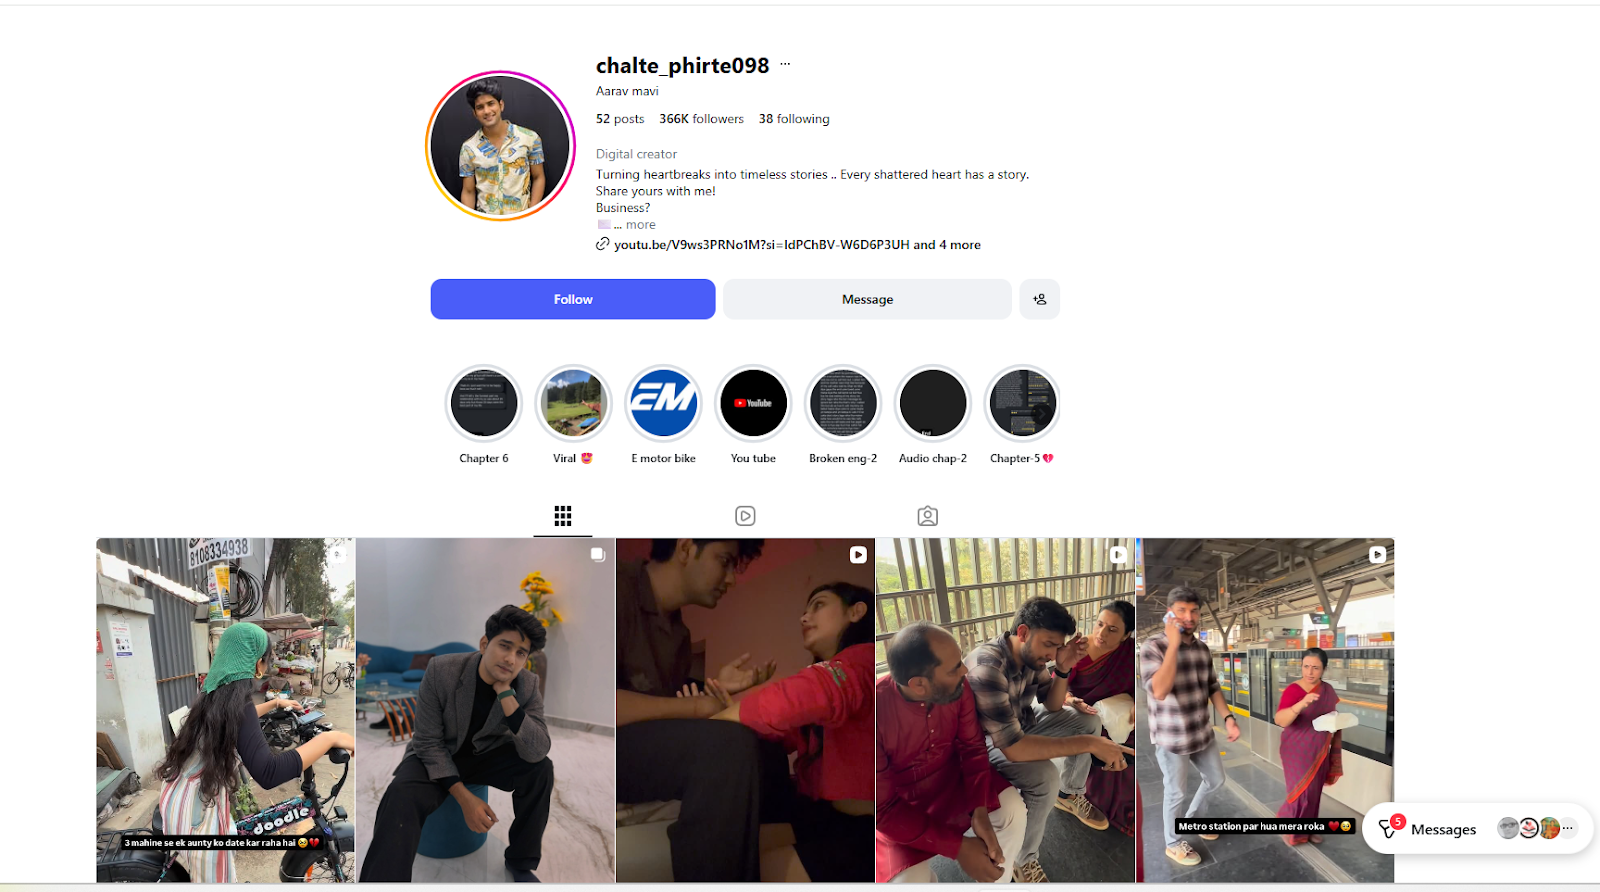
To verify the claim, we conducted a reverse image search using Google Lens on screenshots from the viral video. We found the same video was first uploaded on February 5, 2026, by an Instagram account named “chalte_phirte098.” The profile belongs to digital content creator Aarav Mavi, who regularly posts relationship and breakup-related videos.
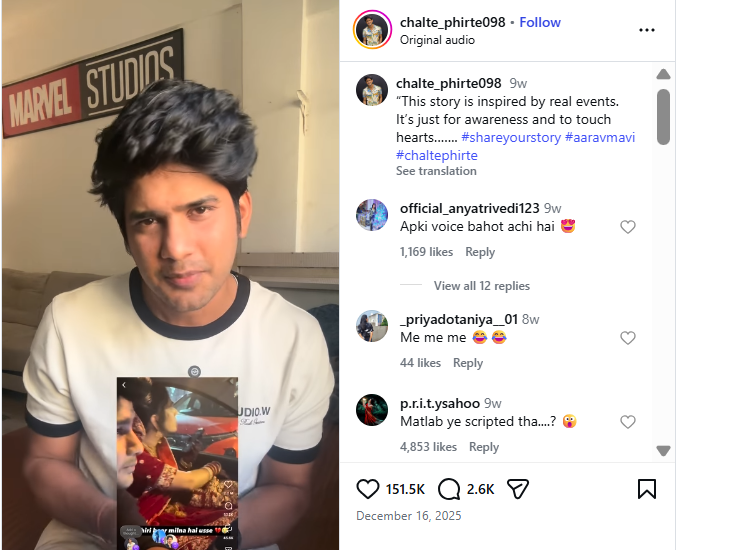
Although the viral clip does not include any disclaimer stating that it is scripted, an older video posted by the creator on December 16, 2025, clarifies that his content is based on real-life stories shared by people but is filmed using professional actors. Several similar staged videos are also available on his profile on Instagram.
Conclusion:
Our research clearly shows that the viral video claiming to show a pre-wedding Roka ceremony at a metro station is not real. It was created by a content creator for entertainment purposes. Therefore, the claim circulating on social media is misleading.

In Delhi there is a bank branch where a lot of money was stolen from people over the country. This bank branch is where all the money disappeared. The people who did this did not wear masks. Break in at midnight. They just used a passbook a rubber stamp and a form that nobody checked carefully. This is the truth that the people who investigate cybercrime keep finding. The way that cybercriminals get away with the money is not by using a computer it is by using a bank account. The police in Delhi who investigate cybercrime have found that a lot of accounts were opened at bank branches. These accounts were opened using identity documents that were borrowed bought or stolen. Then these accounts were rented out to groups of criminals. One bank branch keeps coming up in complaints. This is not bad luck it is a sign of a bigger problem with how banks check who is opening an account.
These fake accounts, which are called " accounts" are controlled by criminal groups, not the people whose names are on the accounts. These accounts are a part of the cybercrime problem in India. The mistakes that bank branches make which allow these accounts to be opened raise a lot of questions. These questions are about how banks check who is opening an account how they prevent money laundering and how they work with groups to stop cybercrime. The bank accounts are the way that cybercriminals in India get away with the money they steal from people. The cybercrime investigators keep finding bank accounts like the ones at the bank branch, in Delhi, where the money was stolen.
The Anatomy of a Mule Account Network
The pattern is now familiar to investigators. A fraud complaint on the National Cyber Crime Reporting Portal traces a victim's stolen money to a beneficiary account. When police pull the account-opening file, the person named on the KYC documents often denies ever visiting the branch or signing the forms; signature verification frequently shows a mismatch. In one recent Delhi case, a cooperative bank's deputy manager was arrested after a single account he had helped open surfaced in 159 separate cyber fraud complaints from across the country, with transactions worth nearly Rs 68 crore routed through it before detection. Similar investigations have uncovered supply gangs that procure dozens of accounts at a time using POS machines, stacks of ATM cards, and cheque books belonging to different people and rent them out to fraudsters as ready-made conduits for stolen money.
What makes a single branch or a small cluster of accounts significant is what it reveals about entry-point failure. Investigators do not describe these as sophisticated hacking operations; they describe them as verification failures as are accounts opened without the mandatory in-person checks, video KYC, or document authentication that RBI rules require. When 96, or 700, or 8.5 lakh mule accounts are traced back through a handful of branches and intermediaries, the story is not really about the fraudsters at the far end of the chain. It is about the choke point where honest oversight should have stopped the account from ever existing.
Where the KYC Framework Is Breaking Down
The RBI's Know Your Customer Master Direction requires banks to establish customer identity, verify a genuine business relationship, and apply risk-based due diligence before allowing an account to operate. In practice, investigators have repeatedly found accounts opened through complicit or negligent bank staff, business correspondents, and third-party agents who bypass these checks entirely. Analysts note that mule accounts systematically exploit gaps in customer onboarding, KYC verification, transaction monitoring, and dormant-account surveillance, with criminals using forged or stolen identity documents and layering funds across multiple accounts to escape detection. Economically vulnerable individuals who are daily-wage workers, students, the unemployed are frequently paid a small commission to hand over their documents or existing accounts, often without understanding that they could face criminal liability for transactions they never authorised.
This is compounded by a financial-inclusion paradox that regulators themselves acknowledge: India has expanded banking access faster than it has expanded financial and digital literacy, leaving a population that is easy to recruit knowingly or unknowingly into mule networks. The result is a KYC regime that looks robust on paper but is only as strong as its weakest branch-level implementation, and weak implementation has proved trivially easy for organised networks to locate and exploit at scale.
The Regulatory and Institutional Response
RBI: From Static Compliance to Active Detection
The Reserve Bank of India has moved beyond periodic KYC audits toward technology-driven detection. It has directed banks to tighten onboarding controls, strengthen transaction monitoring, and report suspicious activity more proactively, and it has proposed additional safeguards, including limits on aggregate credits into accounts where a satisfactory business relationship has not yet been established. Its most significant intervention is MuleHunter.ai, an AI and machine-learning system built to flag suspected mule accounts from transaction-behaviour patterns rather than static KYC data alone; the platform is already operational across roughly two dozen banks and is being expanded. The RBI Innovation Hub has also begun working directly with the Indian Cyber Crime Coordination Centre (I4C) to share fraud-risk intelligence and coordinate detection in near real time.
FIU-IND and the PMLA Framework
The Prevention of Money Laundering Act, 2002 (PMLA) is the backbone of India's AML architecture. It mandates KYC verification, Customer Due Diligence, record maintenance, and timely reporting of suspicious transactions to the Financial Intelligence Unit–India (FIU-IND). Banks are required to file Suspicious Transaction Reports (STRs) and Cash Transaction Reports with FIU-IND, which in turn analyses financial intelligence and shares it with law enforcement and regulators. On paper, this creates a feedback loop between banks, the RBI, and enforcement agencies; in practice, the sheer volume of mule-linked transactions are hundreds of thousands of accounts flagged nationally has strained the capacity of this reporting chain to generate timely, actionable freezes before funds are withdrawn or converted to cryptocurrency.
The IT Act, CERT-In, and Cyber Enforcement
The Information Technology Act, 2000, together with provisions of the Bharatiya Nyaya Sanhita, provides the criminal-law basis for prosecuting mule account operators, aggregators, and the fraudsters who direct them. CERT-In's role sits slightly upstream of the banking layer: it issues advisories on phishing, fake payment gateways, and compromised digital infrastructure that fraud syndicates use to recruit mule account holders and move money. The Ministry of Home Affairs' I4C coordinates the National Cyber Crime Reporting Portal and the 1930 helpline, which allow victims to report fraud and trigger a limited window for freezing beneficiary accounts. I4C has also issued direct public alerts against illegal payment gateways built on mule accounts, warning citizens not to rent or sell their bank credentials to intermediaries.
The Coordination Gap
None of these institutions is short of legal authority. The gap is operational: banks, the RBI, FIU-IND, state police cyber cells, the CBI, and I4C each hold a piece of the picture, but no single agency has a real-time, end-to-end view of an account from opening to fraud to freeze. A mule account can be flagged by one bank's internal monitoring, reported through a completely different victim's complaint in another state, and investigated by a third jurisdiction's cyber police with each step introducing delay. The Indian Banks' Association has publicly pushed for the RBI to be given clearer power to directly freeze accounts flagged as mule accounts, rather than requiring each bank to act unilaterally or wait for a police request, precisely because this fragmentation lets fraudsters withdraw or launder funds within hours of a transaction.
Policy Recommendations
1. Mandatory video-KYC and biometric re-verification for all new accounts opened through business correspondents and third-party agents, with personal liability for verifying bank officials found complicit.
2. A statutory, RBI-backed mechanism allowing banks to freeze accounts flagged by MuleHunter.ai-type systems or FIU-IND intelligence within hours, rather than only after a formal police complaint.
3. A unified, interoperable case database linking the National Cyber Crime Reporting Portal, FIU-IND's STR system, and state cyber cells, so that an account flagged once is visible to every agency instantly.
4. Stronger due-diligence audits of banking correspondents and cooperative banks, which recur disproportionately in mule account cases relative to their share of total accounts.
5. Public financial-literacy campaigns targeted at the economically vulnerable groups most often recruited as unwitting mule account holders, paired with clear legal guidance distinguishing victims from willing participants.
Conclusion
The branch-level mule account cases surfacing across Delhi and other cities are not isolated policing stories; they are a live audit of India's AML and KYC architecture. The RBI, FIU-IND, CERT-In, and law enforcement agencies each have credible tools and legal mandates like MuleHunter.ai, PMLA reporting, IT Act prosecutions, and I4C's coordination portal chief among them but fraud syndicates continue to outpace the system by exploiting the seams between institutions rather than any single point of failure. Closing that gap requires less new law and more operational integration: faster account freezes, verified accountability at the point of account opening, and a shared, real-time picture of mule networks across every agency involved. Until banks, regulators, and investigators can act as one system rather than several disconnected ones, every dismantled racket will simply be replaced by the next.
References
- https://aninews.in/news/national/general-news/delhi-police-arrests-bank-deputy-manager-in-83776792-crore-mule-account-case-linked-to-159-cyber-fraud-complaints20260610130737/
- https://the420.in/delhi-bank-manager-mule-account-cyber-fraud-case/
- https://www.business-standard.com/finance/news/what-are-mule-accounts-cybercrime-banking-layer-india-fraud-rbi-126062400855_1.html
- https://www.business-standard.com/india-news/centre-freezes-450-000-mule-bank-accounts-used-in-cyber-fraud-schemes-124111200320_1.html
- https://www.medianama.com/2025/04/223-iba-rbi-cyber-fraud-measures-freeze-bank-accounts-cybercrime/
- https://www.deccanherald.com/amp/story/india%2Fcentre-warns-of-illegal-payment-gateways-and-mule-accounts-3252723
- https://www.deccanherald.com/india/over-85-lakh-mule-accounts-in-700-bank-branches-used-by-cyber-criminals-cbi-3604229
- https://website.rbi.org.in/en/web/rbi/-/notifications/master-direction-know-your-customer-kyc-direction-2016-updated-as-on-may-04-2023-lt-span-gt-11566
- https://www.indiacode.nic.in/bitstream/123456789/15402/1/moneylaunderingact2002.pdf
- https://www.indiacode.nic.in/bitstream/123456789/13116/1/it_act_2000_updated.pdf
- https://www.mha.gov.in/en/division_of_mha/cyber-and-information-security-cis-division/Details-about-Indian-Cybercrime-Coordination-Centre-I4C-Scheme

Executive Summary:
The video that allegedly showed cars running into an Indian flag while Pakistan flags flying in the air in Indian states, went viral on social media but it has been established to be misleading. The video posted is neither from Kerala nor Tamil Nadu as claimed, instead from Karachi, Pakistan. There are specific details like the shop's name, Pakistani flags, car’s number plate, geolocation analyses that locate where the video comes from. The false information underscores the importance of verifying information before sharing it.


Claims:
A video circulating on social media shows cars trampling the Indian Tricolour painted on a road, as Pakistani flags are raised in pride, with the incident allegedly taking place in Tamil Nadu or Kerala.


Fact Check:
Upon receiving the post we closely watched the video, and found several signs that indicated the video was from Pakistan but not from any place in India.
We divided the video into keyframes and found a shop name near the road.
We enhanced the image quality to see the shop name clearly.


We can see that it’s written as ‘Sanam’, also we can see Pakistan flags waving on the road. Taking a cue from this we did some keyword searches with the shop name. We found some shops with the name and one of the shop's name ‘Sanam Boutique’ located in Karachi, Pakistan, was found to be similar when analyzed using geospatial Techniques.


We also found a similar structure of the building while geolocating the place with the viral video.


Additional confirmation of the place is the car’s number plate found in the keyframes of the video.

We found a website that shows the details of the number Plate in Karachi, Pakistan.

Upon thorough investigation, it was found that the location in the viral video is from Karachi, Pakistan, but not from Kerala or Tamil Nadu as claimed by different users in Social Media. Hence, the claim made is false and misleading.
Conclusion:
The video circulating on social media, claiming to show cars trampling the Indian Tricolour on a road while Pakistani flags are waved, does not depict an incident in Kerala or Tamil Nadu as claimed. By fact-checking methodologies, it has been confirmed now that the location in the video is actually from Karachi, Pakistan. The misrepresentation shows the importance of verifying the source of any information before sharing it on social media to prevent the spread of false narratives.
- Claim: A video shows cars trampling the Indian Tricolour painted on a road, as Pakistani flags are raised in pride, taking place in Tamil Nadu or Kerala.
- Claimed on: X (Formerly known as Twitter)
- Fact Check: Fake & Misleading
