
#FactCheck - Viral Video of Man ‘Running on Water’ Found to Be AI-Generated
Executive Summary:
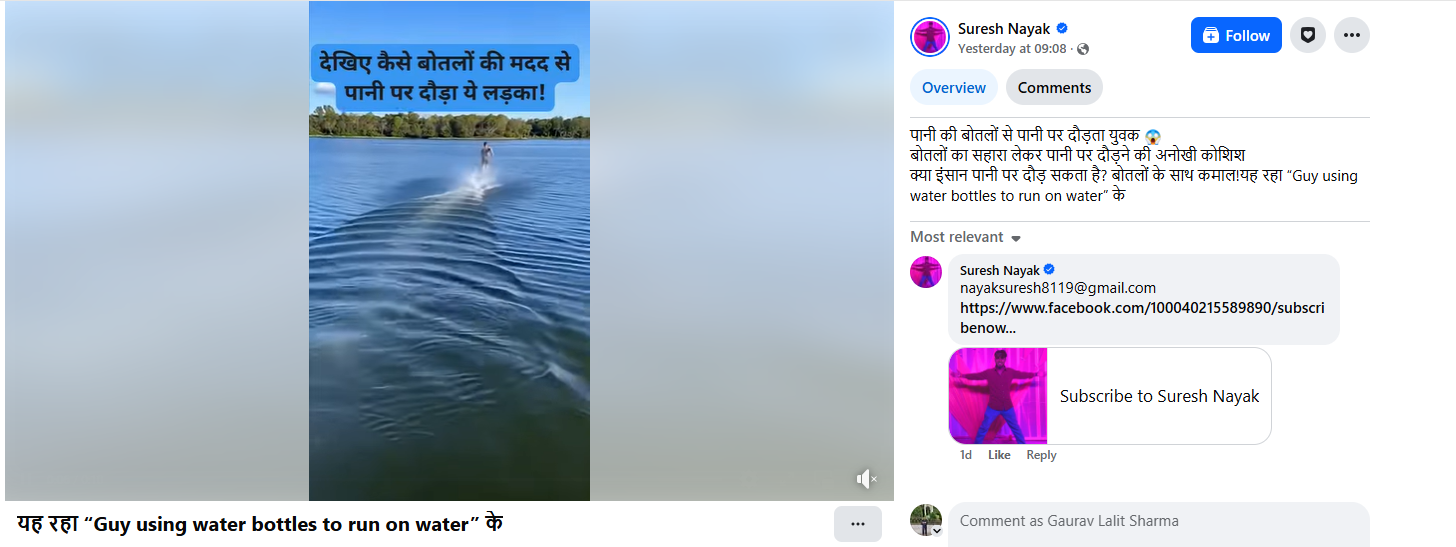
A video is being shared on social media showing a man running rapidly in a river with water bottles tied to both his feet. Users are circulating the video claiming that the man is attempting to run on water using the support of the bottles. CyberPeace’s research found the viral claim to be false. Our research revealed that the video being shared on social media is not real but has been generated using artificial intelligence (AI).
Claim :
The claim was shared by a Facebook user on February 5, 2026, who wrote that a man was running on water using water bottles tied to his feet, calling it a unique attempt and questioning whether humans can run on water. Links to the post, its archived version, and screenshots are provided below.
Fact Check:
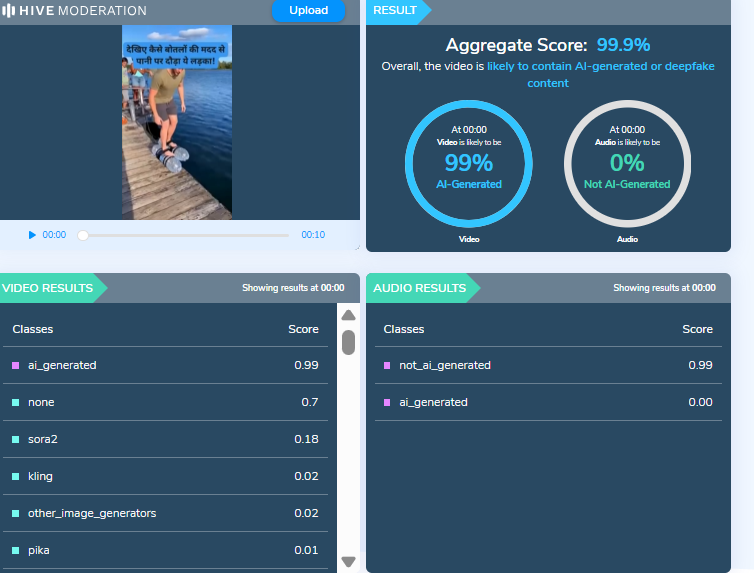
To verify the claim, we searched relevant keywords on Google but did not find any credible media reports supporting the incident. A closer examination of the viral video revealed several visual irregularities, raising suspicion that it may have been AI-generated. The video was then scanned using the AI detection tool Hive Moderation. According to the tool’s results, the video is 99 percent likely to be AI-generated.
Conclusion:
Our research confirms that the viral video does not depict a real incident and has been falsely shared as a genuine attempt to run on water.

Related Blogs

Introduction
MSMEs, being the cornerstone of the Indian economy, are one of the most vulnerable targets in cyberspace and no enterprise is too small to be a target for malicious actors. MSMEs hardly ever perform a cyber-risk assessment, but when they do, they may run into a number of internal problems, such as cyberattacks brought on by inadequate networking security, online fraud, ransomware assaults, etc. Tackling cyber threats in MSMEs is critical mainly because of their high level of dependance on digital technologies and the growing sophistication of cyber attacks. Protecting them from cyber threats is essential, as a security breach can have devastating consequences, including financial loss, reputational damage, and operational disruptions.
Key Cyber Threats that MSMEs are facing
MSMEs are most vulnerable to are phishing attacks, ransomware, malware and viruses, insider threats, social engineering attacks, supply chain attacks, credential stuffing and brute force attacks and Distributed Denial of Service (DDoS) Attacks. Some of these attacks are described as under-
- Insider threats arise from employees or contractors who intentionally or unintentionally compromise security. It involves data theft, misuse of access privileges, or accidental data exposure.
- Social engineering attacks involve manipulating individuals into divulging confidential information or performing actions that compromise security by pretexting, baiting, and impersonation.
- Supply chain attacks exploit the trust in relationships between businesses and their suppliers and introduce malware, compromise data integrity, and disrupt operations.
- Credential stuffing and brute force attacks give unauthorized access to accounts and systems, leading to data breaches and financial losses.
Challenges Faced by MSMEs in Cybersecurity
The challenges faced by MSMEs in cyber security are mainly due to limited resources and budget constraints which leads to other issues such as a lack of specialized expertise as MSMEs often lack the IT support of cyber security experts. Awareness and training are needed to mitigate poor understanding of cyber threats and their complexity in nature. Vulnerabilities in the supply chain are present as they rely on third-party vendors and partners often, introducing potential supply chain vulnerabilities. Regulatory compliance is often complex and is taken seriously only when an issue crops up but it needs special attention especially with the DPDP Act coming in. The lack of an incident response plan leads to delayed and inadequate responses to cyber incidents, increasing the impact of breaches.
Best Practices for Tackling Cyber Threats for MSMEs
To effectively tackle cyber threats, MSMEs should adopt a comprehensive approach such as:
- Implementing and enforcing strong access controls by using MFA or 2FA and password policies. Limiting employee access as role based and updating the same as and when needed.
- Regularly apply security patches and use automated patch management solutions to prevent exploitation of known vulnerabilities.
- Conduct employee training and awareness programs and promote a security-first approach for the employees and assessing employee readiness to identify improvement areas.
- Implement network security measures by using firewalls and intrusion detection systems. Using secure Wi-Fi networks via strong encryptions and changing default credentials for the router are recommended, as is segmenting networks to limit lateral movement within the network in case of a breach.
- Regular data backup ensures that in case of an attack, data loss can be recovered and made available in secure offsite locations to protect it from unauthorized access.
- Developing an incident response plan that outlines the roles, responsibilities and procedure for responding to cyber incidents with regular drills to ensure readiness and clear communication protocols for incident reporting to regulators, stakeholders and customers.
- Implement endpoint security solutions using antivirus and anti-malware softwares. Devices should be against unauthorized access and implement mobile device management solutions enforcing security policies on employee-owned devices used for work purposes.
- Cyber insurance coverage will help in transferring financial risks in case of cyber incidents. It should have comprehensive coverage including business interruptions, data restoration, legal liabilities and incident response costs.
Recommended Cybersecurity Solutions Tailored for MSMEs
- A Managed Security Service Provider offers outsourced cybersecurity services, including threat monitoring, incident response, and vulnerability management that may be lacking in-house.
- Cloud-Based Security Solutions such as firewall as a service and Security Information and Event Management , provide scalable and cost-effective protection for MSMEs.
- Endpoint Detection and Response (EDR) Tools detect and respond to threats on endpoints, providing real-time visibility into potential threats and automating incident response actions.
- Security Awareness Training Platforms deliver interactive training sessions and simulations to educate employees about cybersecurity threats and best practices.
Conclusion
Addressing cyber threats in MSMEs requires a proactive and multi-layered approach that encompasses technical solutions, employee training, and strategic planning. By implementing best practices and leveraging cybersecurity solutions tailored to their specific needs, MSMEs can significantly enhance their resilience against cyber threats. As cyber threats continue to evolve, staying informed about the latest trends and adopting a culture of security awareness will be essential for MSMEs to protect their assets, reputation, and bottom line.
References:
- https://economictimes.indiatimes.com/small-biz/security-tech/security/cyber-security-pitfalls-and-how-negligence-can-be-expensive-for-msmes/articleshow/99508822.cms?from=mdr
- https://www.investopedia.com/financial-edge/0112/3-ways-cyber-crime-impacts-business.aspx
- https://www.financialexpress.com/business/sme-msme-tech-cisco-launches-new-tool-for-smbs-to-assess-their-cybersecurity-readiness-2538348/
- https://www.cloverinfotech.com/blog/small-businesses-big-problems-are-cyber-attacks-crushing-indias-msmes/

Smart Wearable devices are designed to track several activities in defined parameters and are increasingly becoming a part of everyday life. According to Markets and Markets Report, the global wearable tech market is projected to reach a staggering USD 256.4 billion by 2026. One of the main areas of use of wearable devices is health, including biomedical research, health care, personal health practices and tracking, technology development, and engineering. These wearable devices often include digital health technologies such as consumer smartwatches that monitor an individual's heart rate and step count, and other body-worn sensors like those that continuously monitor blood glucose concentration.
Wearable devices used by the general population are getting increasingly popular. Health devices like fitness trackers and smartwatches enable continuous monitoring of personal health. Privacy is an emerging concern due to the real-time collection of sensitive data. Vulnerabilities due to unauthorised access or discrimination in case of information being revealed without consent are the primary concerns with these devices. While these concerns are present a lot of related misinformation is emerging due to the same.
While wearable devices typically come with terms of use that outline how data is collected and used, and there are regulations in place such as EU Law GDPR, such regulations largely govern the regulatory compliances on the handling of personal data, however, the implementation and compliances by the manufacturer is a one another aspect which might present the question on privacy protection. In addition, beyond the challenge of regulatory compliance, the rise of myths and misinformation surrounding wearable tech presents a separate issue.
Common Misconceptions About Privacy with Wearable Tech
- With the rapid development and growth of wearable technology their use has been subject to countless rumours which fuel misinformation narratives in the minds of general public. Addressing these misconceptions and privacy concerns requires targeted strategies.
- A prevalent misconception is that they are constantly spying on users. While wearable devices collect users’ data in real time, their vulnerability to unauthorised access is similar to that of a non-wearable device. The issue is of consent when it comes to wearable technology because it gives the ability to record. If permissions are not asked when a person is being recorded then the data is accessible to external entities.
- There is a common myth that wearable tech is surveillance tool. This is entirely a conjecture. These devices collect the user data with their prior consent and have been created to provide them with real-time information, most commonly physical health information. Since users choose the information shared, the idea of wearable tech serving as a surveillance tool is unfounded.
- Another misconception about wearable tech is that it can diagnose medical conditions. These devices collect real-time health data, such as heart rate or activity levels, they are not designed for medical diagnosis. The data collected may not always be accurate or reliable for clinical use to be interpreted by a healthcare professional. This is mainly because the makers of these devices are not held to the safety and liability standards that medical providers are.
- A prevalent misconception is that wearable tech can cure health issues, which is simply untrue. Wearable tech devices are essentially tracking the health parameters that a user sets. It in no way is a cure for any health issue that one suffers from. A user can manage their health based on the parameters they set on the device such as the number of steps that they walk, check on the heart rate and other metrics for their mental satisfaction but they are not a cure to treat diseases. Wearable tech acts as alerts, notifying users of important health metrics and encouraging proactive health management.
Addressing Privacy and Health Concerns in Wearable Tech
Wearable technology raises concerns for privacy and health due to the colossal amount of personal data collected. To address these, strong data protection measures are essential, ensuring that sensitive health information is securely stored and shared only with consent. Providing users with control over their data is one of the ways to build user trust. It includes enabling them to opt in, access, or delete the data in question. Regulators should establish clear guidelines, ensuring wearables ensure the compliances with data protection regulations like HIPPA, GDPR or DPDP Act, whichever is applicable as per the jurisdiction. Furthermore, global standards for data encryption, device security, and user privacy should be implemented to mitigate risks. Transparency in data usage and consistent updates to software security are also crucial for protecting users' privacy and health while promoting the responsible use of wearable tech.
CyberPeace Insights
- Making informed decisions about wearable tech starts with thorough research. Start by reading reviews and comparing products to assess their features, compatibility, and security standards.
- Investigate the manufacturer’s reputation for data protection and device longevity. Understanding device capabilities is crucial. One should evaluate whether the wearable meets their needs, such as fitness tracking, health monitoring, or communication features. Consider software security and updates, and data accuracy when comparing options. Opt for devices that offer two-factor authentication for an additional layer of security.
- Check the permissions requested by the accompanying app; only grant access to data that is necessary for the device's functionality. Always read the terms of use to understand your rights and responsibilities regarding the use of the device. Review and customize data-sharing settings for better control to prevent unauthorised access.
- Staying updated on the tech is equally important. A user should follow the advancements in wearable technology be it regular security updates, or regulatory changes that may affect privacy and usability. This ensures getting tech that aligns with user lifestyle while meeting privacy and security expectations.
Conclusion
Privacy and Misinformation are key concerns that emerge due to the use of wearable tech designed to offer benefits such as health monitoring, fitness tracking, and personal convenience. It requires a combination of informed decision-making by users and stringent regulatory oversight to overcome the issues that emerge due to misinformation about these devices. Users must ensure they understand the capabilities and limitations of their devices, from data accuracy to privacy risks. Additionally, manufacturers and regulators need to prioritise transparency, data protection, and compliance with global standards like GDPR or DPDP to build trust. As wearable tech continues to evolve, a balanced approach to innovation and privacy will be essential in fostering its responsible and beneficial use for all.
References
- https://thehealthcaretechnologyreport.com/privacy-data-security-concerns-rise-as-healthcare-wearables-gain-popularity/
- https://journals.plos.org/digitalhealth/article?id=10.1371/journal.pdig.0000104
- https://www.marketsandmarkets.com/Market-Reports/wearable-electronics-market-983.html?gclid=Cj0KCQjwgMqSBhDCARIsAIIVN1V0sqrk6SpYSga3rcDtWcwh8npZ08L0_s4X91gh7yPAa6QmsctB-lMaAlpqEALw_wcB
- https://www.cambridge.org/core/journals/legal-information-management/article/health-data-on-the-go-navigating-privacy-concerns-with-wearable-technologies/05DAF11EFA807051362BB39260C4814C

Introduction
In the digital realm of social media, Meta Platforms, the driving force behind Facebook and Instagram, faces intense scrutiny following The Wall Street Journal's investigative report. This exploration delves deeper into critical issues surrounding child safety on these widespread platforms, unravelling algorithmic intricacies, enforcement dilemmas, and the ethical maze surrounding monetisation features. Instances of "parent-managed minor accounts" leveraging Meta's subscription tools to monetise content featuring young individuals have raised eyebrows. While skirting the line of legality, this practice prompts concerns due to its potential appeal to adults and the associated inappropriate interactions. It's a nuanced issue demanding nuanced solutions.
Failed Algorithms
The very heartbeat of Meta's digital ecosystem, its algorithms, has come under intense scrutiny. These algorithms, designed to curate and deliver content, were found to actively promoting accounts featuring explicit content to users with known pedophilic interests. The revelation sparks a crucial conversation about the ethical responsibilities tied to the algorithms shaping our digital experiences. Striking the right balance between personalised content delivery and safeguarding users is a delicate task.
While algorithms play a pivotal role in tailoring content to users' preferences, Meta needs to reevaluate the algorithms to ensure they don't inadvertently promote inappropriate content. Stricter checks and balances within the algorithmic framework can help prevent the inadvertent amplification of content that may exploit or endanger minors.
Major Enforcement Challenges
Meta's enforcement challenges have come to light as previously banned parent-run accounts resurrect, gaining official verification and accumulating large followings. The struggle to remove associated backup profiles adds layers to concerns about the effectiveness of Meta's enforcement mechanisms. It underscores the need for a robust system capable of swift and thorough actions against policy violators.
To enhance enforcement mechanisms, Meta should invest in advanced content detection tools and employ a dedicated team for consistent monitoring. This proactive approach can mitigate the risks associated with inappropriate content and reinforce a safer online environment for all users.
The financial dynamics of Meta's ecosystem expose concerns about the exploitation of videos that are eligible for cash gifts from followers. The decision to expand the subscription feature before implementing adequate safety measures poses ethical questions. Prioritising financial gains over user safety risks tarnishing the platform's reputation and trustworthiness. A re-evaluation of this strategy is crucial for maintaining a healthy and secure online environment.
To address safety concerns tied to monetisation features, Meta should consider implementing stricter eligibility criteria for content creators. Verifying the legitimacy and appropriateness of content before allowing it to be monetised can act as a preventive measure against the exploitation of the system.
Meta's Response
In the aftermath of the revelations, Meta's spokesperson, Andy Stone, took centre stage to defend the company's actions. Stone emphasised ongoing efforts to enhance safety measures, asserting Meta's commitment to rectifying the situation. However, critics argue that Meta's response lacks the decisive actions required to align with industry standards observed on other platforms. The debate continues over the delicate balance between user safety and the pursuit of financial gain. A more transparent and accountable approach to addressing these concerns is imperative.
To rebuild trust and credibility, Meta needs to implement concrete and visible changes. This includes transparent communication about the steps taken to address the identified issues, continuous updates on progress, and a commitment to a user-centric approach that prioritises safety over financial interests.
The formation of a task force in June 2023 was a commendable step to tackle child sexualisation on the platform. However, the effectiveness of these efforts remains limited. Persistent challenges in detecting and preventing potential child safety hazards underscore the need for continuous improvement. Legislative scrutiny adds an extra layer of pressure, emphasising the urgency for Meta to enhance its strategies for user protection.
To overcome ongoing challenges, Meta should collaborate with external child safety organisations, experts, and regulators. Open dialogues and partnerships can provide valuable insights and recommendations, fostering a collaborative approach to creating a safer online environment.
Drawing a parallel with competitors such as Patreon and OnlyFans reveals stark differences in child safety practices. While Meta grapples with its challenges, these platforms maintain stringent policies against certain content involving minors. This comparison underscores the need for universal industry standards to safeguard minors effectively. Collaborative efforts within the industry to establish and adhere to such standards can contribute to a safer digital environment for all.
To align with industry standards, Meta should actively participate in cross-industry collaborations and adopt best practices from platforms with successful child safety measures. This collaborative approach ensures a unified effort to protect users across various digital platforms.
Conclusion
Navigating the intricate landscape of child safety concerns on Meta Platforms demands a nuanced and comprehensive approach. The identified algorithmic failures, enforcement challenges, and controversies surrounding monetisation features underscore the urgency for Meta to reassess and fortify its commitment to being a responsible digital space. As the platform faces this critical examination, it has an opportunity to not only rectify the existing issues but to set a precedent for ethical and secure social media engagement.
This comprehensive exploration aims not only to shed light on the existing issues but also to provide a roadmap for Meta Platforms to evolve into a safer and more responsible digital space. The responsibility lies not just in acknowledging shortcomings but in actively working towards solutions that prioritise the well-being of its users.
References
- https://timesofindia.indiatimes.com/gadgets-news/instagram-facebook-prioritised-money-over-child-safety-claims-report/articleshow/107952778.cms
- https://www.adweek.com/blognetwork/meta-staff-found-instagram-tool-enabled-child-exploitation-the-company-pressed-ahead-anyway/107604/
- https://www.tbsnews.net/tech/meta-staff-found-instagram-subscription-tool-facilitated-child-exploitation-yet-company
