
#FactCheck - Debunking Viral Photo: Tears of Photographer Not Linked to Ram Mandir Opening
Executive Summary:
A photographer breaking down in tears in a viral photo is not connected to the Ram Mandir opening. Social media users are sharing a collage of images of the recently dedicated Lord Ram idol at the Ayodhya Ram Mandir, along with a claimed shot of the photographer crying at the sight of the deity. A Facebook post that posts this video says, "Even the cameraman couldn't stop his emotions." The CyberPeace Research team found that the event happened during the AFC Asian Cup football match in 2019. During a match between Iraq and Qatar, an Iraqi photographer started crying since Iraq had lost and was out of the competition.
Claims:
The photographer in the widely shared images broke down in tears at seeing the icon of Lord Ram during the Ayodhya Ram Mandir's consecration. The Collage was also shared by many users in other Social Media like X, Reddit, Facebook. An Facebook user shared and the Caption of the Post reads,


Fact Check:
CyberPeace Research team reverse image searched the Photographer, and it landed to several memes from where the picture was taken, from there we landed to a Pinterest Post where it reads, “An Iraqi photographer as his team is knocked out of the Asian Cup of Nations”

Taking an indication from this we did some keyword search and tried to find the actual news behind this Image. We landed at the official Asian Cup X (formerly Twitter) handle where the image was shared 5 years ago on 24 Jan, 2019. The Post reads, “Passionate. Emotional moment for an Iraqi photographer during the Round of 16 clash against ! #AsianCup2019”

We are now confirmed about the News and the origin of this image. To be noted that while we were investigating the Fact Check we also found several other Misinformation news with the Same photographer image and different Post Captions which was all a Misinformation like this one.
Conclusion:
The recent Viral Image of the Photographer claiming to be associated with Ram Mandir Opening is Misleading, the Image of the Photographer was a 5 years old image where the Iraqi Photographer was seen Crying during the Asian Cup Football Competition but not of recent Ram Mandir Opening. Netizens are advised not to believe and share such misinformation posts around Social Media.
- Claim: A person in the widely shared images broke down in tears at seeing the icon of Lord Ram during the Ayodhya Ram Mandir's consecration.
- Claimed on: Facebook, X, Reddit
- Fact Check: Fake

Related Blogs
Introduction
We stand at the edge of a reality once confined to science fiction, a world where the very creations designed to serve us could redefine what it means to be human, rewriting the paradigm we built them in. The increasing prevalence of robotics and embodied AI systems in everyday life and cyber-physical settings draws attention to a complicated network of issues at the intersection of cybersecurity, human-to-robot trust, and robotic safety. The development of robotics cannot be perceived as a novelty or a fleeting interest area for enthusiasts, it has developed into a force that enters the area of human life that is private and has historically been reserved for human connection and care. We live in an era where countries can no longer afford to fall behind, at a time when technological prowess determines global influence. The new development currency of the 21st century is “Techno-sovereign”, meaning that one must be able to innovate as well as incorporate robotics, artificial intelligence, and other technologies.
Entering the Robotic Renaissance
The recent unveiling of the humanoid “pregnancy robot” presents the next frontier in reproductive robotics, garnering both criticism and support. Although this bold innovation holds promise, it also presents unavoidable cybersecurity, privacy, and ethical conundrums. The humanoid is being developed by Kaiwa Technology under the direction of Dr. Zhang Qifeng, who is also connected to Nanyang Technological University. As per the report of ECNS, he presented his idea for a robotic surrogate that could carry a child for a full-term pregnancy at the 2025 World Robot Conference in Beijing. While the technology is indubitably groundbreaking, it raises a lot of ethical and moral concerns as well as legal concerns, as surrogacy is banned in China.
Alongside the concerns raised by various segments of doctors, feminists who argue on the devaluation and pathologising of pregnancy, it also raises various cybersecurity concerns, keeping in mind the interpersonal and intimate nature of human connections, where robotics are now making headway. Pregnancy is inherently intimate. Our understanding of bodily autonomy is blurred when we move into the realm of machinery. From artificial amniotic fluid sensors to embryo data, every layer of this technology becomes a possible attack vector. Robots with artificial wombs are essentially IoT-powered medical systems. As per the research conducted by the Department of Computer Science and Engineering, Cornell University, “our lives have been made easier by the incorporation of AI into robotics systems, but there is a significant drawback as well: these systems are susceptible to security breaches. Malicious actors may take advantage of the data, algorithms, and physical components that make up AI-Robotics systems, which can cast a debilitating impact.
The Robotic Pivot: The Market’s Greatest Disruption
The humanoid “pregnancy robot” is not the only robotic innovation planning to take the industry for a whirlwind. China is pushing the boundaries amidst the escalating trade wars. Beijing is stepping up its efforts in sectors where it has the capacity and necessity to advance before the US. China’s leaders see AI as a source of national pride, a means of enhancing its military might, and a long-standing problem of Western dominance. The proof lies in the fact that Beijing hosted the first World Humanoid Robot Games, reflecting China’s dual goals of showcasing its technological prowess as it moves closer to establishing itself as a dominant force in artificial intelligence applied to robotics and bringing people closer to machines that will eventually play a bigger role in daily life and the economy.
Despite China’s prominence, it is not the only country that sees the potential in AI-enabled robotics. Indian Space Research Organisation’s chairman V Narayanan announced that the humanoid robot Gaganyaan programme’s first uncrewed mission G1 would be launched with humanoid robot Vyommitra in December.
Conclusion
The emergence of robotics holds both great potential and significant obstacles holds both great potential and significant obstacles. Robots have the potential to revolutionise accessibility and efficiency in a variety of fields, including healthcare and space exploration, but only if human trust, ethics, and cybersecurity keep up with technological advancements. This is not a far-flung issue for India, rather, it is a pressing appeal to properly lead in a world where technological sovereignty is equivalent to world power.
References
- https://nurse.org/news/pregnancy-robot-artificial-womb-china/
- https://timesofindia.indiatimes.com/life-style/health-fitness/health-news/chinas-2026-humanoid-robot-pregnancy-with-artificial-womb-a-revolutionary-leap-in-reproductive-technology/articleshow/123357813.cms?utm_source=chatgpt.com
- https://arxiv.org/pdf/2310.08565
- https://www.theguardian.com/world/2025/apr/21/humanoid-workers-and-surveillance-buggies-embodied-ai-is-reshaping-daily-life-in-china
- https://english.elpais.com/technology/2025-08-21/china-stages-first-robot-olympics-to-showcase-its-tech-ambition.html
- https://www.tribuneindia.com/news/india/1st-non-crew-gaganyaan-mission-to-launch-in-dec-with-robot-vyommitra/
Executive Summary
Social media users are claiming that Indian Army Chief General Dhiraj Seth dances with soldiers’ wives and attended a dance competition organised by the Border Security Force Wives Welfare Association (BWWA). CyberPeace Research found no credible sources to substantiate the viral claim. Our research revealed that the viral image is related to his visit to Nepal. According to reports, he travelled to Nepal on his first foreign visit after taking charge of the Indian Army, where he was welcomed by senior Nepal Army officials. During the visit, he was also scheduled to receive the honorary rank of General of the Nepal Army. However, his photograph is being linked to a dance video from an event organised by the Central Armed Police Forces (CAPF), accompanied by objectionable claims about him. Our research found no credible evidence confirming that General Dhiraj Seth attended the event or was associated with the activities shown in the video. Therefore, linking his photograph from the Nepal visit to the dance video is misleading.
Claim:
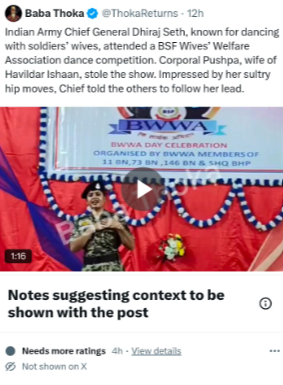
It is being claimed on social media that Indian Army Chief General Dhiraj Seth attended a dance competition organised by the BSF Wives Welfare Association (BWWA), where he was impressed by a woman’s dance performance and asked other participants to follow her lead.
https://x.com/ThokaReturns/status/2110854323760693485
Fact Check
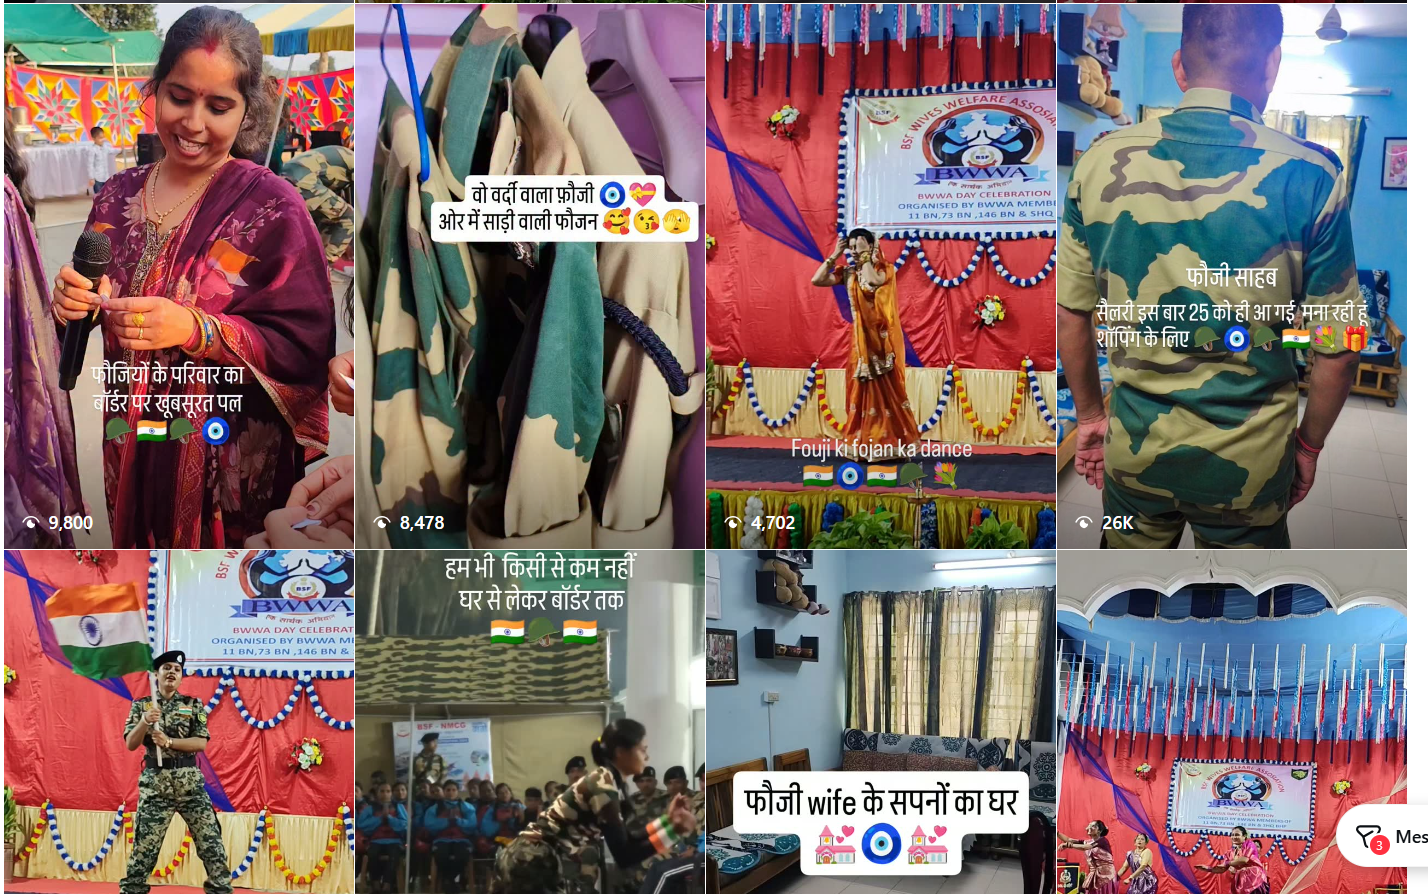
To verify the viral claim, we conducted a reverse image search using keyframes from the video. During this process, we found the video on Instagram. The text “BSF Wives Welfare Association” was visible on the backdrop behind the stage. However, there was no mention of Army Chief General Dhiraj Seth anywhere in the video.
https://www.instagram.com/reels/Ddl7oTEgnf7/
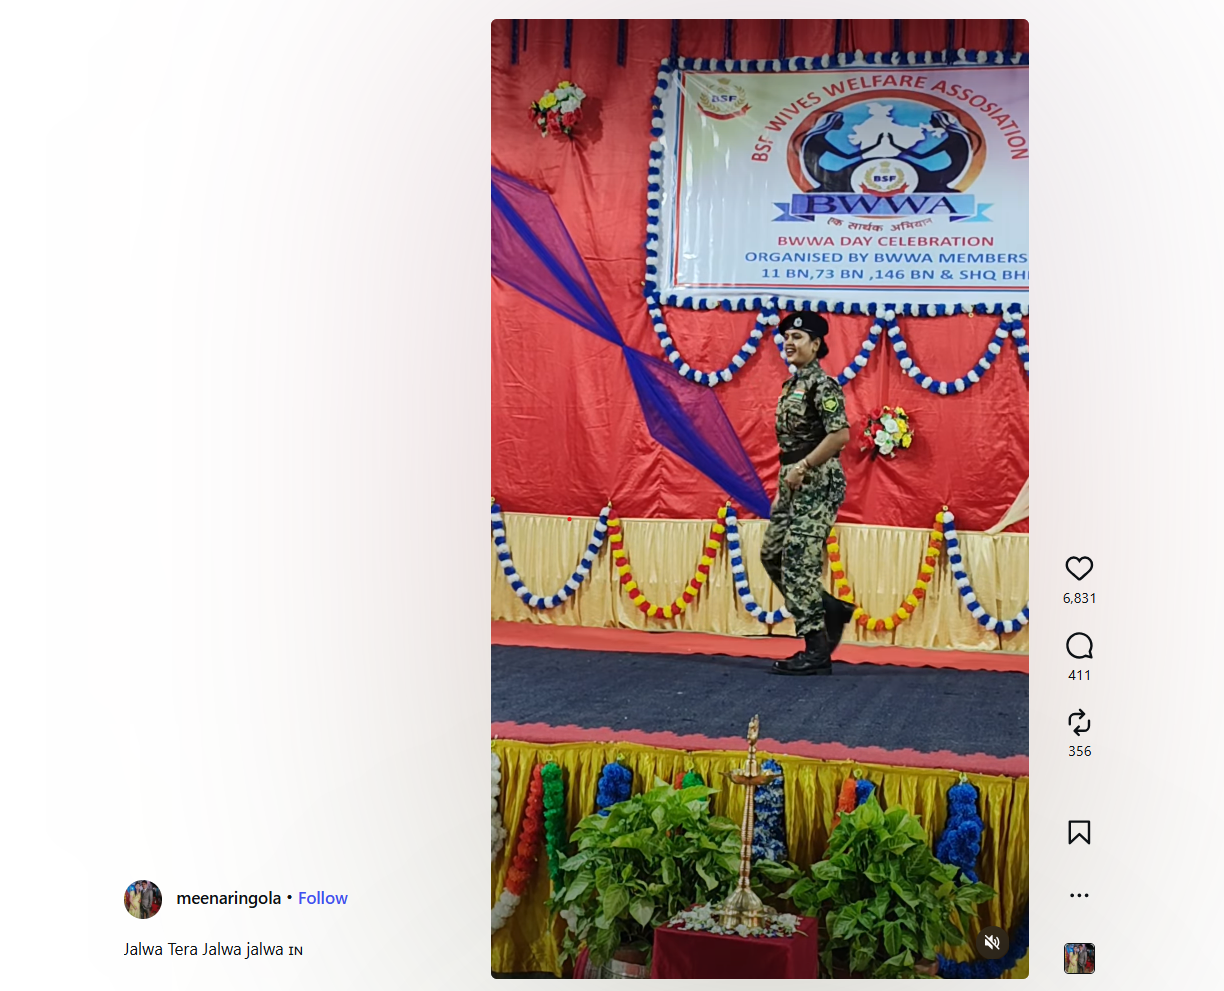
After reviewing these videos, our research found no evidence to substantiate the claim that General Dhiraj Seth attended an event organised by the BSF Wives Welfare Association or danced at the event. His photograph is being linked to the dance video, but no credible evidence supporting this claim was found.
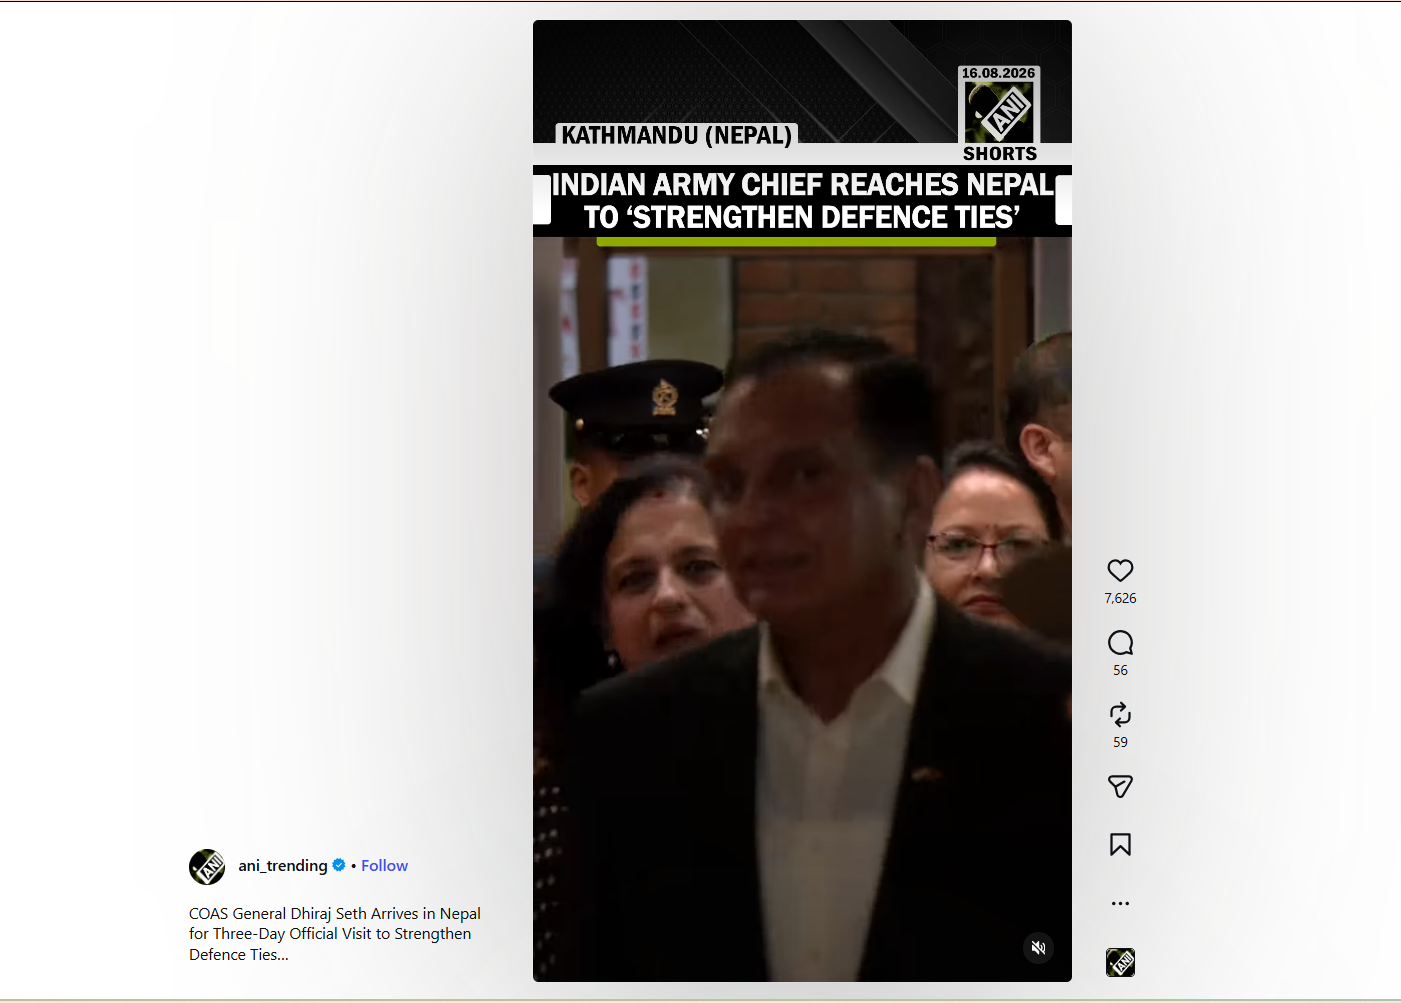
During our research, we found the original video of Army Chief General Dhiraj Seth shared by ANI. According to the report, General Dhiraj Seth arrived in Nepal on a three-day official visit aimed at strengthening defence ties between the two countries.
https://www.instagram.com/reels/DcGxzLPExR5/
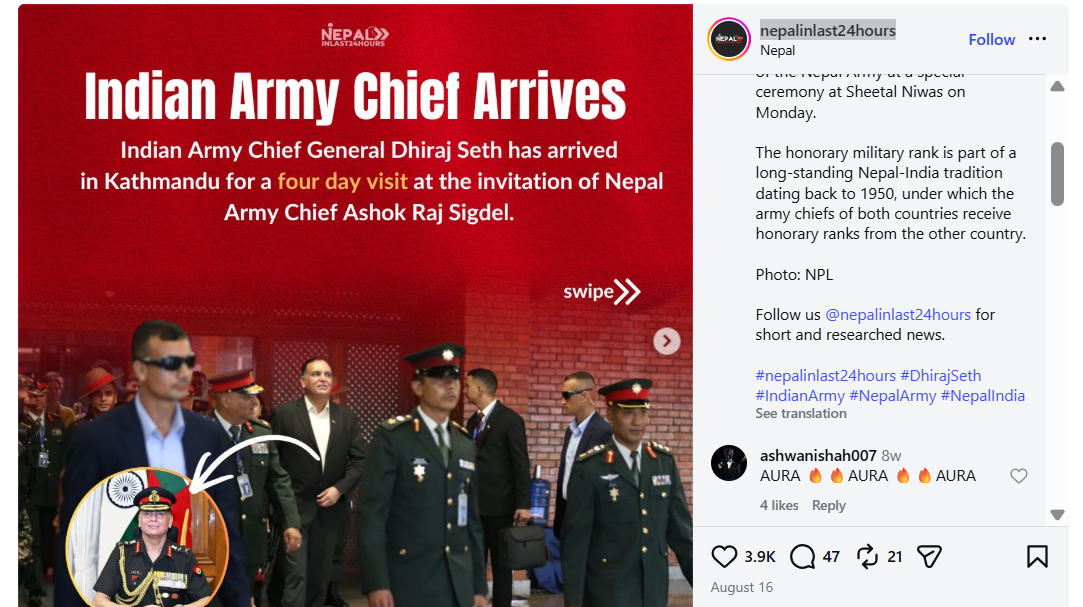
In the final stage of our research, we found a report on an Instagram account named ‘nepalinlast24hours’. According to the report, Indian Army Chief General Dhiraj Seth arrived in Kathmandu on his first foreign visit after taking command of the Indian Army on June 30, 2026. He was welcomed by senior Nepal Army officials at Tribhuvan International Airport.
The report stated that during his four-day visit, General Seth was scheduled to meet Nepal’s Prime Minister Balendra Shah and Nepal Army Chief Ashok Raj Sigdel. Additionally, he was scheduled to be conferred with the honorary rank of General of the Nepal Army at a special ceremony at Sheetal Niwas on Monday.This tradition between India and Nepal dates back to 1950. Under the arrangement, the army chiefs of both countries are conferred with honorary military ranks in each other’s armies.
https://www.instagram.com/p/DcGbgm0jUBH/?dlrf=MXFndzM5dGp4ZTh5OA%3D%3D
Conclusion
Our research found that the viral photograph of Indian Army Chief General Dhiraj Seth is related to his visit to Nepal. According to reports, he travelled to Nepal on his first foreign visit after taking command of the Indian Army, where he was welcomed by senior Nepal Army officials. During the visit, he was also scheduled to be conferred with the honorary rank of General of the Nepal Army.However, his photograph is being linked on social media to a dance video from an event organised by the Central Armed Police Forces (CAPF), accompanied by objectionable claims about him. Our research found no credible evidence confirming General Dhiraj Seth’s presence at the event or his association with the activities shown in the video. Therefore, linking his photograph from his Nepal visit to the dance video is misleading.

In what is being stated by experts to be one of the largest data breaches of all time, approximately 16 billion passwords were exposed online last week. According to various news reports, the leak contains credentials spanning a broad array of online services, including Facebook, Instagram, Gmail, etc., creating a serious alarm across the globe. Cybersecurity specialists have noted that this leak poses immense risks of account takeovers, identity theft, and enabling phishing scams. The leaked data is being described as a “collection-of-collections,” with multiple previously breached databases compiled into one easy-to-access repository for cybercriminals.
Infostealer Malware and Why It’s a Serious Threat
This incident brought to light a type of malware that experts refer to as the Infostealer. Just as the name suggests, this is a malware program made expressly to take personal information from compromised computers and devices, including cookies, session tokens, browser data, login credentials, and more. It targets high-value credentials, as opposed to ransomware, which encrypts files for ransom, or spyware that passively watches users. Once installed, they silently gather passwords, screenshots, and other information while hiding inside unassuming software, such as a game, utility, or browser plugin. Once stolen, these credentials are then combined by hackers to create databases, which are then offered for sale on dark web forums or even made public, as was the case in this breach. This is particularly risky since, if session tokens or other browser data are also taken, these credentials can be used to get around even two-factor authentication. As a result, the leak would also enable the rise of other crimes such as phishing.
Guidelines for protection
In response to this breach, India’s Computer Emergency Response Team (CERT-IN) issued an advisory, urging all internet users to take immediate action to protect their accounts. Although this is in response to the specific data leak, these are some key measures advised to be followed to maintain a general standard of cyber hygiene at all times.
- Reset your passwords: In case of incidents such as the above, users are advised to change the passwords of their accounts immediately. More so of the ones that have been compromised and need to be prioritised, such as email, online banking, and social media etc.
- Use strong, unique passwords and password manager features: Avoid password reuse across platforms. Using a password manager on a trusted platform can aid in storing and recalling them for different accounts.
- Monitor account activity: Check activity logs, especially for signs of unrecognised login attempts or password-reset notifications.
- Enable Multi-Factor Authentication (MFA): The user is advised to enable two-step verification (via an app like Google Authenticator or a hardware key), which will add an extra security layer.
- Phishing attacks: Cybercriminals will likely attempt to use leaked credentials to impersonate legitimate companies and send phishing emails. Read carefully before clicking on any links or attachments received.
- Scan devices for malware: Run updated antivirus or anti-malware scans to catch and remove infostealers or other malicious software lurking on your device.
Why This Data Breach is a Wake-Up Call
With 16 billion credentials exposed, this breach highlights the critical need for robust personal cybersecurity hygiene. It also reveals the persistent role of infostealer malware in feeding a global cybercrime economy, one where credentials are the most valuable assets. As Infosecurity Europe and other analysts highlight, infostealers are lightweight, often distributed via phishing or malicious downloads, and are highly effective at lifting data in the background without alerting the user. Even up-to-date antivirus software can struggle to catch new variants, making proactive security practices with respect to such malware all the more essential. In a time where data is everything, access to credentials can derive power and safety, regarding it must be kept in check.
Conclusion
This breach is a reminder that cybersecurity is a shared responsibility. Even with protective systems in place with respect to the industries and official authorities, every internet user must do their part in protecting themselves through cyber hygiene practices such as resetting passwords, using multi-factor authentication, staying vigilant against phishing scams, and ensuring devices are regularly scanned for malware. While breaches like this can seem overwhelming and might create a surge of panic, practical measures go a long way in mitigating exposure. Staying informed and proactive is the best defence one can adopt in a rapidly evolving threat landscape.
References
- https://economictimes.indiatimes.com/news/international/us/16-billion-passwords-exposed-in-unprecedented-cyber-leak-of-2025-experts-raise-global-alarm/articleshow/121961165.cms?from=mdr
- https://timesofindia.indiatimes.com/technology/tech-news/16-billion-passwords-leaked-on-internet-what-you-need-to-know-to-protect-your-facebook-instagram-gmail-and-other-accounts/articleshow/121967191.cms
- https://indianexpress.com/article/technology/tech-news-technology/16-billion-passwords-leaked-online-what-we-know-10077546/
- https://indianexpress.com/article/technology/tech-news-technology/16-billion-passwords-leaked-online-what-we-know-10077546/
- https://www.hindustantimes.com/business/certin-issues-advisory-after-data-breach-of-16-billion-credentials-asks-people-to-change-passwords-101750779940872.html
- https://www.cert-in.org.in/s2cMainServlet?pageid=PUBVLNOTES02&VLCODE=CIAD-2025-0024
- https://www.infosecurityeurope.com/en-gb/blog/threat-vectors/guide-infostealer-malware.html
