
#FactCheck – False Claim of Lord Ram's Hologram in Srinagar - Video Actually from Dehradun
Executive Summary:
A video purporting to be from Lal Chowk in Srinagar, which features Lord Ram's hologram on a clock tower, has gone popular on the internet. The footage is from Dehradun, Uttarakhand, not Jammu and Kashmir, the CyberPeace Research Team discovered.
Claims:
A Viral 48-second clip is getting shared over the Internet mostly in X and Facebook, The Video shows a car passing by the clock tower with the picture of Lord Ram. A screen showcasing songs about Lord Ram is shown when the car goes forward and to the side of the road.

The Claim is that the Video is from Kashmir, Srinagar

Similar Post:

Fact Check:
The CyberPeace Research team found that the Information is false. Firstly we did some keyword search relating to the Caption and found that the Clock Tower in Srinagar is not similar to the Video.

We found an article by NDTV mentioning Srinagar Lal Chowk’s Clock Tower, It's the only Clock Tower in the Middle of Road. We are somewhat confirmed that the Video is not From Srinagar. We then ran a reverse image search of the Video by breaking down into frames.
We found another Video that visualizes a similar structure tower in Dehradun.

Taking a cue from this we then Searched for the Tower in Dehradun and tried to see if it matches with the Video, and yes it’s confirmed that the Tower is a Clock Tower in Paltan Bazar, Dehradun and the Video is actually From Dehradun but not from Srinagar.
Conclusion:
After a thorough Fact Check Investigation of the Video and the originality of the Video, we found that the Visualisation of Lord Ram in the Clock Tower is not from Srinagar but from Dehradun. Internet users who claim the Visual of Lord Ram from Srinagar is totally Baseless and Misinformation.
- Claim: The Hologram of Lord Ram on the Clock Tower of Lal Chowk, Srinagar
- Claimed on: Facebook, X
- Fact Check: Fake

Related Blogs
Introduction
Recently in July 2026, India's Cyber Crime Coordination Centre (I4C) under the Ministry of Home Affairs quietly tried to do something almost no government has managed before: switch off an app that doesn't need the internet to work. On July 23, 2026, I4C sent takedown notices to Google, Apple and GitHub, ordering them to pull three offline messaging apps – like BitChat, Briar and Bridgefy – from the Play Store, App Store and GitHub's code repository, respectively, giving a three-hour deadline. The notices followed a period of student-led demonstrations at Jantar Mantar, New Delhi, associated with a group "Cockroach Janata Party," a period that also saw a mobile internet shutdown in parts of central Delhi. When Twitter co-founder Jack Dorsey, who built and open-sourced BitChat, publicised the GitHub notice on X, the episode made international news. Google and Apple got near-identical orders the same night, and telecom operators were reportedly told, and then just as quickly untold, to block the apps at the network level. By July 29, all three apps were still live on both app stores, and BitChat's code was still on GitHub. This incident is worth unpacking carefully, because it sits at the intersection of three things most people care about but rarely see explained together: how this technology actually works, what the law actually allows, and why an app can be "banned" on paper while still working perfectly on your phone.
What makes these apps different
Ordinary apps like WhatsApp or Telegram are centralised: your message travels from your phone to a company's server, and then to the recipient's phone. Block or seize the server, and communication stops. BitChat, Briar and Bridgefy are built differently. They use Bluetooth mesh networking, a system where nearby phones talk directly to each other, and each device also relays messages onwards to phones further away, like a bucket brigade. No message ever touches a central server. Briar adds a further layer by routing traffic over Tor, an anonymity network, when internet access is available, and falls back to Bluetooth or Wi-Fi Direct when it isn't. Bridgefy is tuned for larger crowds, useful during concerts, natural disasters, or protests where thousands of phones are packed into a small area and cellular networks buckle under the load. This design, often called decentralised or peer-to-peer communication, is precisely why these apps are useful during disasters and precisely why they worry law enforcement: they keep working when the internet doesn't, whether that's because a cyclone knocked out cell towers or because the government itself ordered a shutdown.
The legal machinery behind a takedown notice
India's power to block online content mainly comes from Section 69A of the Information Technology Act, 2000, which lets the central government order blocking on grounds like sovereignty, public order or preventing incitement to an offence but only through a defined process set out in the IT (Blocking) Rules, 2009: a designated officer, a review committee, and recorded written reasons. The Supreme Court examined this exact provision in its landmark 2015 ruling, Shreya Singhal v. Union of India. While the judgement is best remembered for striking down the vague "offensive speech" law under Section 66A, it separately upheld Section 69A specifically because it came with procedural guardrails, a reasoned order, an opportunity to be heard, and the possibility of judicial review that stopped it from becoming an unchecked censorship tool. The July 23 notices, however, reportedly leaned on a different lever: Section 79(3)(b) of the IT Act, read with Rule 3(1)(d) of the IT Intermediary Guidelines and Digital Media Ethics Code Rules, 2021. That provision governs when an intermediary loses its legal immunity ("safe harbour") for user content if it fails to act on a government or court order, a mechanism built for content takedowns, not necessarily for pulling an entire app off a store shelf within three hours. Legal commentators have flagged this as significant, since Shreya Singhal itself read down Section 79(3)(b) to require action only pursuant to a court order or a properly authorised government direction, not an informal notice. This isn't the first time a mesh-messaging app has run into this machinery. In 2023, following an I4C request, the government blocked Briar and thirteen other apps in Jammu and Kashmir under Section 69A, citing use, the first known instance of Section 69A being used for a regional block. Briar's developers challenged this in the Delhi High Court; in 2024, the court dismissed the challenge, holding that principles of natural justice can give way in matters of national security.
Why you can't easily switch off a mesh network
Here's the technical wrinkle that made the July order largely symbolic: removing an app from the Play Store stops new downloads, but it does nothing to phones that already have it installed, and it does nothing at all to the Bluetooth radios exchanging messages between those phones. Unlike an internet shutdown, which works by controlling the pipes that all traffic must pass through, a mesh network has no chokepoint, no server to seize, no IP address to blacklist, and no single company to compel.
GitHub, for its part, said it followed its standard process of notifying the account holder and offering an appeal before taking any action, which is one reason BitChat's source code stayed publicly accessible throughout. Within a day, officials reportedly told the companies orally that enforcement wasn't necessary after all, though no public clarification or official document has been released explaining why the notices were issued or withdrawn.
Two legitimate, competing interests
None of this means the government's underlying worry is baseless. Law enforcement agencies genuinely lose visibility when communication moves off networks they can lawfully intercept, and coordination of unlawful assembly or violence is a real concern during volatile protests.
The transparency gap
The single biggest problem with how this played out isn't the underlying concern it's the absence of a public, reasoned order. Under the blocking rules, disclosure is restricted, and courts, including the Supreme Court in Anuradha Bhasin v. Union of India, have said that when access is restricted, reasons must be recorded and, where possible, made available. A three-hour notice, issued and then informally withdrawn without explanation, sits uneasily with that standard. A more durable approach, one that CyberPeace and other digital-rights researchers have called for, would combine clearly identified statutory authority; published (even if redacted) reasoning; proportionality review; and investment in lawful digital forensics, rather than blanket app-store takedowns that decentralised technology is, by design, built to survive.
CyberPeace's policy recommendations
Alongside the legal analysis above, CyberPeace puts forward a ten-point framework for how India should approach decentralised communication technologies going forward, instead of defaulting to blanket takedowns:
- Strengthen transparency in blocking decisions
- Ensure statutory clarity
- Apply legality, necessity and proportionality
- Differentiate technology from misuse
- Invest in advanced investigative capabilities
- Establish a multi-stakeholder advisory mechanism
- Develop a framework for emerging decentralised technologies
- Promote responsible innovation
- Enhance public awareness
- Foster international cooperation
Conclusion
The referred incident illustrates that regulating decentralised technologies requires more than swift takedown notices. As communication networks become increasingly resilient and distributed, effective governance must combine legal certainty, technical realism, transparency, and proportionate enforcement. India's challenge is not simply to regulate emerging technologies but to develop a kind of regulatory framework that safeguards national security and the constitutional values of privacy, free expression, and due process.
Sources
- MediaNama — Bitchat was not the only mesh-messaging app targeted by a government takedown notice
- Outlook Business — Beyond GitHub, Govt Also Directed Google To Take Down Bitchat, Briar And Bridgefy
- The Wire — Government Asks GitHub to Remove Bluetooth Messaging App Bitchat Over Concerns of 'Misuse'
- The Tech Trace (Substack) — The Indian govt's crackdown on Bluetooth-enabled messaging apps that wasn't?
- Bar and Bench — Section 69A IT Act and the expanding architecture of digital censorship in India
- Supreme Court Observer — X relies on 'Shreya Singhal' in arbitrary content-blocking case in Karnataka HC
- LiveLaw — Internet Freedom, Shreya Singhal v Union of India, IT Act, Blocking Rules 2009
- Manupatra — Full text, Shreya Singhal v. Union of India (2015) 5 SCC 1
- Open Magazine — CJP Protests at Jantar Mantar: How Offline Mesh Messaging Apps Powered a Network of Resistance

In Delhi there is a bank branch where a lot of money was stolen from people over the country. This bank branch is where all the money disappeared. The people who did this did not wear masks. Break in at midnight. They just used a passbook a rubber stamp and a form that nobody checked carefully. This is the truth that the people who investigate cybercrime keep finding. The way that cybercriminals get away with the money is not by using a computer it is by using a bank account. The police in Delhi who investigate cybercrime have found that a lot of accounts were opened at bank branches. These accounts were opened using identity documents that were borrowed bought or stolen. Then these accounts were rented out to groups of criminals. One bank branch keeps coming up in complaints. This is not bad luck it is a sign of a bigger problem with how banks check who is opening an account.
These fake accounts, which are called " accounts" are controlled by criminal groups, not the people whose names are on the accounts. These accounts are a part of the cybercrime problem in India. The mistakes that bank branches make which allow these accounts to be opened raise a lot of questions. These questions are about how banks check who is opening an account how they prevent money laundering and how they work with groups to stop cybercrime. The bank accounts are the way that cybercriminals in India get away with the money they steal from people. The cybercrime investigators keep finding bank accounts like the ones at the bank branch, in Delhi, where the money was stolen.
The Anatomy of a Mule Account Network
The pattern is now familiar to investigators. A fraud complaint on the National Cyber Crime Reporting Portal traces a victim's stolen money to a beneficiary account. When police pull the account-opening file, the person named on the KYC documents often denies ever visiting the branch or signing the forms; signature verification frequently shows a mismatch. In one recent Delhi case, a cooperative bank's deputy manager was arrested after a single account he had helped open surfaced in 159 separate cyber fraud complaints from across the country, with transactions worth nearly Rs 68 crore routed through it before detection. Similar investigations have uncovered supply gangs that procure dozens of accounts at a time using POS machines, stacks of ATM cards, and cheque books belonging to different people and rent them out to fraudsters as ready-made conduits for stolen money.
What makes a single branch or a small cluster of accounts significant is what it reveals about entry-point failure. Investigators do not describe these as sophisticated hacking operations; they describe them as verification failures as are accounts opened without the mandatory in-person checks, video KYC, or document authentication that RBI rules require. When 96, or 700, or 8.5 lakh mule accounts are traced back through a handful of branches and intermediaries, the story is not really about the fraudsters at the far end of the chain. It is about the choke point where honest oversight should have stopped the account from ever existing.
Where the KYC Framework Is Breaking Down
The RBI's Know Your Customer Master Direction requires banks to establish customer identity, verify a genuine business relationship, and apply risk-based due diligence before allowing an account to operate. In practice, investigators have repeatedly found accounts opened through complicit or negligent bank staff, business correspondents, and third-party agents who bypass these checks entirely. Analysts note that mule accounts systematically exploit gaps in customer onboarding, KYC verification, transaction monitoring, and dormant-account surveillance, with criminals using forged or stolen identity documents and layering funds across multiple accounts to escape detection. Economically vulnerable individuals who are daily-wage workers, students, the unemployed are frequently paid a small commission to hand over their documents or existing accounts, often without understanding that they could face criminal liability for transactions they never authorised.
This is compounded by a financial-inclusion paradox that regulators themselves acknowledge: India has expanded banking access faster than it has expanded financial and digital literacy, leaving a population that is easy to recruit knowingly or unknowingly into mule networks. The result is a KYC regime that looks robust on paper but is only as strong as its weakest branch-level implementation, and weak implementation has proved trivially easy for organised networks to locate and exploit at scale.
The Regulatory and Institutional Response
RBI: From Static Compliance to Active Detection
The Reserve Bank of India has moved beyond periodic KYC audits toward technology-driven detection. It has directed banks to tighten onboarding controls, strengthen transaction monitoring, and report suspicious activity more proactively, and it has proposed additional safeguards, including limits on aggregate credits into accounts where a satisfactory business relationship has not yet been established. Its most significant intervention is MuleHunter.ai, an AI and machine-learning system built to flag suspected mule accounts from transaction-behaviour patterns rather than static KYC data alone; the platform is already operational across roughly two dozen banks and is being expanded. The RBI Innovation Hub has also begun working directly with the Indian Cyber Crime Coordination Centre (I4C) to share fraud-risk intelligence and coordinate detection in near real time.
FIU-IND and the PMLA Framework
The Prevention of Money Laundering Act, 2002 (PMLA) is the backbone of India's AML architecture. It mandates KYC verification, Customer Due Diligence, record maintenance, and timely reporting of suspicious transactions to the Financial Intelligence Unit–India (FIU-IND). Banks are required to file Suspicious Transaction Reports (STRs) and Cash Transaction Reports with FIU-IND, which in turn analyses financial intelligence and shares it with law enforcement and regulators. On paper, this creates a feedback loop between banks, the RBI, and enforcement agencies; in practice, the sheer volume of mule-linked transactions are hundreds of thousands of accounts flagged nationally has strained the capacity of this reporting chain to generate timely, actionable freezes before funds are withdrawn or converted to cryptocurrency.
The IT Act, CERT-In, and Cyber Enforcement
The Information Technology Act, 2000, together with provisions of the Bharatiya Nyaya Sanhita, provides the criminal-law basis for prosecuting mule account operators, aggregators, and the fraudsters who direct them. CERT-In's role sits slightly upstream of the banking layer: it issues advisories on phishing, fake payment gateways, and compromised digital infrastructure that fraud syndicates use to recruit mule account holders and move money. The Ministry of Home Affairs' I4C coordinates the National Cyber Crime Reporting Portal and the 1930 helpline, which allow victims to report fraud and trigger a limited window for freezing beneficiary accounts. I4C has also issued direct public alerts against illegal payment gateways built on mule accounts, warning citizens not to rent or sell their bank credentials to intermediaries.
The Coordination Gap
None of these institutions is short of legal authority. The gap is operational: banks, the RBI, FIU-IND, state police cyber cells, the CBI, and I4C each hold a piece of the picture, but no single agency has a real-time, end-to-end view of an account from opening to fraud to freeze. A mule account can be flagged by one bank's internal monitoring, reported through a completely different victim's complaint in another state, and investigated by a third jurisdiction's cyber police with each step introducing delay. The Indian Banks' Association has publicly pushed for the RBI to be given clearer power to directly freeze accounts flagged as mule accounts, rather than requiring each bank to act unilaterally or wait for a police request, precisely because this fragmentation lets fraudsters withdraw or launder funds within hours of a transaction.
Policy Recommendations
1. Mandatory video-KYC and biometric re-verification for all new accounts opened through business correspondents and third-party agents, with personal liability for verifying bank officials found complicit.
2. A statutory, RBI-backed mechanism allowing banks to freeze accounts flagged by MuleHunter.ai-type systems or FIU-IND intelligence within hours, rather than only after a formal police complaint.
3. A unified, interoperable case database linking the National Cyber Crime Reporting Portal, FIU-IND's STR system, and state cyber cells, so that an account flagged once is visible to every agency instantly.
4. Stronger due-diligence audits of banking correspondents and cooperative banks, which recur disproportionately in mule account cases relative to their share of total accounts.
5. Public financial-literacy campaigns targeted at the economically vulnerable groups most often recruited as unwitting mule account holders, paired with clear legal guidance distinguishing victims from willing participants.
Conclusion
The branch-level mule account cases surfacing across Delhi and other cities are not isolated policing stories; they are a live audit of India's AML and KYC architecture. The RBI, FIU-IND, CERT-In, and law enforcement agencies each have credible tools and legal mandates like MuleHunter.ai, PMLA reporting, IT Act prosecutions, and I4C's coordination portal chief among them but fraud syndicates continue to outpace the system by exploiting the seams between institutions rather than any single point of failure. Closing that gap requires less new law and more operational integration: faster account freezes, verified accountability at the point of account opening, and a shared, real-time picture of mule networks across every agency involved. Until banks, regulators, and investigators can act as one system rather than several disconnected ones, every dismantled racket will simply be replaced by the next.
References
- https://aninews.in/news/national/general-news/delhi-police-arrests-bank-deputy-manager-in-83776792-crore-mule-account-case-linked-to-159-cyber-fraud-complaints20260610130737/
- https://the420.in/delhi-bank-manager-mule-account-cyber-fraud-case/
- https://www.business-standard.com/finance/news/what-are-mule-accounts-cybercrime-banking-layer-india-fraud-rbi-126062400855_1.html
- https://www.business-standard.com/india-news/centre-freezes-450-000-mule-bank-accounts-used-in-cyber-fraud-schemes-124111200320_1.html
- https://www.medianama.com/2025/04/223-iba-rbi-cyber-fraud-measures-freeze-bank-accounts-cybercrime/
- https://www.deccanherald.com/amp/story/india%2Fcentre-warns-of-illegal-payment-gateways-and-mule-accounts-3252723
- https://www.deccanherald.com/india/over-85-lakh-mule-accounts-in-700-bank-branches-used-by-cyber-criminals-cbi-3604229
- https://website.rbi.org.in/en/web/rbi/-/notifications/master-direction-know-your-customer-kyc-direction-2016-updated-as-on-may-04-2023-lt-span-gt-11566
- https://www.indiacode.nic.in/bitstream/123456789/15402/1/moneylaunderingact2002.pdf
- https://www.indiacode.nic.in/bitstream/123456789/13116/1/it_act_2000_updated.pdf
- https://www.mha.gov.in/en/division_of_mha/cyber-and-information-security-cis-division/Details-about-Indian-Cybercrime-Coordination-Centre-I4C-Scheme
A video of Bollywood actor Salman Khan is being widely circulated on social media, in which he can allegedly be heard saying that he will soon join Asaduddin Owaisi’s party, the All India Majlis-e-Ittehadul Muslimeen (AIMIM). Along with the video, a purported image of Salman Khan with Asaduddin Owaisi is also being shared. Social media users are claiming that Salman Khan is set to join the AIMIM party.
CyberPeace research found the viral claim to be false. Our research revealed that Salman Khan has not made any such statement, and that both the viral video and the accompanying image are AI-generated.
Claim
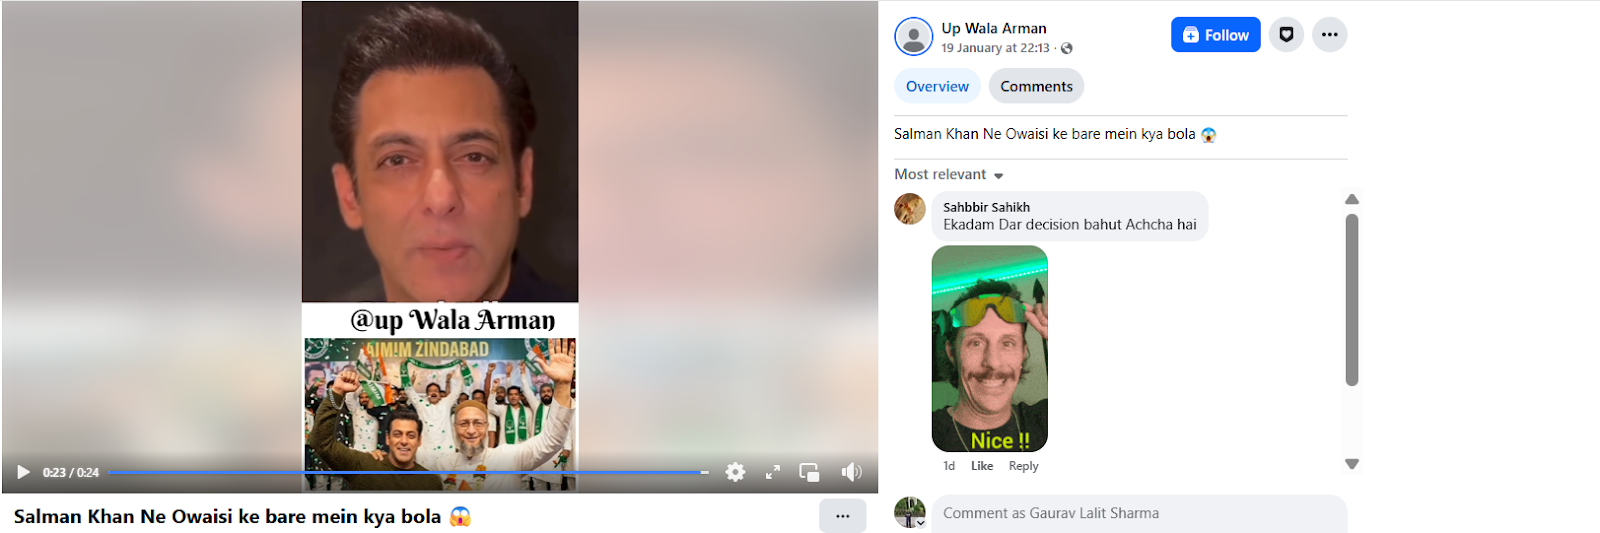
Social media users claim that Salman Khan has announced his decision to join AIMIM.On 19 January 2026, a Facebook user shared the viral video with the caption, “What did Salman say about Owaisi?” In the video, Salman Khan can allegedly be heard saying that he is going to join Owaisi’s party. (The link to the post, its archived version, and screenshots are available.)
Fact Check:
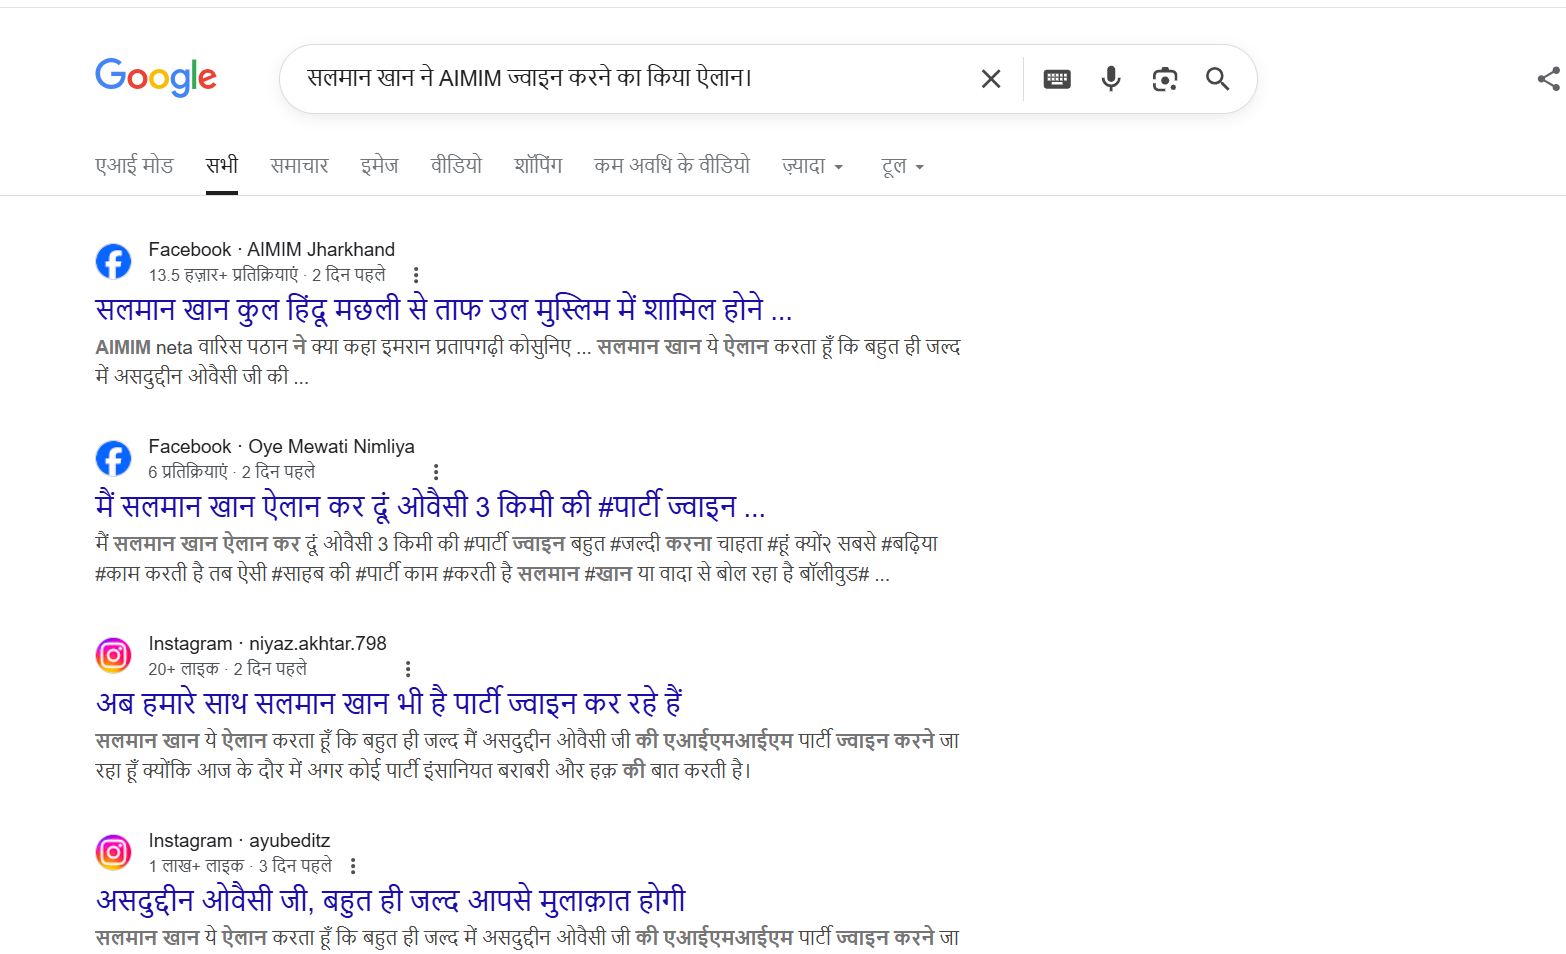
To verify the claim, we first searched Google using relevant keywords. However, no credible or reliable media reports were found supporting the claim that Salman Khan is joining AIMIM.
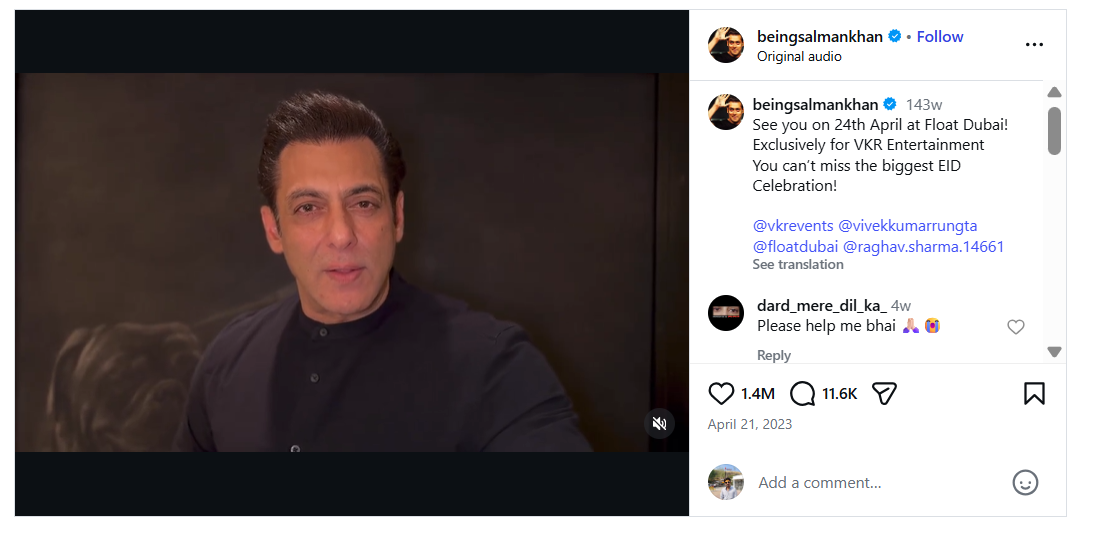
In the next step of verification, we extracted key frames from the viral video and conducted a reverse image search using Google Lens. This led us to a video posted on Salman Khan’s official Instagram account on 21 April 2023. In the original video, Salman Khan is seen talking about an event scheduled to take place in Dubai. A careful review of the full video confirmed that no statement related to AIMIM or Asaduddin Owaisi is made.
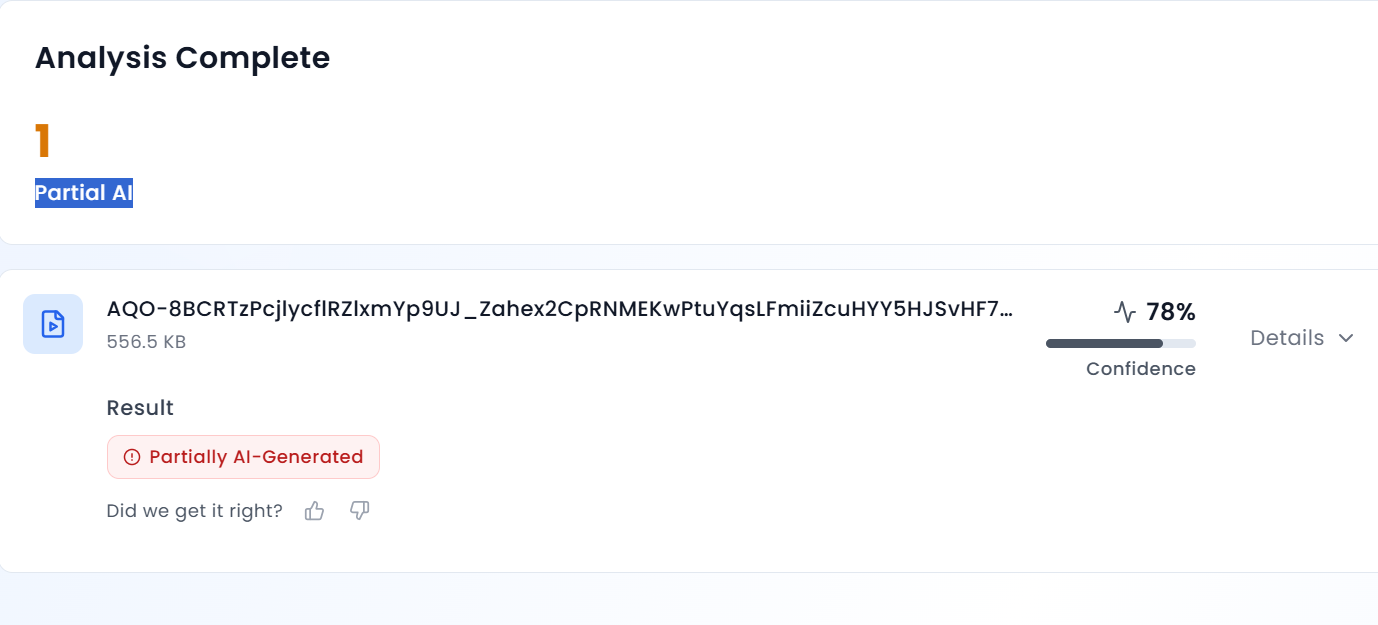
Further analysis of the viral clip revealed that Salman Khan’s voice sounds unnatural and robotic. To verify this, we scanned the video using AURGIN AI, an AI-generated content detection tool. According to the tool’s analysis, the viral video was generated using artificial intelligence.
Conclusion
Salman Khan has not announced that he is joining the AIMIM party. The viral video and the image circulating on social media are AI-generated and manipulated.
