
#FactCheck - A misleading video falsely shows Former Prime Minister of India Pandit Jawaharlal Nehru admitting he had no role in India's independence
Executive Summary:
A misleading video has been widely shared online, falsely portraying Pandit Jawaharlal Nehru stating that he was not involved in the Indian independence struggle and he even opposed it. The video is a manipulated excerpt from Pandit Nehru’s final major interview in 1964 with American TV host Arnold Mich. The original footage available on India’s state broadcaster Prasar Bharati’s YouTube channel shows Pandit Nehru discussing about Muhammad Ali Jinnah, stating that Jinnah did not participate in the independence movement and opposed it. The viral video falsely edits Pandit Nehru’s comments to create a false narrative, which has been debunked upon reviewing the full, unedited interview.

Claims:
In the viral video, Pandit Jawaharlal Nehru states that he was not involved in the fight for Indian independence and even opposed it.


Fact check:
Upon receiving the posts, we thoroughly checked the video and then we divided the video into keyframes using the inVid tool. We reverse-searched one of the frames of the video. We found a video uploaded by Prasar Bharati Archives official YouTube channel on 14 May 2019.

The description of the video reads, “Full video recording of what was perhaps Pandit Jawaharlal Nehru's last significant interview to American TV Host Arnold Mich Jawaharlal Nehru's last TV Interview - May 1964e his death. Another book by Chandrika Prasad provides a date of 18th May 1964 when the interview was aired in New York, this is barely a few days before the death of Pandit Nehru on 27th May 1964.”
On reviewing the full video, we found that the viral clip of Pandit Nehru runs from 14:50 to 15:45. In this portion, Pandit Nehru is speaking about Muhammad Ali Jinnah, a key leader of the Muslim League.
At the timestamp 14:34, the American TV interviewer Arnold Mich says, “You and Mr. Gandhi and Mr. Jinnah, you were all involved at that point of Independence and then partition in the fight for Independence of India from the British domination.” Pandit Nehru replied, “Mr. Jinnah was not involved in the fight for independence at all. In fact, he opposed it. Muslim League was started in about 1911 I think. It was started really by the British encouraged by them so as to create factions, they did succeed to some extent. And ultimately there came the partition.”
Upon thoroughly analyzing we found that the viral video is an edited version of the real video to misrepresent the actual context of the video.
We also found the same interview uploaded on a Facebook page named Nehru Centre for Social Research on 1 December 2021.

Hence, the viral claim video is misleading and fake.
Hence, the viral video is fake and misleading and netizens must be careful while believing in such an edited video.
Conclusion:
In conclusion, the viral video claiming that Pandit Jawaharlal Nehru stated that he was not involved in the Indian independence struggle is found to be falsely edited. The original footage reveals that Pandit Nehru was referring to Muhammad Ali Jinnah's participation in the struggle, not his own. This explanation debunks the false story conveyed by the manipulated video.
- Claim: Pandit Jawaharlal Nehru stated that he was not involved in the struggle for Indian independence and even he opposed it.
- Claimed on: YouTube, LinkedIn, Facebook, X (Formerly known as Twitter)
- Fact Check: Fake & Misleading

Related Blogs

Executive Summary:
A viral picture on social media showing UK police officers bowing to a group of social media leads to debates and discussions. The investigation by CyberPeace Research team found that the image is AI generated. The viral claim is false and misleading.

Claims:
A viral image on social media depicting that UK police officers bowing to a group of Muslim people on the street.


Fact Check:
The reverse image search was conducted on the viral image. It did not lead to any credible news resource or original posts that acknowledged the authenticity of the image. In the image analysis, we have found the number of anomalies that are usually found in AI generated images such as the uniform and facial expressions of the police officers image. The other anomalies such as the shadows and reflections on the officers' uniforms did not match the lighting of the scene and the facial features of the individuals in the image appeared unnaturally smooth and lacked the detail expected in real photographs.

We then analysed the image using an AI detection tool named True Media. The tools indicated that the image was highly likely to have been generated by AI.

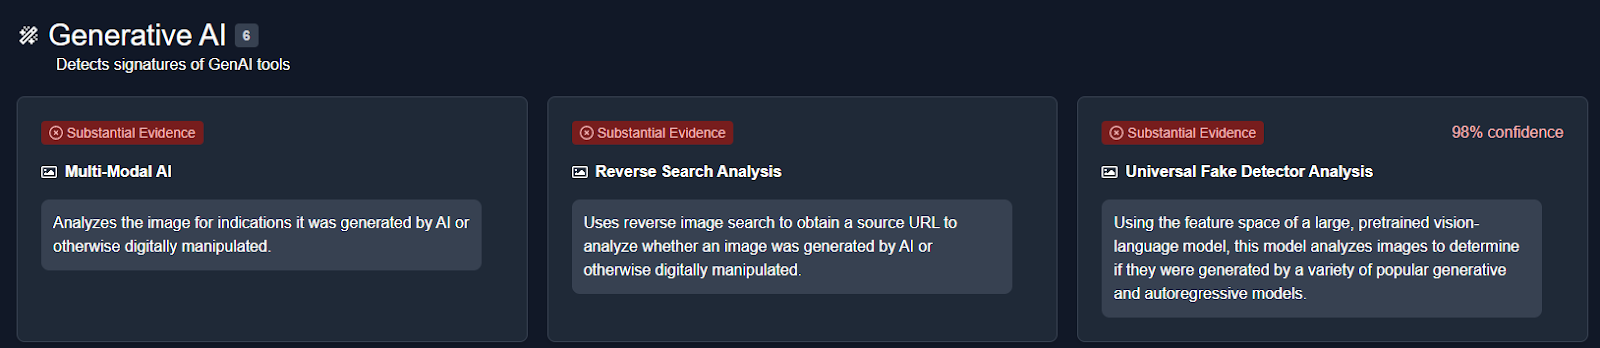

We also checked official UK police channels and news outlets for any records or reports of such an event. No credible sources reported or documented any instance of UK police officers bowing to a group of Muslims, further confirming that the image is not based on a real event.
Conclusion:
The viral image of UK police officers bowing to a group of Muslims is AI-generated. CyberPeace Research Team confirms that the picture was artificially created, and the viral claim is misleading and false.
- Claim: UK police officers were photographed bowing to a group of Muslims.
- Claimed on: X, Website
- Fact Check: Fake & Misleading
Somewhere in a compliance meeting right now, someone is saying "we have eighteen months, we're fine." That sentence is doing the same thing a snooze button does at 6 a.m.: technically buying time, while quietly making the actual wake up call worse. India's data protection law just started its countdown, and the 18 months everyone keeps citing is not a grace period to procrastinate through. It is closer to a runway before takeoff. Runways exist for one purpose: building up speed until the plane has no choice but to leave the ground. Standing still on one is not a strategy.
What actually got notified, and when
On 13 November 2025, the Ministry of Electronics and Information Technology notified the Digital Personal Data Protection Rules, 2025, giving operational shape to the Digital Personal Data Protection Act that Parliament had passed back in August 2023. Alongside the Rules themselves, MeitY issued a separate Enforcement Notification setting out exactly when different provisions kick in, and a further notification establishing the Data Protection Board of India, headquartered in the National Capital Region with four members. The final Rules followed a genuinely deliberative process, MeitY had floated draft Rules in January 2025 for public consultation and received 6,915 individual inputs from startups, industry bodies, civil society groups, and citizens before finalising the version now in force. The headline structural decision, and the one causing the most confusion in boardrooms, is that the Rules do not commence all at once. They commence in three distinct phases spread across eighteen months, and different obligations become legally binding at each stage.
The phased timeline, laid out plainly
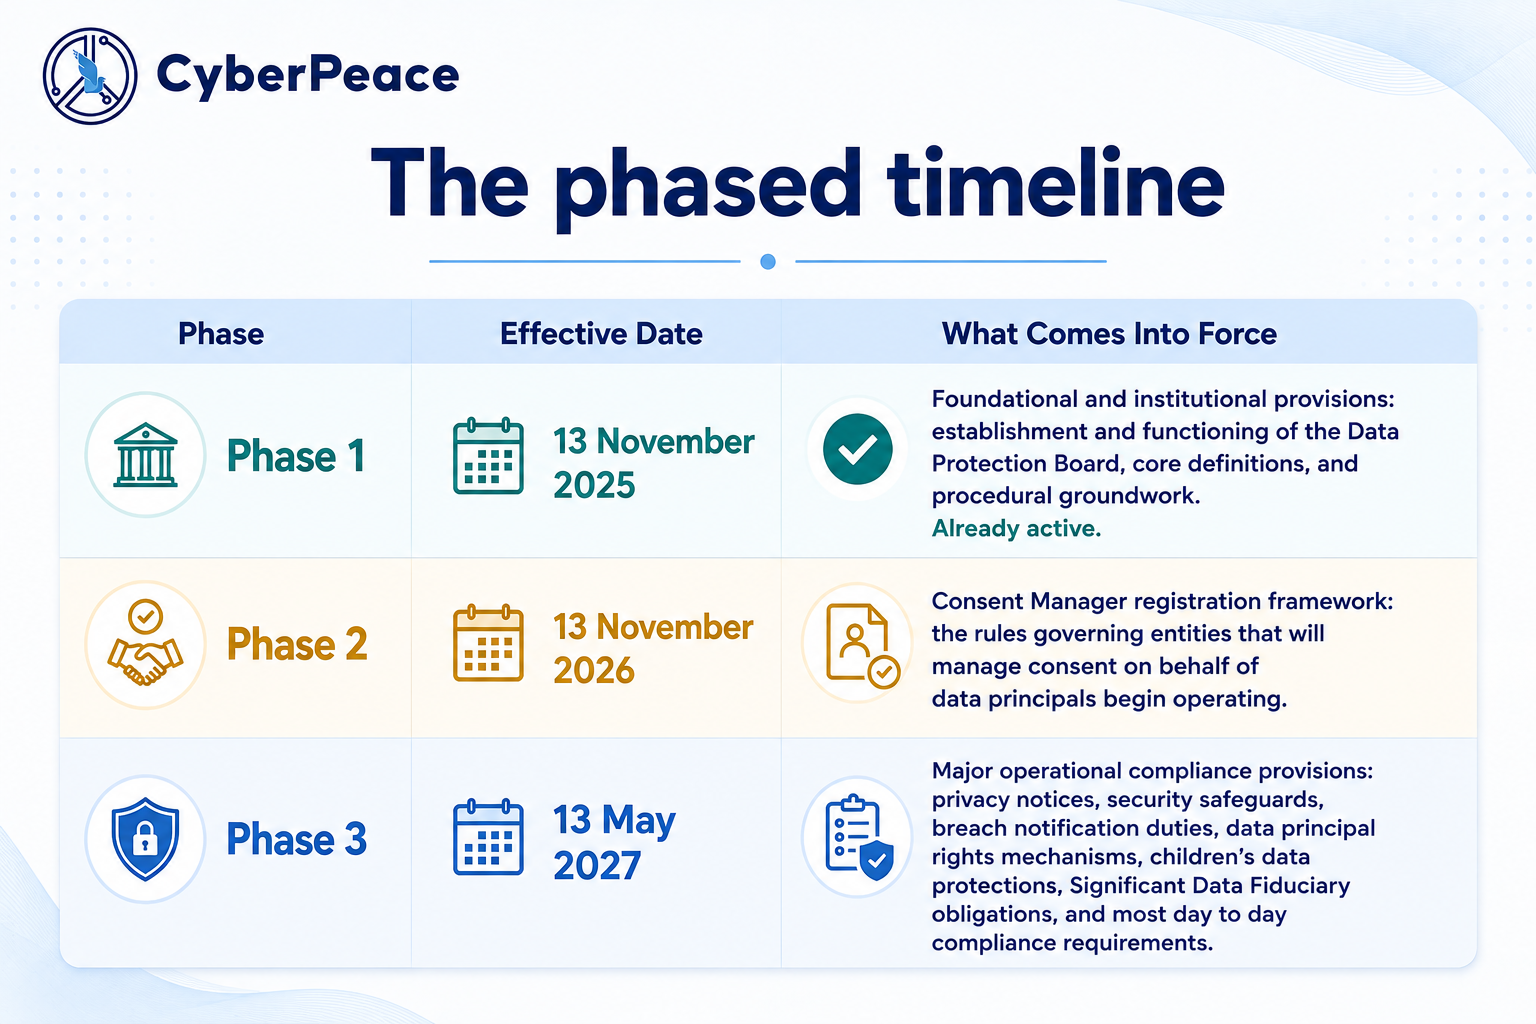
That third date, 13 May 2027, is the one that matters most for the vast majority of organisations, since it is where the bulk of actual operational obligations, the parts that touch product design, customer facing notices, and breach response, become enforceable. Legal commentary tracking the rollout has been consistent that this is described as a hard deadline with no grace period expected once it arrives, since the Data Protection Board is already operational and can begin receiving complaints well before Phase 3 obligations formally take effect.
Why "later" is a genuinely expensive plan
The financial stakes attached to Phase 3 non-compliance are not modest. The Schedule to the DPDP Act sets fixed penalty ceilings rather than turnover linked fines, which sounds gentler than Europe's GDPR model until you look at the actual numbers. Failure to implement reasonable security safeguards that results in a data breach can draw a penalty of up to 250 crore rupees per instance, the single highest tier in the Schedule. Failing to notify the Board or affected individuals after a breach occurs can draw up to 200 crore rupees, as can non-compliance with the Act's specific protections for children's data. Because these are assessed per instance rather than as a single capped exposure, a single incident that trips more than one obligation, say, inadequate safeguards that also delay breach notification, can compound into penalty exposure running into hundreds of crores from one event. All penalties collected go to the Consolidated Fund of India rather than to affected individuals directly, meaning the deterrent is aimed squarely at organisational behaviour, not compensation.
The part everyone keeps underestimating: this is not just a legal department problem
Perhaps the most consequential shift buried inside the DPDP framework is who actually has to own it. Reading the Rules as a checklist for the legal or privacy team alone misses how far the obligations actually reach. Building a compliant consent lifecycle touches product design. Security safeguards touch cybersecurity and IT infrastructure directly. Retention and deletion logic touches data governance and engineering. Third party risk review touches procurement. Breach preparedness touches internal audit and incident response. And increasingly, as organisations deploy AI systems that process personal data, AI governance enters the picture too, since a model trained or fine tuned on personal data inherits the same DPDP obligations as any other processing activity.
That cross functional reality is where most readiness programmes currently fall short. Treating DPDP compliance as a documentation exercise, updating a privacy policy PDF and calling it done, produces the appearance of compliance without the operational substance a Data Protection Board investigation would actually test. A breach response plan that exists only on paper and has never been rehearsed will not hold up against the 72 hour data principal notification window the Rules impose once Phase 3 lands. A consent mechanism bolted onto a website without corresponding backend logic to honour withdrawal requests will not satisfy an actual audit.
What a serious readiness posture looks like right now
Organisations that are ahead of this curve are already treating the eighteen month window as three overlapping workstreams rather than one deadline to hit at the end.
- The first is discovery: mapping what personal data exists, where it flows, who owns each system that touches it, and why it is collected in the first place, since compliance is structurally impossible without first knowing what you are protecting. This stage typically surfaces uncomfortable findings, shadow data sets nobody formally owns, vendor integrations nobody fully mapped, legacy systems still holding data well past any reasonable retention justification.
- The second is build: standing up the actual mechanisms, consent flows that can genuinely honour a withdrawal request end to end, rights request handling that does not depend on a single overworked employee checking an inbox, retention and deletion logic wired into the systems themselves rather than described only in a policy document, and security controls proportionate to the sensitivity of what is being protected.
- The third is proof: generating the internal evidence, audit trails, documented decisions, tested response procedures, that demonstrates governance was real rather than retrofitted after the fact. A Data Protection Board investigation, when it eventually happens, will not be satisfied by a well written policy; it will look for evidence that the policy was actually operational.
The actual question worth asking
The right question was never "when does DPDP become enforceable." Phase 1 already answered that; the law is live, and the Data Protection Board already exists and can act. The better question, the one worth taking into any leadership review between now and May 2027, is simpler and considerably less comfortable: will the organisation actually be ready when each phase's obligations become operational, or will readiness be assembled in a scramble once the deadline stops being theoretical. 18 months sounds long right up until the week it does not, and by the time Phase 3 lands, "we'll get to it" will no longer be a sentence any organisation gets to finish.
References
- Ministry of Electronics and Information Technology, Digital Personal Data Protection Rules, 2025, notified 13 November 2025. Press Information Bureau, "Digital Personal Data Protection Rules, 2025 Notified," 14 November 2025. https://static.pib.gov.in/WriteReadData/specificdocs/documents/2025/nov/doc20251117695301.pdf
- Shardul Amarchand Mangaldas & Co, "Enforcement of the DPDP Act and notification of the DPDP rules." https://www.amsshardul.com/insight/enforcement-of-the-dpdp-act-and-notification-of-the-dpdp-rules/
- S&R Associates, "India's Digital Personal Data Protection Regime Takes Effect." https://www.snrlaw.in/indias-digital-personal-data-protection-regime-takes-effect/
- Khurana & Khurana, "MeitY Notifies Rules Operationalising The DPDP Framework." https://www.khuranaandkhurana.com/update-meity-notifies-rules-operationalising-the-dpdp-framework-in-india
- Exchange4media, "DPDP Act 2025: Penalties for violations can reach Rs 250 crore." https://www.exchange4media.com/digital-news/dpdp-act-2025-penalties-for-confirmed-violations-can-reach-rs-250-crore-149360.html
- Seclore, "DPDP Rules 2025: India's Complete Compliance Guide." https://www.seclore.com/fundamentals/dpdp-rules-2025-compliance-guide/

Introduction
Sexual Offences against children have recently come under scrutiny after the decision of the Madras High Court which has ruled that watching and downloading child sexual porn is an inchoate crime. In response, the Supreme Court, on 23 September 2024, ruled that Section 15 of the POCSO and Section 67B of the IT Act penalise any form of use of child pornography, including storing and watching such pornographic content. Along with this, the Supreme Court has further recommended replacing the term “Child Pornography” which it said acts as a misnomer and does not capture the full extent of the crime, with a more inclusive term “Child Sexual Exploitative and Abuse Material” (CESAM). This term would more accurately reflect the reality that these images and videos are not merely pornographic but are records of incidents, where a child has either been sexually exploited and abused or where any abuse of children has been portrayed through any self-generated visual depiction.
Intermediaries cannot claim exemption from Liability U/S 79
Previously, intermediaries claimed safe harbour by only complying with the requirements stipulated under the MOU. As per the decision of the SC, now, an intermediary cannot claim exemption from the liability under Section 79 of the IT Act for any third-party information, data, or communication link made available or hosted by it unless due diligence is conducted by it and compliance is made of these provisions of the POCSO Act. This is as per the provisions of Sections 19 and 20 of the POCSO read with Rule 11 of the POCSO Rules which have a mandatory nature.
The due diligence under section 79 of the IT Act includes the removal of child pornographic content and immediate reporting of such content to the concerned police units in the manner specified under the POCSO Act and the Rules. In this way, the Supreme Court has broadened the Interpretation and scope of the ‘Due Diligence’ obligation under section 79 of the IT Act. It was also stated that is to be duly noted that merely because an intermediary complies with the IT Act, will not absolve it of any liability under the POCSO. This is unless it duly complies with the requirements and procedure set out under it, particularly Section 20 of the POCSO Act and Rule 11 of the POCSO Rules.
Bar on Judicial Use of the term ‘Child Porn’
Supreme Court found that the term child pornography can be trivialised as pornography is often seen as a consensual act between adults. Supreme Court emphasised using the term Child Sexual Exploitative and Abuse Material (CESAM) as it would emphasise the exploitation of children highlight the criminality of the act and shift the focus to a more robust framework to counter these crimes. The Supreme Court also stated that the Union of India should consider amending the POCSO Act to replace the "child pornography" term with "child sexual exploitative and abuse material" (CSEAM). This would reflect more accurately on the reality of such offences. Supreme Court also directed that the term "child pornography" shall not be used in any judicial order or judgment, and instead, the term "CSEAM" should be endorsed.
Curbing CSEAM Content on Social Media Platforms
Social Media Intermediaries and Expert Organisations play an important role in curbing CESAM content. Per the directions of the Apex Court, a need to impart positive age-appropriate sex education to prevent youth from engaging in harmful sexual behaviours, including the distribution, and viewing of CSEAM is important and all stakeholders must engage in proactive measures to counter these offences which are under the umbrella of CSEAM. This should entail promoting age-appropriated and lawful content on social media platforms and social media platforms to ensure compliance with applicable provisions.
Conclusion
In light of the Supreme Court’s landmark ruling, it is imperative to acknowledge the pressing necessity of establishing a safer online environment that shields children from exploitation. The shift towards using "Child Sexual Exploitative and Abuse Material" (CSEAM) emphasizes the severity of the crime and the need for a vigilant response. The social media intermediaries must respect their commitment to report and remove exploitive content and must ensure compliance with POCSO and IT regulations. Furthermore, comprehensive, age-appropriate sex education can also be used as a preventive measure, educating young people about the moral and legal ramifications of sexual offences, encouraging respect and awareness and ensuring safer cyberspace.
References
- https://www.scconline.com/blog/post/2024/09/23/storing-watching-child-pornography-crime-supreme-court-pocso-it-act/#:~:text=Supreme%20Court%3A%20The%20bench%20of,watching%20of%20such%20pornographic%20content
- https://timesofindia.indiatimes.com/india/supreme-court-viewing-child-porn-is-offence-under-pocso-it-acts/articleshow/113613572.cms
- https://bwlegalworld.com/article/dont-use-term-child-pornography-says-sc-urges-parliament-to-amend-pocso-act-534053
- https://indianexpress.com/article/india/child-pornography-law-pocso-it-supreme-court-9583376/

