
#Fact Check-Misleading Newspaper from Kerala stating ban on paper currency
Executive Summary:
Recently, our team came across a widely circulated post on X (formerly Twitter), claiming that the Indian government would abolish paper currency from February 1 and transition entirely to digital money. The post, designed to resemble an official government notice, cited the absence of advertisements in Kerala newspapers as supposed evidence—an assertion that lacked any substantive basis

Claim:
The Indian government will ban paper currency from February 1, 2025, and adopt digital money as the sole legal tender to fight black money.

Fact Check:
The claim that the Indian government will ban paper currency and transition entirely to digital money from February 1 is completely baseless and lacks any credible foundation. Neither the government nor the Reserve Bank of India (RBI) has made any official announcement supporting this assertion.
Furthermore, the supposed evidence—the absence of specific advertisements in Kerala newspapers—has been misinterpreted and holds no connection to any policy decisions regarding currency
During our research, we found that this was the prediction of what the newspaper from the year 2050 would look like and was not a statement that the notes will be banned and will be shifted to digital currency.
Such a massive change would necessitate clear communication to the public, major infrastructure improvements, and precise policy announcements which have not happened. This false rumor has widely spread on social media without even a shred of evidence from its source, which has been unreliable and is hence completely false.
We also found a clip from a news channel to support our research by asianetnews on Instagram.

We found that the event will be held in Jain Deemed-to-be University, Kochi from 25th January to 1st February. After this advertisement went viral and people began criticizing it, the director of "The Summit of Future 2025" apologized for this confusion. According to him, it was a fictional future news story with a disclaimer, which was misread by some of its readers.
The X handle of Summit of Future 2025 also posted a video of the official statement from Dr Tom.

Conclusion:
The claim that the Indian government will discontinue paper currency by February 1 and resort to full digital money is entirely false. There's no government announcement nor any evidence to support it. We would like to urge everyone to refer to standard sources for accurate information and be aware to avoid misinformation online.
- Claim: India to ban paper currency from February 1, switching to digital money.
- Claimed On: X (Formerly Known As Twitter)
- Fact Check: False and Misleading

Related Blogs
Executive Summary:
A video is rapidly circulating on social media following claims that Iran’s national security chief Ali Larijani was killed in an Israeli airstrike. The viral clip is being shared with the assertion that it shows the moment Israel launched a powerful attack on Iran to eliminate Larijani, allegedly shaking the ground due to the intensity of the strike However, research by CyberPeace has found the claim to be misleading. The viral video is AI-generated and has no connection to real-world events.
Claim:
Social media users have shared the video with alarming captions. One such post by Deepak Sharma reads:
“WAR UPDATE… Iran is in its final phase… Israel is striking selectively… This attack will leave you shocked… Iran’s national security chief Ali Larijani has been killed in this attack… The intensity of the strike shook the Iranian الأرض.
Post links:
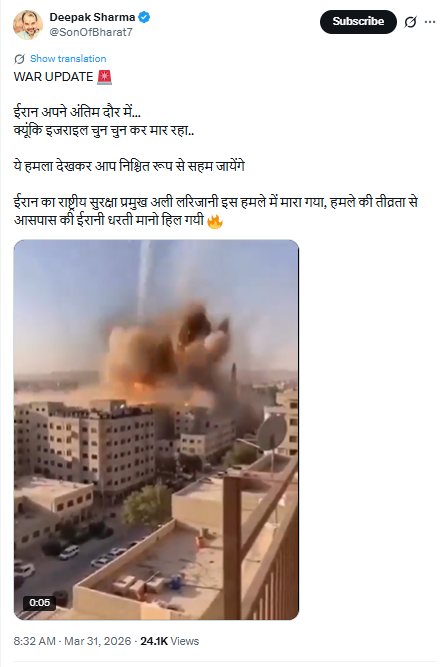
Similar videos were also shared by other users:
- urabh_raj3026/status/2038834832869032026
- https://x.com/ibmindia20/status/2038938020154597447
- https://x.com/Saurabh_raj3026/status/2038834832869032026
Fact Check
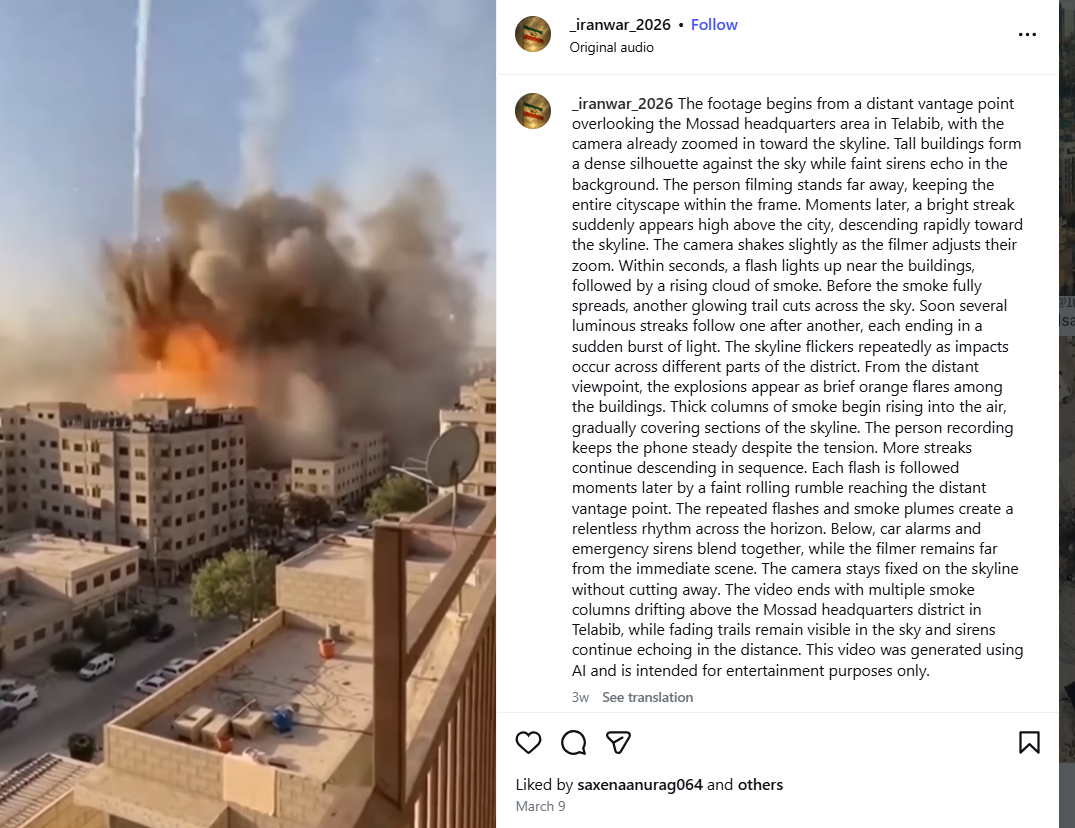
To verify the claim, we extracted keyframes from the viral video and conducted a reverse image search. During this process, we found the same video on Instagram, uploaded on March 9, 2026, by the account “_iranwar_2026” without any descriptive caption.
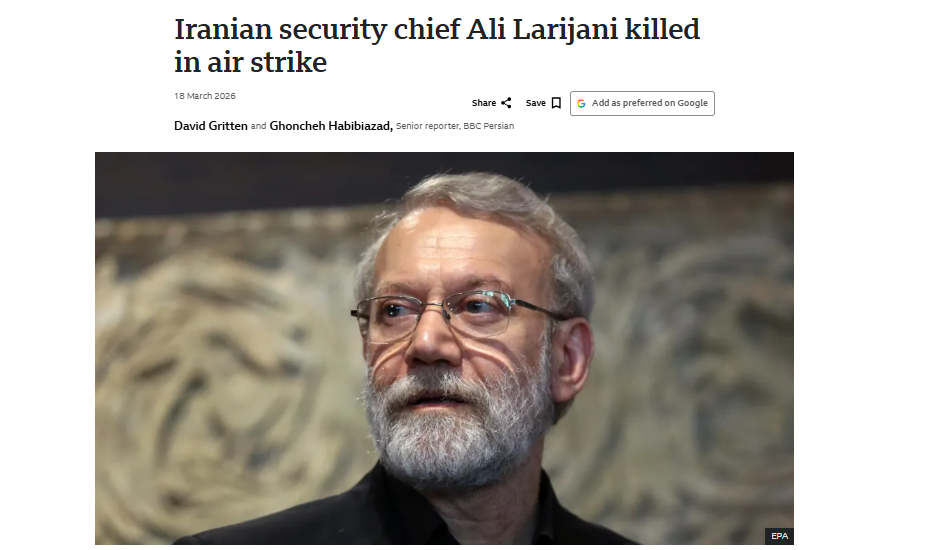
According to a BBC report, Ali Larijani died on March 17 in an Israeli strike. This establishes that the viral video predates the reported incident, making the claim factually inconsistent. Further examination of the Instagram account revealed that it frequently shares pro-Iran content, including gaming visuals and AI-generated clips, raising doubts about the authenticity of the video.
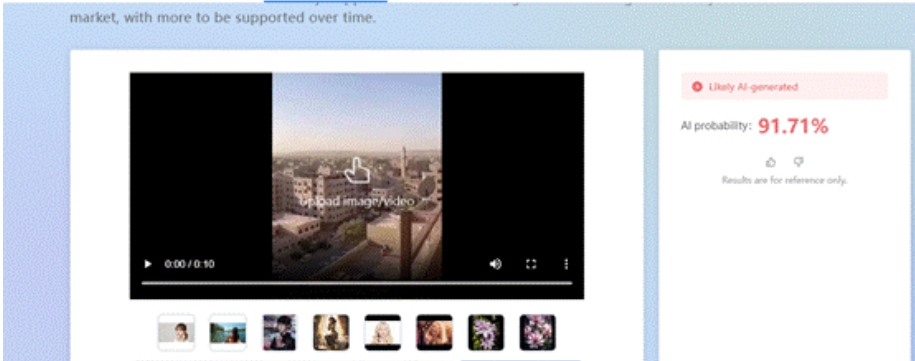
To strengthen the verification, we analyzed the viral clip using the AI detection tool “Zhuque AI Detection Assistant.” The results indicated a 91.71% probability that the video is AI-generated, confirming that it is not real footage.
Conclusion
The viral claim linking the video to an Israeli airstrike that allegedly killed Ali Larijani is misleading and factually incorrect. Multiple layers of verification show that the video existed online before the reported incident, ruling out any direct connection. Additionally, AI detection analysis strongly suggests that the video is artificially generated. The source account’s pattern of sharing AI and gaming-related content further weakens the credibility of the claim. There is no verified evidence to support that the viral clip depicts a real attack or any event related to Larijani’s death. Instead, the video appears to be a digitally created visual circulated without context to amplify misinformation.
Introduction
In today’s digital world, data has emerged as the new currency that influences global politics, markets, and societies. Companies, governments, and tech behemoths aim to control data because it accords them influence and power. However, a fundamental challenge brought about by this increased reliance on data is how to strike a balance between privacy protection and innovation and utility.
In recognition of these dangers, more than 200 Nobel laureates, scientists, and world leaders have recently signed the Global Call for AI Red Lines. Governments are urged by this initiative to create legally binding international regulations on artificial intelligence by 2026. Its goal is to stop AI from going beyond moral and security bounds, particularly in areas like political manipulation, mass surveillance, cyberattacks, and dangers to democratic institutions.
One way to address the threat to privacy is through pseudonymization, which makes it possible to use data valuable for research and innovation by substituting personal identifiers for artificial ones. Pseudonymization thus directly advances the AI Red Lines initiative's mission of facilitating technological advancement while lowering the risks of data misuse and privacy violations.
The Red Lines of AI: Why do they matter?
The Global Call for AI Red Lines initiative represents a collective attempt to impose precaution before catastrophe, which was done with the objective of recognising the Red Lines in the use of AI tools. Thus, anything that unites the risks of using AI is due to the absence of global safeguards. Some of these Red Lines can be understood as;
- Cybersecurity breaches in the form of exposure of financial and personal data due to AI-driven hacking and surveillance.
- Occurrence of privacy invasions due to endless tracking.
- Generative AI can also help to create realistic fake content, undermining the trust of public discourses, leading to misinformation.
- Algorithmic amplification of polarising content can also threaten civic stability, leading to a demographic disruption.
Legal Frameworks and Regulatory Landscape
The regulations of Artificial Intelligence stand fragmented across jurisdictions, leaving significant loopholes aside. Some of the frameworks already provide partial guidance. The European Union’s Artificial Intelligence Act 2024 bans “unacceptable” AI practices, whereas the US-China Agreement also ensures that nuclear weapons remain under human, not machine-controlled. The UN General Assembly has adopted resolutions urging safe and ethical AI usage, with a binding and elusive global treaty.
On the front of data protection, the General Data Protection Regulations (GDPR) of EU offers a clear definition of Pseudonymisation under Article 4(5). It also describes a process where personal data is altered in a way that it cannot be attributed to an individual without additional information, which must be stored securely and separately. Importantly, pseudonymised data still qualifies as “personal data” under GDPR. However, India’s Digital Personal Data Protection Act (DPDP) 2023 adopts a similar stance. It does not explicitly define pseudonymisation in broad terms, such as “personal data” by including potentially reversible identifiers. According to Section 8(4) of the Act, companies are meant to adopt appropriate technical or organisational measures. International bodies and conventions like the OECD Principles on AI or the Council of Europe Convention 108+ emphasize accountability, transparency, and data minimisation. Collectively, these instruments point towards pseudonymization as a best practice, though interpretations of its scope differ.
Strategies for Corporate Implementation
For a company, pseudonymisation is not just about compliance, it is also a practical solution that offers measurable benefits. By pseudonymising data, businesses can get benefits, such as;
- Enhancing Privacy protection by masking identifiers like names or IDs by reducing the impact of data breaches.
- Preserving Data Utility, unlike having a full anonymisation, pseudonymisation also retains patterns that are essential for analytical innovation.
- Facilitating data sharing can allow organizations to collaborate with their partners and researchers while maintaining proper trust.
According to these benefits, competitive advantages get translated to clauses where customers find it more likely to trust organizations that prioritise data protection, while pseudonymisation further enables the firms to engage in cross-border collaboration without violating local data laws.
Balancing Privacy Rights and Data Utility
Balancing is a central dilemma; on one side lies the case of necessity over data utility, where companies, researchers and governments rely on large datasets to enhance the scale of AI innovation. On the other hand lies the question of the right to privacy, which is a non-negotiable principle protected under the international human rights law.
Pseudonymisation offers a practical compromise by enabling the use of sensitive data while reducing the privacy risks. Taking examples of different domains, such as healthcare, it allows the researchers to work with patient information without exposing identities, whereas in finance, it supports fraud detection without revealing the customer details.
Conclusion
The rapid rise of artificial intelligence has led to the outpacing of regulations, raising urgent questions related to safety, fairness and accountability. The global call for recognising the AI red lines is a bold step that looks in the direction of setting universal boundaries. Yet, alongside the remaining global treaties, practical safeguards are also needed. Pseudonymisation exemplifies such a safeguard, which is legally recognised under the GDPR and increasingly relevant in India’s DPDP Act. It balances the twin imperatives of privacy, protection, and data utility. For organizations, adopting pseudonymisation is not only about ensuring regulatory compliance, rather, it is also about building trust, ensuring resilience, and aligning with the broader ethical responsibilities in this digital age. As the future of AI is debatable, the guiding principles also need to be clear. By embedding techniques for preserving privacy, like pseudonymisation, into AI systems, we can take a significant step towards developing a sustainable, ethical and innovation-driven digital ecosystem.
References
https://www.techaheadcorp.com/blog/shadow-ai-the-risks-of-unregulated-ai-usage-in-enterprises/
https://planetmainframe.com/2024/11/the-risks-of-unregulated-ai-what-to-know/
https://cepr.org/voxeu/columns/dangers-unregulated-artificial-intelligence
https://www.forbes.com/sites/bernardmarr/2023/06/02/the-15-biggest-risks-of-artificial-intelligence/
Introduction
Over the last few years, several public data breaches in Venezuela have revealed a lack of cohesion and progress in its data privacy system and left many people susceptible to fraud, identity theft and long-term harm via the internet. It is clear from these data breaches that when organizations fail to adequately protect their data, both through cybersecurity failures and weak legal protections, they can lead to problems throughout an entire system through which all individuals in the system could potentially suffer.
Among the more notable breaches are the Movistar Venezuela data breach from 2025 and the Cashea App data leak from earlier this year. Each of these examples demonstrates to some extent how the absence of an adequate privacy regulatory scheme can worsen the results of a data breach.
The Movistar Breach: A Regulatory Warning (2025)
Venezuelan digital rights group VE Sin Filtro published a report late in April 2025, which found a database revealed to have been opened onto the internet containing personal information belonging to over 3.2 million Movistar customers. The initial breach contained personal, and confidential, data of Venezuelan citizens such as national identification numbers, full names, city of residence, and phone numbers which could have been exploited to commit identity theft, SIM-swap fraud, and targeted scams.
One significant issue with this situation was that Movistar failed to disclose the breach publicly or contact impacted customers at the time of the disclosure. As a result, there appears to be a significant gap in Sanctions / Other Means of Enforcing Security Countermeasures Laws. Since there are numerous countries that enforce GDPR-style regulations and as such, this matter should lead to a complete investigation and possible fines against those responsible but in Venezuela there is still a lack of accountability.
Cashea App Leak: A 2026 Data Shock
A second alleged data breach came to light in February of 2026. It involved a Venezuelan buy-now-pay-later (BNPL) fintech called Cashea App, which is typically heavily utilized domestically. Reports have circulated that threat actors have been offering a database, believed to hold more than 79 million transaction records. This is more than double the size and sensitivity of the data involved in the Movistar Breach.
According to reports, the leaked data included:
- Bank account details and payment methods
- Merchant profiles and internal business identifiers
- Detailed transaction histories with names, national ID numbers, timestamps, and installment data
This level of exposure goes far beyond basic identifiers. Financial transaction histories combined with personal identifiers enable sophisticated fraud, targeted social engineering, and long-term misuse of financial identities. As with the Movistar breach, no official acknowledgment or notification was issued by Cashea at the time of reporting, again underscoring Venezuela’s weak enforcement environment.
Why These Breaches Matter: The Legal Dimension
The incidents show us that there is a bigger problem with the way Venezuela has set up its framework for protecting data. For instance, the Venezuelan Constitution recognises the principles of data protection and privacy; however, these rights only exist in a theoretical manner; they lack implementing legislation, procedural clarity, and institutional enforcement.
Constitutional Basis of Data Protection
The Supreme Tribunal of Justice (TSJ) stated the core principles for protecting data are found in the Venezuelan Constitution. After the TSJ issued its 2011 ruling, Article 28 of the Venezuelan Constitution gives individuals the right to know what data the state has about them, how the state uses that data, and to correct or delete any harmful data. Article 60 of the Venezuelan Constitution protects individuals' privacy and restricts excessive data collection by the state.
The Constitutional Chamber also put into place additional guiding principles for how to protect personal data, including:
- The data subject must give prior informed and revocable consent.
- The purpose for which the data is collected must be specified and only the minimum amount of information necessary can be collected.
- The data collected must be accurate and of good quality.
- There are confidentiality obligations for third parties regarding the use of the data.
- It is the government's responsibility to put into place procedures and mechanisms to monitor compliance with the data protection laws.
- There are civil, criminal and administrative liabilities for individuals and legal entities that violate the data protection laws.
But, in a civil law country, when courts make rulings, they usually are persuasive only as opposed to being legally binding, and even constitutional rulings cannot be implemented until enabling legislation is passed.
Absence of a Comprehensive Data Protection Law
In contrast to the European Union's GDPR (General Data Protection Regulation), the United States' sectoral approach, and emerging Latin American data protection systems such as the ones in Brazil, Chile and Colombia, Venezuela has no independent data protection law. This lack of law leads to numerous types of uncertainty in the realm of data protection laws:
- No defined data controller or processor obligations
- No standardized lawful bases for processing
- No clear breach notification timelines
- No independent data protection authority
- No procedural pathway for individuals to seek redress
As a result, data protection in Venezuela is not treated as an independent legal discipline but instead becomes derivative, arising incidentally within constitutional litigation or sector-specific disputes.
Regulatory Fragmentation and Institutional Weakness
Due to the TSJ decisions made in 2011, there has been a lack of regulatory action taken in a systematic fashion and instead most actions have been done on a case by case basis as valid incidents arise. The National Cybersecurity Council was established in 2024; however, its function is to support the establishment of cybersecurity infrastructure and has no defined powers regarding the enforcement of privacy.
This creates a fragmented institutional landscape where:
- Authorities lack clear jurisdiction over privacy violations
- Companies face minimal compliance guidance
- Individuals struggle to understand or enforce their rights
The Movistar and Cashea incidents highlight how this fragmentation translates into practical impunity following major data exposures.
What’s Next? A Legal Opportunity for Reform
The repercussions of insufficient safeguards for data protection extend past the damage incurred to a person's privacy:
- Loss of trust in both financial and digital services
- Heightened likelihood of financial fraud and crime
- Lack of willingness from foreign companies to conduct business with Venezuela’s platforms.
- Long-term negative impact on the reputation of domestic companies.
- Possible inability to access cross-border transfer of data due to other jurisdictions’ decisions to restrict transfers into jurisdictions without cutting-edge enforcement of protections for privacy.
In a digital economy that increasingly requires robust data protection to function successfully, a lack of action to create strong protections will cause a significant economic impact.
Conclusion
Major data breaches such as the ones at Movistar in 2025 and Cashea App in 2026 show that constitutional privacy rights alone are insufficient without enforceable legal framework. Privacy laws must move from being just a principle to being a law that has institutions, procedures, and accountability to make sure the privacy of the users is protected.
Now with the global digital economy being so interconnected, not having regulations creates openings for vulnerabilities for people. If Venezuela hopes to protect their citizens, create an innovation-friendly environment, and compete in the global market, they must implement comprehensive data privacy reforms as soon as possible.
REFERENCES
- https://iapp.org/news/a/venezuela-data-breach-highlights-scattered-privacy-regulation
- https://www.apolocybersecurity.com/en/blog-posts/ciberataque-a-movistar-que-ha-pasado-a-quien-afecta-y-como-proteger-tus-datos
- https://darknetsearch.com/knowledge/news/en/cashea-app-data-leak-79m-records-exposed-in-venezuela/
- https://www.binance.com/en-IN/square/post/294369884695410
