
#Fact Check: Viral Video Falsely Claims Israel Launched Nuclear Attack on Iran
Executive Summary:
A viral video circulating on social media inaccurately suggests that it shows Israel moving nuclear weapons in preparation for an assault on Iran, but a detailed research has established that it instead shows a SpaceX Starship rocket (Starship 36) being towed for a pre-planned test in Texas, USA, and the footage does not provide any evidence to back-up the claim of an Israeli action or a nuclear missile.

Claim:
Multiple posts on social media sharing a video clip of what appeared to be a large, missile-like object being towed to an unknown location by a very large vehicle and stated it is Israel preparing for a nuclear attack on Iran.
The caption of the video said: "Israel is going to launch a nuclear attack on Iran! #Israel”. The viral post received lots of engagement, helpingClaim: to spread misinformation and unfounded fear about the rising conflicts in the Middle East.

Fact check:
By doing reverse image search using the key frames of the viral footage, this landed us at a Facebook post dated June 16, 2025.

A YouTube livestream from NASASpaceflight is dated 15th June 2025. Both sources make it clear that the object was clearly identified as SpaceX Starship 36. This rocket was being towed at SpaceX's Texas facility in advance of a static fire test and as part of the overall preparation for the 10th test flight. In the video, there is clearly no military ordinance or personnel, or Israel’s nuclear attack on Iran markings.
More support for our conclusions came from several articles from SPACE.com, which briefly reported on the Starship's explosion shortly thereafter during various testing iterations.


Also, there was no mention of any Israeli nuclear mobilization by any reputable media or defence agencies. The resemblance between a large rocket and a missile likely added some confusion. Below is a video describing the difference, but the context and upload location have no relation to the State of Israel or Iran.

Conclusion:
The viral video alleging that the actual video showed Israel getting ready to launch a nuclear attack on Iran is false and misleading. In fact, the video was from Texas, showing the civilian transport of SpaceX’s Starship 36. This highlighted how easily unrelated videos can be used to create panic and spread misinformation. If you plan on sharing claims like this, verify them instead using trusted websites and tools.
- Claim: Misleading video on Israel is ready to go nuclear on Iran
- Claimed On: Social Media
- Fact Check: False and Misleading

Related Blogs

Introduction
With the increasing frequency and severity of cyber-attacks on critical sectors, the government of India has formulated the National Cyber Security Reference Framework (NCRF) 2023, aimed to address cybersecurity concerns in India. In today’s digital age, the security of critical sectors is paramount due to the ever-evolving landscape of cyber threats. Cybersecurity measures are crucial for protecting essential sectors such as banking, energy, healthcare, telecommunications, transportation, strategic enterprises, and government enterprises. This is an essential step towards safeguarding these critical sectors and preparing for the challenges they face in the face of cyber threats. Protecting critical sectors from cyber threats is an urgent priority that requires the development of robust cybersecurity practices and the implementation of effective measures to mitigate risks.
Overview of the National Cyber Security Policy 2013
The National Cyber Security Policy of 2013 was the first attempt to address cybersecurity concerns in India. However, it had several drawbacks that limited its effectiveness in mitigating cyber risks in the contemporary digital age. The policy’s outdated guidelines, insufficient prevention and response measures, and lack of legal implications hindered its ability to protect critical sectors adequately. Moreover, the policy should have kept up with the rapidly evolving cyber threat landscape and emerging technologies, leaving organisations vulnerable to new cyber-attacks. The 2013 policy failed to address the evolving nature of cyber threats, leaving organisations needing updated guidelines to combat new and sophisticated attacks.
As a result, an updated and more comprehensive policy, the National Cyber Security Reference Framework 2023, was necessary to address emerging challenges and provide strategic guidance for protecting critical sectors against cyber threats.
Highlights of NCRF 2023
- Strategic Guidance: NCRF 2023 has been developed to provide organisations with strategic guidance to address their cybersecurity concerns in a structured manner.
- Common but Differentiated Responsibility (CBDR): The policy is based on a CBDR approach, recognising that different organisations have varying levels of cybersecurity needs and responsibilities.
- Update of National Cyber Security Policy 2013: NCRF supersedes the National Cyber Security Policy 2013, which was due for an update to align with the evolving cyber threat landscape and emerging challenges.
- Different from CERT-In Directives: NCRF is distinct from the directives issued by the Indian Computer Emergency Response Team (CERT-In) published in April 2023. It provides a comprehensive framework rather than specific directives for reporting cyber incidents.
- Combination of robust strategies: National Cyber Security Reference Framework 2023 will provide strategic guidance, a revised structure, and a proactive approach to cybersecurity, enabling organisations to tackle the growing cyberattacks in India better and safeguard critical sectors.
Rising incidents of malware attacks on critical sectors
In recent years, there has been a significant increase in malware attacks targeting critical sectors. These sectors, including banking, energy, healthcare, telecommunications, transportation, strategic enterprises, and government enterprises, play a crucial role in the functioning of economies and the well-being of societies. The escalating incidents of malware attacks on these sectors have raised concerns about the security and resilience of critical infrastructure.
- Banking: The banking sector handles sensitive financial data and is a prime target for cybercriminals due to the potential for financial fraud and theft.
- Energy: The energy sector, including power grids and oil companies, is critical for the functioning of economies, and disruptions can have severe consequences for national security and public safety.
- Healthcare: The healthcare sector holds valuable patient data, and cyber-attacks can compromise patient privacy and disrupt healthcare services. Malware attacks on healthcare organisations can result in the theft of patient records, ransomware incidents that cripple healthcare operations, and compromise medical devices.
- Telecommunications: Telecommunications infrastructure is vital for reliable communication, and attacks targeting this sector can lead to communication disruptions and compromise the privacy of transmitted data. The interconnectedness of telecommunications networks globally presents opportunities for cybercriminals to launch large-scale attacks, such as Distributed Denial-of-Service (DDoS) attacks.
- Transportation: Malware attacks on transportation systems can lead to service disruptions, compromise control systems, and pose safety risks.
- Strategic Enterprises: Strategic enterprises, including defence, aerospace, intelligence agencies, and other sectors vital to national security, face sophisticated malware attacks with potentially severe consequences. Cyber adversaries target these enterprises to gain unauthorised access to classified information, compromise critical infrastructure, or sabotage national security operations.
- Government Enterprises: Government organisations hold a vast amount of sensitive data and provide essential services to citizens, making them targets for data breaches and attacks that can disrupt critical services.
Conclusion
The sectors of banking, energy, healthcare, telecommunications, transportation, strategic enterprises, and government enterprises face unique vulnerabilities and challenges in the face of cyber-attacks. By recognising the significance of safeguarding these sectors, we can emphasise the need for proactive cybersecurity measures and collaborative efforts between public and private entities. Strengthening regulatory frameworks, sharing threat intelligence, and adopting best practices are essential to ensure our critical infrastructure’s resilience and security. Through these concerted efforts, we can create a safer digital environment for these sectors, protecting vital services and preserving the integrity of our economy and society. The rising incidents of malware attacks on critical sectors emphasise the urgent need for updated cybersecurity policy, enhanced cybersecurity measures, a collaboration between public and private entities, and the development of proactive defence strategies. National Cyber Security Reference Framework 2023 will help in addressing the evolving cyber threat landscape, protect critical sectors, fill the gaps in sector-specific best practices, promote collaboration, establish a regulatory framework, and address the challenges posed by emerging technologies. By providing strategic guidance, this framework will enhance organisations’ cybersecurity posture and ensure the protection of critical infrastructure in an increasingly digitised world.
Introduction
The advancement of technology has brought about remarkable changes in the aviation industry, including the introduction of inflight internet access systems. While these systems provide passengers with connectivity during their flights, they also introduce potential vulnerabilities that can compromise the security of aircraft systems.
Inflight Internet Access Systems
Inflight internet access systems have become integral to the modern air travel experience, allowing passengers to stay connected even at 30,000 feet. However, these systems can also be attractive targets for hackers, raising concerns about the safety and security of aircraft operations.
The Vulnerabilities of Inflight Internet Access Systems:
Securing Networked Avionics
Avionics, the electronic systems that support aircraft operation, play a crucial role in flight safety and navigation. While networked avionics are designed with robust security measures, they are not invulnerable to cyber threats. Therefore, it is essential to implement comprehensive security measures to protect these critical systems.
- Ensuring Robust Architecture: Networked avionics should be designed with a strong focus on security. Implementing secure network architectures, such as segmentation and isolation, can minimise the risk of unauthorised access and limit the potential impact of a breach.
- Rigorous Security Testing: Avionics systems should undergo rigorous security testing to identify vulnerabilities and weaknesses. Regular assessments, penetration testing, and vulnerability scanning are essential to proactively address any security flaws.
- Collaborative Industry Efforts: Collaboration between manufacturers, airlines, regulatory bodies, and security researchers is crucial in strengthening the security of networked avionics. Sharing information, best practices, and lessons learned can help identify and address emerging threats effectively.
- Continuous Monitoring and Updtes: Networked avionics should be continuously monitored for any potential security breaches. Prompt updates and patches should be applied to address newly discovered vulnerabilities and protect against known attack vectors.
Best practices to be adopted for the security of Aircraft Systems
- Holistic Security Approach: Recognizing the interconnectedness of inflight internet access systems and networked avionics is essential. A holistic security approach should be adopted to address vulnerabilities in both systems and protect the overall aircraft infrastructure.
- Comprehensive Security Measures: The security of inflight internet access systems should be on par with any other internet-connected device. Strong authentication, encryption, intrusion detection, and prevention systems should be implemented to mitigate risks and ensure the integrity of data transmissions.
- Responsible Practices and Industry Collaboration: Encouraging responsible practices and fostering collaboration between security researchers and industry stakeholders can accelerate the identification and remediation of vulnerabilities. Open communication channels and a cooperative mindset are vital in addressing emerging threats effectively.
- Robust Access Controls: Strong access controls, such as multi-factor authentication and role-based access, should be implemented to limit unauthorised access to avionics systems. Only authorised personnel should have the necessary privileges to interact with these critical systems.
Conclusion
Inflight internet access systems bring convenience and connectivity to air travel but also introduce potential risks to the security of aircraft systems. It is crucial to understand and address the vulnerabilities associated with these systems to protect networked avionics and ensure passenger safety. By implementing robust security measures, conducting regular assessments, fostering collaboration, and adopting a comprehensive approach to aircraft cybersecurity, the aviation industry can mitigate the risks and navigate the sky with enhanced safety and confidence. Inflight internet access systems and networked avionics are vital components of modern aircraft, providing connectivity and supporting critical flight operations. Balancing connectivity and cybersecurity is crucial to ensure the safety and integrity of aircraft systems.
Executive Summary
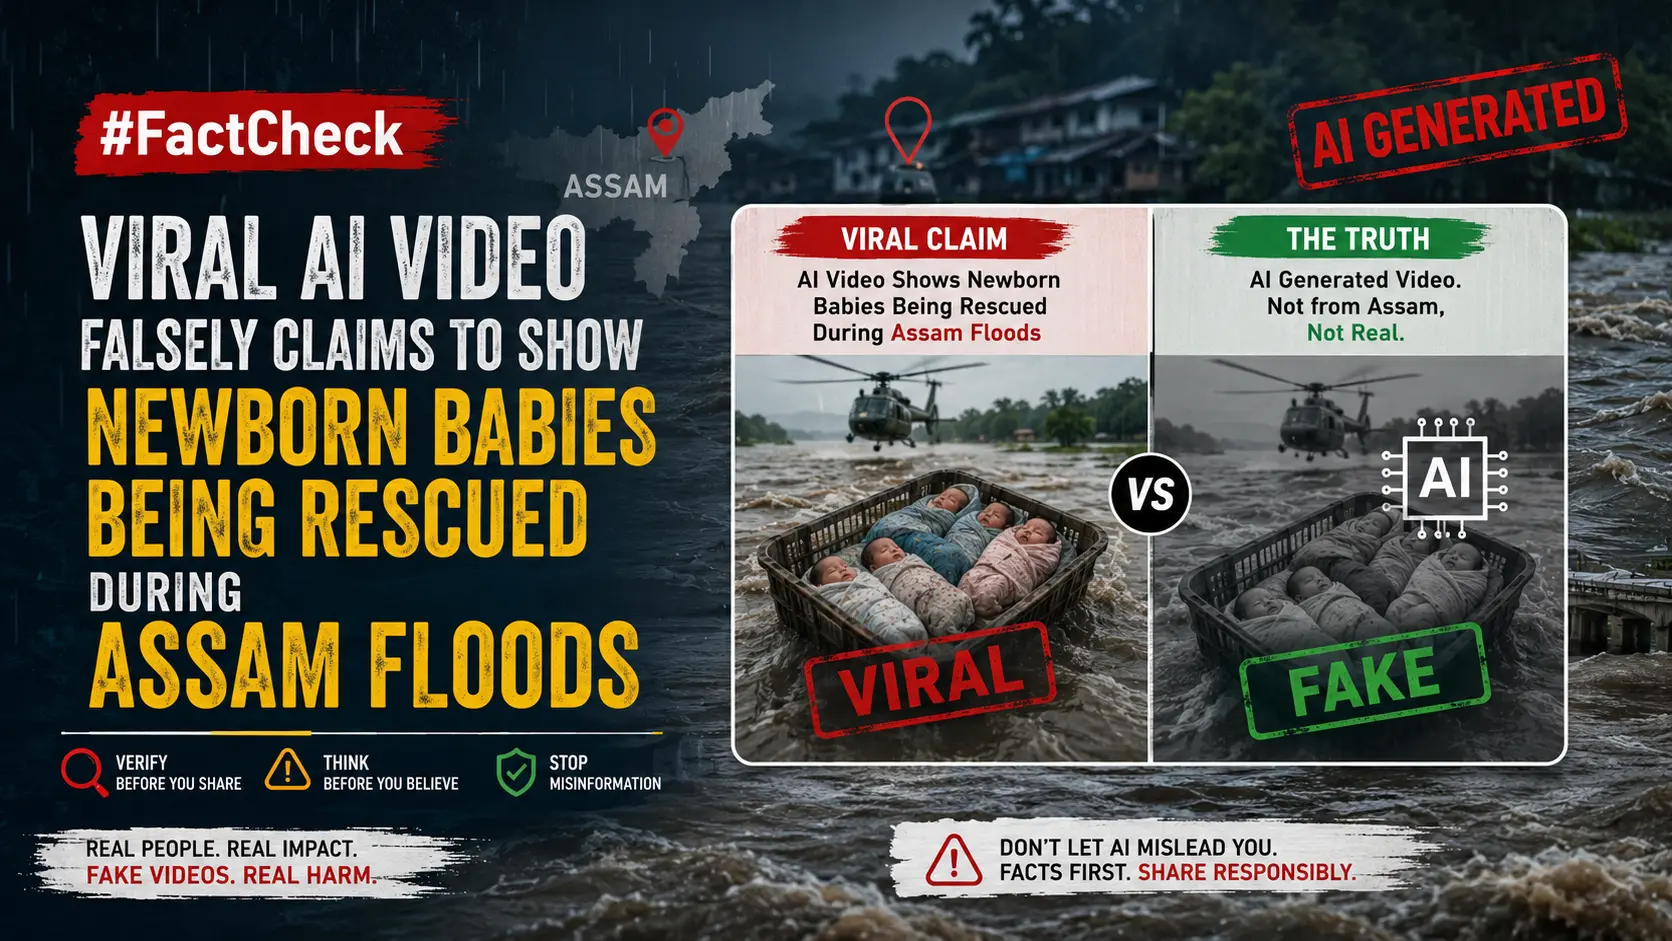
A video is being widely shared on social media with the claim that it shows the recent Assam floods, where nurses are rescuing newborn babies after water entered a hospital. The caption accompanying the viral video claims that the babies are not drowning; instead, healthcare workers and rescue teams are carrying them to safety amid floodwaters inside a hospital. It further states that the video shows humanity and courage during a time of crisis. CyberPeace Research Wing’s research found the claim to be false. The research revealed that the viral video showing healthcare workers rescuing newborn babies is not real but was created using Artificial Intelligence (AI).
Claim:
An Instagram user named kamlakritika shared the video and claimed that it showed the Assam floods. The post stated that the babies were not drowning but were being rescued by healthcare workers and rescue teams from a flooded hospital. In the viral video, several nurses can be seen running through waterlogged areas while trying to protect incubators — containers used to keep newborn babies — from being submerged or swept away. According to the caption, a devastating flood had turned the entire area into a disaster zone. It claimed that incubators containing premature newborn babies were floating in floodwaters, while nurses were running behind them amid strong water currents to save the infants. The caption further claimed that several incubators were overturning and sinking with babies inside, putting hundreds of fragile lives at risk.
https://www.instagram.com/reel/DbXvJwgz72X/?utm_source=ig_web_copy_link&igsh=NTc4MTIwNjQ2YQ==

Factcheck
To verify the claim, CyberPeace Research Wing conducted a Google search using relevant keywords. During the search, the video was found shared by several other Instagram accounts. During the research, we found a report published by News18 on August 1, 2026. Although the report was related to the Assam floods, it mentioned a different incident. According to the report, a viral video showed floodwaters surrounding houses, with water spread across the area. In the video, a rescue team member can be seen carefully carrying a newborn baby in his arms through the flooded area and handing the child over to another rescue worker near a boat so that the baby could be taken to safety.

However, during our research, we could not find any information from credible news organisations or official sources confirming the viral video showing newborn babies being rescued in incubators. As part of further research, we closely examined the viral video and noticed several indications suggesting that it could be AI-generated. The video was then analysed using the AI detection tool FauxLens, which indicated that the video was approximately 75% AI-generated.

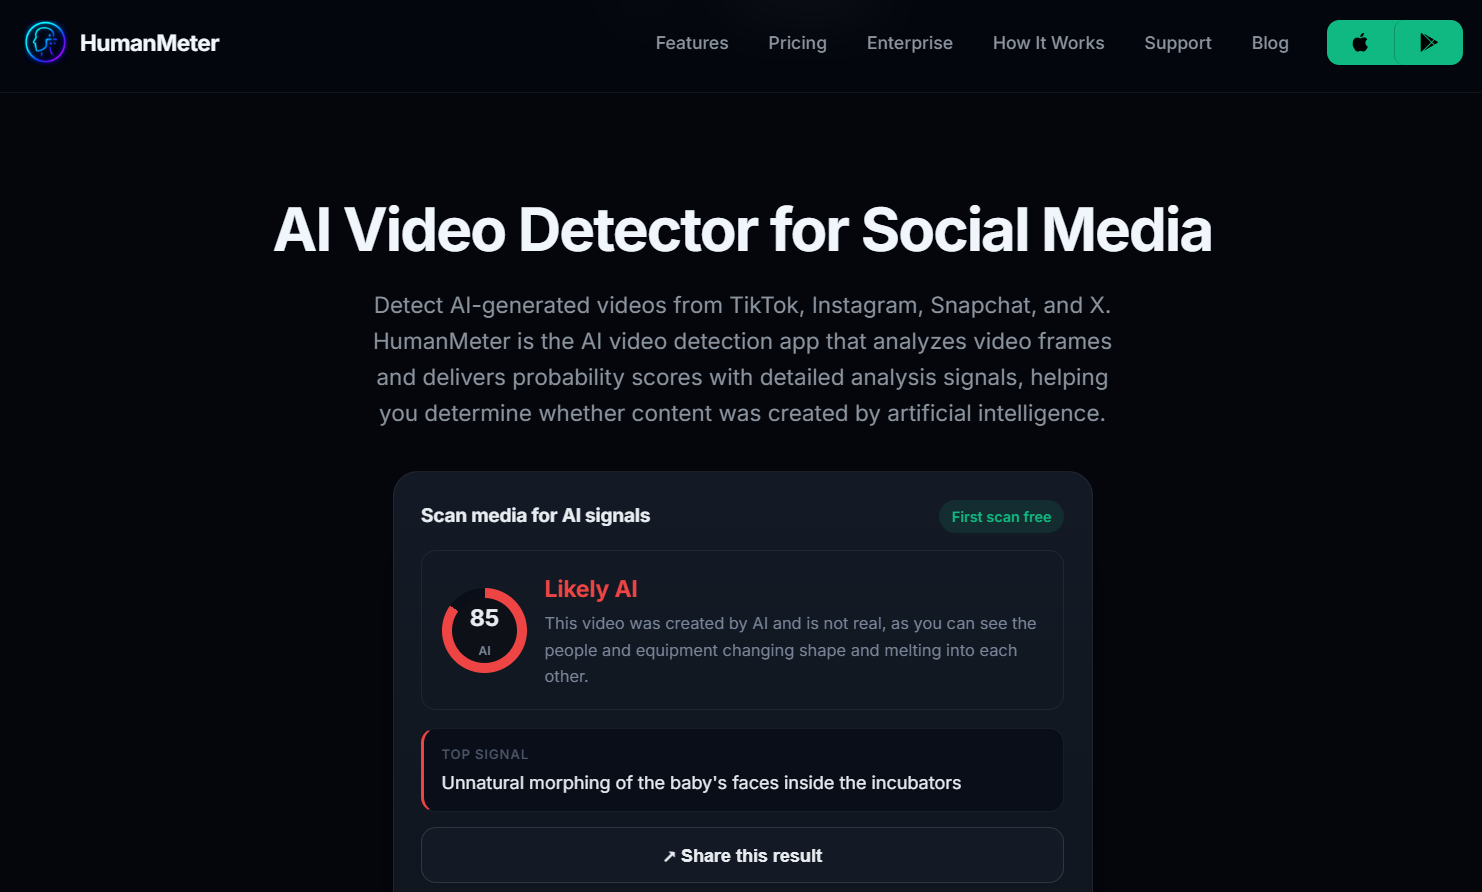
To further verify the authenticity of the video, we also analysed it using another AI detection tool, Human Meter. The tool showed an 85% probability of the video being generated with the help of AI.
Conclusion:
CyberPeace Research Wing’s research found that the viral video claiming to show nurses rescuing newborn babies during Assam floods is false. The video is not an actual incident but an AI-generated creation.
