
#FactCheck: Viral video of Unrest in Kenya is being falsely linked with J&K
Executive Summary:
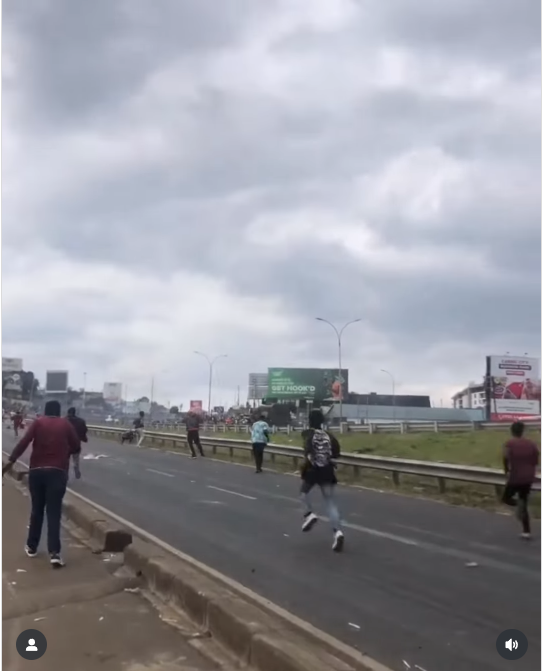
A video of people throwing rocks at vehicles is being shared widely on social media, claiming an incident of unrest in Jammu and Kashmir, India. However, our thorough research has revealed that the video is not from India, but from a protest in Kenya on 25 June 2025. Therefore, the video is misattributed and shared out of context to promote false information.
Claim:
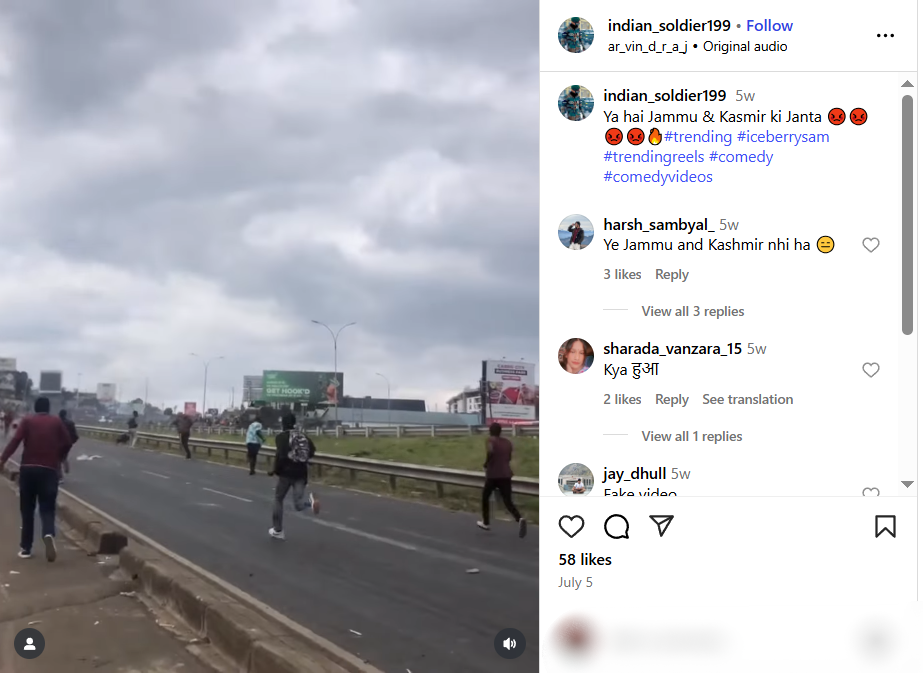
The viral video shows people hurling stones at army or police vehicles and is claimed to be from Jammu and Kashmir, implying ongoing unrest and anti-government sentiment in the region.
Fact Check:
To verify the validity of the viral statement, we did a reverse image search by taking key frames from the video. The results clearly demonstrated that the video was not sourced from Jammu and Kashmir as claimed, but rather it was consistent with footage from Nairobi, Kenya, where a significant protest took place on 25 June 2025. Protesters in Kenya had congregated to express their outrage against police brutality and government action, which ultimately led to violent clashes with police.
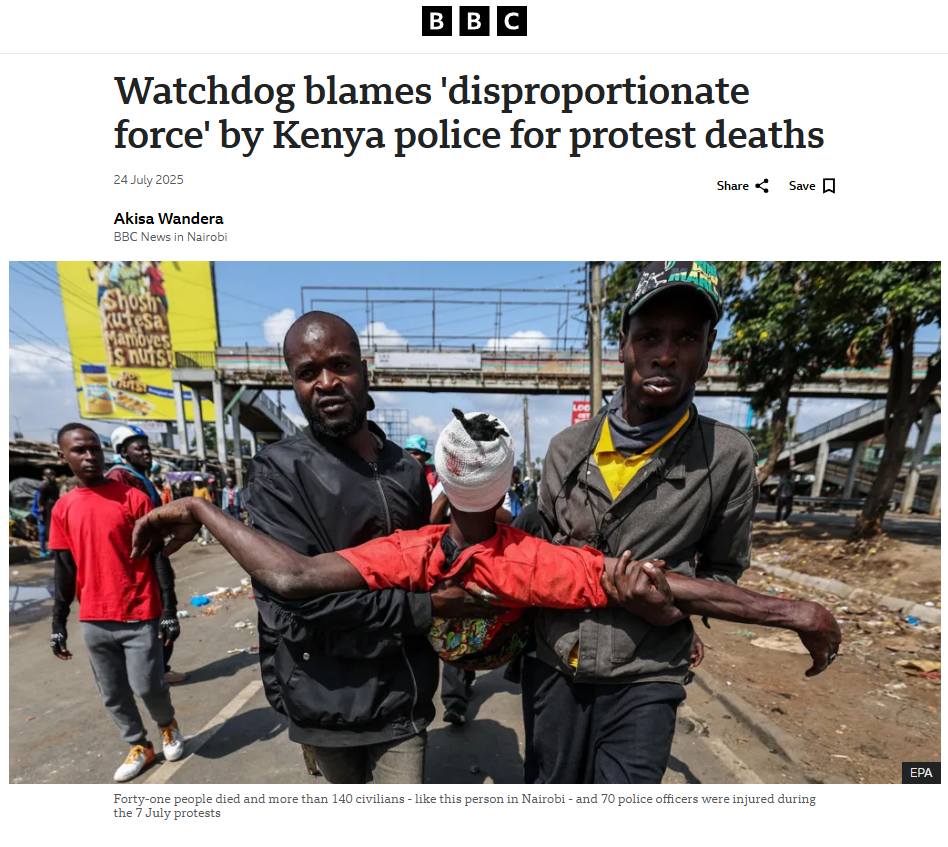
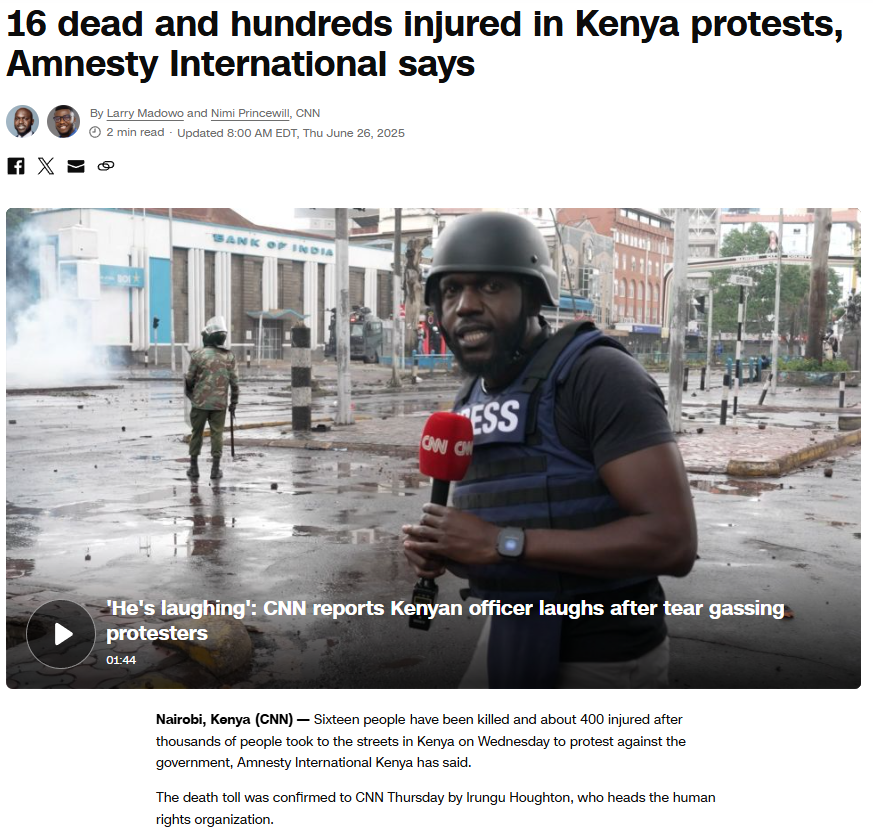
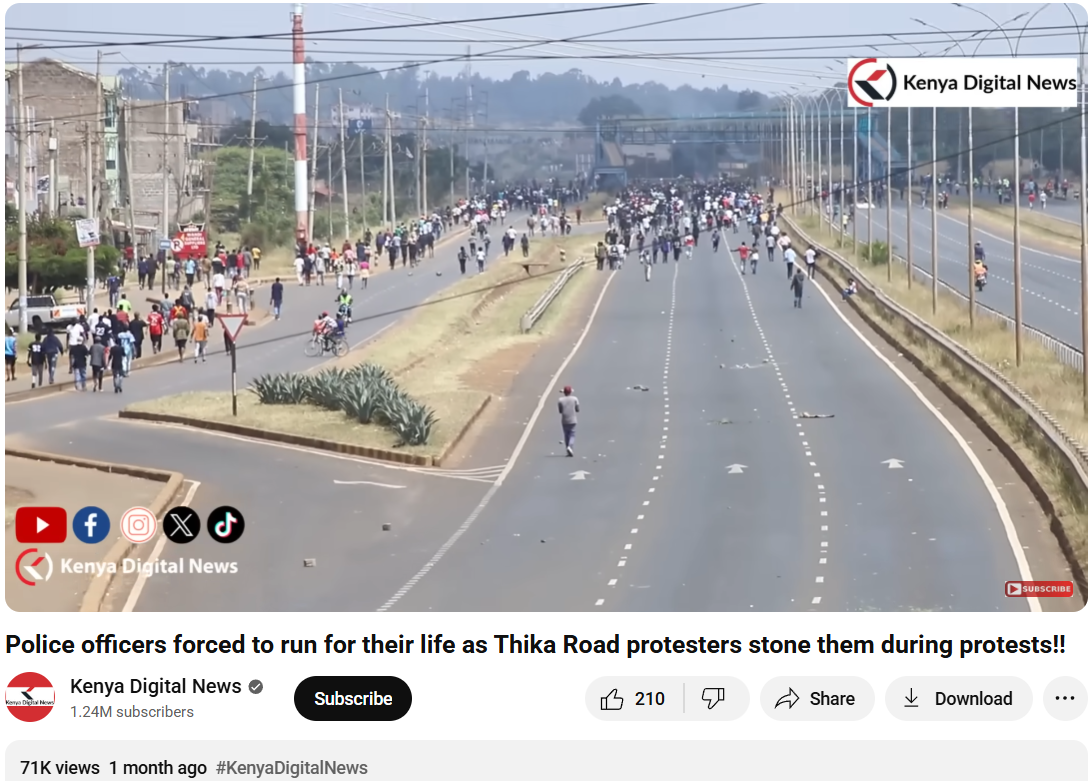
We also came across a YouTube video with similar news and frames. The protests were part of a broader anti-government movement to mark its one-year time period.
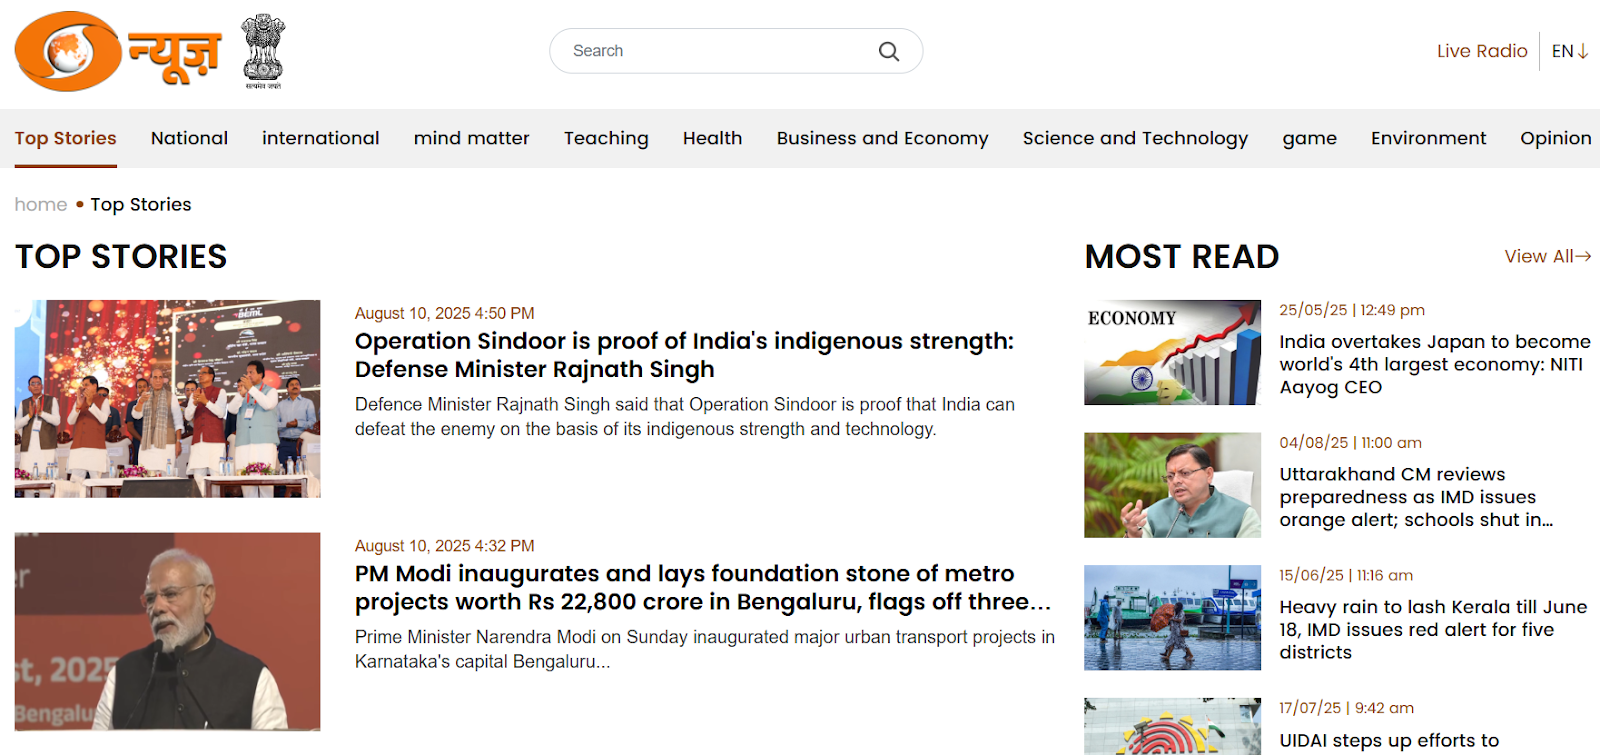
To support the context, we did a keyword search of any mob violence or recent unrest in J&K on a reputable Indian news source, But our search did not turn up any mention of protests or similar events in J&K around the relevant time. Based on this evidence, it is clear that the video has been intentionally misrepresented and is being circulated with false context to mislead viewers.
Conclusion:
The assertion that the viral video shows a protest in Jammu and Kashmir is incorrect. The video appears to be taken from a protest in Nairobi, Kenya, in June 2025. Labeling the video incorrectly only serves to spread misinformation and stir up uncalled for political emotions. Always be sure to verify where content is sourced from before you believe it or share it.
- Claim: Army faces heavy resistance from Kashmiri youth — the valley is in chaos.
- Claimed On: Social Media
- Fact Check: False and Misleading

Related Blogs

Introduction
In the labyrinthine world of cybersecurity, a new spectre has emerged from the digital ether, casting a long shadow over the seemingly impregnable orchards of Apple's macOS. This phantom, known as SpectralBlur, is a backdoor so cunningly crafted that it remained shrouded in the obscurity of cyberspace, undetected by the vigilant eyes of antivirus software until its recent unmasking. The discovery of SpectralBlur is not just a tale of technological intrigue but a narrative that weaves together the threads of geopolitical manoeuvring, the relentless pursuit of digital supremacy, and the ever-evolving landscape of cyber warfare.
SpectralBlur, a term that conjures images of ghostly interference and elusive threats, is indeed a fitting moniker for this new macOS backdoor threat. Cybersecurity researchers have peeled back the layers of the digital onion to reveal a moderately capable backdoor that can upload and download files, execute shell commands, update its configuration, delete files, and enter states of hibernation or sleep, all at the behest of a remote command-and-control server. Greg Lesnewich, a security researcher whose name has become synonymous with the relentless pursuit of digital malefactors, has shed light on this new threat that overlaps with a known malware family attributed to the enigmatic North Korean threat actors.
SpectralBlur similar to Lazarus Group’s KANDYKORN
The malware shares its DNA with KANDYKORN, also known as SockRacket, an advanced implant that functions as a remote access trojan capable of taking control of a compromised host. It is a digital puppeteer, pulling the strings of infected systems with a malevolent grace. The KANDYKORN activity also intersects with another campaign orchestrated by the Lazarus sub-group known as BlueNoroff, or TA444, which culminates in the deployment of a backdoor referred to as RustBucket and a late-stage payload dubbed ObjCShellz.
Recently, the threat actor has been observed combining disparate pieces of these two infection chains, leveraging RustBucket droppers to deliver KANDYKORN. This latest finding is another sign that North Korean threat actors are increasingly setting their sights on macOS to infiltrate high-value targets, particularly those within the cryptocurrency and blockchain industries. 'TA444 keeps running fast and furious with these new macOS malware families,' Lesnewich remarked, painting a picture of a relentless adversary in the digital realm.
Patrick Wardle, a security researcher whose insights into the inner workings of SpectralBlur have further illuminated the threat landscape, noted that the Mach-O binary was uploaded to the VirusTotal malware scanning service in August 2023 from Colombia. The functional similarities between KANDYKORN and SpectralBlur have raised the possibility that they may have been built by different developers with the same requirements. What makes the malware stand out are its attempts to hinder analysis and evade detection while using grant to set up a pseudo-terminal and execute shell commands received from the C2 server.
The disclosure comes as 21 new malware families designed to target macOS systems, including ransomware, information stealers, remote access trojans, and nation-state-backed malware, were discovered in 2023, up from 13 identified in 2022. 'With the continued growth and popularity of macOS (especially in the enterprise!), 2024 will surely bring a bevvy of new macOS malware,' Wardle noted, his words a harbinger of the digital storms on the horizon.
Hackers are beefing up their efforts to go after the best MacBooks as security researchers have discovered a brand new macOS backdoor which appears to have ties to another recently identified Mac malware strain. As reported by Security Week, this new Mac malware has been dubbed SpectralBlur and although it was uploaded to VirusTotal back in August of last year, it remained undetected by the best antivirus software until it recently caught the attention of Proofpoint’s Greg Lesnewich.
Lesnewich explained that SpectralBlur has similar capabilities to other backdoors as it can upload and download files, delete files and hibernate or sleep when given commands from a hacker-controlled command-and-control (C2) server. What is surprising about this new Mac malware strain though is that it shares similarities to the KandyKorn macOS backdoor which was created by the infamous North Korean hacking group Lazarus.
Just like SpectralBlur, KandyKorn is designed to evade detection while providing the hackers behind it with the ability to monitor and control infected Macs. Although different, these two Mac malware strains appear to be built based on the same requirements. Once installed on a vulnerable Mac, SpectralBlur executes a function that allows it to decrypt and encrypt network traffic to help it avoid being detected. However, it can also erase files after opening them and then overwrite the data they contain with zeros..
How to keep your Apple computers safe from hackers
As with the best iPhones, keeping your Mac up to date is the easiest and most important way to keep it safe from hackers. Hackers often prey on users who haven’t updated their devices to the latest software as they can exploit unpatched vulnerabilities and security flaws.
Checking to see if you're running the latest macOS version is quite easy. Just click on the Apple Logo in the top right corner of your computer, head to System Preferences and then click on Software Update. If you need a bit more help, check out our guide on how to update a Mac for more detailed instructions with pictures.
Even though your Mac has its own built-in malware scanner from Apple called xProtect, you should consider using one of the best Mac antivirus software solutions for additional protection. Paid antivirus software is often updated more frequently and you often also get access to other extras to help keep you safe online like a password manager or a VPN.
Besides updating your Mac frequently and using antivirus software, you must be careful online. This means sticking to trusted online retailers, carefully checking the URLs of the websites you visit and avoiding opening links and attachments sent to you via email or social media from people you don’t know. Likewise, you should also learn how to spot a phishing scam to know which emails you want to delete right away.
Conclusion
The thing about hackers and other cybercriminals is that they are constantly evolving their tactics and attack methods. This helps them avoid detection and allows them to devise brand-new ways to trick ordinary people. With the surge we saw in Mac malware last year, though, Apple will likely be working on beefing up xProtect and macOS to better defend against these new threats.
References
- https://www.scmagazine.com/news/new-macos-malware-spectralblur-idd-as-north-korean-backdoor
- https://www.tomsguide.com/news/this-new-macos-backdoor-lets-hackers-take-over-your-mac-remotely-how-to-stay-safe
- https://thehackernews.com/2024/01/spectralblur-new-macos-backdoor-threat.html

Executive Summary:
In the recent advisory the Indian Computer Emergency Response Team (CERT-In) has released a high severity warning in the older versions of the software across Apple devices. This high severity rating is because of the multiple vulnerabilities reported in Apple products which could allow the attacker to unfold the sensitive information, and execute arbitrary code on the targeted system. This warning is extremely useful to remind of the necessity to have the software up to date to prevent threats of a cybernature. It is important to update the software to the latest versions and cyber hygiene practices.
Devices Affected:
CERT-In advisory highlights significant risks associated with outdated software on the following Apple devices:
- iPhones and iPads: iOS versions that are below 18 and the 17.7 release.
- Mac Computers: All macOS builds before 14.7 (20G71), 13.7 (20H34), and earlier 20.2 for Sonoma, Ventura, Sequoia, respectively.
- Apple Watches: watchOS versions prior to 11
- Apple TVs: tvOS versions prior to 18
- Safari Browsers: versions prior to 18
- Xcode: versions prior to 16
- visionOS: versions prior to 2
Details of the Vulnerabilities:
The vulnerabilities discovered in these Apple products could potentially allow attackers to perform the following malicious activities:
- Access sensitive information: The attackers could easily access the sensitive information stored in other parts of the violated gadgets.
- Execute arbitrary code: The web page could be compromised with malcode and run on the targeted system which in the worst scenario would give the intruder full Administrator privileges on the device.
- Bypass security restrictions: Measures agreed to safeguard the device and information contained on it may be easily bypassed and the system left open to more proliferation.
- Cause denial-of-service (DoS) attacks: The vulnerabilities could be used to cause the targeted device or service to be unavailable to the rightful users.
- Perform spoofing attacks: There could be a situation where the attackers created fake entities or users or accounts to have a way into important information or do other unauthorized activities.
- Elevate privileges: It is also stated that weaknesses might be exploited to authorize the attacker a higher level of privileges in the system they are targets.
- Engage in cross-site scripting (XSS) attacks: Some of them make the associated Web applications/sites prone to XSS attacks by injecting hostile scripts into Web page code.
Vulnerabilities:
CVE-2023-42824
- Attack vector could allow a local attacker to elevate their privileges and potentially execute arbitrary code.
Affected System
- Apple's iOS and iPadOS software
CVE-2023-42916
- To improve the out of bounds read it was mitigated with improved input validation which was resolved later.
Affected System
- Safari, iOS, iPadOS, macOS, and Apple Watch Series 4 and later devices running watchOS 10.2
CVE-2023-42917
- leads to arbitrary code execution, and there have been reports of it being exploited in earlier versions of iOS.
Affected System
- Apple's Safari browser, iOS, iPadOS, and macOS Sonoma systems
Recommended Actions for Users:
To mitigate these risks, that users take immediate action:
- Update Software: Ensure all your devices are on the most current version of the operating systems they use. Repetitive updates have important security updates that fix identified weaknesses or flaws within the system.
- Monitor Device Activity: Stay vigilant if something doesn’t seem right; if your gadgets are accessed by someone who isn’t you.
- Always use strong, distinct passwords and use two-factor authentication.
- Install and update the antivirus and Firewall softwares.
- Avoid downloading any applications or clicking link from unknown sources
Conclusion:
The advisory from CERT-In, clearly demonstrates the fundamental need of keeping the software on all Apple devices up to date. Consumers need to act right away to patch their devices and apply best security measures like using multiple factors for login and system scanning. This advisory has come out when Apple has just released new products into the market such as the iPhone 16 series in India. When consumers embrace new technologies it is important for them to observe relevant measures of security precautions. Maintaining good cyber hygiene is a critical process for the protection against new threats.
Reference:
- https://www.cert-in.org.in/s2cMainServlet?pageid=PUBVLNOTES02&VLCODE=CIAD-2023-0043
- https://www.cve.org/CVERecord?id=CVE-2023-42916
- https://www.cve.org/CVERecord?id=CVE-2023-42917
- https://www.bizzbuzz.news/technology/gadjets/cert-in-issues-advisory-on-vulnerabilities-affecting-iphones-ipads-and-macs-1337253#google_vignette
- https://www.wionews.com/videos/india-warns-apple-users-of-high-severity-security-risks-in-older-software-761396

Introduction
The AI Action Summit is a global forum that brings together world leaders, policymakers, technology experts, and industry representatives to discuss AI governance, ethics, and its role in society. This year, the week-long Paris AI Action Summit officially culminated on the 11th of February, 2025. It brought together experts from the industry, policymakers, and other dignitaries to discuss Artificial Intelligence and its challenges. The event was co-chaired by Indian Prime Minister Narendra Modi and French President Emmanuel Macron. In line with the summit, the Indian delegation actively engaged in the 2nd India-France AI Policy Roundtable, an official side event of the summit, and the 14th India-France CEOs Forum. These discussions were on diverse sectors including defense, aerospace, technology, etc. among other things.
Prime Minister Modi’s Address
During the AI Action Summit in Paris, Prime Minister Narendra Modi drew attention to the revolutionary effect of AI in politics, the economy, security, and society. Stressing the requirement of international cooperation, he promoted strong frameworks of governance to combat AI-based risks and consequently, build public confidence in new technologies. Needed efforts with respect to cybersecurity issues such as deepfakes and disinformation were also acknowledged.
Democratising AI, and sharing its benefits, particularly with the Global South not only aligned with Sustainable Development Goals (SDGs) but also affirmed India’s resolve towards sharing expertise and best practices. India’s remarkable feat of creating a Digital Public Infrastructure, that caters to a population of 1.4 billion through open and accessible technology was highlighted as well.
Among the key announcements, India revealed its plans to create its own Large Language Model (LLM) that reflects the country's linguistic diversity, strengthening its AI aspirations. Further, India will be hosting the next AI Action Summit, reaffirming its position in international AI leadership. The Prime Minister also welcomed France's initiatives, such as the launch of the "AI Foundation" and the "Council for Sustainable AI", initiated by President Emmanuel Macron. He emphasized the necessity to extend the Global Partnership for AI and to get it more representative and inclusive so that Global South voices are actually incorporated into AI innovation and governance.
Other Perspectives
Though there were 58 countries that signed the international agreement on a more open, inclusive, sustainable, and ethical approach to AI development (including India, France, and China), the UK and the US have refused to sign the international agreement at the AI Summit stating their issues with global governance and national security. While the former raised concerns about the lack of sufficient details regarding the establishment of global AI governance and AI’s effect on national security as their reason, the latter showcased its reservations about the overly wide AI regulations which had the potential to hamper a transformative industry. Meanwhile, the US is also looking forward to ‘Stargate’, its $500 billion AI infrastructure project alongside the companies- OpenAI, Softbank, and Oracle.
CyberPeace Insights
The Summit has garnered greater significance with the backdrop of the release of platforms such as DeepSeek R1, China’s AI assistant system similar to that of OpenAI’s ChatGPT. On its release, it was the top-rated free application on Apple’s app store and sent the technology stocks tumbling. Moreover, investors world over appreciated the creation of the model which was made roughly in about $5 million while other AI companies spent more in comparison (keeping in mind the restrictions caused by the chip export controls in China). This breakthrough challenges the conventional notion that massive funding is a prerequisite for innovation, offering hope for India’s burgeoning AI ecosystem. With the IndiaAI mission and fewer geopolitical restrictions, India stands at a pivotal moment to drive responsible AI advancements.
References:
- https://www.mea.gov.in/press-releases.htm?dtl/39023/Prime_Minister_cochairs_AI_Action_Summit_in_Paris_February_11_2025
- https://indianexpress.com/article/explained/explained-sci-tech/what-is-stargate-trumps-500-billion-ai-project-9793165/
- https://pib.gov.in/PressReleasePage.aspx?PRID=2102056
- https://pib.gov.in/PressReleasePage.aspx?PRID=2101947
- https://pib.gov.in/PressReleasePage.aspx?PRID=2101896
- https://www.timesnownews.com/technology-science/uk-and-us-decline-to-sign-global-ai-agreement-at-paris-ai-action-summit-here-is-why-article-118164497
- https://www.thehindu.com/sci-tech/technology/india-57-others-sign-paris-joint-statement-on-inclusive-sustainable-ai/article69207937.ece
