
#FactCheck: Fake viral AI video captures a real-time bridge failure incident in Bihar
Executive Summary:
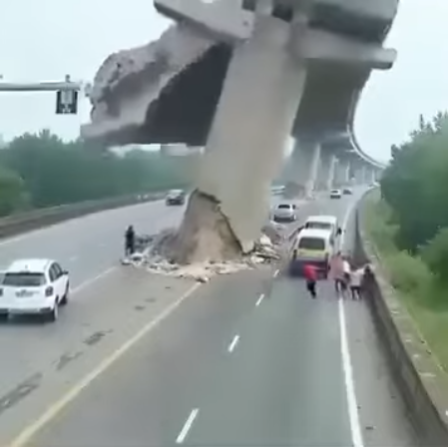
A video went viral on social media claiming to show a bridge collapsing in Bihar. The video prompted panic and discussions across various social media platforms. However, an exhaustive inquiry determined this was not real video but AI-generated content engineered to look like a real bridge collapse. This is a clear case of misinformation being harvested to create panic and ambiguity.
Claim:
The viral video shows a real bridge collapse in Bihar, indicating possible infrastructure failure or a recent incident in the state.
Fact Check:
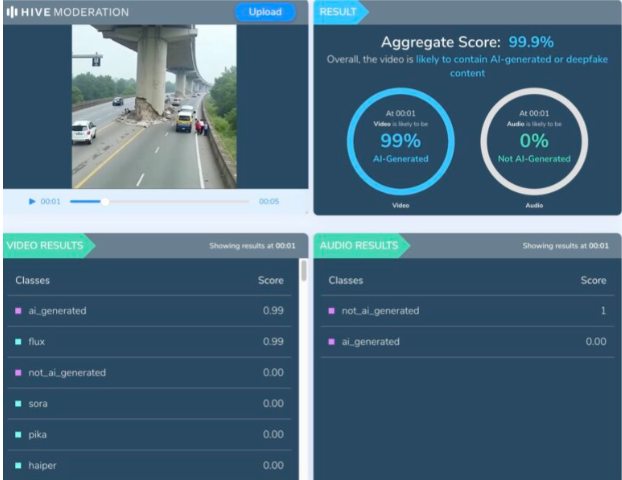
Upon examination of the viral video, various visual anomalies were highlighted, such as unnatural movements, disappearing people, and unusual debris behavior which suggested the footage was generated artificially. We used Hive AI Detector for AI detection, and it confirmed this, labelling the content as 99.9% AI. It is also noted that there is the absence of realism with the environment and some abrupt animation like effects that would not typically occur in actual footage.
No valid news outlet or government agency reported a recent bridge collapse in Bihar. All these factors clearly verify that the video is made up and not real, designed to mislead viewers into thinking it was a real-life disaster, utilizing artificial intelligence.
Conclusion:
The viral video is a fake and confirmed to be AI-generated. It falsely claims to show a bridge collapsing in Bihar. This kind of video fosters misinformation and illustrates a growing concern about using AI-generated videos to mislead viewers.
Claim: A recent viral video captures a real-time bridge failure incident in Bihar.
Claimed On: Social Media
Fact Check: False and Misleading

Related Blogs

Introduction
National AVGC-XR stands for National Animation, Visual Effects, Gaming, Comics, and Extended Reality. On 21 Aug 2024 Shri Sanjay Jaju, Secretary, Ministry of Information and Broadcasting, Speaking at the 5th Global AVGC and Immersive Media Summit 2024, announced that the National AVGC-XR Policy will be implemented soon. National AVGC-XR policy aims to facilitate investment, foster innovation, ensure skill development, protect intellectual property and help build world-class infrastructure. Additionally, Atul Kumar Tiwari, Secretary of Ministry of Skills and Entrepreneurship, said that the Centre's decision to revamp 1,000 ITIs is pivotal in aligning workforce skills with AVGC industry needs. He called for enhanced intellectual property rights to retain talent and content in India.
Key Highlights of National AVGC-XR Policy
- The policy will be implemented in conjunction with the National AVGC-XR Mission to improve India's AVGC sectors through infrastructure development, skill enhancement, innovation, and regulatory support.
- The policy aims to improve India's international competitiveness in the AVGC industry, specifically by supporting the creation of unique intellectual properties (IPs) that can gain worldwide acclaim.
- The policy acknowledges the significance of adapting and converting content for various international viewers, which has become easier considering technological advancements.
- The government is dedicated to providing strong policies and financial backing to the AVGC industry, ensuring that India continues to be a worldwide leader in the sector.
Tech-driven trends in the AVGC-XR Sector promoting exponential growth
- Advancements in technology specifically when we talk about the Animation and VFX industry, emerging trends such as AR, VR, and real-time 3D technology, are driving the expansion of the metaverse, resulting in a rising need for fresh jobs and broadening uses beyond gaming into education, e-commerce, and entertainment. Moreover, the transition to cloud-oriented production processes and the increase in unique or original content on OTT platforms are improving cooperation and propelling industry growth. To drive expansion, global OTT leaders are commissioning more original content. This has increased the need for VFX, post-production, and animation services.
- Technological advancements in India's gaming industry, like cloud gaming, increased popularity of mobile gaming, the introduction of 5G and 6G, and recognition of e-gaming at national and international forums, are breaking down obstacles and fueling swift growth, positioning India as a key player in growing e-gaming sector worldwide. Furthermore, the integration of gamification and XR in education and training is generating immersive experiences that improve learning and skill building, contributing to the expansion of the AVGC-XR industry.
- The comics industry is being transformed by technological advancements like digital technology and self-publishing, which are increasing access and distribution through online platforms and social media. The rising popularity of graphic novels and the greater use of digital comics, particularly among young audiences with smartphones, are fueling substantial growth in the AVGC-XR industry.
- The use of AR, VR, and MR (Mixed Reality) technologies is rapidly growing due to tech-driven trends in Extended Reality (XR), transforming industries such as healthcare, education, and retail. The rising number of startups in this sector, boosted by higher venture capital funding, is speeding up the uptake of XR services, establishing it as a primary catalyst of innovation and expansion in various industries.
Final Words:
Just like the IT revolution, the Indian AVGC-XR industry along with technological trends and advancements has great potential. With the growth in various sectors within the AVGC industry, the right policy framework in place and government support, it will be forefront of India’s global standing in the AVGC sectoral growth including various Intellectual Property (IP), creations, and outsourcing services. The proposed AVGC-XR policy with a forward-thinking approach will drive the industry growth. Thus, a comprehensive integrated and collaborative approach is essential. Furthermore with rising trends in technological space including the use of AR, VR, cloud spaces, 6G and expansion of the OTT sector, the safe and secure use in terms of cybersecurity is encouraged to ultimately protect the interest of users and establish a safe secure cyber world driven by exponential growth in various sectors including AVGC. We’re at the cusp of a new era, where we’re looking at technological advancements not as a tool but as a way of life, hence safe and secure usage remains a top priority.
References:
- https://www.cii.in/PressreleasesDetail.aspx?enc=IkIXRoaDhS+jXtgjqb7UcbWSnaI7mgIS485nHsQEMbw
- https://www.thehindu.com/sci-tech/technology/avgc-xr-policy-to-be-implemented-in-tandem-with-national-avgc-xr-mission-ib-secretary/article68550433.ece#:~:text=Speaking%20at%20the%20Fifth%20Global,competitiveness%20by%20fostering%20infrastructure%20development%2C
- https://mib.gov.in/sites/default/files/Annexure%20C-AVGC-XR%20-%20Draft%20for%20National%20Policy_16th%20December%202022-AG%20EDIT.pdf
- https://www.drishtiias.com/daily-updates/daily-news-analysis/potential-of-india-s-avgc-xr-sector

Introduction
The unprecedented cyber espionage attempt on the Indian Air Force has shocked the military fraternity in the age of the internet where innovation is vital to national security. The attackers have shown a high degree of expertise in their techniques, using a variant of the infamous Go Stealer and current military acquisition pronouncements as a cover to obtain sensitive information belonging to the Indian Air Force. In this recent cyber espionage revelation, the Indian Air Force faces a sophisticated attack leveraging the infamous Go Stealer malware. The timing, coinciding with the Su-30 MKI fighter jets' procurement announcement, raises serious questions about possible national security espionage actions.
A sophisticated attack using the Go Stealer malware exploits defense procurement details, notably the approval of 12 Su-30 MKI fighter jets. Attackers employ a cunningly named ZIP file, "SU-30_Aircraft_Procurement," distributed through an anonymous platform, Oshi, taking advantage of heightened tension surrounding defense procurement.
Advanced Go Stealer Variant:
The malware, coded in Go language, introduces enhancements, including expanded browser targeting and a unique data exfiltration method using Slack, showcasing a higher level of sophistication.
Strategic Targeting of Indian Air Force Professionals:
The attack strategically focuses on extracting login credentials and cookies from specific browsers, revealing the threat actor's intent to gather precise and sensitive information.
Timing Raises Espionage Concerns:
The cyber attack coincides with the Indian Government's Su-30 MKI fighter jets procurement announcement, raising suspicions of targeted attacks or espionage activities.
The Deceitful ZIP ArchiveSU-30 Aircraft Acquisition
The cyberattack materialised as a sequence of painstakingly planned actions. Using the cleverly disguised ZIP file "SU-30_Aircraft_Procurement," the perpetrators took benefit of the authorisation of 12 Su-30 MKI fighter jets by the Indian Defense Ministry in September 2023. Distributed via the anonymous file storage network Oshi, the fraudulent file most certainly made its way around via spam emails or other forms of correspondence.
The Spread of Infection and Go Stealer Payload:
The infiltration procedure progressed through a ZIP file to an ISO file, then to a.lnk file, which finally resulted in the Go Stealer payload being released. This Go Stealer version, written in the programming language Go, adds sophisticated capabilities, such as a wider range of browsing focussed on and a cutting-edge technique for collecting information using the popular chat app Slack.
Superior Characteristics of the Go Stealer Version
Different from its GitHub equivalent, this Go Stealer version exhibits a higher degree of complexity. It creates a log file in the machine owned by the victim when it is executed and makes use of GoLang utilities like GoReSym for in-depth investigation. The malware focuses on cookies and usernames and passwords from web browsers, with a particular emphasis on Edge, Brave, and Google Chrome.
This kind is unique in that it is more sophisticated. Its deployment's cyber enemies have honed its strengths, increasing its potency and detection resistance. Using GoLang tools like GoReSym for comprehensive evaluation demonstrates the threat actors' careful planning and calculated technique.
Go Stealer: Evolution of Threat
The Go Stealer first appeared as a free software project on GitHub and quickly became well-known for its capacity to stealthily obtain private data from consumers who aren't paying attention. Its effectiveness and stealthy design rapidly attracted the attention of cyber attackers looking for a sophisticated tool for clandestine data exfiltration. It was written in the Go programming language.
Several cutting-edge characteristics distinguish the Go Stealer from other conventional data thieves. From the beginning, it showed a strong emphasis on browser focusing on, seeking to obtain passwords and login information from particular websites including Edge, Brave, and Google Chrome.The malware's initial iteration was nurtured on the GitHub database, which has the Go Stealer initial edition. Threat actors have improved and altered the code to serve their evil goals, even if the basic structure is freely accessible.
The Go Stealer version that has been discovered as the cause of the current internet spying by the Indian Air Force is not limited to its GitHub roots. It adds features that make it more dangerous, like a wider range of browsers that may be targeted and a brand-new way to exfiltrate data via Slack, a popular messaging app.
Secret Communications and Information Expulsion
This variation is distinguished by its deliberate usage of the Slack API for secret chats. Slack was chosen because it is widely used in company networks and allows harmful activity to blend in with normal business traffic. The purpose of the function "main_Vulpx" is specifically to upload compromised information to the attacker's Slack route, allowing for covert data theft and communication.
The Time and Strategic Objective
There are worries about targeted assaults or espionage activities due to the precise moment of the cyberattack, which coincides with the Indian government's declaration of its acquisition of Su-30 MKI fighter fighters. The deliberate emphasis on gathering cookies and login passwords from web browsers highlights the threat actor's goal of obtaining accurate and private data from Indian Air Force personnel.
Using Caution: Preventing Possible Cyber Espionage
- Alertness Against Misleading Techniques: Current events highlight the necessity of being on the lookout for files that appear harmless but actually have dangerous intent. The Su-30 Acquisition ZIP file is a stark illustration of how these kinds of data might be included in larger-scale cyberespionage campaigns.
- Potentially Wider Impact: Cybercriminals frequently plan coordinated operations to target not just individuals but potentially many users and government officials. Compromised files increase the likelihood of a serious cyber-attack by opening the door for larger attack vectors.
- Important Position in National Security: Recognize the crucial role people play in the backdrop of national security in the age of digitalisation. Organised assaults carry the risk of jeopardising vital systems and compromising private data.
- Establish Strict Download Guidelines: Implement a strict rule requiring file downloads to only come from reputable and confirmed providers. Be sceptical, particularly when you come across unusual files, and make sure the sender is legitimate before downloading any attachments.
- Literacy among Government Employees: Acknowledge that government employees are prime targets as they have possession of private data. Enable people by providing them with extensive cybersecurity training and awareness that will increase their cognition and fortitude.
Conclusion
Indian Air Force cyber surveillance attack highlights how sophisticated online dangers have become in the digital era. Threat actors' deliberate and focused approach is demonstrated by the deceptive usage of a ZIP archive that is camouflaged and paired with a sophisticated instance of the Go Stealer virus. An additional level of complication is introduced by integrating Slack for covert communication. Increased awareness, strict installation guidelines, and thorough cybersecurity education for government employees are necessary to reduce these threats. In the digital age, protecting national security necessitates ongoing adaptation as well as safeguards toward ever-more potent and cunning cyber threats.
References
- https://www.overtoperator.com/p/indianairforcemalwaretargetpotential
- https://cyberunfolded.in/blog/indian-air-force-targeted-in-sophisticated-cyber-attack-with-su-30-procurement-zip-file#go-stealer-a-closer-look-at-its-malicious-history
- https://thecyberexpress.com/cyberattack-on-the-indian-air-force/https://therecord.media/indian-air-force-infostealing-malware
Executive Summary
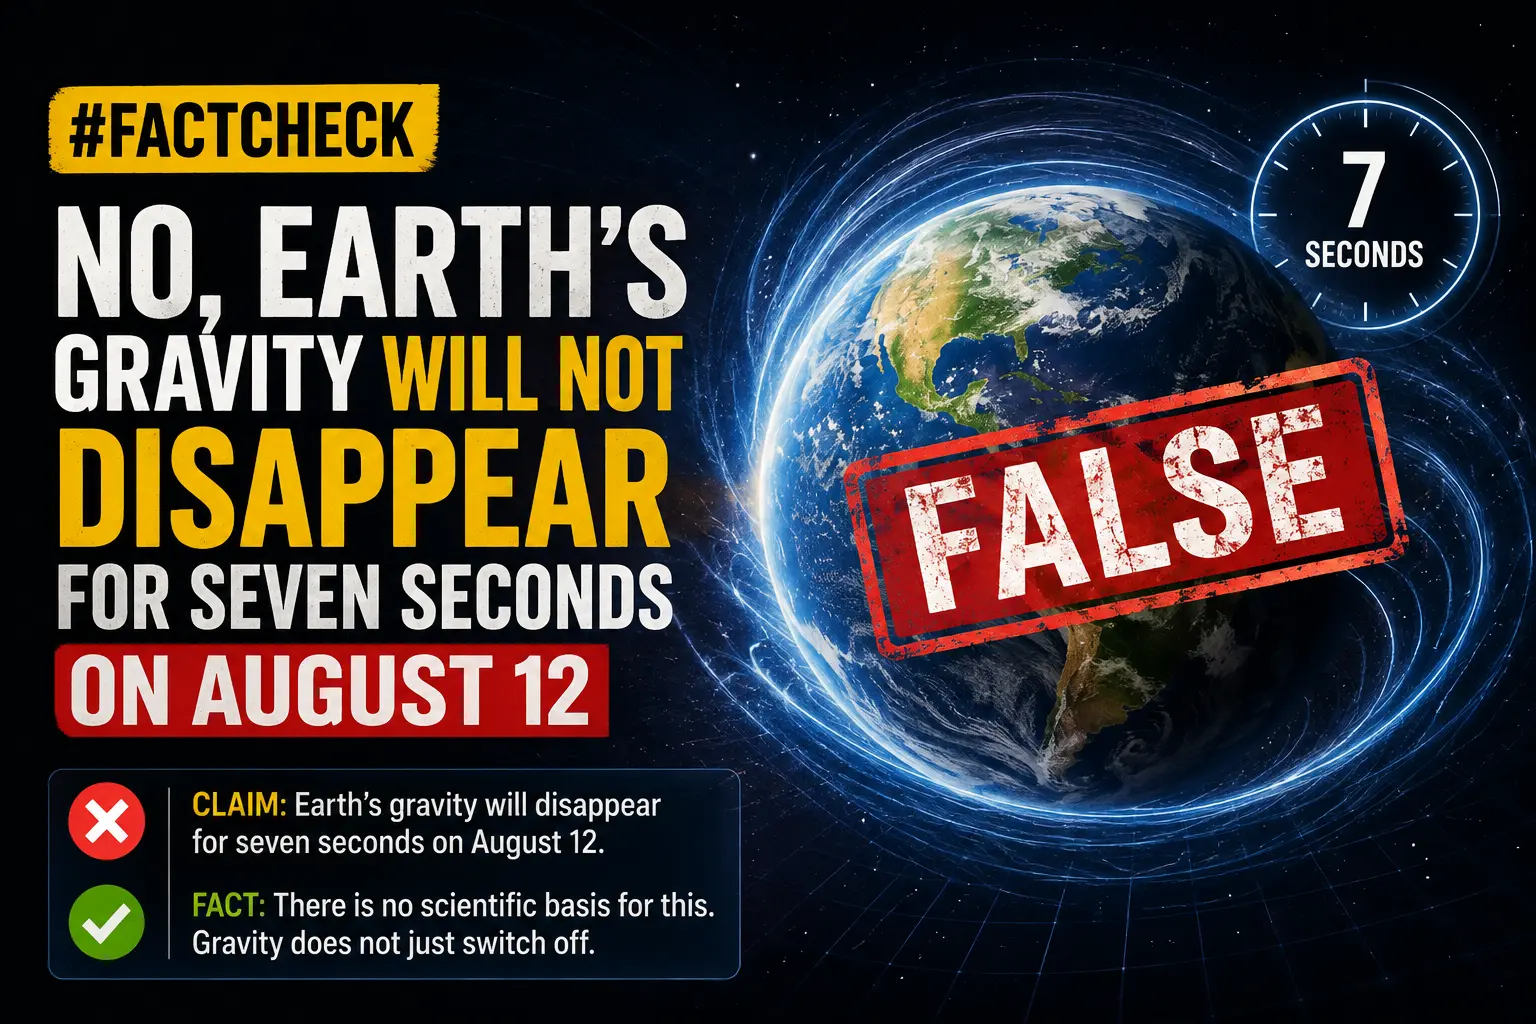
A claim is going viral across social media platforms stating that Earth’s gravity will disappear for seven seconds on the night of August 12, 2026, causing people to feel as if they are floating in the air. According to the viral posts, the phenomenon will occur due to a leaked confidential document related to the US space agency NASA’s alleged “Project Anchor.” The CyberPeace Research Wing found the claim to be false. The National Aeronautics and Space Administration (NASA) has denied that Earth’s gravity will disappear for seven seconds on August 12. According to NASA, the astronomical event taking place on August 12 is a total solar eclipse visible from parts of the Northern Hemisphere, which will not cause any unusual change in Earth’s gravity.
Claim
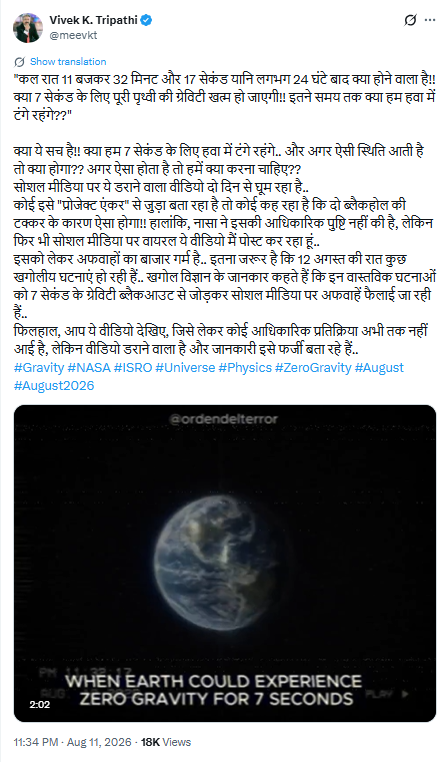
X user ‘Vivek K. Tripathi’ shared a post on August 11, 2026, asking whether Earth’s gravity would disappear for seven seconds at 11:32:17 p.m. the following night, causing people to remain suspended in the air.
The post also claimed that some social media users were linking the alleged phenomenon to “Project Anchor” or the collision of two black holes, while acknowledging that NASA had not officially confirmed the claim.
https://x.com/meevkt/status/2087238637687869773?s=20
FactCheck
To verify the claim, we conducted both basic and advanced searches for information related to NASA’s alleged “Project Anchor” and the supposed leaked document. However, we could not find any credible source confirming the existence of such a project or document. Information about NASA’s projects is available through its official database.
We then checked NASA’s official website and social media accounts for any announcement regarding Earth’s gravity disappearing on August 12. We found no such information. Instead, an August 12, 2026 post by NASA discussed the astronomical event of a total solar eclipse visible from parts of the Northern Hemisphere.
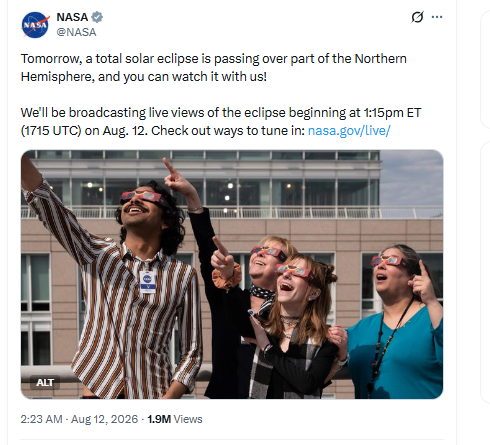
According to a NASA spokesperson quoted by Snopes, Earth’s gravity will not disappear on August 12, 2026. The spokesperson explained that Earth’s gravity is determined by its mass. It could only disappear if the total mass of Earth—including its core, mantle, crust, oceans, surface water and atmosphere—were to disappear. A total solar eclipse does not cause any unusual effect on Earth’s gravity. The gravitational pull of the Sun and Moon does not affect Eart
https://www.snopes.com/fact-check/nasa-project-anchor-earth-gravity/
Conclusion
The claim that Earth’s gravity will disappear for seven seconds on the night of August 12, 2026, is false. The claim is based on an unfounded online conspiracy theory involving the fictitious “Project Anchor.” NASA has also rejected the alleged “gravity blackout” claim. The actual astronomical event taking place on August 12 is a total solar eclipse visible from parts of the Northern Hemisphere, which will not cause any unusual change in Earth’s gravity. While the Sun and Moon exert gravitational forces that influence tides, they do not cause Earth’s overall gravity to disappear.
