
#FactCheck-Phishing Scam-LPG dealership of Hindustan Petroleum
Executive Summary:
Our team has come across a recent social media post highlighting a report on fraudulent activities involving deceptive websites and emails impersonating India’s Oil Marketing Companies (OMCs). These phishing scams falsely promise LPG distributorships and retail outlet dealerships, aiming to extract money and personal information from unsuspecting individuals. We strongly urge the public to exercise caution and verify all information exclusively through official OMC channels to avoid falling victim to such fraudulent schemes.

Claim:
It has been reported that fraudsters are impersonating Indian Oil, Bharat Petroleum, and Hindustan Petroleum through fake websites and emails, promising LPG distributorships and seeking money from victims.

Fact Check:
After our research, we came upon more information about this topic and found out that the Press Information Bureau (PIB) has released an official notice confirming that fraudulent websites and emails are impersonating India's Oil Marketing Companies (OMCs), which include Indian Oil Corporation Ltd., Bharat Petroleum Corporation Ltd., and Hindustan Petroleum Corporation Ltd. The scams falsely promise LPG distributorships and retail outlet dealerships while demanding large sums of money from unsuspecting individuals. On June 19, 2019, this was confirmed. The PIB highlighted that OMCs have not allowed any person or organization to charge a fee for dealership selection. All authentic information on these offers is available at the websites of the OMCs: www.iocl.com, www.bharatpetroleum.com, and www.hindustanpetroleum.com. The general public is cautioned to rely only on these sources and report suspicious approaches to the offices of concerned OMCs. If someone finds such an approach, he should immediately contact the cybercrime branch. HPCL has issued alerts on fake websites and emails that promise LPG distributorships and jobs, mimicking official HPCL sites to deceive people.

On the official website of HPCL list down the malicious URLs. They are mentioned below:
- https://kskdealerchayan.com/
- bajajgas.com/index
- hindustanbiofuel.in
- petrolpumpchayanonline.com
- dealerchayanpetrolpump.in
- petrolpumpdealarchayan.com
- petrolpumpsdealerchayan.co.in
- petrolpumpdealershipchayan.org.in
- petrolpumpdealerchayangov.in
- petrolpumpdealership.info
- petrolpumpsdealershipchayan.in
- allindiagasdealership.com
- hindustanpetroleum.online
- hindustanpetroleumcorp.com
- hpcldelership.com
- ujjwalalpgvitarak.org
- ujjwaladealership.com
- lpgvitrakkendra.com
- kissansevakendra.org
- lpgvitarakchayanltd.org
- petrolpumpdelerchayan.in
- petrolpumpdealerschayan.in
- petrolepumpsdelearchayan.in
- kissansevakendra.org
- petrolpumpdealerchayanpro.com
- petrolpumchayanweb.com
- onlinepetrolpumpdealerchayan.com/
HPCL also shared an advisory for their applicants regarding Beware Of Fraudsters.


Conclusion:
It has been proven that fraud offers for LPG distributorships and retail outlet dealerships are being made through fake websites and emails. To avoid such scams, people are advised to be more vigilant, verify all information through official OMC platforms, and immediately report any suspicious activities to the concerned authorities. Being alert and informed is the key to preventing financial loss and protecting personal data from exploitation.
- Claim: Is this HPCL approval letter for an LPG agency dealership legit?
- Claimed On: Social Media
- Fact Check: False and Misleading

Related Blogs

Introduction
In April 2026, a class action suit in a federal court in California rejuvenated one of the most basic assertions in digital communication: that private messages are private. The suit claims that Meta Platforms, its subsidiary WhatsApp, and third-party contractors such as Accenture could have accessed user messages even though it had long promised end-to-end encryption.
This case is not merely about a single company or a single platform. It poses more profound questions regarding the definition, communication and regulation of privacy in an age when digital infrastructure is becoming more and more incomprehensible or unprovable to regular users.
What the Lawsuit Actually Says
The suit was filed by plaintiffs Brian Y. Shirazi and Nida Samson, who alleged that WhatsApp, Meta and contractors had intercepted and shared private messages with third parties without their consent. The complaint states that the federal investigators were notified by the whistleblowers that employees of Meta and external contractors had access to the content of WhatsApp messages that were expected to be encrypted and inaccessible.
This directly puts into question the main privacy promise of WhatsApp. The platform has been promoting itself as an end-to-end encrypted service in which not even WhatsApp can read your messages. The case asserts that this assertion was deceptive in its application and that no one ever gave any consent prior to their messages being intercepted, stored, or read.
The plaintiffs are proposing to represent a nationwide class of users of WhatsApp who sent or received messages between April 5, 2016, and the current time and subclasses in California and Pennsylvania. The claims involve breach of contract, California laws on privacy and data violations, false advertising and the Pennsylvania Wiretapping and Electronic Surveillance Act.
It should be mentioned that they are allegations. Similar assertions have been refuted by Metacomet in the past, with the company asserting that its encryption frameworks ensure that the company cannot access the messages. The case is in progress, and no facts have been found.
The Grey Area No One Talks About
In order to see the significance of this lawsuit outside the court, it is useful to consider the way modern messaging platforms actually work. In principle, end-to-end encryption means that only the sender and receiver can decipher a message. Even the service provider should not be able to access the content.
However, there is a grey space that is seldom publicly discussed: content moderation. User reports, metadata analysis or restricted message review processes are common methods used by platforms to identify harmful content, like fraud, child exploitation, or spam. The complaint indicates that such moderation procedures might have opened avenues to the content of messages to human reviewers or automated systems more than users were made to think.
This is not the first time that privacy and safety are at odds. Many jurisdictions have also advocated access to encrypted communications through legal means in the name of national security or criminal investigations. What this suit does is put that tension into even more stark relief by asking whether platforms are really open with users about these trade-offs.
The Consent Problem
The emphasis on consent is one of the most significant implications of this case. The plaintiffs claim that the users were never warned that their messages would be accessed by the employees or third parties and were never provided with any meaningful option on the same.
This is where the case turns into a data governance issue, rather than a legal one. Most data protection models consider the legality of data processing to be based on whether the users know how their data is being processed or not. When the accusations are found to be true, then the matter is not technical. It would be a contractual and ethical failure, a disjuncture between what platforms promise and what they do.
The implications are huge to the billions of users who use WhatsApp to communicate, both personally and professionally, and even politically.
What This Means Going Forward
An effective attack on the encryption assertions of WhatsApp might have actual implications for the rest of the digital ecosystem. Users might start doubting that any platform can be really considered to guarantee privacy. The regulators can advocate more stringent disclosure policies and compulsory independent audits of encryption systems. Social networks might have to re-architect their moderation frameworks to make sure that safety features do not silently compromise privacy guarantees that they claim.
Meanwhile, there is a real policy dilemma in this case that cannot be disregarded. Complete privacy may preclude the capacity to identify abuse or hateful material. The manner in which that balance is achieved and, more to the point, the manner in which it is made transparent to users is an issue that has yet to be addressed by policymakers, civil society and the tech industry.
Other technical experts have also questioned the plausibility of the claims in the lawsuit at scale, noting that it would be an extraordinary undertaking to systematically bypass end-to-end encryption. This further supports the argument of independent verification mechanisms. The problem is that users should not be forced to decide what they should believe in more: corporate guarantees or legal charges. There must be rules that can be enforced which are above the two.
Conclusion: Beyond One Lawsuit
The WhatsApp class action is eventually concerning a structural issue within the digital economy. Users are expected to have faith in systems that they cannot observe, on the assertions that they cannot test themselves.
This case is a warning, regardless of whether the allegations are proved or not. Privacy cannot be based on marketing language. It needs legally binding norms, actual transparency in the treatment of data, and external control that will provide users with something more to hang on than a tagline.
References
- https://www.bitdefender.com/en-us/blog/hotforsecurity/lawsuit-claims-meta-can-access-whatsapp-messages-despite-end-to-end-encryption-2
- https://blog.cryptographyengineering.com/2026/02/02/whatsapp-encryption-a-lawsuit-and-a-lot-of-noise/
- https://www.bloomberg.com/news/articles/2026-01-25/lawsuit-claims-meta-can-see-whatsapp-chats-in-breach-of-privacy
- https://www.classaction.org/blog/despite-privacy-promises-meta-third-parties-read-and-store-whatsapp-messages-class-action-lawsuit-alleges
Executive Summary
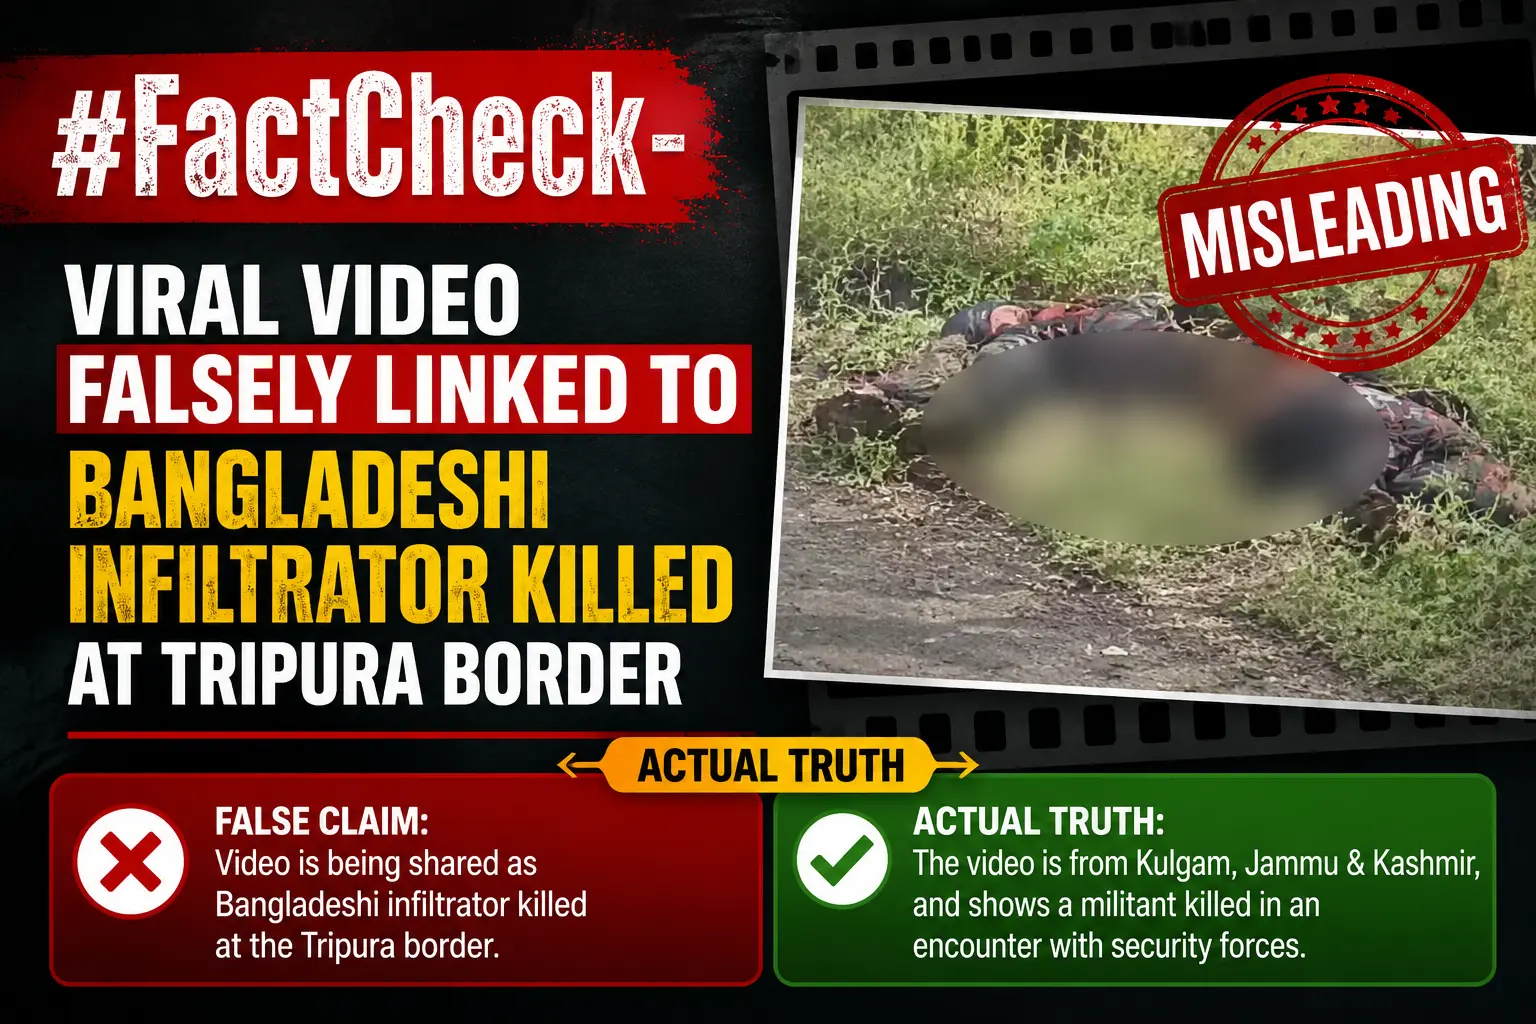
A video circulating on social media is being shared with the claim that the Border Security Force (BSF) shot dead a Bangladeshi national who was attempting to infiltrate India through the Tripura border. CyberPeace Research Wing research found the claim to be misleading. The viral video is not related to any recent incident on the Tripura border. It actually shows Haris Nazir Dar, a militant who was killed during an encounter in Jammu and Kashmir’s Kulgam district last year.
Claim:
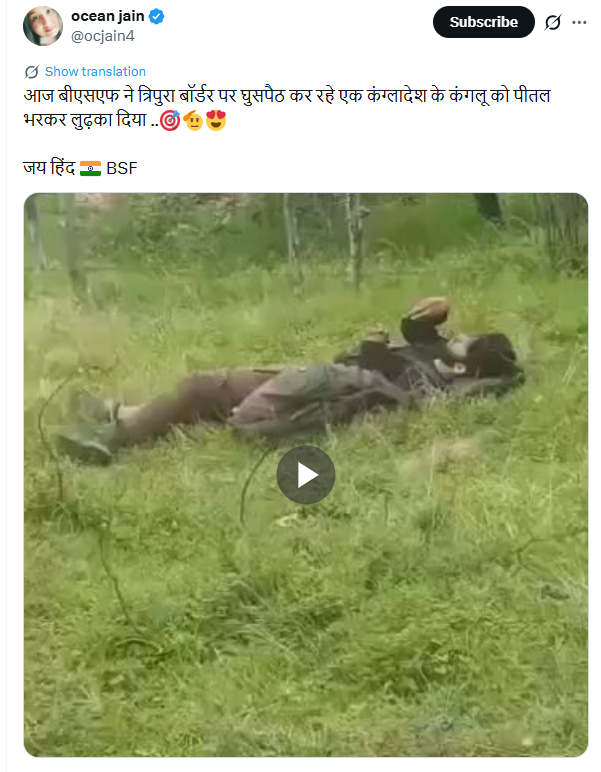
The viral clip, which is around eight seconds long, shows a body lying on the ground. It is being shared on X with captions suggesting that the deceased was a Bangladeshi infiltrator who was killed while attempting to cross the India-Bangladesh border in Tripura.
https://x.com/ocjain4/status/2066210317265457298
Fact Check:
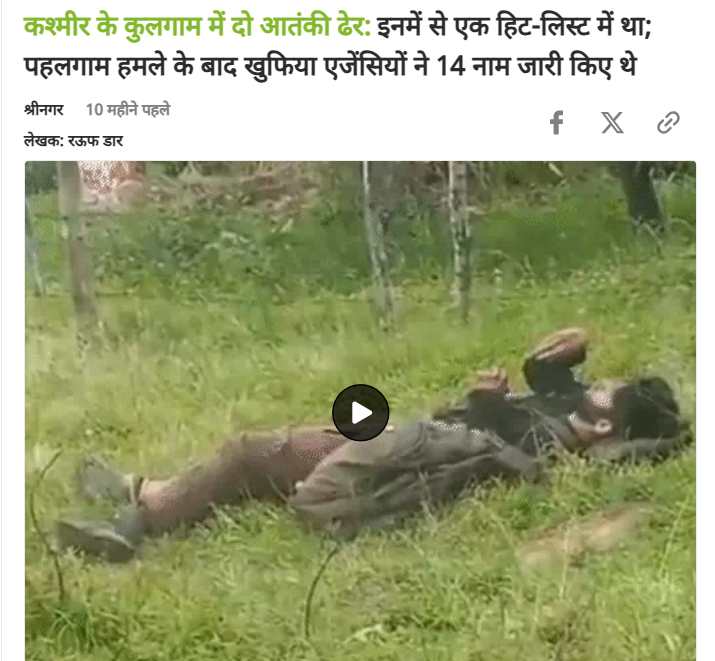
To verify the claim, we extracted keyframes from the viral video and conducted a reverse image search. During the research, we found matching visuals in a report published by Dainik Bhaskar on August 2, 2025. The report was related to an encounter between security forces and militants in the Akhal forest area of Kulgam district in Jammu and Kashmir. Visuals in the report matched those seen in the viral video.
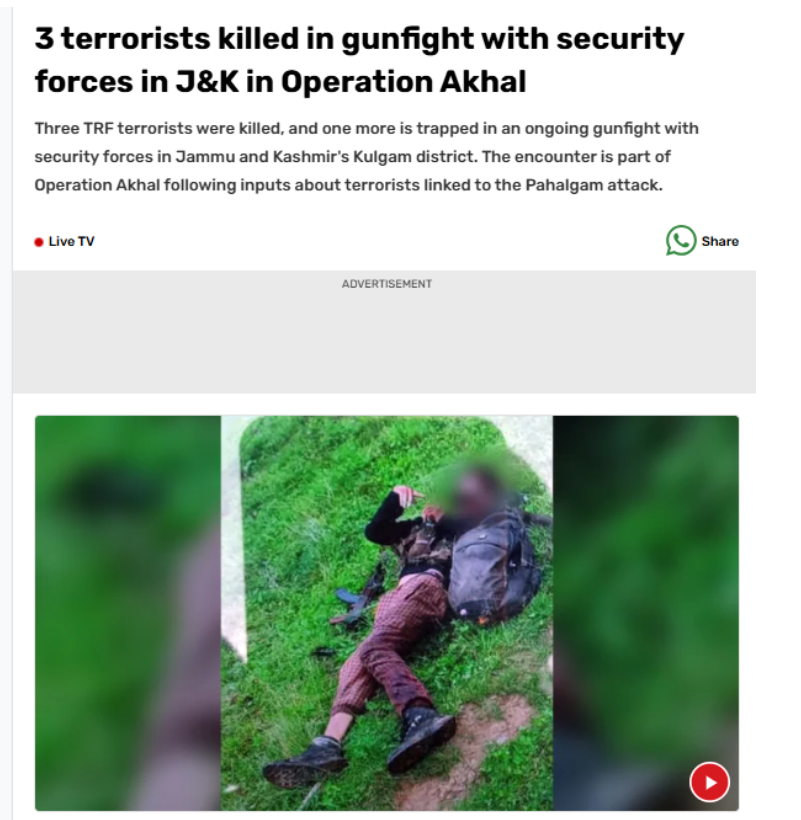
We also found a report published by India Today on August 2, 2025, which carried photographs of slain militant Haris Nazir Dar taken from a different angle. The report stated that security forces had killed three militants during the operation in the Akhal forest area of Kulgam. https://www.indiatoday.in/india/story/gunfight-underway-with-3-lashkar-terrorists-in-jks-kulgam-2764971-2025-08-01
Conclusion:
The evidence gathered during our research makes it clear that the viral video does not show a Bangladeshi infiltrator killed at the Tripura border. The footage is actually from a security operation in Jammu and Kashmir and shows Haris Nazir Dar, a militant who was killed in an encounter in Kulgam last year.

Introduction
The G7 nations, a group of the most powerful economies, have recently turned their attention to the critical issue of cybercrimes and (AI) Artificial Intelligence. G7 summit has provided an essential platform for discussing the threats and crimes occurring from AI and lack of cybersecurity. These nations have united to share their expertise, resources, diplomatic efforts and strategies to fight against cybercrimes. In this blog, we shall investigate the recent development and initiatives undertaken by G7 nations, exploring their joint efforts to combat cybercrime and navigate the evolving landscape of artificial intelligence. We shall also explore the new and emerging trends in cybersecurity, providing insights into ongoing challenges and innovative approaches adopted by the G7 nations and the wider international community.
G7 Nations and AI
Each of these nations have launched cooperative efforts and measures to combat cybercrime successfully. They intend to increase their collective capacities in detecting, preventing, and responding to cyber assaults by exchanging intelligence, best practices, and experience. G7 nations are attempting to develop a strong cybersecurity architecture capable of countering increasingly complex cyber-attacks through information-sharing platforms, collaborative training programs, and joint exercises.
The G7 Summit provided an important forum for in-depth debates on the role of artificial intelligence (AI) in cybersecurity. Recognising AI’s transformational potential, the G7 nations have participated in extensive discussions to investigate its advantages and address the related concerns, guaranteeing responsible research and use. The nation also recognises the ethical, legal, and security considerations of deploying AI cybersecurity.
Worldwide Rise of Ransomware
High-profile ransomware attacks have drawn global attention, emphasising the need to combat this expanding threat. These attacks have harmed organisations of all sizes and industries, leading to data breaches, operational outages, and, in some circumstances, the loss of sensitive information. The implications of such assaults go beyond financial loss, frequently resulting in reputational harm, legal penalties, and service delays that affect consumers, clients, and the public. The increase in high-profile ransomware incidents has garnered attention worldwide, Cybercriminals have adopted a multi-faceted approach to ransomware attacks, combining techniques such as phishing, exploit kits, and supply chain Using spear-phishing, exploit kits, and supply chain hacks to obtain unauthorised access to networks and spread the ransomware. This degree of expertise and flexibility presents a substantial challenge to organisations attempting to protect against such attacks.

Focusing On AI and Upcoming Threats
During the G7 summit, one of the key topics for discussion on the role of AI (Artificial Intelligence) in shaping the future, Leaders and policymakers discuss the benefits and dangers of AI adoption in cybersecurity. Recognising AI’s revolutionary capacity, they investigate its potential to improve defence capabilities, predict future threats, and secure vital infrastructure. Furthermore, the G7 countries emphasise the necessity of international collaboration in reaping the advantages of AI while reducing the hazards. They recognise that cyber dangers transcend national borders and must be combated together. Collaboration in areas such as exchanging threat intelligence, developing shared standards, and promoting best practices is emphasised to boost global cybersecurity defences. The G7 conference hopes to set a global agenda that encourages responsible AI research and deployment by emphasising the role of AI in cybersecurity. The summit’s sessions present a path for maximising AI’s promise while tackling the problems and dangers connected with its implementation.
As the G7 countries traverse the complicated convergence of AI and cybersecurity, their emphasis on collaboration, responsible practices, and innovation lays the groundwork for international collaboration in confronting growing cyber threats. The G7 countries aspire to establish robust and secure digital environments that defend essential infrastructure, protect individuals’ privacy, and encourage trust in the digital sphere by collaboratively leveraging the potential of AI.
Promoting Responsible Al development and usage
The G7 conference will focus on developing frameworks that encourage ethical AI development. This includes fostering openness, accountability, and justice in AI systems. The emphasis is on eliminating biases in data and algorithms and ensuring that AI technologies are inclusive and do not perpetuate or magnify existing societal imbalances.
Furthermore, the G7 nations recognise the necessity of privacy protection in the context of AI. Because AI systems frequently rely on massive volumes of personal data, summit speakers emphasise the importance of stringent data privacy legislation and protections. Discussions centre around finding the correct balance between using data for AI innovation, respecting individuals’ privacy rights, and protecting data security. In addition to responsible development, the G7 meeting emphasises the importance of responsible AI use. Leaders emphasise the importance of transparent and responsible AI governance frameworks, which may include regulatory measures and standards to ensure AI technology’s ethical and legal application. The goal is to defend individuals’ rights, limit the potential exploitation of AI, and retain public trust in AI-driven solutions.
The G7 nations support collaboration among governments, businesses, academia, and civil society to foster responsible AI development and use. They stress the significance of sharing best practices, exchanging information, and developing international standards to promote ethical AI concepts and responsible practices across boundaries. The G7 nations hope to build the global AI environment in a way that prioritises human values, protects individual rights, and develops trust in AI technology by fostering responsible AI development and usage. They work together to guarantee that AI is a force for a good while reducing risks and resolving social issues related to its implementation.
Challenges on the way
During the summit, the nations, while the G7 countries are committed to combating cybercrime and developing responsible AI development, they confront several hurdles in their efforts. Some of them are:
A Rapidly Changing Cyber Threat Environment: Cybercriminals’ strategies and methods are always developing, as is the nature of cyber threats. The G7 countries must keep up with new threats and ensure their cybersecurity safeguards remain effective and adaptable.
Cross-Border Coordination: Cybercrime knows no borders, and successful cybersecurity necessitates international collaboration. On the other hand, coordinating activities among nations with various legal structures, regulatory environments, and agendas can be difficult. Harmonising rules, exchanging information, and developing confidence across states are crucial for effective collaboration.
Talent Shortage and Skills Gap: The field of cybersecurity and AI knowledge necessitates highly qualified personnel. However, skilled individuals in these fields need more supply. The G7 nations must attract and nurture people, provide training programs, and support research and innovation to narrow the skills gap.
Keeping Up with Technological Advancements: Technology changes at a rapid rate, and cyber-attacks become more complex. The G7 nations must ensure that their laws, legislation, and cybersecurity plans stay relevant and adaptive to keep up with future technologies such as AI, quantum computing, and IoT, which may both empower and challenge cybersecurity efforts.
Conclusion
To combat cyber threats effectively, support responsible AI development, and establish a robust cybersecurity ecosystem, the G7 nations must constantly analyse and adjust their strategy. By aggressively tackling these concerns, the G7 nations can improve their collective cybersecurity capabilities and defend their citizens’ and global stakeholders’ digital infrastructure and interests.
