
#FactCheck: Fake Viral Video Claiming Vice Admiral AN Pramod saying that next time if Pakistan Attack we will complain to US and Prez Trump.
Executive Summary:
A viral video (archived link) circulating on social media claims that Vice Admiral AN Pramod stated India would seek assistance from the United States and President Trump if Pakistan launched an attack, portraying India as dependent rather than self-reliant. Research traced the extended footage to the Press Information Bureau’s official YouTube channel, published on 11 May 2025. In the authentic video, the Vice Admiral makes no such remark and instead concludes his statement with, “That’s all.” Further analysis using the AI Detection tool confirmed that the viral clip was digitally manipulated with AI-generated audio, misrepresenting his actual words.
Claim:
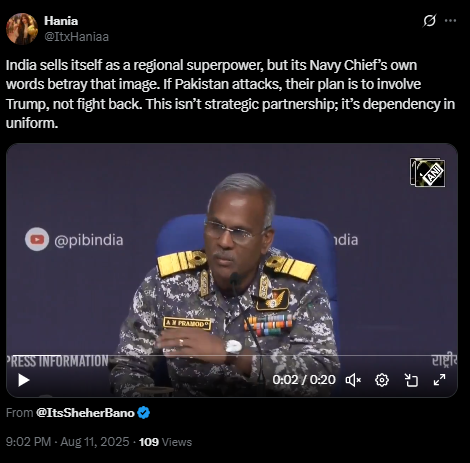
In the viral video an X user posted with the caption
”India sells itself as a regional superpower, but its Navy Chief’s own words betray that image. If Pakistan attacks, their plan is to involve Trump, not fight back. This isn’t strategic partnership; it’s dependency in uniform”.
In the video the Vice Admiral was heard saying
“We have worked out among three services, this time if Pakistan dares take any action, and Pakistan knows it, what we are going to do. We will complain against Pakistan to the United States of America and President Trump, like we did earlier in Operation Sindoor.”
Fact Check:
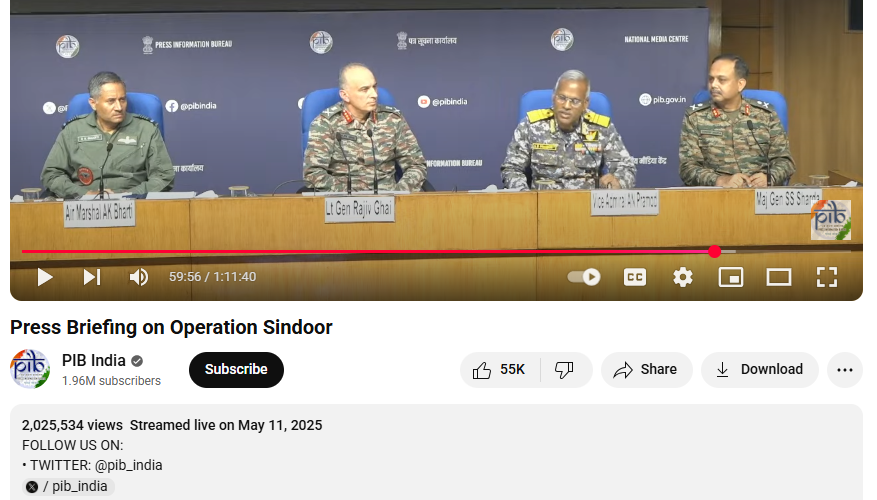
Upon conducting a reverse image search on key frames from the video, we located the full version of the video on the official YouTube channel of the Press Information Bureau (PIB), published on 11 May 2025. In this video, at the 59:57-minute mark, the Vice Admiral can be heard saying:
“This time if Pakistan dares take any action, and Pakistan knows it, what we are going to do. That’s all.”
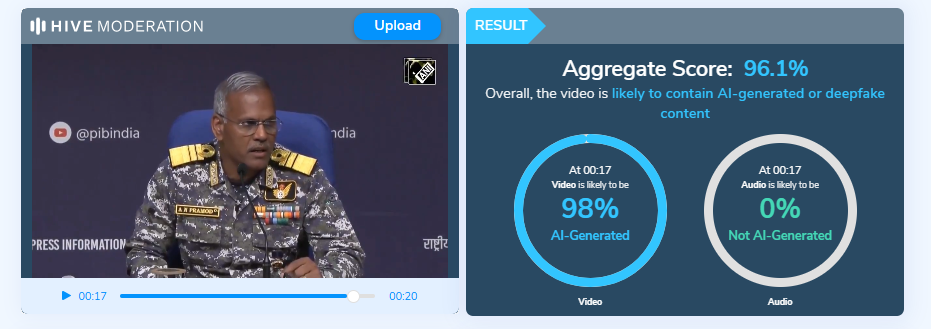
Further analysis was conducted using the Hive Moderation tool to examine the authenticity of the circulating clip. The results indicated that the video had been artificially generated, with clear signs of AI manipulation. This suggests that the content was not genuine but rather created with the intent to mislead viewers and spread misinformation.
Conclusion:
The viral video attributing remarks to Vice Admiral AN Pramod about India seeking U.S. and President Trump’s intervention against Pakistan is misleading. The extended speech, available on the Press Information Bureau’s official YouTube channel, contained no such statement. Instead of the alleged claim, the Vice Admiral concluded his comments by saying, “That’s all.” AI analysis using Hive Moderation further indicated that the viral clip had been artificially manipulated, with fabricated audio inserted to misrepresent his words. These findings confirm that the video is altered and does not reflect the Vice Admiral’s actual remarks.
Claim: Fake Viral Video Claiming Vice Admiral AN Pramod saying that next time if Pakistan Attack we will complain to US and Prez Trump.
Claimed On: Social Media
Fact Check: False and Misleading

Related Blogs

What are Deepfakes?
A deepfake is essentially a video of a person in which their face or body has been digitally altered so that they appear to be someone else, typically used maliciously or to spread false information. Deepfake technology is a method for manipulating videos, images, and audio utilising powerful computers and deep learning. It is used to generate fake news and commit financial fraud, among other wrongdoings. It overlays a digital composite over an already-existing video, picture, or audio; cybercriminals use Artificial Intelligence technology. The term deepfake was coined first time in 2017 by an anonymous Reddit user, who called himself deepfake.
Deepfakes works on a combination of AI and ML, which makes the technology hard to detect by Web 2.0 applications, and it is almost impossible for a layman to see if an image or video is fake or has been created using deepfakes. In recent times, we have seen a wave of AI-driven tools which have impacted all industries and professions across the globe. Deepfakes are often created to spread misinformation. There lies a key difference between image morphing and deepfakes. Image morphing is primarily used for evading facial recognition, but deepfakes are created to spread misinformation and propaganda.
Issues Pertaining to Deepfakes in India
Deepfakes are a threat to any nation as the impact can be divesting in terms of monetary losses, social and cultural unrest, and actions against the sovereignty of India by anti-national elements. Deepfake detection is difficult but not impossible. The following threats/issues are seen to be originating out of deep fakes:
- Misinformation: One of the biggest issues of Deepfake is misinformation, the same was seen during the Russia-Ukraine conflict, where in a deepfake of Ukraine’s president, Mr Zelensky, surfaced on the internet and caused mass confusion and propaganda-based misappropriation among the Ukrainians.
- Instigation against the Union of India: Deepfake poses a massive threat to the integrity of the Union of India, as this is one of the easiest ways for anti-national elements to propagate violence or instigate people against the nation and its interests. As India grows, so do the possibilities of anti-national attacks against the nation.
- Cyberbullying/ Harassment: Deepfakes can be used by bad actors to harass and bully people online in order to extort money from them.
- Exposure to Illicit Content: Deepfakes can be easily used to create illicit content, and oftentimes, it is seen that it is being circulated on online gaming platforms where children engage the most.
- Threat to Digital Privacy: Deepfakes are created by using existing videos. Hence, bad actors often use photos and videos from Social media accounts to create deepfakes, this directly poses a threat to the digital privacy of a netizen.
- Lack of Grievance Redressal Mechanism: In the contemporary world, the majority of nations lack a concrete policy to address the aspects of deepfake. Hence, it is of paramount importance to establish legal and industry-based grievance redressal mechanisms for the victims.
- Lack of Digital Literacy: Despite of high internet and technology penetration rates in India, digital literacy lags behind, this is a massive concern for the Indian netizens as it takes them far from understanding the tech, which results in the under-reporting of crimes. Large-scale awareness and sensitisation campaigns need to be undertaken in India to address misinformation and the influence of deepfakes.
How to spot deepfakes?
Deepfakes look like the original video at first look, but as we progress into the digital world, it is pertinent to establish identifying deepfakes in our digital routine and netiquettes in order to stay protected in the future and to address this issue before it is too late. The following aspects can be kept in mind while differentiating between a real video and a deepfake
- Look for facial expressions and irregularities: Whenever differentiating between an original video and deepfake, always look for changes in facial expressions and irregularities, it can be seen that the facial expressions, such as eye movement and a temporary twitch on the face, are all signs of a video being a deepfake.
- Listen to the audio: The audio in deepfake also has variations as it is imposed on an existing video, so keep a check on the sound effects coming from a video in congruence with the actions or gestures in the video.
- Pay attention to the background: The most easiest way to spot a deepfake is to pay attention to the background, in all deepfakes, you can spot irregularities in the background as, in most cases, its created using virtual effects so that all deepfakes will have an element of artificialness in the background.
- Context and Content: Most of the instances of deepfake have been focused towards creating or spreading misinformation hence, the context and content of any video is an integral part of differentiating between an original video and deepfake.
- Fact-Checking: As a basic cyber safety and digital hygiene protocol, one should always make sure to fact-check each and every piece of information they come across on social media. As a preventive measure, always make sure to fact-check any information or post sharing it with your known ones.
- AI Tools: When in doubt, check it out, and never refrain from using Deepfake detection tools like- Sentinel, Intel’s real-time deepfake detector - Fake catcher, We Verify, and Microsoft’s Video Authenticator tool to analyze the videos and combating technology with technology.
Recent Instance
A deepfake video of actress Rashmika Mandanna recently went viral on social media, creating quite a stir. The video showed a woman entering an elevator who looked remarkably like Mandanna. However, it was later revealed that the woman in the video was not Mandanna, but rather, her face was superimposed using AI tools. Some social media users were deceived into believing that the woman was indeed Mandanna, while others identified it as an AI-generated deepfake. The original video was actually of a British-Indian girl named Zara Patel, who has a substantial following on Instagram. This incident sparked criticism from social media users towards those who created and shared the video merely for views, and there were calls for strict action against the uploaders. The rapid changes in the digital world pose a threat to personal privacy; hence, caution is advised when sharing personal items on social media.
Legal Remedies
Although Deepfake is not recognised by law in India, it is indirectly addressed by Sec. 66 E of the IT Act, which makes it illegal to capture, publish, or transmit someone's image in the media without that person's consent, thus violating their privacy. The maximum penalty for this violation is ₹2 lakh in fines or three years in prison. The DPDP Act's applicability in 2023 means that the creation of deepfakes will directly affect an individual's right to digital privacy and will also violate the IT guidelines under the Intermediary Guidelines, as platforms will be required to exercise caution while disseminating and publishing misinformation through deepfakes. The indirect provisions of the Indian Penal Code, which cover the sale and dissemination of derogatory publications, songs and actions, deception in the delivery of property, cheating and dishonestly influencing the delivery of property, and forgery with the intent to defame, are the only legal remedies available for deepfakes. Deep fakes must be recognized legally due to the growing power of misinformation. The Data Protection Board and the soon-to-be-established fact-checking body must recognize crimes related to deepfakes and provide an efficient system for filing complaints.
Conclusion
Deepfake is an aftermath of the advancements of Web 3.0 and, hence is just the tip of the iceberg in terms of the issues/threats from emerging technologies. It is pertinent to upskill and educate the netizens about the keen aspects of deepfakes to stay safe in the future. At the same time, developing and developed nations need to create policies and laws to efficiently regulate deepfake and to set up redressal mechanisms for victims and industry. As we move ahead, it is pertinent to address the threats originating out of the emerging techs and, at the same time, create a robust resilience for the same.
References
Introduction
Imagine receiving a WhatsApp message from your CEO late on a Friday afternoon. The message is urgent: a confidential business deal requires an immediate wire transfer before markets close. The profile picture matches, the tone sounds familiar, and the account it came from has your CEO's name on it. Everything appears legitimate except it is not. This is the essence of the 'Boss Scam,' a sophisticated form of CEO impersonation fraud that has emerged as one of the most financially devastating cybercrime trends of 2025. India's Indian Cyber Crime Coordination Centre (I4C), under the Ministry of Home Affairs, issued an urgent national advisory on this threat in June 2025, warning that organisations across the country are falling victim to an evolved and technically advanced version of executive impersonation fraud that bypasses many traditional cybersecurity safeguards.
Understanding the Boss Scam
What Is CEO Impersonation Fraud?
CEO fraud, also known as Business Email Compromise (BEC) or executive impersonation fraud, is a targeted cyberattack in which criminals assume the digital identity of a high-ranking executive most commonly the Chief Executive Officer to deceive subordinate employees into authorising fraudulent financial transactions or divulging sensitive information. Unlike generic phishing campaigns that cast a wide net, CEO fraud is a precision attack. Cybercriminals invest significant time and resources researching their targets, studying organisational hierarchies, communication styles, and internal financial workflows before executing the scam. The attack is devastatingly effective because it weaponises one of the most powerful forces in any workplace: authority. An instruction that appears to originate from the CEO carries an implicit demand for immediate compliance, often bypassing normal checks and verification procedures. The FBI's Internet Crime Complaint Center (IC3) has consistently identified BEC as one of the most financially destructive categories of cybercrime, with adjusted losses of approximately USD 2.77 billion reported in 2024 alone across the United States.
The New and Evolved Variant: India's I4C Advisory
The variant identified by India's I4C represents a dangerous evolution of traditional CEO fraud. The earlier versions of this scam relied on spoofed email addresses or fake WhatsApp profiles that merely mimicked an executive's account. Employees were trained to spot tell-tale warning signs suspicious domains, unusual sender addresses, or spelling errors in email IDs. The latest
Boss Scam variant eliminates many of these red flags entirely by hijacking the executive's actual and legitimate WhatsApp account. This sophisticated attack begins not with the employee, but with the CEO. Cybercriminals approach senior executives through email or WhatsApp while posing as regulatory authorities in India's context, this includes impersonating officials from the Reserve Bank of India (RBI) or other government bodies. These messages claim an urgent compliance violation or regulatory breach requiring immediate remedial action. The communication contains a compressed ZIP archive, which the executive is prompted to open. Inside the archive are malicious executable (.exe) and Dynamic Link Library (.dll) files that, when run on a Windows system, deploy a Trojan dropper a form of malware capable of establishing persistent access on the device and hijacking active WhatsApp Web session tokens.
Once the session token is compromised, the attacker gains complete control over the executive's WhatsApp account without needing the phone, password, or any two-factor authentication code. The legitimate account is now in criminal hands, and any message sent from it appears entirely authentic to recipients.
How the Boss Scam Operates: A Step-by-Step Breakdown
Stage 1: Targeting the Executive: The operation begins with careful reconnaissance. Attackers study the target organisation's leadership, identify the CEO or a senior executive, and gather publicly available information about their communication patterns, business relationships, and company operations through LinkedIn, corporate websites, and news sources. They then contact the executive under a false regulatory identity, engineering a sense of crisis and urgency.
Stage 2: Malware Deployment:The fraudulent regulatory communication contains a ZIP file disguised as a compliance document, a security patch, or a mandatory software update. Upon execution on a Windows machine, the embedded malware installs itself and begins hijacking the WhatsApp Web session. Critically, in many documented cases, the CEO innocently forwards this regulatory message and the malicious attachment to their own finance officer or IT team, inadvertently widening the attack surface.
Stage 3: Account Takeover and Impersonation:With the CEO's legitimate WhatsApp account now under their control, cybercriminals send highly convincing messages to subordinate staff, particularly those in finance, accounts payable, or treasury functions. These messages carry the full weight of genuine executive authority correct name, profile photo, and account history making them extraordinarily difficult to distinguish from authentic communications.
Stage 4: The Financial Strike:The fraudulent instruction typically requests an urgent, confidential wire transfer to an unfamiliar account, often accompanied by requests for complete secrecy. The employee, believing the instruction to be genuine and fearing the consequences of non-compliance with a directive from their CEO, processes the transaction. By the time the fraud is discovered, the funds have been routed through multiple mule accounts, making recovery extremely difficult.
The Broader Landscape: Scale and Impact
The Boss Scam is not an isolated Indian phenomenon it represents the cutting edge of a global epidemic of executive impersonation fraud. According to the FBI's data, BEC has been the costliest category of cybercrime for several years running, with cumulative global losses that officials have described as exceeding USD 50 billion over the past decade. A 2025 fraud survey found that 90 per cent of U.S. companies experienced attempted cyber-fraud in 2024, with business email compromise and impersonation scams surging by 103 per cent year-on-year. The technological sophistication of these attacks has grown in lockstep with the availability of AI tools. In early 2024, a finance worker at a multinational firm in Hong Kong was tricked into authorising a payment of USD 25 million after attending a video conference in which the CFO and other senior executives were entirely fabricated using deepfake technology. In March 2025, a similar attack unfolded in Singapore, where a finance director authorised nearly USD 499,000 after joining a Zoom call populated entirely by AI-generated deepfakes of company executives. Deepfake attacks against businesses reportedly surged by 3,000 per cent in 2023, and voice cloning fraud rose by 680 per cent the following year. In India, the Telangana Cyber Security Bureau reported over 300 complaints related to the Boss Scam variant alone within a twenty-day period in June 2025. In one prominent case, formerPrime Minister I.K. Gujral's son, Naresh Gujral, reportedly lost approximately Rs 7.8 crorethrough a messaging-app impersonation scheme targeting his company's Chief Financial Officer.
Warning Signs Every Employee Must Recognise
Identifying a Boss Scam attempt requires situational awareness and healthy scepticism. The following red flags should prompt immediate caution:
● Any request for urgent or secret financial transfers received via WhatsApp or email, without prior discussion or formal documentation.
● Instructions to bypass standard approval procedures or to maintain secrecy from colleagues or senior management.
● Compressed files (.zip, .rar) or executable attachments received from any source, including apparently known contacts, claiming to be compliance documents or regulatory updates.
● Messages from executives at unusual hours, particularly those emphasising that a transaction must be completed immediately.
● Claims that a request comes from a government regulator, such as the RBI, delivered through informal channels like WhatsApp.
● Any communication that creates extreme urgency, invokes authority, and simultaneously demands confidentiality the classic triangle of social engineering manipulation. Protective Measures: Defending Against the Boss Scam
For Employees and Finance Teams
The I4C advisory and global cybersecurity authorities recommend several concrete steps that employees can take. The most important is to independently verify any urgent financial instruction through a direct voice call or in-person confirmation before taking action, regardless of how convincing the digital message appears. No financial transaction of significance should be authorised on the basis of a WhatsApp message or email alone.
For Organisations and Leadership
Organisations must implement multi-layered verification protocols for all wire transfers above a defined threshold, making dual authorisation and out-of-band verification mandatory. IT teams should deploy updated malware detection tools, enforce software restriction policies that block unauthorised executable files, and regularly audit devices for signs of compromise. WhatsApp linked devices should be reviewed periodically. Leadership must also commit to regular, mandatory cybersecurity awareness training for all staff, with particular attention to social engineering tactics. The I4C has also emphasised that legitimate regulatory bodies including the RBI , do not distribute software, compliance tools, or security patches via WhatsApp or email attachments. Any such communication must be treated as a potential attack vector and reported immediately.
Conclusion
The Boss Scam exploits organisational trust and human psychology rather than technical vulnerabilities and with deepfake technology now capable of replicating familiar voices and faces, traditional verification instincts are no longer reliable. The strongest defence is a culture of verification without embarrassment, where questioning an unusual instruction is seen as diligence, not insubordination. Awareness, clear protocols, and scepticism towards urgency remain our most powerful tools. If you've encountered such a scam, contact India's National Cybercrime Helpline at 1930 or report at cybercrime.gov.in.
References
- https://www.cybercrime.gov.in
- https://www.business-standard.com/india-news/boss-scam-ceo-impersonation-fraudgovt- advisory-i4c-126062300353_1.html
- https://www.indiatvnews.com/news/india/boss-scam-all-about-the-new-cyber-fraudtargeting- corporates-and-precautions-listed-by-mha-2026-06-23-1045827
- https://www.freepressjournal.in/business/boss-scam-on-whatsapp-new-ceo-fraudbypasses- traditional-cybersecurity-checks
- https://hyderabadmail.com/tgcsb-warns-boss-scam-ceo-impersonation-fraud-malwarealert/
- https://www.newkerala.com/news/a/rising-boss-scam-threat-targets-senior-executiveswarns- 242.html
- https://www.ic3.gov
- https://www.mcafee.com/learn/is-that-really-your-boss/
- https://abnormal.ai/glossary/ceo-fraud
- https://www.brside.com/blog/deepfake-ceo-fraud-50m-voice-cloning-threat-cfos
- https://www.eftsure.com/blog/cyber-crime/these-7-deepfake-ceo-scams-prove-that-nobusiness- is-safe/
- https://www.knowbe4.com/ceo-fraud
- https://trustpair.com/blog/ceo-fraud-how-to-protect-your-organization-from-fraudsters/
- https://hacked.com/services/executive-impersonation-and-ceo-fraud-protecting-high-networth- individuals/
- https://www.certifid.com/article/ceo-fraud
Executive Summary:
A video from an India TV news show related to the Assam elections is going viral on social media. In the clip, anchor Meenakshi Joshi is allegedly seen claiming that there is a rift between the BJP and the RSS in Assam. The video further suggests that RSS chief Mohan Bhagwat wrote a letter to Prime Minister Narendra Modi stating that former Congress members have taken over the BJP, and that RSS volunteers would not work for the party in Assam. However, a research by the CyberPeace found that the viral video is edited and misleading. The original video contains no such claims.
Claim:
A social media user Ajit Singh shared the video on X with the caption:“The core idea of today’s BJP is to capture power by any means. We have been saying this for long, and now even RSS has accepted that BJP in Assam has been taken over by Congress mindset.”
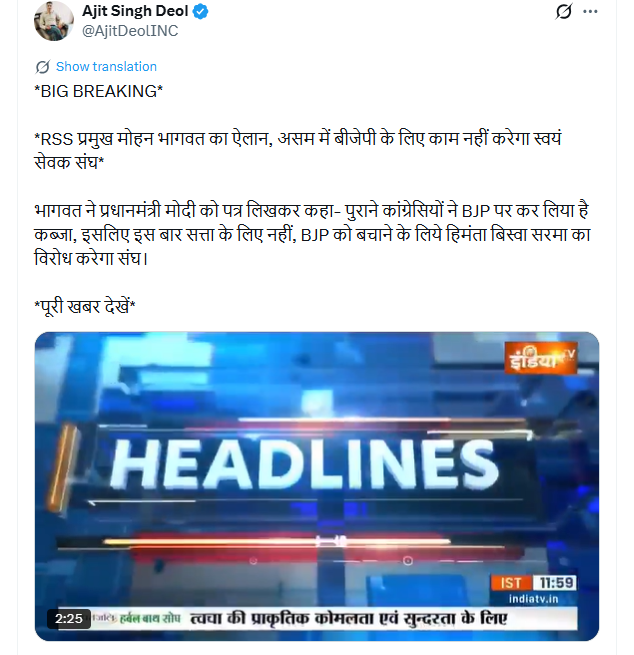
Fact Check:
To verify the claim, we searched relevant keywords about the alleged letter by RSS chief Mohan Bhagwat to Prime Minister Narendra Modi. However, we found no credible media reports supporting this claim. We then checked the YouTube channel of India TV but could not find the viral clip there. During the search, we did find a similar video from Meenakshi Joshi’s show. In the beginning of that video, the portion seen in the viral clip appears.
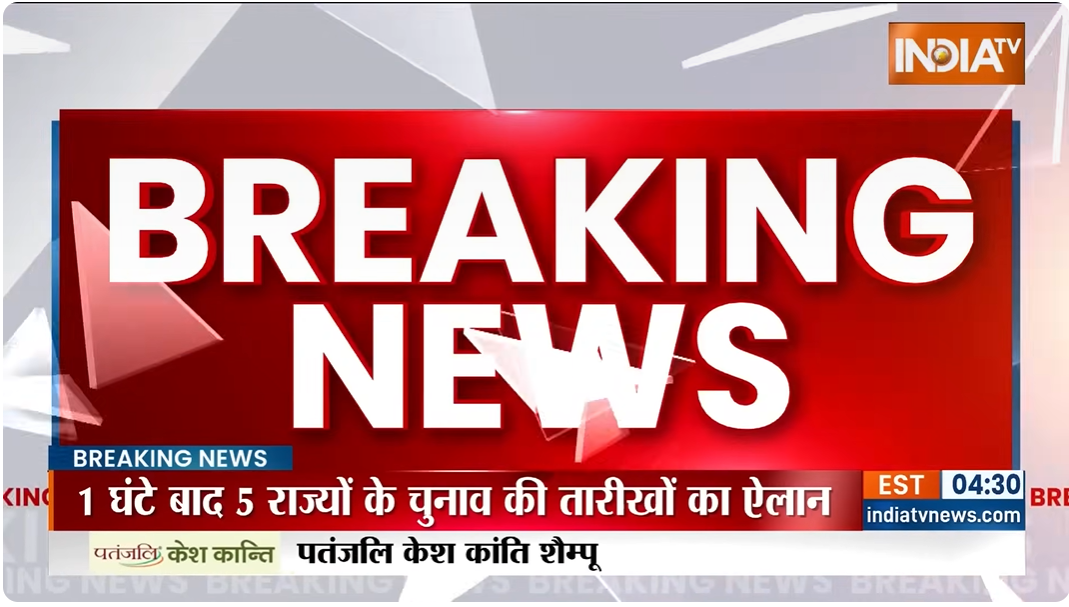
In the original video, the anchor is discussing the announcement of election dates in five states. There is no mention of any rift between the BJP and RSS in Assam.
Conclusion:
The viral India TV video claiming a rift between the BJP and RSS in Assam is edited and misleading. The original broadcast was about election dates in five states and did not include any such claims.
