
#FactCheck:Old 9/11 Videos Falsely Linked to Iran’s Attack on Israel Amid Ongoing Conflict
Executive Summary
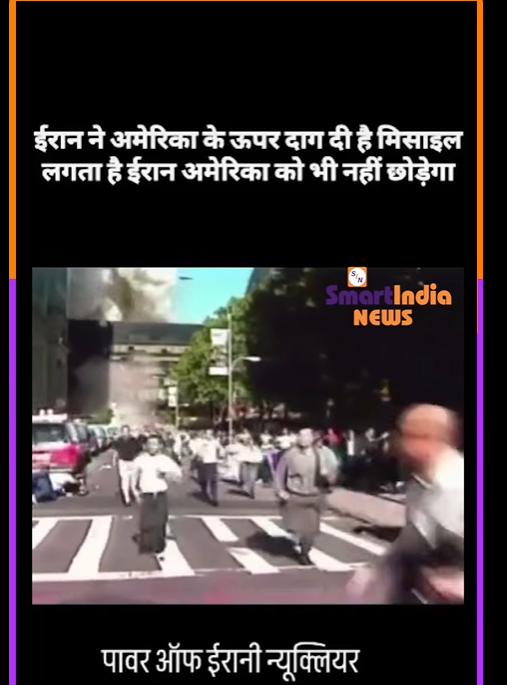
Amid the ongoing war between the United States–Israel alliance and Iran since February 28, 2026, two videos are going viral across social media platforms. The clips show people running in panic, with visuals suggesting a large-scale attack. Users are sharing these videos with the claim that they depict Iran’s recent strikes on Israel. However, a research by the CyberPeace has found both claims to be false. The viral posts are misleading, as the videos are actually from the 9/11 terrorist attacks on the World Trade Center in New York, United States. They have no connection to the current conflict involving Iran or Israel.
Claim
A Facebook page titled ‘Bihar Ko Nihar’ shared one of the videos on March 25, 2026, with the caption: “Iran has launched its most powerful attack on Israel so far. Thousands of soldiers are reported dead, triggering massive protests within the country, and Israel appears completely helpless.” Similarly, another video is being circulated with the false claim that Iran has launched a missile attack on the United States.
The above claims are being widely shared by multiple users across different social media platforms. Archived versions of these posts are also available.
- https://www.facebook.com/reel/4317571078525937
- https://www.facebook.com/reel/1485000739860984
- https://perma.cc/E98R-A4CT
Fact Check
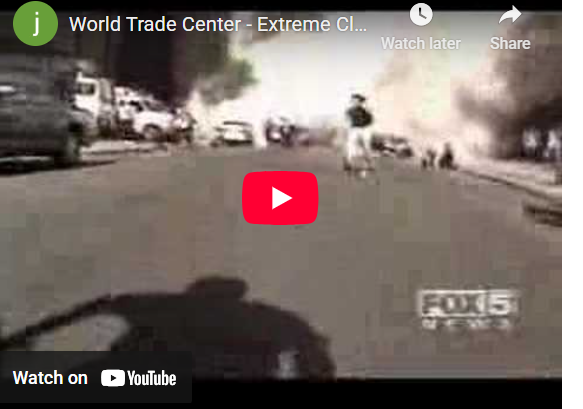
To verify the authenticity of the videos, keyframes were extracted and analyzed using Google Lens. The first viral clip was traced back to a YouTube video uploaded on September 11, 2007, by a channel named ‘Jumperwtc’, which clearly identifies the footage as being from the World Trade Center attacks in the United States. This confirms that the viral video is a segment from that older footage.
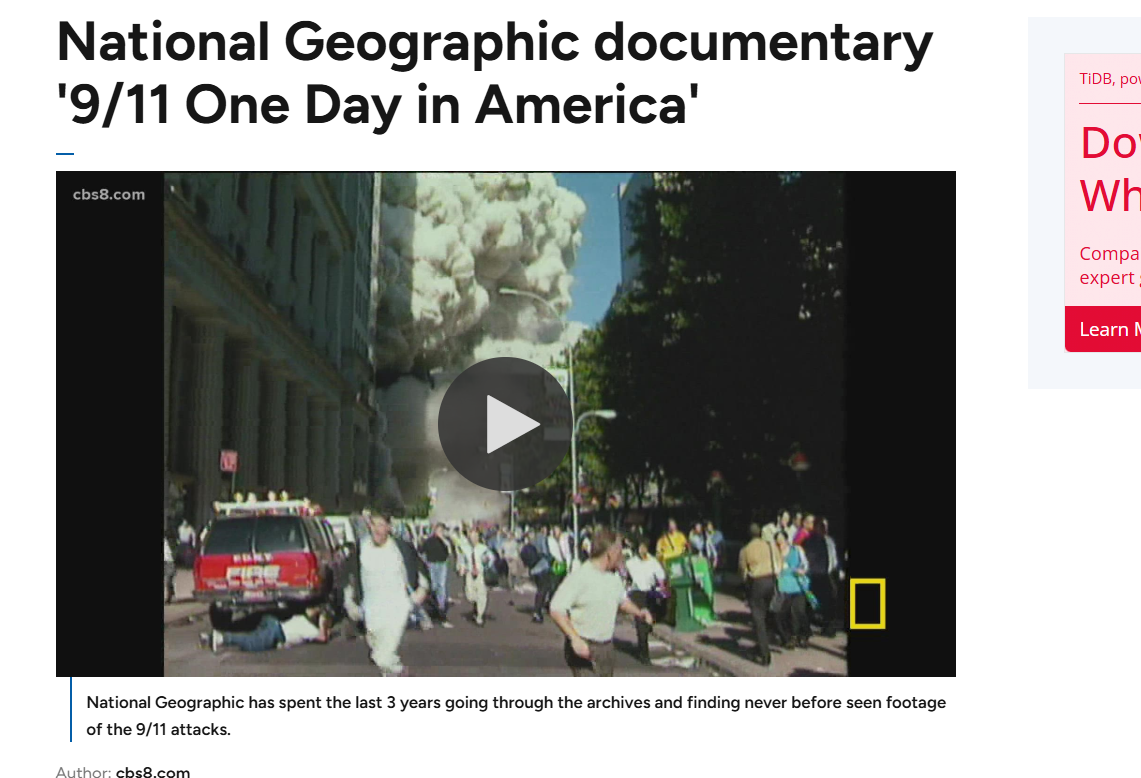
For the second video, reverse image searches led to a report published on CBS8.com on September 10, 2021, where the same visuals were found. Further reesearch revealed that the footage also appears in a video uploaded on September 11, 2021, by the YouTube channel ‘CBS 8 San Diego’. The viral segment can be seen around the 1:11 timestamp in that video.
Conclusion
Both viral videos being shared as recent attacks by Iran on Israel or the United States are actually old clips from the 9/11 attacks on the World Trade Center in New York. The claims are false, and the videos are unrelated to the ongoing conflict in West Asia.

Related Blogs

Brief Overview of the EU AI Act
The EU AI Act, Regulation (EU) 2024/1689, was officially published in the EU Official Journal on 12 July 2024. This landmark legislation on Artificial Intelligence (AI) will come into force just 20 days after publication, setting harmonized rules across the EU. It amends key regulations and directives to ensure a robust framework for AI technologies. The AI Act, a set of EU rules governing AI, has been in development for two years and now, the EU AI Act enters into force across all 27 EU Member States on 1 August 2024, with certain future deadlines tied up and the enforcement of the majority of its provisions will commence on 2 August 2026. The law prohibits certain uses of AI tools, including those that threaten citizens' rights, such as biometric categorization, untargeted scraping of faces, and systems that try to read emotions are banned in the workplace and schools, as are social scoring systems. It also prohibits the use of predictive policing tools in some instances. The law takes a phased approach to implementing the EU's AI rulebook, meaning there are various deadlines between now and then as different legal provisions will start to apply.
The framework puts different obligations on AI developers, depending on use cases and perceived risk. The bulk of AI uses will not be regulated as they are considered low-risk, but a small number of potential AI use cases are banned under the law. High-risk use cases, such as biometric uses of AI or AI used in law enforcement, employment, education, and critical infrastructure, are allowed under the law but developers of such apps face obligations in areas like data quality and anti-bias considerations. A third risk tier also applies some lighter transparency requirements for makers of tools like AI chatbots.
In case of failure to comply with the Act, the companies in the EU providing, distributing, importing, and using AI systems and GPAI models, are subject to fines of up to EUR 35 million or seven per cent of the total worldwide annual turnover, whichever is higher.
Key highlights of EU AI Act Provisions
- The AI Act classifies AI according to its risk. It prohibits Unacceptable risks such as social scoring systems and manipulative AI. The regulation mostly addresses high-risk AI systems.
- Limited-risk AI systems are subject to lighter transparency obligations and according to the act, the developers and deployers must ensure that the end-users are aware that the interaction they are having is with AI such as Chatbots and Deepfakes. The AI Act allows the free use of minimal-risk AI. This includes the majority of AI applications currently available in the EU single market like AI-enabled video games, and spam filters, but with the advancement of Gen AI changes with regards to this might be done. The majority of obligations fall on providers (developers) of high-risk AI systems that intend to place on the market or put into service high-risk AI systems in the EU, regardless of whether they are based in the EU or a third country. And also, a third-country provider where the high-risk AI system’s output is used in the EU.
- Users are natural or legal persons who deploy an AI system in a professional capacity, not affected end-users. Users (deployers) of high-risk AI systems have some obligations, though less than providers (developers). This applies to users located in the EU, and third-country users where the AI system’s output is used in the EU.
- General purpose AI or GPAI model providers must provide technical documentation, and instructions for use, comply with the Copyright Directive, and publish a summary of the content used for training. Free and open license GPAI model providers only need to comply with copyright and publish the training data summary, unless they present a systemic risk. All providers of GPAI models that present a systemic risk – open or closed – must also conduct model evaluations, and adversarial testing, and track and report serious incidents and ensure cybersecurity protections.
- The Codes of Practice will account for international approaches. It will cover but not necessarily be limited to the obligations, particularly the relevant information to include in technical documentation for authorities and downstream providers, identification of the type and nature of systemic risks and their sources, and the modalities of risk management accounting for specific challenges in addressing risks due to the way they may emerge and materialize throughout the value chain. The AI Office may invite GPAI model providers, and relevant national competent authorities to participate in drawing up the codes, while civil society, industry, academia, downstream providers and independent experts may support the process.
Application & Timeline of Act
The EU AI Act will be fully applicable 24 months after entry into force, but some parts will be applicable sooner, for instance the ban on AI systems posing unacceptable risks will apply six months after the entry into force. The Codes of Practice will apply nine months after entry into force. Rules on general-purpose AI systems that need to comply with transparency requirements will apply 12 months after the entry into force. High-risk systems will have more time to comply with the requirements as the obligations concerning them will become applicable 36 months after the entry into force. The expected timeline for the same is:
- August 1st, 2024: The AI Act will enter into force.
- February 2025: Prohibition of certain AI systems - Chapters I (general provisions) & II (prohibited AI systems) will apply; Prohibition of certain AI systems.
- August 2025: Chapter III Section 4 (notifying authorities), Chapter V (general purpose AI models), Chapter VII (governance), Chapter XII (confidentiality and penalties), and Article 78 (confidentiality) will apply, except for Article 101 (fines for General Purpose AI providers); Requirements for new GPAI models.
- August 2026: The whole AI Act applies, except for Article 6(1) & corresponding obligations (one of the categories of high-risk AI systems);
- August 2027: Article 6(1) & corresponding obligations apply.
The AI Act sets out clear definitions for the different actors involved in AI, such as the providers, deployers, importers, distributors, and product manufacturers. This means all parties involved in the development, usage, import, distribution, or manufacturing of AI systems will be held accountable. Along with this, the AI Act also applies to providers and deployers of AI systems located outside of the EU, e.g., in Switzerland, if output produced by the system is intended to be used in the EU. The Act applies to any AI system within the EU that is on the market, in service, or in use, covering both AI providers (the companies selling AI systems) and AI deployers (the organizations using those systems).
In short, the AI Act will apply to different companies across the AI distribution chain, including providers, deployers, importers, and distributors (collectively referred to as “Operators”). The EU AI Act also has extraterritorial application and can also apply to companies not established in the EU, or providers outside the EU if they -make an AI system or GPAI model available on the EU market. Even if only the output generated by the AI system is used in the EU, the Act still applies to such providers and deployers.
CyberPeace Outlook
The EU AI Act, approved by EU lawmakers in 2024, is a landmark legislation designed to protect citizens' health, safety, and fundamental rights from potential harm caused by AI systems. The AI Act will apply to AI systems and GPAI models. The Act creates a tiered risk categorization system with various regulations and stiff penalties for noncompliance. The Act adopts a risk-based approach to AI governance, categorizing potential risks into four tiers: unacceptable, high, limited, and low. Violations of banned systems carry the highest fine: €35 million, or 7 percent of global annual revenue. It establishes transparency requirements for general-purpose AI systems. The regulation also provides specific rules for general-purpose AI (GPAI) models and lays down more stringent requirements for GPAI models with 'high-impact capabilities' that could pose a systemic risk and have a significant impact on the internal market. For high-risk AI systems, the AI Act addresses the issues of fundamental rights impact assessment and data protection impact assessment.
The EU AI Act aims to enhance trust in AI technologies by establishing clear regulatory standards governing AI. We encourage regulatory frameworks that strive to balance the desire to foster innovation with the critical need to prevent unethical practices that may cause user harm. The legislation can be seen as strengthening the EU's position as a global leader in AI innovation and developing regulatory frameworks for emerging technologies. It sets a global benchmark for regulating AI. The companies to which the act applies will need to make sure their practices align with the same. The act may inspire other nations to develop their own legislation contributing to global AI governance. The world of AI is complex and challenging, the implementation of regulatory checks, and compliance by the concerned companies, all pose a conundrum. However, in the end, balancing innovation with ethical considerations is paramount.
At the same hand, the tech sector welcomes regulatory progress but warns that overly-rigid regulations could stifle innovation. Hence flexibility and adaptability are key to effective AI governance. The journey towards robust AI regulation has begun in major countries, and it is important that we find the right balance between safety and innovation and also take into consideration the industry reactions.
References:
- https://eur-lex.europa.eu/legal-content/EN/TXT/PDF/?uri=OJ:L_202401689
- https://www.theverge.com/2024/7/12/24197058/eu-ai-act-regulations-bans-deadline
- https://techcrunch.com/2024/07/12/eus-ai-act-gets-published-in-blocs-official-journal-starting-clock-on-legal-deadlines/
- https://www.wsgr.com/en/insights/eu-ai-act-to-enter-into-force-in-august.html
- https://www.techtarget.com/searchenterpriseai/tip/Is-your-business-ready-for-the-EU-AI-Act
- https://www.simmons-simmons.com/en/publications/clyimpowh000ouxgkw1oidakk/the-eu-ai-act-a-quick-guide

Introduction
In April 2026, a class action suit in a federal court in California rejuvenated one of the most basic assertions in digital communication: that private messages are private. The suit claims that Meta Platforms, its subsidiary WhatsApp, and third-party contractors such as Accenture could have accessed user messages even though it had long promised end-to-end encryption.
This case is not merely about a single company or a single platform. It poses more profound questions regarding the definition, communication and regulation of privacy in an age when digital infrastructure is becoming more and more incomprehensible or unprovable to regular users.
What the Lawsuit Actually Says
The suit was filed by plaintiffs Brian Y. Shirazi and Nida Samson, who alleged that WhatsApp, Meta and contractors had intercepted and shared private messages with third parties without their consent. The complaint states that the federal investigators were notified by the whistleblowers that employees of Meta and external contractors had access to the content of WhatsApp messages that were expected to be encrypted and inaccessible.
This directly puts into question the main privacy promise of WhatsApp. The platform has been promoting itself as an end-to-end encrypted service in which not even WhatsApp can read your messages. The case asserts that this assertion was deceptive in its application and that no one ever gave any consent prior to their messages being intercepted, stored, or read.
The plaintiffs are proposing to represent a nationwide class of users of WhatsApp who sent or received messages between April 5, 2016, and the current time and subclasses in California and Pennsylvania. The claims involve breach of contract, California laws on privacy and data violations, false advertising and the Pennsylvania Wiretapping and Electronic Surveillance Act.
It should be mentioned that they are allegations. Similar assertions have been refuted by Metacomet in the past, with the company asserting that its encryption frameworks ensure that the company cannot access the messages. The case is in progress, and no facts have been found.
The Grey Area No One Talks About
In order to see the significance of this lawsuit outside the court, it is useful to consider the way modern messaging platforms actually work. In principle, end-to-end encryption means that only the sender and receiver can decipher a message. Even the service provider should not be able to access the content.
However, there is a grey space that is seldom publicly discussed: content moderation. User reports, metadata analysis or restricted message review processes are common methods used by platforms to identify harmful content, like fraud, child exploitation, or spam. The complaint indicates that such moderation procedures might have opened avenues to the content of messages to human reviewers or automated systems more than users were made to think.
This is not the first time that privacy and safety are at odds. Many jurisdictions have also advocated access to encrypted communications through legal means in the name of national security or criminal investigations. What this suit does is put that tension into even more stark relief by asking whether platforms are really open with users about these trade-offs.
The Consent Problem
The emphasis on consent is one of the most significant implications of this case. The plaintiffs claim that the users were never warned that their messages would be accessed by the employees or third parties and were never provided with any meaningful option on the same.
This is where the case turns into a data governance issue, rather than a legal one. Most data protection models consider the legality of data processing to be based on whether the users know how their data is being processed or not. When the accusations are found to be true, then the matter is not technical. It would be a contractual and ethical failure, a disjuncture between what platforms promise and what they do.
The implications are huge to the billions of users who use WhatsApp to communicate, both personally and professionally, and even politically.
What This Means Going Forward
An effective attack on the encryption assertions of WhatsApp might have actual implications for the rest of the digital ecosystem. Users might start doubting that any platform can be really considered to guarantee privacy. The regulators can advocate more stringent disclosure policies and compulsory independent audits of encryption systems. Social networks might have to re-architect their moderation frameworks to make sure that safety features do not silently compromise privacy guarantees that they claim.
Meanwhile, there is a real policy dilemma in this case that cannot be disregarded. Complete privacy may preclude the capacity to identify abuse or hateful material. The manner in which that balance is achieved and, more to the point, the manner in which it is made transparent to users is an issue that has yet to be addressed by policymakers, civil society and the tech industry.
Other technical experts have also questioned the plausibility of the claims in the lawsuit at scale, noting that it would be an extraordinary undertaking to systematically bypass end-to-end encryption. This further supports the argument of independent verification mechanisms. The problem is that users should not be forced to decide what they should believe in more: corporate guarantees or legal charges. There must be rules that can be enforced which are above the two.
Conclusion: Beyond One Lawsuit
The WhatsApp class action is eventually concerning a structural issue within the digital economy. Users are expected to have faith in systems that they cannot observe, on the assertions that they cannot test themselves.
This case is a warning, regardless of whether the allegations are proved or not. Privacy cannot be based on marketing language. It needs legally binding norms, actual transparency in the treatment of data, and external control that will provide users with something more to hang on than a tagline.
References
- https://www.bitdefender.com/en-us/blog/hotforsecurity/lawsuit-claims-meta-can-access-whatsapp-messages-despite-end-to-end-encryption-2
- https://blog.cryptographyengineering.com/2026/02/02/whatsapp-encryption-a-lawsuit-and-a-lot-of-noise/
- https://www.bloomberg.com/news/articles/2026-01-25/lawsuit-claims-meta-can-see-whatsapp-chats-in-breach-of-privacy
- https://www.classaction.org/blog/despite-privacy-promises-meta-third-parties-read-and-store-whatsapp-messages-class-action-lawsuit-alleges

Executive Summary
A video of Tamil Nadu Chief Minister Thalapathy Vijay is being widely circulated on social media with the claim that he reached Jantar Mantar in New Delhi and participated in an ongoing protest. CyberPeace Research Wing’s research found the viral claim to be misleading. During the research, we found an official clarification issued by the Delhi Police, which clearly refuted the claim and stated that the video was being shared with a false context.
Claim
A user on social media platform Instagram shared the viral video claiming that Thalapathy Vijay had reached Delhi’s Jantar Mantar and joined a protest there.
https://www.instagram.com/reels/Da-tsmSpC-V/
https://archive.ph/submit/?url
https://www.instagram.com/reels/Da-tsmSpC-V/

Fact Check
To verify the claim, we extracted multiple keyframes from the viral video and conducted a reverse image search using Google Lens. During the research, we found a similar image posted on Instagram on May 5, 2026, which contained visuals matching the viral video. The post did not mention any connection with a protest at Delhi’s Jantar Mantar.
https://www.instagram.com/p/DX8cmt6oqP9/

Further research revealed that the first major on-ground protest of the Cockroach Janta Party (CJP) was organised at Jantar Mantar on June 6, 2026. This confirms that the viral video, which is being linked to the CJP protest, is being shared with an incorrect context.

During further verification, we found a report published by BBC Tamil on May 4, 2026, which carried visuals similar to the viral video. https://www.bbc.com/tamil/articles/c202nd32v5ro

According to the BBC report, TVK (Tamilaga Vettri Kazhagam) leader Vijay won from the Perambur and Tiruchirappalli East assembly constituencies during the Tamil Nadu Assembly elections. The visuals in the viral video are related to Vijay’s political activities in Tamil Nadu and are not from Delhi’s Jantar Mantar. Additionally, the Delhi Police issued an official clarification stating that the claim linking the video to Jantar Mantar was false.
https://x.com/DCPNewDelhi/status/2078932755023577234?s=20

Conclusion
CyberPeace Research Wing’s research found that the viral video of Thalapathy Vijay is not from a protest at Delhi’s Jantar Mantar. The video is being circulated with a false and misleading claim. The Delhi Police has also officially denied the claim. Users are advised not to share such misleading content without verification.
