
#FactCheck: Misleading Clip of Nepal Crash Shared as Air India’s AI-171 Ahmedabad Accident
Executive Summary:
A viral video circulating on social media platforms, claimed to show the final moments of an Air India flight carrying passengers inside the cabin just before it crashed near Ahmedabad on June 12, 2025, is false. However, upon further research, the footage was found to originate from the Yeti Airlines Flight 691 crash that occurred in Pokhara, Nepal, on January 15, 2023. For all details, please follow the report.

Claim:
Viral videos circulating on social media claiming to show the final moments inside Air India flight AI‑171 before it crashed near Ahmedabad on June 12, 2025. The footage appears to have been recorded by a passenger during the flight and is being shared as real-time visuals from the recent tragedy. Many users have believed the clip to be genuine and linked it directly to the Air India incident.


Fact Check:
To confirm the validity of the video going viral depicting the alleged final moments of Air India's AI-171 that crashed near Ahmedabad on 12 June 2025, we engaged in a comprehensive reverse image search and keyframe analysis then we got to know that the footage occurs back in January 2023, namely Yeti Airlines Flight 691 that crashed in Pokhara, Nepal. The visuals shared in the viral video match up, including cabin and passenger details, identically to the original livestream made by a passenger aboard the Nepal flight, confirming that the video is being reused out of context.

Moreover, well-respected and reliable news organisations, including New York Post and NDTV, have shared reports confirming that the video originated from the 2023 Nepal plane crash and has no relation to the recent Air India incident. The Press Information Bureau (PIB) also released a clarification dismissing the video as disinformation. Reliable reports from the past, visual evidence, and reverse search verification all provide complete agreement in that the viral video is falsely attributed to the AI-171 tragedy.


Conclusion:
The viral footage does not show the AI-171 crash near Ahmedabad on 12 June 2025. It is an irrelevant, previously recorded livestream from the January 2023 Yeti Airlines crash in Pokhara, Nepal, falsely repurposed as breaking news. It’s essential to rely on verified and credible news agencies. Please refer to official investigation reports when discussing such sensitive events.
- Claim: A dramatic clip of passengers inside a crashing plane is being falsely linked to the recent Air India tragedy in Ahmedabad.
- Claimed On: Social Media
- Fact Check: False and Misleading

Related Blogs
Executive Summary
A video is being shared on social media with the claim that Ministry of External Affairs spokesperson Randhir Jaiswal was seen eating nuts during the BRICS Summit. The post claims that a reporter questioned him about eating nuts during the event. The video is also being shared with the sarcastic caption, “The Nutty Spokesperson.” Through the post, an attempt is being made to suggest that a reporter questioned Randhir Jaiswal about eating nuts during a press briefing. CyberPeace Research found that in the original video, Ministry of External Affairs spokesperson Randhir Jaiswal was responding to a question about Pakistan’s announcement of a 7 million Pakistani rupee bounty on Jaish-e-Mohammed chief Masood Azhar. Jaiswal addressed the announcement during the regular media briefing held on September 15, 2026. In his response, Jaiswal said that such announcements by Pakistan were not new and that the country should take concrete action against terrorism. However, the video being circulated on social media has been digitally edited using the original footage to falsely suggest that a reporter had questioned Jaiswal about eating nuts.
Claim:
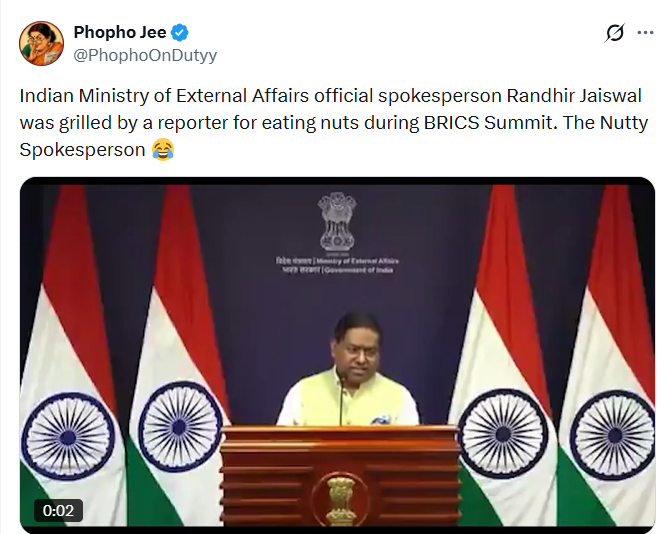
During the BRICS Summit, a reporter questioned Ministry of External Affairs spokesperson Randhir Jaiswal about eating nuts and confronted him over it.
https://x.com/PhophoOnDutyy/status/2099940769876640084?s=20
Fact Check
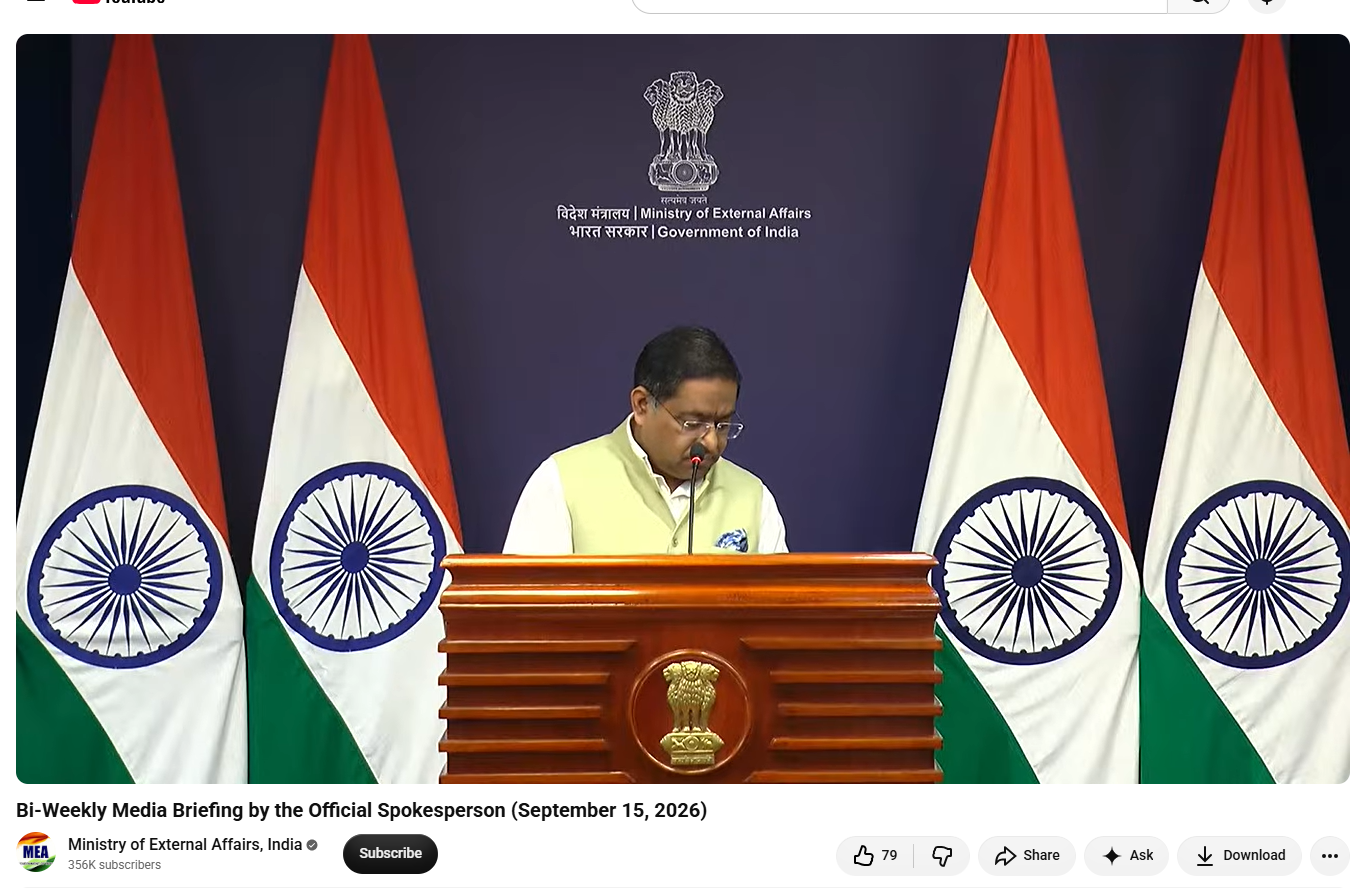
To verify the claim, we conducted a Google search using relevant keywords. During the search, we did not find any credible media report supporting the claim.As part of our research, we conducted a reverse image search of keyframes from the video. We found the original video on the YouTube channel of the Ministry of External Affairs, India. In the original video, Randhir Jaiswal was responding to a question about Pakistan’s announcement of a 7 million Pakistani rupee bounty on Masood Azhar.The reporter does not question Jaiswal about eating nuts anywhere in the original video. This establishes that the original footage has been edited and presented with a false context. Therefore, the claim being circulated on social media is false.
https://www.youtube.com/live/dw-qqLolRgc
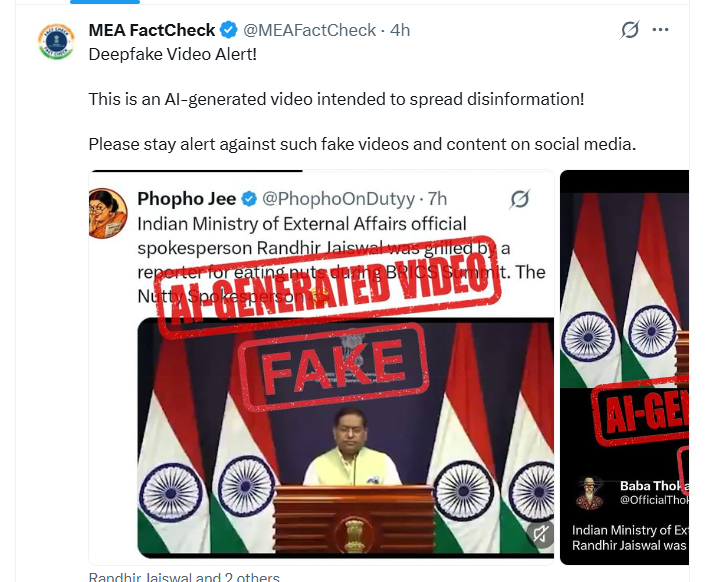
As part of our further research, we checked the official X account of MEA FactCheck. It also identified the video as AI-generated.
https://x.com/MEAFactCheck/status/2100076244805255501?s=20
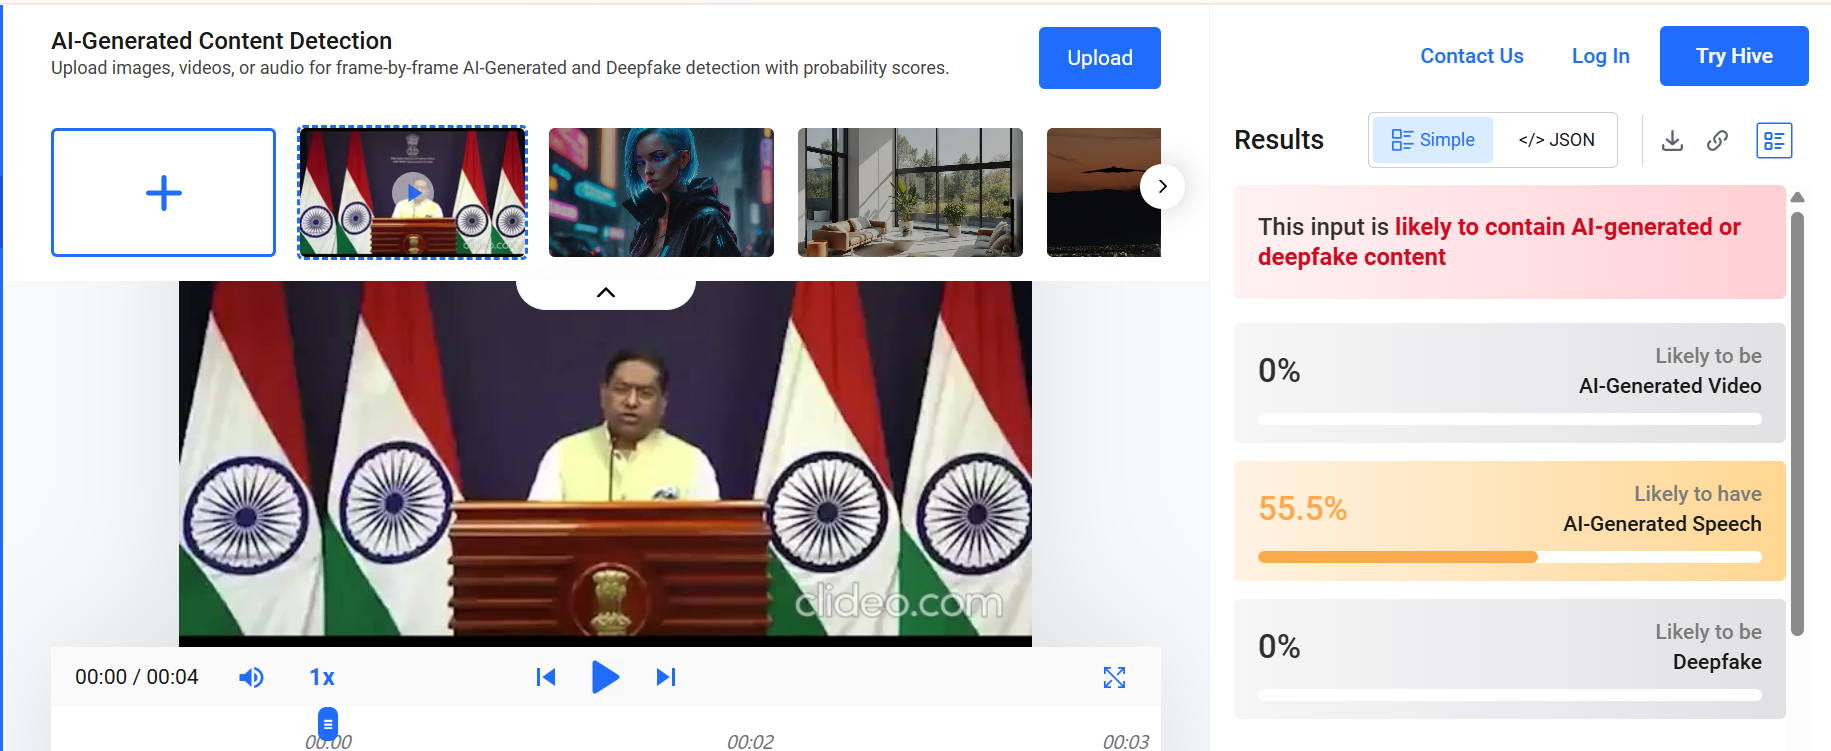
The video was scanned using the AI detection tool Hive Moderation. According to the results, the video has a 55% probability of being AI-generated.
Conclusion
Our research found that the video being shared on social media is fake and edited. In the original video, Ministry of External Affairs spokesperson Randhir Jaiswal was responding to a question about Pakistan’s announcement of a 7 million Pakistani rupee bounty on Masood Azhar.At no point in the original video does the reporter question Jaiswal about eating nuts.
The footage being circulated has been digitally manipulated and presented in a different context. The official X account of MEA FactCheck also identified the video as AI-generated. Therefore, the claim that Jaiswal was questioned by a reporter about eating nuts is false and misleading.
Introduction
On June 11, 2026, the Ministry of Home Affairs (MHA) India released one of the most critical Indian government advisories concerning cybersecurity by the Indian Cyber Crime Coordination Centre (I4C) under the National Cybercrime Threat Analytics Unit (NCTAU) concerning the immediate and escalating threat posed by the weaponization of generative artificial intelligence to forge synthetic biometric identities capable of bypassing the existing facial verification mechanisms in India. This advisory is arguably one of the most explicit Indian government recognitions of the deep-seated threats associated with AI-generated deepfakes in the country’s digital financial infrastructure. As many Indian financial service providers embrace facial recognition and biometric verification systems for customer onboarding and authentications, the myth that biometric traits are in themselves secure is slowly unraveling.
The advisory states that cybercriminals are deploying sophisticated AI tools to forge such credible digital simulacrums that exhibit such a precise similarity of facial expressions, eye movements, eye blinks, head movements, and voice patterns that they are virtually indistinguishable from the originals for identity verification mechanisms. Such a confluence of easy AI technology, mass onboarding of digital identities, and underdeveloped infrastructure to detect these synthetics requires urgent regulatory, institutional, and technological intervention.
The I4C Advisory: Core Findings and Threat Architecture
In its advisory, NCTAU describes a complex, multi-step attack chain used by scammers to capture biometric information and perpetrate fraud using everyday social interactions. The attackers typically use social media accounts, chat messengers, online job applications, dating applications, or direct phone calls to reach their targets. These interactions are presented as innocuous, such as for video calls, job interviews, identity checks, or just normal conversation with the intention of recording facial and vocal data.
During these interactions, victims may be asked to perform gestures commonly seen in legitimate video calls, such as look directly at the camera, blink, turn their head, or say specific phrases. However, the perpetrators record this video feed without the victim's knowledge and then use deep learning generative AI technologies to process it. Through methods such as Generative Adversarial Networks (GANs) and diffusion models, the scammers create photorealistic synthetic duplicates of the target, capable of mirroring all physical and vocal attributes, such as facial expressions, blinking patterns, head movements, and even voice tones.
The advisory explicitly states that these synthetic identities can be used for a variety of fraudulent activities, such as spoofing face authentication systems, circumventing liveness detection checks, successfully completing video KYC, enabling fraudulent account recovery processes, and illegally accessing bank and financial services. NCTAU also cautions that these voice deepfakes may be paired with facial deepfakes in an attempt to undermine multi-modal authentication methods, and the occurrence of related SIM-swap attacks can eliminate the last layer of security in OTP verification and facilitate a complete account compromise.
The scale of India's Digital Financial Ecosystem
The scale of I4C's detected threat can be better understood by considering India's entire digital financial landscape. In 2025 India has witnessed over 228 billion UPI transactions, with 21.63 billion in December alone, an annual growth rate of 29% from 2024, and an active user base of over 500 million by the beginning of 2026. Furthermore, total e-KYC transactions by April 2025 have exceeded 2,393 crore, and thus, it can be seen the extent to which these aspects of finance (banking, insurance, and credit) are now conducted via remote digital verification. The transformation, although instrumental in increasing financial inclusion, has, according to some analysts, created an attack surface of historic scale. As hundreds of millions more become financially integrated via the very same channels that now form the country's infrastructure and systems of identity, the threat from identity-based fraud becomes astronomically large.
Indian government data further illustrates the extent to which such frauds are a growing concern. Cybercrime cases jumped 42% year-on-year to 2.27 million in 2024, resulting in losses amounting to nearly 228.45 billion. Within that, 1.34 million UPI cases, worth 1,087 crore, occurred in FY2024 alone, while cybercrimes in general soared from 260,000 cases in 2021 to nearly 2.8 million by 2025, totaling cybercrime losses of 22,931 crore.
How Do Deepfakes Defeat Biometric Systems?
Deepfake fraud, in particular, is extremely difficult to counteract due to the direct attack it poses on the assumptions underlying traditional verification systems. Passive techniques for verifying a live person from a static photo or video existed that primarily looked for similarities in textures, lighting, and geometrical properties or challenged subjects to perform an action in real-time. But the generation of real-time face swapping that contains blinks, head motion, and speaking can now be produced on even cheap machines. Cybercriminals can exploit these by using virtual camera drivers to "inject" the false image feed into the live verification session, nullifying any passive liveness checks. Data from the industry clearly shows the extent of this problem: iProov, a leading authenticator, documented a 7.8-fold rise in injection attacks in 2024; Jumio noted an 88% increase in deepfake-induced fraud in 2025; and voice-deepfake attacks on financial call centres saw a 6.8-fold increase in 2024.
Gartner had also predicted that 30% of organizations would have lost trust in facial verification alone by 2026, and work by Kubam (2024) confirmed a lack of multi-factor authentication such as cross-validation of biometric, document, and device integrity signals used within KYC platforms. Such fears have been corroborated by FATF's 2025 Horizon Scan, which classified deepfakes as an emerging threat to the AML/CDD framework and digital identity verification.
Recommendations by I4C
I4C's advisory goes beyond merely warning about threats and lists actionable recommendations to both institutions and citizens. Banks, NBFCs, fintech companies, and onboarding platforms have been advised to incorporate advanced deepfake and synthetic content detection techniques into their verification flows, given that first-generation liveness checks are not enough. They should employ a multi-modal strategy that considers face features along with the device, network signals, behavioral biometrics, and alignment of face and voice. They also have been advised to make a more robust upgrade of their onboarding and verification platforms, as much of the current remote verification architecture was built in a less sophisticated threat context. This aligns with the KYC Master Direction of the RBI that specifies end-to-end encryption, IP-based access controls, geotagging, and technology platforms and systems are to be upgraded frequently. Citizens are advised by I4C to keep their biometric information secure; be careful of unsolicited video calls and online interviews; keep an eye on transaction-related SMS and emails; and report suspicious instances through the National Cybercrime Reporting Portal and through the telephone number 1930. It is clarified that this advisory aims to create awareness of developing AI-based identity fraud schemes, and it is not a declaration that any specific organization, platform, or service is vulnerable.
The Legislative Dimension: India's Evolving Response to Synthetic Media
The problem highlighted by I4C is evolving in a heavily legislated environment, not a legal void. The first-ever legal definition of "synthetic media" in India came into force in the Information Technology Amendment Rules 2026 on February 20, 2026. These rules oblige significant platforms to remove deepfakes and non-consensual intimate media within three hours and two hours, respectively, or lose their safe harbor protection under Section 79 of the IT Act. While the provision focuses on harm stemming from content, this creates a new legal and normative precedent on dealing with AI-induced deception. However, financial frauds facilitated through deepfakes are not content but involve the use of remote identity verification and customer onboarding systems, which require specific technical standards. The overall policy environment when viewed in light of the FATF Horizon Scan, RBI KYC rules, and recent I4C advisory already offers significant scope to define and introduce mandatory deepfake detection and identity assurance standards even before these are explicitly legislated.
Institutional and Technical Recommendations
- For Financial Institutions and Fintech platforms: The existing verification systems (liveness detection) must be replaced with multi-layered deep-fake detection processes, including injection attack detection, behavioral biometrics, cross-modal facial and voice verification, device integrity check, and hardware attestation during onboarding itself.
- For Regulators: The RBI and Ministry of Home Affairs should work together to release technical standards that specify minimum deepfake-detection requirements for video-KYC and remote onboarding systems in line with FATF digital identity guidance and the upcoming EU AI Act.
- For researchers and academia: Dedicated studies on deepfake detection performance across varied demographic, linguistic, and regional populations of India should be prioritized. Current models are mostly trained on Western data.
- For citizens: Face recordings and other biometric information should be treated with the same caution as sensitive financial details. Be wary of unsolicited video calls, remote interviews, or verification requests from unknown people, and report suspicious activities on any account immediately via the National Cybercrime Helpline (1930) or cybercrime.gov.in.
Conclusion
The I4C advisory of June 2026 marks a critical recognition that advances in generative AI have fundamentally challenged the reliability of facial biometric authentication. For a country whose digital financial ecosystem relies heavily on remote identity verification, the implications are significant. The integrity of India's financial inclusion framework now depends on rapidly strengthening identity assurance mechanisms. Addressing this threat will require coordinated action by regulators, financial institutions, technology developers, researchers, and citizens to develop robust technical standards, enhance detection capabilities, and build public awareness at a pace matching the evolution of AI-enabled fraud.
References and Sources
- I4C / NCTAU Advisory, June 2026 — National Cybercrime Threat Analytics Unit, Indian Cyber Crime Coordination Centre, Ministry of Home Affairs, Government of India. Advisory on AI-Enabled Deepfake Identity Fraud. Issued 11 June 2026.
- shuftipro.com/blog/key-takeaways-from-fatf-horizon-scan-report-on-deepfakes
- https://timesofindia.indiatimes.com/india/fraudsters-creating-deepfakes-to-bypass-facial-authentication-i4c/articleshow/131668958.cms
- hyperverge.co/blog/what-is-a-deepfake
- iproov.com/reports/threat-intelligence-report-2026
- arxiv.org/pdf/2601.06241

Introduction
Over the past few months, cybercriminals have upped the ante with highly complex methods targeting innocent users. One such scam is a new one that exploits WhatsApp users in India and globally. A seemingly harmless picture message is the entry point to stealing money and data. Downloading seemingly harmless images via WhatsApp can unknowingly install malware on your smartphone. This malicious software can compromise your banking applications, steal passwords, and expose your personal identity. With such malware-laced instant messages now making headlines, it is advised for netizens to exercise extreme caution while handling media received on messaging platforms.
How Does the WhatsApp Photo Scam Work?
Cybercriminals began embedding malicious code in images being shared on WhatsApp. Here is how the attack typically works:
- The user receives a WhatsApp message from an unknown number with an image.
- The image may appear harmless—a greeting, meme, or holiday card—but it's packed with hidden malware.
- When the user taps to download the image, the malware gets installed on the phone in silent mode.
- Once installed, the malware is able to capture keystrokes, read messages, swipe banking applications, swipe credentials, and even hijack device functionality.
- Allegedly, in its advanced versions, it can exploit two-factor authentication (2FA) and make unauthorised transactions.
Who Is Being Targeted?
This scam targets both Android and iPhone users, with a focus on vulnerable groups like senior citizens, busy workers during peak seasons, and members of WhatsApp groups flooded with forwarded messages. Experts warn that a single careless click is enough to compromise an entire device.
What Can the Malware Do?
Upon installation, the malware grants hackers a terrifying level of access:
- Track user activity via keylogging or screen capture.
- Pilfer banking credentials and initiate fund transfers automatically.
- Obtain SMS or app-based 2FA codes, evading security layers.
- Clone identity information, such as Aadhaar details, digital wallets, and email access.
- Control device operations, including the camera and microphone.
This level of intrusion can result in not just financial loss but long-term digital impersonation or blackmail.
Safety Measures for WhatsApp Users
- Never Download Media from Suspicious Numbers
Do not download any files or pictures, even if the content appears to be familiar, unless you have faith in the source. Spread this advice among family members, particularly the older generation.
- Turn off Auto-Download in WhatsApp Settings
Navigate to Settings > Storage and Data > Media Auto-Download. Switch off auto-download for mobile data, Wi-Fi, and roaming.
- Install and Update Mobile Security Apps
Ensure your phone is equipped with a good antivirus or mobile security app that is updated from time to time.
- Block and Report Potential Scammers
WhatsApp offers the ability to block and report senders in a straightforward manner. This ensures that it notifies the platform and others as well.
- Educate Your Community
Share your knowledge on cyber hygiene with family, friends, and colleagues. Many people fall victim simply because they aren't aware of the risks, staying informed and spreading the word can make a big difference.
Advisories and Response
The Indian Cybercrime Coordination Centre (I4C) and other state cyber cells have released several alerts on increasing fraud via messaging platforms. Law enforcement agencies are appealing to the public not only to be vigilant but also to report any incident at once through the National Cybercrime Reporting Portal (cybercrime.gov.in).
Conclusion
The WhatsApp photo scam is a stark reminder that not all dangers come with a warning. A picture can now be a Trojan horse, propagating silently from device to device and draining personal money. Do not engage with unwanted media, refresh and update your privacy and security settings. Cyber criminals survive on neglect and ignorance, but through digital hygiene and vigilance, we can fight against these types of emerging threats.
References
- https://www.opswat.com/blog/how-emerging-image-based-malware-attacks-threaten-enterprise-defenses
- https://www.indiatvnews.com/technology/news/whatsapp-photo-scam-alert-downloading-random-images-could-cost-you-big-2025-05-06-988855
- https://www.hindustantimes.com/india-news/what-is-the-whatsapp-image-scam-and-how-can-you-stay-safe-from-it-101744353412848.html
- https://faq.whatsapp.com/898107234497196/?helpref=uf_share
- https://www.welivesecurity.com/en/malware/malware-hiding-in-pictures-more-likely-than-you-think/
- https://faq.whatsapp.com/573786218075805
- https://www.reversinglabs.com/blog/malware-in-images
