
#FactCheck: AI-Generated Audio Falsely Claims COAS Admitted to Loss of 6 Jets and 250 Soldiers
Executive Summary:
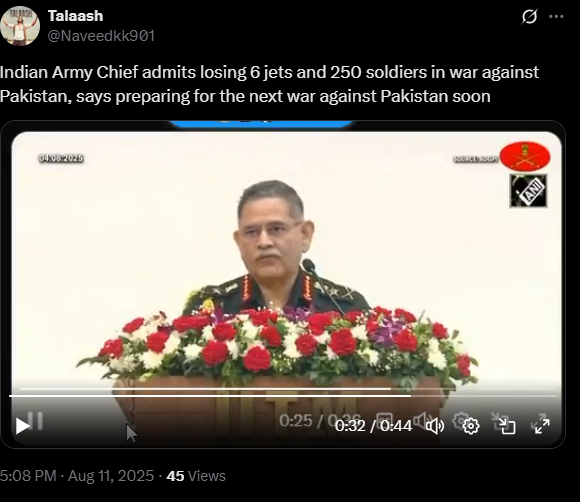
A viral video (archive link) claims General Upendra Dwivedi, Chief of Army Staff (COAS), admitted to losing six Air Force jets and 250 soldiers during clashes with Pakistan. Verification revealed the footage is from an IIT Madras speech, with no such statement made. AI detection confirmed parts of the audio were artificially generated.
Claim:
The claim in question is that General Upendra Dwivedi, Chief of Army Staff (COAS), admitted to losing six Indian Air Force jets and 250 soldiers during recent clashes with Pakistan.
Fact Check:
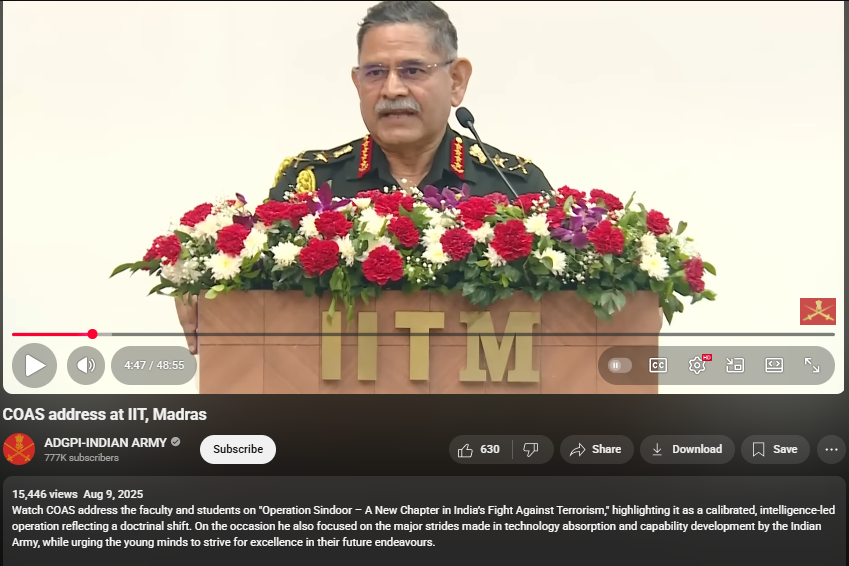
Upon conducting a reverse image search on key frames from the video, it was found that the original footage is from IIT Madras, where the Chief of Army Staff (COAS) was delivering a speech. The video is available on the official YouTube channel of ADGPI – Indian Army, published on 9 August 2025, with the description:
“Watch COAS address the faculty and students on ‘Operation Sindoor – A New Chapter in India’s Fight Against Terrorism,’ highlighting it as a calibrated, intelligence-led operation reflecting a doctrinal shift. On the occasion, he also focused on the major strides made in technology absorption and capability development by the Indian Army, while urging young minds to strive for excellence in their future endeavours.”
A review of the full speech revealed no reference to the destruction of six jets or the loss of 250 Army personnel. This indicates that the circulating claim is not supported by the original source and may contribute to the spread of misinformation.
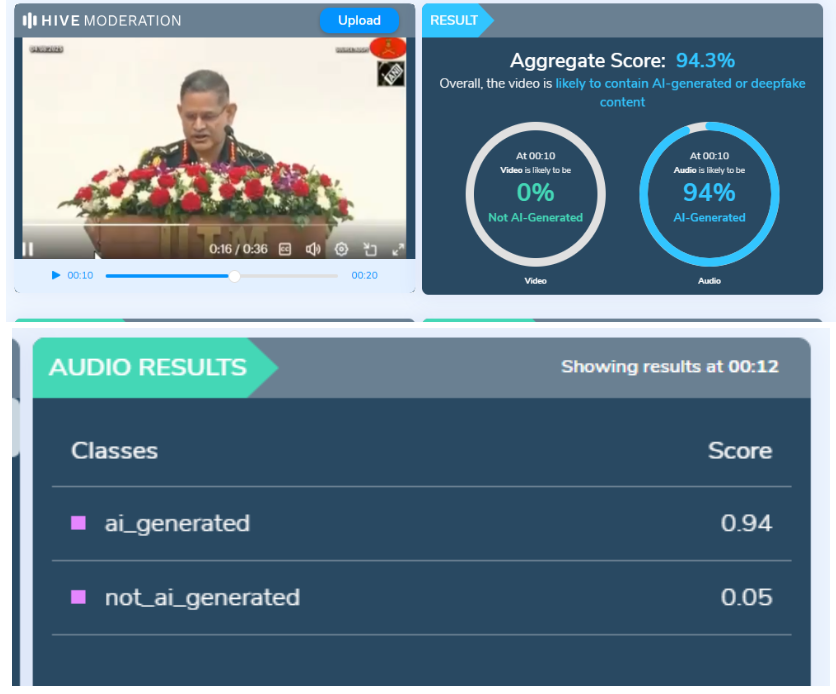
Further using AI Detection tools like Hive Moderation we found that the voice is AI generated in between the lines.
Conclusion:
The claim is baseless. The video is a manipulated creation that combines genuine footage of General Dwivedi’s IIT Madras address with AI-generated audio to fabricate a false narrative. No credible source corroborates the alleged military losses.
- Claim: AI-Generated Audio Falsely Claims COAS Admitted to Loss of 6 Jets and 250 Soldiers
- Claimed On: Social Media
- Fact Check: False and Misleading

Related Blogs

Executive Summary:
An online claim alleging that U.S. bombers used Indian airspace to strike Iran has been widely circulated, particularly on Pakistani social media. However, official briefings from the U.S. Department of Defense and visuals shared by the Pentagon confirm that the bombers flew over Lebanon, Syria, and Iraq. Indian authorities have also refuted the claim, and the Press Information Bureau (PIB) has issued a fact-check dismissing it as false. The available evidence clearly indicates that Indian airspace was not involved in the operation.
Claim:
Various Pakistani social media users [archived here and here] have alleged that U.S. bombers used Indian airspace to carry out airstrikes on Iran. One widely circulated post claimed, “CONFIRMED: Indian airspace was used by U.S. forces to strike Iran. New Delhi’s quiet complicity now places it on the wrong side of history. Iran will not forget.”

Fact Check:
Contrary to viral social media claims, official details from U.S. authorities confirm that American B2 bombers used a Middle Eastern flight path specifically flying over Lebanon, Syria, and Iraq to reach Iran during Operation Midnight Hammer.

The Pentagon released visuals and unclassified briefings showing this route, with Joint Chiefs of Staff Chair Gen. Dan Caine explained that the bombers coordinated with support aircraft over the Middle East in a highly synchronized operation.

Additionally, Indian authorities have denied any involvement, and India’s Press Information Bureau (PIB) issued a fact-check debunking the false narrative that Indian airspace was used.

Conclusion:
In conclusion, official U.S. briefings and visuals confirm that B-2 bombers flew over the Middle East not India to strike Iran. Both the Pentagon and Indian authorities have denied any use of Indian airspace, and the Press Information Bureau has labeled the viral claims as false.
- Claim: Fake Claim that US has used Indian Airspace to attack Iran
- Claimed On: Social Media
- Fact Check: False and Misleading
Introduction
On 14 October 2026, ANI reported that the Sashastra Seema Bal (SSB), the force responsible for guarding India’s borders with Nepal and Bhutan, had directed its personnel not to fall for online honey traps, open suspicious APK files, or become victims of cyber scams. The warning was issued a day after the force’s annual cybersecurity awareness week and is relevant to every smartphone user in India. The three threats highlighted in the advisory, emotional exploitation, malware disguised as APK files, and financial scams, are often interconnected in a cyberattack chain that can compromise a person’s device or finances. This blog examines the advisory, the methods used by cybercriminals, and the everyday precautions users can take to stay safe.
What the Advisory Says
As per the ANI report, the SSB has cautioned its personnel about talking to strangers on the internet, where they have been instructed not to share photos or videos with anyone in the public eye, accept suspicious calls or video calls, or entertain requests for money, and not to install APKs or applications from any untrusted sources or websites, only use an authorised Android market to install applications, not to share your OTP, PIN, password, or banking details, and to be cautious while receiving an unknown call, suspicious SMS, or click on unknown links and scan QR codes. Personnel have been told not to tell something that does not seem right, and any fraud should be reported through cybercrime helpline number 1930 or cybercrime.gov.in. "Always verify before any transaction" & "Stop, think, check, then act." The SSB caution has been read.
How Online Honey Traps Operate
A honey trap, by definition, is a trap set through the manipulation of a fictitious romantic or social identity designed to gain trust, which is then used against it. There are certain elements that almost always constitute the honey trap.
- Contact: A fake profile, typically an attractive picture, reaches out to the targeted person on social media or a messaging platform.
- Rapport: Created via a mix of small talk, flattery, and "shares" or "interests."
- Escalation: The chatting advances to private messaging, involving sharing of photos or video.
- Extortion: The victim is subsequently threatened with blackmail through recordings, forced to make payments, or extorted for personal information.
This is not an isolated case. Earlier, the Delhi Police had revealed that fake Facebook female profiles were used to lure and befriend defence personnel and extract confidential information (The Quint). Even more recently, a case was reported of an IAF wing commander being lured on social media while undergoing troubled times and, thereafter, made to reveal sensitive defence-related information (Outlook India). While the matter is sub judice, it draws our attention towards an important point of analytical significance – most probably it is emotional trauma, which an attacker would rely upon, rather than technical and security flaws.
The Risk of Malicious APK Files
APK – Android Package Kit, is the package file format used by the Android operating system for the distribution and installation of mobile applications. Downloaded from Play Store, the application goes through a rigorous screening. However, those downloaded from WhatsApp, Telegram or SMS have not been screened. This is the modus operandi of the cybercriminals. They hide malware behind seemingly harmless files like a challan, a gas bill update, a KYC or a wedding invite. Proof from Moneylife pointing to an alert issued by CERT-In as well as file names like RTO Challan.apk and Gas Bill Update.apk establishes that government departments would not send an APK file over any messaging platform.
According to the CERT-In research of India's cybersecurity agency, the way this malware works: The malware Drinik posed as a download application from the Income Tax Department and asked for a long list of admin permissions, including SMS, call history, and contacts. It then presented a fake banking app to steal credentials, as Madhyamam reports. The Tribune reported that the SOVA trojan was hidden in fake apps with famous brands' logos. The report also states that the Black Rock malware variant was targeting 337 applications, including social, communication, and dating applications.
A security advisory by the bank, dated 24 November 2023, mentions what happens if a virus-infected app is installed. Once installed, the attackers would be able to access the messages with the one-time passwords (OTPs) and personal identification numbers (PINs). They could take over the device and make money transactions from the bank account of the owner of the device, says the advisory.
Social Engineering: The Common Thread
Although honey traps and APK frauds may appear on the surface to be very different, there is one aspect they have in common: both are social engineering tricks. The attacker does not rely solely on technological control or access control but also on human vulnerabilities – the fear, intimidation, lust, or love – to persuade the target to behave in a certain manner. The "opposite" sex may ask you to install some "video call app", or a "bank officer" may advise you to update KYC via a file that you may or may not be having. In any of these instances, it is the final step that you will likely carry out without hesitation. The SSB's four steps (stop, think, check, then act) provide a mechanism to break this cycle.
Implications for Personal, Financial and National Security
A phone on the compromised list reveals contacts, snaps, messages and location. Honey trap nudity can take a toll on a person's mental health and reputation via sextortion.
Financial security- Since malware can read SMS, OTP-based protection works quietly. The fraudster can authorise the transaction without the victim providing a code.
National security – For service members, it's not just their personal information at risk. A compromised device can disclose information about their location and their colleagues or how they operate. Border forces operate in a high-risk environment, and no information is too small; even duty rosters or images taken against a landmark background could be of interest to a hostile person, and honey trap recruitment for spy work is one of the oldest.
Practical Precautions
- Avoid sideloading APKs at all costs. Sideloading APKs is highly discouraged. It is best to keep the "Install from unknown sources" option turned off and install apps only from the Google Play Store or the Apple App Store.
- Whenever you have an unsolicited contact, it is not worth believing. It is believed that reversing the search of profile images and being very careful with new acquaintances who quickly begin chatting in private is protective. Never comply with any requests for money.
- Sharing intimate images or receiving surprise video calls from unknown people should be avoided.
- Storing credentials is especially sensitive. Research has shown that a legitimate bank or government body would not typically ask for details like OTPs, PINs or passwords.
- Scrutinise app permissions. Beware of a seemingly simple app requesting permission to access SMS, call logs or contacts.
- It should be verified from an official source. Challans, KYC or taxes are to be submitted using the official website or app and not the link provided in the message.
- It is important to keep professional and personal lives separate. Do not discuss comments, movements or chores or post location-tagged updates.
- Keeping your devices updated and turning on Google Play Protect are crucial.
- In case you are a victim, do take quick actions. Remove the suspicious app, disconnect from the web, and inform your bank. You can report to 1930 or cybercrime.gov.in. Do not pass the suspicious file as it is going to pass on the same.
Conclusion
The SSB advisory today is a reminder that cyberattacks are less about technology and more about exploiting human vulnerabilities. Studies indicate that fake ID cards, realistic files and misinformation are easy to implement and hard to detect. It appears that cultivating verification routines, instilling a "careful hygiene of use", and quick reporting on 1930 or cybercrime.gov.in are the best initiatives that border forces and citizens can take. Creating awareness about pausing, analysing, verifying and acting if in doubt could be an even better way of building resilience. It is crucial for everyone to remain cognisant and alert and keep cyber safety at the top of the mind.
Executive Summary
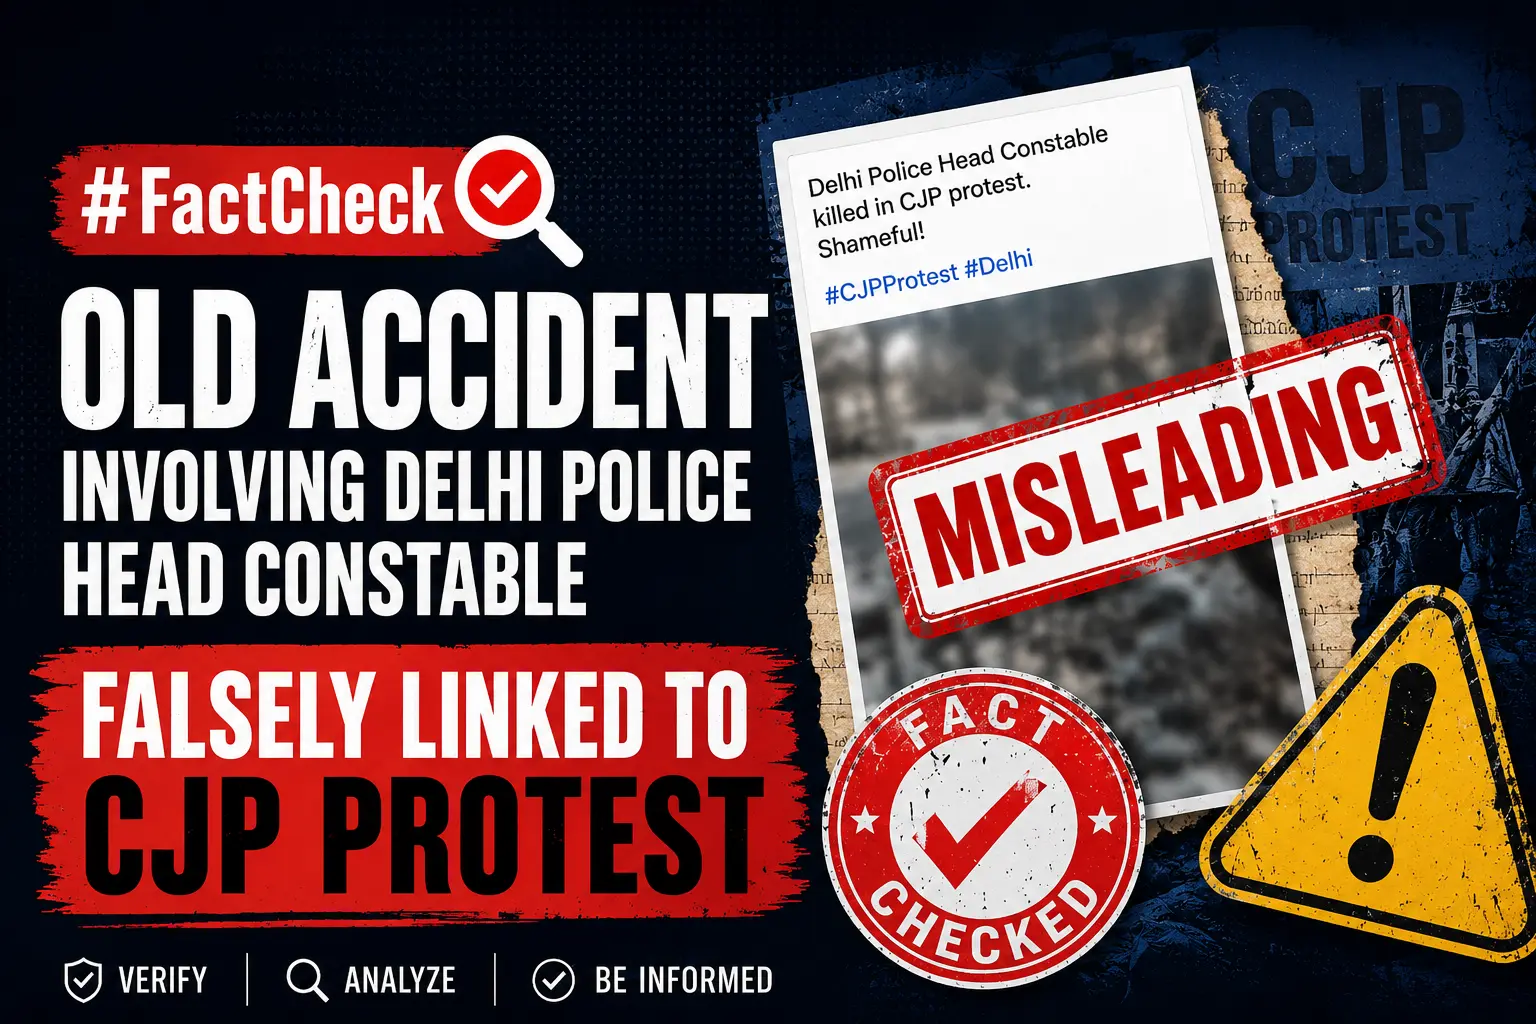
A social media post is being widely circulated claiming that Delhi Police personnel Amit died during the Cockroach Janata Party (CJP) ‘Sansad Chalo’ protest held on July 20, 2026. The post attempts to link his death to violence that allegedly took place during the demonstration. CyberPeace Research Wing’s research found the claim to be false. The research revealed that the death of Head Constable Amit was not related to the CJP protest held on July 20. He died on July 15 after being hit by a speeding vehicle while on duty at Singhu Border. An old accident has been falsely linked to the recent protest through a misleading claim.
Claim:
A Facebook user shared a post on July 23, 2026, claiming that a police personnel was martyred during the alleged protest carried out by “student goons and their supporters from Congress and Kejriwal’s party” on July 20. The user further claimed that the protest was responsible for the death of a police personnel and questioned criticism over alleged police action against protesters.
The post’s link, archive link and screenshot are provided below:
https://www.facebook.com/photo?fbid=3562630610568369&set=a.100838436747621
https://ghostarchive.org/archive/m8QM8

Fact Check:
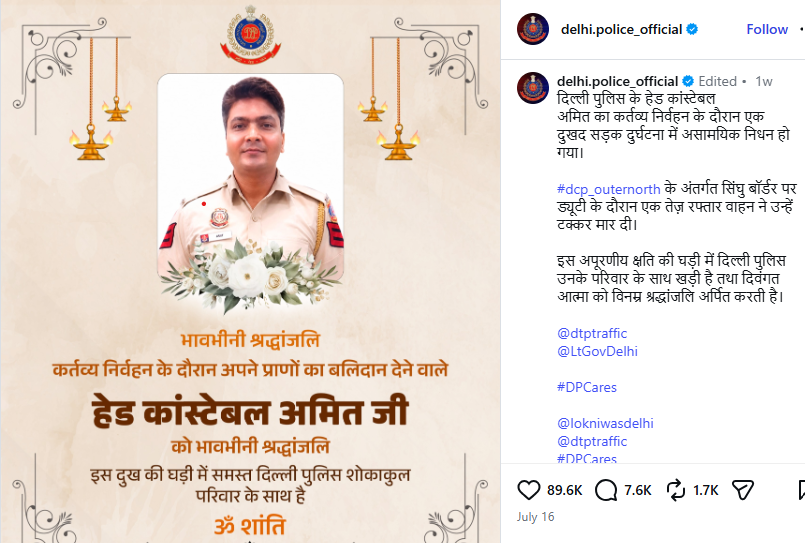
To verify the authenticity of the viral claim, the Desk first examined the official social media accounts of Delhi Police. During the research, the Desk found a post shared on Delhi Police’s official Instagram account on July 16, 2026, which contained the same image being circulated in the viral post.
https://www.instagram.com/p/Da19BQxEmQv/?igsh=cnN1bXZhaHg5OWRs
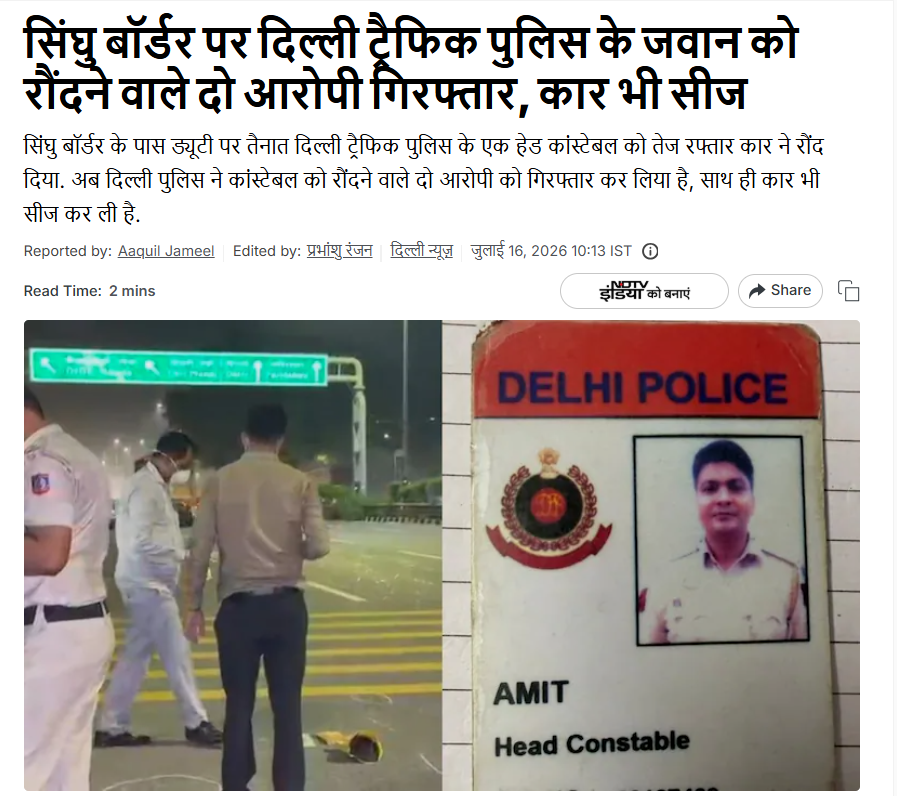
In the next stage of the research, the Desk found an NDTV report published on July 16, 2026. According to the report, Delhi Police had arrested two accused in connection with the death of Head Constable Amit. The arrested individuals were identified as Kuldeep alias Karan and Neeraj. The report stated that police had also seized the vehicle bearing registration number DL11CG2268, which was involved in the accident. An FIR was registered at Alipur Police Station and further research was underway.
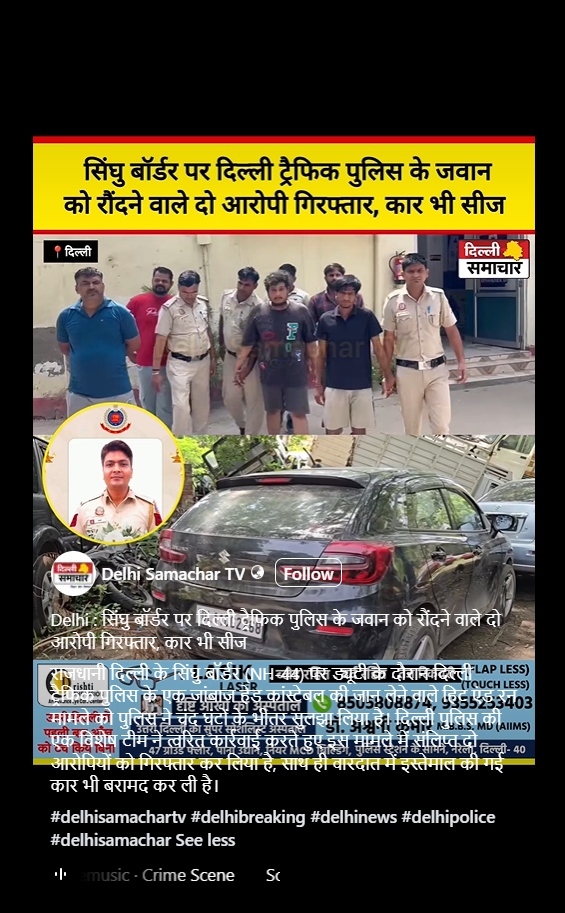
Further research led the Desk to a related post on the Facebook page of Delhi Samachar TV. According to the post, the hit-and-run case involving Head Constable Amit, who was hit while performing duty at Singhu Border (NH-44), was solved by Delhi Police within hours. The police team arrested two accused and recovered the vehicle used in the incident.
The post’s link and screenshot are provided below:
https://www.facebook.com/reel/1006635078843860
Conclusion:
The research established that the death of Delhi Police Head Constable Amit was not connected to the CJP ‘Sansad Chalo’ protest held on July 20, 2026. Amit died on July 15 after being hit by a speeding vehicle while on duty at Singhu Border. The old accident is being falsely linked to the recent protest with a misleading claim.
