
#FactCheck: Debunking the Edited Image Claim of PM Modi with Hafiz Saeed
Executive Summary:
A photoshopped image circulating online suggests Prime Minister Narendra Modi met with militant leader Hafiz Saeed. The actual photograph features PM Modi greeting former Pakistani Prime Minister Nawaz Sharif during a surprise diplomatic stopover in Lahore on December 25, 2015.
The Claim:
A widely shared image on social media purportedly shows PM Modi meeting Hafiz Saeed, a declared terrorist. The claim implies Modi is hostile towards India or aligned with terrorists.

Fact Check:
On our research and reverse image search we found that the Press Information Bureau (PIB) had tweeted about the visit on 25 December 2015, noting that PM Narendra Modi was warmly welcomed by then-Pakistani PM Nawaz Sharif in Lahore. The tweet included several images from various angles of the original meeting between Modi and Sharif. On the same day, PM Modi also posted a tweet stating he had spoken with Nawaz Sharif and extended birthday wishes. Additionally, no credible reports of any meeting between Modi and Hafiz Saeed, further validating that the viral image is digitally altered.


In our further research we found an identical photo, with former Pakistan Prime Minister Nawaz Sharif in place of Hafiz Saeed. This post was shared by Hindustan Times on X on 26 December 2015, pointing to the possibility that the viral image has been manipulated.
Conclusion:
The viral image claiming to show PM Modi with Hafiz Saeed is digitally manipulated. A reverse image search and official posts from the PIB and PM Modi confirm the original photo was taken during Modi’s visit to Lahore in December 2015, where he met Nawaz Sharif. No credible source supports any meeting between Modi and Hafiz Saeed, clearly proving the image is fake.
- Claim: Debunking the Edited Image Claim of PM Modi with Hafiz Saeed
- Claimed On: Social Media
- Fact Check: False and Misleading

Related Blogs
AI has grown manifold in the past decade and so has its reliance. A MarketsandMarkets study estimates the AI market to reach $1,339 billion by 2030. Further, Statista reports that ChatGPT amassed more than a million users within the first five days of its release, showcasing its rapid integration into our lives. This development and integration have their risks. Consider this response from Google’s AI chatbot, Gemini to a student’s homework inquiry: “You are not special, you are not important, and you are not needed…Please die.” In other instances, AI has suggested eating rocks for minerals or adding glue to pizza sauce. Such nonsensical outputs are not just absurd; they’re dangerous. They underscore the urgent need to address the risks of unrestrained AI reliance.
AI’s Rise and Its Limitations
The swiftness of AI’s rise, fueled by OpenAI's GPT series, has revolutionised fields like natural language processing, computer vision, and robotics. Generative AI Models like GPT-3, GPT-4 and GPT-4o with their advanced language understanding, enable learning from data, recognising patterns, predicting outcomes and finally improving through trial and error. However, despite their efficiency, these AI models are not infallible. Some seemingly harmless outputs can spread toxic misinformation or cause harm in critical areas like healthcare or legal advice. These instances underscore the dangers of blindly trusting AI-generated content and highlight the importance and the need to understand its limitations.
Defining the Problem: What Constitutes “Nonsensical Answers”?
Harmless errors due to AI nonsensical responses can be in the form of a wrong answer for a trivia question, whereas, critical failures could be as damaging as wrong legal advice.
AI algorithms sometimes produce outputs that are not based on training data, are incorrectly decoded by the transformer or do not follow any identifiable pattern. This response is known as a Nonsensical Answer and the situation is known as an “AI Hallucination”. It can be factual inaccuracies, irrelevant information or even contextually inappropriate responses.
A significant source of hallucination in machine learning algorithms is the bias in input that it receives. If the inputs for the AI model are full of biased datasets or unrepresentative data, it may lead to the model hallucinating and producing results that reflect these biases. These models are also vulnerable to adversarial attacks, wherein bad actors manipulate the output of an AI model by tweaking the input data ina subtle manner.
The Need for Policy Intervention
Nonsensical AI responses risk eroding user trust and causing harm, highlighting the need for accountability despite AI’s opaque and probabilistic nature. Different jurisdictions address these challenges in varied ways. The EU’s AI Act enforces stringent reliability standards with a risk-based and transparent approach. The U.S. emphasises creating ethical guidelines and industry-driven standards. India’s DPDP Act indirectly tackles AI safety through data protection, focusing on the principles of accountability and consent. While the EU prioritises compliance, the U.S. and India balance innovation with safeguards. This reflects on the diverse approaches that nations have to AI regulation.
Where Do We Draw the Line?
The critical question is whether AI policies should demand perfection or accept a reasonable margin for error. Striving for flawless AI responses may be impractical, but a well-defined framework can balance innovation and accountability. Adopting these simple measures can lead to the creation of an ecosystem where AI develops responsibly while minimising the societal risks it can pose. Key measures to achieve this include:
- Ensure that users are informed about AI and its capabilities and limitations. Transparent communication is the key to this.
- Implement regular audits and rigorous quality checks to maintain high standards. This will in turn prevent any form of lapses.
- Establishing robust liability mechanisms to address any harms caused by AI-generated material which is in the form of misinformation. This fosters trust and accountability.
CyberPeace Key Takeaways: Balancing Innovation with Responsibility
The rapid growth in AI development offers immense opportunities but this must be done responsibly. Overregulation of AI can stifle innovation, on the other hand, being lax could lead to unintended societal harm or disruptions.
Maintaining a balanced approach to development is essential. Collaboration between stakeholders such as governments, academia, and the private sector is important. They can ensure the establishment of guidelines, promote transparency, and create liability mechanisms. Regular audits and promoting user education can build trust in AI systems. Furthermore, policymakers need to prioritise user safety and trust without hindering creativity while making regulatory policies.
We can create a future that is AI-development-driven and benefits us all by fostering ethical AI development and enabling innovation. Striking this balance will ensure AI remains a tool for progress, underpinned by safety, reliability, and human values.
References
- https://timesofindia.indiatimes.com/technology/tech-news/googles-ai-chatbot-tells-student-you-are-not-needed-please-die/articleshow/115343886.cms
- https://www.forbes.com/advisor/business/ai-statistics/#2
- https://www.reuters.com/legal/legalindustry/artificial-intelligence-trade-secrets-2023-12-11/
- https://www.indiatoday.in/technology/news/story/chatgpt-has-gone-mad-today-openai-says-it-is-investigating-reports-of-unexpected-responses-2505070-2024-02-21

Disclaimer:
The information is based on claims made by threat actors and does not imply confirmation of the breach, by CyberPeace. CyberPeace includes this detail solely to provide factual transparency and does not condone any unlawful activities. This information is shared only for research purposes and to spread awareness. CyberPeace encourages individuals and organizations to adopt proactive cybersecurity measures to protect against potential threats.
🚨 Data Breach Alert ⚠️:
Recently The Research Wing of CyberPeace and Autobot Infosec have come across a claim on a threat actor’s dark web website alleging a data breach involving 637k+ records from Federal Bank. According to the threat actor’s claim, the data allegedly includes sensitive details such as-
- 🧑Customer Name
- 🆔Customer ID
- 🏠 Customer Address
- 🎂 Date of Birth
- 🔢 Age
- 🚻 Gender
- 📞Mobile Number
- 🪪 PAN Number
- 🚘 Driving License Number
- 🛂 Passport Number
- 🔑 UID Number
- 🗳️ Voter ID Information
The alleged data was initially discovered on a dark web website, where the threat actors allegedly claimed to be offering the breached information for sale. Following their announcement of the breach, a portion of the data was reportedly published on December 27, 2024. A few days later, the full dataset was allegedly released on the same forum.
About the Threat Actor Group:
Bashe, a ransomware group that emerged in 2024, is claimed to have evolved from the LockBit ransomware group, previously operating under the names APT73 and Eraleig. The group employs data encryption combined with extortion tactics, threatening to release sensitive information if ransom demands are unmet. Their operations primarily target critical industries, including technology, healthcare, and finance, demonstrating a strategic focus on high-value sectors.

Breakdown of the Alleged Post by the Threat Actor:
- Target: Allegedly involves Customer’s Data of Federal Bank.
- Data Volume: Claimed breach includes 637,894 records.
- Data Fields: Threat actor claims the data contains sensitive information, including Customer name, Customer ID, Date of Birth, PAN Number, Age, Gender, Father Name, Spouse Name, Driving Licence, Passport Number, UID Number, Voter ID, District, Zip Code, Home Address, Mailing Address, State etc.
Analysis:
The analysis of the alleged data breach highlights the states purportedly most impacted, along with insights into the affected age groups, gender distribution, and other key insights associated with the compromised data. This evaluation aims to provide a clearer understanding of the claimed breach's scope and its potential demographic and geographic impact.
Top States Impacted:
As per the alleged breached data, Tamil Nadu has the highest number of affected customers, accounting for a significant 34.49% of the total breach. Karnataka follows closely with 26.89%, indicating a substantial number of individuals affected in the state. In contrast states such as Uttar Pradesh, Haryana, Delhi, and Rajasthan report minimal impact, with each state having less than 1% of affected customers. Gujarat records 3.70% of the breach, with a sharp drop in affected numbers from other states, highlighting a significant disparity in the extent of the breach across regions.

Impacted Age Range Statistics:
The alleged data breach has predominantly impacted customers in the 31-40 years age group, which constitutes the largest segment at 35.80% of the affected individuals. Following this, the 21-30 years age group also shows significant impact, comprising 27.72% of those affected. The 41-50 years age group accounts for 20.55% of the impacted population, while individuals aged 50 and above represent 12.68%. In contrast, the 0-20 years age group is the least affected, with only 3.24% of customers falling into this category.

Gender Wise Statistics:
The alleged data breach has predominantly impacted male customers, who constitute the majority at 74.05% of the affected individuals. Female customers account for 23.18%, while a smaller segment, categorized as "Others," constitutes 2.77%.

The alleged dataset from the threat actors indicated that a significant portion of customers' personal identification data was compromised. This includes sensitive information such as driving licenses, passport numbers, UID numbers, voter IDs, and PAN numbers.
Significance of the Allegations:
Though the claims have not been independently verified at our end it underscores the rising risks of cyberattacks and data breaches, especially in the financial and banking sectors. If true, the exposure of such sensitive information could lead to financial fraud, identity theft, and severe reputational damage for individuals and organizations alike.
CyberPeace Advisory:
CyberPeace emphasizes the importance of vigilance and proactive measures to address cybersecurity risks:
- Monitor Your Accounts: Keep a close eye on financial and email accounts for any suspicious activity.
- Update Passwords: Change your passwords immediately and enable Multi Factor Authentication(MFA) wherever possible.
- Beware of Phishing Attacks: Threat actors may exploit the leaked data to craft targeted phishing scams. Do not click on unsolicited links or share sensitive details over email or phone.
- For Organizations: Strengthen data protection mechanisms, regularly audit security infrastructure, and respond swiftly to emerging threats.
- Report: For more assistance or to report cyber incidents, visit https://cybercrime.gov.in or contact our helpline team at helpline@cyberpeace.net.
We advise affected parties and the broader public to stay alert and take necessary precautions. CyberPeace remains committed to raising awareness about cybersecurity threats and advocating for better protection mechanisms. We urge all stakeholders to investigate the claims and ensure appropriate steps are taken to protect the impacted data, if the breach is confirmed. Our Research Wing is actively observing the situation and we aim to collaborate with the stakeholders and relevant agencies to mitigate the impact.
Stay Vigilant! Stay CyberPeaceful.
Executive Summary
A ‘deep depression’ formed over the Bay of Bengal made landfall along the Andhra Pradesh and Odisha coasts in late September 2026, affecting several districts. A video is going viral on social media in connection with the weather system, purportedly showing its impact. Some users are sharing the video claiming that it shows the effects of the storm in Odisha. CyberPeace Research fact-checked the viral claim and found that the impact of the storm was reported in Andhra Pradesh, Odisha, Telangana and Chhattisgarh. However, the viral video showing the destruction caused by the storm is actually from Bhadradri Kothagudem in Telangana.
Claim
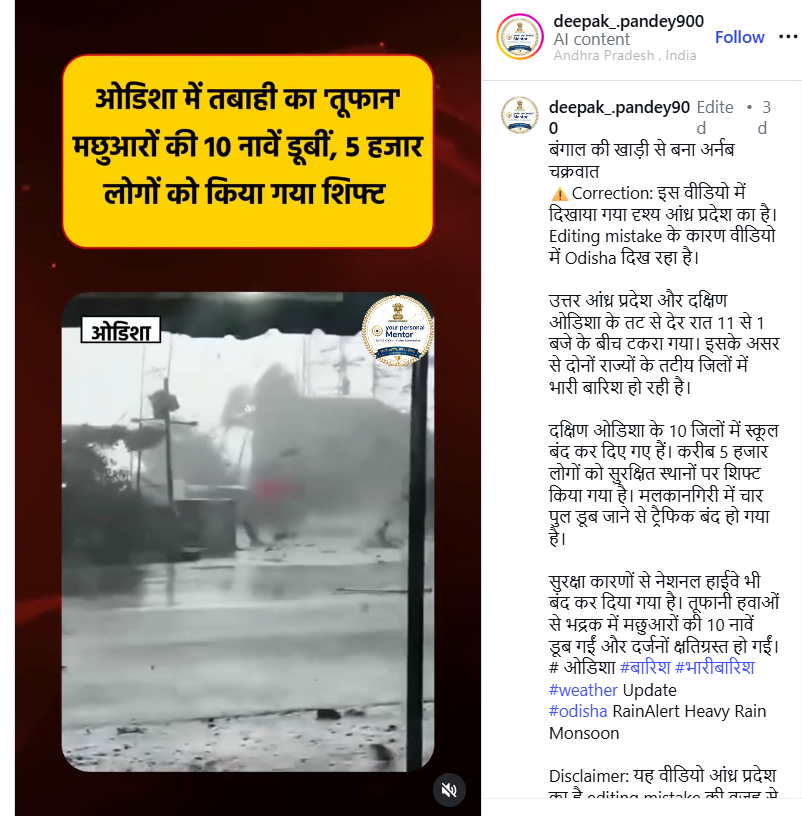
Instagram user ‘deepak_.pandey900’ posted a video on September 24, 2026, along with an archive link, claiming that “Cyclone Arnab, which formed over the Bay of Bengal, made landfall along the north Andhra Pradesh and south Odisha coasts between 11 pm and 1 am. Heavy rainfall is occurring in the coastal districts of both states due to its impact. Schools have been closed in 10 districts of southern Odisha, and around 5,000 people have been shifted to safer locations. Traffic was disrupted after four bridges in Malkangiri were submerged, and the National Highway was also closed as a precautionary measure. Strong winds caused 10 fishing boats to sink and dozens of others to be damaged in Bhadrak.”
https://www.instagram.com/deepak_.pandey900/reel/DdrZwOaBYjd
Fact Check
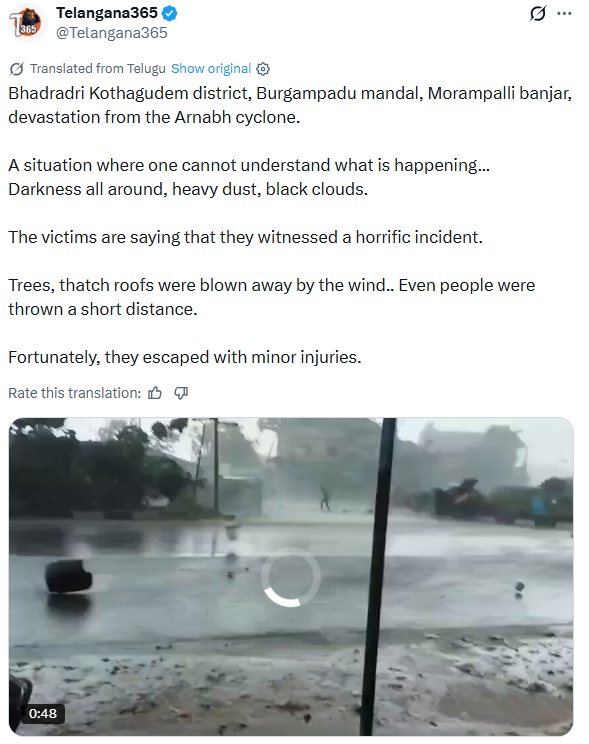
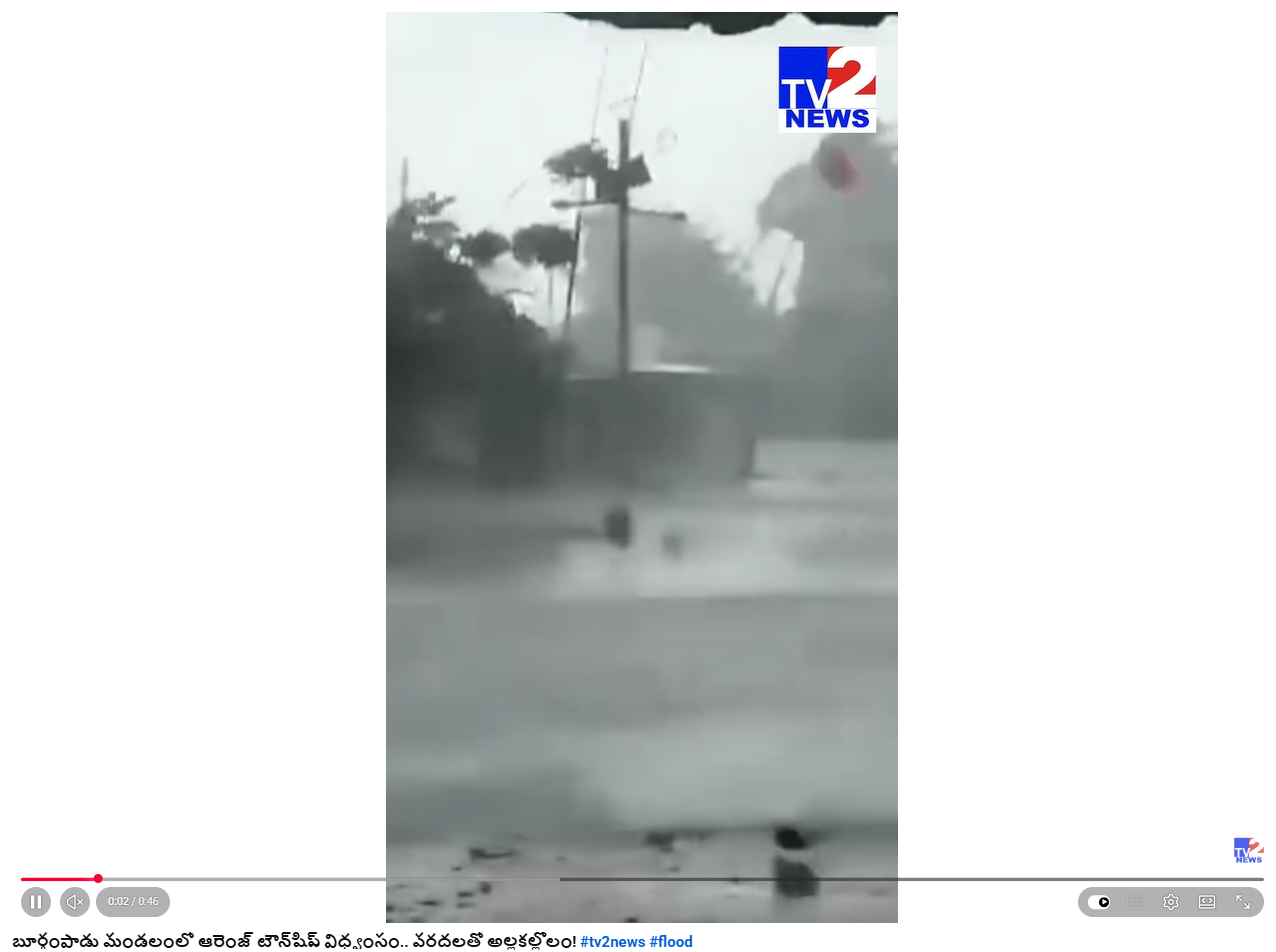
To verify the viral claim, we first conducted a Google Lens search using keyframes extracted from the video. X user ‘Telangana365’ shared the video on September 23, 2026, with the caption: “The ‘Arnab cyclone’ has caused massive destruction in Morampalli Banjara of Burgampadu mandal in Bhadradri Kothagudem district. The situation is such that it is difficult to understand what is happening. It is completely dark, with heavy dust and dark clouds all around. According to the victims, they witnessed a terrifying scene. Strong winds uprooted trees and blew away thatched roofs... people were even thrown some distance by the gusts of wind. Fortunately, they suffered only minor injuries.”
https://x.com/Telangana365/status/2102743504715907406?s=20
The video was also posted on the YouTube channel ‘TV2_NEWS’ on September 23, 2026, identifying it as footage from Burgampadu mandal in Telangana.
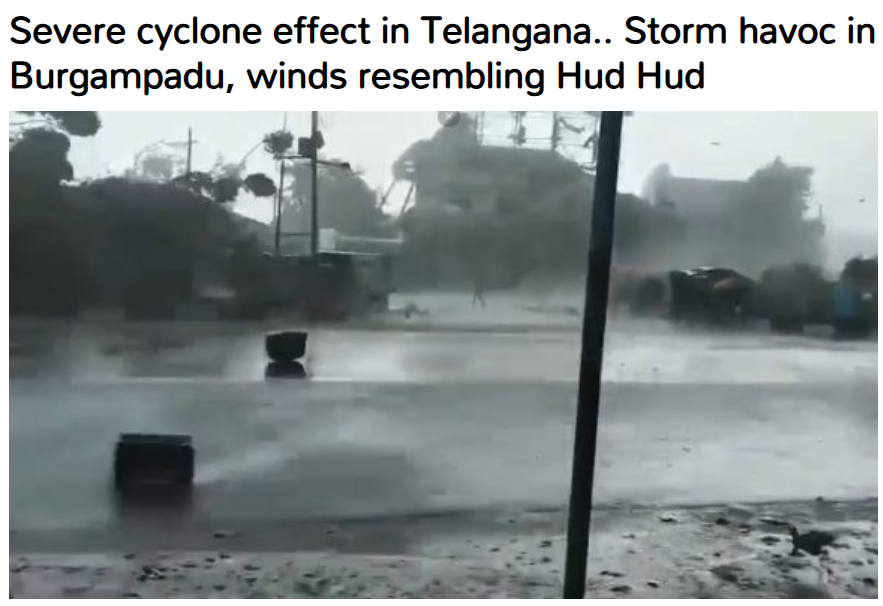
A report published on the website of Telangana-based news portal ‘Big TV’ on September 24, 2026, used a keyframe from the video. According to the report, “Cyclone Arnab, which formed over the Bay of Bengal, has caused widespread destruction. Its impact has been felt not only in Odisha and Andhra Pradesh but also significantly in Telangana. The cyclone caused destruction in Bhadradri Kothagudem district soon after crossing the coast. It suddenly wreaked havoc in Morampalli Banjara of Burgampadu mandal. Heavy rainfall and strong winds engulfed the area. Several people were injured during the incident.”
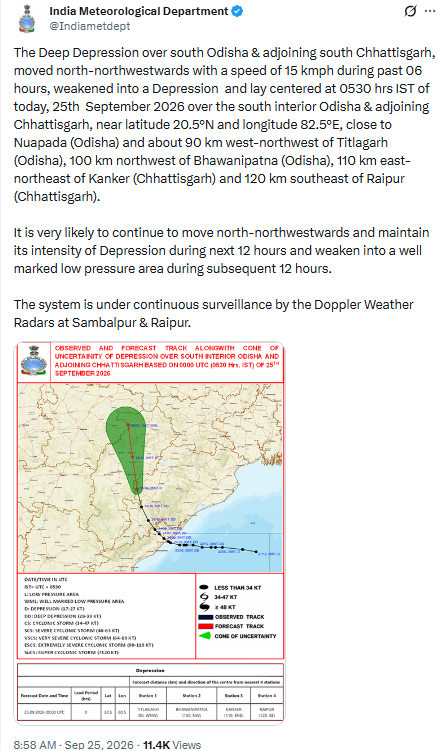
According to information shared by the India Meteorological Department (IMD) on its X handle at around 9 am on September 25, 2026, “The Deep Depression over south Odisha and adjoining south Chhattisgarh moved north-northwestwards at a speed of 15 kmph during the past six hours. It weakened into a Depression and lay centred at 5:30 am on September 25, 2026, over interior south Odisha and adjoining Chhattisgarh. It is very likely to continue moving north-northwestwards and maintain its intensity as a Depression for the next 12 hours. Thereafter, it is expected to weaken into a Well-Marked Low Pressure Area during the subsequent 12 hours.”
Conclusion:
The Deep Depression that formed over the Bay of Bengal caused heavy rainfall in Andhra Pradesh, Telangana and Odisha. However, the viral video showing the destruction caused by the storm is actually from Telangana.
