
#FactCheck: Beware of Fake Emails Distributing Fraudulent e-PAN Cards
Executive Summary:
We have identified a post addressing a scam email that falsely claims to offer a download link for an e-PAN Card. This deceptive email is designed to mislead recipients into disclosing sensitive financial information by impersonating official communication from Income Tax Department authorities. Our report aims to raise awareness about this fraudulent scheme and emphasize the importance of safeguarding personal data against such cyber threats.

Claim:
Scammers are sending fake emails, asking people to download their e-PAN cards. These emails pretend to be from government authorities like the Income Tax Department and contain harmful links that can steal personal information or infect devices with malware.
Fact Check:
Through our research, we have found that scammers are sending fake emails, posing as the Income Tax Department, to trick users into downloading e-PAN cards from unofficial links. These emails contain malicious links that can lead to phishing attacks or malware infections. Genuine e-PAN services are only available through official platforms such as the Income Tax Department's website (www.incometaxindia.gov.in) and the NSDL/UTIITSL portals. Despite repeated warnings, many individuals still fall victim to such scams. To combat this, the Income Tax Department has a dedicated page for reporting phishing attempts: Report Phishing - Income Tax India. It is crucial for users to stay cautious, verify email authenticity, and avoid clicking on suspicious links to protect their personal information.

Conclusion:
The emails currently in circulation claiming to provide e-PAN card downloads are fraudulent and should not be trusted. These deceptive messages often impersonate government authorities and contain malicious links that can result in identity theft or financial fraud. Clicking on such links may compromise sensitive personal information, putting individuals at serious risk. To ensure security, users are strongly advised to verify any such communication directly through official government websites and avoid engaging with unverified sources. Additionally, any phishing attempts should be reported to the Income Tax Department and also to the National Cyber Crime Reporting Portal to help prevent the spread of such scams. Staying vigilant and exercising caution when handling unsolicited emails is crucial in safeguarding personal and financial data.
- Claim: Fake emails claim to offer e-PAN card downloads.
- Claimed On: Social Media
- Fact Check: False and Misleading

Related Blogs
Introduction
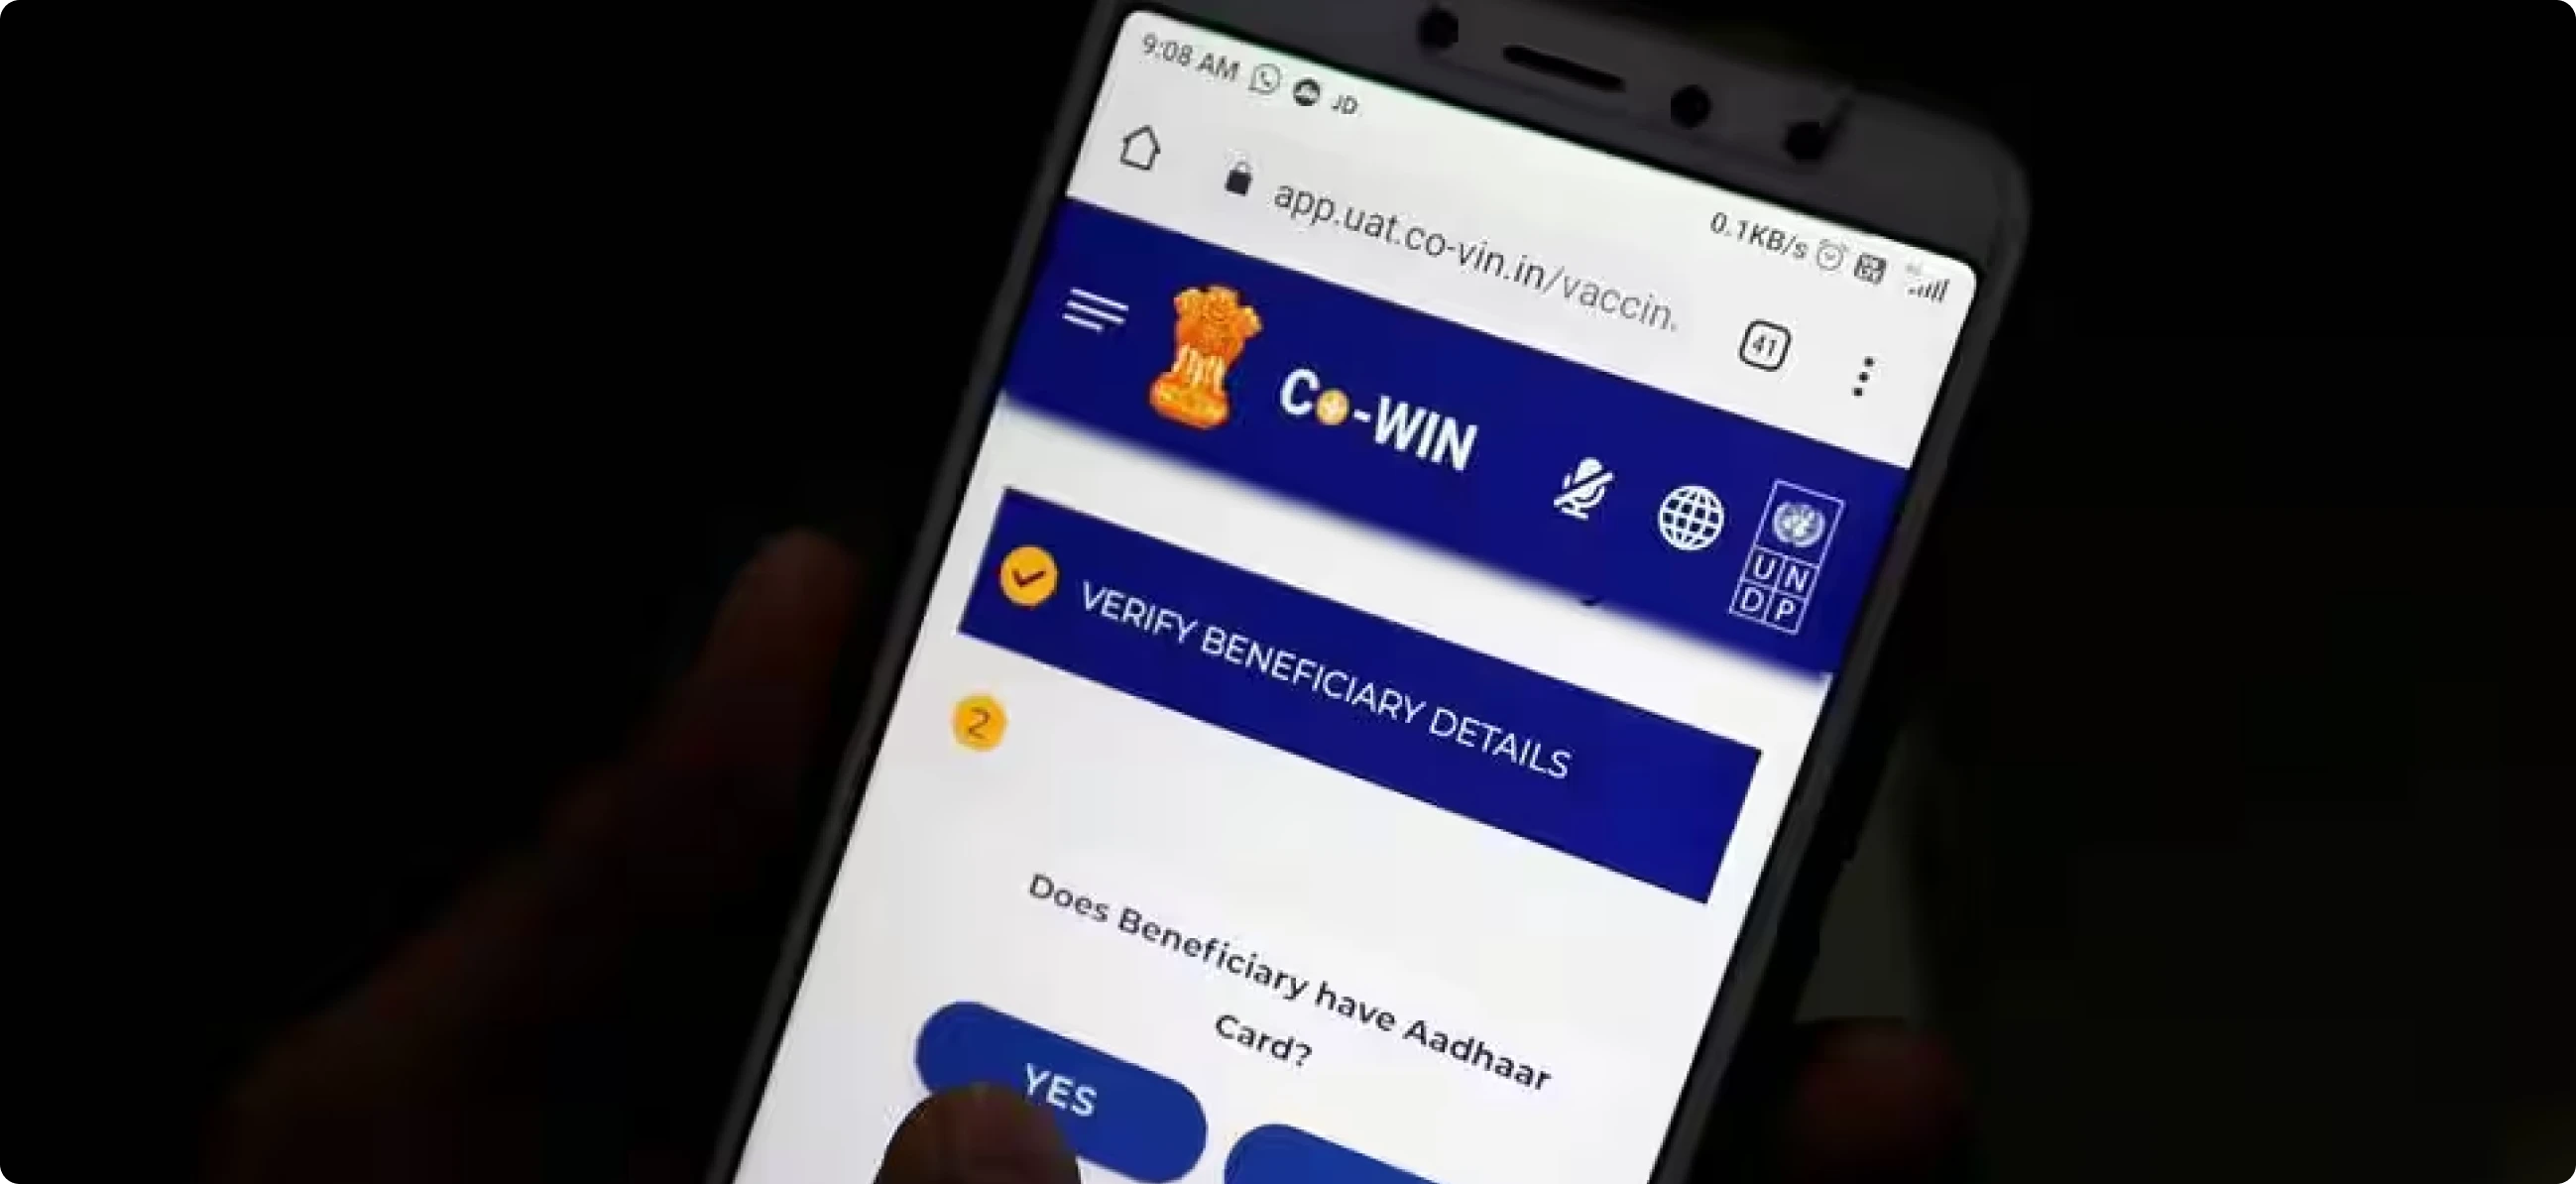
The information of hundreds of thousands of Indians who received the COVID vaccine was Leaked in a significant data breach and posted on a Telegram channel. Numerous reports claim that sensitive information, including a person’s phone number, gender, ID card details, and date of birth, leaked over Telegram. It could be obtained by typing a person’s name into a Telegram bot.
What really happened?
The records pertaining to the mobile number registered in the CoWin portal are accessible on the Malayalam news website channel. It is also feasible to determine which vaccination was given and where it was given.
According to The Report, the list of individuals whose data was exposed includes BJP Tamil Nadu president K Annamalai, Congress MP Karti Chidambaram, and former BJP union minister for health Harsh Vardhan. Telangana’s minister of information and communication technology, Kalvakuntla Taraka Rama Rao, is also on the list.
MEITY stated in response to the data leak, “It is old data, we are still confirming it. We have requested a report on the matter.
After the media Report, the bot was disabled, but experts said the incident raised severe issues because the information might be used for identity theft, phishing emails, con games, and extortion calls. The Indian Computer Emergency Response Team (CERT-In), the government’s nodal body, has opened an investigation into the situation
The central government declared the data breach reports regarding the repository of beneficiaries against Covid to be “mischievous in nature” on Monday and claimed the ‘bot’ that purportedly accessed the confidential data was not directly accessing the CoWIN database.
According to the first complaint by CERT-In, the government’s cybersecurity division, the government claimed the bot might be displaying information from “previously stolen data.” Reports.
The health ministry refuted the claim, asserting that no bots could access the information without first verifying with a one-time password.
“It is made clear that all of these rumours are false and malicious. The health ministry’s CoWIN interface is entirely secure and has sufficient data privacy protections. The security of the data on the CoWIN portal is being ensured in every way possible, according to a statement from the health ministry.
Meity said the CoWin program or database was not directly compromised, and the shared information appeared to be taken from a previous intrusion. But the hack again highlights the growing danger of cyber assaults, particularly on official websites.

Recent cases of data leak
Dominos India 2021– Dominos India, a division of Jubilant FoodWorks, faced a cyberattack on May 22, 2021, which led to the disclosure of information from 180 million orders. The breach exposed order information, email addresses, phone numbers, and credit card information. Although Jubilant FoodWorks acknowledged a security breach, it refuted any illegal access to financial data.
Air India – A cyberattack that affected Air India in May 2021 exposed the personal information of about 4.5 million customers globally. Personal information recorded between August 26, 2011, and February 3, 2021, including names, dates of birth, contact information, passport information, ticket details, frequent flyer information from Star Alliance and Air India, and credit card information, were exposed in the breach.
Bigbasket – BigBasket, an online supermarket, had a data breach in November 2020, compromising the personal information of approximately 20 million consumers. Email IDs, password hashes, PINs, phone numbers, addresses, dates of birth, localities, and IP addresses were among the information released from an insecure database containing over 15 GB of customer data. BigBasket admitted to the incident and reported it to the Bengaluru Cyber Crime Department.
Unacademy – Unacademy, an online learning platform, experienced a data breach in May 2020, compromising the email addresses of approximately 11 million subscribers. While no sensitive information, such as financial data or passwords, was compromised, user data, including IDs, passwords, date joined, last login date, email IDs, names, and user credentials, was. The breach was detected when user accounts were uncovered for sale on the dark web.
2022 Card Data- Cybersecurity researchers from AI-driven Singapore-based CloudSEK found a threat actor offering a database of 1.2 million cards for free on a Dark Web forum for crimes on October 12, 2022. This came after a second problem involving 7.9 million cardholder records that were reported on the BidenCash website. This comprised information pertaining to State Bank of India (SBI) clients. And other well-known companies were among those targeted in high-profile data breach cases that have surfaced in recent years.

Conclusion
Data breach cases are increasing daily, and attackers are mainly attacking the healthcare sectors and health details as they can easily find personal details. This recent CoWIN case has compromised thousands of people’s data. The All-India Institute of Medical Sciences’ systems were compromised by hackers a few months ago. Over 95% of adults have had their vaccinations, according to the most recent data, even if the precise number of persons impacted by the CoWin privacy breach could not be determined.
The digital ecosystem of India has experienced rapid growth, which has created numerous opportunities for economic development, better governance and increased social connections. The increasing use of digital technology has resulted in a higher incidence of cyber-enabled crimes, which include online fraud and cyber harassment, child exploitation and the spread of misinformation. The Government of India has established multiple initiatives to enhance a complete and unified framework that will help in combatting cybercrime more effectively. The latest updates presented to Parliament demonstrate how different institutional frameworks and legal provisions, capacity building efforts, and public awareness programs work together to handle new cyber threats.
A Coordinated Institutional Framework
The Indian system for investigating and prosecuting cybercrimes assigns responsibility to States and Union Territories, which operate their own Law Enforcement Agencies. The central government established the Indian Cyber Crime Coordination Centre (I4C) to support these operations through its Ministry of Home Affairs.
The I4C functions as a central hub that allows various stakeholders in cybercrime prevention and investigation to share intelligence and build their operational capacities. The initiative establishes a cybersecurity system that will improve its organisational structure through better central and state agency collaboration.
The National Cyber Crime Reporting Portal (NCCRP) serves as a primary project of this framework by providing online cyber incident reporting for citizens. The portal enables users to register complaints more efficiently while enhancing access to crime reporting, which particularly benefits victims of crimes against women and children. The system offers special channels which allow users to report Child Sexual Exploitative and Abuse Material (CSEAM) and rape-related materials while providing options for anonymous reporting and case tracking. After a complaint is lodged, the appropriate state authorities initiate the process to investigate the matter and proceed with legal procedures.
Capacity Building and Cyber Forensics
The response to cybercrime requires both expert investigators and advanced forensic technology systems. The Cyber Crime Prevention against Women and Children (CCPWC) Scheme, which provides financial backing and technical training to states and union territories, was instituted by the Ministry of Home Affairs to address this requirement.
The scheme has authorised the release of ₹132.93 crore for developing cyber forensic facilities and investigative technologies. The funding has supported the establishment of cyber forensic-cum-training laboratories across multiple states and union territories. The total number of operational laboratories has reached 33 at this time.
The organisation has prioritised its training initiatives together with its infrastructure development projects. More than 24,600 law enforcement personnel, prosecutors, and judicial officers have received training on cybercrime investigation, digital evidence handling, and forensic analysis. The capacity-building initiatives were designed to provide investigators and judicial authorities with essential skills needed to handle advanced cyber incidents.
International Cooperation for Child Protection
International cooperation is essential for addressing online child exploitation because these crimes utilise digital networks that connect multiple countries. The National Crime Records Bureau (NCRB) established a partnership with the National Centre for Missing and Exploited Children (NCMEC) of the United States in 2019 through a Memorandum of Understanding, which aims to enhance regional collaboration in this field.
The partnership enables the sharing of tipline reports about online child exploitation, which Indian authorities use for their investigative work. Under the Information Technology Act provisions, NCRB has received official powers to issue removal notices to intermediaries because they oversee child sexual abuse material and other dangerous content.
Promoting Online Safety Awareness
Cybercrime prevention requires two essential elements, which are public knowledge and digital expertise. The National Commission for Protection of Child Rights (NCPCR) has developed several resources to educate children, parents, teachers, and school administrators about online safety. The guidelines include Being Safe Online, together with school safety manuals that protect against cyberbullying and the 2024 updates, which provide new recommendations for cyberbullying prevention. The commission has established multiple conferences and training sessions throughout various states to educate both educators and school administrators about child protection regulations and school security measures, and cyber protection standards.
The digital responsibility programs educate communities about proper online conduct and teach them how to recognise and handle cybersecurity threats.
Legal Framework for Digital Safety
The Information Technology Act of 2000, together with the Information Technology Intermediary Guidelines and Digital Media Ethics Code Rules of 2021, (Updated as of 2026) serve as the core legal foundation through which India combats cybercrime. The laws establish penalties for online distribution of obscene and sexually explicit material while requiring digital intermediaries to block access to illegal content.
The Bharatiya Nyaya Sanhita 2023 contains additional legal provisions that deal with two types of offences that involve disseminating obscene material and spreading dangerous misinformation.
The regulatory framework requires intermediaries to eliminate illegal content within specified timeframes, while they must prevent their platforms from being used to conduct dangerous or unlawful activities.
Conclusion
India establishes its cybercrime response strategy through a multi-layered method that uses different institutional systems, technological systems, legal systems, and public education programs. Cyber threats develop through technological progress, yet authorities must establish effective cybersecurity, which depends on their ability to investigate, their systems for reporting incidents, and their dedication to maintaining proper online conduct.
India needs continuous cooperation among government bodies, police forces, technology companies, and community organisations to maintain secure and strong digital networks that provide equal access to all citizens.
References
- https://www.pib.gov.in/PressReleasePage.aspx?PRID=2238260®=3&lang=2
- https://www.policyedge.in/p/rajya-sabha-strengthening-indias-coordinated-response-to-cyber-crimes

Executive Summary:
Microsoft rolled out a set of major security updates in August, 2024 that fixed 90 cracks in the MS operating systems and the office suite; 10 of these had been exploited in actual hacker attacks and were zero-days. In the following discussion, these vulnerabilities are first outlined and then a general analysis of the contemporary cyber security threats is also undertaken in this blog. This blog seeks to give an acquainted and non-acquainted audience about these updates, the threat that these exploits pose, and prevent measures concerning such dangers.
1. Introduction
Nowadays, people and organisations face the problem of cybersecurity as technologies develop and more and more actions take place online. These cyber threats have not ceased to mutate and hence safeguarding organisations’ digital assets requires a proactive stand. This report is concerned with the vulnerabilities fixed by Microsoft in August 2024 that comprised a cumulative of 90 security weaknesses where six of them were zero-day exploits. All these make a terrible risk pose and thus, it is important to understand them as we seek to safeguard virtual properties.
2. Overview of Microsoft’s August 2024 Security Updates
August 2024 security update provided by Microsoft to its products involved 90 vulnerabilities for Windows, Office, and well known programs and applications. These updates are of the latest type which are released by Microsoft under its Patch Tuesday program, a regular cum monthly release of all Patch updates.
- Critical Flaws: As expected, seven of the 90 were categorised as Critical, meaning that these are flaws that could be leveraged by hackers to compromise the targeted systems or bring operations to a halt.
- Zero-Day Exploits: A zero-day attack can be defined as exploits, which are as of now being exploited by attackers while the software vendor has not yet developed a patch for the same. It had managed 10 zero-days with the August update, which underlines that Microsoft and its ecosystems remain at risk.
- Broader Impact: These are not isolated to the products of Microsoft only They still persist Despite this, these vulnerabilities are not exclusive to the Microsoft products only. Other vendors such as Adobe, Cisco, Google, and others also released security advisories to fix a variety of issues which proves today’s security world is highly connected.
3. Detailed Analysis of Key Vulnerabilities
This section provides an in-depth analysis of some of the most critical vulnerabilities patched in August 2024. Each vulnerability is explained in layman’s terms to ensure accessibility for all readers.
3. 1 CVE-2024-38189: Microsoft Project Remote Code Execution Vulnerability (CVSS score:8. 8) :
The problem is in programs that belong to the Microsoft Project family which is known to be a popular project management system. The vulnerability enables an attacker to produce a file to entice an user into opening it and in the process execute code on the affected system. This could possibly get the attacker full control of the user’s system as mentioned in the following section.
Explanation for Non-Technical Readers: Let us assume that one day you received a file which appears to be a normal word document. When it is opened, it is in a format that it secretly downloads a problematic program in the computer and this goes unnoticed. This is what could happen with this vulnerability, that is why it is very dangerous.
3. 2 CVE-2024-38178: Windows Scripting Engine Memory Corruption Vulnerability (CVSS score: 7.5):
Some of the risks relate to a feature known as the Windows Scripting Engine, which is an important system allowing a browser or an application to run scripts in a web page or an application. The weak point can result in corruption of memory space and an attacker can perform remote code execution with the possibility to affect the entire system.
Explanation for Non-Technical Readers: For the purpose of understanding how your computer memory works, imagine if your computer’s memory is a library. This vulnerability corrupts the structure of the library so that an intruder can inject malicious books (programs) which you may read (execute) on your computer and create havoc.
3. 3 CVE-2024-38193: WinSock Elevation of Privilege Vulnerability (CVSS score: 7. 8 )
It opens up a security weakness in the Windows Ancillary Function Driver for WinSock, which is an essential model that masks the communication between the two. It enables the attacker to gain new privileges on the particular system they have attacked, in this case they gain some more privileges on the attacked system and can access other higher activities or details.
Explanation for Non-Technical Readers: This flaw is like somebody gaining access to the key to your house master bedroom. They can also steal all your valuable items that were earlier locked and could only be accessed by you. It lets the attacker cause more havoc as soon as he gets inside your computer.
3. 4 CVE-2024-38106: Windows Kernel Elevation of Privilege Vulnerability (CVSS score: 7. 0)
This vulnerability targets what is known as the Windows Kernel which forms the heart or main frameworks of the operating system that controls and oversees the functions of the computer components. This particular weakness can be exploited and an opponent will be able to get high-level access and ownership of the system.
Explanation for Non-Technical Readers: The kernel can be compared to the brain of your computer. It is especially dangerous that if someone can control the brain he can control all the rest, which makes it a severe weakness.
3. 5 CVE-2024-38213: Windows Mark of the Web Security Feature Bypass Vulnerability (CVSS score: 6.5).
This vulnerability enables the attackers to evade the SmartScreen component of Windows which is used to safeguard users from accessing unsafe files. This weakness can be easily used by the attackers to influence the users to open files that are otherwise malicious.
Explanation for Non-Technical Readers: Usually, before opening a file your computer would ask you in advance that opening the file may harm your computer. This weak point makes your computer believe that this dangerous file is good and then no warning will be given to you.
4. Implications of the Vulnerabilities
These vulnerabilities, importantly the zero-day exploits, have significant implications on all users.
- Data Breaches: These weaknesses can therefore be manipulated to cause exposures of various data, occasioning data leaks that put individual and corporate information and wealth.
- System Compromise: The bad guys could end up fully compromising the impacted systems meaning that they can put in malware, pilfer data or simply shut down a program.
- Financial Loss: The organisations that do not patch these vulnerabilities on the shortest notice may end up experiencing a lot of losses because of having to deal with a lot of downtimes on their systems, having to incur the costs of remediating the systems that have been breached and also dealing with legal repercussions.
- Reputation Damage: Security breaches and IT system corruptions can result in loss of customer and partner confidence in an organisation’s ability to protect their information affecting its reputation and its position in the market.
5. Recommendations for Mitigating Risks
Immediate measures should be taken regarding the risks linked to these issues since such weaknesses pose a rather high threat. The following are recommendations suitable for both technical and non-technical users.
5. 1 Regular Software Updates
Make it a point that all the software, particularly operating systems and all Microsoft applications are updated. Any system out there needs to update it from Microsoft, and its Patch Tuesday release is crucial.
For Non-Technical Users: As much as possible, reply ‘yes’ to updates whenever your computer or smartphone prompts for it. These updates correct security matters and secure your instruments.
5. 2 Realisation of Phishing Attacks
Most of the risks are normally realised through phishing techniques. People should be taught diversifiable actions that come with crazy emails like clicking on links and opening attachments.
For Non-Technical Users: Do not respond to emails from unknown people and if they make you follow a link or download a file, do not do it. If it looks like spam, do not click on it.
5. 3 Security Software
Strong and reliable antivirus and anti-malware software can be used to identify and avoid the attacks that might have high chances of using these vulnerabilities.
For Non-Technical Users: Ensure you download a quality antivirus and always update it. This works like a security guard to your computer by preventing bad programs.
5. 4 Introduce Multi Factor Authentication (MFA)
MFA works in a way to enforce a second factor of authentication before the account can be accessed; for instance, a user will be asked to input a text message or an authentication application.
For Non-Technical Users: NS is to make use of two-factor authentication on your accounts. It is like increasing the security measures that a man who has to burgle a house has to undergo by having to hammer an additional lock on the door.
5. 5 Network segmentations and Privileges management
Network segmentation should be adopted by organisations to prevent the spread of attacks while users should only be granted the privileges required to do their activities.
For Non- Technical Users: Perform the assessments of user privileges and the networks frequently and alter them in an effort of reducing the extent of the attacks.
6. Global Cybersecurity Landscape and Vendor Patches
The other major vendors have also released patches to address security vulnerabilities in their products. The interdependent nature of technology has the effect on the entire digital ecosystem.
- Adobe, Cisco, Google, and Others: These companies have released updates to address the weaknesses in their products that are applied in different sectors. These patches should be applied promptly to enhance cybersecurity.
- Collaboration and Information Sharing:Security vendors as well as researchers and experts in the cybersecurity domain, need to remain vigilant and keep on sharing information on emerging threats in cyberspace.
7. Conclusion
The security updates companies such as Microsoft and other vendors illustrate the present day fight between cybersecurity experts and cybercriminals. All the vulnerabilities addressed in this August 2024 update cycle are a call for prudence and constant protection of digital platforms. These vulnerabilities explain the importance of maintaining up-to-date systems, being aware of potential threats, and implementing robust security practices. Therefore, it is important to fortify our shield in this ever expanding threat domain, in order to be safe from attackers who use this weakness for their malicious purposes.
