
#FactCheck - Old Japanese Earthquake Footage Falsely Linked to Tibet
Executive Summary:
A viral post on X (formerly Twitter) gained much attention, creating a false narrative of recent damage caused by the earthquake in Tibet. Our findings confirmed that the clip was not filmed in Tibet, instead it came from an earthquake that occurred in Japan in the past. The origin of the claim is traced in this report. More to this, analysis and verified findings regarding the evidence have been put in place for further clarification of the misinformation around the video.

Claim:
The viral video shows collapsed infrastructure and significant destruction, with the caption or claims suggesting it is evidence of a recent earthquake in Tibet. Similar claims can be found here and here

Fact Check:
The widely circulated clip, initially claimed to depict the aftermath of the most recent earthquake in Tibet, has been rigorously analyzed and proven to be misattributed. A reverse image search based on the Keyframes of the claimed video revealed that the footage originated from a devastating earthquake in Japan in the past. According to an article published by a Japanese news website, the incident occurred in February 2024. The video was authenticated by news agencies, as it accurately depicted the scenes of destruction reported during that event.

Moreover, the same video was already uploaded on a YouTube channel, which proves that the video was not recent. The architecture, the signboards written in Japanese script, and the vehicles appearing in the video also prove that the footage belongs to Japan, not Tibet. The video shows news from Japan that occurred in the past, proving the video was shared with different context to spread false information.

The video was uploaded on February 2nd, 2024.
Snap from viral video

Snap from Youtube video

Conclusion:
The video viral about the earthquake recently experienced by Tibet is, therefore, wrong as it appears to be old footage from Japan, a previous earthquake experienced by this nation. Thus, the need for information verification, such that doing this helps the spreading of true information to avoid giving false data.
- Claim: A viral video claims to show recent earthquake destruction in Tibet.
- Claimed On: X (Formerly Known As Twitter)
- Fact Check: False and Misleading

Related Blogs

Introduction
Rapid growth in India’s Digital Economy has opened up various options for companies to utilise digital technology as part of their operations. Examples of these technologies include cloud computing; online payment systems; digitally enabled supply chains; and platforms that facilitate remote working. As small and medium enterprises(SMEs) represent a major part of India’s economy, they have quickly been able to capitalise on the benefits these technologies provide in improving their operational efficiency and developing an increased presence within the market. However, this rapid pace of digitalisation creates an exposure to a much greater breadth of cyber-security threats than ever for SMEs. Today, perhaps the greatest cyber-threat facing SMEs in India is ransomware, an increasing frequent type of cyber-attack that has been increasing on a global scale over the past few years and in response, there have been numerous initiatives by various government agencies, industry organisations, and cyber-security firms designed to educate the general public on the risks of ransomware.
What is Ransomware?
Ransomware is a type of malware, which prevents all users being able to access their file system or access their data until they pay a ransom. In a standard ransomware event an attacker will breach the company's network, and encrypt all critical files so that they are unable to be used. The attacker usually demands payment in bitcoin because it is a difficult trace and promises to provide a key to unlock the data in exchange for the payment. Attackers gain access to company networks by using social engineering techniques such as phishing email, stolen password, or exploiting an unpatched vulnerability in the software that is running on the company's network.
The Rising Threat of Ransomware
Cybercriminals have created one of the most destructive varieties of cybercrimes around the world through ransomware; while experts in the cybersecurity field project losses to global ransomware damage may reach $30 billion by 2025. There has also been a marked increase in SMEs being attacked by ransomware-based cybercriminals throughout India. NASSCOM has done research and found that many SMEs in India have experienced attempted ransomware attacks in the past few years alone. According to incident reports provided through CERT-In, there has been a noticeable increase in the number of cybercrime occurrences throughout different sectors of India’s economy since those reports began. These developments have shown an increase in the size and level of sophistication of ransomware related threats.
Why Indian SMEs Remain Vulnerable Despite Awareness
Despite increased awareness about cyber threats, there is a large number of Indian SMEs that continue to be vulnerable to ransomware. The main reason is financial limitations. Many small businesses typically have limited financial resources and those limited resources more often than not, go towards operations, including production, logistics, and marketing - cybersecurity costs are usually viewed as additional costs.
Another significant problem facing SMEs is a shortage of skilled cybersecurity professionals. Large enterprises typically have dedicated security teams responsible for protecting the enterprise, whereas SMEs will employ IT staff generally without any specific expertise in detecting/countering cyber threats. Human error are also significant contributors to these cyber incursion events. An employee can inadvertently click on an email link or download an infected attachment, or use a weak password - all of which could provide opportunities for cybercriminals to access the company's network. Phishing emails continue to be the most common approach for initiating ransomware.
Furthermore - many SMEs have implemented digital platforms, such as cloud-based applications and payment processing, without appropriately executing cybersecurity planning prior to implementation. Many of the issues that have arisen from such rapid digitisation are due to a lack of sufficient planned cybersecurity measures as part of the implementation process. This has also resulted in a situation where technological advancements such as Ransomware as a Service (RaaS) have created an even larger pool of potential perpetrators (cybercriminals) with little-to-no expertise being able to launch a widespread ransomware campaign using readily available/pre-manufactured tools.
Real-World Cyber Incidents Affecting Indian SMEs
As several examples recently demonstrate, Indian SMEs continue to experience significant cyber attack risks. Recently, a logistics firm located in Gurugram found itself locked out of nearly 4,000 shipments due to a ransomware attack, which cost them ₹12 lakhs to fix because they had poor backups and another incident in Gurugram which highlights how vulnerable many SMEs in the country continue to be to ransomware attacks. In the case of a garments company, a hacker compromised the company's server by placing ransomware on its system. The company was forced to shut down its computerised warehouse system as a result of the attack. Only after the company had lost access to its system, did it receive a ransom demand from the hacker, in the form of an email requesting payment of 15 bitcoins (approximately ₹25 lakh), in order for the hacker to restore the company's access to the system. The hacker also threatened to delete the company's financial and banking records if the ransom were not paid. Gurgaon Police's Cyber Cell received the report of the incident, and registered a first information report (FIR) against unknown hackers. The case represents an opportunity for SMEs to evaluate the risks associated with ransomware.
Bridging the Gap Between Awareness and Implementation
Although awareness campaigns can show organisations what types of cybersecurity risks they’re exposed to, these campaigns will not keep businesses from being victims of a ransomware attack by themselves.. The most critical step forward is the implementation of the principles of cybersecurity from an understanding viewpoint to that of an active action. Organisations need to go beyond being aware of the risks related to cyber and then put measures in place to mitigate those risks.
To improve cybersecurity, organisations may need to spend money on developing and maintaining systems; set up regular training for employees on handling cyber threats and implementing an incident response plan to address security incidents; back up data regularly; maintain the hardware and software used in the organisation's computer systems at least once a month (or more often if necessary); and monitor all aspects of its computer systems continuously for weaknesses or problems.
The Way Forward: Strengthening SME Cybersecurity
In order to truly address the ransomware threat, collaboration by businesses, government agencies and cyber security professionals is mandatory. One of the biggest roles in this collaboration is through governmental initiatives to enhance the overall level of awareness of digital security among SMEs (small to medium-sized enterprises). Improved SME understanding of cyber risks will be based on the availability of affordable security solutions that are specifically tailored for small businesses.
Industry partnerships as well as public-private partnerships also aid the sharing of threat intelligence to strengthen collaborative defense against all cybercriminal activity.
Conclusion
Despite Indian SMEs being aware of cyber threats, they have been unable to implement safeguards or Cyber Security plans due to limited financial resources, insufficient qualified personnel, human errors, and the rapid pace at which digital technology is being adopted without adequate Cyber Security measures. In order to respond effectively to the growing threat of Ransomware, Indian SMEs must evolve from being aware of cyber threats to proactively developing Cyber Security strategies that will allow them to prevent, prepare for, and recover from the increased cyber threat posed by the rapidly growing digitalisation of business within an increasingly globalised economy.
References
- https://www.ibm.com/think/topics/ransomware
- https://primeinfoserv.com/indias-sme-cybersecurity-crisis-real-incidents-real-lessons-2024-2025/
- https://timesofindia.indiatimes.com/city/gurgaon/ransomware-attack-on-apparel-firm-all-data-lost/articleshow/59496777.cms#
- https://ciso.economictimes.indiatimes.com/news/cybercrime-fraud/indian-businesses-face-nearly-700-ransomware-attacks-per-day-kaspersky/120471668
- https://smestreet.in/msmenews/indian-smes-remain-alarmingly-exposed-to-ransomware-threats-sophos-report-2025-9456628
- https://m.economictimes.com/news/how-to/how-can-indian-smes-combat-ransomware-attacks/articleshow/108047111.cms
Executive Summary:
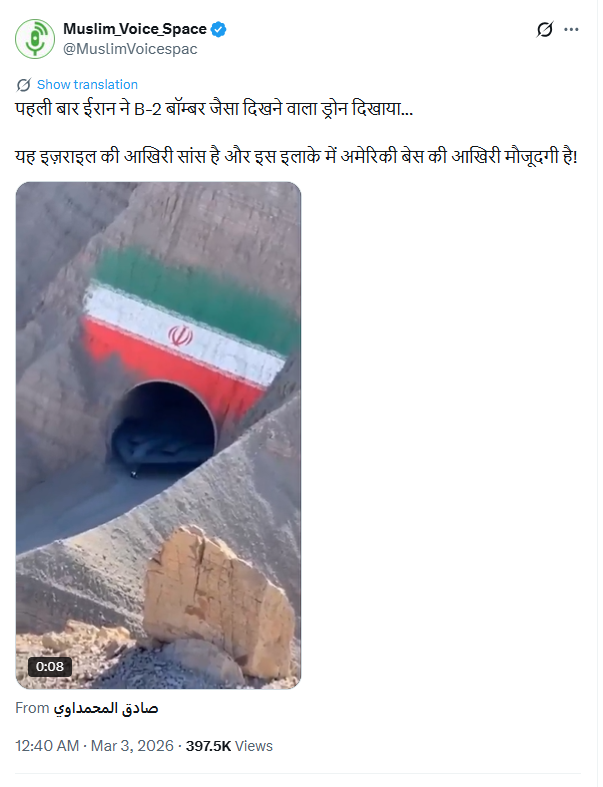
Amid the ongoing war involving the United States, Israel, and Iran, a video clip circulating on social media claims to show Iran unveiling a drone resembling the US B-2 stealth bomber. In the viral clip, an aircraft-like object can be seen emerging from a cave before taking off. Several users are sharing the video with the claim that Iran has deployed a B-2-style drone in the conflict.
However, research by the CyberPeace found that the viral video is not real and was generated using artificial intelligence. While the United States has reportedly used B-2 stealth bombers in strikes against Iran during the conflict, the viral clip does not show an actual Iranian drone.
Claim
X user “Muslim_Voice_Space” posted the video on March 3, 2026, claiming that Iran had rolled out a drone resembling the B-2 bomber for use in the war.
Fact Check
To verify the claim, we first closely examined the viral video. In the opening moments of the clip, the wing of the alleged drone appears to hit the side of the cave while exiting. Despite the apparent collision, the aircraft continues flying smoothly without any visible damage. This unusual detail raised doubts about the authenticity of the footage.
We then analyzed the video using the AI detection tool Hive Moderation, which flagged the clip as likely AI-generated.

Further analysis using the Sightengine AI detection tool also suggested that the video was artificially created. The tool estimated a 75% probability that the footage was generated using AI. It also indicated a 70% likelihood that the clip may have been created using Sora, an AI video-generation tool.

Conclusion
The viral video claiming to show an Iranian drone resembling the US B-2 stealth bomber emerging from a cave is not authentic. Analysis indicates that the clip was created using AI tools and is being misleadingly shared in the context of the ongoing conflict.
Executive Summary
Amid reports that the U.S. military rescued a missing crew member of a fighter jet in Iran, a video is going viral on social media. The clip is being shared with the claim that it shows a U.S. F-15 pilot captured in Iran after his aircraft was shot down. In the video, the detained officer can be heard identifying himself as “Colonel David William Everly.”
However, research by the CyberPeace has found this claim to be misleading. The viral video is real but not recent. It is from the 1991 Gulf War, when U.S. Air Force Colonel David William Everly was captured in Iraq during Operation Desert Storm.
Claim
A social media user “palestinereports786” shared the video with the caption suggesting that a U.S. F-15 fighter jet was shot down over Iran and that one crew member may have been captured.
Fact Check
In the viral video, the officer is heard responding to questions, stating his name as Colonel David William Everly and identifying himself as a U.S. national and an F-15 pilot from the 4th Tactical Fighter Wing. Using these details, we conducted a news search and found several old reports confirming that this incident dates back to the 1991 Gulf War.
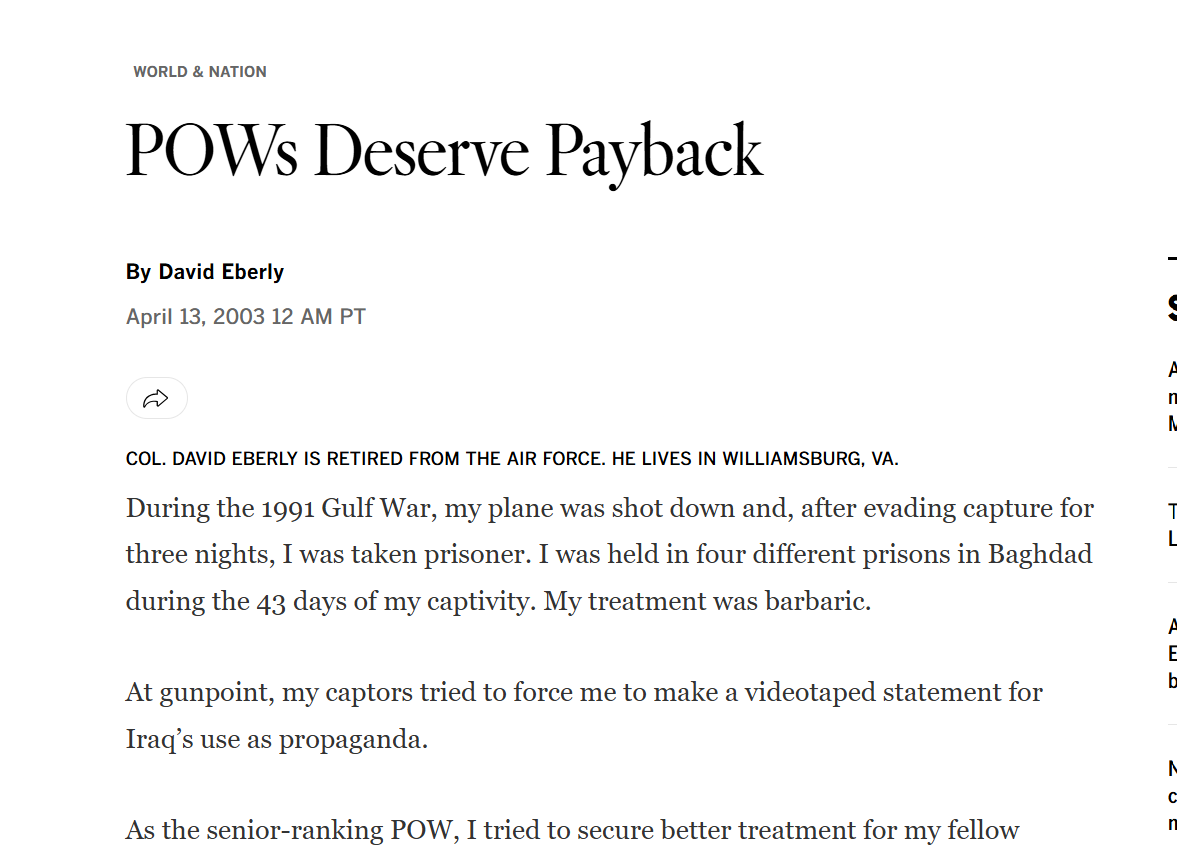
A report by the Los Angeles Times (April 13, 2003) recounts Everly’s experience, stating that his aircraft was shot down during the Gulf War. After evading capture for three nights, he was eventually taken prisoner and held for 43 days in multiple prisons in Baghdad, where he faced harsh treatment.
Additional references to the incident were also found on platforms such as pownetwork.org, nara.getarchive.net, and the National Air and Space Museum’s “Wall of Honor,” all documenting Everly’s captivity and eventual return to the United States. We also found an older interview of Everly, where he narrates the same incident.
According to data from acleddata.com, military tensions involving the United States, Israel, and Iran escalated after February 28, 2026, when operations against Iran reportedly began and are ongoing. However, reports indicate that the crew members of the recently downed F-15 aircraft were able to eject safely before the crash. Both crew members survived, and at least one has already been rescued by U.S. forces. There is no confirmed evidence that any pilot has been captured in Iran.
Conclusion
The viral video claiming to show a U.S. pilot captured in Iran is misleading. The footage is not related to any recent incident but originates from the 1991 Gulf War, when Colonel David William Everly was captured in Iraq. The old video has been shared with a false narrative to link it to the current geopolitical situation involving Iran. There is no verified evidence supporting claims that a U.S. pilot has been captured in Iran in the recent conflict.
