
Survivors Unveil the Dark Reality of Cyber Slavery
Introduction
Cyber slavery has emerged as a serious menace. Offenders target innocent individuals, luring them with false promises of employment, only to capture them and subject them to horrific torture and forced labour. According to reports, hundreds of Indians have been imprisoned in 'Cyber Slavery' in certain Southeast Asian countries. Indians who have travelled to South Asian nations such as Cambodia in the hopes of finding work and establishing themselves have fallen victim to the illusion of internet slavery. According to reports, 30,000 Indians who travelled to this region on tourist visas between 2022 and 2024 did not return. India Today’s coverage demonstrated how survivors of cyber slavery who have somehow escaped and returned to India have talked about the terrifying experiences they had while being coerced into engaging in cyber slavery.
Tricked by a Job Offer, Trapped in Cyber Slavery
India Today aired testimonials of cyber slavery victims who described how they were trapped. One individual shared that he had applied for a well-paying job as an electrician in Cambodia through an agent in Delhi. However, upon arriving in Cambodia, he was offered a job with a Chinese company where he was forced to participate in cyber scam operations and online fraudulent activities.
He revealed that a personal system and mobile phone were provided, and they were compelled to cheat Indian individuals using these devices and commit cyber fraud. They were forced to work 12-hour shifts. After working there for several months, he repeatedly requested his agent to help him escape. In response, the Chinese group violently loaded him into a truck, assaulted him, and left him for dead on the side of the road. Despite this, he managed to survive. He contacted locals and eventually got in touch with his brother in India, and somehow, he managed to return home.
This case highlights how cyber-criminal groups deceive innocent individuals with the false promise of employment and then coerce them into committing cyber fraud against their own country. According to the Ministry of Home Affairs' Indian Cyber Crime Coordination Center (I4C), there has been a significant rise in cybercrimes targeting Indians, with approximately 45% of these cases originating from Southeast Asia.
CyberPeace Recommendations
Cyber slavery has developed as a serious problem, beginning with digital deception and progressing to physical torture and violent actions to commit fraudulent online acts. It is a serious issue that also violates human rights. The government has already taken note of the situation, and the Indian Cyber Crime Coordination Centre (I4C) is taking proactive steps to address it. It is important for netizens to exercise due care and caution, as awareness is the first line of defence. By remaining vigilant, they can oppose and detect the digital deceit of phony job opportunities in foreign nations and the manipulative techniques of scammers. Netizens can protect themselves from significant threats that could harm their lives by staying watchful and double-checking information from reliable sources.
References
- CyberPeace Highlights Cyber Slavery: A Serious Concern https://www.cyberpeace.org/resources/blogs/cyber-slavery-a-serious-concern
- https://www.indiatoday.in/india/story/india-today-operation-cyber-slaves-stories-of-golden-triangle-network-of-fake-job-offers-2642498-2024-11-29
- https://www.indiatoday.in/india/video/cyber-slavery-survivors-narrate-harrowing-accounts-of-torture-2642540-2024-11-29?utm_source=washare

Related Blogs
Executive Summary
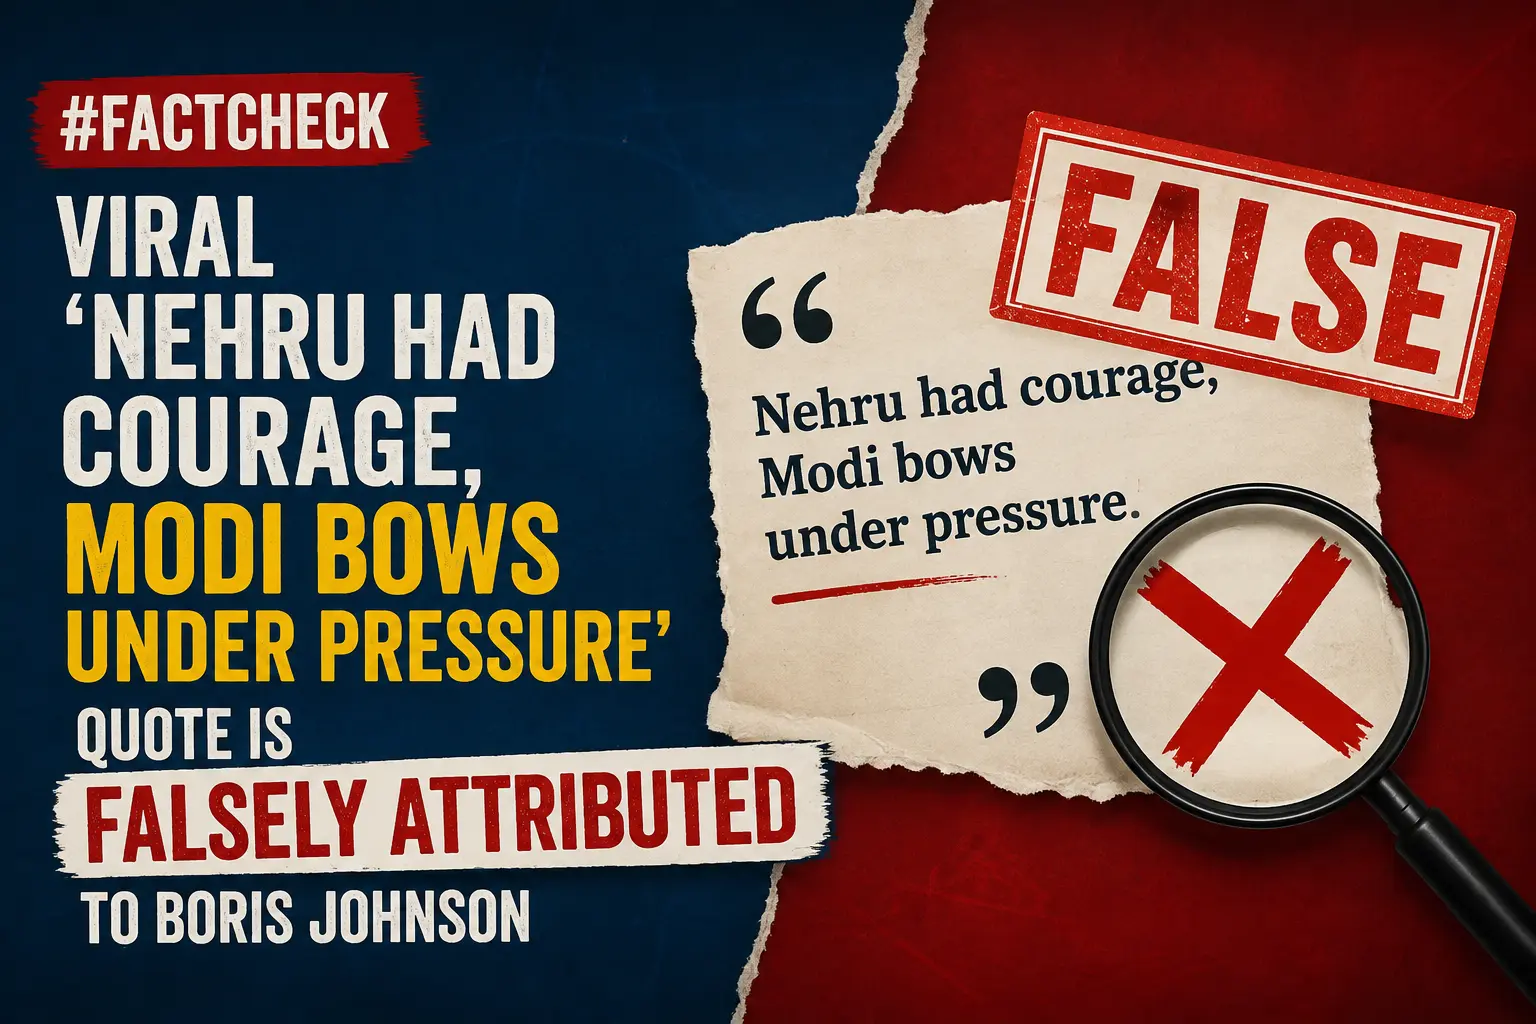
A purported statement attributed to former British Prime Minister Boris Johnson is going viral on social media. The post claims that Johnson said about Prime Minister Narendra Modi, “Modi bows under pressure.” It also attributes a comparison between Jawaharlal Nehru and Modi to Johnson, portraying Nehru as more courageous. A research done by the Research Wing of the CyberPeace found the viral claim to be false. During the research, the team examined Boris Johnson’s interview at the ET World Leaders Forum 2026, along with media reports related to the interview. The available transcript contains no remark by Johnson saying “Modi bows under pressure” or anything similar. On the contrary, he praised the changes and development taking place in India.
Claim:
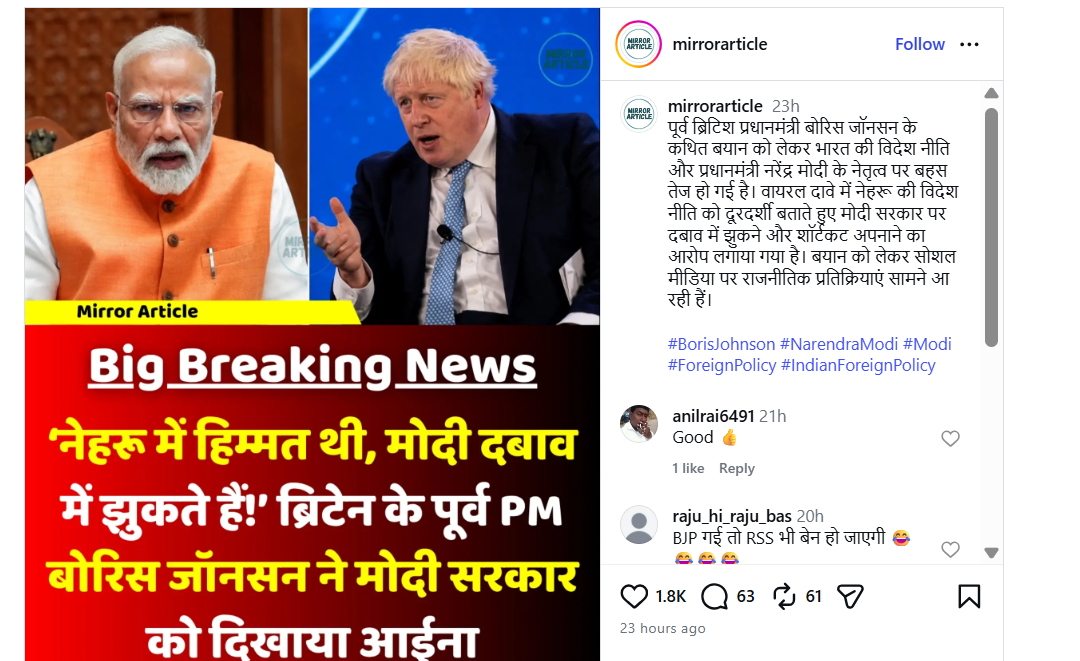
A user on Instagram shared the viral claim, writing: “The purported statement by former British Prime Minister Boris Johnson has intensified the debate over India’s foreign policy and Prime Minister Narendra Modi’s leadership. The viral claim describes Nehru’s foreign policy as visionary while accusing the Modi government of bowing under pressure and taking shortcuts. The statement has triggered political reactions on social media.” The link to the post, its archive link, and a screenshot are provided below.
https://www.instagram.com/p/Dcdo_TGy-W0/
Fact Check
To verify the authenticity of the viral claim, the Desk examined the available transcript and reports of Boris Johnson’s interview at the ET World Leaders Forum 2026. The Desk found that Johnson also praised India’s current situation. He said that India is going through a “very good period under very strong and stable leadership.” He described India’s progress as “a really wonderful story” and expressed optimism about the country’s future.
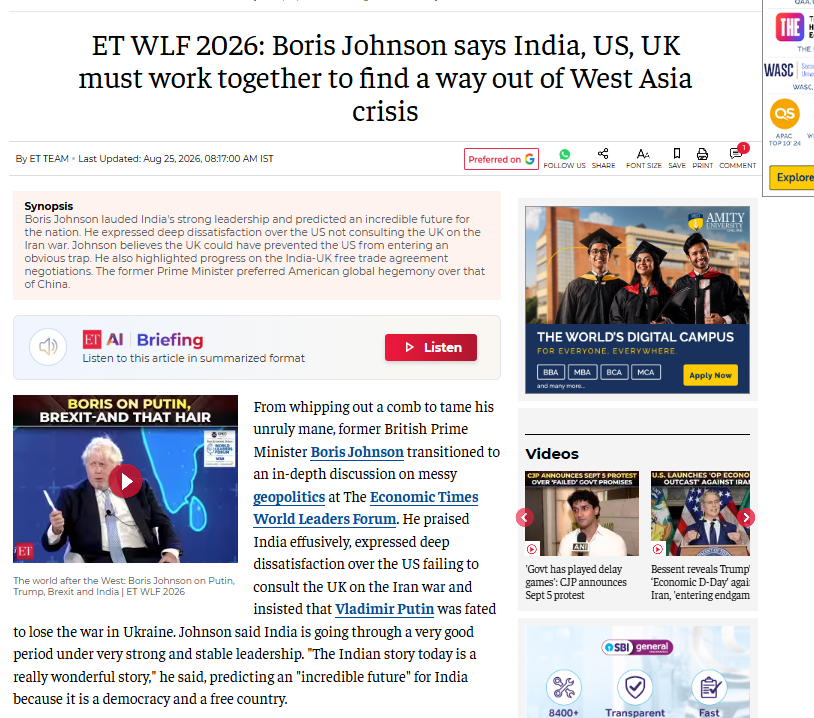
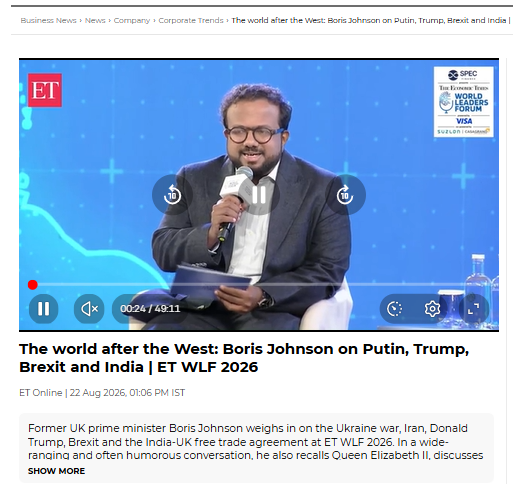
During the interview, Johnson discussed several international issues, including India-UK relations, US-UK ties, NATO defence spending, the Iran war and the Ukraine war. The available interview transcript contains no statement from him saying that “Modi bows under pressure” or that Nehru was more courageous than Modi. Johnson also referred to Jawaharlal Nehru in the context of India-Russia relations. He recalled that the late Queen Elizabeth II had once shared an anecdote about a conversation she had with Nehru in the 1950s, during which Nehru reportedly told her that India would always stand by Russia and that some things never change.
Conclusion
Boris Johnson did not make any statement at the ET World Leaders Forum 2026 suggesting that “Modi bows under pressure” or that “Nehru had courage.” On the contrary, he praised India’s progress and spoke positively about Prime Minister Narendra Modi’s leadership. Johnson did mention Nehru during the conversation, but his reference was in the context of India-Russia relations and an old conversation between Nehru and the late Queen Elizabeth II. He did not compare Nehru with Modi, nor did he criticise Modi. Therefore, the claim circulating on social media attributing the statement “Nehru had courage, Modi bows under pressure” to Boris Johnson is false.
A word rooted in medical terminology keeps getting mistaken for a word rooted in technology, and that confusion is not just semantic. On 6 August 2026, it sat at the heart of a case where police in Uttar Pradesh reportedly treated the absence of WhatsApp chats, call recordings, and social media material as grounds to disbelieve a sexual assault complaint altogether, before the Allahabad High Court intervened. For an organisation working at the intersection of digital literacy and public safety, this case is less a story about a legal term and more a case study in how assumptions about digital evidence, when left unchecked, can become a barrier to justice rather than a tool for it. "Digital" here refers to a finger, not a device, and the gap between what police expected and what the law actually required is exactly where this case becomes instructive. Digital rape has nothing to do with the internet. Digit simply means finger, and the word describes non-consensual penetration by a finger, thumb, toe, or similar body part or object. That basic clarification matters because the same investigating officers who were expected to know the law also appear to have leaned on a mistaken evidentiary standard, one where a complaint without a digital trail was treated as a complaint without merit. The judgment that followed says as much about how the criminal justice system treats sexual assault complaints, and how it treats digital evidence, as it does about legal terminology.
The case, in brief
The matter is Arpit Gupta v. State of U.P. and 2 others, 2026 LiveLaw (AB) 571, neutral citation 2026:AHC:168404-DB, decided by a Division Bench of Justice Chandra Dhari Singh and Justice Tarun Saxena. Arpit Gupta, the owner of a Noida based real estate firm, Parit Associates (OPC) Private Limited, approached the High Court under Article 226 of the Constitution seeking to quash an FIR registered against him at Wave City police station, Ghaziabad, alleging rape, sexual harassment, and criminal intimidation. The complainant, a former employee of Gupta's company, alleged sustained workplace sexual harassment culminating in an act legally categorised as digital penetration, along with subsequent threats and intimidation. She resigned in April 2026. What followed procedurally is where the case becomes significant: Gupta filed a separate extortion complaint against her, she was arrested and later released on bail, and only after that sequence did she attempt to formally report the sexual assault, a report the police initially declined to register.
What followed complicates the picture considerably, and is central to why the case reached the High Court at all. On 14 April 2026, Gupta filed his own FIR against the complainant alleging extortion, claiming she had demanded 10 crore rupees from him. She was arrested in connection with that case and secured bail on 21 May 2026. After her release, she attempted to register her own complaint of sexual assault, but police at Wave City station declined to register an FIR. A written complaint dated 7 July 2026 addressed directly to the Commissioner of Police, Ghaziabad, also produced no result. The police investigating officer's report, dated 16 July 2026, went further still, terming her allegations false and characterising the sexual assault complaint as a retaliatory counter-blast to Gupta's extortion case, citing in particular the absence of supporting electronic material such as WhatsApp chats, call recordings, or social media evidence. Only after she approached a Magistrate under Section 173(4) of the Bharatiya Nagarik Suraksha Sanhita, 2023, did the FIR finally get registered, by Magisterial order dated 20 July 2026.
The legal terminology: what "digital rape" actually means under BNS
Section 63 of the Bharatiya Nyaya Sanhita, 2023, which replaced Section 375 of the erstwhile Indian Penal Code, defines rape. Clause (b) of Section 63 extends that definition to cover non-penile penetrative acts, specifically insertion, to any extent, of any object or body part other than the penis into specified parts of a woman's body, done without her consent or against her will, subject to the circumstances of absent consent set out in the section. Digital penetration, meaning penetration by finger or thumb, falls squarely within this clause. There is no standalone offence in the BNS titled "digital rape"; the term is a widely used medico-legal shorthand, not a separate statutory category, and the offence itself is prosecuted and punished as rape under Section 64 BNS, which prescribes the punishment provisions. In this particular case, the FIR reportedly also invoked Sections 74, 75(2), and 76 BNS, provisions dealing with assault or use of criminal force with intent to outrage modesty, sexual harassment by a person in a position of authority, and related offences, alongside Section 351(3) BNS concerning criminal intimidation.
CyberPeace View
This is where the case circles back to the concern raised at the outset. The most instructive part of this judgment for the wider public may not be the definition of digital rape at all, but the police's original insistence on WhatsApp chats and call recordings before treating the complaint as credible. That reflex, a growing habit of associating the credibility of any complaint with the existence of a corresponding digital trail, reflects a wider and increasingly common misunderstanding about how evidence actually works in criminal law. Not every offence leaves an electronic footprint, and sexual assault, by its nature, frequently occurs without any accompanying digital record at all. Treating the absence of a chat log or a recording as evidence of falsehood inverts the legal presumption entirely, and risks turning digital literacy gaps within law enforcement into a structural barrier for genuine complainants who have no messages to produce because none were ever exchanged. As India's criminal justice system increasingly interacts with digital evidence, this case is a useful reminder that digital forensics should supplement an investigation, never gatekeep its starting point.
There is a genuinely technology rooted counterpart to this terminology confusion worth flagging, and it sits at the opposite end of the spectrum from where this case began. While "digital rape" has nothing to do with computers, "virtual rape" very much does, and it is an emerging harm India's legal framework is still catching up to. In January 2024, British police opened what was reported as the first investigation of its kind after a minor's avatar was allegedly gang assaulted by other avatars on Meta's metaverse platform, and similar incidents, avatars groped or sexually harassed within minutes of entering platforms like Horizon Worlds, have been documented repeatedly since, including a widely reported case involving psychotherapist Nina Jane Patel as far back as 2021. These incidents involve no physical contact whatsoever, yet researchers and legal scholars studying virtual reality note that immersive VR environments are specifically engineered to create a sense of embodiment, where the brain processes an avatar's violation as something closer to a real bodily experience than a typical online interaction, producing genuine trauma responses in victims. India's legal position here remains only partially settled. The POCSO Act's coverage of non-contact sexual abuse of minors likely extends to avatar based assaults on children, but adult victims of virtual sexual violence in India currently have no clearly dedicated statutory provision, leaving prosecutors to stretch existing harassment and outraging modesty provisions, originally drafted for a physical world, onto a form of harm the legislature has not yet explicitly addressed. As metaverse and VR platforms grow their user base in India, that gap is one worth closing before, rather than after, a case forces the question, much as this one forced the question of how police ought to treat digital evidence.
Conclusion
Two lessons run through this judgment. First, that the law's protection of bodily autonomy extends well beyond narrow, traditional definitions of penetration, a principle Section 63(b) BNS makes explicit. Second, that a complainant reporting a cognizable offence cannot be made to investigate her own case before the police will even open a file. FIR registration is not conviction, and conviction requires investigation, evidence, and trial to follow. What this case asks of the system is simpler than any of that: register the complaint, then do the work of finding out what happened.
References
- https://www.barandbench.com/news/digital-rape-allahabad-hc-orders-inquiry-against-senior-ghaziabad-police-officers-for-not-filing-fir
- https://www.livelaw.in/high-court/allahabad-high-court/allahabad-hc-police-cant-refuse-fir-sexual-complaint-non-production-evidence-545374
A dark screen has always meant one thing to most of us: the television is off, and whatever we say in the room is ours again. A new investigation into LG's smart TVs suggests that assumption may no longer hold, and the findings are detailed enough, and corroborated widely enough, that they deserve a careful look rather than a shrug.
What the investigation actually found
On 7 September 2026, hardware review outlet Gamers Nexus published a 135 minute video investigation, the product of more than 500 hours of testing and roughly 70,000 dollars in resources, conducted alongside hardware channel Level1Techs and independent security researchers. The team tested retail LG OLED televisions, including the current flagship G5 model, using Wireshark, a widely used network packet analysis tool that lets researchers see exactly what data a device is sending and receiving.
What they reported was substantial. Using the UPnP protocol, a standard that lets devices on a network automatically discover one another, the televisions were found actively sweeping the entire home network, mapping phones, smartwatches, laptops, and other connected hardware that had nothing to do with the television itself, including devices belonging to people who were not part of the testing. The sets also collected information about neighbouring Wi-Fi networks, their names and signal strength, data that combined with other signals can help build a fairly precise picture of where a television physically sits and who else shares its environment.
The audio findings drew the most attention, and for good reason. Researchers reported pulling clear microphone audio from a television with a dark screen, in standby mode, and repeated the test after physically disconnecting the set's Ethernet cable. According to the investigation, speech spoken near the television during that disconnected period was stored locally and then uploaded automatically the moment connectivity was restored, with researchers reporting audio pickup from roughly 60 feet away through a wall. Muting the television's primary microphone through its settings menu reportedly did not fully solve the problem either, since the team said they were able to pull a usable recording from a second, less obvious microphone that the mute control did not appear to govern. Voice input, according to the reporting, was also converted into plain text and saved in on device logs, with the microphone said to remain active for ten to fifteen seconds after speech ended.
Separately, the investigation also examined Automatic Content Recognition, commonly called ACR, a longstanding smart TV feature that samples audio or video snippets and matches them against a reference database to identify what is being watched. Gamers Nexus reported that LG's implementation continued functioning even when the television was used purely as an HDMI monitor for a laptop or game console, meaning switching inputs away from the TV's own smart platform did not switch ACR off. The team also said security researchers identified unpatched remote access vulnerabilities in LG's webOS software, and separately found code associated with residential proxy functionality, which, if accurate, could theoretically allow a device's internet connection to be quietly used to route other people's traffic.
What LG has said
LG's public position predates this specific investigation and has not changed since. Responding earlier this year to a Texas lawsuit targeting several television manufacturers over ACR practices, the company stated that LG Electronics reaffirms that LG TVs do not collect, record, or store ambient conversations, describing voice recognition as an optional, user initiated feature that only processes voice data when a user activates it for a specific request. LG has reportedly not issued a specific response addressing the Gamers Nexus findings directly, though multiple outlets note the company was approached for comment. It is worth noting LG had already settled with Texas regulators earlier this year, agreeing to stop collecting viewing data without informed consent, a separate matter concerning ACR rather than the standby microphone claims raised in this newer investigation.
The commercial context that makes this matter
None of this data collection happens in a vacuum. LG Ad Solutions, the company's advertising division, openly markets first party ACR data and cross device advertising reach to advertisers, citing access to 49 million LG smart TVs in the United States and 363 million connected devices reachable through them. That figure confirms the scale of commercial value sitting inside the largest screen in most homes, though it is worth being precise here: that statistic describes LG's advertising reach broadly, and does not by itself prove that every one of those secondary devices was specifically discovered through a television's own local network scanning, a distinction some careful reporting on this story has been right to preserve rather than collapse into a single alarming number. Multiple LG Ad Solutions executives, according to footage referenced in coverage of the investigation, have spoken candidly about tying a household's viewing habits to the other devices under the same roof, describing the underlying business model in terms that leave little ambiguity about how central this data pipeline is to the company's advertising strategy. This is not a hidden side project; it is a openly promoted revenue stream built on exactly the kind of information the Gamers Nexus investigation says a television collects well beyond what a customer would reasonably expect from a screen they believe is switched off.
Why this extends well past the living room
Smart televisions and large connected displays are not confined to homes. They sit in hospital waiting rooms and patient areas, hotel rooms, corporate boardrooms, and office common areas, environments where the conversations happening nearby, and the information displayed on screen, frequently carry a genuine expectation of confidentiality. A device capable of logging speech and identifying on screen content in a home is the same device, running the same software, in every one of those settings.
What LG owes an honest answer to
Several questions remain squarely LG's to answer, and general reassurance language will not resolve them. Which specific models and firmware versions were affected, and under what settings. What precisely activates the microphone, and for how long it stays active. What is stored locally on the device, what gets transmitted externally, and under what circumstances. Whether any of this collection continues while the display is in standby rather than actively in use. And critically, whether an ordinary user, without specialised network analysis tools, has any reliable way to independently verify that microphone access, ACR, and cross device tracking are genuinely disabled once turned off in a settings menu.
CyberPeace Advisory
What owners can do while those answers are pending
Until LG addresses the specific findings in detail, several practical steps meaningfully reduce exposure.
- Disable voice recognition and ACR through the television's settings menu, even knowing the investigation raises questions about whether every microphone path is fully governed by that toggle.
- Review all privacy and data sharing permissions the television requests, and install the latest available security updates, since some of the vulnerabilities reported concern webOS software flaws LG could patch.
- Place the television on a separate guest or IoT network segment, isolated from computers, phones, and other sensitive devices, so that even if the TV's own network behaviour cannot be fully controlled, it cannot see or map everything else in the home.
- For genuinely sensitive environments, hospitals, boardrooms, and similar settings, the more reliable option is disconnecting the television from the network entirely and routing all content through a separately secured streaming device instead.
A dark screen has never meant a device is truly powered down in any technical sense, but this investigation is a useful, concrete reminder that the gap between how a device appears and what it is actually doing can be considerably wider than most people assume. Confirming exactly how wide that gap is, model by model and setting by setting, is now squarely LG's responsibility to demonstrate, not simply assert.
References
- Notebookcheck, "LG smart TVs caught logging audio with screen off and snooping on local devices." https://www.notebookcheck.net/LG-smart-TVs-caught-logging-audio-with-screen-off-and-snooping-on-local-devices.1391214.0.html
- Cybernews, "LG smart TVs may log voice commands and scan homes." https://cybernews.com/privacy/up-to-200m-lg-smart-tvs-could-be-secretly-listening-in-on-conversations/
- All About Cookies, "LG Smart TVs Caught Listening With the Screen Off and Snooping Around Your Wi-Fi." https://allaboutcookies.org/lg-smart-tvs-snooping
- Decrypt, "Your LG TV Might Still Be Listening to You, Even When It Looks Like It's Off." https://decrypt.co/377637/lg-tv-might-be-listening-even-when-off
- Yahoo Tech, "Your LG TV Might Still Be Listening to You, Even When It Looks Like It's Off." https://tech.yahoo.com/cybersecurity/articles/lg-tv-might-still-listening-214604684.html
- TechRadar, "LG's gaming monitors and TVs are facing a user revolt." https://www.techradar.com/televisions/lgs-gaming-monitors-and-tvs-are-facing-a-user-revolt
- Quest Review Center, "LG faces renewed privacy backlash over smart TV data collection and monitor practices." https://questreviewcenter.com/smart-home-tech/lg-faces-renewed-privacy-backlash-over-smart-tv-data-collection-and-monitor-practices/
- The CyberSec Guru, "LG Smart TV Spying Exposed: 216M TVs, Full Breakdown." https://thecybersecguru.com/news/lg-smart-tv-spying-investigation/
- Ynetnews, "Your LG TV may be listening: Researchers uncover audio recording and network scanning." https://www.ynetnews.com/tech-and-digital/article/bydiqhhume
- UNILAD Tech, "Major TV brand accused of snooping on customers while devices are supposed to be off." https://www.uniladtech.com/gadgets/lg-tv-accused-snooping-customers-devices-off-021514-20260907
