
India’s New Broadcasting Bill 2023 and the Future of Media Freedom
Introduction
The Indian Ministry of Information and Broadcasting has proposed a new legislation. On the 10th of November, 2023, a draft bill emerged, a parchment of governance seeking to sculpt the contours of the nation's broadcasting landscape. The Broadcasting Services (Regulation) Bill, 2023, is not merely a legislative doctrine; it is a harbinger of change, an attestation to the storm of technology and the diversification of media in the age of the internet.
The bill, slated to replace the Cable Television Networks (Regulation) Act of 1995, acknowledges the paradigm shifts that have occurred in the media ecosystem. The emergence of Internet Protocol Television (IPTV), over-the-top (OTT) platforms and other digital broadcasting services has rendered the previous legislation a relic, ill-suited to the dynamism of the current milieu. The draft bill, therefore, stands at the precipice of the future, inviting stakeholders and the vox populi to weigh in on its provisions, to shape the edifice of regulation that will govern the airwaves and the digital streams.
Defining the certain Clauses of the bill
Clause 1 (dd) - The Programme
In the intricate tapestry of the bill's clauses, certain threads stand out, demanding scrutiny and careful consideration. Clause 1(dd), for instance, grapples with the definition of 'Programme,' a term that, in its current breadth, could ensnare the vast expanse of audio, visual, and written content transmitted through broadcasting networks. The implications are profound: content disseminated via YouTube or any website could fall within the ambit of this regulation, a prospect that raises questions about the scope of governmental oversight in the digital realm.
Clause 2(v) - The news and current affairs
Clause 2(v) delves into the murky waters of 'news and current affairs programmes,' a definition that, as it stands, is a maelstrom of ambiguity. The phrases 'newly-received or noteworthy audio, visual or audio-visual programmes' and 'about recent events primarily of socio-political, economic or cultural nature' are a siren's call, luring the unwary into a vortex of subjective interpretation. The threat of potential abuse looms larger, threatening the right to freedom of expression enshrined in Article 19 of the Indian Constitution. It is a clarion call for stakeholders to forge a definition that is objective and clear, one that is in accordance with the Supreme Court's decision in Shreya Singhal v. Union of India, which upheld the sanctity of digital expression while advocating for responsible content creation.
Clause 2(y) Over the Top Broadcasting Services
Clause 2(y) casts its gaze upon OTT broadcasting services, entities that operate in a realm distinct from traditional broadcasting. The one-to-many paradigm of broadcast media justifies a degree of governmental control, but OTT streaming is a more intimate affair, a one-on-one engagement with content on personal devices. The draft bill's attempt to umbrella OTT services under the broadcasting moniker is a conflation that could stifle the diversity and personalised nature of these platforms. It is a conundrum that other nations, such as Australia and Singapore, have approached with nuanced regulatory frameworks that recognise the unique characteristics of OTT services.
Clause 4(4) - Requirements for Broadcasters and Network Operators
The bill's journey through the labyrinth of regulation is fraught with other challenges. The definition of 'Person' in Clause 2(z), the registration exemptions in Clause 4(4), the prohibition on state governments and political parties from engaging in broadcasting in Clause 6, and the powers of inspection and seizure in Clauses 30(2) and 31, all present a complex puzzle. Each clause, each sub-section, is a cog in the machinery of governance that must be calibrated with precision to balance the imperatives of regulation with the freedoms of expression and innovation.
Clause 27 - Advisory Council
The Broadcast Advisory Council, envisioned in Clause 27, is yet another crucible where the principles of impartiality and independence must be tempered. The composition of this council, the public consultations that inform its establishment, and the alignment with constitutional principles are all vital to its legitimacy and efficacy.
A Way Forward
It is up to us, as participants in the democratic process and citizens, to interact with the bill's provisions as it makes its way through the halls of public discourse and legislative examination. To guarantee that the ultimate version of the Broadcasting Services (Regulation) Bill, 2023, is a symbol of advancement and a charter that upholds our most valued liberties while welcoming the opportunities presented by the digital era, we must employ the instruments of study and discussion.
The draft bill is more than just a document in this turbulent time of transition; it is a story of India's dreams, a testament to its dedication to democracy, and a roadmap for its digital future. Therefore, let us take this duty with the seriousness it merits, as the choices we make today will have a lasting impact on the history of our country and the media environment for future generations.
References
- https://scroll.in/article/1059881/why-indias-new-draft-broadcast-bill-has-raised-fears-of-censorship-and-press-suppression#:~:text=The%20bill%20extends%20the%20regulatory,regulation%20through%20content%20evaluation%20committees.
- https://pib.gov.in/PressReleasePage.aspx?PRID=1976200
- https://www.hindustantimes.com/india-news/new-broadcast-bill-may-also-cover-those-who-put-up-news-content-online-101701023054502.html

Related Blogs
Executive Summary:
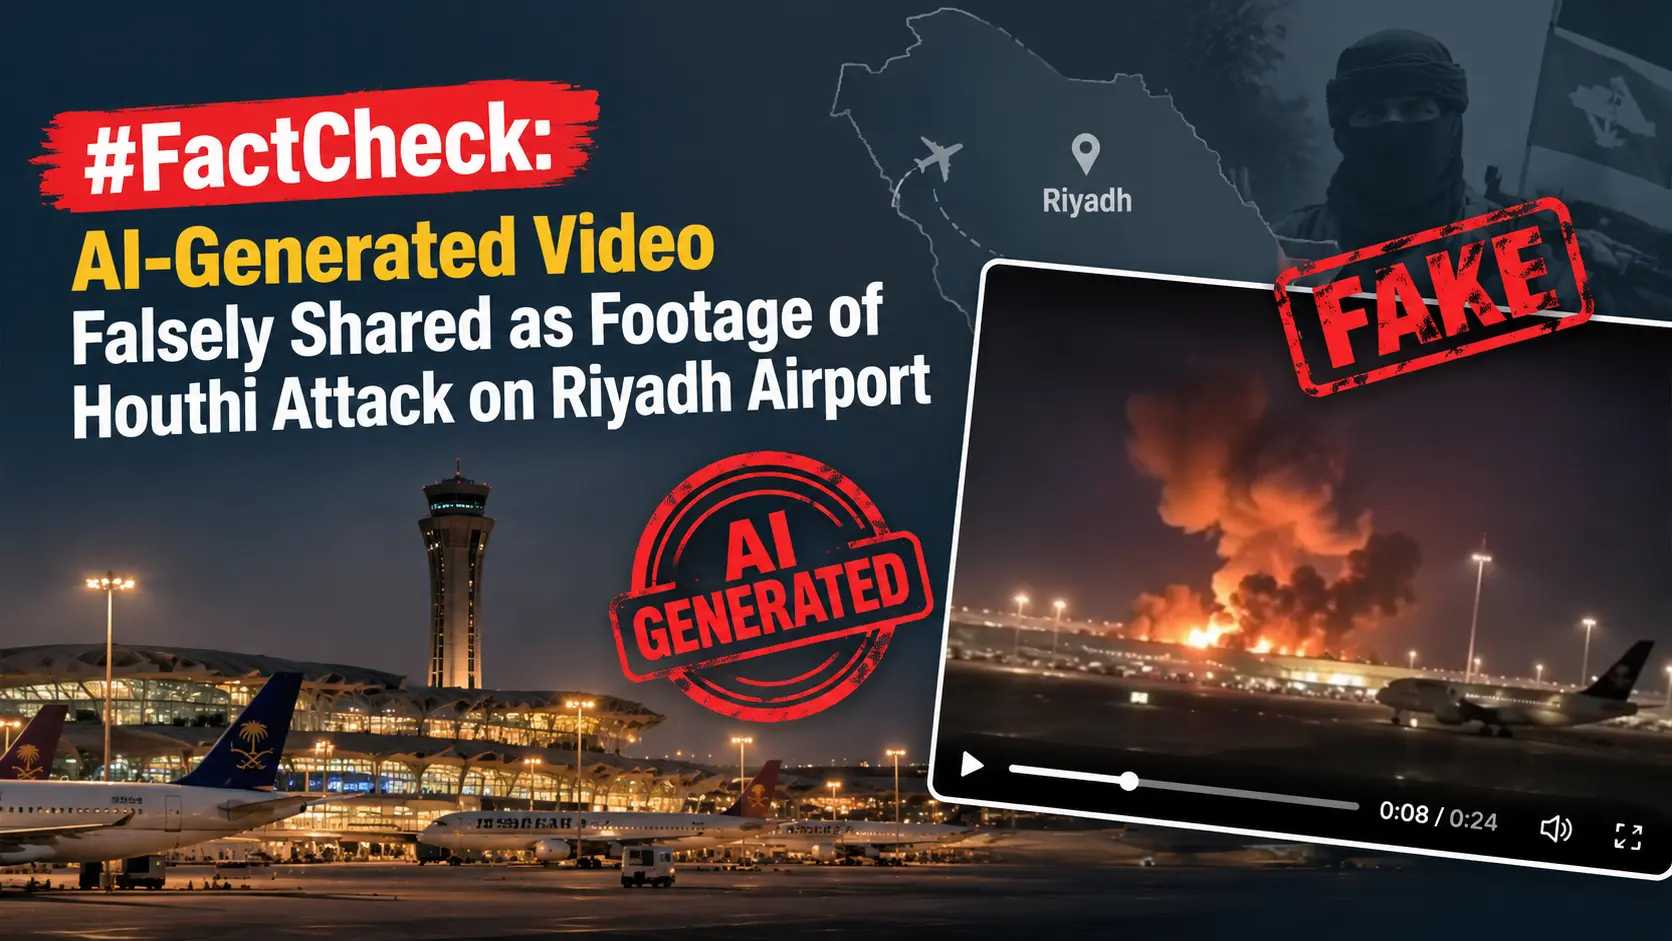
A missile attack was reportedly carried out by Yemen-based Houthi militants at King Khalid International Airport in Riyadh, the capital of Saudi Arabia, on October 8, damaging an aircraft at the airport. Following the attack, a video has gone viral on social media. The video is being shared with the claim that it shows footage from the time of the Houthi attack. CyberPeace Research found that the video is not authentic. It was created using AI with the help of an image from 2016.
Claim:
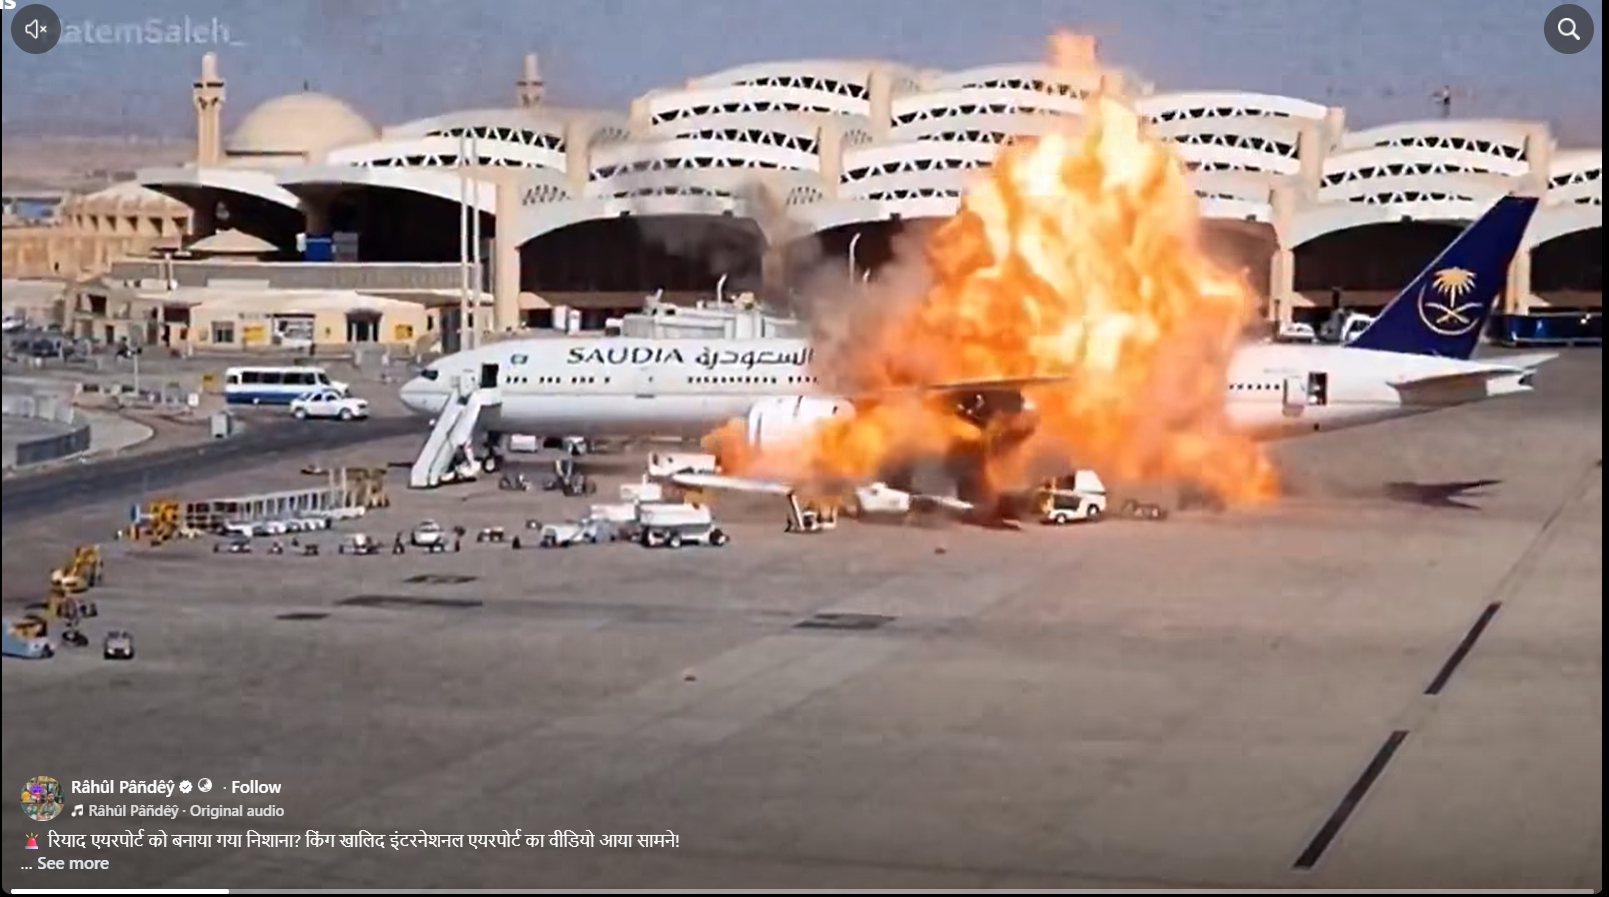
A Facebook user shared the video with the caption: “New video footage has emerged showing the moments when King Khalid International Airport in Riyadh, the capital of Saudi Arabia, was targeted.”
https://www.facebook.com/reel/1482618257069151
Fact Check:
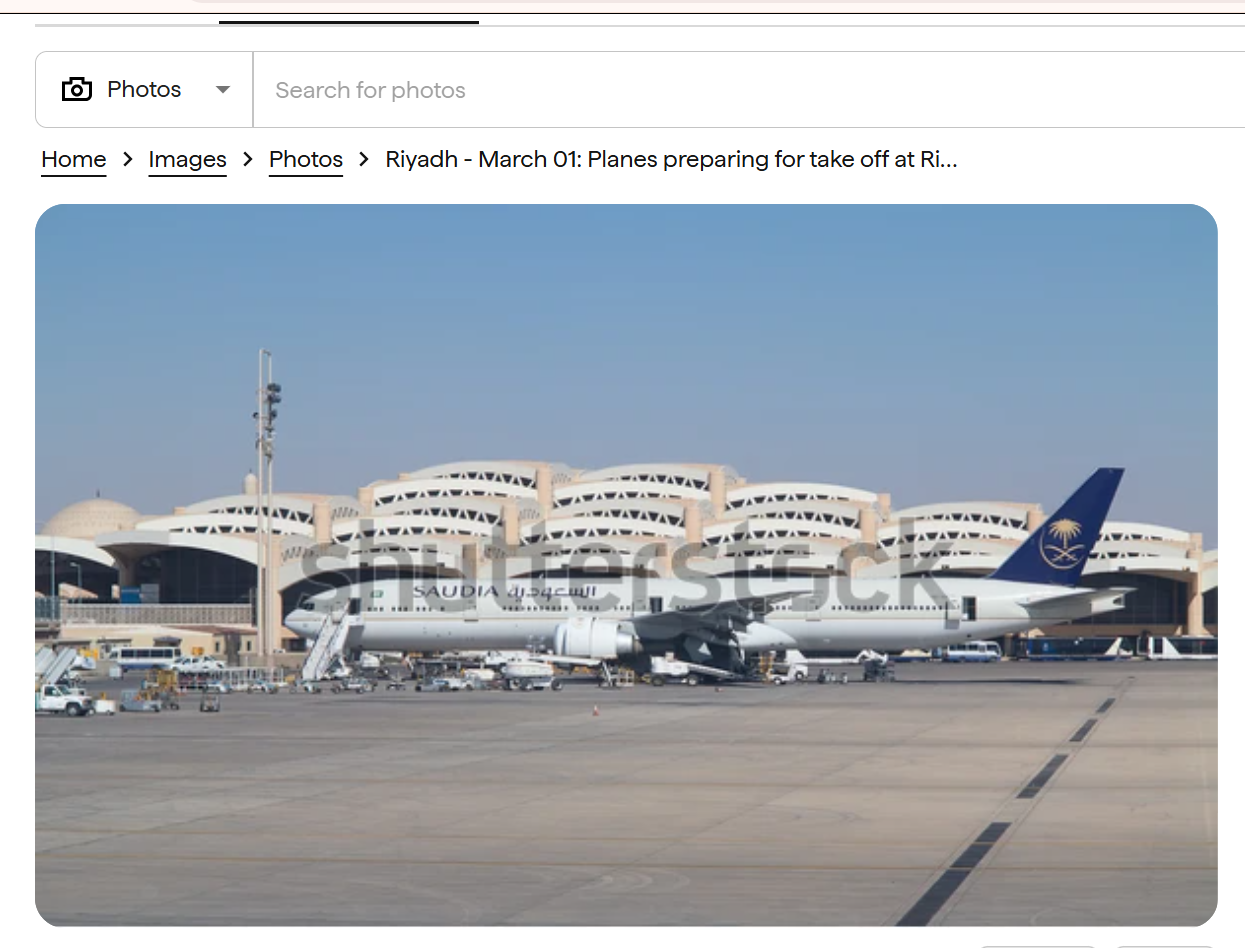
To verify the viral claim, we conducted a Google keyword search using relevant terms. However, we did not find any credible media reports corroborating the claim.A reverse image search led us to a similar image on the stock photo website Shutterstock. According to the listing, the image was taken on March 1, 2016, at King Khalid International Airport in Riyadh, showing an aircraft preparing for takeoff. A close examination of the viral video makes it clear that the same image was used to create the viral video.
Upon closely examining the viral video, we suspected that it could be AI-generated. We then scanned the viral video using the AI detection tool Undetectable AI. According to the results, the video was found to be 85% AI-generated.
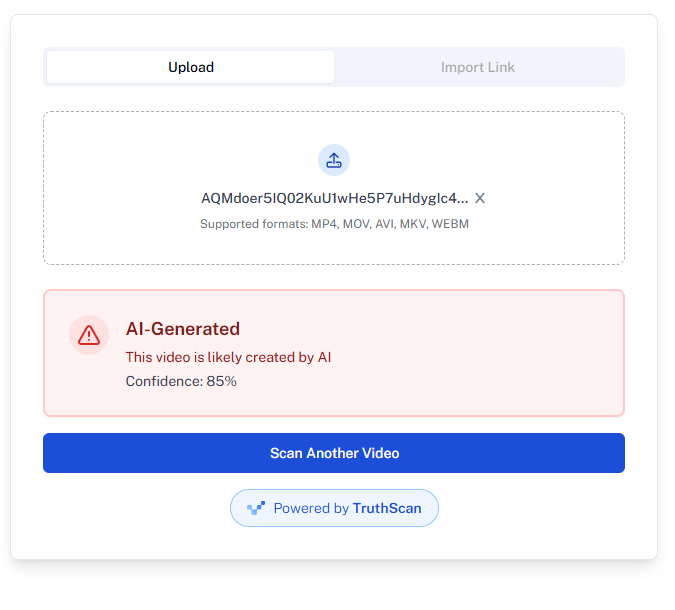
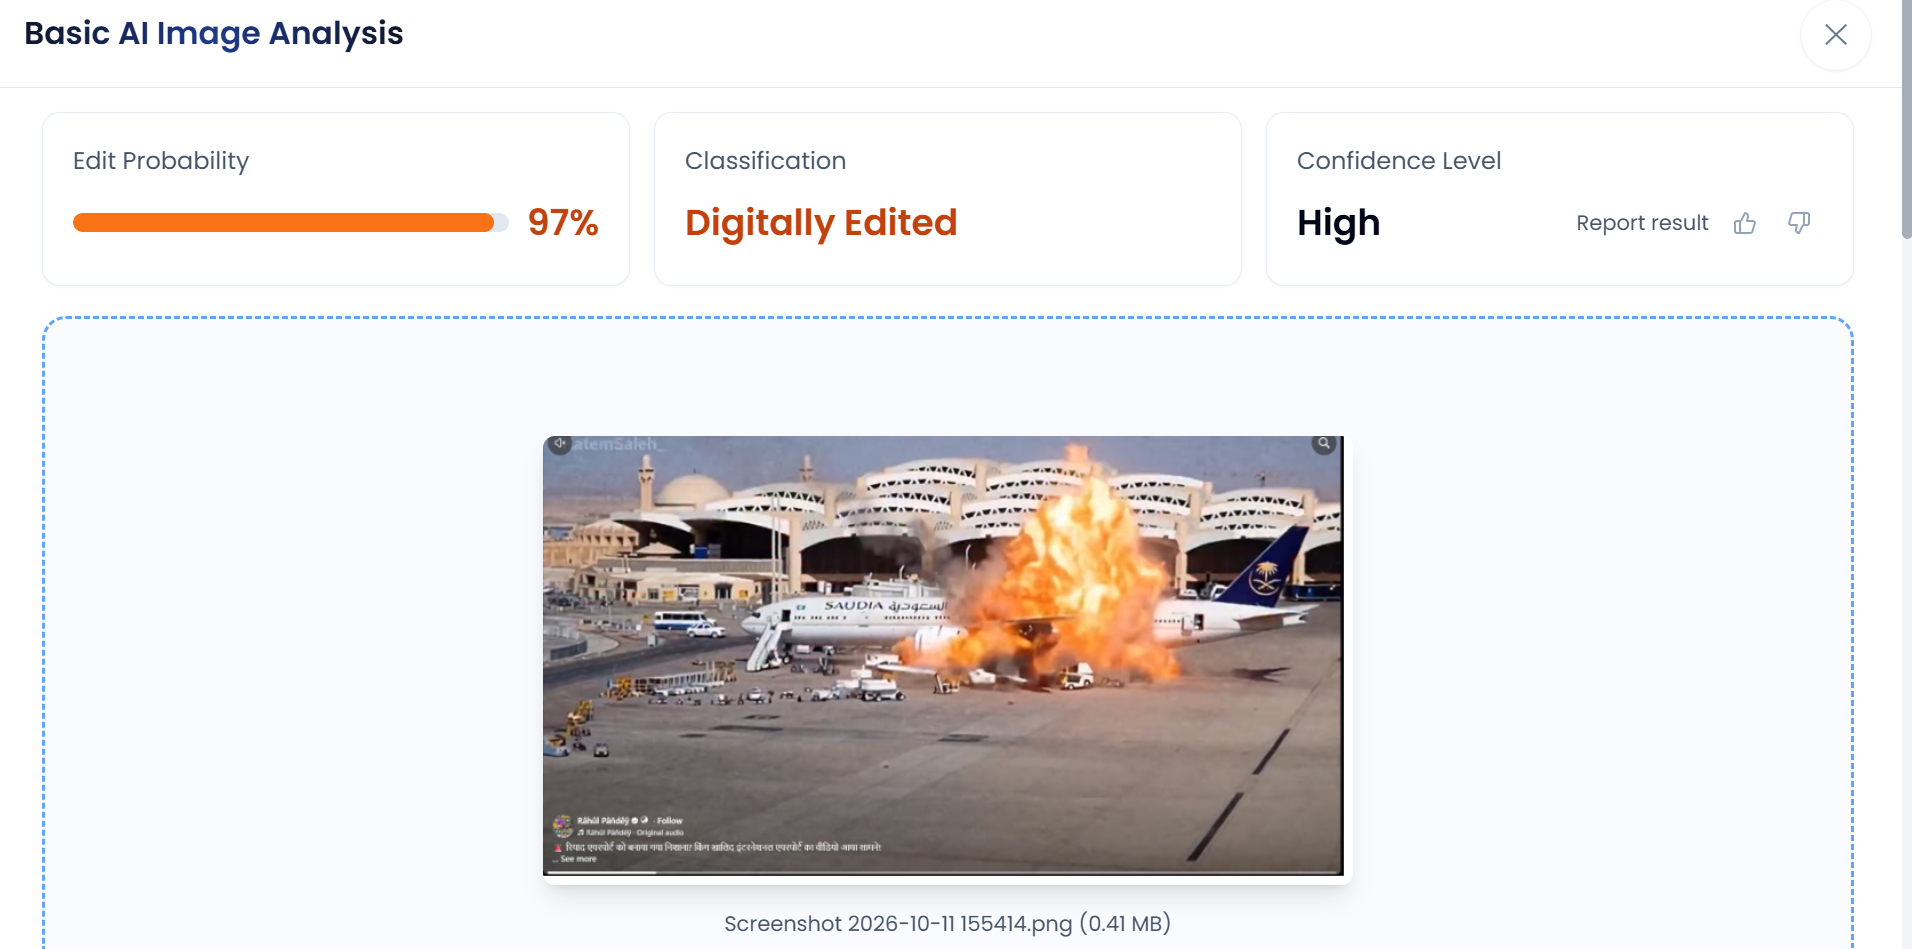
As part of our further research, we scanned the viral image using TruthScan. According to the results, the image was found to be 97% AI-generated.
Conclusion:
CyberPeace Research found the viral claim to be misleading. The video being shared as footage of the alleged Houthi missile attack on King Khalid International Airport in Riyadh is not authentic. Our research revealed that the video was AI-generated using a photograph taken at the airport on March 1, 2016. AI detection tools further indicated that the video and the image showed strong signs of being AI-generated.
Introduction
For years, Indian companies could get away with vague privacy promises. That window closed on 13 November 2025, when the government notified the Digital Personal Data Protection Rules, giving teeth to the broad principles Parliament had passed back in 2023 under the DPDP Act. The Rules turned soft commitments into specific, auditable duties, and a lot of organisations are only now realising how much that actually changes.
Start with Section 8(4). It requires every Data Fiduciary to put "appropriate technical and organisational measures" in place. Most readers skim past "organisational" and focus on the technical half, but that's a mistake, because the word is doing real work. It's asking for defined roles, written policies, staff training, and someone actually watching whether any of it holds up over time, not just firewalls and encryption keys. Section 8(5) goes further, demanding reasonable security safeguards against breaches, and Rule 6 spells out exactly what that phrase means in practice: encrypt data at rest and in transit, restrict access on a need to know basis, require multi factor authentication, log and monitor activity, run regular vulnerability checks, bind your data processors contractually to the same standard, and keep relevant logs for at least a year.
Then there's Rule 7, and this is where the clock starts running. Once a Data Fiduciary becomes aware of a breach, the Data Protection Board must be told without delay, and a full report has to follow within 72 hours covering what happened, when, why, what's being done about it, and confirmation that affected individuals were notified. Unlike GDPR, there's no minimum severity threshold here. A breach affecting ten people triggers the same obligation as one affecting ten million. And CERT-In's existing six hour reporting window under its 2022 Directions still applies separately, which means a serious incident can trigger two overlapping regulatory clocks running side by side.
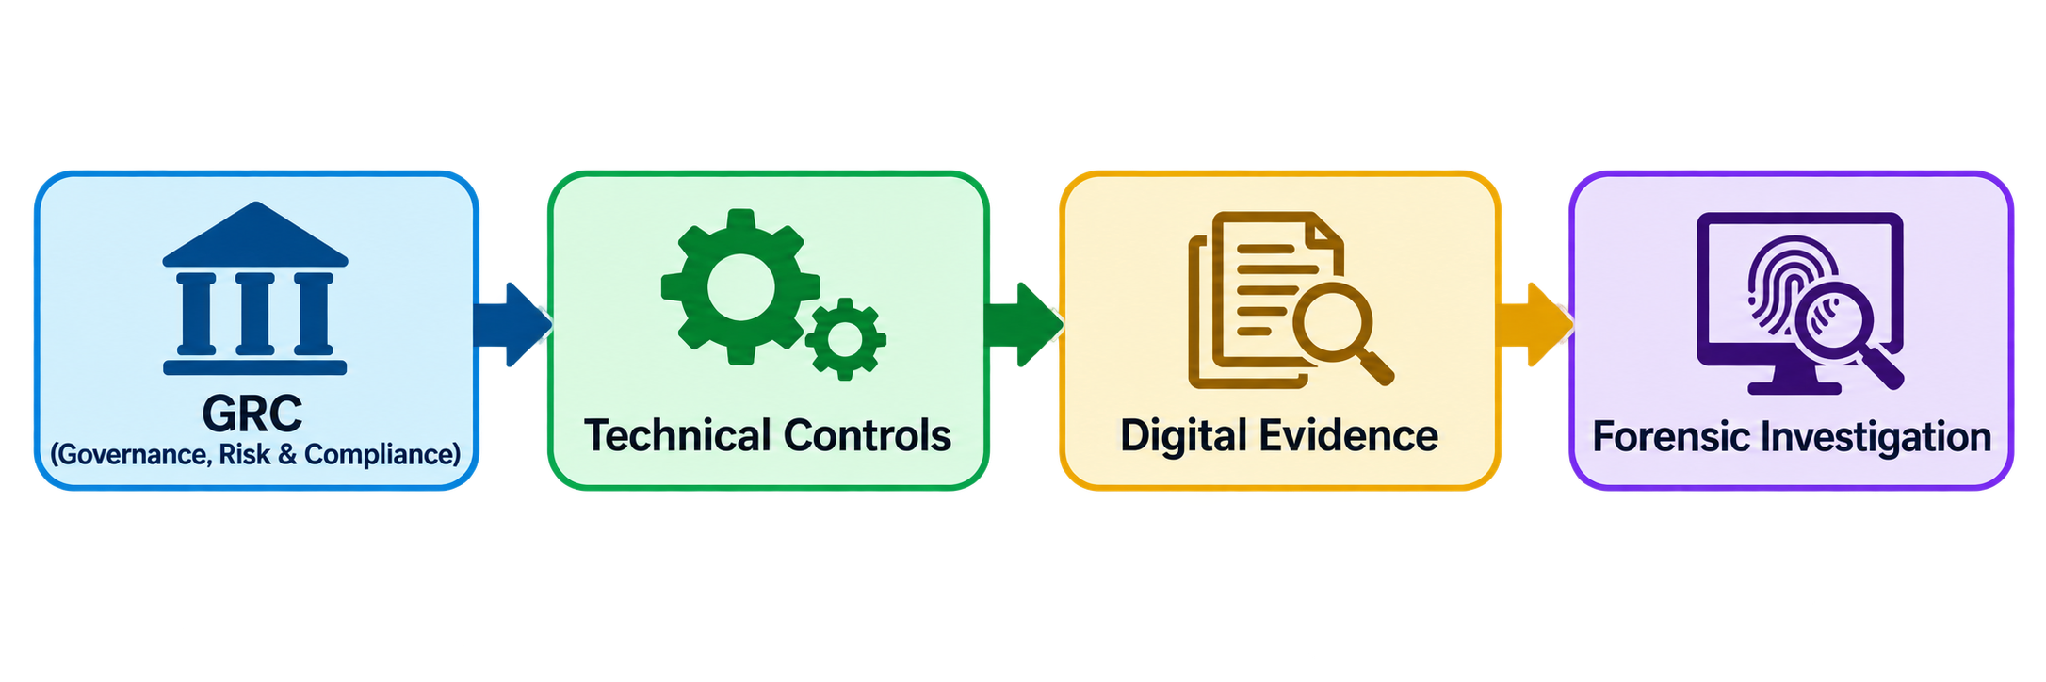
Put all of this together and a pattern emerges. The law assumes an organisation already knows what it's protecting, has actually protected it, kept usable records the whole way through, and can explain clearly what happened the moment something breaks. That coordination job belongs to Governance, Risk and Compliance, or GRC for short. GRC decides who's accountable, which risks actually matter, which controls address them, and how anyone checks whether compliance is real rather than assumed. Skip that structure and security work tends to splinter into a pile of disconnected tasks nobody truly owns.
GRC gives a legal duty somewhere to live. Forensic readiness is what lets an organisation prove, months or years later, that the duty was actually being met.
The Role of Governance, Risk and Compliance
On paper, most cybersecurity programmes look fine. There's an incident response plan somewhere, access control rules exist, logging is "in place," and someone has a title that says they're responsible for security. None of that gets tested until something actually breaks. A phishing compromise, a ransomware infection, a leaked database, a hijacked admin account, whatever the trigger, the questions that follow are always the same, and they're not comfortable ones. What happened, exactly, and when did it start? Which systems, which data, were actually touched? Were the controls the organisation claims to run genuinely functioning at that moment, or just described in a slide deck somewhere? And can anyone produce records solid enough to answer those questions with confidence rather than a shrug?
This is the exact seam where GRC and digital forensics meet. GRC lays out what's expected, who's responsible, and what evidence a control should be generating in the background. Digital forensics is the craft of taking whatever technical traces actually exist and turning them into an account of events that will hold up to scrutiny. Passing an audit was never really the point. Being able to stand in front of a regulator, mid incident, and show that the processes described on paper were real, active, and generating trustworthy evidence, that's the actual bar.
Why Compliance Alone Falls Short
Compliance, in the narrow sense, just means meeting whatever legal, contractual, or internal requirement applies. But a policy sitting in a document repository proves nothing about what actually happens on a Tuesday afternoon when someone requests admin access. A written incident response plan says nothing about whether the team can actually execute it under real pressure, at 2am, with a ransomware note on every screen. A logging policy is close to worthless if the logs it promises were switched off somewhere along the way, or overwritten, or scattered across systems that were never synchronised to the same clock.
NIST's Cybersecurity Framework 2.0 essentially built this concern into its core structure, placing "Govern" alongside Identify, Protect, Detect, Respond, and Recover as one of five equal functions rather than background paperwork sitting off to the side. India's own regulatory posture pushes in the same direction. CERT-In's 2022 Directions require certain incidents to be reported within six hours of discovery, and its guidance for government entities leans heavily on documented incident handling and disciplined evidence practices. The underlying message from both is identical: figure out, before anything goes wrong, whether the evidence you'll eventually need is actually going to exist when someone asks for it.
Where GRC and Forensics Actually Connect
A good GRC programme spells out what's supposed to happen. Forensic readiness is what lets you later prove what actually did.
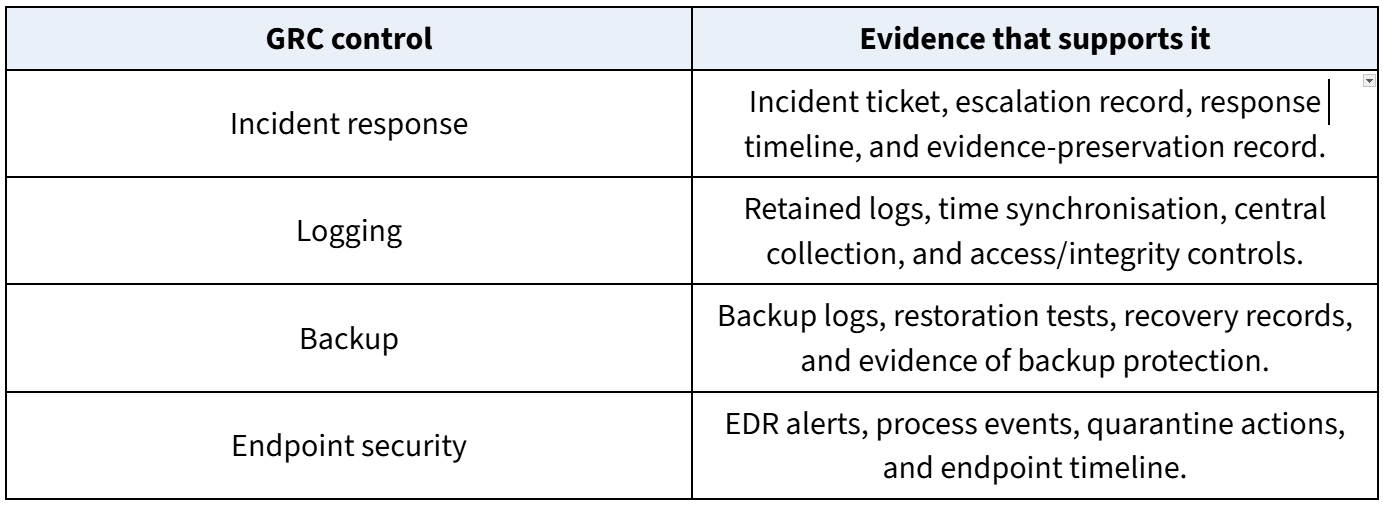
Access control is a useful example here. On the GRC side, an organisation might require least privilege access, multi factor authentication, periodic reviews of who holds privileged accounts, and prompt removal of access once someone leaves or changes roles. On the forensic side, none of that means anything without the underlying records that let investigators actually test it, authentication logs, MFA usage history, privilege change records, and account activity trails. The table below lines up a few common GRC controls against the specific evidence needed to show they were genuinely operating.
A Practical Scenario: After a Ransomware Incident
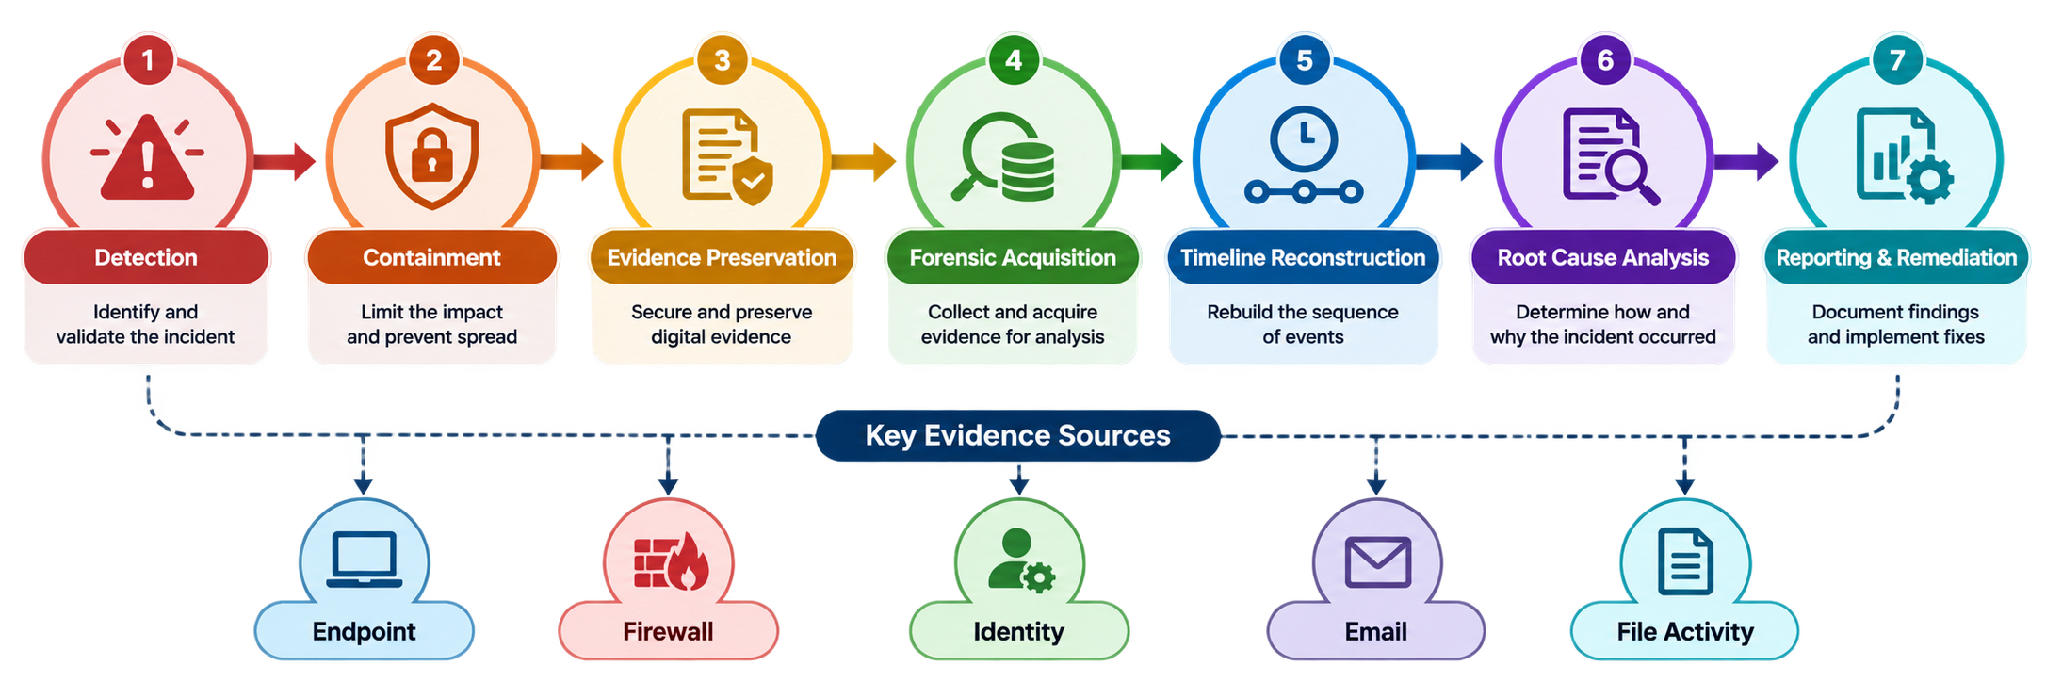
Picture a mid-sized company waking up to find half its file servers encrypted. There's an incident response plan somewhere in the shared drive, technically, but nobody's actually run through it in over a year. The security team isolates the obviously compromised endpoint and starts escalating. Now the forensic side of the house has to reconstruct what happened, working backward through endpoint telemetry, authentication logs, firewall events, email traffic, and file activity, hunting for the original point of entry, how the attacker escalated privileges, how they moved sideways through the network, what data they actually touched, and finally how the ransomware got deployed.
This is where the quality of everything collected beforehand suddenly matters a great deal. If server clocks were never properly synchronised, the timeline investigators build might not line up cleanly enough to trust. If logs only ever lived locally on individual machines rather than being pulled centrally, some of them are probably gone by now. If nobody ever bothered logging administrator actions, there are going to be real, unexplained gaps in the story. And if whatever evidence does exist wasn't collected the right way, its integrity can be challenged later, sometimes fatally, in a legal or regulatory proceeding. CERT-In actually ran a programme on exactly this in July 2026, "Inside the Breach," covering system artefacts, investigative technique, and chain of custody requirements, precisely because this is where real investigations tend to succeed or quietly fall apart.
Building a Forensic Ready GRC Programme
For an organisation starting more or less from scratch, forensic readiness doesn't need to be bolted on as some separate initiative. It can be built straight into the GRC programme that already exists. Start by identifying the systems, applications, cloud services, and privileged accounts that actually matter. Map the real risks and regulatory requirements onto the controls meant to address them. Then get specific about what evidence each control should be generating, and how that evidence gets protected and kept over time. Time synchronisation, centralised logging, tightly controlled access to security records, and clear ownership of preservation, escalation, and investigation all need to exist well before an incident, not be improvised during one. And none of it means much until it's actually been tested, through tabletop exercises and simulated incidents rather than assumed to work because it's written down somewhere. NIST SP 800-61 Revision 3 frames incident response as one continuous loop of preparation, detection, response, recovery, and improvement, rather than a series of separate boxes to check.
There's one question worth asking of every important control an organisation runs: could you actually prove this was working at the moment an incident happened? If the honest answer is no, what you have is a compliance process on paper, and a forensic readiness gap sitting quietly underneath it.
Conclusion
Cyber readiness was never really about how many policies sit in a binder or how many boxes get ticked in an audit. It shows up, or doesn't, in the hours right after something breaks, when an organisation has to move fast, preserve evidence that can actually stand up to scrutiny, explain clearly what happened, and prove that governance and technical controls were genuinely working together rather than just coexisting on paper. GRC sets the direction, the accountability, the risk priorities, and the compliance expectations. Digital forensics does the work of preserving and interpreting the technical evidence once something actually happens. Forensic readiness sits in between the two, making sure they're actually talking to each other long before an incident forces the conversation. The practical task for most organisations comes down to something simple to say, if not always simple to build: design controls that hold up under real incident response, not just an auditor's checklist. The strongest compliance posture was never the one with the thickest binder. It's the one that can back every document up with evidence, on the day it actually matters.
References
- Digital Personal Data Protection Act, 2023, Sections 8(4), 8(5), 8(6). https://www.meity.gov.in/writereaddata/files/Digital%20Personal%20Data%20Protection%20Act%202023.pdf
- Digital Personal Data Protection Rules, 2025, Rules 6 and 7, notified 13 November 2025. https://www.meity.gov.in
- National Institute of Standards and Technology, The NIST Cybersecurity Framework (CSF) 2.0, CSWP 29, 2024. https://csrc.nist.gov/pubs/cswp/29/the-nist-cybersecurity-framework-csf-20/final
- Indian Computer Emergency Response Team (CERT-In), Directions under Section 70B of the Information Technology Act, 2000, dated 28 April 2022. https://www.cert-in.org.in/Directions70B.jsp
- Indian Computer Emergency Response Team (CERT-In), Guidelines on Information Security Practices for Government Entities. https://www.cert-in.org.in/Downloader?fileName=CIPS-2026-0014.pdf&pageid=5&type=2
- National Institute of Standards and Technology, SP 800-86: Guide to Integrating Forensic Techniques into Incident Response, 2006. https://csrc.nist.gov/pubs/sp/800/86/final
- International Organization for Standardization, ISO/IEC 27037:2012, Guidelines for identification, collection, acquisition and preservation of digital evidence. CERT-In, "Inside the Breach: Advanced Cyber Forensics & Incident Investigation," 31 July 2026. https://www.cert-in.org.in/s2cMainServlet?pageid=PRSTNVIEW03&reCode=CIWS-2026-3569
- National Institute of Standards and Technology, SP 800-61 Rev. 3: Incident Response Recommendations and Considerations for Cybersecurity Risk Management, 2025. https://csrc.nist.gov/pubs/sp/800/61/r3/final
- Matters.ai, "DPDP Breach Notification: 72-Hour Rule & ₹200 Cr Penalty." https://www.matters.ai/article/dpdp-breach-notification MediaNama, "Data Breach Reporting Timeline of DPDP Rules 2025 Explained." https://www.medianama.com/2025/11/223-data-breach-reporting-timeline-of-dpdp-rules-2025-explained/

Introduction
AI has transformed the way we look at advanced technologies. As the use of AI is evolving, it also raises a concern about AI-based deepfake scams. Where scammers use AI technologies to create deep fake videos, images and audio to deceive people and commit AI-based crimes. Recently a Kerala man fall victim to such a scam. He received a WhatsApp video call, the scammer impersonated the face of the victim’s known friend using AI-based deep fake technology. There is a need for awareness and vigilance to safeguard ourselves from such incidents.
Unveiling the Kerala deep fake video call Scam
The man in Kerala received a WhatsApp video call from a person claiming to be his former colleague in Andhra Pradesh. In actuality, he was the scammer. He asked for help of 40,000 rupees from the Kerala man via google pay. Scammer to gain the trust even mentioned some common friends with the victim. The scammer said that he is at the Dubai airport and urgently need the money for the medical emergency of his sister.
As AI is capable of analysing and processing data such as facial images, videos, and audio creating a realistic deep fake of the same which closely resembles as real one. In the Kerala Deepfake video call scam the scammer made a video call that featured a convincingly similar facial appearance and voice as same to the victim’s colleague which the scammer was impersonating. The Kerala man believing that he was genuinely communicating with his colleague, transferred the money without hesitation. The Kerala man then called his former colleague on the number he had saved earlier in his contact list, and his former colleague said that he has not called him. Kerala man realised that he had been cheated by a scammer, who has used AI-based deep-fake technology to impersonate his former colleague.
Recognising Deepfake Red Flags
Deepfake-based scams are on the rise, as they pose challenges that really make it difficult to distinguish between genuine and fabricated audio, videos and images. Deepfake technology is capable of creating entirely fictional photos and videos from scratch. In fact, audio can be deepfaked too, to create “voice clones” of anyone.
However, there are some red flags which can indicate the authenticity of the content:
- Video quality- Deepfake videos often have compromised or poor video quality, and unusual blur resolution, which might pose a question to its genuineness.
- Looping videos: Deepfake videos often loop or unusually freeze or where the footage repeats itself, indicating that the video content might be fabricated.
- Verify Separately: Whenever you receive requests for such as financial help, verify the situation by directly contacting the person through a separate channel such as a phone call on his primary contact number.
- Be vigilant: Scammers often possess a sense of urgency leading to giving no time to the victim to think upon it and deceiving them by making a quick decision. So be vigilant and cautious when receiving and entertaining such a sudden emergency which demands financial support from you on an urgent basis.
- Report suspicious activity: If you encounter such activities on your social media accounts or through such calls report it to the platform or to the relevant authority.
Conclusion
The advanced nature of AI deepfake technology has introduced challenges in combatting such AI-based cyber crimes. The Kerala man’s case of falling victim to an AI-based deepfake video call and losing Rs 40,000 serves as an alarming need to remain extra vigilant and cautious in the digital age. So in the reported incident where Kerala man received a call from a person appearing as his former colleague but in actuality, he was a scammer and tricking the victim by using AI-based deepfake technology. By being aware of such types of rising scams and following precautionary measures we can protect ourselves from falling victim to such AI-based cyber crimes. And stay protected from such malicious scammers who exploit these technologies for their financial gain. Stay cautious and safe in the ever-evolving digital landscape.
