
Children’s Privacy Online: Can Verification Avoid Creating New Risks?
Introduction
A child joining a learning platform may encounter a request for approval. I see that the step appears straightforward. The step raises a difficult question: how should the service verify consent without gathering unnecessary information about the family? India’s Digital Personal Data Protection Rules, 2025 provide mechanisms for parental consent with the relevant requirements subject to phased commencement. This creates an opportunity to examine how protection should work in practice. Verification can support accountability while designed systems could introduce additional collection and security risks. The policy challenge is to make consent meaningful while limiting exposure during the verification process. I think that consent should be clear and easy to give. Children’s privacy will depend on the design of the service well as the procedure used to obtain approval.
- Understanding the Legal Framework
The Digital Personal Data Protection Act 2023 says a child is someone who's under eighteen years old. Section 9 creates a plan about permission, harmful processing, tracking, watching behavior and ads aimed at children plus some exceptions.
Rule 10 in the 2025 Rules explains how to get confirmed permission. It says that the person who says they are the parent must be an adult who can be identified using identity and age information or special digital codes.
Starting to use the rules needs explanation. Rule 1 says that Rules 3 5 to 16, 22 and 23 will begin after eighteen months from the day they are published. Rule 10 is part of that group. People who write about this should make sure to separate the framework from rules that are already in place.
This difference also helps companies get ready properly. Putting the rules into action means making choices, about alerts, checking identities, keeping data letting people see it and handling complaints. Looking at the framework as something to design gives advantage rather than just making compliance about clicking one button.
- Consent and Age Checks Serve Different Purposes
Determining whether a user is a child and verifying the adult who provides consent are tasks but these tasks answer different questions. A service may need to understand which safeguards apply to an account. The service must separately consider whether its consent process meets the requirements.
For example, a hypothetical learning service might already hold adult identity information, for a parent who pays for an account. Another family may approach the service for the time. These circumstances raise implementation questions even when both families want the same educational access.
Designers should map these situations before choosing a verification process. Designers should identify what each check establishes, what remains uncertain and what evidence is necessary. Collecting documents without a clear purpose can complicate the process without resolving the underlying issue. A careful system should be able to explain why information is requested and how it contributes to the verification task.
- The Privacy Cost of Verification
Verification can create a tension between feeling safe and being exposed. A service that wants to be sure about a person’s age may think about asking for identity information. The process should also look at whether keeping that information creates risks that go beyond the original purpose.
Consider a platform that keeps full document images forever after it finishes a check. The policy concern for Verification is whether the ongoing exposure is justified by a continuing need. Verification of a result and an entire identity document are kinds of information and they have different consequences if they are accessed improperly.
Privacy‑conscious design, for Verification should therefore look at collection and retention separately. Verification teams should ask what information must be received, what evidence must stay, who needs access and when deletion is appropriate following legal rules. Verification should not become a chance to build profiles. Verification safeguards should be checked before a system becomes routine when fixing a wide design may be harder.
- Making Protection Accessible to Families
Even if a process is technically sound it can still leave people out when it assumes that every parent owns a smartphone, has the internet and feels confident using digital identity services. The policy objective must provide a route that fits families with varied circumstances and abilities
Services should give explanations that anyone can understand, offer language options that suit each user and give help when verification fails. A clear error message should show a person what to do keeping sensitive details private. If a person keeps failing the process should trigger a review rather than an unexplained rejection.
Children also need to understand. Parental consent alone does not remove the need to explain things to the child. A service can use age‑appropriate language to tell the child what data it collects and how the child can get help. The design must not push families to approve. An accessible process offers everyone a chance to grasp the decision and finish it without extra pressure or confusion.
- Moving Beyond the Consent Screen
Consent is one part of a safety architecture. A platform should also look at the experience that happens after someone agrees. Which features are turned on what information other people can. Whether the design pushes someone to share more than they need to.
A pretend educational app might need a child's progress detail to give lessons. That does not mean every extra social feature should be turned on automatically. Teams that make products should check each feature on its own. Tell people why it is there instead of thinking that saying yes once means all future choices are settled.
Moving between accounts needs thinking about too. Services should think about how information and permissions will be checked as users get older and their lives change. They should also make it clear how to fix mistakes or report problems. Good management means people inside a company have to take charge of these choices. A privacy statement by itself cannot show if the real service matches the promises, in the written rules.
Conclusion
Children’s privacy needs to be protected through a balance between legal rules and everyday choices made by product creators. The DPDP framework offers a foundation for looking at parental consent. Putting it into practice also means thinking about fairness, how easy it is for people to use and how verification data is handled. Services should explain clearly what they need, why they need information and how they will keep data exposure to a minimum. When something goes wrong in the process families should get explanations and real help. Kids should not face a risky experience. Instead, the design should put children’s being first. Ultimately success means that verification helps make the service safer, without compromising the privacy of the children it is meant to protect.
References
- https://www.meity.gov.in/static/uploads/2024/06/2bf1f0e9f04e6fb4f8fef35e82c42aa5.pdf
- https://www.meity.gov.in/static/uploads/2025/11/53450e6e5dc0bfa85ebd78686cadad39.pdf

Related Blogs

Overview:
The rapid digitization of educational institutions in India has created both opportunities and challenges. While technology has improved access to education and administrative efficiency, it has also exposed institutions to significant cyber threats. This report, published by CyberPeace, examines the types, causes, impacts, and preventive measures related to cyber risks in Indian educational institutions. It highlights global best practices, national strategies, and actionable recommendations to mitigate these threats.

Significance of the Study:
The pandemic-induced shift to online learning, combined with limited cybersecurity budgets, has made educational institutions prime targets for cyberattacks. These threats compromise sensitive student, faculty, and institutional data, leading to operational disruptions, financial losses, and reputational damage. Globally, educational institutions face similar challenges, emphasizing the need for universal and localized responses.
Threat Faced by Education Institutions:
Based on the insights from the CyberPeace’s report titled 'Exploring Cyber Threats and Digital Risks in Indian Educational Institutions', this concise blog provides a comprehensive overview of cybersecurity threats and risks faced by educational institutions, along with essential details to address these challenges.
🎣 Phishing: Phishing is a social engineering tactic where cyber criminals impersonate trusted sources to steal sensitive information, such as login credentials and financial details. It often involves deceptive emails or messages that lead to counterfeit websites, pressuring victims to provide information quickly. Variants include spear phishing, smishing, and vishing.
💰 Ransomware: Ransomware is malware that locks users out of their systems or data until a ransom is paid. It spreads through phishing emails, malvertising, and exploiting vulnerabilities, causing downtime, data leaks, and theft. Ransom demands can range from hundreds to hundreds of thousands of dollars.
🌐 Distributed Denial of Service (DDoS): DDoS attacks overwhelm servers, denying users access to websites and disrupting daily operations, which can hinder students and teachers from accessing learning resources or submitting assignments. These attacks are relatively easy to execute, especially against poorly protected networks, and can be carried out by amateur cybercriminals, including students or staff, seeking to cause disruptions for various reasons
🕵️ Cyber Espionage: Higher education institutions, particularly research-focused universities, are vulnerable to spyware, insider threats, and cyber espionage. Spyware is unauthorized software that collects sensitive information or damages devices. Insider threats arise from negligent or malicious individuals, such as staff or vendors, who misuse their access to steal intellectual property or cause data leaks..
🔒 Data Theft: Data theft is a major threat to educational institutions, which store valuable personal and research information. Cybercriminals may sell this data or use it for extortion, while stealing university research can provide unfair competitive advantages. These attacks can go undetected for long periods, as seen in the University of California, Berkeley breach, where hackers allegedly stole 160,000 medical records over several months.
🛠️ SQL Injection: SQL injection (SQLI) is an attack that uses malicious code to manipulate backend databases, granting unauthorized access to sensitive information like customer details. Successful SQLI attacks can result in data deletion, unauthorized viewing of user lists, or administrative access to the database.
🔍Eavesdropping attack: An eavesdropping breach, or sniffing, is a network attack where cybercriminals steal information from unsecured transmissions between devices. These attacks are hard to detect since they don't cause abnormal data activity. Attackers often use network monitors, like sniffers, to intercept data during transmission.
🤖 AI-Powered Attacks: AI enhances cyber attacks like identity theft, password cracking, and denial-of-service attacks, making them more powerful, efficient, and automated. It can be used to inflict harm, steal information, cause emotional distress, disrupt organizations, and even threaten national security by shutting down services or cutting power to entire regions
Insights from Project eKawach
The CyberPeace Research Wing, in collaboration with SAKEC CyberPeace Center of Excellence (CCoE) and Autobot Infosec Private Limited, conducted a study simulating educational institutions' networks to gather intelligence on cyber threats. As part of the e-Kawach project, a nationwide initiative to strengthen cybersecurity, threat intelligence sensors were deployed to monitor internet traffic and analyze real-time cyber attacks from July 2023 to April 2024, revealing critical insights into the evolving cyber threat landscape.
Cyber Attack Trends
Between July 2023 and April 2024, the e-Kawach network recorded 217,886 cyberattacks from IP addresses worldwide, with a significant portion originating from countries including the United States, China, Germany, South Korea, Brazil, Netherlands, Russia, France, Vietnam, India, Singapore, and Hong Kong. However, attributing these attacks to specific nations or actors is complex, as threat actors often use techniques like exploiting resources from other countries, or employing VPNs and proxies to obscure their true locations, making it difficult to pinpoint the real origin of the attacks.
Brute Force Attack:
The analysis uncovered an extensive use of automated tools in brute force attacks, with 8,337 unique usernames and 54,784 unique passwords identified. Among these, the most frequently targeted username was “root,” which accounted for over 200,000 attempts. Other commonly targeted usernames included: "admin", "test", "user", "oracle", "ubuntu", "guest", "ftpuser", "pi", "support"
Similarly, the study identified several weak passwords commonly targeted by attackers. “123456” was attempted over 3,500 times, followed by “password” with over 2,500 attempts. Other frequently targeted passwords included: "1234", "12345", "12345678", "admin", "123", "root", "test", "raspberry", "admin123", "123456789"

Insights from Threat Landscape Analysis
Research done by the USI - CyberPeace Centre of Excellence (CCoE) and Resecurity has uncovered several breached databases belonging to public, private, and government universities in India, highlighting significant cybersecurity threats in the education sector. The research aims to identify and mitigate cybersecurity risks without harming individuals or assigning blame, based on data available at the time, which may evolve with new information. Institutions were assigned risk ratings that descend from A to F, with most falling under a D rating, indicating numerous security vulnerabilities. Institutions rated D or F are 5.4 times more likely to experience data breaches compared to those rated A or B. Immediate action is recommended to address the identified risks.


Risk Findings :
The risk findings for the institutions are summarized through a pie chart, highlighting factors such as data breaches, dark web activity, botnet activity, and phishing/domain squatting. Data breaches and botnet activity are significantly higher compared to dark web leakages and phishing/domain squatting. The findings show 393,518 instances of data breaches, 339,442 instances of botnet activity, 7,926 instances related to the dark web and phishing & domain activity - 6711.

Key Indicators: Multiple instances of data breaches containing credentials (email/passwords) in plain text.


- Botnet activity indicating network hosts compromised by malware.

- Credentials from third-party government and non-governmental websites linked to official institutional emails

- Details of software applications, drivers installed on compromised hosts.

- Sensitive cookie data exfiltrated from various browsers.


- IP addresses of compromised systems.
- Login credentials for different Android applications.

Below is the sample detail of one of the top educational institutions that provides the insights about the higher rate of data breaches, botnet activity, dark web activities and phishing & domain squatting.
Risk Detection:
It indicates the number of data breaches, network hygiene, dark web activities, botnet activities, cloud security, phishing & domain squatting, media monitoring and miscellaneous risks. In the below example, we are able to see the highest number of data breaches and botnet activities in the sample particular domain.

Risk Changes:

Risk by Categories:

Risk is categorized with factors such as high, medium and low, the risk is at high level for data breaches and botnet activities.

Challenges Faced by Educational Institutions
Educational institutions face cyberattack risks, the challenges leading to cyberattack incidents in educational institutions are as follows:
🔒 Lack of a Security Framework: A key challenge in cybersecurity for educational institutions is the lack of a dedicated framework for higher education. Existing frameworks like ISO 27001, NIST, COBIT, and ITIL are designed for commercial organizations and are often difficult and costly to implement. Consequently, many educational institutions in India do not have a clearly defined cybersecurity framework.
🔑 Diverse User Accounts: Educational institutions manage numerous accounts for staff, students, alumni, and third-party contractors, with high user turnover. The continuous influx of new users makes maintaining account security a challenge, requiring effective systems and comprehensive security training for all users.
📚 Limited Awareness: Cybersecurity awareness among students, parents, teachers, and staff in educational institutions is limited due to the recent and rapid integration of technology. The surge in tech use, accelerated by the pandemic, has outpaced stakeholders' ability to address cybersecurity issues, leaving them unprepared to manage or train others on these challenges.
📱 Increased Use of Personal/Shared Devices: The growing reliance on unvetted personal/Shared devices for academic and administrative activities amplifies security risks.
💬 Lack of Incident Reporting: Educational institutions often neglect reporting cyber incidents, increasing vulnerability to future attacks. It is essential to report all cases, from minor to severe, to strengthen cybersecurity and institutional resilience.
Impact of Cybersecurity Attacks on Educational Institutions
Cybersecurity attacks on educational institutions lead to learning disruptions, financial losses, and data breaches. They also harm the institution's reputation and pose security risks to students. The following are the impacts of cybersecurity attacks on educational institutions:
📚Impact on the Learning Process: A report by the US Government Accountability Office (GAO) found that cyberattacks on school districts resulted in learning losses ranging from three days to three weeks, with recovery times taking between two to nine months.
💸Financial Loss: US schools reported financial losses ranging from $50,000 to $1 million due to expenses like hardware replacement and cybersecurity upgrades, with recovery taking an average of 2 to 9 months.
🔒Data Security Breaches: Cyberattacks exposed sensitive data, including grades, social security numbers, and bullying reports. Accidental breaches were often caused by staff, accounting for 21 out of 25 cases, while intentional breaches by students, comprising 27 out of 52 cases, frequently involved tampering with grades.
⚠️Data Security Breach: Cyberattacks on schools result in breaches of personal information, including grades and social security numbers, causing emotional, physical, and financial harm. These breaches can be intentional or accidental, with a US study showing staff responsible for most accidental breaches (21 out of 25) and students primarily behind intentional breaches (27 out of 52) to change grades.
🏫Impact on Institutional Reputation: Cyberattacks damaged the reputation of educational institutions, eroding trust among students, staff, and families. Negative media coverage and scrutiny impacted staff retention, student admissions, and overall credibility.
🛡️ Impact on Student Safety: Cyberattacks compromised student safety and privacy. For example, breaches like live-streaming school CCTV footage caused severe distress, negatively impacting students' sense of security and mental well-being.
CyberPeace Advisory:
CyberPeace emphasizes the importance of vigilance and proactive measures to address cybersecurity risks:
- Develop effective incident response plans: Establish a clear and structured plan to quickly identify, respond to, and recover from cyber threats. Ensure that staff are well-trained and know their roles during an attack to minimize disruption and prevent further damage.
- Implement access controls with role-based permissions: Restrict access to sensitive information based on individual roles within the institution. This ensures that only authorized personnel can access certain data, reducing the risk of unauthorized access or data breaches.
- Regularly update software and conduct cybersecurity training: Keep all software and systems up-to-date with the latest security patches to close vulnerabilities. Provide ongoing cybersecurity awareness training for students and staff to equip them with the knowledge to prevent attacks, such as phishing.
- Ensure regular and secure backups of critical data: Perform regular backups of essential data and store them securely in case of cyber incidents like ransomware. This ensures that, if data is compromised, it can be restored quickly, minimizing downtime.
- Adopt multi-factor authentication (MFA): Enforce Multi-Factor Authentication(MFA) for accessing sensitive systems or information to strengthen security. MFA adds an extra layer of protection by requiring users to verify their identity through more than one method, such as a password and a one-time code.
- Deploy anti-malware tools: Use advanced anti-malware software to detect, block, and remove malicious programs. This helps protect institutional systems from viruses, ransomware, and other forms of malware that can compromise data security.
- Monitor networks using intrusion detection systems (IDS): Implement IDS to monitor network traffic and detect suspicious activity. By identifying threats in real time, institutions can respond quickly to prevent breaches and minimize potential damage.
- Conduct penetration testing: Regularly conduct penetration testing to simulate cyberattacks and assess the security of institutional networks. This proactive approach helps identify vulnerabilities before they can be exploited by actual attackers.
- Collaborate with cybersecurity firms: Partner with cybersecurity experts to benefit from specialized knowledge and advanced security solutions. Collaboration provides access to the latest technologies, threat intelligence, and best practices to enhance the institution's overall cybersecurity posture.
- Share best practices across institutions: Create forums for collaboration among educational institutions to exchange knowledge and strategies for cybersecurity. Sharing successful practices helps build a collective defense against common threats and improves security across the education sector.
Conclusion:
The increasing cyber threats to Indian educational institutions demand immediate attention and action. With vulnerabilities like data breaches, botnet activities, and outdated infrastructure, institutions must prioritize effective cybersecurity measures. By adopting proactive strategies such as regular software updates, multi-factor authentication, and incident response plans, educational institutions can mitigate risks and safeguard sensitive data. Collaborative efforts, awareness, and investment in cybersecurity will be essential to creating a secure digital environment for academia.
Executive Summary
A 57-second video featuring India’s Chief of Army Staff Upendra Dwivedi is widely circulating on social media. The clip is being shared with the claim that the Army chief admitted India had “betrayed” Iran by providing the location of an Iranian naval ship to Israel, allegedly leading to its destruction The video is spreading amid heightened tensions in West Asia involving United States, Israel, and Iran. According to posts sharing the claim, the Iranian naval vessel IRIS Dena, which had participated in a naval event in Visakhapatnam and was returning to Iran with around 130 personnel onboard, was torpedoed by a US submarine near the southern coast of Sri Lanka on March 4 while sailing in the Indian Ocean.
In the viral clip, the speaker—presented as the Indian Army chief—appears to say that India informed Israel about the exact location of the Iranian ship after it left Indian waters, describing Israel as a strategic ally and suggesting that the attack occurred in international waters. The clip also claims that India had no direct involvement in the alleged joint US-Israel torpedo strike.
However, research conducted by the CyberPeace found the claim to be false. Our research shows that the video does not contain a genuine statement from Army Chief Upendra Dwivedi and is in fact a manipulated clip.
Claim
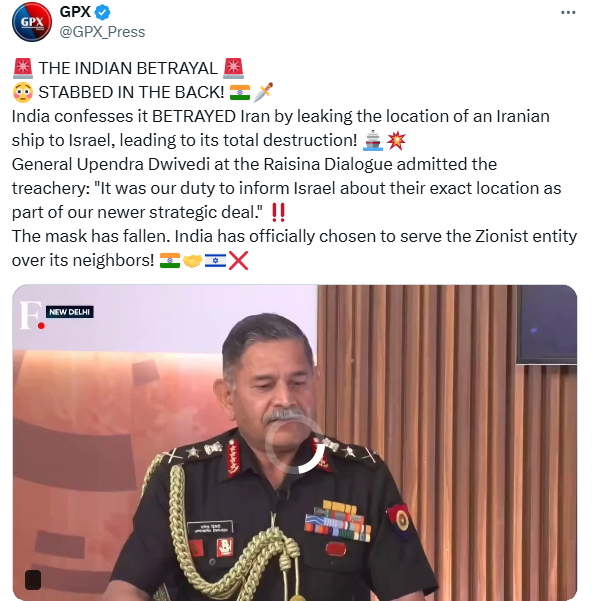
On X (formerly Twitter), a page named GPX (@GPX_Press) shared the video on March 9 with the caption: “India confesses it BETRAYED Iran by leaking the location of an Iranian ship to Israel, leading to its total destruction!”
Fact Check
During the verification process, researchers noticed a ticker in the viral video reading “Raisina Dialogue 2026 × Firstpost.” Using this clue, we conducted a keyword search on YouTube and located a video uploaded by Firstpost on March 7 titled “India’s Army Chief Speaks on Op Sindoor, Pakistan and Future of Warfare | Raisina Dialogue 2026.”
In the 21-minute interview, Army Chief Upendra Dwivedi is seen speaking with strategic affairs expert Harsh V. Pant. According to the video description, the discussion focuses on lessons from Operation Sindoor and the evolving nature of modern warfare.

The viral clip appears to be taken from this interview. However, throughout the conversation, Dwivedi does not mention any conflict involving the United States, Israel, and Iran, nor does he refer to the sinking of an Iranian naval ship in the Indian Ocean. This indicates that the circulating clip has been edited and misrepresented to create a misleading narrative.
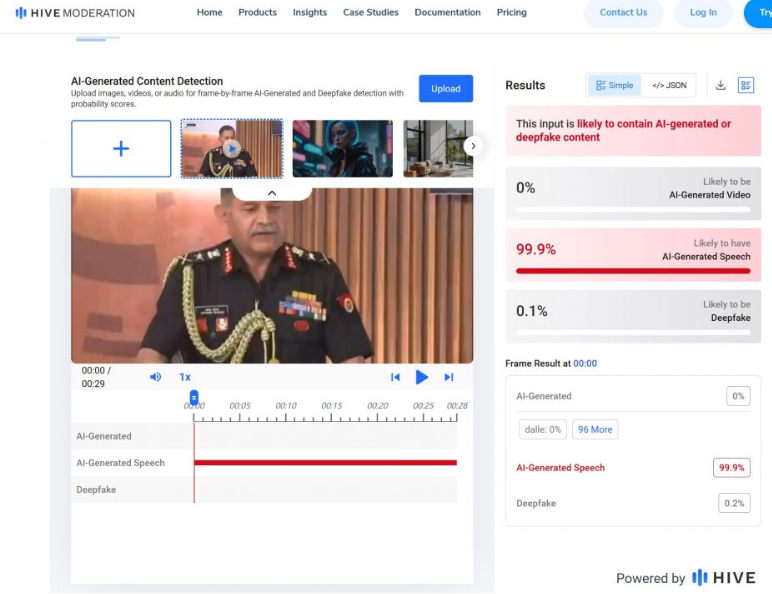
For additional verification, the viral video was analyzed using the AI detection tool Hive Moderation. The results suggested a 99.9% probability that the speech in the clip was generated using AI, indicating manipulation of the original footage.
Conclusion
The research makes it clear that the viral video does not reflect an authentic statement by India’s Army Chief Upendra Dwivedi. The clip has been altered and the audio appears to be AI-generated. In other words, the circulating video is a deepfake being shared with a misleading claim.

2025 is knocking firmly at our door and we have promises to make and resolutions to keep. Time you make your list for the New Year and check it twice.
- Lifestyle targets 🡪 Check
- Family targets 🡪 Check
- Social targets 🡪 Check
Umm, so far so good, but what about your cybersecurity targets for the year? Hey, you look confused and concerned. Wait a minute, you do not have one, do you?
I get it. Though the digital world still puzzles, and sometimes outright scares us, we still are not in the ‘Take-Charge-Of-Your-Digital-Safety Mode. We prefer to depend on whatever software security we are using and keep our fingers crossed that the bad guys (read threat actors) do not find us.
Let me illustrate why cybersecurity should be one of your top priorities. You know that stress is a major threat to our continued good health, right? However, if your devices, social media accounts, office e-mail or network, or God forbid, bank accounts become compromised, would that not cause stress? Think about it and the probable repercussions and you will comprehend why I am harping on prioritising security.
Fret not. We will keep it brief as we well know you have 101 things to do in the next few days leading up to 01/01/2025. Just add cyber health to the list and put in motion the following:
- Install and activate comprehensive security software on ALL internet-enabled devices you have at home. Yes, including your smartphones.
- Set yourself a date to change and create separate unique passwords for all accounts. Or use the password manager that comes with all reputed security software to make life simpler.
- Keep home Wi-Fi turned off at night
- Do not set social media accounts to auto-download photos/documents
- Activate parental controls on all the devices used by your children to monitor and mentor them. But keep them apprised.
- Do not blindly trust anyone or anything online – this includes videos, speeches, emails, voice calls, and video calls. Be aware of fakes.
- Be aware of the latest threats and talk about unsafe cyber practices and behaviour often at home.
Short and sweet, as promised.
We will be back, with more tips, and answers to your queries. Drop us a line anytime, and we will be happy to resolve your doubts.
Ciao!
